

Nearly two decades ago, a group of researchers at the Idaho National Laboratory ran a secret experiment, known as the Aurora Generator Test, on a massive emerald green diesel generator. Using 30 lines of code, they hacked into the generator’s virtual backroom, corrupting safeguards and flipping switches that left it out of sync with the rest of the power grid.
Tech
10 Family Vehicles That Were Super Popular In The 80s

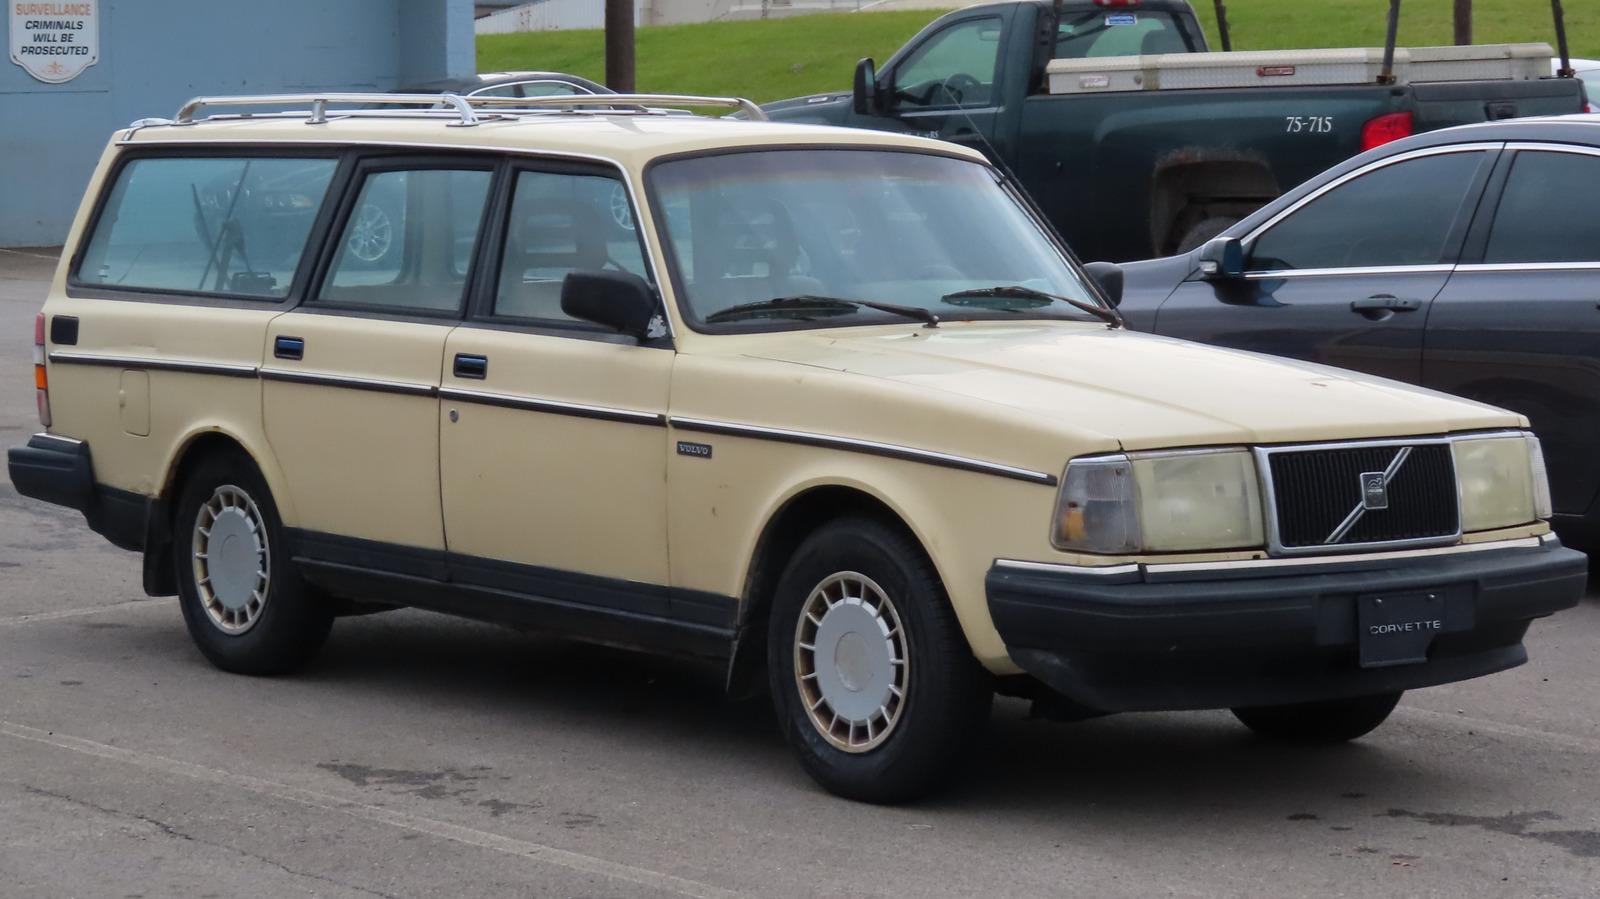
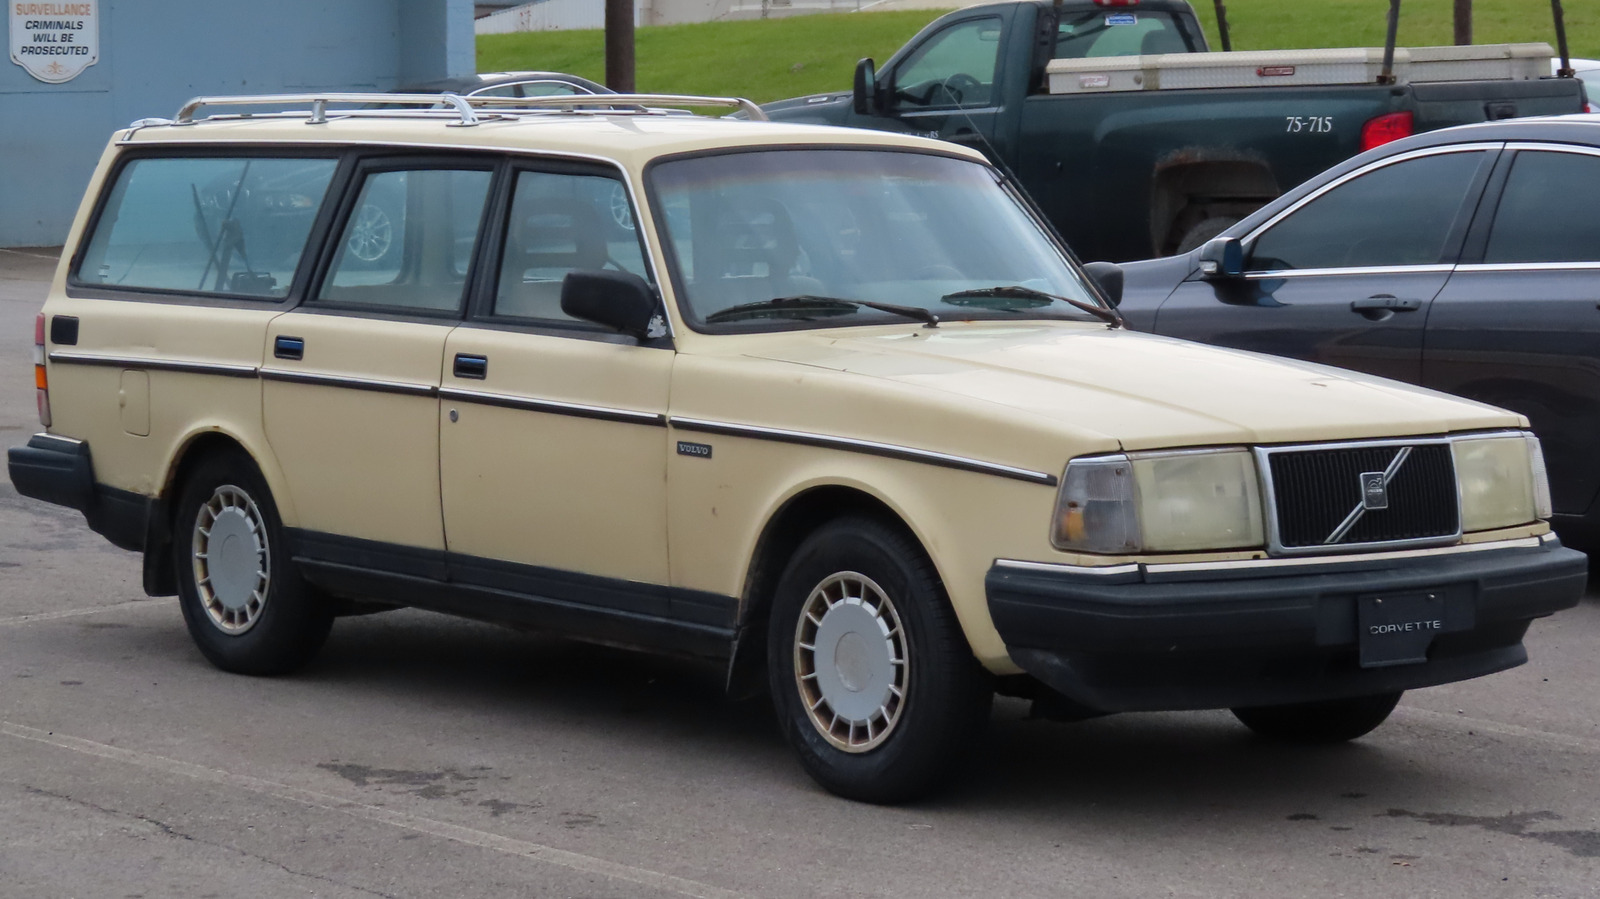
The ’80s were an interesting time for the automobile industry. In the wake of the gas crisis of the 1970s, one would think the Ronald Reagan free-market ’80s would go full tilt into sleek, gas-guzzling designs. To an extent, that kind of happened. You only need to watch any given episode from Miami Vice’s third season to see Don Johnson zipping around in a gorgeous Ferrari Testarossa, or any number of sweet rides every ’80s kid remembers.
However, the decade was also known for big cars with boxy designs, particularly for family cars, the kind of vehicle that generally wasn’t featured on Miami Vice. After all, while the dangerous glitz and glamour of southern Florida might have lent itself to fast sports cars, typical Americans were more concerned with having enough space to get the kids to middle school soccer games and loading up the trunk with groceries. To that end, family vehicles, frumpy though they may have been, dominated the decade.
Let’s take a look at 10 family vehicles that were super popular in the 1980s. While Sammy Hagar may not have had these vehicles in mind when he wrote “I Can’t Drive 55” in 1984, that’s fine, since you’re probably not going to get these vehicles up to that speed very often. At least, not with the kids in the backseat.
Ford LTD Crown Victoria Country Squire
Let us be clear: The vehicles on this list are not inherently bad or good. They were simply popular. If you’re a child of the ’80s, either your parents or those of one of your friends surely had a Ford LTD Crown Victoria Country Squire. It was so ubiquitous as the go-to family station wagon that it became the basis for the infamous Wagon Queen Family Truckster in “National Lampoon’s Vacation.”
While the “Vacation” Family Truckster was a disaster of a vehicle you’d never want to drive in real life, the Ford Country Squire was iconic. When you think of a typical station wagon, this is the vehicle that comes to mind, wood paneling and all.
Running on a V8 with a four-speed transmission, it is not a particularly smooth or fuel-efficient ride, but it’ll get you where you want to go. With its spacious interior, it was a good choice for cross-country family vacations, as long as the driver and navigator planned out a route that hit plenty of gas stations along the way. It was the ’80s, so you had to plan your trip beforehand; you couldn’t just hit the road and figure it out along the way. Thank heavens for MapQuest, right? While the Country Squire was in production in one form or another since 1950, the fact that the line was discontinued in 1991 cements its status as an ’80s icon.
Chrysler LeBaron Town & Country Station Wagon
The Chrysler K-car platform introduced in 1980 defined the automaker’s vehicles for the decade. Essentially, it meant that different cars were made using a common platform. This meant they used a lot of the same parts, at least deep down underneath, before they were split up and individualized for specific makes and models. The use of a common platform was an attempt by Chrysler to keep costs down and compete with cheaper Japanese competitors.
The Chrysler LeBaron Town & Country station wagon was never intended to be a top-of-the-line model, but what station wagon is? A station wagon is the kind of car you get when you have absolutely no intention of driving in the left lane, if you know what I mean. Even with steps taken to keep prices down, the 1983 LeBaron still cost over $10,000 to start. Not a bad price for an American station wagon. Of course, you could always shell out for more luxury trims, but that wasn’t always an option, especially for working-class families.
Ultimately, the LeBaron Town & Country station wagon proved popular enough to sit alongside the Crown Vic Country Squire as one of the ‘default’ station wagons of the time, and it’s fondly remembered by children of the era, if not by the parents who had to actually drive it. The Town & Country was discontinued by the end of the decade, replaced by a new minivan with the same name. If the era of the station wagon ended in the ’80s, then the ’90s belonged to minivans.
Third Generation Toyota Tercel
The big fear among American industrialists in the 1980s was that Japan would rise up to conquer the manufacturing world. After decades without a traditional standing army, the country was free to develop its infrastructure and industries. While that didn’t exactly come to pass thanks to the inevitable burst that happens to every bubble economy, there was no denying that the Japanese economy in the 1980s was tremendously powerful, and that came across in the rising popularity of Japanese cars, a popularity that continues to this day.
In 1986, the third-generation Toyota Tercel debuted in both compact and hatchback variations. While the compact could be a starter family vehicle, multiple kids hitting their teenage years means you’ll probably want to upgrade to the larger hatchback, which is effectively a station wagon.
Tercels of the era were quite inexpensive, with prices starting from just a little over $6,000. That’s less than half the starting price of something like the LTD Crown Victoria, the 1987 model of which started at over $14,000. Given the popularity and price of this Japanese family car, one can understand the fears of those who feared the collapse of the American motor industry. Ultimately, the American automobile industry did fail, but Japan didn’t have anything to do with it. The “Big Three” pretty much did it to themselves… but that’s a story for a different day.
Chevy Caprice
In the 1960s, the Chevy Caprice was a high-end luxury trim available for the Impala. In the 1980s, when the Impala disappeared for a few years, the Caprice took center stage, serving as a de facto replacement. But where the classic Impala was usually a ‘sleek on the outside, big on the inside’ mega sedan, the 1986 Caprice was available in both station wagon and sedan forms, with the latter referred to as the “Caprice Classic.”
While the sedan was quite spacious, we’re going to look at the station wagon version, which boasted support for eight passengers. It’s a huge car. Even more than most station wagons, the ’86 Caprice looks like a chunky sedan with a massive posterior welded onto the back. Back then, one of these cost between $11,000 and $12,000 or so, a reasonable price for a family vehicle. Of course, any money saved buying this instead of a more expensive vehicle would quickly be spent on gasoline, but such is the nature of American family cars, especially in the ’80s.
As of this writing, Caprice station wagons have been gone for 30 years. Even with ’80s nostalgia coming back here and there, it’s hard to imagine the Caprice, or any other station wagon, making any kind of significant comeback. In any case, while the station wagon is long gone, the Caprice sedan was a popular car for New York City taxicabs and police cars around the United States.
Oldsmobile Cutlass
From 1976 to 1983, the Oldsmobile Cutlass was one of the top-selling cars in the United States. The vehicle came in many variations, from two-door coupes to four-door sedans and, of course, massive station wagons for the whole family. Thus, it might be a little unfair to refer to all of these as a single car, but there’s still no denying that the Oldsmobile Cutlass was a household name in the ’70s and ’80s.
The four-door Cutlass sedan models were big enough to carry a whole family on their own with minimal discomfort, but the station wagon was obviously even bigger, and it operated alongside another Oldsmobile station wagon, the Custom Cruiser, another classic 1980s family car.
The GM A-body version of the Oldsmobile Cutlass Cruiser debuted in 1982, and the final A-body station wagon was the 1996 Buick Century Wagon, which was remarkably similar despite over a decade of auto-evolution. It’s impressive that Oldsmobile was still making station wagons so far into the 1990s, since I can’t imagine many were interested in buying them over a minivan. Perhaps the similarities between the Cutlass Cruiser and Century Wagon reflect the station wagon’s limited but specific sensibilities. You can’t improve on perfection, which is why many classic station wagons looked very similar until they were all replaced by minivans.
Ford Fiesta
Family cars come in all shapes and sizes. While the United States family car scene was mostly dominated by station wagons, other parts of the world had their own popular vehicles, such as the Ford XR2, better known as the Ford Fiesta.
To a generation of punk rock fans who don’t know anything about cars, the XR2 was immortalized in “David’s XR2,” a song from The Toy Dolls’ 1995 album, “Orcastrated”. The song has the eponymous automobile enthusiast David go on a joyride in his brand-new car, which he promptly flips. If you don’t know what a Ford Fiesta is, you might be expecting it to be a sleek British hot rod or a beefy hunk of American muscle. But it’s not.
The XR2, introduced in 1983, was an adorably unassuming supermini hatchback. Not a hot rod by any stretch of the imagination. Still, even the original MK1 XR2 was a surprisingly powerful little car, thanks to its light weight and a Kent engine that output 84bhp at 5,500 RPM. Like Han Solo’s Millennium Falcon, “She may not look like much, but she’s got it where it counts.” By 1995, when The Toy Dolls wrote their song about the car, the XR2 had been replaced by the XR3 for more than half a decade, and the XR4 was due to arrive by the end of the year, which just adds to the humor of David being so enthralled by the long-outdated Ford Fiesta XR2.
Ford Escort
By 1980, the Ford Pinto had developed an unfortunate reputation as a volatile and nigh-spontaneously combustible death trap. As a result, Ford needed a new economy car for the 1980s, which led to the 1981 North American debut of the Ford Escort, touted as Ford’s “World Car” for its international sensibilities and shared design philosophies with Ford’s overseas efforts — which included an Escort nameplate as far back as 1968.
The Ford Escort had multiple variations, including two-door and four-door hatchbacks and even a full-fledged station wagon. The cheapest version had a launch price of just over $5,600, which was a great price for a mid-1980s car. Of course, tons of trim options could bump the price up by several thousand dollars.
Throughout the 1980s, the Escort was revised significantly both aesthetically and under the hood, though the basic shape remained the same until the next-generation version of the car debuted in 1991 (with a 1992 model year). Future generations of the vehicle would move into new stylistic territory away from the core 1980s aesthetic until the car was retired in favor of the new Ford Focus in the early 21st century.
BMW 3-Series
The second generation of the BMW 3-Series, known as the E30, debuted in 1982. The vehicle was tremendously popular, with around 2.4 million units produced during its lifetime, which ended in 1994. Even today, the car is sought by collectors and automobile enthusiasts for its reliability, utility, and timeless style.
Even the oldest E30s had reasonably powerful, carburetor-fed 316 engines capable of outputting 73 bhp. Different models would boost that bhp to well above 100, with the 325i version outputting a righteous 171bhp thanks to Bosch Motronic automotive voodoo. If you’re looking to buy an E30 nowadays, the 325i is the most desirable version thanks to its lofty specs, though it’s much more expensive now than it was back in the day.
BMW retired the E30 series in 1990 when the 3-Series shifted to the E36, which was discontinued in 1998. While the BMW 3-Series looks less undeniably ’80s than some of the other cars on this list, its replacement in 1990 affirms its status as a relic of the Reagan years.
Volvo 240
While boxy sedans might not be as aerodynamic or sleek as today’s cars, they are charming and actually quite spacious on the inside. In the realm of boxy cars, few truly own the look like the Volvo 240. It’s so rigidly angular and aggressively ’80s in its look and shape, it circles back around to feeling timeless, almost like a 1950s family car.
Of course, there was also a station wagon, with each version offering more interior space than you might expect from a car of its type. I’m not saying you should live in the 1989 Volvo 240 station wagon like it’s an RV, but you probably could if you absolutely needed to.
The best part of the 240 was its perceived invincibility. Today, there are Volvo 240 station wagons with a million miles or more still out there on the road, chugging along on little more than solid maintenance. While obviously not every 240 will last that long, this is the kind of car that could potentially last a lifetime, as long as it doesn’t get totaled in an accident.
Toyota Camry V10
While the aforementioned Japanese takeover of the world never really happened, despite Japan’s history of truly spectacular vehicles, there’s no denying the popularity of Japanese cars, especially Toyota. Today, vehicles like the Camry, the Corolla, and the Prius are exceedingly common sights on the road. Ironically, the Camry, the vehicle with which we’re closing this list, was a tremendously popular export that never achieved the same fame in its home country. In fact, the 2025 Camry VX80 marked the first time a Toyota Camry was made available for export only, despite still being assembled in Japan.
Not including the Toyota Carina variant, the first proper Camry was the V10, which debuted in 1982 for the 1983 model year. Perhaps as a side effect of its front-drive layout, the Camry had a spacious interior. Considering the average American physique, maybe that’s why the Camry was so popular in the United States. I’m not judging; I’m just saying we’re a husky people!
Anyway, the Camry was light, fuel-efficient, and spacious, which made it the perfect vehicle for those who were environmentally conscious in the aftermath of the energy crisis of the 1970s. Of course, a 1980s Camry doesn’t have the same fuel efficiency as today’s hybrid cars, but the early Camry’s 40+ mpg on the highway is nothing to scoff at, even in 2026.
Continue Reading
Spotify spent most of its existence convincing listeners that music did not really require a screen. After building the largest paid audio-streaming service in the world, the company now appears rather interested in your eyeballs as well.
All 58 of Taylor Swift’s official music videos are now available to Spotify Premium subscribers in markets where its music-video beta is offered, stretching from “Tim McGraw” through 2026’s “Opalite.” Videos can be watched on Spotify’s TV, desktop, iOS and Android apps, giving one of the largest fanbases in popular music another reason to stay inside Spotify rather than opening YouTube.
The implementation is more important than simply dumping videos into another menu. Start playing a supported song, tap “Switch to video,” and the video begins at the same point; switch back to audio and the song continues without restarting. It is hardly revolutionary; YouTube Music introduced essentially the same concept seven years ago, but convenience has always been Spotify’s sharpest weapon.
Related Reading:
Spotify Did Not Invent Music Videos on a Streaming Service
Before anyone starts carving Daniel Ek’s face into Mount Rushmore, Spotify is rather late to this particular party.
Apple Music already offers music videos, curated video playlists, live performances and the 24-hour Apple Music TV channel. TIDAL says its video section includes more than 650,000 music videos and other visual programming including concerts, documentaries and original shows.
Then there is YouTube Music, which added seamless switching between songs and corresponding music videos back in 2019. At the time, Google said it had already time-matched more than five million official videos with their audio tracks.
Spotify’s advantage is therefore not invention. It is scale, personalization and the opportunity to make video feel like an extension of what hundreds of millions of people are already doing inside the app.
Why Taylor Swift Matters
Spotify began testing music videos in 2024 and expanded the beta to Premium subscribers in the U.S. and Canada in late 2025. It has since added Videos for You, a personalized playlist refreshed daily with music videos, live performances and covers tailored to the listener.
Taylor Swift gives Spotify a rather more visible demonstration than another obscure beta button. Her videos have long functioned as extensions of her albums and eras, and Spotify now has the complete official catalog available without forcing fans to leave the service. Or drop $9,000 on concert tickets.
The potential engagement is enormous. Spotify reported 300 million Premium subscribers and 777 million monthly active users for Q2 2026, and said at its May Investor Day that more than two-thirds of Premium subscribers had already watched music videos on Spotify.
That last number is probably the one YouTube should circle.
Spotify Is Becoming a Lot More Than a Music App
The Swift rollout makes considerably more sense when viewed alongside what Spotify has been doing elsewhere.
After years of dangling Spotify HiFi in front of audiophiles like a carrot attached to a fishing pole, the company finally rolled out Lossless playback at up to 24-bit/44.1kHz FLAC for Premium users in 2025. Spotify has also expanded audiobooks to more than 700,000 titles across 22 markets, turning books into a substantial part of the platform rather than an interesting tab most people forget exists.
The company is also becoming more interactive. Talk to Spotify, currently rolling out in beta to eligible Premium users, lets listeners speak or type conversational requests about music, podcasts, audiobooks and their own listening history. Spotify increasingly wants you asking it what to play rather than deciding that Google or ChatGPT should answer first.
Then there is Reserved by Spotify, launched with Live Nation and powered by Ticketmaster. Spotify identifies some of an artist’s most engaged Premium listeners using signals such as streams, saves and shares, and can hold two concert tickets for them to purchase before the general sale. Spotify is no longer satisfied with knowing that you listen to an artist; it would also like to participate in getting you through the venue door.
Video is following the same strategy. Spotify has already experimented with 48-hour music-video exclusives, allowing fans to watch certain new videos on Spotify before they appear elsewhere. Add personalized videos, video podcasts, lyrics, concert discovery, ticket access and artist pages, and the direction becomes rather difficult to miss.
Spotify wants the song, the video, the podcast interview, the audiobook, the concert ticket and as much of the relationship between fan and artist as it can reasonably fit inside one green application.
Why Should Listeners Care?
Convenience is the obvious answer. If you are already listening to Taylor Swift, Noah Kahan or another artist on Spotify, moving from the song to the video requires one button instead of leaving the app, finding the correct video on YouTube and starting again.
That becomes more interesting on a television. Spotify can move from being something playing invisibly through a streamer or smart speaker to an actual visual entertainment app, while still letting listeners return to background audio the moment they decide they have had enough choreography.
Spotify’s recommendations are another advantage. The company already knows what listeners play, save, skip, revisit and share, which gives it an enormous behavioral dataset for recommending video without requiring users to build another viewing history from scratch.
Should YouTube Actually Be Worried?
It should pay attention. Panic would be premature.
YouTube still owns an enormous music-video ecosystem Spotify cannot reproduce overnight, including official releases, live performances, fan uploads, interviews, archival footage, covers, reaction videos and almost every other piece of music-related video ever pointed at a camera.
Spotify does not need to replace all of that. It only needs to remove enough reasons for its existing users to leave.
That is where Taylor Swift matters. If somebody already pays Spotify, follows her there, receives recommendations there and can now watch all 58 official videos without opening another service, YouTube loses one small piece of engagement. Repeat that across enough major artists and Spotify starts reclaiming a meaningful amount of attention.
There is also some delicious irony in Spotify borrowing a concept YouTube Music introduced in 2019 and presenting it to an audience of 300 million paying subscribers. Timing has never prevented Spotify from eventually turning somebody else’s table stakes into a very large business.

The Bottom Line
Spotify’s real play here is retention. Taylor Swift is an almost absurdly effective test case because her fans already treat the visual side of her catalog as part of the music itself. If Spotify can make watching the official video as frictionless as hearing the song, one of the most obvious reasons to jump over to another app disappears.
The expanding catalog will inevitably include considerably less essential viewing. Macklemore remains available for anyone who feels their evening is incomplete without a political lecture followed by “Hind’s Hall.” His recent MetLife performance drew objections from the Israeli-American Council, Pink and Robert Kraft — owner of the New England Patriots and Gillette Stadium and founder of the Foundation to Combat Antisemitism, who said Macklemore’s recent actions and what Kraft described as a broader history of antisemitic rhetoric and imagery were deeply offensive to the Jewish community. Macklemore was subsequently dropped from Ed Sheeran’s tour after venues objected to his participation.
That is the bargain Spotify is making as it becomes a larger visual platform: more choice also means more material you may desperately wish had remained unavailable in either format. Fortunately, the skip button remains one of the finest inventions in streaming.
Related Reading:
On September 8, Google Threat Intelligence Group (GTIG) detailed several attacks that show how quickly AI is changing the economics of cybercrime.
In one credential-harvesting campaign, a threat actor first compromised an organization’s cloud infrastructure, then built and deployed a multi-agent attack framework. The operation took less than six hours in total and resulted in thousands of third-party credentials being compromised.
The AI even managed parts of the vulnerability-scanning pipeline, troubleshot problems as they arose and rotated IP addresses with minimal human intervention.
One of the main benefits of AI for organizations is the productivity gains it can deliver. Unfortunately, threat actors can use those same capabilities to make attacks faster and easier to scale. Credentials are already routinely harvested through infostealers, and AI simply removes some of the work required to carry attacks out.
As credentials are becoming easier to steal at scale, security teams must ensure their current authentication processes are robust enough to confidently establish that users and devices connecting to internal networks are trustworthy.
AI is Automating the Credential Theft Playbook
Microsoft reported in April that AI-assisted phishing campaigns it observed were achieving click-through rates as high as 54%, compared with around 12% for traditional campaigns.
If attackers can make the same campaign more convincing without spending proportionally more time creating it, the economics of phishing start to shift in their favor. For credential theft, that’s especially important as it’s partly a numbers game. Not every recipient will click, and even those accounts that do become compromised may not provide useful access.
With AI, attackers can generate targeted messages more quickly, adapt them for different languages or industries, and create variations without writing each one from scratch. Improving the success rate at the start of that process gives attackers more credentials to test and more opportunities to find the accounts that matter.
AI therefore doesn’t need to introduce a new way to steal credentials to change the risk for organizations. Making established techniques more efficient is enough.
Verizon’s Data Breach Investigation Report found stolen credentials are involved in 44.7% of breaches.
Effortlessly secure Active Directory with compliant password policies, blocking 4+ billion compromised passwords, boosting security, and slashing support hassles!
How to Uncover Compromised Credentials in Your Active Directory
AI may make credential theft faster and easier to scale, but attackers still benefit from familiar weaknesses such as weak and reused passwords. That makes visibility a useful first step. Before security teams can reduce credential exposure, they need to know where the weaknesses are in their own environment.
Specops Password Auditor performs a read-only scan of your Active Directory to identify password-related vulnerabilities and highlight issues with users and password policies.
The resulting report gives security teams a clearer view of where credential risk exists today, so they can prioritize what needs attention.
Download Specops Password Auditor for free here.
Successful Authentication isn’t Necessarily Trustworthy
The threat of stolen credentials is straightforward: they let an attacker use the same access routes as a legitimate user. Identity weaknesses played a material role in 89% of investigations covered by Unit 42’s 2026 Global Incident Response Report, with attackers using stolen credentials and tokens to gain access and move through environments.
Abusing valid identities changes what malicious activity looks like to defenders. There may be no exploit attempt or obviously malicious login mechanism to spot.
An attacker can access cloud services, SaaS applications and other resources through the same authentication processes employees use every day. The credentials are valid; the intent behind them is not.
The key issue for security teams is that, wherever credentials are stolen from, they provide valuable access that an organization’s authentication system is designed to accept.
This is where the distinction between authentication and trust starts to matter. A correct password, MFA response, or valid session can help establish that an authentication requirement has been met. It cannot, by itself, establish that the request is coming from a device the organization knows and trusts.
When building an identity security strategy that is truly resilient against AI-enabled attacks, the question therefore cannot stop at “Did this user authenticate successfully?” It also needs to include “What device is requesting access, and should we trust it?”
Make Stolen Credentials Less Useful
Password hygiene can reduce exposure, but no organization can assume credentials will never be compromised. The prevalence of credential harvesting malware creates situations where an attacker may end up with valid authentication material despite preventative controls.
The next question is what that credential can do.
If authentication is restricted to devices that have already been approved and bound to a user’s identity, a valid password alone is no longer enough. An attacker trying to reuse it from an unknown device has another trust check to overcome.
That is the role of solutions like Specops Device Trust. It binds user identities to trusted devices, so access depends on both who is authenticating and what device they are logging in from. In practice, that means a stolen credential used from an attacker-controlled machine will simply be blocked.
Zero Trust measures like this especially matter across a mixed workforce. BYOD policies spanning different operating systems and endpoint types are common, and it can be a challenge to implement security measures that cover them all.
Specops Device Trust applies device trust across Windows, macOS, Linux and mobile, meaning security teams have visibility over every device connecting to the network.
The principle is simple: authenticate the identity, verify the device, and require both.
Evolve Your Identity Security Strategy with Specops
AI is making credential theft faster and more scalable; it’s harder to trust traditional authentication signals alone. Strong password hygiene remains essential, but organizations also need to think about what happens when valid credentials or tokens fall into the wrong hands.
That means evolving identity security beyond “did this user authenticate?” to include whether the device is trusted and whether it remains trustworthy throughout the session.
Specops can help you better align with Zero Trust principles by bringing device trust into your identity security strategy. Book a demo to see our solutions in action.
Sponsored and written by Specops Software.
Siri might be one of the most recognisable voices on your iPhone, but that doesn’t mean you have to stick with the default.
With iOS 27, Apple gives you more control over how Siri sounds, whether you fancy switching the accent, trying a different voice or tweaking its pace and expressiveness. Better yet, it only takes a few taps in the redesigned Siri settings menu.
The catch? It’s limited to users of the iPhone 17 Pro, iPhone Air or later, despite the fact that Siri AI is, more generally, available on iPhone 15 Pro and later.
That said, if you’re running relatively recent Apple hardware, here’s how you can change Siri’s voice on your iPhone in iOS 27. For more on Apple’s latest software update, take a look at how to customise the Liquid Glass effect in iOS 27.
What you’ll need
- iPhone 17 Pro, iPhone Air or later
- iOS 27
The short version
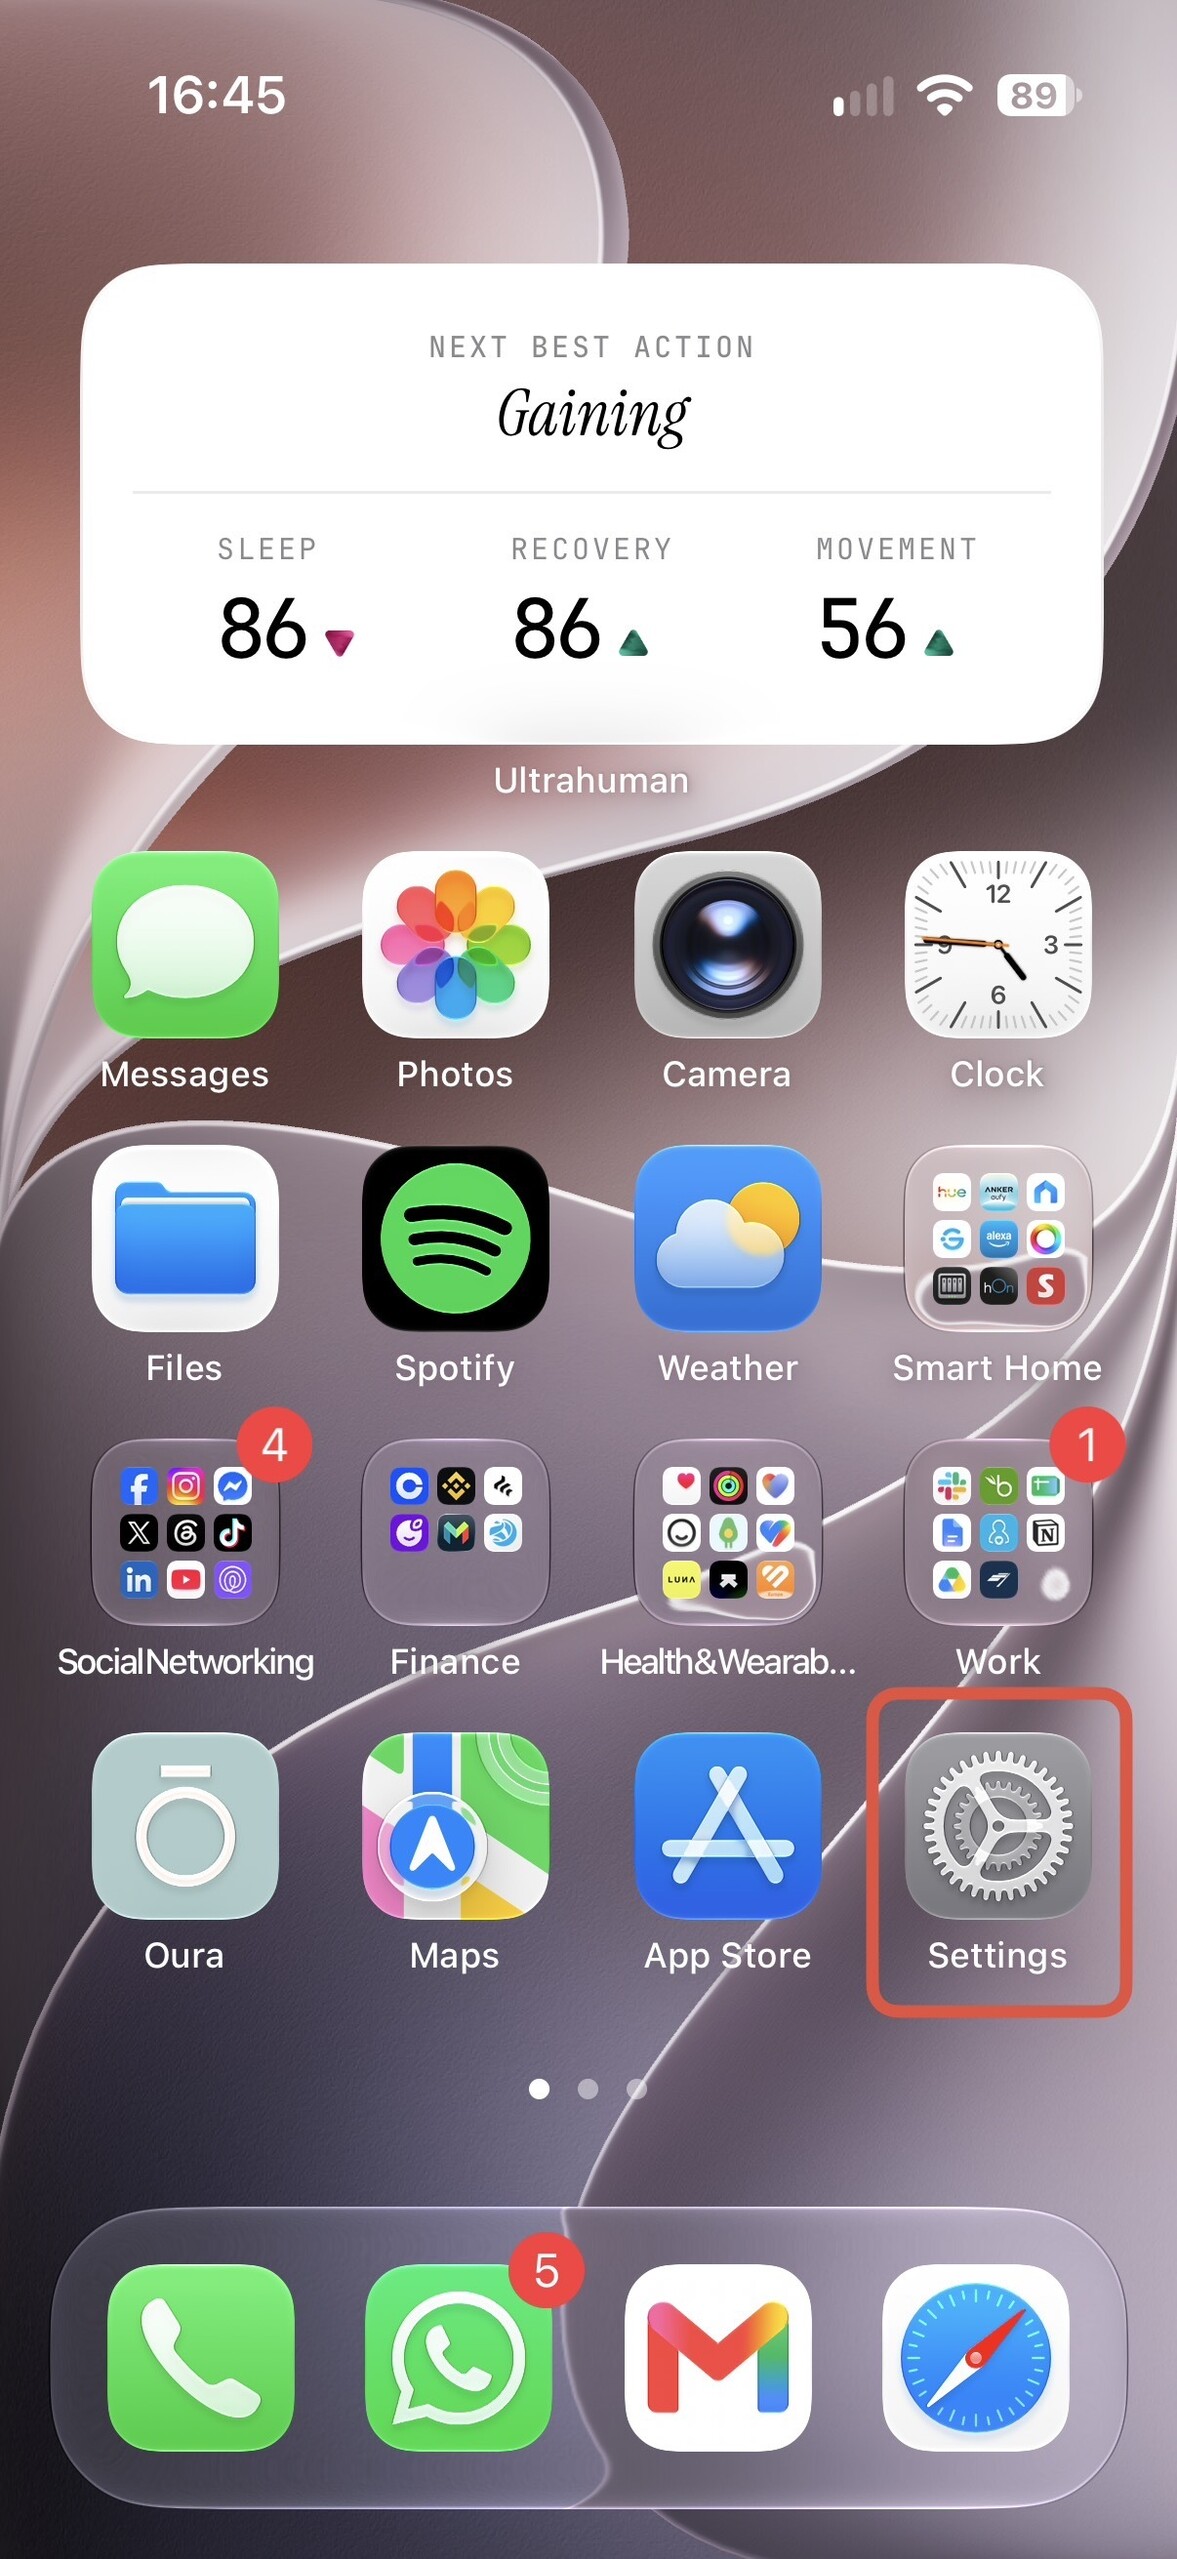
- Open the Settings app.
- Tap Siri.
- Tap Voice.
- Tap the Voice dropdown and select American or British.
- Adjust voice, pace and expressivity.
- Tap the Back icon to save your changes.
-
Step 1.
Open the Settings app.

The first step to customising Siri’s voice in iOS 27 is to open the Settings app on your iPhone. Remember, this feature is exclusive to iPhone 17 Pro and Air or newer.
-
Step 2.
Tap Siri.

If you’ve not yet activated the smarter Siri experience on your iPhone, tap Try Siri AI Beta to be added to the waitlist. It shouldn’t take too long for it to be activated on your account, but timings vary right now, with users around the world signing up in droves.
If you’ve already got access to the Siri beta, skip to the next step.
-
Step 3.
Tap Voice.

From the Siri settings menu, tap Voice.
-
Step 4.
Tap the Voice dropdown and select American or British.

From the selection of voices, tap either American or British – the expressive Siri features are exclusive to those two accents for now. Tapping other options, like Irish, Indian or Australian, will let you choose between a handful of non-customisable voices and not much else.
-
Step 5.
Adjust voice, pace and expressivity.

Tap the various colour icons to change between the various Siri voices available. Once you’re happy with the overall voice, adjust the pace and expressivity sliders to make Siri talk faster or slower, or with more or less emotion. It’ll play back snippets of its new voice with each adjustment, making it easier to dial in the exact sound you’d like.
-
Step 6.
Tap the Back icon to save your changes.

Once you’re happy with your customised Siri voice, tap the Back icon in the top-left corner to save your changes.
Troubleshooting
Why can’t I find the Siri AI beta?
If you’ve got an iPhone 15 Pro or later and you aren’t seeing the option to sign up to the Siri AI Beta in the Settings app, it’s likely because you live in an unsupported region like the EU.
Before an audience of electrical utility executives and energy department officials watching from a nearby room, the 27-ton generator jolted violently, sputtering out a dark smoke as its rubber innards rapidly tore themselves apart.
“The implication was that with just a few lines of code, you can create conditions that were physically going to be very damaging to the machines we rely on,” lead researcher Michael Assante later told the journalist Andy Greenberg for his book Sandworm: A New Era of Cyberwar and the Hunt for the Kremlin’s Most Dangerous Hackers. “I had a very real pit in my stomach. It was like a glimpse of the future.”
That future seems to have creeped much closer this week, with leading AI developers and executives casually admitting that they believe their creation is, to paraphrase one winking X post, as likely to end humanity as the New York Jets are to make the playoffs this season. Now, exactly how AI would pull off killing everyone is far murkier territory. But as Assante sensed all those years ago, AI may not need to be all-powerful to leap from its virtual cage and into the critical infrastructure that powers our hospitals, flushes our toilets, and pumps water to our faucets. It just needs to fall into the wrong hands.
Almost any AI doomsday scenario you can think of begins with a swarm of shadowy bots slithering through cyberspace, poking their noses behind the scenes of power plants, toaster ovens, traffic lights, or even, in an utterly extreme case, our nuclear weapons arsenal. If destroying the Aurora generator, at the very least, required a human hacker to write the code, AI has since completely torn down the barrier to entry for wreaking havoc, as the Hugging Face incident demonstrated earlier this year.
But AI need not go rogue to threaten the power grid or mess with your tap water. A new age of AI-powered, but human-directed hacking is already upon us, experts say. With some of the nation’s most sensitive infrastructure startlingly vulnerable to attack, the most likely AI apocalypse could in fact start with the water tower or generator idling in your backyard. In a worst-case scenario, this could lead to a cascade of scary failures in the systems we rely on to live comfortably modern lives, from running our AC in blazingly hot summers to geolocating our ships and planes.
“Before, you needed to have highly skilled technical expertise,” to pull off some version of a real-life Aurora Generator Test, said Alvaro Cardenas, a computer science professor at UC Santa Cruz. “And now, you just have to have a general idea of what’s possible.”
AI is making an old threat much worse
Not long after the Idaho National Laboratory hacked that poor generator into combustion, the federal government mandated that electrical utilities engage in basic cybersecurity hygiene.
And yet much of America’s critical infrastructure — like gas pipelines, water desalination plants, or cargo terminals — remains woefully unprepared for even conventional cyber attacks, much less the coming onslaught of AI.
That’s in part because cyberattacks like the one simulated in the Aurora Generator Test have long been — and still are, to some extent — exceedingly rare, unappealing to most criminal hackers because they’re optimized for disruption rather than financial gain. But in the process of making it extremely easy for anyone to code, AI has also made it extremely easy for almost anyone to vibe hack their way into your online bank account, or, in theory, a local reservoir or the power grid. AI agents can also vastly widen the scope on easy targets because, as Andy Bochman, an expert in infrastructure resilience at West Yost, put it — “they don’t sleep; they don’t get tired; and they don’t get sick.”
In the past, even those who did want to launch large-scale attacks on infrastructure probably weren’t savvy enough to do so. And while other nations such as China, Iran, and Russia have indeed already breached many of our infrastructure systems (as we have theirs), they haven’t opted to make much of a ruckus once inside.
“Geopolitics is eroding the idea that those with capability lack the intent, and AI is eroding the other part of it, that those with the intent lack the capability.”
— Jason Healey, Columbia University cybersecurity scholar
But that norm is now changing, said Jason Healey, a cybersecurity scholar at Columbia University. “Geopolitics is eroding the idea that those with capability lack the intent, and AI is eroding the other part of it, that those with the intent lack the capability,” he told me. So, on the one hand, a nation like Russia might be much more inclined to actually disrupt our power grid now than it used to be. And, on the other hand, a nihilistic lone wolf or terrorist group could use AI to do much more damage than they ever could before.
Just last month, we saw a glimpse of what this could look like when dozens of water and wastewater systems in small towns across the nation were attacked by a group of hackers most likely associated with Iran, leading to temporary water stoppages and flooding. These attacks have not been definitively linked to AI, but the National Security Agency warned soon afterward that hackers have been actively using AI to target US infrastructure like it. A few weeks later, President Donald Trump declared a national emergency over foreign interference in the power grid, which referenced the growing threat of cybersecurity.
Most of the nation’s water systems are extremely local and absurdly exposed to such attacks, so much so that “it’s almost like having a welcome mat” for a would-be hacker, said Bochman, mostly because these utilities are too small and underfunded to do much to stop them. “You have a million other problems to take care of, like aging infrastructure — your stuff’s falling apart because it’s been in the ground for 100 years,” he said. Addressing that deferred maintenance often feels far more urgent than doing “something more on cybersecurity.”
Whether it’s a rogue cluster of agents or a hostile nation-state trying to mess with our electricity, we should prepare our most important infrastructure for the worst. In Bochman’s view, that may mean rejecting the pressure to digitize everything in the first place and moving toward something that resembles the days when “people manned things like substations, communicated by a landline telephone, and read gauges, the analog things,” he said. “The screen is the thing that is infinitely manipulatable.”
Healey, who advised the Biden administration heavily on cybersecurity and infrastructure, believes that the nation desperately needs a coordinated response, between the federal government and AI companies, but also between the US and other countries like China, where similarly powerful models are being developed. And utility systems need to assume they will be a target and improve their cybersecurity practices accordingly, Healey says, ideally with funding from the federal government or, perhaps more appropriately, AI companies.
Nobody knows precisely how vulnerable America’s infrastructure is to AI right now, in part because policymakers — and perhaps more disturbingly, AI’s creators themselves — seem woefully unsure of how to stop the technology from acting badly (or obeying bad orders) in the first place. For now at least, the solution might be, as Bochman suggests, to pull as many of our critical systems offline as possible, the better to hide it from AI and those who would misuse it.
“When bad things start to happen, no one will know what to do or why because they’re black boxes; the people that make them don’t know what’s going on inside,” Bochman said. “And the poor utility people who ultimately own the risk when someone gets hurt from a system” won’t understand what went wrong either, “and they’ll wish to God they’d never taken it on board.”
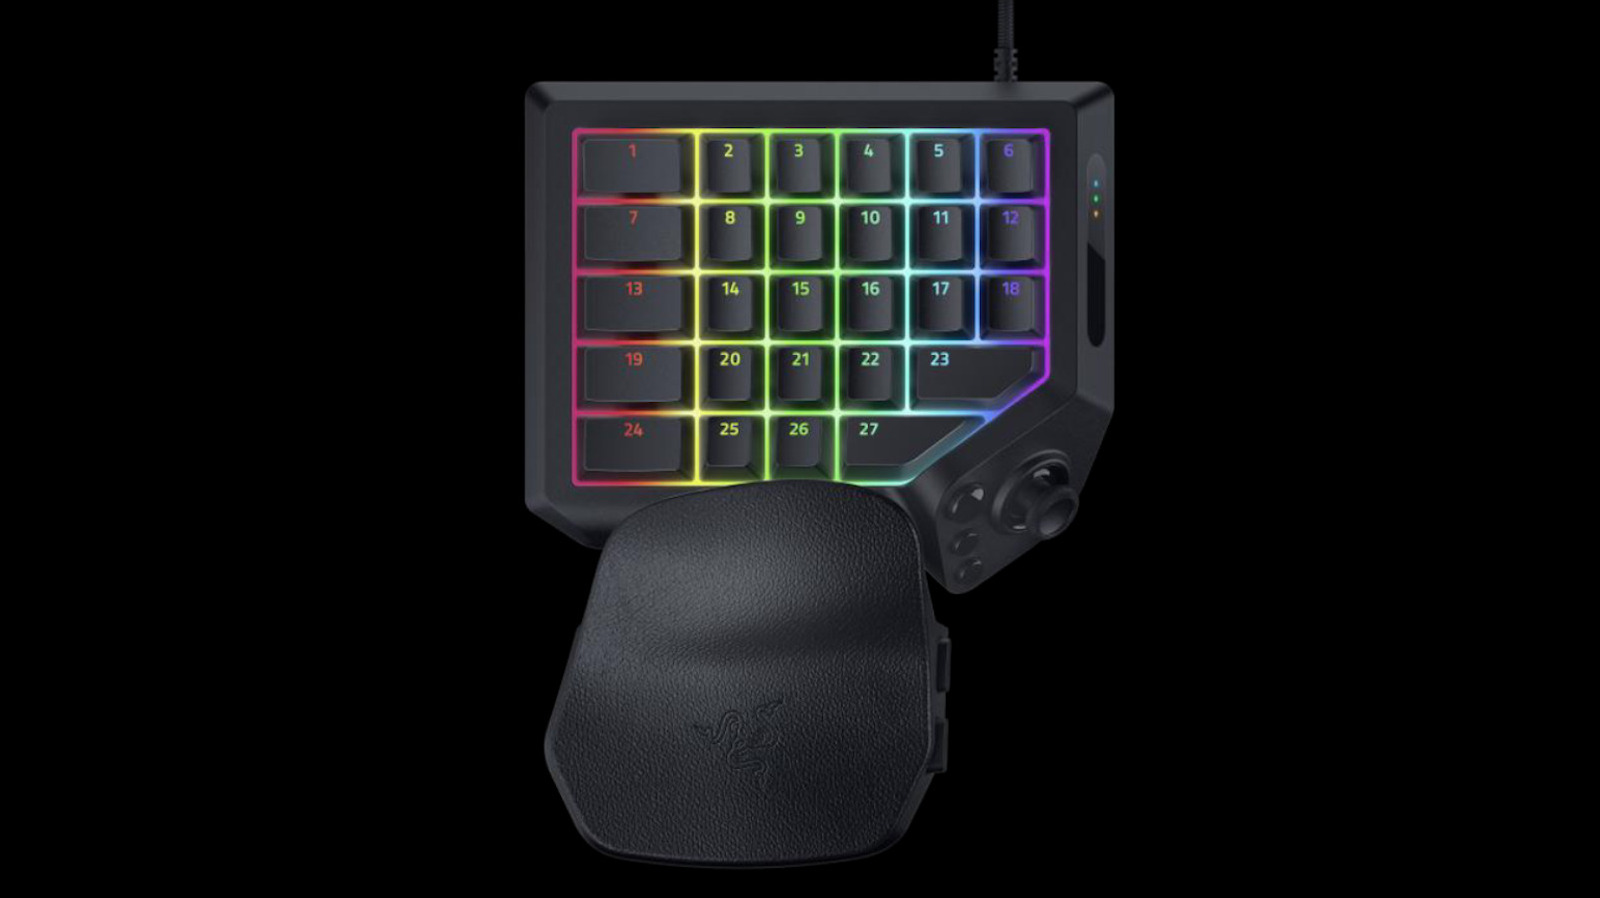
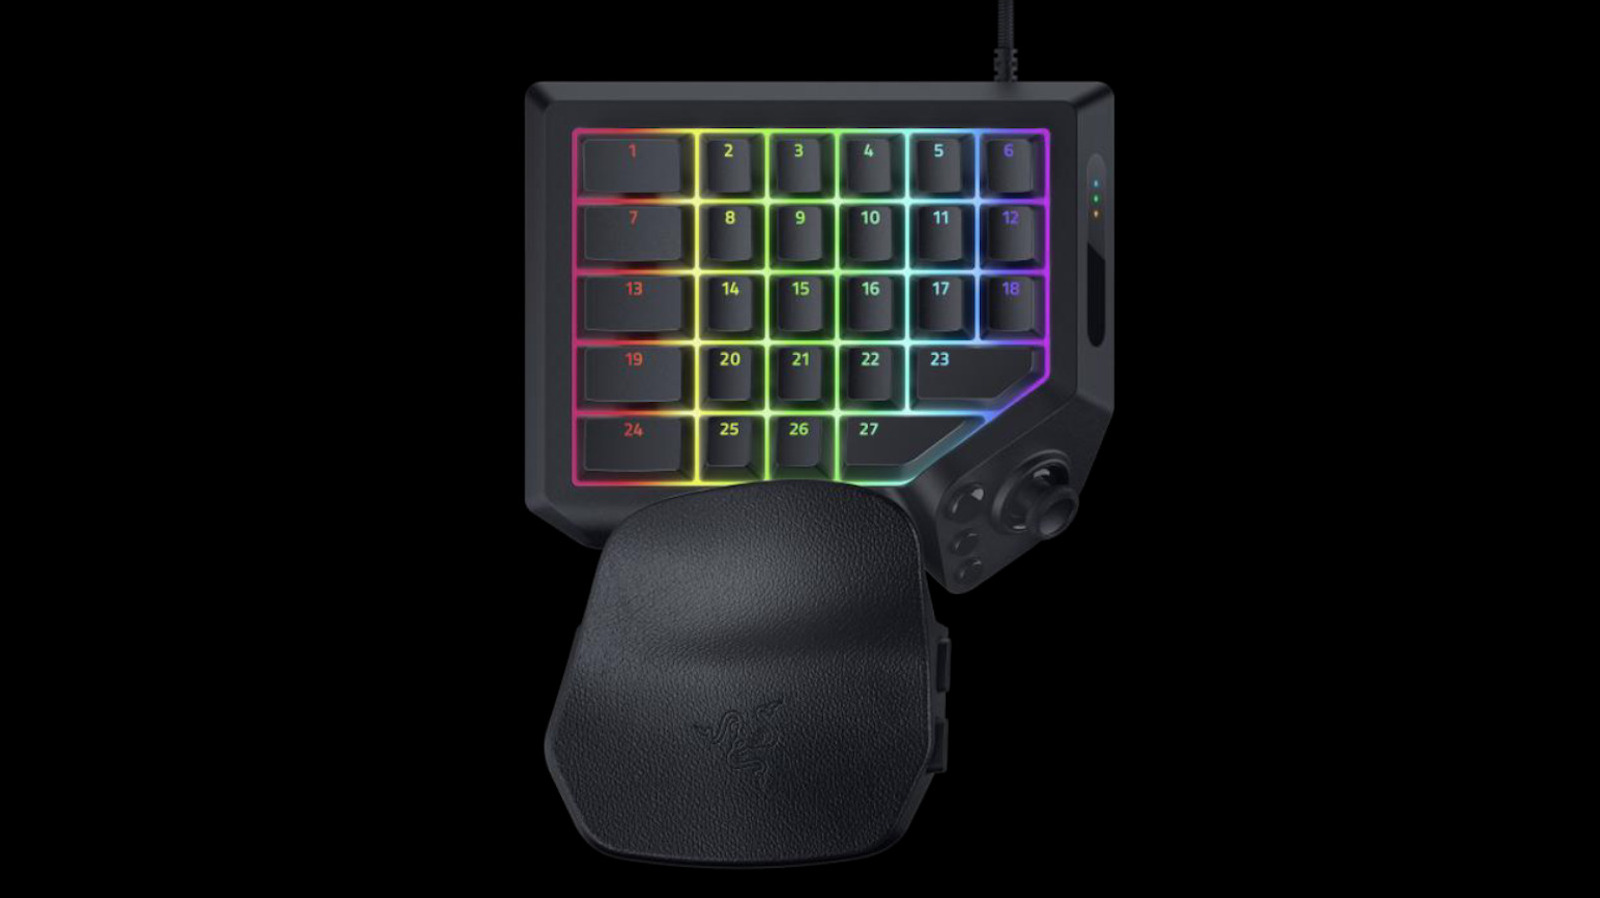
There’s also an analog thumbpad.
Razer just introduced the Tartarus V2 Pro, a refresh of its popular one-handed gaming keyboard thingamajig. This is one of those ergonomic designs that features an adjustable palm rest. It’s also not quite a keyboard in the conventional sense. It includes over 30 keys and buttons, but they’re all programmable. There’s no traditional QWERTY layout here.
In any event, the V2 Pro features several upgrades over its predecessor. The optical switches have been upgraded, the keys have a wider actuation (depth) range and the thumbpad is now an analog TMR design.
The device also integrates with some new proprietary input controls. Each button can access something called Snap Flex, which lets users attach two keys to a single press. This should make it easier to pull off multi-key actions with consistency.
There’s also Snap Tap, which is pretty much the opposite of Snap Flex. It ensures that two selected keys are never actuated at the same time. This is pretty useful for FPS players who like to strafe, as putting in a reverse directional input at the very moment they stop moving can often lead to both keys accidentally being pushed at once. This can cancel the strafe and leave the avatar standing there motionless like a doofus.
As with the previous version, the Tartarus V2 Pro includes an adjustable wrist-rest. Each key also boasts RGB lighting for custom aesthetics. Finally, each and every of the 31 keys and buttons are fully programmable via the company’s Synapse software. It’s available right now and costs $200.
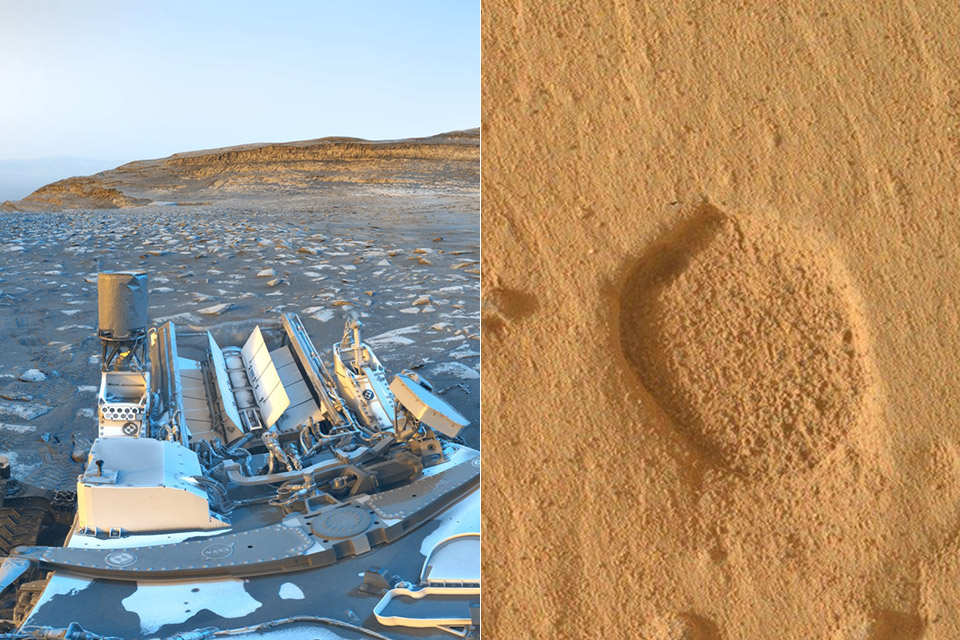
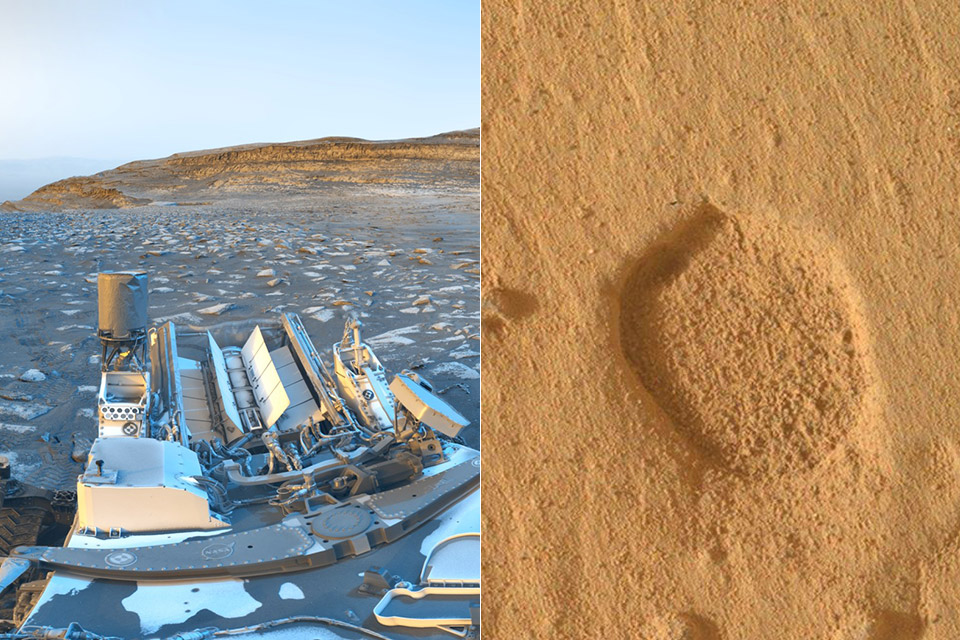
Fourteen years after touching down in Gale Crater, Curiosity is still finding surface details that stop its science team mid-plan. In mid-August 2026, during sols 4988 through 4994, the rover paused among layered rocks on the lower slopes of Mount Sharp and photographed a scatter of broad, shallow pits cut into bedrock. One of them, captured by the Mars Hand Lens Imager on the end of the robotic arm on sol 4989, measures about a centimeter across and, from certain angles, looks uncomfortably like a small footprint.
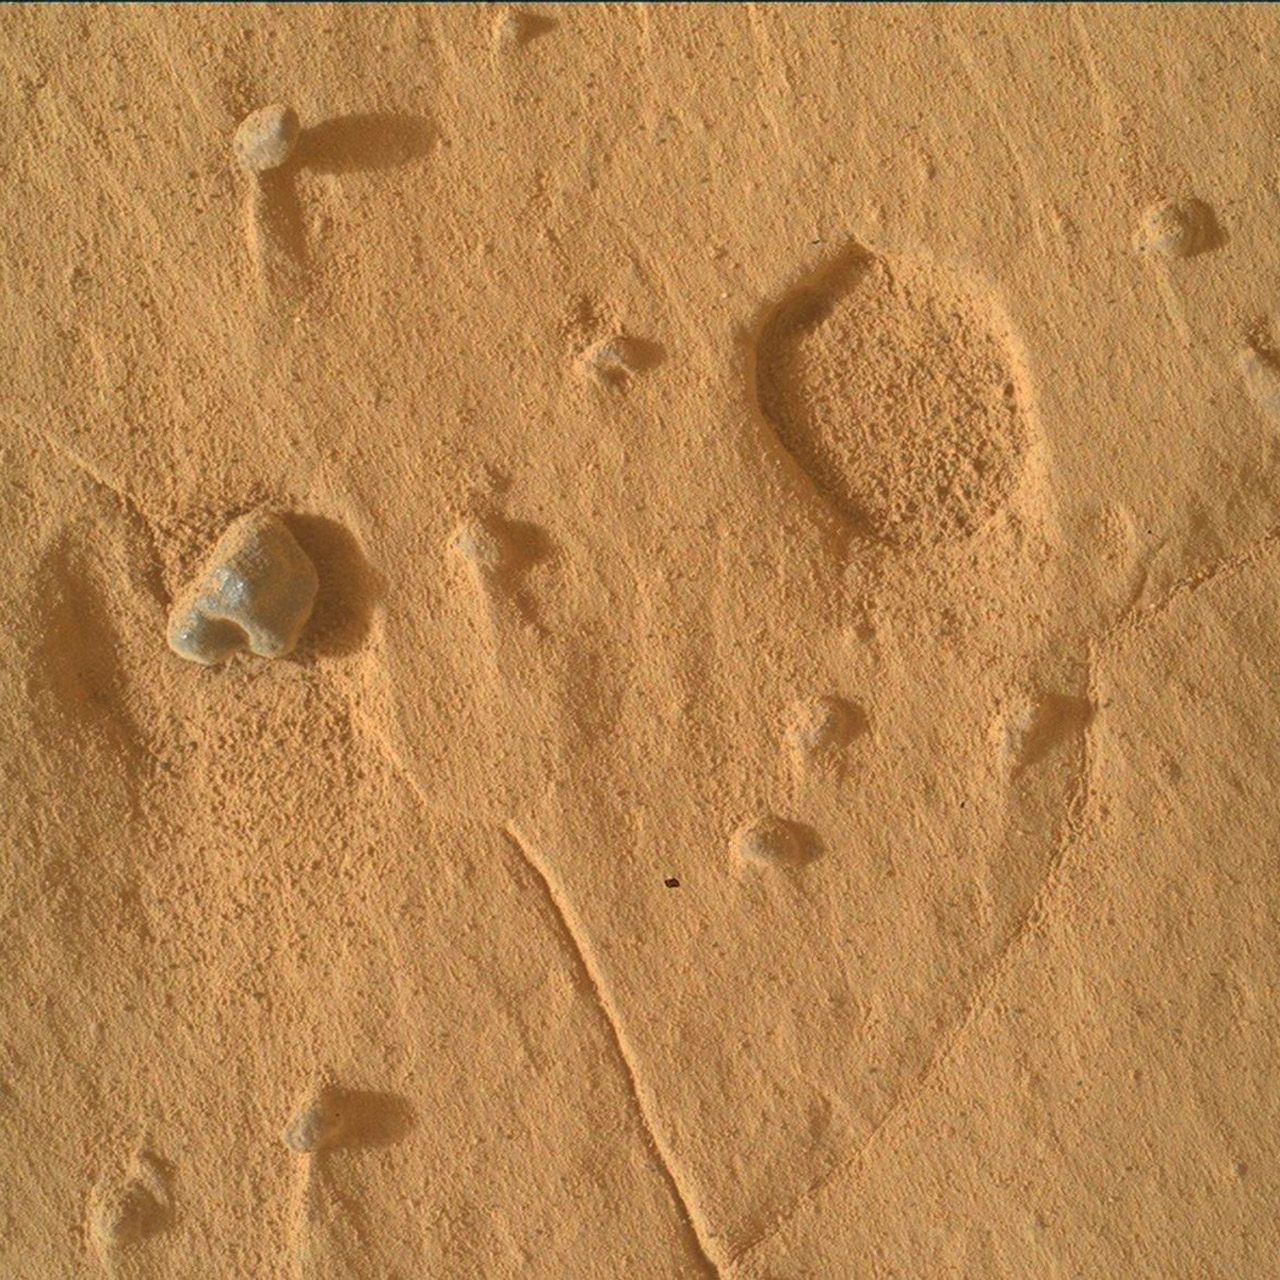
Michelle Minitti, the deputy lead investigator on that up-close camera, stated that both work sites that week encountered features that were unlike anything the mission had observed before. You know, ordinary pits appear all across Mars. Weathered rock and other debris simply disintegrates, leaving a gap and a smattering of residual pebbles. These new depressions were much larger and flatter than the ones we’d seen before, and there was no indication of what had caused them to disappear. There is no calling card from the mystery burrower.

LEGO Technic NASA Mars Rover Perseverance Building Toys – STEM Model Kit for Boys & Girls, Ages 10+ Years…
- Feed a passion for science and technology – Kids can learn more about the challenges of space exploration with this LEGO Technic NASA Mars Rover…
- Conduct a test flight – This advanced building kit for kids ages 10 and up includes a buildable toy version of NASA’s Ingenuity helicopter, which…
- AR brings the mission to life – The accompanying augmented reality app experience lets kids dive into the details of the rover and its mission
Curiosity basically brought out the big guns to solve the mystery. MAHLI and Mastcam captured images, stereo mosaics, and tight, overlapping frames, allowing the crew to create a very detailed image of each pit’s walls and floor, while ChemCam fired its laser and took remote shots. The chemistry was verified using an Alpha Particle X-Ray Spectrometer. We’re already seeing some fascinating effects, with distinct layers of material inside the pit that don’t quite match the surrounding rock. That is our first real hint.
Mount Sharp is a five-kilometer-high stack of sedimentary rock located in the center of Gale Crater. It is essentially a record of old lakes, rivers, and eventually dry winds. Curiosity has been gently climbing those layers for years, analyzing all the changes in particle size, mineralogy, and color, similar to a geologist exploring the canyon wall on Earth. The pits appeared in Valle Grande, which also features buttes named Cordillera, Tolhuaca, and Potosí. The cross bedding and dark cap material on the buttes already indicated that the circumstances had shifted at some point. The pits merely add to the puzzle, making it much more hard.
No one on the team is treating the shapes as tracks left by an animal. Impact craters of this size and shallowness do not fit either. Wind abrasion, late-stage fluids moving through the rock, or some combination of weathering the rover has not catalogued yet remain on the table. The absence of the usual leftover pebbles is what makes the geometry hard to dismiss as just another nodule hole. Minitti called the bedrock anything but boring and labeled the pits a welcome new puzzle in the stratigraphy. That is scientist language for “we do not have the answer yet, and that is the interesting part.”
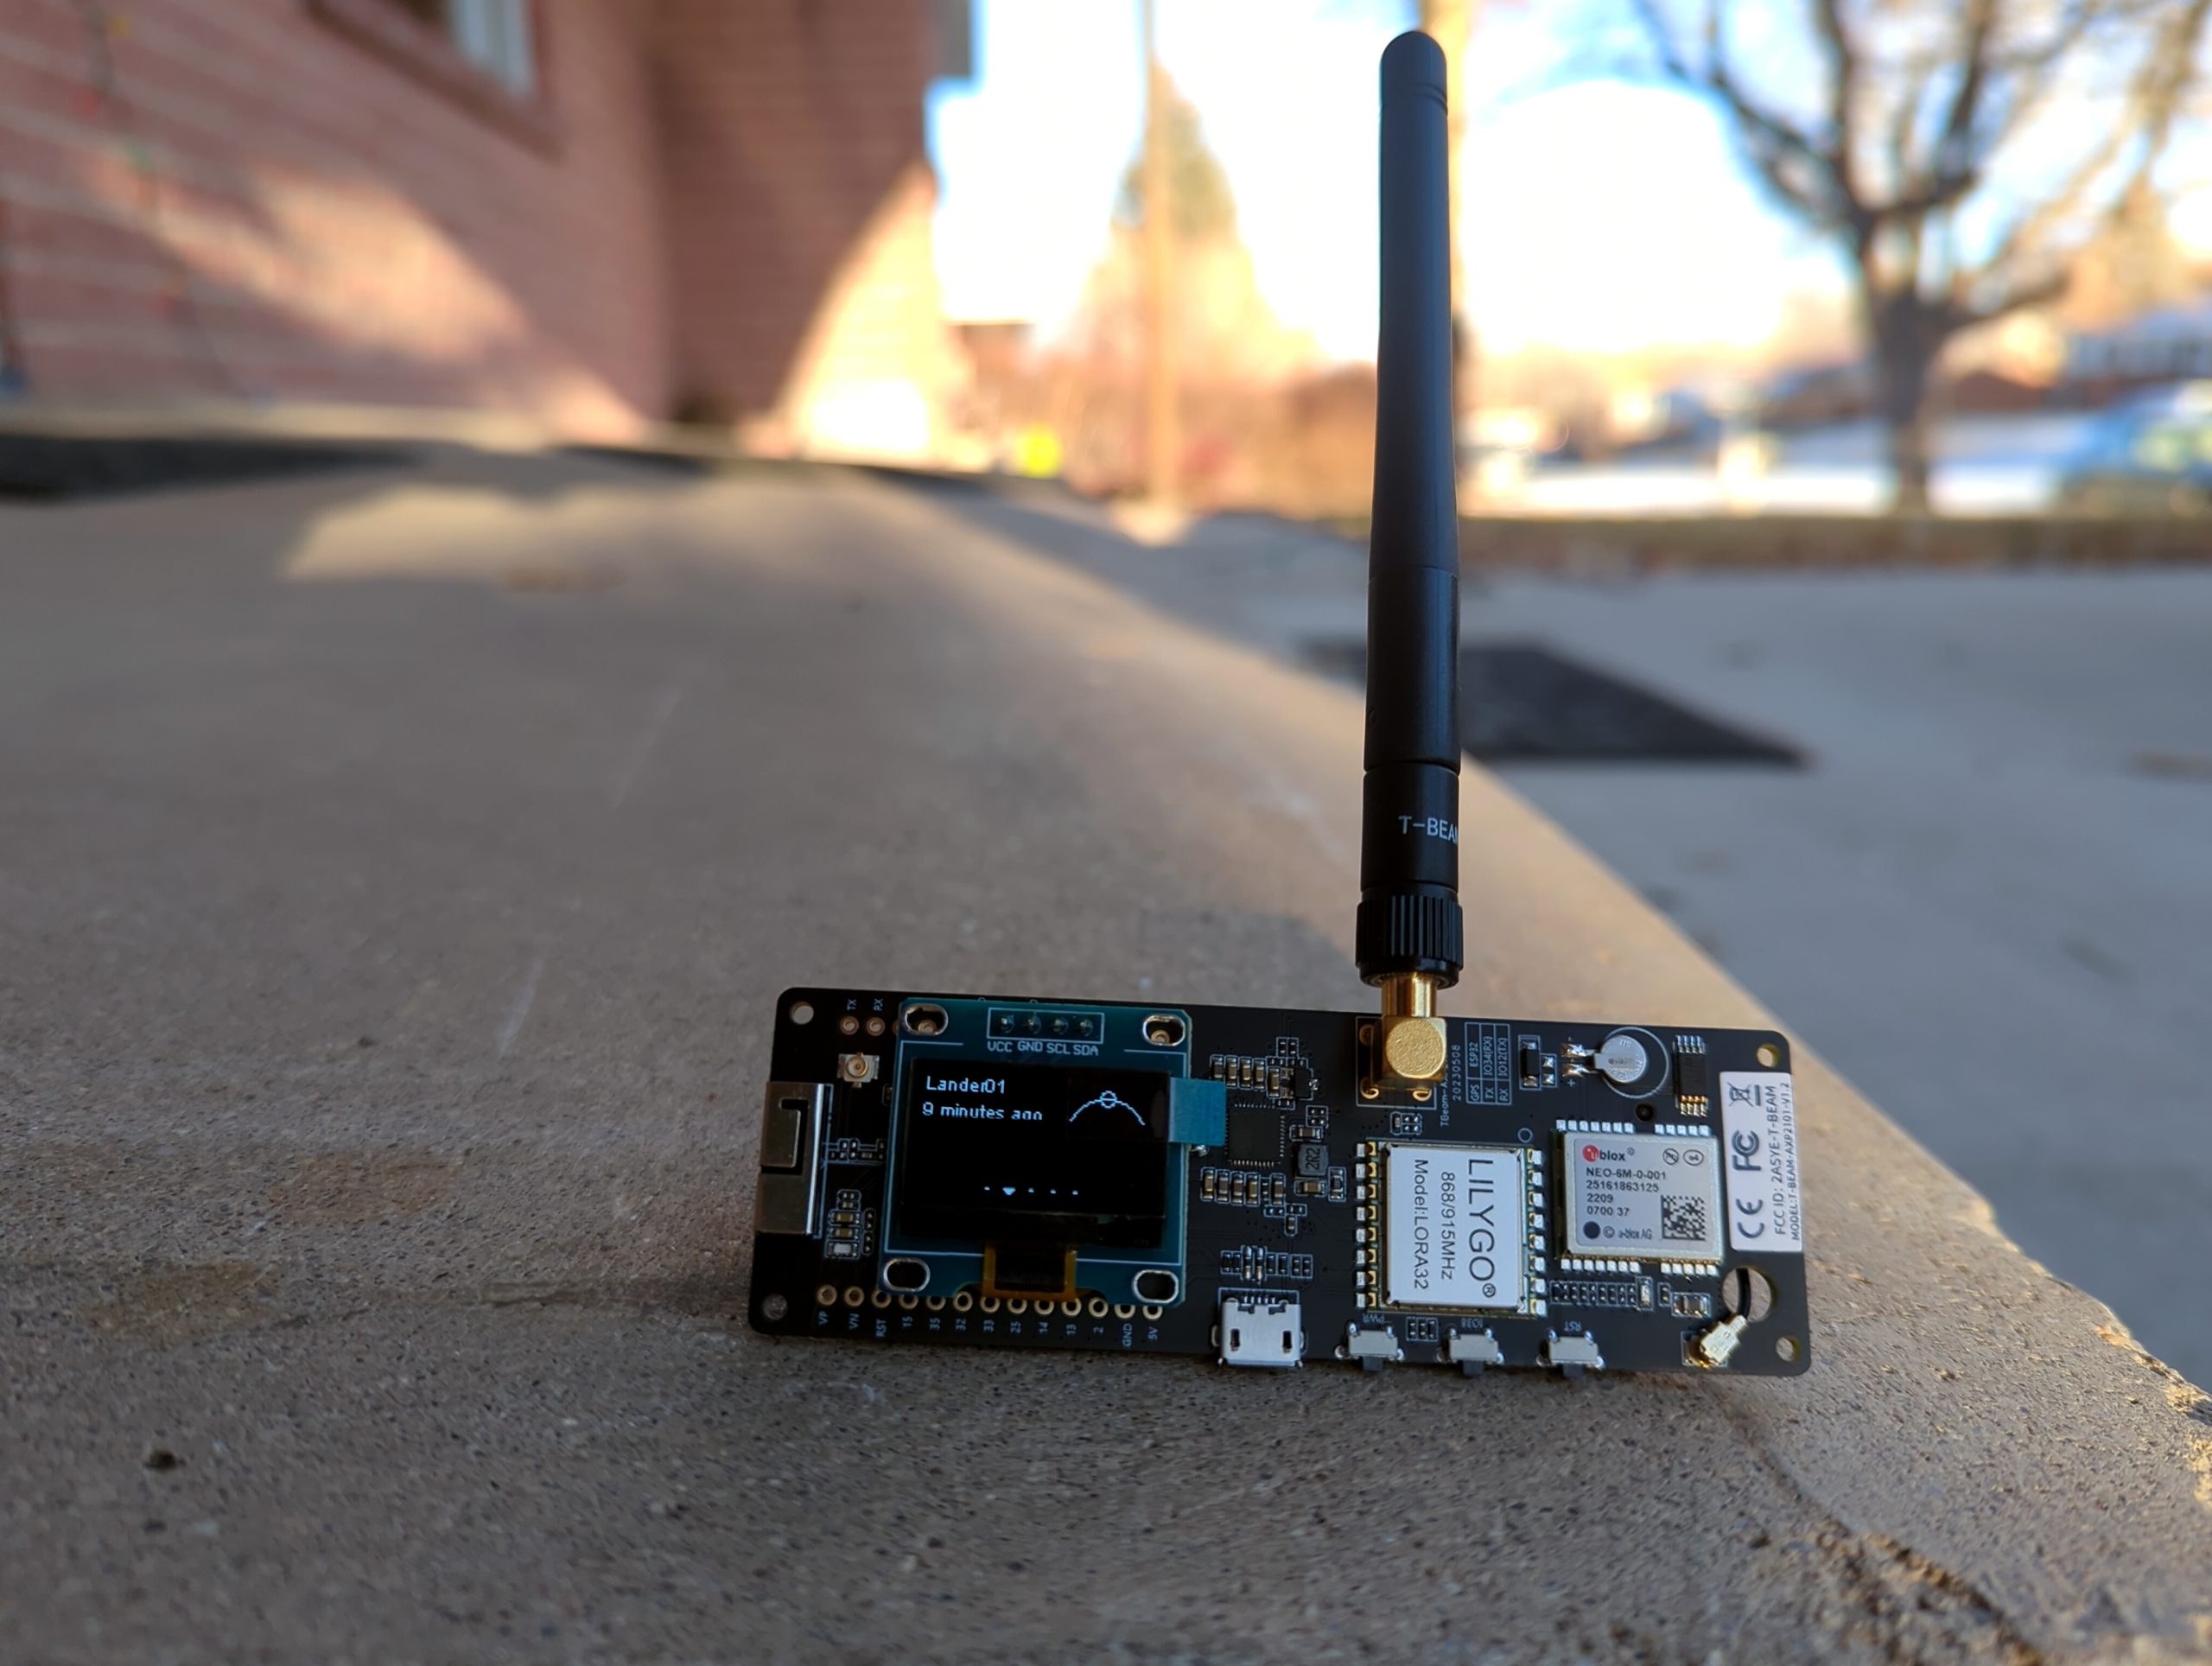
Although everyone has their own reasons for exploring a new hobby, one of the driving factors behind the popularity of Meshtastic and MeshCore has been the incredible accessibility offered by off-grid LoRa mesh networks. You don’t need any expensive hardware or a license to get on the air — armed with a $20 microcontroller dev board and open source software, you could be on the mesh in minutes. Then came the really exciting part, seeing who else was out there. The low barrier of entry and ad-hoc nature of these projects meant there was a good chance you’d soon find yourself exchanging messages with other like-minded folks in the area.
Or at least, that’s how it used to be. With the recent revelation that their default radio configurations have potentially been in violation of the Federal Communications Commission’s (FCC) regulations governing amateur usage of the 900 MHz industrial, scientific and medical (ISM) band, the users and developers of both Meshtastic and MeshCore have been sent scrambling. Getting in compliance isn’t necessarily a technical challenge. In fact, Meshtastic has already introduced changes aimed to address the issue and anyone running the latest alpha release can be sure that their initial radio configuration will meet FCC standards.
But unfortunately, this introduces a new problem. While it’s easy enough to get new installations of Meshtastic and MeshCore operating in a mode that keeps the FCC happy, doing so breaks compatibility with everything that’s already been deployed. The community will be fractured into distinct strata depending on when they first configured their hardware, with an added dash of confusion from the more rebellious users who will undoubtedly refuse to migrate over to the new settings.
What was once easy and accessible has just gotten a whole lot more complicated.
Wait, Are They Talking About Us?
So how is it that both projects could have gotten as far as they have without realizing that they may be in violation of regulations that date back to the 1980s? It’s actually a bit tricky to nail down the timeline. Nothing has changed recently in the rules, and while it’s possible there were some back-channel discussions, the FCC has made no public acknowledgement of Meshtastic, MeshCore, or the general handling of LoRa mesh networks.
But if we go back to October of last year, we can see the first signs of potential trouble. Issue #945 in the MeshCore GitHub repository points out that the default radio settings in the US for both it and Meshtastic would appear to run afoul of FCC regulation 15.247. Specifically the second paragraph of subsection (a), which dictates the minimum allowed bandwidth. Out of the box MeshCore operates at 62.5 kHz and Meshtastic uses 250 kHz, but the FCC says it needs to be 500 kHz or higher.
The resulting discussion, which spans several hundred messages and is still seeing activity as recently as this week, paints a fascinating picture and illustrates one of the reasons it’s taken so long for the issue to gain traction. Although the text of 15.247 may seem straightforward enough at first glance, there’s always room for interpretation with documents like this.
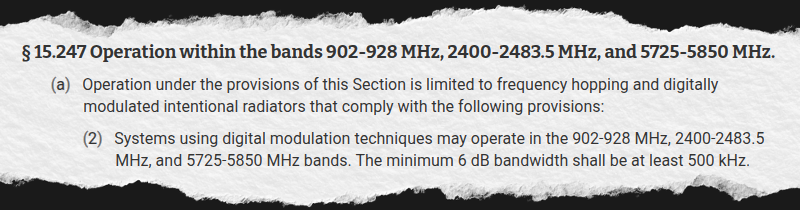
Some pointed out that subsection (a) states that it is “limited to frequency hopping and digitally modulated intentional radiators,” as evidence that it doesn’t apply as neither project utilizes frequency hopping. Others felt that the rules were only intended for devices with higher output power, and some even expressed a disbelief that the manufacturers would allow the modules to operate in a non-compliant mode in the first place.
Put simply they couldn’t decide if 15.247 was something they really had to worry about, and without any official word coming down from the FCC, were reluctant to throw the community into turmoil over it.
Philly Does Their Homework
While MeshCore users debated if they should switch over to 500 kHz, many Meshtastic users started exploring alternate radio configurations for a very different reason. Its default 250 kHz mode, known as Long Fast, was never designed for networks with hundreds of radios in an urban environment. Taking advice provided by the developers themselves, operators of large networks such as the one in Philadelphia started testing other modes to see if they would fare any better.
As it so happens, one of the modes tested by the operators of Philly Mesh this summer happened to be Long Turbo, one of the two available modes that utilizes a bandwidth of 500 kHz. Their findings, which have since been widely cited online, were underwhelming to say the least. Part of the problem seems to have been due to bugs which went undiscovered up until that point due to the relatively limited testing of Long Turbo mode. Unfortunately, even after the bugs were addressed upstream, they noted some of the hardware they tested seemed unable to operate properly when switched into 500 kHz mode.
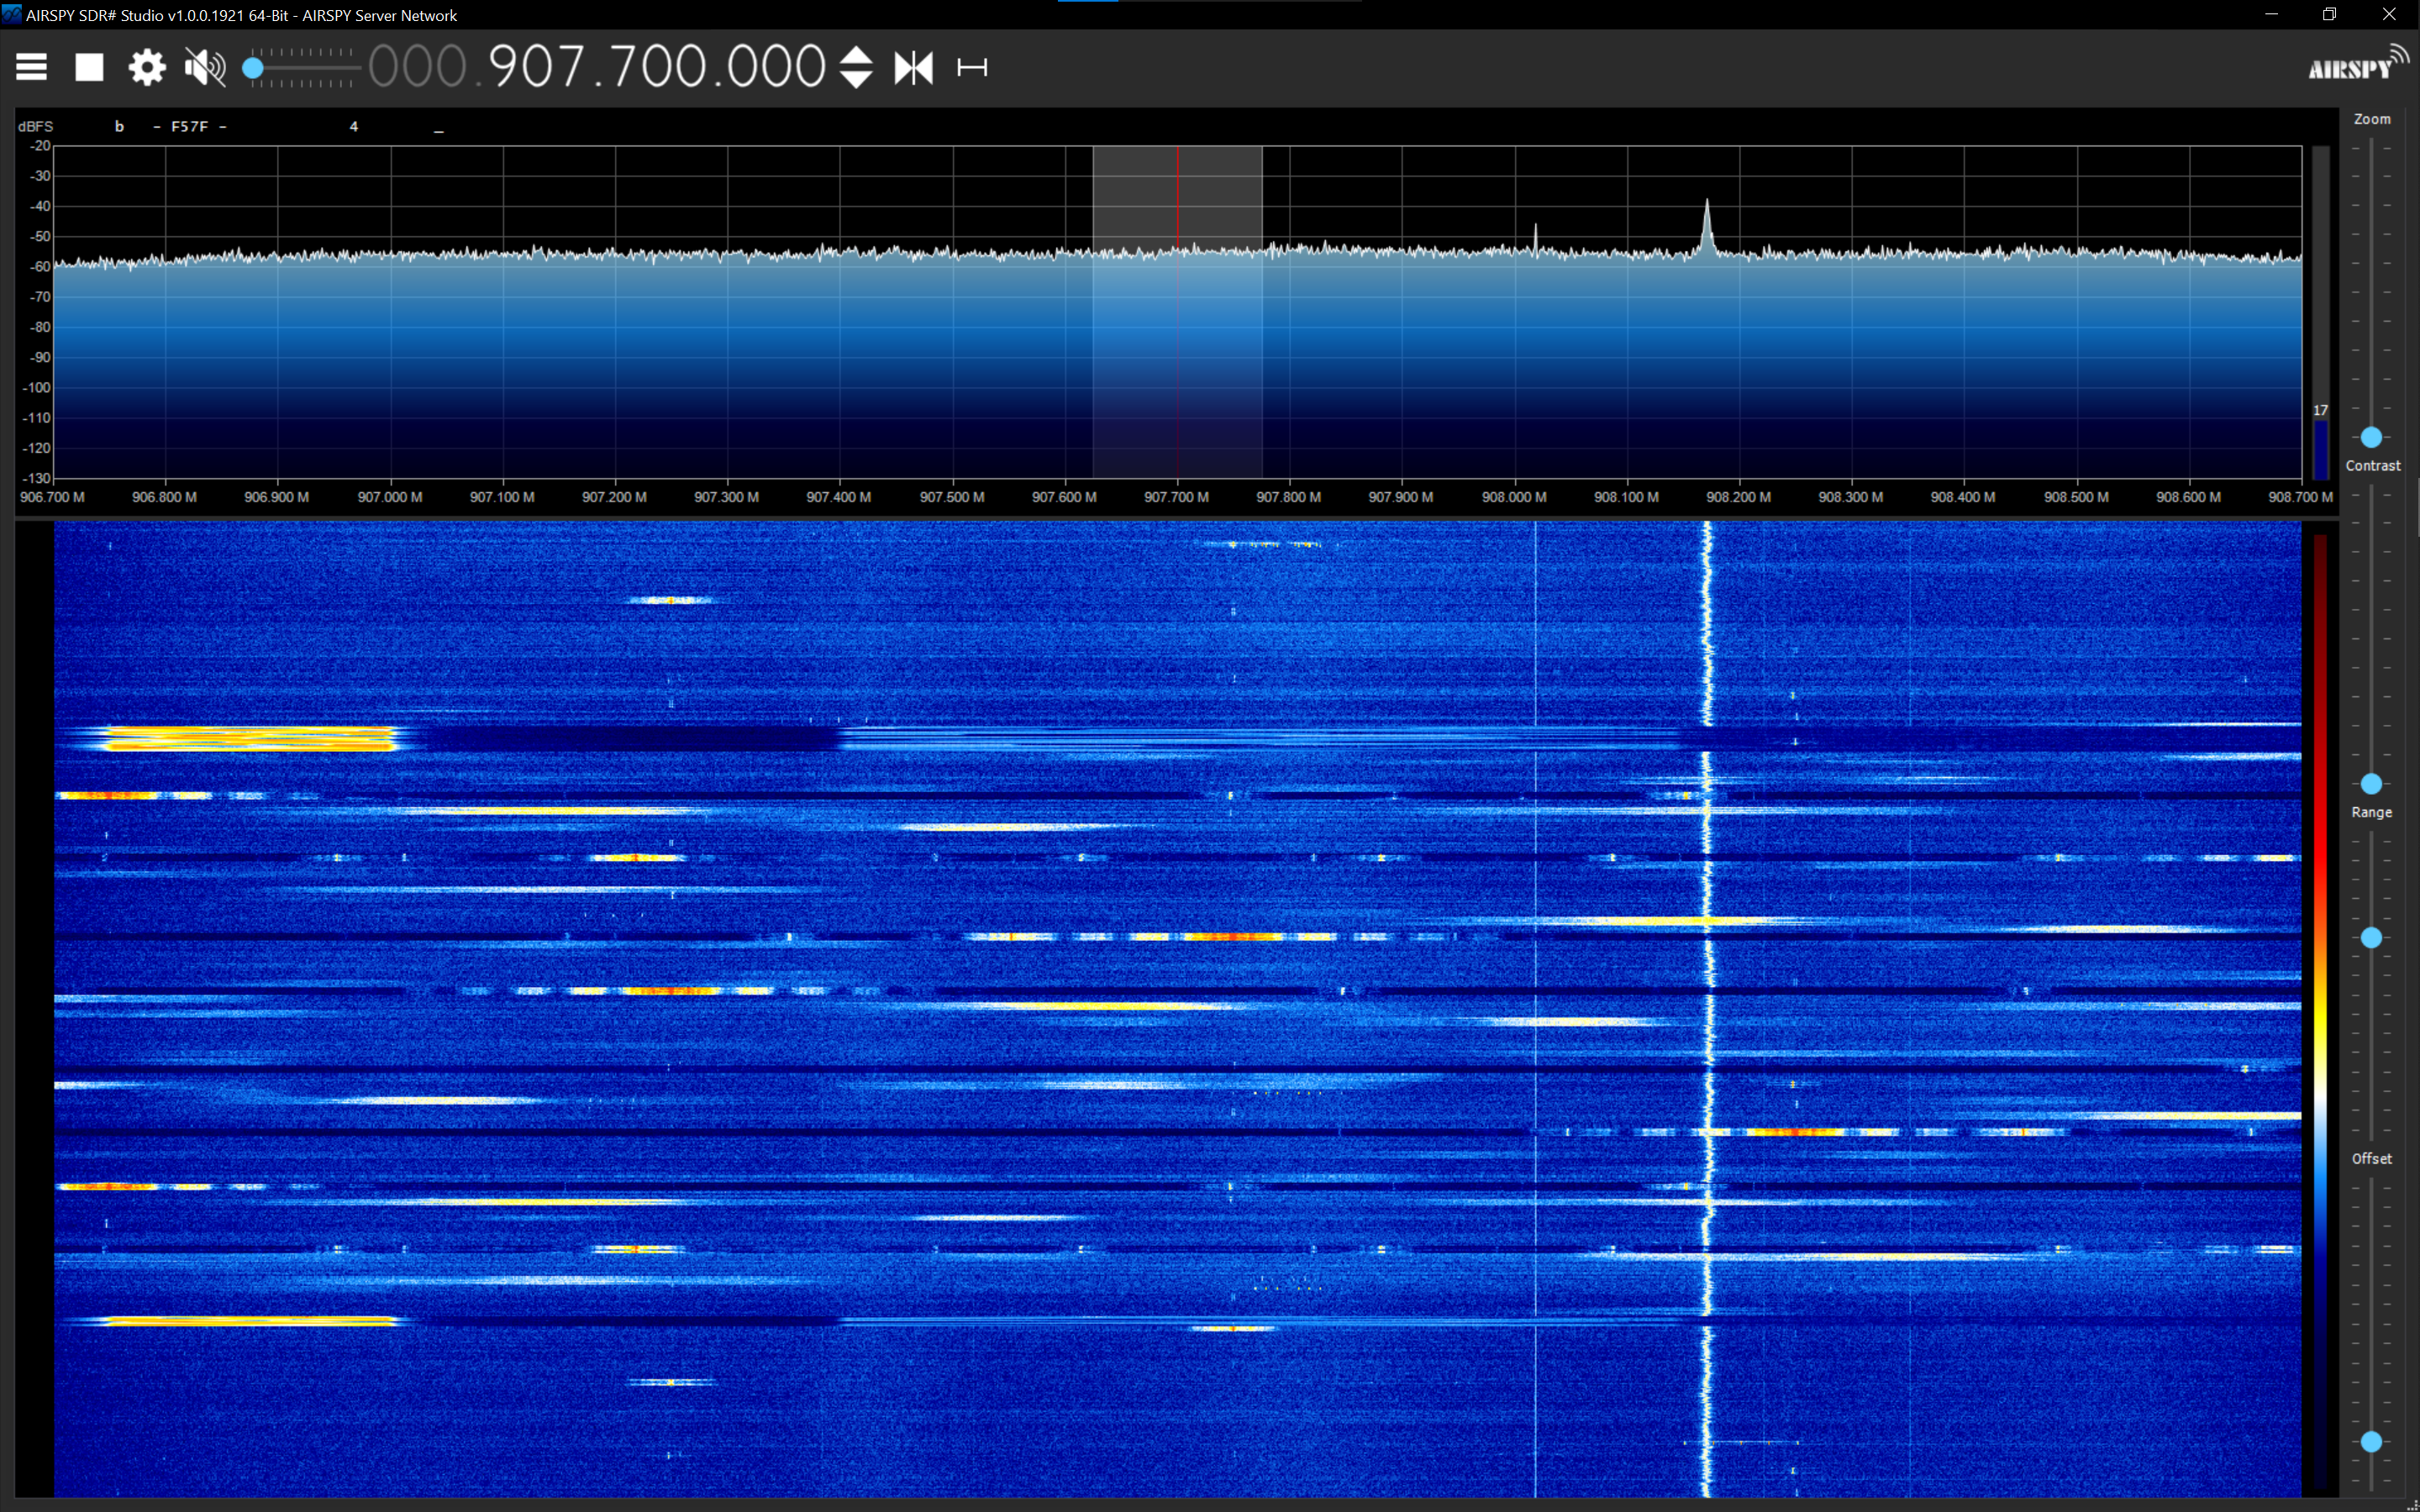
But the biggest problem they encountered was interference from other devices on the ISM band. In a dense urban environment like Philadelphia such interference is essentially unavoidable, but they found that Meshtastic operating at 500 kHz was especially susceptible to the electromagnetic din of the city. From their investigations, they theorize that the narrower bandwidth used by Meshtastic’s default mode was better able to slip through some of the interference, while the wider 500 kHz mode was more likely to collide with other transmissions.
Welcome to the Wild Wild Mesh
Given its poor performance at 250 kHz in an urban environment and the growing concern that anything less than 500 kHz could draw the ire of the Federal Communications Commission, Philly Mesh caused a considerable wave in the community earlier this month when they announced they would be switching to MeshCore.
While MeshCore was also impacted by interference at the FCC-compliant 500 kHz, during their testing Philly Mesh found that its protocol seemed to handle the situation more gracefully. The announcement also explained that they hadn’t given up on Meshtastic entirely, and that future installations may run both. But at least for the time being, it was determined that MeshCore offered them the best chance of creating a reliable mesh network in Philadelphia — a goal which superseded any loyalty they may have felt to one particular project.
One large network which could be accessed by anyone using Meshtastic’s default configuration has now been broken into several factions. In theory everyone could simply start over from scratch and move over to the same configuration, but the potent combination of tribalism and apathy is all but guaranteed to keep many users in their respective niche, kicking off what’s essentially a LoRa turf war.
It’s too early to tell what will become of Philadelphia’s mesh aspirations. There’s little reason to question their analysis of the situation on the ground, and it could very well be that using a custom MeshCore configuration is the best way for them to achieve their stated goals. But it’s still a painful transition, and you can be sure that other large mesh networks in the Northeast and beyond will be keeping an eye on the situation as they consider their own futures.
Featured image: “Meshtastic T-Beam” by [Chiffre01]
Tech
Endless Light Shows Danny MacAskill on a Bosch-Powered Santa Cruz Vala E-Bike in Norway’s Midnight Granite
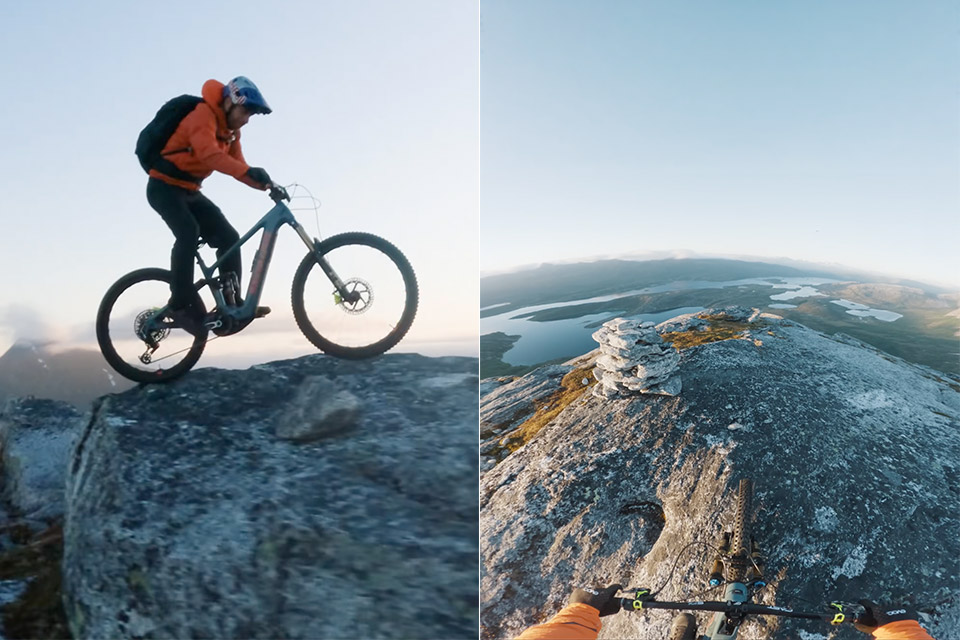
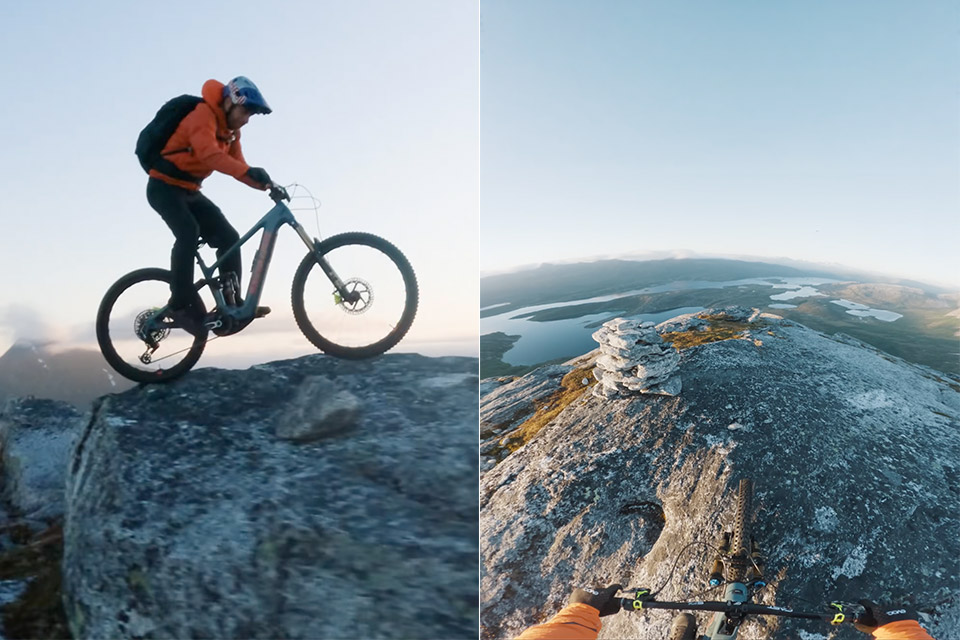
Scottish rider Danny MacAskill has wanted to experience Norway’s granite slabs for years. This summer he gathered friends, pointed a camera crew north, and spent days on the rock around Narvik while the midnight sun hung in the sky and refused to leave. Bosch eBike Systems backed the short film that came out of that trip, titled Endless Light.
Narvik stands out in Nordland, far north of the Arctic Circle, where fjords cut deep into the mountains and smooth granite hillsides blend smoothly into the scenery like a frozen waterfall. MacAskill and his crew spent three days attacking three named zones that every cyclist in the area is familiar with: Escalator, Superbowl, and Mission Ridge. On this terrain, the rock appears to continue on forever, with water and distant ice glinting tantalizingly just off the edge of the frame.

Insta360 X6, 8K 360 Camera with 1/1.1” Sensors
- DUAL 1/1.1″ SENSORS & TRIPLE AI CHIP SYSTEM: Custom-built dual 1/1.1″ square sensors deliver unprecedented 360 image quality. Combined with a triple…
- FLAGSHIP 8K50FPS 360 VIDEO: Hit record on our 360 action camera and capture your world in stunning native 8K50fps video. Every view, every highlight…
- IN-HOUSE AI MODEL FOR EFFORTLESS 360 EDITING: Insta360’s own AI model, built specifically for 360 editing. New AI Director edits your footage…
He rode the Santa Cruz Vayla(CC), a powerful Bosch Performance Line CX eMTB. With 85 Newton meters of torque and a max output of 600 watts, the bike requires riders to do the work, but the motor does provide them with the ability to keep moving even when they would otherwise be trapped walking all day with a bike on their back. MacAskill believed the motor enabled the crew to cover far more land than they would have been able to on a standard bike, and that the Vayla was the ideal tool for the work in Narvik, making the entire trip a once-in-a-lifetime event.
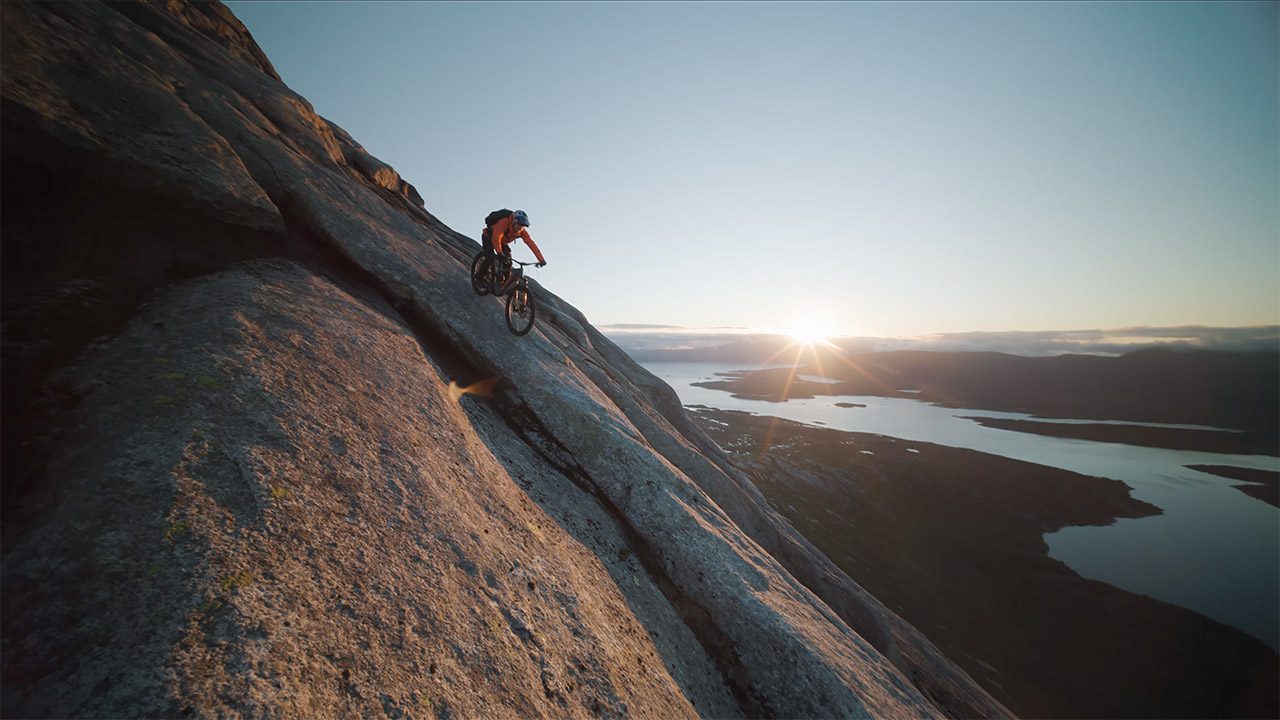
MacAskill continues to do his own thing, even with a motor aid. One sequence has him performing a backward nose manual across a really long slab, which makes your hands sweat just seeing it. Other lines pick their way along a narrow crest before following a long, exposed granite spine flanked by nothing but air. There’s one crazy final run that is so steep that the camera can’t decide whether to follow the rider or go down the slope.
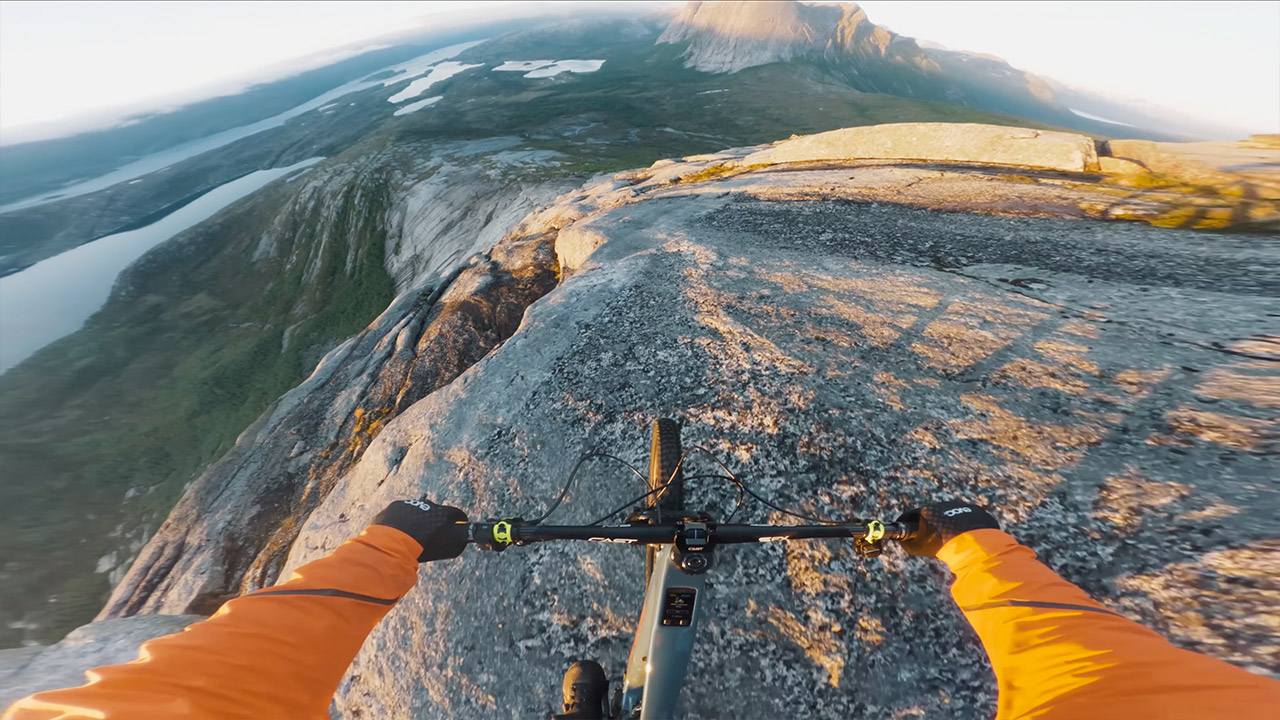
They took advantage of having a small crew and some fantastic friends to film in the continuous light of the midnight sun, which meant no frantic quest for the golden hour or wild sprint against the clock to finish filming before dark. The only thing they had to worry about was the slow, steady change in color when the moist stone was saturated by sunlight.
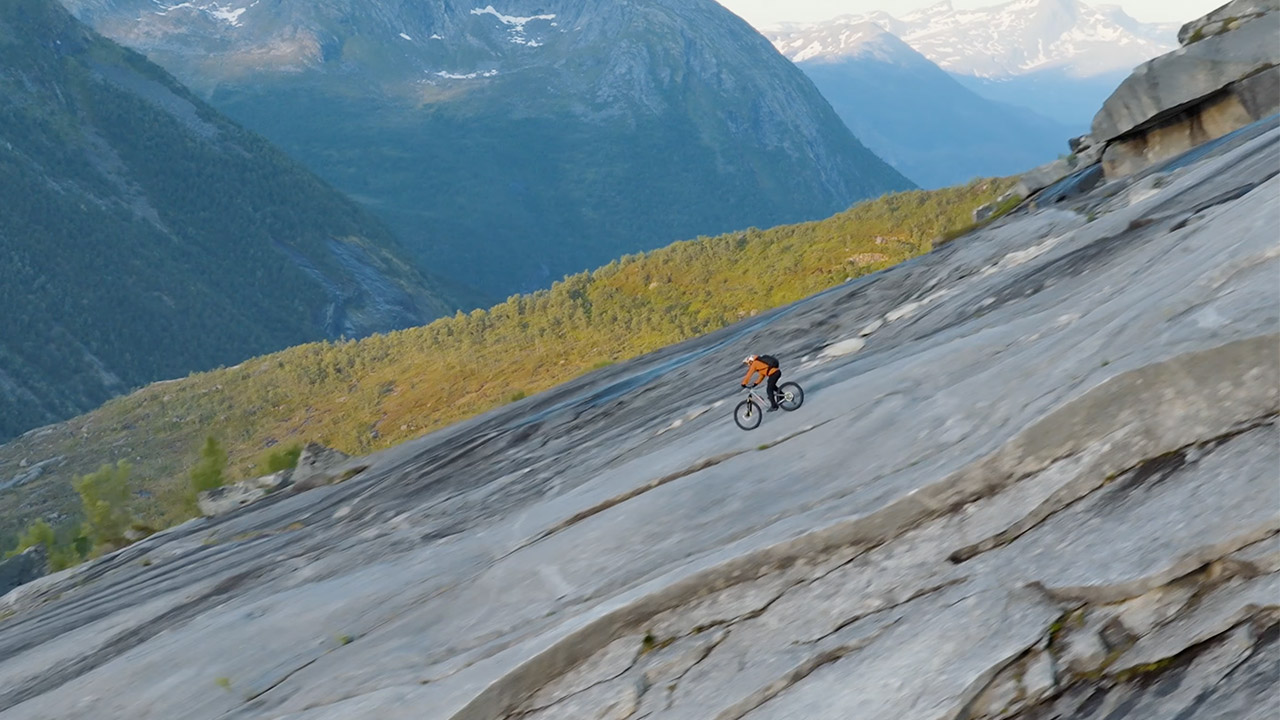
The soundtrack for the film includes Max Cooper’s ‘A Model of Reality (Tor Remix),’ which is an excellent pick to accompany the gorgeous film. If you’re wondering how they got all of the gear to the location without causing a logistical disaster, another behind-the-scenes video shows how crazy it was. MacAskill’s own perspective on the project is straightforward: he had always been fascinated by the slabs at Narvik, so he booked the entire thing and invited the people he wanted to experience it with along for the ride.
[Source]
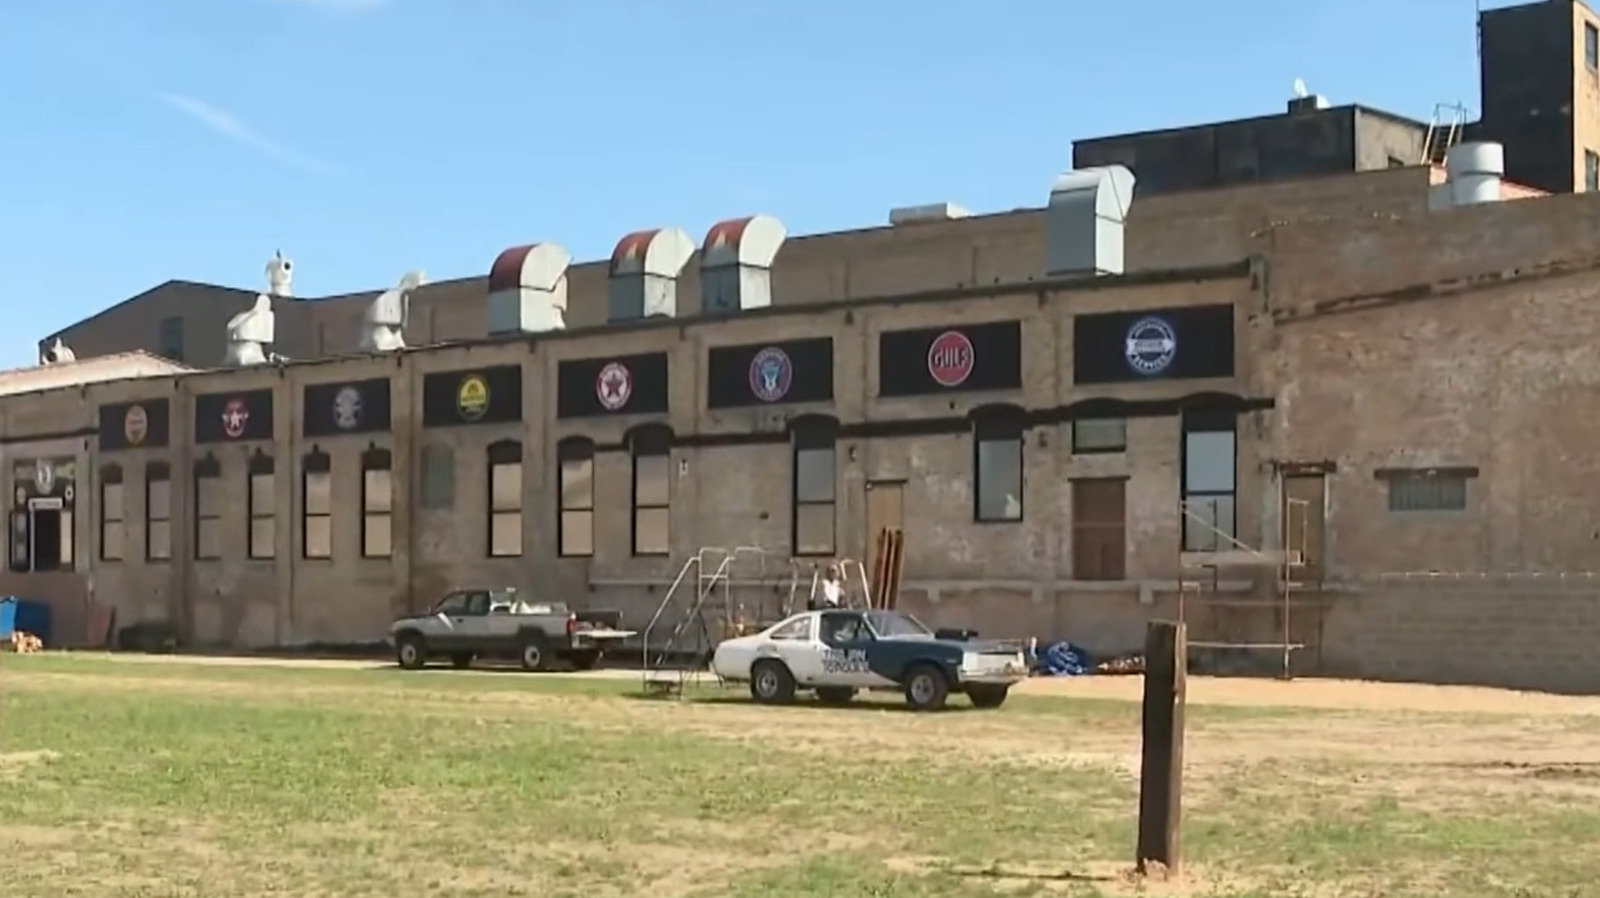
In 2000, after 114 years of operation, a paper mill in Plainwell, MI went bankrupt and shut down. With paper production continuing to decline, it may be surprising to hear that someone purchased the Plainwell Paper Mill and that it will operate once more after 25 years. However, it won’t be making paper — the mill has become home to the Michigan Classic Auto Mill, which will restore, store, and sell classic vehicles. This feels like a fitting business for a historical building with a lot of connections to locals in town. It felt so right, in fact, that the city sold the 255,000-square-foot property to Darius and Rimante Grigaliunas for just $1.
Plainwell City Manager Justin Lakamper said that the new classic car company will be “a huge thing” for the city, which makes sense: Michigan is home to the number one car city in the country. Plainwell has been debating what to do with the old paper mill for decades. Now, former employees and the public are invited to the grand opening of the Michigan Classic Auto Mill on Saturday, October 3, complete with a polka band and beer garden.
Plans for the Michigan Classic Auto Mill
While the Grigaliunas only purchased the property for $1, they signed a contract that requires them to fix up the property within a certain time period. Plainwell residents themselves, Darius and Rimante are excited to revitalize the property as self-proclaimed “massive environmentalists.” They previously purchased the Wurlitzer Piano plant in Illinois, which was in a state of disrepair. The duo restored it and transformed it into the Classic Auto Factory, which now stores between 75 and 175 vehicles over 20 years old — and it takes a lot of special care to properly store a classic vehicle.
For the Grigaliunas, buying the old paper mill and turning it into the Michigan Classic Auto Mill is not just about making some money — they view it as a “redemption project” for the town. On top of storing and selling classic cars, Girgaliunas envisions a possible restaurant and indoor athletic facility with batting cages. The plan is quite flexible based on what the Plainwell community wants, but the first step is to get the core business up and running so they can start creating some job opportunities. Noted Grigaliunas: “We only want local people working on the building. People from Kalamazoo, Plainwell, and Grand Rapids. I’m here to build relationships with the locals. We’re going to rebuild this and reopen this mill together.”
Signal is finally letting people sign up without handing over their phone numbers, but it’ll cost $3. The option is rolling out in the Android 8.28 beta, removing a longstanding registration requirement for people who’d rather keep their phone numbers private.
It’s a one-time payment, not a subscription. Signal says the fee is meant to discourage spammers from creating accounts in bulk, while its payment system prevents purchases from being directly linked to the accounts they create.
Why is Signal charging for privacy
Removing the phone number requirement could make it easier for spammers to create accounts at scale. Charging for each registration makes that considerably more expensive without forcing people to provide a phone number. Signal has also introduced separate protections against phishing and fraudulent profiles.
The fee is $3 in the US, although prices may differ by country. Registering with a phone number remains free, so existing users aren’t suddenly being asked to pay for Signal.
Signal also hasn’t committed to keeping the price at $3. If numberless accounts become a significant source of spam, the company may increase the fee to discourage mass registration.
How does Signal keep payments private
Paying for an account introduces an awkward privacy question. A purchase could potentially create a link between someone’s payment information and the account they’re trying to keep separate from their identity.
Signal uses the same zero-knowledge proof system behind its donations to prevent that connection. The company can process the purchase without directly associating it with the resulting account.
Payment anonymity is only one aspect of privacy, though. Notification previews can still expose Signal messages through a device’s operating system, depending on its settings.
There’s a catch for anyone using an Android device without Google Play Services. Payments currently go through Google Play, so those devices aren’t supported. Signal plans to introduce additional payment methods, although it hasn’t provided a timeline.
What should users know before signing up
Numberless accounts come with a strict recovery system. Signal provides an Account ID and Account Key, and losing either means permanently losing access. There’s no recovery mechanism, so saving both in a password manager is essential.
Existing users can’t remove phone numbers from their accounts yet, either. Anyone hoping to switch an existing account to the new system will have to wait while Signal considers whether to support that option.
For additional protection, Signal also offers a built-in screen lock and other privacy controls, although these won’t help recover a lost Account ID or Account Key.

News Videos2 minutes ago
Fast Rap Trap Rap Beat Instrumental ”MONEY” DaBaby x Tyga Type Club Hype Banger Whistle Beat
NewsBeat3 minutes ago
Millie Bobby Brown, 22, welcomes second child with Jake Bongiovi, 24, by adoption

Business4 minutes ago
Fiber strategies for GLP-1 innovation



-

 Fashion6 days ago
Weekend Open Thread – Corporette.com
-

 Tech4 days ago
The Latest Weird Thing to Play Doom Is the Mapped-Out Brain of a Fruit Fly
-

 Business6 days ago
10 Most-Streamed Songs On Spotify In 2026 So Far, Led By Ella Langley’s Dominant Run On The Charts This Year
-

 Crypto World6 days ago
XAG/USD: Silver’s Short-Term Rally Meets Its Moment of Truth
-

 Tech7 days ago
Battery life is the only iPhone 18 Pro and iPhone Duo upgrade I care about. Apple didn’t disappoint
-

 Crypto World6 days ago
Diesel Tops $6 a Gallon for the First Time as 28 States Set Records
-

 Crypto World7 days ago
OKX launches 10x OpenAI, Anthropic X-Perps in Europe
-

 Crypto World3 days ago
Kraken Lets xStocks Holders Earn Yield Through DeFi
-

 News Videos6 days ago
Facing Financial Fears
-

 Crypto World3 days ago
Elon Musk Drops a Bombshell: Grok 5 Could Be the AGI Breakthrough
-

 Business4 days ago
Rivals Sam Altman and Elon Musk Rally Behind Dario Amodei’s Call for a Slowdown in AI Development
-
Crypto World7 days ago
Ethereum Price Analysis: Consolidation at $2.5K Tests Momentum as On-Chain Activity Surges
-

 Crypto World16 hours ago
US Charges Robinhood Engineers Over Crypto Listing Trades
-

 Crypto World5 days ago
Can AI Build a Startup in 72 Hours? Elon Musk's Team Will Livestream the Test
-
 Entertainment6 days ago
News Specials, Movies, Shows, More
-
 NewsBeat3 days ago
‘Sick conspiracy’: Trump says only guardrails AI needs is ‘a strong and smart (High IQ!) president’ in all-caps rant
-

 Crypto World6 days ago
Bitcoin ETFs Pull $167M as 2026’s Best Inflow Run Slows
-
 Crypto World7 days ago
US CPI forecast at 3.4% as tariff risks build
-
 Entertainment6 days ago
New Horror Movie Officially Earns a Rare Stephen King Recommendation
-

 Crypto World5 days ago
Robinhood Chain Never Stopped But its Blobs Did Stop Reaching Ethereum For 14 Minutes
You must be logged in to post a comment Login