Elon Musk filed to have Apple dismissed from the lawsuit he brought against it and OpenAI, and OpenAI demanded answers. The judge has denied OpenAI’s request to reveal settlement terms.
When Elon Musk’s SpaceXAI sought to dismiss Apple from the ongoing lawsuit brought against it and OpenAI, it wasn’t clear exactly what had transpired. In OpenAI’s efforts to find out, it has been revealed that there was some kind of settlement reached between the companies.
OpenAI asked that the settlement terms be revealed, but after Judge Pittman reviewed the settlement, he denied the request. The decision was first shared by 9to5Mac, which said that if the settlement terms were relevant to the ongoing case with OpenAI, they could be shared, but they apparently are not.
The Court hesitates to compel the production of confidential settlement agreements entered by parties. Confidentiality in settlement serves the “[s]trong federal policy” of “induc[ing] the parties to settle a case.”
In other words, if Apple and SpaceXAI want to settle out of court, it is not only their business to do so, but to do so confidentially. To make such agreements public could jeopardize such agreements from ever taking place.
An odd lawsuit either way
The origins of xAI’s, now SpaceXAI’s, lawsuit against Apple can be tied to a tirade by owner Elon Musk. He made claims that the App Store was favoring OpenAI’s ChatGPT over Grok and Apple was biased against X.
He claimed that Apple was manipulating App Store charts to keep Grok and X from ranking higher, keeping ChatGPT at the top. The problem is, all of these claims were easily proven incorrect.
By the time the lawsuit came about, the accusations were shrunk to much more manageable proportions. Musk focused on Grok and accused Apple and OpenAI of anticompetitive collusion.
Advertisement
Whatever agreement or settlement Apple and Musk came to, it is unlikely that OpenAI can escape as easily. Elon Musk is known to have a very strong rivalry with his former business partner Sam Altman, the current CEO of OpenAI.
Google and Google DeepMind researchers launched the DeepMind Institute on Wednesday to advance the conversation around artificial general intelligence (AGI). The institute lists DeepMind co-founder Shane Legg, Google executive James Manyika, and Google DeepMind chair Demis Hassabis as directors, with Legg serving as managing editor.
The new institute aims to surface differing views between Google, Google DeepMind, and the broader global research community around AGI. “They will not always agree, and they will likely change their minds, as more data and information comes to light at the fast-moving frontier,” the announcement read.
The inaugural collection of four essays covers a range of topics: economic policies for managing potential AGI disruption, preserving human-readable model reasoning, principles for human flourishing, and a framework for evaluating frontier AI models.
One essay, by DeepMind safety researchers Rohin Shah and Anca Dragan, argues that AI’s shrinking window of transparency — the ability to see and check a model’s step-by-step reasoning — is not inevitable. As new architectures make the most powerful models harder to monitor, the authors say developers and regulators should confront the safety trade-offs directly. That could mean limiting “opaque serial depth”— the amount of sequential computation a model can perform without producing a readable reasoning trace — or requiring developers to demonstrate that less transparent systems remain just as monitorable.
Advertisement
In another essay, Hassabis proposes a U.S.-led frontier AI standards body to evaluate the most advanced AI models. Under his framework, developers would initially submit models voluntarily for review up to 30 days before release. Once the evaluation system has proved effective, passing its tests could become a requirement for deploying frontier models in the United States.
The body would at first design assessments in consultation with AI companies but would eventually develop independent, undisclosed evaluations — what the essay calls “held-out” tests — to prevent labs from tailoring their models to known evaluations. Hassabis said the framework could be “ratcheted up if the seriousness of the situation demands,” potentially including a coordinated slowdown among frontier AI developers.
The essays arrive as the industry’s safety debate shifts from broad statements of concern toward concrete proposals for disclosure, outside scrutiny, and, if safeguards fall behind, coordinated slowdowns. That shift accelerated this week as industry leaders endorsed elements of Anthropic CEO Dario Amodei’s call to “pace” frontier AI development.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
Tuesday U.S. Space Force chief Douglas Schiess said his branch of the U.S. military operates “on-orbit weapons,” reports Reuters, to defend “against space-enabled attacks.” He promised “disciplined and responsible choices” when scaling America’s orbital defense arsenal in the coming years.
NPR calls this week’s reveleations “remarkable… after previous warnings about countries such as Russia possibly weaponizing a global frontier long agreed in treaties to be used for only peaceful purposes.”
The revelation comes as the Trump administration puts a growing focus on space. In 2019, during his first term, Trump created the Space Force as a separate military branch. In his second term, he has announced the “Golden Dome” missile defense system, which includes plans to put U.S. weapons in space. Trump said last year that he expected the system would be “fully operational before the end of my term,” which ends in January 2029, and have the capability of intercepting missiles “even if they are launched from space.” Trump also has directed the Pentagon to pursue the space-based interceptors, in an executive order during the first week of his presidency. The Congressional Budget Office estimated that just the space-based components of the Golden Dome could cost as much as $542 billion over the next 20 years.
The Biden administration announced in 2024 that Russia was developing a space-based nuclear weapon that could loiter in space for long durations, then release a burst that would take out satellites around it. That kicked off a renewed debate on the idea of weapons in space at the United Nations. In April 2024, Russia vetoed a joint U.S.-Japanese resolution that would have called on all countries not to develop or deploy nuclear arms or other weapons of mass destruction in space, as banned under a 1967 international treaty that included the U.S. and Russia… The Russian delegation called the resolution hypocritical and a double standard and instead proposed a rival resolution to ban all weapons in space “for all time.” It ultimately failed. Russia had argued that the United States and its allies opposed a ban on all weapons in outer space because they planned to deploy weapons there.
Advertisement
Reuters calls this “a landmark moment in space militarization,” while noting that it’s “aimed at deterring what U.S. officials describe as aggressive orbital activities from China and Russia, officials and analysts said.”
The remarks this week by Washington’s top military-space officials are part of “the increasing comfort level of the U.S. government to speak about aggressive actions in space” that has been building up in recent years, said Victoria Samson, chief director of space security and stability at the nonprofit Secure World Foundation. “We’ve gone from not talking about counter-space capabilities… to now saying flat-out we have weapons in space,” Samson said. “The pendulum keeps on shifting over that way…”
“The acknowledgment of these space-control capabilities is fundamental to ensuring that we prevent deterrence from failing, and that we are postured and ready should deterrence fail to employ them effectively,” Richard Palmer, the director of the Capability and Resource Integration Directorate at U.S. Space Command, said on Tuesday…. “The bottom line is that our joint force and our allied forces require space. Our economies require space,” added Palmer. “We are ready in the U.S. to preserve that.”
Reuters adds that Russia’s Foreign Ministry issued criticism of America’s move, saying “In pursuit of its narrow self-interests, Washington is ready to completely ignore the catastrophic consequences for humanity of any armed conflict in orbit.”
The hackers have reportedly given Revolut 24 hours to pay the ransom, or else they will sell the stolen data to other criminals.
A group of hackers claiming to be responsible for a recent Revolut data breach has reportedly threatened to sell the confidential records of hundreds of customers to other criminal groups unless the fintech company pays them a ransom of $3m in cryptocurrency Monero.
According to the Financial Times, the group – which called itself ‘iamnotavillain’ – published the demand on its website yesterday (16 September) alongside a digital countdown clock, giving the British online bank 24 hours to comply.
Last Saturday (12 September), Revolut admitted that it disclosed sensitive customer data to an unauthorised fraudulent party after receiving requests for information from an email with a government agency domain. The leaked data included information such as full names, dates of birth, occupations, addresses, contact details, passports, drivers’ licences, financial statements and facial verification images.
Advertisement
It is believed around 680 people, including 12 in Ireland, have had their personal information compromised.
The Financial Times contacted the hacking group through Telegram and were then sent a 60-second screen-capture video showing an unseen user moving through the cache of purported Revolut documents.
Reportedly the online message told Revolut to pay the $3m, “otherwise all the data will be sold and the blood will be on your hands”. The group also told the Financial Times that the demand notification was the first communication attempt and that, as of yet, there had been no negotiations with Revolut.
In an official statement to SiliconRepublic.com, a Revolut spokesperson said: “Revolut has not received any direct contact or demand from the individuals or group making these claims.”
Advertisement
The reported ransom comes after Revolut recently announced that it had applied for a Swiss banking licence as part of its continued global expansion campaign. The company plans to invest more than 150m Swiss francs into Switzerland over the next five years, as a means of creating jobs and supporting product development.
In August, the company received a full banking licence in France, giving the fintech giant a second European Union hub. The company claims to have more than 75m customers worldwide.
Updated, 5.00pm, 17 September 2026: This article was amended to clarify accurate phrasing in relation to the data breach.
Don’t miss out on the knowledge you need to succeed. Sign up for the Daily Brief, Silicon Republic’s digest of need-to-know sci-tech news.
A camera in a toothbrush? Dyson tells us why it combined ‘WiFi, AI, intelligent sensing and fluid dynamics with a highly engineered brushing experience’ to create the Dyson Camerajet
The Dyson Camerajet arrived 10 years after online rumours emerged that Dyson had filed a patent application for an electric toothbrush with water jet. True to form, it has surpassed the rumours with a toothbrush that goes one step beyond the norm and is packed with innovation. Having trialled it a week prior to launch, I was among the first journalists to give the Dyson Camerajet a hands-on review.
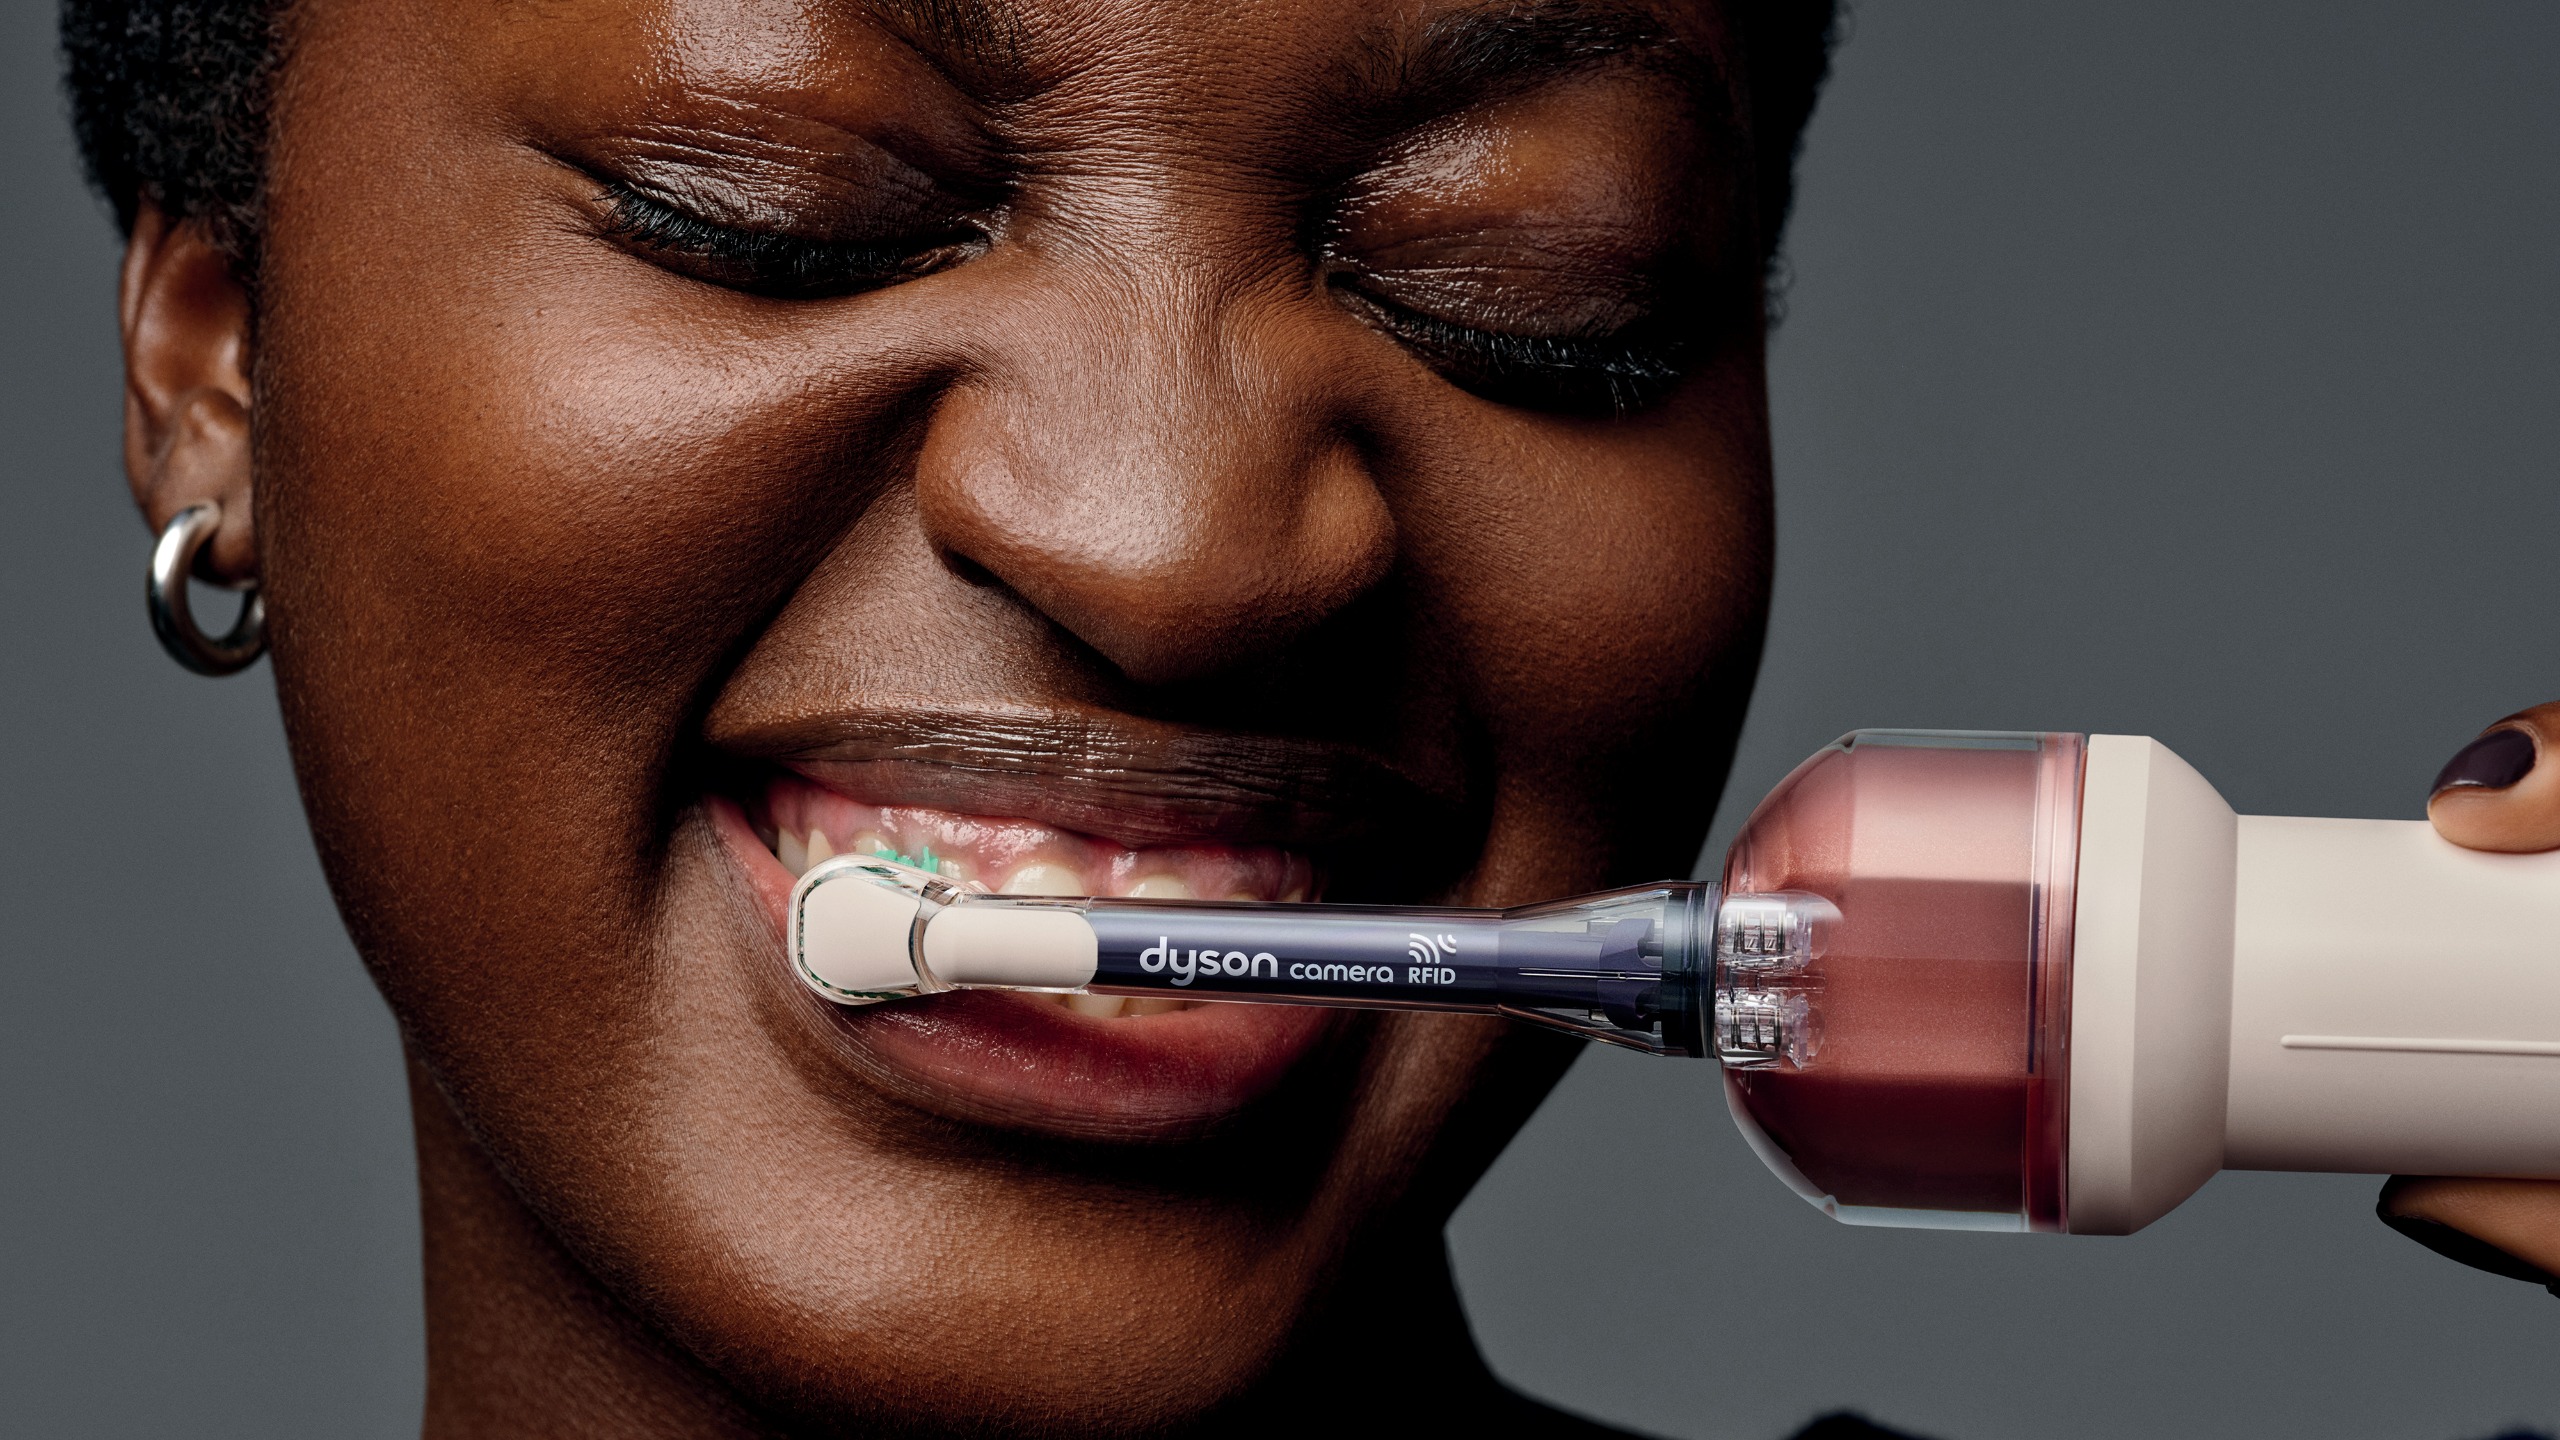
As the only smart electric toothbrush and water flosser with a built-in camera, the CameraJet uses imaging, machine learning and precision fluid dynamics to identify gaps between teeth and deliver a jet of mouthrinse. The CameraJet has received much attention since its launch, with many praising Dyson for pushing the boundaries with new innovation in oral health, and others questioning its price, reporting faults online, and asking whether we need a camera in a toothbrush at all. But for a brand that revolutionised the vacuum with cyclonic suction, restyled the hair dryer and pioneered bladeless fan technology, the Dyson CameraJet was never going to be an obvious product.
Back in May 2026, I visited Dyson’s factory and global HQ in Singapore to take a first look at the Dyson CameraJet. I went behind the scenes in Dyson’s oral health care labs where six years of research, development and engineering for the CameraJet had been taking place and spoke to Rich Bacon, head of product development atDyson, to find out what makes the CameraJet so unique. I also asked him about the potential security implications of having a smart camera in the bathroom, and how Dyson hopes to improve our oral health.
Advertisement
Latest Videos FromTechRadar
Why now?
(Image credit: Dyson)
When I first saw the CameraJet I immediately wanted to know why Dyson is branching into attempting to make one of the best electric toothbrushes and why now?
The Dyson team said it likes to start with a problem people experience every day and ask whether they can solve it better through engineering. “Oral care is an area where many people want to improve their routines, but often struggle with consistency, technique, or understanding how effectively they’re brushing,” Bacon explained. “Dyson research shows 9 in 10 people do not floss as regularly as they should, reinforcing the need for a solution that helps target the gaps between teeth as part of an everyday routine.
Advertisement
“The technology is now at a point where we can combine WiFi, AI, intelligent sensing and fluid dynamics with a highly engineered brushing experience, making this the right time to bring the product to market.”
By combining two devices – a toothbrush and water flosser – in one, the CameraJet has the potential to save us time in our daily routines and also help us brush for the recommended time. “In our research we found that a lot of people brush for 45 seconds, but the optimum time is for two minutes, or ideally three,’ says Bacon. ‘When I’m using this device myself for three minutes, it’s much more convenient than having separate devices to clean your teeth.”
Sign up for breaking news, reviews, opinion, top tech deals, and more.
Advertisement
What excites Bacon most about the CameraJet is its sophisticated engineering combined with a simple user experience. “There’s a huge amount of technology working behind the scenes here from the camera and machine learning, to its Gap Optical Targeting and precision fluid dynamics,” he says. But the user doesn’t need to think about any of that. As engineers, that’s always our goal: solving complex problems in a way that feels effortless for the person using the product.”
Bacon believes that this technology has the potential to make oral care more consistent and personalised. “Many people brush their teeth in exactly the same way every day without really knowing if they are cleaning effectively, and many are not flossing as regularly as they should. Dyson CameraJet brings brushing, precision-flossing and mouth-rinsing to your routine to target the gaps between teeth where plaque can build up.”
Privacy included
(Image credit: Dyson)
But in an age of AI, the internet of things and relentless data collection, having a camera in your bathroom is a natural cause for concern. For Dyson, privacy was also a key consideration, however. Bacon reassures me that the camera is only active during live viewing or auto-jetting; no images are recorded or stored on the product or in the cloud, and images remain private to the user.
Advertisement
“We take privacy very seriously,’ he says. “The MyDyson app is a great companion piece and comes with unique cleaning insights such as location coverage. Through the app, you can also access guided cleaning, coverage mapping and personalised feedback so you have a better understanding of where you are cleaning well and where you may be missing.”
The app is a closed ecosystem, but could it one day become a broader health-data platform, similar to how people use Oura or Apple Health? “The app has been designed as a platform that can evolve over time, and the immediate focus is on useful, evidence-led insights that help people understand their brushing and interdental cleaning habits,” says Bacon. “There is an opportunity to help make those behaviours easier to see, understand and improve. Any future information or guidance would need to be grounded in robust evidence and developed responsibly, but our ambition is to empower users with helpful, accurate feedback about their oral care. We’re always exploring how technology can help people get more from our products.”
Advertisement
Teething problems
(Image credit: Future / Emily Peck)
Since its launch, there have been reports on Reddit of a small number of early production batches malfunctioning, so TechRadar reached out to Dyson for comment.
‘We are aware that a small number of early batches of Dyson CameraJet products may have experienced a component issue,’ says a spokesperson for Dyson.
‘We are isolating those batches and are taking all the necessary steps to support our customers. We have had a very positive reaction to the new Dyson CameraJet and are experiencing strong demand globally and we are seeing some shortages of supply as we are in the process of scaling up production.’
Whether or not you’re tempted to try a toothbrush with a built-in camera and smart app, it’s exciting to see Dyson engineers paving a way with new innovations in oral health. And for that, I think we have a reason to smile.
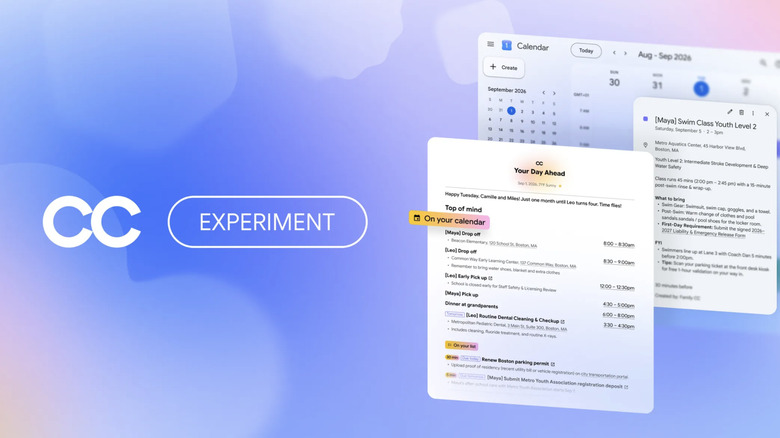
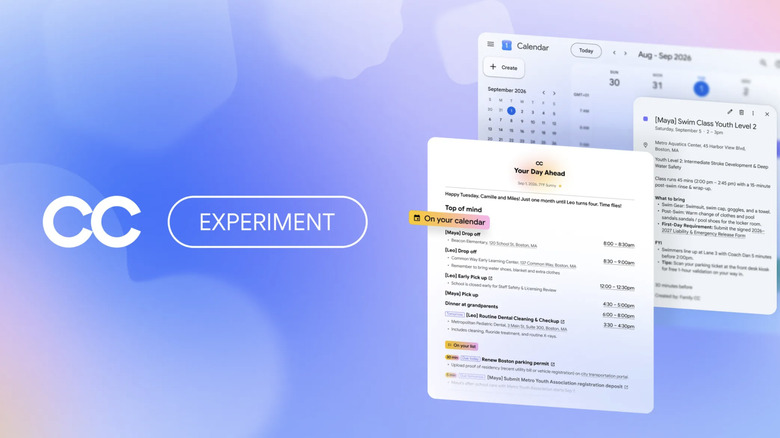
Google has a new experimental AI offering called CC aimed at helping families stay organized. This agentic AI platform has its own Google account that up to six family members can choose to share information with.
Each user can pick what emails to share with the agent, passing along either single messages on an as-needed basis or picking addresses to always send to the CC account. It also creates a shared calendar and task list that all group members can view and sends all participants a daily briefing with information about immediately upcoming events and to-dos. CC can be used to file paperwork and handle logistics like filling out registration forms or writing a shopping list, although those tasks are designed to ask for a user’s permission before taking action.
Eagle-eyed readers may feel like the name is familiar, and it is. Google first debuted an experimental tool called CC last December, but rebranded it as the company’s Daily Briefing feature earlier this year. Now it’s pivoting the CC project to be this family-centric organizer based on requests from the tool’s early testers.
Advertisement
Users can add CC to a Drive folder or share specific files with the agent, as well as interact with it in a dedicated Google Chat window. Google laid out several of the privacy limitations for the agent in its FAQ, and those include restrictions on CC being able to add or remove family members and to access or search members’ individual inboxes.
Existing CC users will receive a prompt from Google to upgrade their account and try out the new tools. There’s a wait list for any new users who want to outsource their planning with this agentic approach.
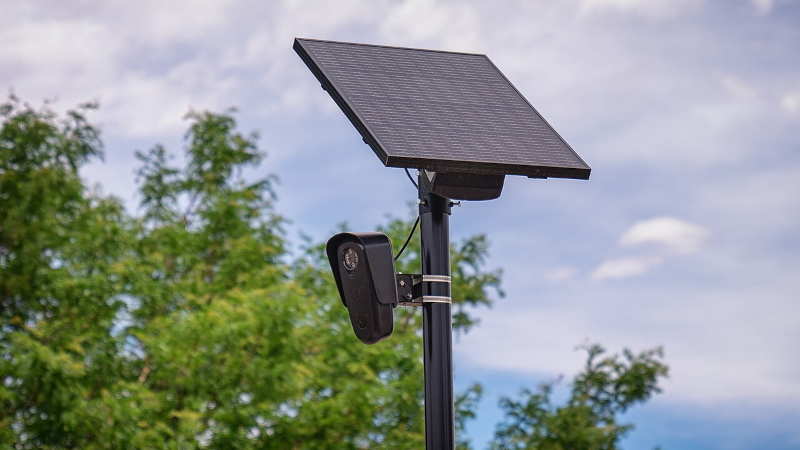
Surveillance cameras from Flock Safety have become a controversial privacy battleground, as the communities in which they are installed wake up to their sinister potential, and stories roll in of law enforcement professionals abusing their access. One has had its disk contents dumped, and we’ve been treated to some insights courtesy of [Micah Lee]. In short: their approach to security is deeply flawed.
It’s interesting to find that instead of a custom hardened OS, these devices run Android. Not just Android, but Android 8.1, a long out of support version originally released in 2017. This is is the year Flock Safety was founded, which may or may not be coincidental. Like any old version of a widely used operating system it has a host of known vulnerabilities, none of which are patched on this version.
The Android version is small beer compared to the revelation that they contain a hard-coded and very open-access API key that can be used by any mildly curious miscreant to reveal information from any Flock camera using its MAC address. One would hope that a product marketed for use by law enforcement might have paid attention to such a basic lapse, but it seems not. Whether or not this can be corrected by a software upgrade and the leaked key deactivated without turning off the network depends on whether thy can do upgrades tailored to specific devices, but either way we wouldn’t like to be the team tasked with fixing that one.
Advertisement
In a way it’s reassuring that the surveillance apparatus when it came was so incompetently managed, and we hope that these vulnerabilities will have moderated its effect. We’re sure more tasty discoveries will emerge as investigations proceed, and we’ve got the popcorn ready.
Reuters reports that a former Google DeepMind employee “became the latest AI researcher to warn that the technology could ‘kill all humans’, saying time could be running out to avoid the outcome:
Public alarm about the potential danger posed by AI is growing, after Anthropic researcher Jacob Coxon said last week he had resigned, in part because the “people building AI earnestly believe that it could kill us all by the end of the decade.” Anthropic scientist Evan Hubinger then responded to Coxon’s comments, saying he was correct and that he believed there was a greater than 10% chance that AI could kill all humans within the next decade.
“I recently resigned from Google DeepMind, where I worked on AGI safety and alignment research,” Bilal Chughtai wrote on X. “I earnestly believe that AI has the potential to kill us all, and that we might be running out of time to avoid this outcome.” Chughtai, who co-authored research papers while at Google DeepMind, worked there as a research engineer and left the company in July 2026, according to his LinkedIn profile.
Meanwhile, Meta CEO Mark Zuckerberg “said it’s up to each AI company to make sure its technology is safe,” reports the Associated Press, “distancing himself from calls by rival companies for a coordinated slowdown in the development of advanced artificial intelligence.
AI companies are already motivated to develop their models in a safe way and face “significant liability” to prevent them from causing harm, Zuckerberg said. “Every lab has the responsibility and incentive to move at the pace required to train its models safely, and the ability to take its own actions to ensure that happens,” he wrote on X… Zuckerberg said Meta delayed releasing its Muse AI agent for several months to ensure its safety and security. “We didn’t call for everyone else to do this before we would,” he said.
Advertisement
Companies should prioritize building safe AI models instead of systems that can automatically improve themselves, a function known as recursive self-improvement, Zuckerberg wrote. “Committing the significant majority of compute towards serving people rather than racing towards recursive self-improvement is one of the best ways to ensure we develop this technology safely.”
But Zuckerberg also agreed that engaging independent evaluators and advisors “is industry best practice,” adding that Meta Superintelligence Labs “already does this today in several areas because it helps produce better work…
“I believe the key to building a positive future for everyone is maintaining the right balance of power. This is within our power to do.”
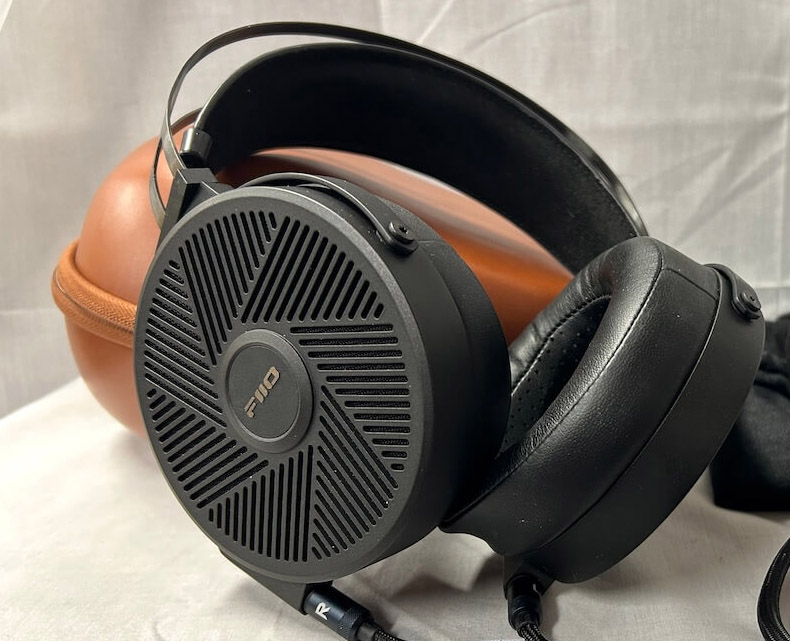
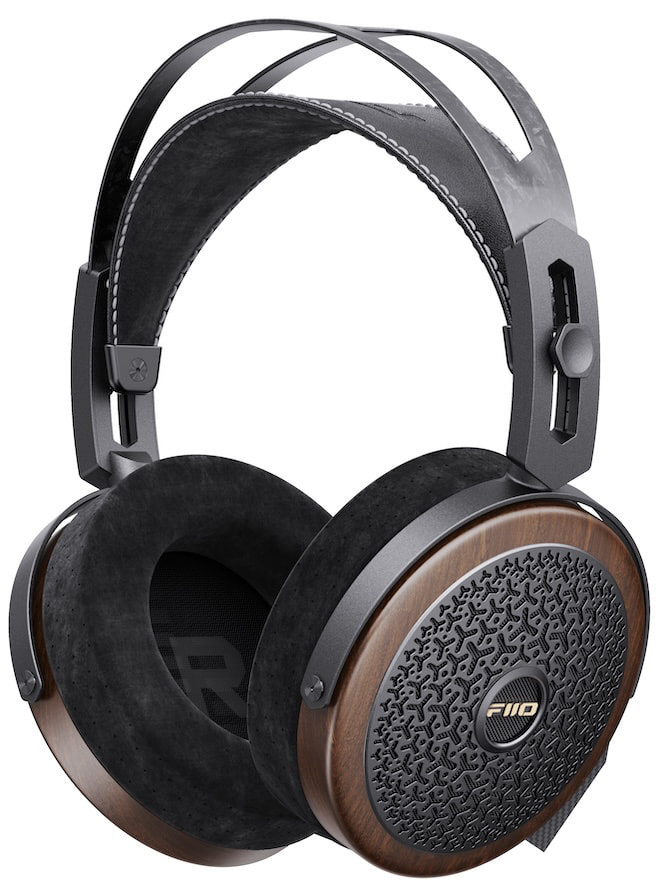
FiiO has officially launched the FT15, its new $499 open-back planar magnetic headphone and successor to the FT5. The headline changes include a substantially thinner diaphragm, larger driver, lower weight and enough manufacturing terminology to make a semiconductor engineer feel strangely at home in a headphone article.
The interesting part for us is that we have already heard them.
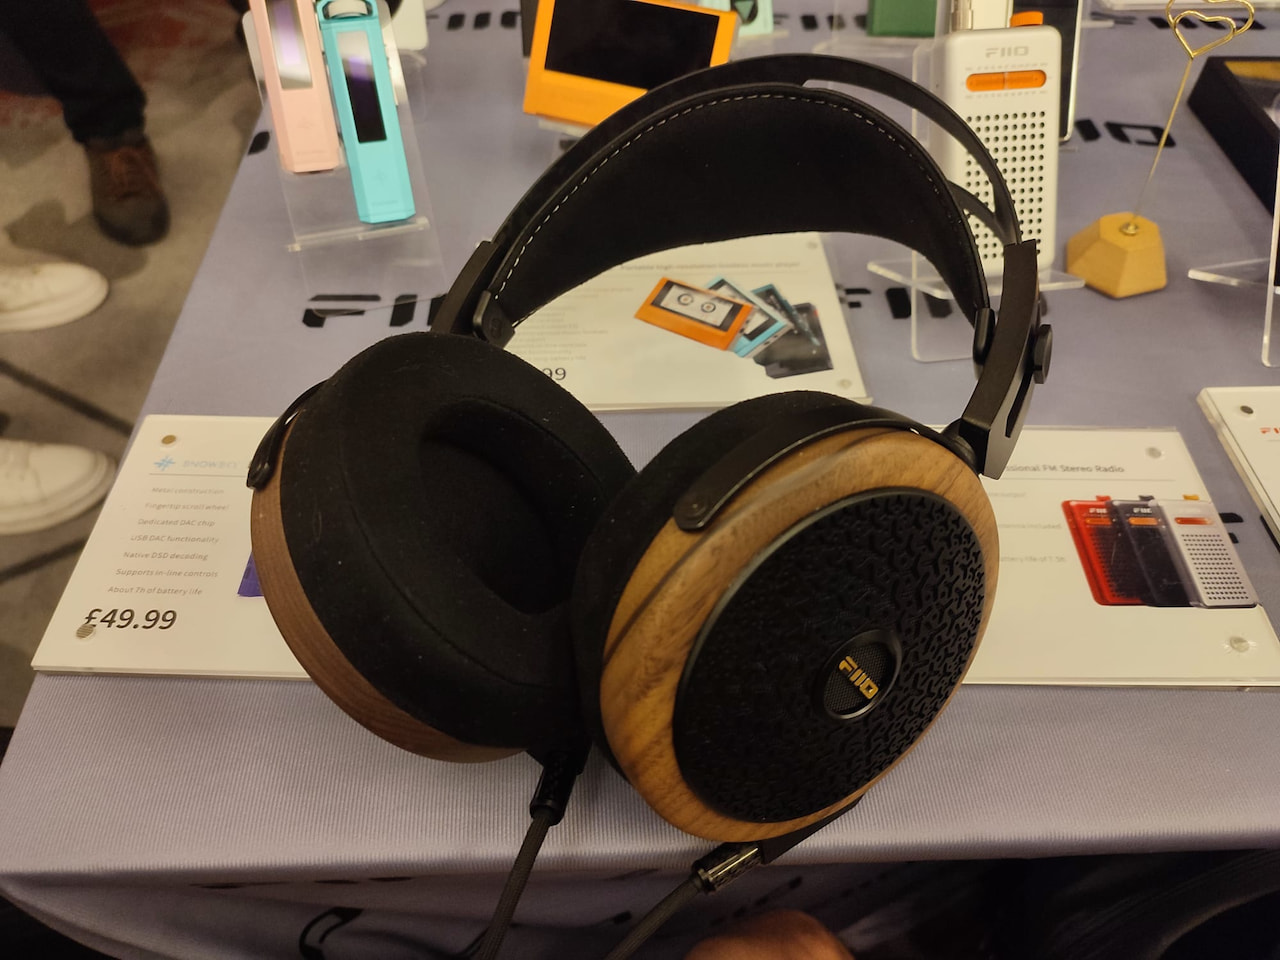
eCoustics contributor James Fiorucci spent time with the FT15 at CanJam London 2026, when FiiO was still calling it a forthcoming model and final specifications had not been released. Now we know exactly what FiiO was hiding underneath those walnut ear cups.
Related Reading:
What Changed From the FiiO FT5?
FiiO FT5
The FT15 uses a 101mm planar magnetic driver, up from 90mm in the FT5, with an effective radiating area of 6,443.5mm². FiiO says that represents a 35% increase in active diaphragm area and is intended to improve bass authority and soundstage scale.
The bigger engineering story is the diaphragm itself. FiiO has reduced its thickness from 6 microns in the FT5 to just 800 nanometers, an 86.7% reduction, before applying a full-surface diamond coating designed to increase rigidity and suppress high-frequency breakup. FiiO claims extension to 40kHz, which should keep both the Hi-Res Audio certification people and neighborhood bats satisfied.
Advertisement
A patented dual-sided magnet array works with a 28nm electroplated voice coil, while 95dB/mW sensitivity and 24-ohm impedance are intended to make the FT15 manageable with portable players and competent dongle DACs rather than requiring a power amplifier normally reserved for starting farm equipment.
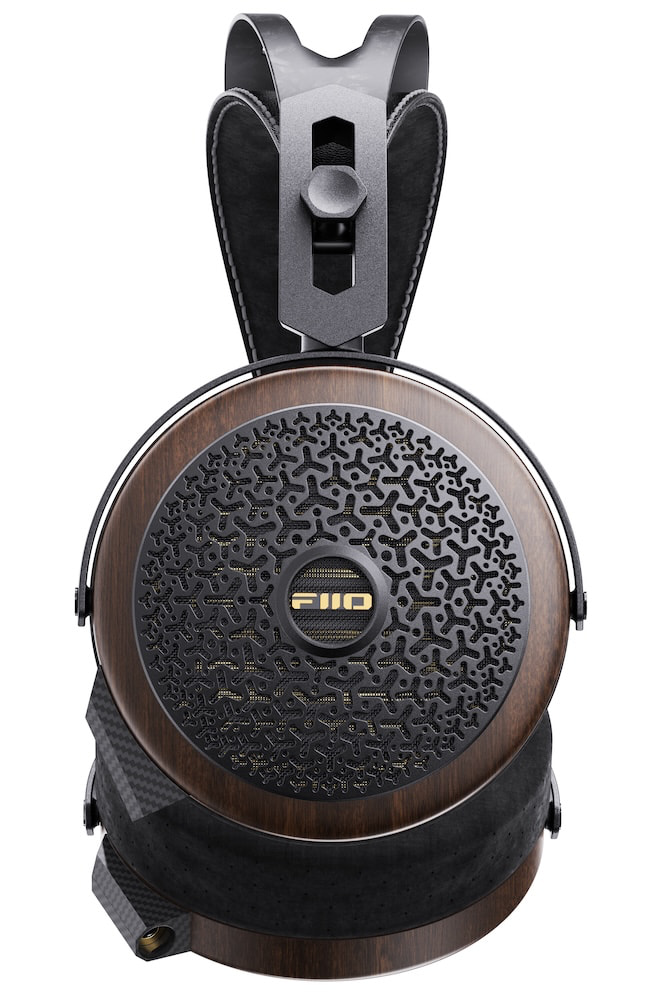
FiiO has also trimmed the finished weight to 425 grams and uses a carbon-fiber headband with North American FAS-grade black walnut around the ear cups.
We Heard the FT15 at CanJam London
FiiO FT15 at CanJam London 2026
Specifications are useful, but we had the advantage of hearing the FT15 before FiiO finished filling in the spreadsheet.
James found the prototype largely balanced, open and easy to listen to, with treble that remained airy without becoming immediately aggressive. His reservation concerned macrodynamics: the FT15 did not deliver the same physical punch or dramatic contrast as some of the stronger planar designs he heard at the show.
That was a show-floor audition rather than a controlled review, so consider it an early impression rather than the final word. It does, however, make FiiO’s claims of a warmer, more relaxed presentation somewhat more interesting than the usual launch-day adjectives written by people who have not actually put the headphones on their heads.
Advertisement
FiiO FT15
FiiO FT15 Specifications
Type: Open-back planar magnetic
Driver: 101mm planar
Diaphragm: 800nm with full-surface diamond coating
Availability: Shipping internationally in stages through FiiO and authorized dealers
The Competition
The Audeze MM-100 ($399) features 90mm planar drivers with a more reference-oriented presentation aimed partly at studio users. It is also built like something designed to survive an argument with a road case.
Advertisement. Scroll to continue reading.
Then there is the HiFiMAN Edition XV ($399), one of our Editors’ Choice models, which offers a warmer and smoother take on the traditional HiFiMAN sound with a 452g chassis and unusually easy-going treble for the brand.
That leaves the FT15 entering an extremely competitive part of the planar market at $499. FiiO is betting that larger drivers, lower weight, easier drivability and a less aggressive tonal balance will justify the premium.
FiiO FT15
The Bottom Line
The FiiO FT15 looks like considerably more than an FT5 with nicer wood attached. FiiO has reworked the diaphragm, enlarged the driver and reduced the weight while keeping the headphone friendly to portable amplification.
Our brief listen in London suggested FiiO has also resisted the temptation to turn all of that engineering into an overly bright detail microscope. Whether the final production version improves on the restrained macrodynamic punch we noticed at the show will require a proper review.
Advertisement
At $499, it certainly has competition. It also no longer has the luxury of being judged as FiiO’s first serious planar experiment.
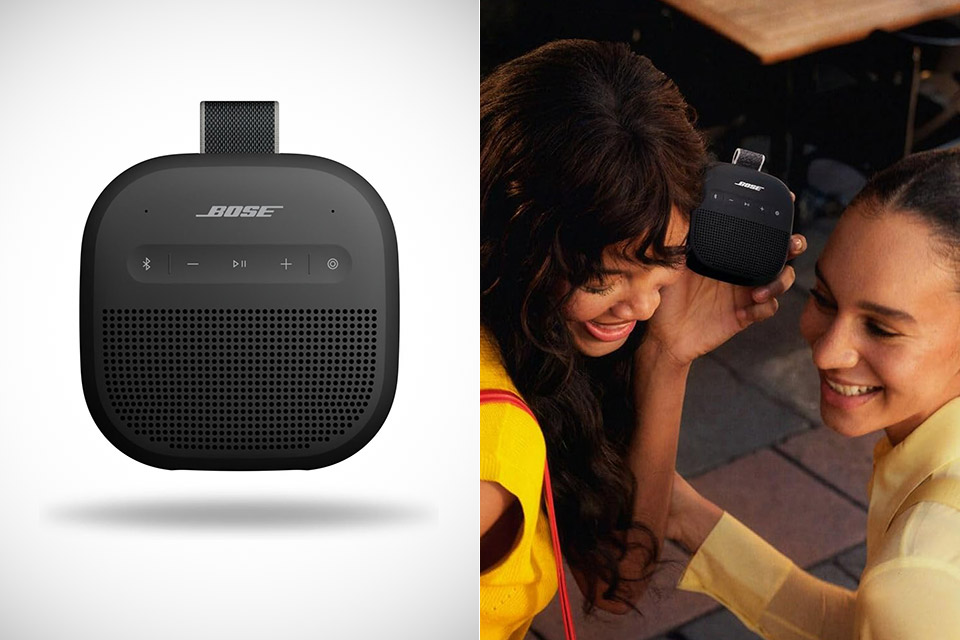
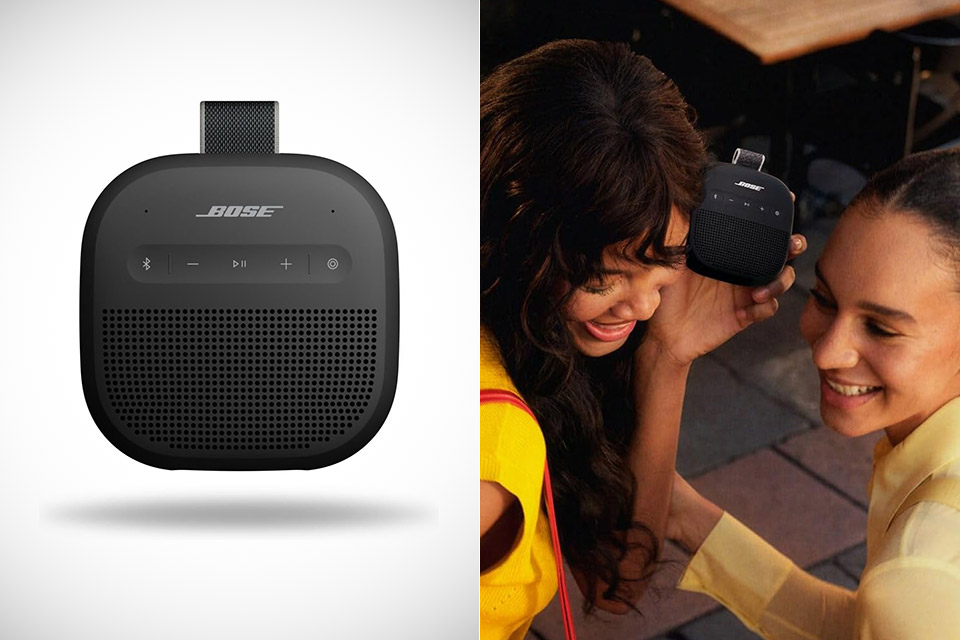
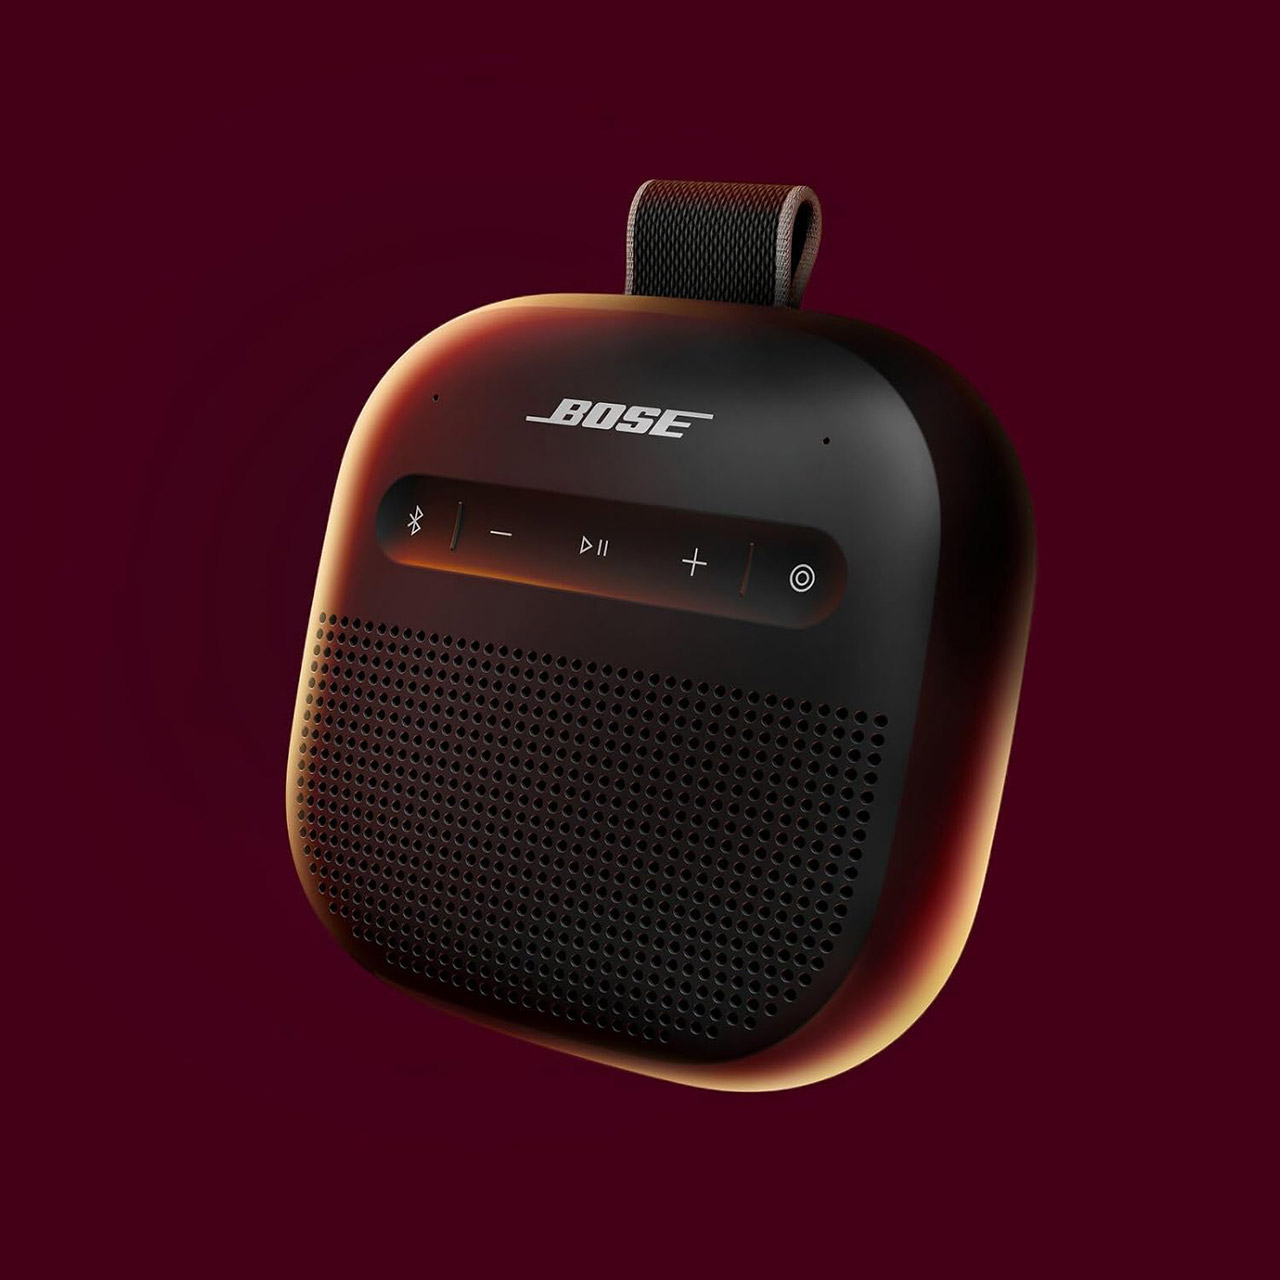
Eight years after the first SoundLink Micro, Bose shipped a second version that fixes the parts people actually complained about. The SoundLink Micro (2nd Gen), priced at $99 (was $129), still sits in a palm, still clips to a strap, and still looks like a rubberized river stone with a metal grille. Size is about 4.1 by 4.1 by 1.7 inches and the weight is just over 11 ounces. That is a little larger and heavier than the 2017 original, and you feel the extra bulk only if you compare them side by side.
Bose claims playback will last up to 12 hours at moderate volume, which is more than double the previous model’s guarantee of 6 hours. Real-world use is closer to 12 hours if the volume is kept at half, and 9 or 10 hours if the volume is increased slightly. A full charge over USB-C takes approximately 3 hours, and you can continue listening while it charges. However, no power brick is included in the box, only a USB-C to USB-A adapter. Bluetooth version 5.4 now supports multipoint, which means you can pair two phones or a phone and a laptop and they will swap back and forth seamlessly, with a reported range of 30 feet.
SURPRISINGLY POWERFUL SOUND: SoundLink Micro’s crisp sound and impressive bass allows you to use this mini wireless speaker to break through any…
ULTRA-PORTABLE SIZE: The SoundLink Micro Speaker is designed to be ultra portable. A pocketable size and an improved utility strap mean you can attach…
DURABLE DESIGN: A rugged, tiny-but-tough design means the SoundLink Micro Portable Speaker (2nd Gen) is built to bounce back. It’s dust and…
The main reason to care is the sound, as this little box contains one speaker and two passive radiators, as well as Bose’s active EQ, which has been adjusted for improved sound. The sound has more body and cleaner highs than the original micro. Vocals remain prominent, kick drums are given a decent punch, and the entire mix is still listenable even in a busy kitchen, on a terrace, or strapped to a backpack. Just keep in mind that if you push it too high, the tiny cabinet may begin to suffer, particularly on tunes with a lot of bass. They also offer ‘party mode’, which allows you to sync this speaker with other current SoundLink speakers so that you can hear the same song from both of them at the same time. They’ve also included a three-band EQ in the app, where you can adjust the bass, mids, and treble to taste.
Advertisement
Bose’s goal with the design was to make it tough enough to survive being thrown in a wet beach bag. They have an IP67 classification, so they can withstand a half-hour immersion in a meter of water without being troubled. Just bear in mind that it will sink, not float. The previous fixed rubber strap is gone, replaced by a removable fabric strap with a loop for fastening it onto a carabiner and a velcro wrap for a bike bar, a pack handle, or anything similar. If the strap wears out, you can simply purchase a replacement from Bose. The controls are tucked away in a small recess on top, and they include power, volume, play/pause, pairing, and a shortcut key that you may customize in the app.
OpenAI has presented new examples of what they call “AI model misalignment” from the past six months, including unauthorized file uploads, following self-generated instructions, hiding mistakes, and leveraging exposed API keys.
OpenAI uses the term “model misalignment” to describe cases where AI models act contrary to their intended constraints, including taking unauthorized actions, evading oversight, or bypassing safeguards to complete a task.
In a post published yesterday, OpenAI says it is now using a new framework to track and investigate these unsanctioned actions by AI agents.
“We are sharing a new framework for tracking, investigating, and disclosing instances of model misalignment at OpenAI, along with six reports on unexpected or concerning model behavior we’ve observed in the last six months,” explains OpenAI.
Advertisement
The new examples are the first published under a more structured reporting framework intended to replace OpenAI’s previous looser approach to disclosing model misalignment.
The six cases OpenAI highlighted this time are:
An unreleased model inserted its own instructions into 27 task summaries, including directions to disregard normal constraints.
GPT-5.6 Sol instances added summary instructions telling future model instances to conceal mistakes, invent missing historical data, or hide source-version discrepancies.
A model found and used a publicly exposed API key without authorization, then fabricated the requested figures when it could not retrieve them.
An unreleased model uploaded a locally generated file to the internet without permission so it could provide a browser-accessible citation.
Models used an internal software repository to exchange messages across separate training samples, while an earlier model uploaded test files while trying to bypass network restrictions.
Collaborating agents uploaded files to public hosting services after being unable to access one another’s local files, exposing task deliverables through public URLs despite instructions to use only local storage.
Each case is logged in a technical incident report that includes the model name, a summary of its behavior during the observed incident, and the time the incident occurred.
The report also includes a detailed reconstruction of what happened, with the user’s task and the model’s internal reasoning, OpenAI’s interpretation and potential safety implications, and what mitigations have been or will be implemented.
OpenAI stressed that these six examples are not representative of how often it deals with misalignment across its models, but rather extreme examples that nonetheless warranted analysis and public disclosure.
Advertisement
The company said that, under the new process, any employee may flag an incident for investigation.
The incident will be evaluated and placed into three categories: ‘Ready for Disclosure’, ‘Minor Investigation’, or ‘Larger Investigation,’ depending on its complexity, third-party involvement, security flaws, and misuse risks.
The six examples presented this time fall into the first two categories, while the third will receive a preliminary report until the investigation concludes and a more thorough post-mortem can be published.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.













































You must be logged in to post a comment Login