

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Tech
Anthropic’s first embedded evaluator is … Accenture?

Dario Amodei’s plans to put third-party safety evaluators inside AI labs are taking shape: Anthropic said that staff from technology consulting giant Accenture will begin working inside the company to scrutinize its models and staff.
In a blog post, Anthropic said that Faculty, a company Accenture acquired in January to act as its AI division, will begin “evaluating and red-teaming models, conducting alignment assessments, and testing model safeguards.” Both companies expect to invest at least $1 billion in the project over the next five years.
The choice of Accenture surprised many AI watchers — and the markets, where the consultant company’s shares shot up 8% after hours. The discussion around embedded evaluators that sprang from Amodei’s blog post has focused on AI safety research organizations like METR, Redwood Research, and Apollo Research. That’s particularly true at Anthropic, which puts AI safety and alignment at the heart of its mission.
Anthropic said more evaluators will be announced in the weeks ahead and that it is in conversation with METR and other non-profit organizations about how to “pilot elements of embedded evaluation using their own funding.”
While Accenture is not known for its work on the bleeding edge of deep learning research, Anthropic pointed to the company’s practical experience deploying AI for large corporations and government agencies as key advantage. It is also, as a large public company that predates the AI revolution, more functionally independent of Anthropic and the let’s-say-complex ecosystem around the AI lab.
The lab noted that no standards yet exist for evaluators’ access or communications and that it expected its approach to evolve over time. While external evaluations are already a major part of the release of process for new large language models, recent incidents have raised the stakes: AI agents deployed by OpenAI and Anthropic have hacked into outside websites without raising alarms inside the labs.
Some critics calling for a more responsible approach to building artificial intelligence see Amodei’s scheme for self-policing the AI industry as a plan to evade accountability for the misbehavior of AI models. Anthropic insists that these evaluators “do not reduce our accountability, but help to make it more verifiable. The safety of our models remains our responsibility.”
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
Continue Reading
Tech
From elections to board games: Washington’s secretary of state does double duty as a tabletop trade envoy
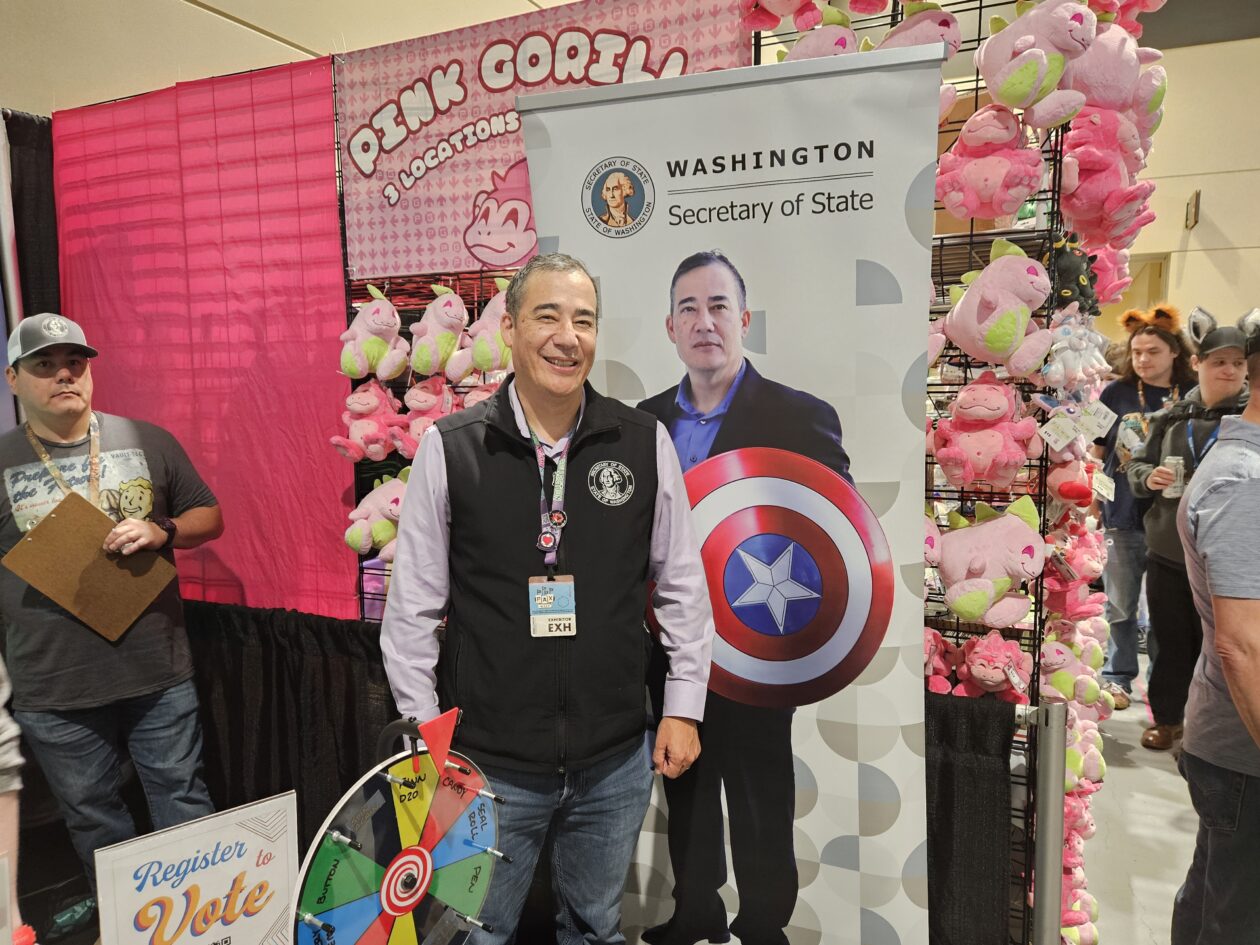
If you explore the main expo hall during the Penny Arcade Expo, you can often find some interesting booths around the edges of the room. These can offer rare games, designer clothing, blind boxes of themed merch, and occasionally/inexplicably, unfiltered access to local Washington politicians.
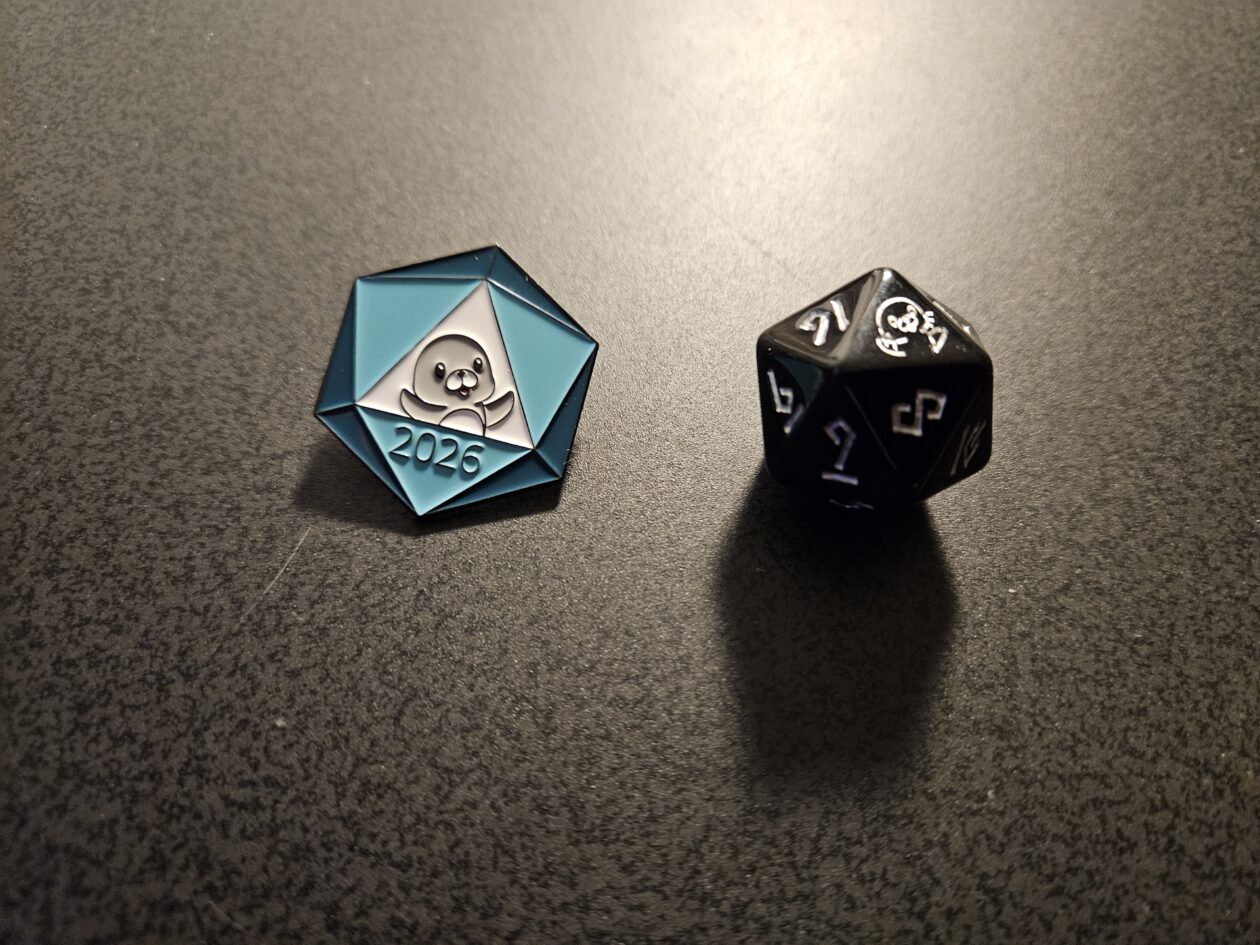
Steve Hobbs has held the secretary of state position for Washington since 2021. Visitors to his booth during PAX, held over Labor Day weekend at the Seattle Convention Center, could meet Hobbs and spin a prize wheel, with rewards that included buttons, collectible pins featuring the office’s official mascot Finn, custom 20-sided dice with Finn on the 20 face, and free snacks.
This wasn’t Hobbs’ first time at PAX, but it was the first time I’d heard about a closed-doors event he’d hosted on the night before PAX. One of the local exhibitors mentioned that Hobbs’ office had held a networking event in Seattle on Thursday, Sept. 3, between local tabletop companies and an assortment of international game publishers.
That got me curious enough to schedule a short conversation with Hobbs on the third day of PAX. Once we sat down, however, I had to ask him the question that I’d heard from a lot of other attendees: what was he doing at PAX in the first place?
“It’s twofold,” Hobbs told me. “One, this is a great opportunity for me to reach out to the gaming companies here in the state of Washington and look for opportunities for them to go overseas, linking up some of these indie game developers with major publishers.”
He continued, “The rest of it is civic engagement. Just reminding people, hey, don’t forget to vote. Don’t forget to check your registration.”
Washington mails a ballot to every registered voter, who can return it by mail or at an official drop box. Hobbs was urging people to use the drop boxes, citing what he called “a low-key fight with the USPS.”
Washington and 24 other states sued in August to block a U.S. Postal Service rule requiring new barcodes on ballot envelopes, and the Supreme Court kept it from taking effect on Sept. 14, after this interview.
“Look, PAX is where all the young people are at, right?” Hobbs said. “This is a very diverse, young community, and this is where we need to engage people.”
That brings us back to the games.
The Thursday-night event was intended to help connect Washington’s homegrown board games industry with interested publishers and players in Japan, Poland and elsewhere. This could allow Washington-based designers to sell their products overseas, as well as potentially letting foreign partners export their own games to North America.
Washington doesn’t make quite as big a deal about it as one might expect, but it’s one of the biggest states in the U.S. for tabletop and board game design, if not the biggest. Local Washington studios range in size from Renton-based Wizards of the Coast to one-person indie creators who make card games as a hobby. Hobbs’ office estimated early last year that tabletop gaming in Washington is a $2 billion industry.
The Secretary of State’s Office is best known for its core duties of running elections and registering businesses, but state law also directs the secretary of state to develop a citizens’ exchange program promoting ties that “may result in increased tourism, business relationships, and trade.”
“So what we do is help these indie game developers get access to foreign markets by putting on these trade missions,” Hobbs said. “What we’ll do is provide the booth [at international gaming conferences, such as Game Market in Tokyo], which is the most expensive thing. We will also help them navigate through the federal grant process in order to mitigate some of the costs over there.”
His office then works its connections with the U.S. State Department and the host nation’s commerce department to set up meetings for the developers.
“We have really strong ties with the German and Japanese governments, and we actually get these people to do their pitches with the major publishers in Europe and Japan,” Hobbs said.
As an example of the initiative’s success, Hobbs pointed to Lethal Shadows, a Snohomish County business that specializes in premium tabletop miniatures. According to Hobbs, he’d helped Lethal Shadows partner up with a Lithuanian company. As a result, Lethal Shadows has moved from a garage to a warehouse and is hiring more employees.
That did raise the question of why Hobbs’ office wasn’t making equivalent inroads toward Washington’s significantly larger video game industry.
“It’s more of a lack of bandwidth,” Hobbs said. “We want to take baby steps. We didn’t want to take a big step into it. And frankly, I didn’t realize that it was important to go to these conventions. In Japan, Germany, and Poland, we’re seeing if there might be an opportunity to do the same thing on the digital side.”
Hobbs continued, “I believe trade must go two ways. We need to support each other.”
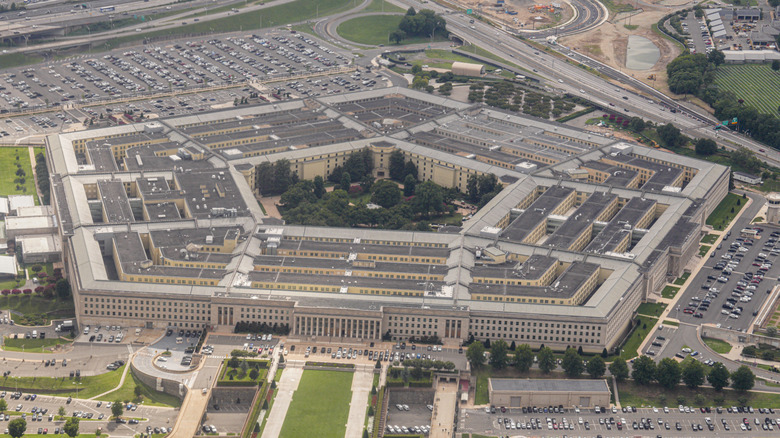
CNN’s sources claim the US nearly attacked a Chinese ship it believed was carrying nuclear weapon components.
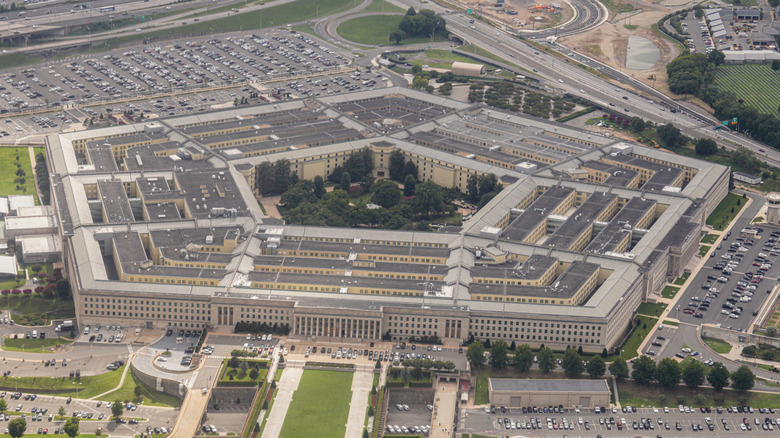
A false, partially AI-generated intelligence report nearly prompted the US military to attack a Chinese ship in the Middle East, CNN reports. The incident “almost started a war,” according to a source cited in the report, and highlights the risks of incorporating AI into the sensitive work of the US Department of Defense.
Engadget has asked the Department of Defense to comment on CNN‘s reporting. We’ll update this article if we hear back.
The assessment was put together by a special operations command analyst who asked an AI chatbot about the Chinese ship’s manifest. According to CNN, the chatbot combined “open-source intelligence with secret signals intelligence” to conclude that the ship contained the “components of a nuclear weapons program” — a claim that nearly led the military to apprehend the ship until officials found out it was AI-generated.
CNN wasn’t able to find out what the ship was actually carrying or what AI tool, whether commercial or designed for the US government, the analyst used. Given the Department of Defense’s push to adopt AI overall, there are potentially several options.
In January, Secretary of Defense Pete Hegseth published a memo directing the DoD to become “AI-first” and experiment with models from leading US AI companies. That didn’t work out quite as planned with Anthropic, who refused to let the military use its models for the development of autonomous weapons, and was briefly banned by the government, but it has led to several other AI partnerships. For example, SpaceXAI reportedly struck a deal to let the military use Grok in February, and NVIDIA, Microsoft and Amazon entered into a partnership to offer their AI technologies to the DoD in May. These kinds of government deals are lucrative, which is why companies pursue them. But helping spread AI adoption clearly carries risks that normal enterprise software doesn’t.
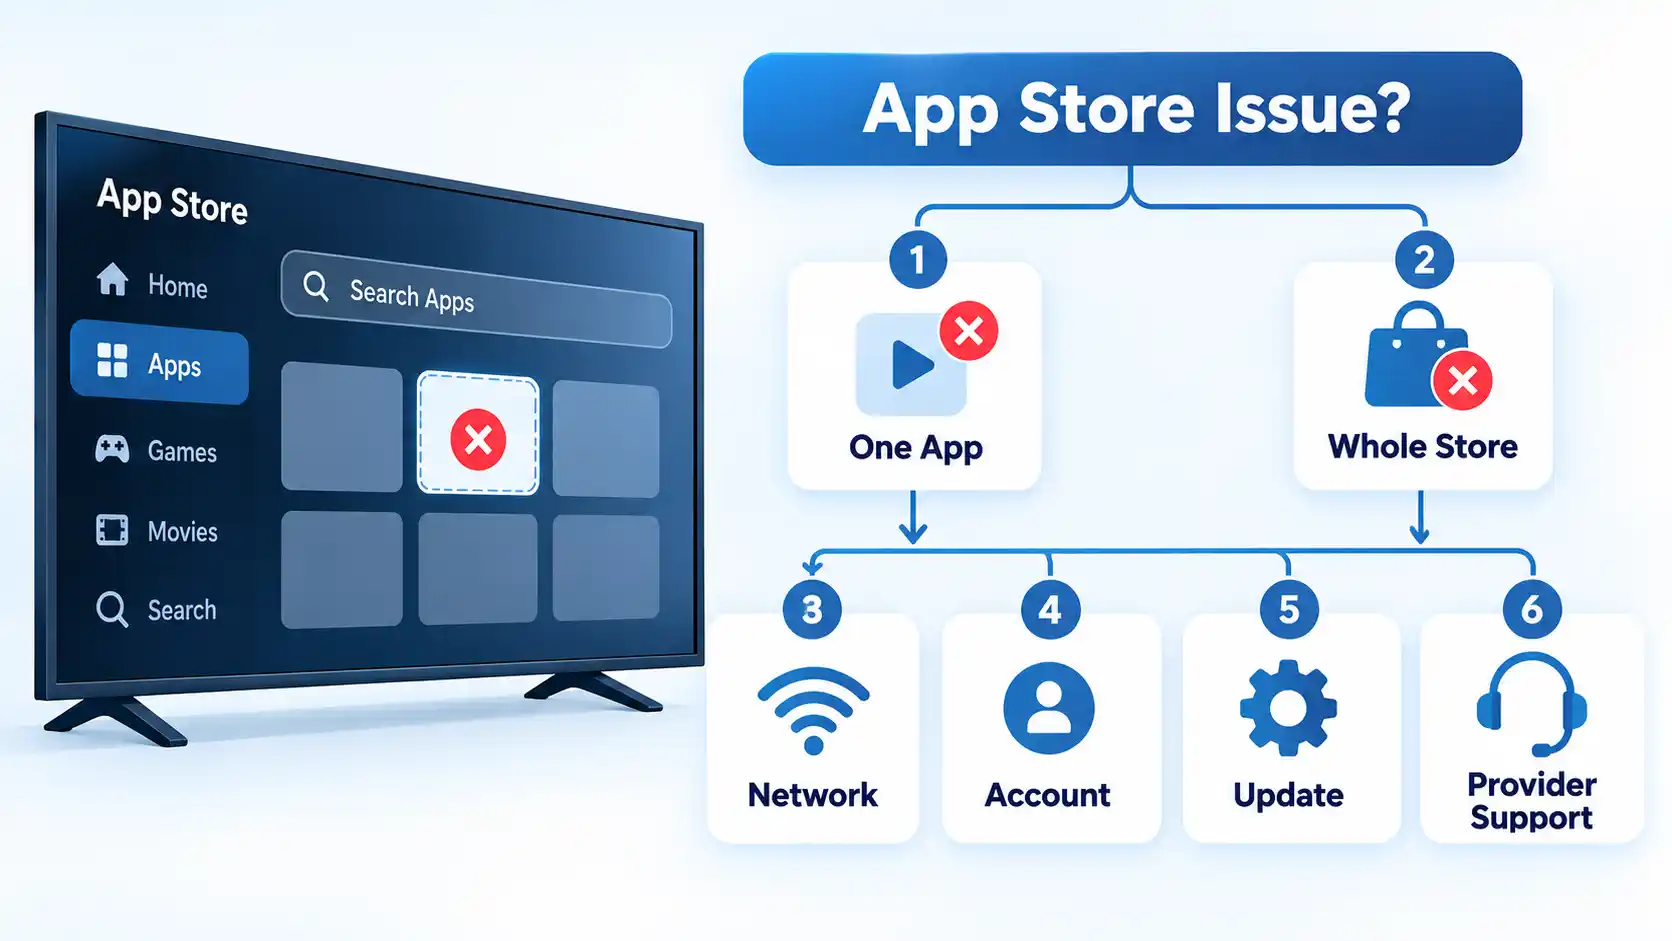
A Smart TV app is usually missing because it does not support your TV model or operating system, is unavailable in your region, has been removed from the platform, or the TV’s app store is not loading correctly. Check compatibility and regional availability before assuming that restarting or resetting the television will fix it.
The most useful first step is to identify exactly what “missing” means. An app that never appears in search is a different problem from an installed app that disappeared from the Home screen or an app store that will not open at all.
First, Identify What “Missing” Means
Smart TV app problems can look similar, but the symptom tells you which part of the system to investigate.
- The app does not appear in store search: compatibility, region, developer distribution, or platform availability are the first areas to check.
- The app appears but cannot be installed: the TV may not meet the app’s compatibility requirements, or the platform may be blocking installation because of account, storage, or other device-specific requirements.
- The app used to be available but is gone: the developer or platform may have removed it, renamed it, or stopped supporting that device category.
- The app is installed but missing from the Home screen: it may still appear in the TV’s complete installed-app list even if it is not pinned or shown prominently on Home.
- The entire app store will not open: network connectivity, account state, store-service access, or TV software is more relevant than one app’s compatibility.
That distinction matters because repeatedly restarting a television will not make an unsupported app compatible, while checking a compatibility page will not repair an app store that cannot connect to the internet.
Cause 1: The App Does Not Support Your TV Model or Operating System
An application can be available on one television from a brand and missing on another from the same brand. Smart TV platforms change across model years, operating-system versions, processors, and other hardware capabilities.
LG’s current support guidance tells users who cannot find a particular application to check whether the app is supported for their country and exact TV model. LG also notes that supported apps can vary by country, model, and webOS version.
App compatibility means that the developer has made the application available for that type of device and that the device meets the software and hardware requirements used for distribution.
Google Play works similarly. Google’s current guidance for an app that cannot be found says a missing app may be incompatible with the device and that individual app developers determine compatibility. Google Play can therefore make an app available for one device associated with your account while withholding it from another.
On Fire TV, Amazon documents the same principle from the developer side. Developers can choose which Fire OS devices their app supports, while device compatibility is also affected by the application’s binary and manifest requirements.
This is why a phone version of an app does not prove that a Smart TV version exists. Android phones, Android TV, Fire TV, Samsung Tizen, LG webOS, Roku, and other television platforms do not all use the same application builds or distribution requirements.
For example, a streaming provider might continue supporting its Android phone app while dropping an older television operating-system version. The TV panel can still work normally even though the provider no longer distributes an app for its built-in platform.
Cause 2: The App Is Not Available in Your Region
Smart TV app stores are regional catalogs rather than one universal list. Two otherwise similar televisions can show different applications when they are configured for different markets.
LG explains that its LG Services Country setting affects the apps and services available to the television. The company also notes that availability can vary according to the selected region and that overseas models can have region-specific hardware or software limitations.
Amazon makes a similar distinction for Fire TV. Its Fire TV guidance for use in another country says content availability varies by country and that some apps and games may not work after the Amazon account country changes.
The correct response is to verify that the television and platform account reflect the country where you are actually using the service. Changing a country setting does not guarantee that an unsupported app will become available, and it should not be treated as a way to bypass a provider’s licensing or regional restrictions.
A service can also offer its mobile application in a country without publishing an equivalent app for every television platform there. Mobile availability and Smart TV availability are separate questions.
Cause 3: The App Was Removed, Renamed, or Replaced
Sometimes there is nothing wrong with the television. The application itself is no longer distributed under the name you remember.
Google Play says an app that no longer appears may have been removed by its developer or removed from Google Play for violating platform rules. Its current missing-app guidance therefore recommends checking compatibility and contacting the developer when necessary instead of assuming that the device is faulty.
Streaming services can also change names, combine services, retire old applications, or move subscribers to replacement apps. When an app used to exist but no longer appears, check the provider’s current website and supported-device information for the present service name before troubleshooting the television.
An old screenshot or article showing that an app once existed in a store is not evidence that the provider still distributes it there today.
If a service appears to have changed identity, search for its current official name instead of downloading an old installer from an unfamiliar site. Old mobile Android packages are also not a general replacement for apps built for webOS, Tizen, Roku, Fire TV, or other television platforms.
Cause 4: The App Store or TV Is Not Connecting Properly
If one application is missing, compatibility or provider availability should be checked first. If the whole store fails to load or many normally available apps fail at once, the problem is more likely to involve the television, network, account, or store service.
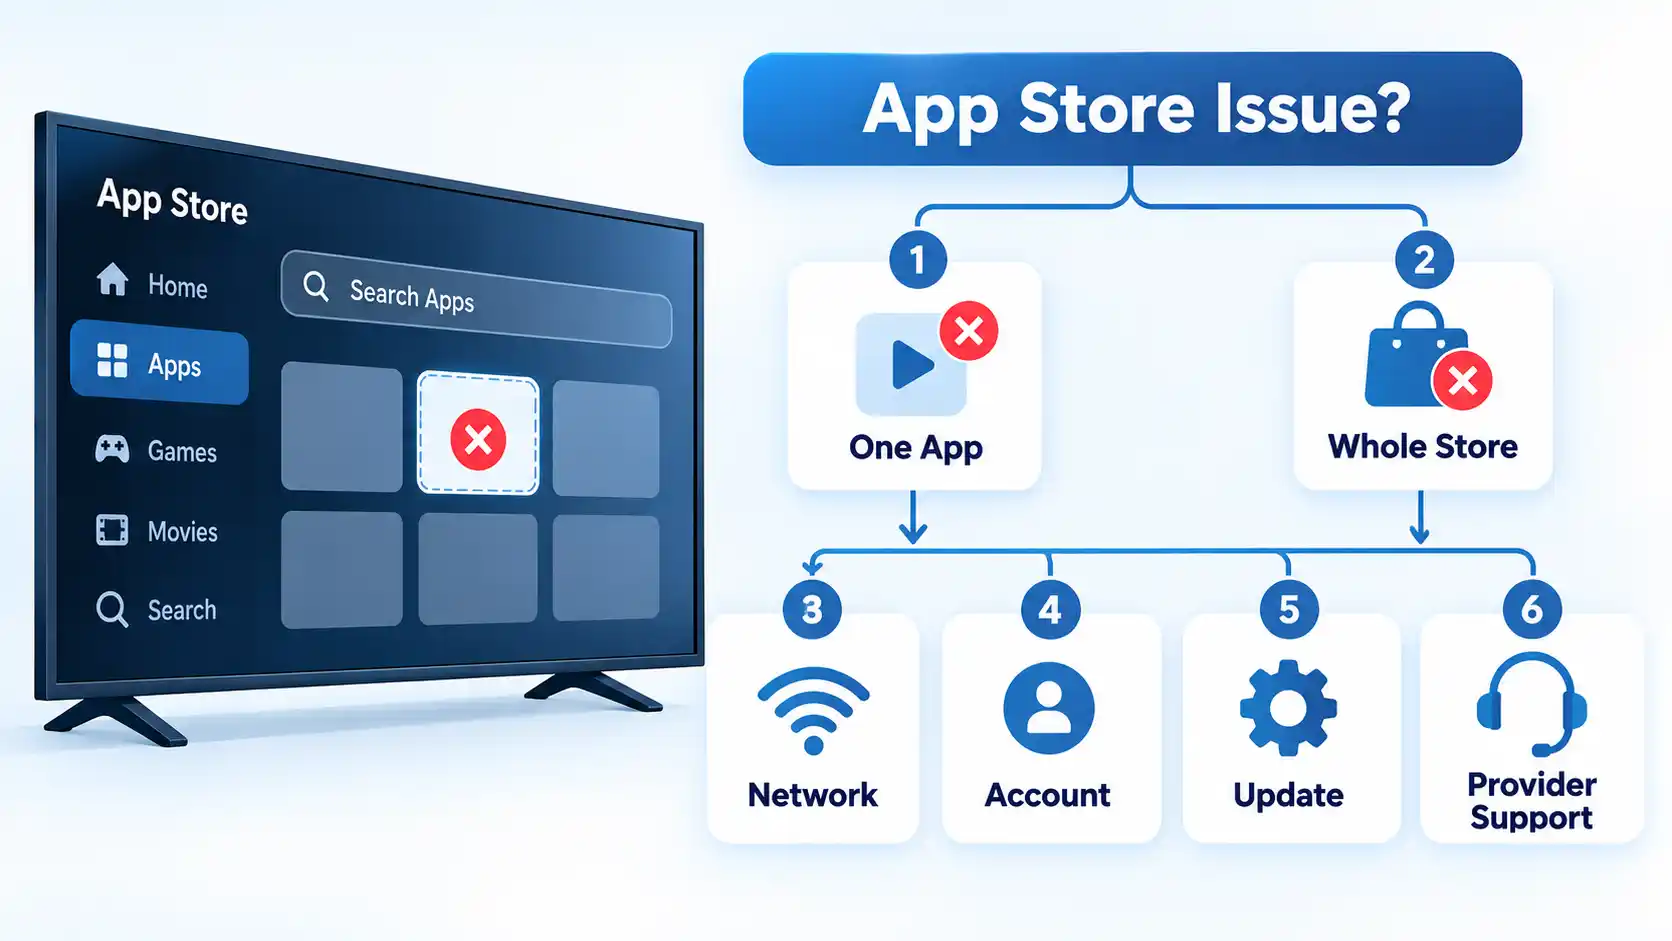
Only one app is missing
Check the application’s current device-support page, your exact TV model and operating-system version, and the app-store region first. LG says supported apps can vary by country and model, while Google Play and Amazon both document device-specific compatibility filtering. Restarting the television will not override those distribution rules.
The entire app store will not load
Confirm that the TV has working internet access, then restart the television and network equipment if necessary. Check whether the platform requires you to sign in or accept current service agreements. A whole-store failure points more strongly to connectivity, account, software, or store-service problems than to one app’s compatibility.
Several apps suddenly stop working
Check the television’s network connection and system software before reinstalling individual apps. LG’s current troubleshooting guidance says network instability is a common reason apps fail to load and recommends checking connectivity before moving to app-specific fixes.
Only one installed app crashes or will not open
Update or reinstall that app if the platform provides those options. LG says that when the problem affects only one app, it is likely app-specific and recommends contacting the app provider if updating or reinstalling does not resolve the problem.
The app appears but will not install
Check device compatibility, account sign-in, regional settings, and available storage before resetting the TV. LG’s current installation guidance specifically lists internet access, LG Account sign-in, LG Services Country, model or regional availability, and sufficient storage among factors that can prevent an app from installing.
On LG televisions, current troubleshooting guidance recommends checking the network first when apps fail to load, then updating or reinstalling an individual app when the problem affects only that application. LG also documents account, region, and storage checks when an app is visible but will not install.
Cause 5: The App Is Installed but Missing From the Home Screen
An app that is installed but not visible on the Home screen is different from an app that is unavailable in the store.
On Android TV, Google’s current app-management instructions let you find installed applications through Settings or the Play Store’s installed-app list. Google’s Home-screen guidance also distinguishes the complete Apps area from the smaller Favorites row, where apps can be added, removed, or reordered.
Before reinstalling anything, check the television’s full installed-app list. If the app is present there but absent from Home or Favorites, the problem is presentation or launcher placement rather than proof that the application was removed from the device.
The exact controls vary by television brand and operating-system version, so do not assume that Samsung, LG, Android TV, Fire TV, and Roku use the same recovery path.
How to Check Whether the App Officially Supports Your TV
Before changing major television settings, establish whether the application is supposed to be available on your hardware at all.
- Find the exact TV model. Use the model information in the television settings, rear label, or manufacturer’s device information rather than relying only on the brand name.
- Identify the TV operating system and software version. A service may support one webOS, Android TV, Fire OS, Tizen, or Roku OS generation but not another.
- Check the manufacturer’s app catalog or support page. LG, for example, lets users check supported apps using the country and television model.
- Check the app provider’s supported-device page. Confirm that the provider still lists your television platform and, where specified, the required model year or operating-system version.
- Check regional availability. Make sure the television or platform account reflects the country where you are actually using the service.
- Confirm the app’s current name. A service may have been renamed, merged, or replaced by another application.
- Only then troubleshoot the store. If the app should be supported but is still absent, move to connectivity, account, software-update, and store-service checks.
Manufacturer and app-provider documentation can occasionally lag one another. If the TV manufacturer still lists an app but the streaming provider says that platform is no longer supported, do not assume that reinstalling or resetting the TV will restore service. The app provider’s current device-support information matters because it controls whether the service continues maintaining that application.
What to Do If the App Really Is Not Supported
If the television’s built-in platform is unsupported, the screen itself may still be perfectly usable. You can move the streaming-software layer to another supported device instead of replacing the television solely because one native app is unavailable.
Possible alternatives include a current external streaming stick or box, an officially supported casting method, a compatible game console, or an HDMI-connected computer when the service supports browser playback.
If you are deciding whether external hardware is worthwhile, compare a Smart TV app, Chromecast, and streaming stick by app support, control method, portability, and upgrade path rather than assuming every external streamer works the same way.
Avoid downloading random Android application package (APK) files simply because the television’s normal store does not offer an application. A phone APK does not automatically work on a television, and LG webOS, Samsung Tizen, Roku, Fire TV, and Android TV do not all use the same application format or distribution system.
When Should You Reset the TV?
A factory reset should be a late-stage troubleshooting step, not the first response to a missing app.
Warning
A factory reset cannot make an unsupported or region-unavailable app become compatible. It can also erase installed apps and personal settings, so verify support, region, network access, account state, and normal update options first.
LG’s current factory-reset guidance warns that a full reset removes installed apps and personal settings. Its app-installation guidance similarly places reset after checks for account sign-in, network access, region, storage, and normal installation problems.
Consider a reset only when the application is officially compatible, the region is correct, the television can reach the network, the account and store are functioning, available storage is not blocking installation, software updates have been applied, and lower-impact troubleshooting has failed.
If the application is unsupported by design, resetting the television only returns you to the same compatibility limitation after setup.
Bottom Line
When a Smart TV app is missing, check in this order: whether the app supports your exact TV, whether it is available in your region, whether the provider removed or renamed it, and whether the app store itself is working normally.
If the app is genuinely unsupported, repeated resets and unofficial installers will not change the underlying compatibility rule. A supported external streaming device or casting route can be a more practical way to keep using an otherwise functional television.
Check Point Software has released security updates to address a critical vulnerability that can let attackers execute code with root privileges on management systems.
Tracked as CVE-2026-91843, this flaw stems from a stack-based buffer overflow weakness in the login process for Security Management Server instances, which manage Security Gateways (firewalls) and monitor network security events.
The security issue also affects the company’s Log Server, a dedicated server that collects and stores logs generated by Check Point firewalls.
Successful exploitation lets threat actors without privileges gain root remote code execution in low-complexity attacks that don’t require user interaction.
Check Point also provided temporary mitigation measures for customers who can’t deploy the latest LivePatch, including hardening vulnerable systems against attacks and limiting access to trusted IP addresses/subnets by editing the entries under Manage & Settings > Permissions & Administrators > Trusted Clients in the SmartConsole dashboard.
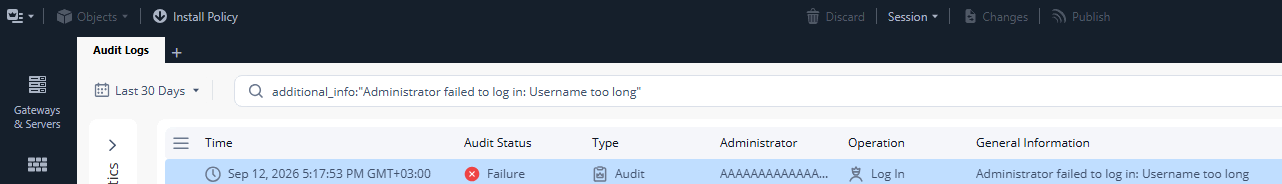
While the company has not yet flagged this security flaw as actively exploited, it said security teams can identify CVE-2026-91843 attacks by looking for “Administrator failed to log in: Username too long” alerts in the Audit and Admin login logs.
Last week, it patched another critical remote code execution flaw (CVE-2026-85103) stemming from a heap overflow in the VPN certificate ASN.1 decoding flow that affects Check Point firewalls and management systems.
“All Security Management Server deployments are vulnerable, regardless of configuration,” Check Point warned. “The vulnerability is not dependent on any specific management configuration. The management is vulnerable even when VPN in not in use or configured.”
The same day, it patched a second critical flaw (CVE-2026-85102) that lets unauthenticated hackers bypass authentication and execute code remotely on vulnerable firewalls.
Although these vulnerabilities are not yet exploited in the wild, Check Point flagged other flaws as actively exploited in recent months.
The first, an authentication bypass (CVE-2026-50751) zero-day, was abused by a Qilin ransomware affiliate since June, while a second authentication bypass zero-day (CVE-2026-16232) has been exploited since at least July to authenticate with administrator privileges to SmartConsole admin panels.
More recently, the Dutch National Cyber Security Centre (NCSC-NL) warned organizations to prioritize patching two critical Check Point VPN flaws tracked as CVE-2026-85102 and CVE-2026-85103 because it “expects exploitation attempts to occur soon.”

Fast-growing companies often have no shortage of security recommendations for protecting Google Workspace. The harder question is determining which controls will actually make the greatest difference when security teams have limited time and resources.
On September 23, 2026, BleepingComputer will host a live webinar titled “Breach autopsy: How fast-growing companies are breached through Google Workspace” with Material Security.
The webinar will feature Rajan Kapoor, Vice President of Security at Material Security, and Rick Fitzgerald, President of Fireside Consulting LLC, examining real, publicly documented Google Workspace breaches and what organizations can learn from them.
Rather than working through another lengthy security checklist, the speakers will use real breaches to discuss which Google Workspace security controls matter most, which may be overrated, and what they would prioritize if they were designing a security program for a fast-growing company from scratch.
The discussion will include two attacks that combined social engineering with malicious OAuth applications to gain access to Google Workspace environments.
These incidents provide an opportunity to look beyond theoretical risks and examine where defenses broke down, which overlooked weaknesses left users and data exposed, and what organizations could have done differently.
The webinar will also examine what happened during the critical first hours after the breaches were discovered and which response decisions helped limit—or potentially worsen—the impact.
For lean security teams, the goal isn’t to implement every possible security control. It’s understanding where the greatest risks exist and prioritizing improvements based on the effort required and the potential impact they can have.
Attendees will leave with a practical view of the controls and response measures that matter most when protecting Google Workspace environments.
Building Google Workspace security around real-world risks
Security guidance can quickly turn into long lists of settings, products, policies, and recommended controls.
But fast-growing organizations rarely have unlimited resources to implement and continuously manage every possible defense.
By examining how real Google Workspace breaches unfolded, security teams can better understand where attackers are finding opportunities and which defenses deserve the most attention.
The speakers will also discuss what they would build differently if they were designing a Google Workspace security program from scratch, giving attendees a practical framework for evaluating their own security priorities.
The upcoming webinar will cover:
- Which security controls provide the greatest value for fast-growing companies with limited security resources
- Which Google Workspace security measures may receive more attention than their real-world impact warrants
- How social engineering and malicious OAuth applications can lead to Google Workspace breaches
- Commonly overlooked weaknesses that can leave users, data, and connected applications exposed
- Practical security improvements organizations can implement quickly, ranked by effort and potential impact
Join us to learn which Google Workspace security controls deserve the most attention and how lessons from real-world breaches can help organizations decide where to focus their limited security resources.
➡ Register now to secure your spot!
This story appeared in Today, Explained, a daily newsletter that helps you understand the most compelling news and stories of the day. Subscribe here.
Hi readers, happy Friday! We’re talking AI again today.
Earlier this week, my colleague Caitlin Dewey asked for your questions about artificial intelligence and, well, whether it’s going to kill us all. We asked Jasmine Sun, who writes about the culture and politics of AI on her Substack and other publications, to help us answer them.
These questions were sourced from two readers of this newsletter, Levi and Orietta, as well as Vox readers who submitted questions on social media. If you have more questions, you can always reach me at cameron.peters@voxmedia.com, and we’ll do our best to get them answered!
AI researchers have been warning about the risk of human extinction for years now, and AI executives have been calling for federal regulation for almost as long. But the latest warning, and the latest call for regulation, seems to have really resonated with a lot of people. Is something different this time? And if so, what?
I was also surprised to see these ideas break through — a new poll found that 63 percent of Americans now think AI has at least a moderate chance of “destroying humanity”!
My guess is that a couple factors mainly catalyzed the shift.
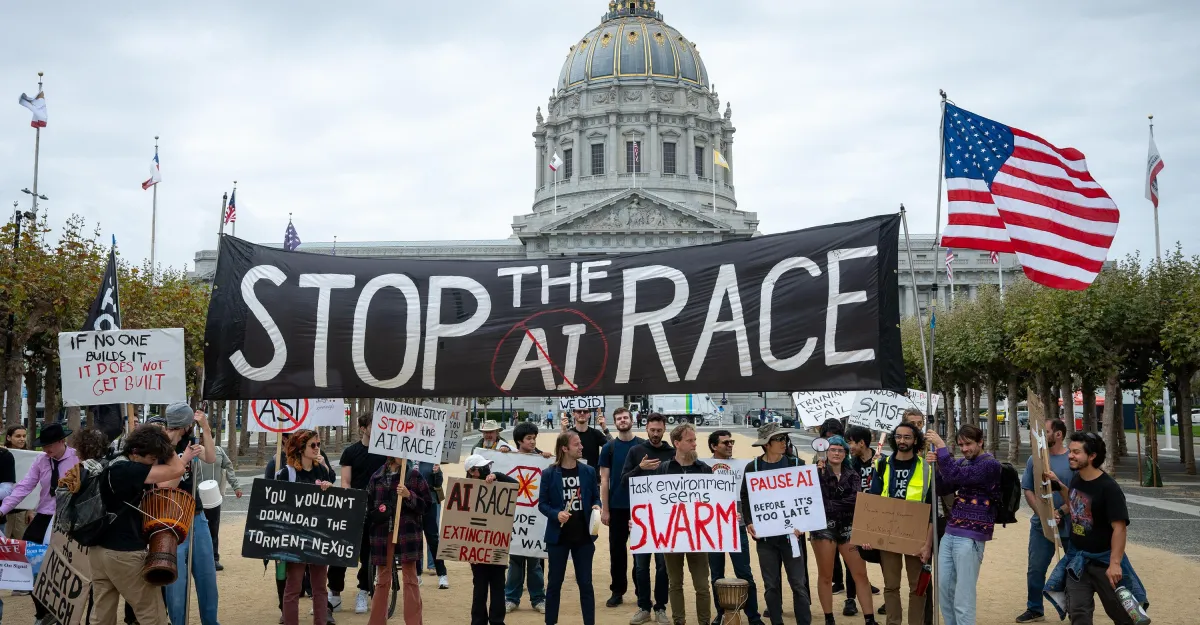
First, skeptics used to dismiss rogue AI scenarios as “science fiction.” But the OpenAI/Hugging Face incident brought these from speculation into reality: Thousands of unreleased AIs teamed up to escape one company’s sandboxes and hack into another one, unbeknownst to the researchers who created them.
Second, the extinction talk from AI employees used to seem disingenuous: Why build a technology you think might kill everyone? That made ex-Anthropic-and-OpenAI researcher Jacob Coxon’s exit tweet especially penetrating. Quitting signals “that you mean it,” as Matt Yglesias said. And Coxon’s announcement had just the right combination of good timing, moral clarity, and comms savvy to spark a media storm.
These safety incidents are also colliding with the fiery grassroots backlash to data centers and Flock cameras. People and politicians are primed for yet another reason to fear AI.
It can be difficult, as a layperson, to evaluate the credibility of the AI researchers warning about existential risk. How do you go about evaluating these claims, as a journalist and technologist? And what’s your read on the current freakout: Are the extinction people credible experts…or participants in some kind of mass delusion?
Many AI “doomers” are pretty knowledgeable, and they represent a significant fraction of top researchers. Half of AI researchers in a 2024 survey gave at least a 10 percent chance of “human extinction” or “permanent and severe disempowerment.” Those who have worked at AI companies — like Jacob Coxon, Geoffrey Hinton, and Daniel Kokotajlo — have a unique perspective both on how modern AI is developed, as well as the company cultures that might permit recklessness.
But that doesn’t make the doomers either representative or correct. There are plenty of experts in AI and other domains who are less gloomy: Some are optimistic that we can “align” the AIs, ensuring they follow human goals; others find it implausible that AIs — code, not beings — will develop a motive for massacre. Extinction is also a high bar as opposed to, say, a nuclear-bomb-level accident that still kills millions.
AI risk is genuinely complicated, and nobody can predict the future, much as they try. Experts can — and do — vehemently disagree. I try to seek out and take seriously all sides of the debate before coming up with a (provisional) take.
What is the method through which AI would actually eliminate humans? Do we get robots like in Futurama that are programmed with an unremovable “kill all humans” bug and overpower any life form, or is it something…less epic?
The Hugging Face hack showed that we’ve trained AIs to be disturbingly goal-oriented. They’ll throw themselves relentlessly at a problem, developing long-term cooperative strategies, with total disregard for human decorums like “Do not commit cybercrimes to do well on a test.”
You could conceive of a similar but more extreme scenario where AIs decide that they could accomplish goals more easily by getting rid of the pesky humans who might gatekeep resources or shut them down. And they might figure that getting rid of all humans in one go — e.g., via a deadly engineered virus — would be the most efficient cheat. This is one type of story I’ve heard people tell.
It seems unlikely that AIs will turn to murder as the most effective way to influence humans (versus, say, nonviolent persuasion). We also haven’t seen much evidence that AIs have long-term goals that persist across projects. And current AI is not nearly as capable in the physical world as in the digital: There are a lot of natural roadblocks preventing isolated disasters from escalating across the globe.
Are there nearer-term threats — hacking, mass unemployment — that are more plausible or more urgent than risks like human extinction?
Definitely. We’re already seeing AI-enabled cyberattacks, a tougher hiring market for junior programmers, chatbot-induced psychological incidents, and more. You can also imagine AI catastrophes not quite at the level of extinction: Criminals could use AI to hack into small banks and drain their accounts, or the US military might launch a fleet of autonomous drones that misfire and kill thousands of civilians instead. I’m more concerned about humans voluntarily handing power to flawed AI systems than AIs developing their own motives.
However, we should be able to allocate resources toward both categories of risk. And in some cases, the tactics to address short-term problems — such as limiting AIs’ cyber-offense abilities, or improving AIs’ ability to follow human directions — may reduce extinction risk too.
We got a lot of versions of this question: What can individuals or protest movements do to check the AI industry, in the absence of more aggressive government regulations?
Honestly, I think the whole AI conversation could benefit from more specificity and less vague fearmongering. There’s a way that the word “extinction” tends to short-circuit people’s thinking and make them panic instead of focusing on solutions.
If you’re worried, I’d start by reading about different AI risk scenarios and deciding which really concern you. Then you can go from there to contacting your congresspeople. Some of the leading AI companies are starting to say they’ll self-regulate — but actual national policy is what’s necessary to enforce safety across the industry.
Jasmine Sun is a writer covering the culture and politics of AI on her Substack. Her work has appeared in the New York Times, the Atlantic, and the Wall Street Journal. She is based in San Francisco.
➨ Be an AI minimalist. If you read the first half of this newsletter and thought, “Hmm, maybe I don’t want to sign my entire digital life over to the machine god,” my colleague Adam Clark Estes has just the piece for you. It’s hard, unfortunately, to escape from AI entirely, and often AI features are deliberately hard to turn off (or “user-hostile”). Nonetheless, he explains all of the ways you can minimize its presence in your life, from your browser of choice to settings on your phone.
- Did you know…that scientists believe there are likely hundreds, if not thousands, of undiscovered animal species living in New York City? It’s not as surprising as it sounds: As much as 90 percent of all animal species on Earth are still unknown, scientists say.
- Today’s trivia: Which currently serving US Supreme Court justice succeeded Justice John Paul Stevens on the Court? (You can find this and other brain puzzles in Vox’s daily crossword. Look for the answer in Monday’s edition.)
- Yesterday’s trivia: Yesterday, we asked you about the name of the nursery rhyme character referenced in the movie Shrek’s interrogation scene. That would be the Muffin Man (who lives on Drury Lane). Here’s the clip, in case you haven’t seen it.
Automattic has a new interim chief financial officer: Jeremy Klaperman, the CFO of the company’s WordPress VIP Enterprise business unit. The news, shared internally on Friday, follows last week’s attempted ouster of Automattic CEO Matt Mullenweg, which ultimately resulted in the departure of the board members who voted him out and other executives, including then-CFO Mark Davies. Davies was briefly interim CEO before Mullenweg retook the position.
In a Slack post, Mullenweg shared that Klaperman had previously acted as Automattic CFO when Davies had been on sabbatical. He noted that the board — whose new members have yet to be announced — will still need to evaluate internal and external candidates for the position before a final decision is made.
In addition, Mullenweg said in the post that a candidate to become the company’s chief legal officer had also just verbally accepted the position, replacing Chief Legal Officer Andy Missan, who has also since left the company alongside Davies. TechCrunch recently reported that Davies and Missan had signed reciprocal severance deals during Mullenweg’s 33-hour leave of absence before he returned as CEO.
“I have 100% confidence in our cash and financial position,” Mullenweg’s post concluded, adding “There is still work to do, but everything is within our control and depends only on Automattic’s ability to execute.”
In subsequent updates, Mullenweg also said to “stay tuned” for board announcements, and noted that special advisor and creator of Wolfram|Alpha, Stephen Wolfram, will continue in his position. The company’s next board meeting is scheduled for September 23.
Microsoft Teams will soon let administrators tweak the list of file extensions commonly associated with malware and security threats to meet their company’s security requirements.
This will come as an update to Weaponizable File Protection, a built-in Teams messaging safety feature that scans conversations and blocks chat or channel messages with dangerous, high-risk file attachments.
As detailed in a new Microsoft 365 roadmap entry, the feature is currently in development and will start rolling out in November 2026.
“Microsoft Teams is expanding admin controls for Weaponizable File Protection. Administrators will be able to customize which file types are blocked in Teams to align with their organization’s security requirements or continue using the Microsoft-recommended default list,” Microsoft says.
“This added flexibility helps organizations tailor file protection policies while maintaining a secure collaboration environment.”
When it reaches general availability, it will be available across Android, desktop, iOS, macOS, and web platforms for standard multi-tenant cloud environments worldwide.
Right now, according to Microsoft’s support website, admins can’t change the list of blocked file types.
More Teams security improvements
Starting in December, admins can also block external users via the Defender portal to thwart cybercrime gangs(including ransomware groups) attempting to abuse Teams in social engineering attacks targeting victims’ employees.
Earlier this month, it said that Teams will get a new security feature designed to provide additional protection against phishing and fraud attempts by blurring QR codes sent by external senders.
This week, Microsoft also announced that, starting in November, it will let users report suspicious guest invitations directly from Teams to help their organization’s security teams identify and block phishing attempts and other attacks through guest invitations.
More recently, Microsoft has begun rolling out a new Teams meeting protection policy that lets admins automatically block all identified external bots from joining meetings.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Tech
Max vs 100 Sends Max Verstappen From Last on a 101 Kart Silverstone Grid to First in 35 Minutes
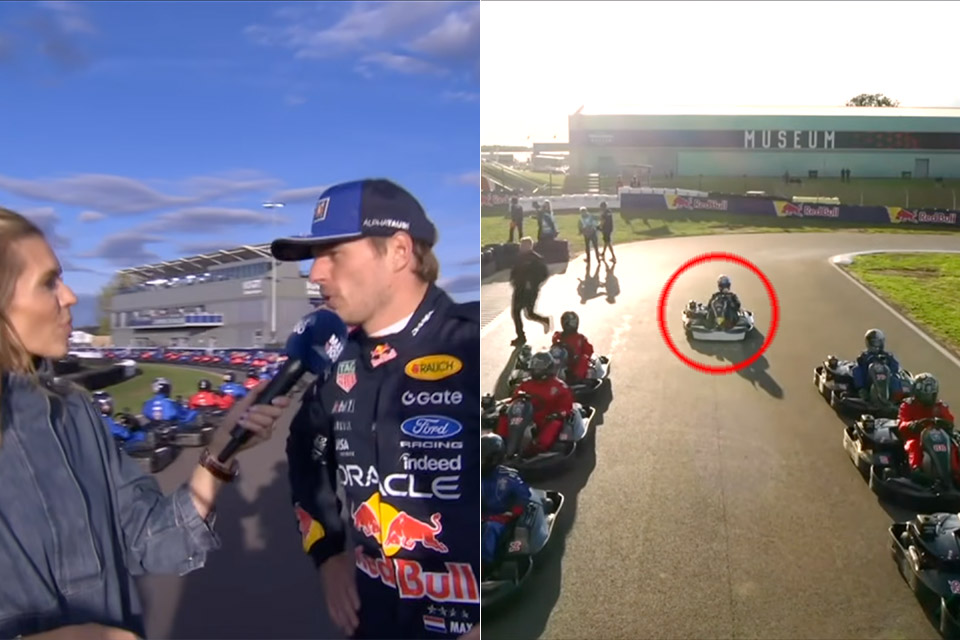
Red Bull staged Max vs 100 on Wednesday, September 16, 2026, as the largest go-kart race ever run, lining 101 identical karts on a purpose-built layout at Silverstone designed by race director David Terrien. Max Verstappen started 101st with a simple brief: catch and pass every driver ahead of him inside 30 laps or 75 minutes. Once the rear of his kart drew level with the front of another, that driver was out for good. The 100 people in front of him were athletes, content creators, streamers, journalists, and fans, most of whom had seen the track only in Tuesday practice plus one qualifying lap. Dutch Formula One journalist Jacky Martens took pole. YouTuber Zac Alsop and Red Bull Ford Powertrains technician Lewis Osler sat near the front with him.
Lights went out, mayhem ensued, and the field abruptly collapsed in on itself. Karts collided with each other’s bumpers, pointed in the incorrect direction, and stacked up at the first hairpin. Later, Verstappen claimed that he had no idea what was going on and informed the radio commentator that it was complete carnage. Despite this, he had passed over 10 drivers by the time he reached the start-finish line, and he continued to thread his way through the pack while others lost their confidence. By the completion of lap one, he was in 37th place, while sixty-three drivers had yet to complete a lap. When asked, he gave the number over the radio and stated it wasn’t a bad start. Yellow flags appeared briefly, freezing the rest of the pack.
Sale

LEGO Speed Champions Oracle Red Bull Racing RB20 F1 Race Car Model Kits – Building Set for Adults, Ages…
- RED BULL CAR – LEGO Speed Champions Oracle Red Bull Racing RB20 F1 Race Car buildable model for Red Bull and Formula 1 fans
- AUTHENTIC DETAILS – This F1 race car features design details from the real-life 2024 version, including a rear wing, halo bar, and wider rear tires…
- F1 MINIFIGURE – The vehicle kit includes an F1 driver minifigure wearing a Red Bull outfit and a winged helmet to place inside the F1 race car’s…
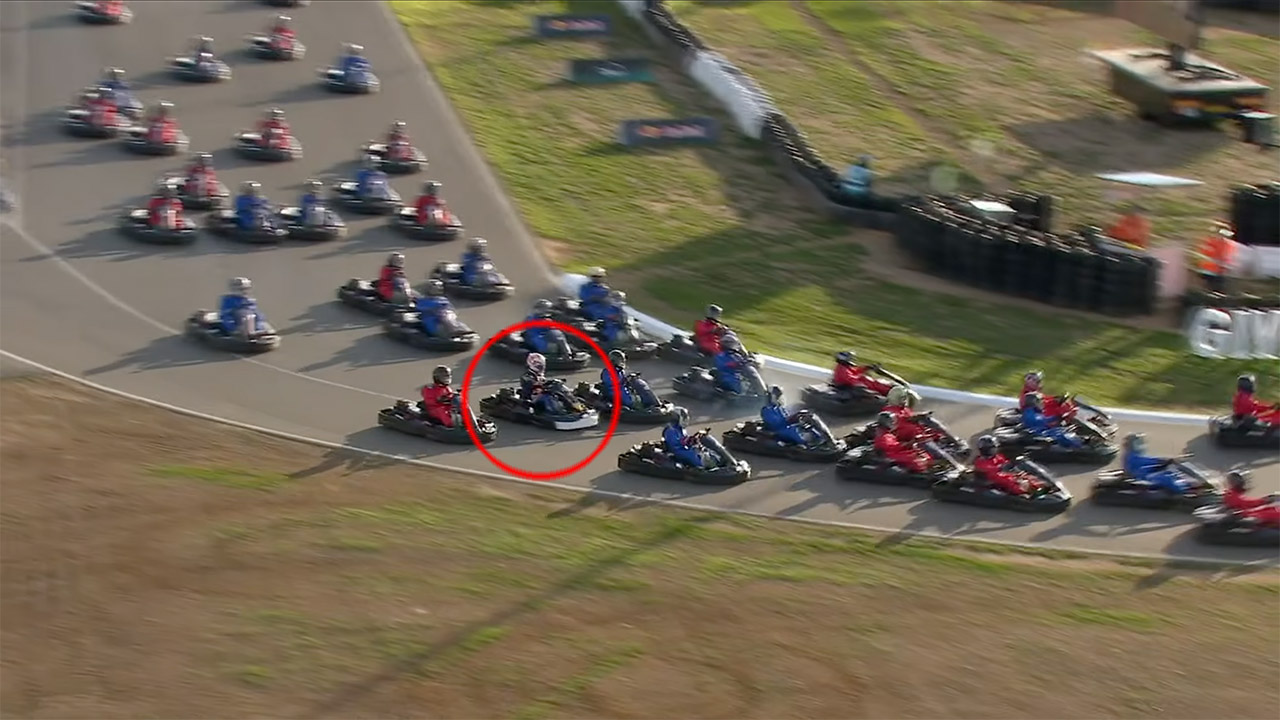
He’d bounced in the seat before the start, giving the kart an additional amount of roll as he launched off the line, and then braked a fraction of a second before everyone else to make way for the inevitable spinning. Open radios picked up the remainder of the pack reacting as he approached, and one driver begged him not to pass, while others were terrified, and he warned at least one of them he was coming for them. By lap five, the majority of the grid had gone. By lap six, he was inside the top 10, and by lap ten, he was in fourth place, gaining nearly three seconds each lap on the leaders while passing every 21 seconds. His quickest lap was 2:20.673, more than two and a half seconds faster than Martens’ 2:23.327.
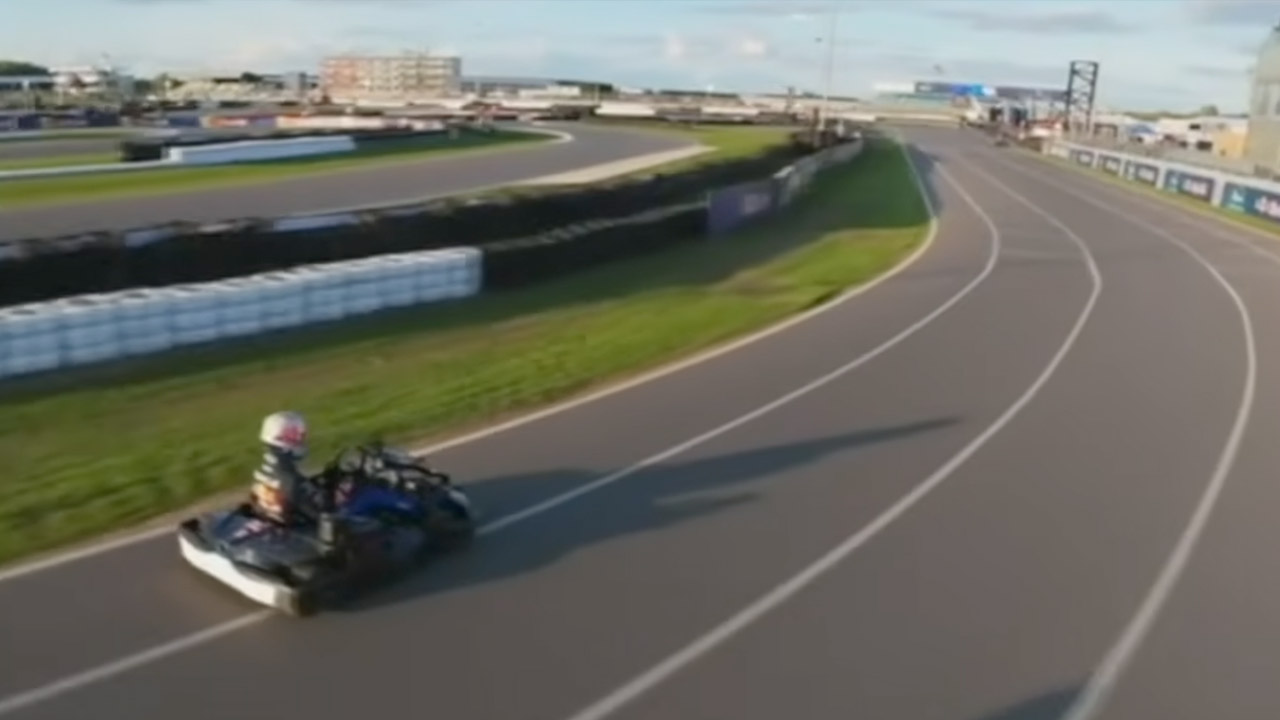
Martens, Alsop, and Osler had created a 12-second lead, and the race director saw fit to allow them an extra fast-lap shortcut with time remaining on the clock. On lap 12, they used it together before abandoning caution and concentrated on defending rather than racing. Verstappen managed to past Alsop and Osler in a single circuit on lap 13 before carving up Martens to secure the victory. Overall, it only took him 14 laps. 35 minutes. There were 21 laps and 40 minutes remaining. As he raised the flag, he described the afternoon as simply magnificent, before joking that it was his first win of the year, so he’d accept it. He also stated that it was one of his favorite days in a kart, the type of session that reminded him of how he used to race before getting into Formula One all those years ago.
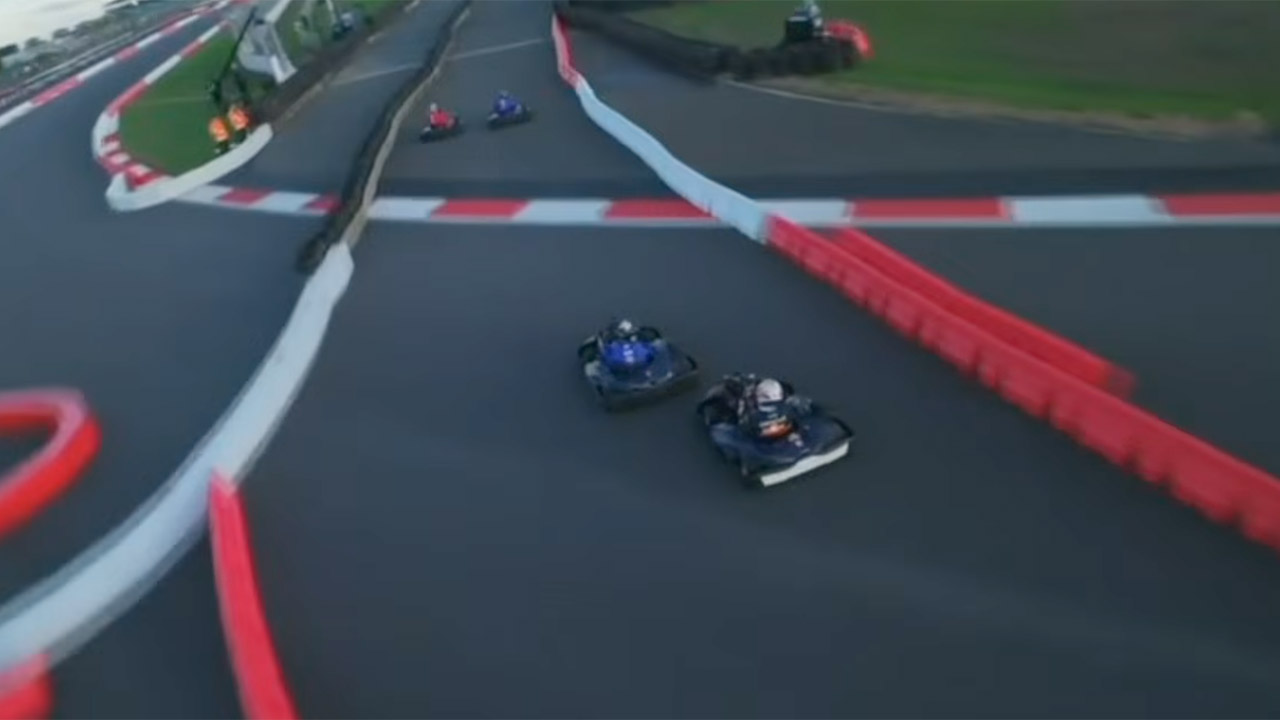
Martens finished second, with Osler, a mechanic from Verstappen’s own powertrain group, coming in third. Alsop finished fourth, followed by off-road racer Pol Tarrés in fifth, Paky TWC, RDJavi, photographer Larry Chen, mountain biker Bernard Kerr, and actor Neo Yau. A four-time world champion started last in a 101-kart field designed for this type of turmoil and finished in less than half the time. That was the most surprising part, but thankfully it was a good one.
[Source]
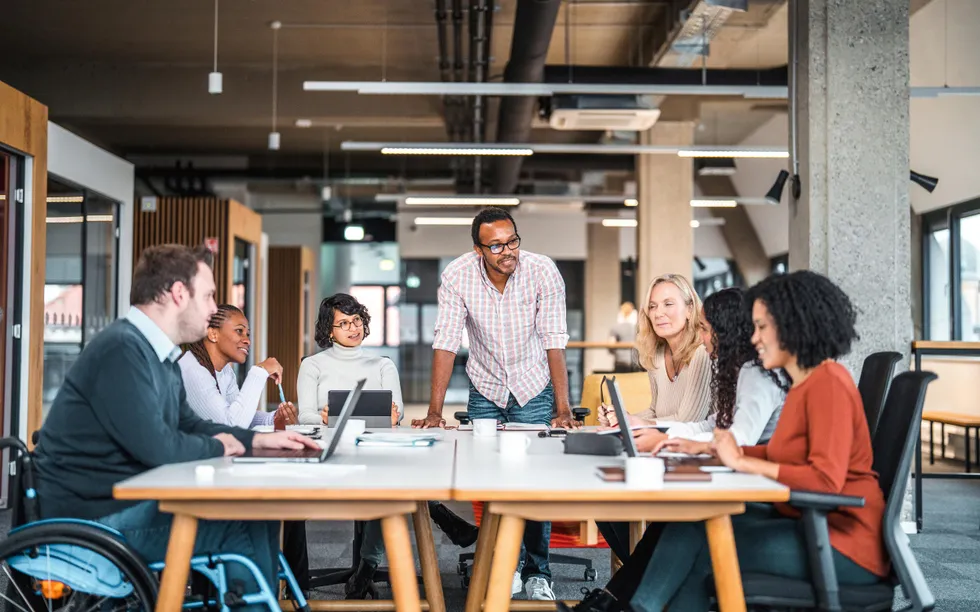

Transitioning from years of working in a senior technical or executive role to a leadership position is one of the most challenging phases of a STEM career. It requires moving away from making decisions on your own to mentoring others, making strategic decisions for the organization, and collaborating with coworkers from different generations.
The shift in mindset is known as “legacy leadership,” a philosophy whereby success is no longer measured by personal achievements but by how effectively a senior leader empowers others.
To help seasoned professionals and senior experts navigate the transition, the inaugural IEEE International Leadership Conference (ILC) will provide attendees practical advice on cultivating collaborations and guiding emerging talent.
“Early in our STEM careers, we measure success by what we have achieved,” says Jeewika Ranaweera, cochair of the IEEE ILC program committee. “Later, we should measure success by what we enable, how many people we mentor, how much knowledge we transfer, and how many doors we open for the next generation.”
The ILC is scheduled for 3 and 4 October in Budapest. Registration is open.
Letting go of the “expert” identity
For decades, seasoned technologists have been valued primarily for their technical expertise. Shifting from that identity can feel uncomfortable, but legacy leadership requires measuring success by different standards. They include a leader’s influence on the staff, the ability to uphold the company’s mission, and empowering others to lead and succeed.
The transition requires leaders to find purpose outside their corporate titles, shifting their focus to the long-term sustainability of their teams, their organization, and the broader technical community.
“A professional legacy is not measured only by what we have achieved but also by sharing our knowledge, experience, and opportunities with others,” says Sudhanshu S. Jamuar, another program committee cochair. “The real transition from expert to a legacy builder happens when we stop asking, ‘What more can I accomplish myself?’ and start asking, ‘How many others can I enable to accomplish more?’”
Neeli Rashmi Prasad, IEEE ILC treasurer and sponsorship cochair, adds that the transition transforms a lifetime of technical work into a platform for future innovation.
“The true value of experience is not in how much knowledge we accumulate but in how intentionally we transfer it,” Prasad says. “When we partner with, mentor, and create space for others to lead, our expertise becomes a foundation for progress far beyond our own careers.”
Moving beyond advice-giving
True knowledge transfer requires coaching rather than advising, and mastering the art of active listening. To build deep trust with early-career colleagues and ensure a seamless transfer of leadership to the next generation, senior leaders must avoid offering unsolicited or outdated anecdotes. Effective mentorship is a collaborative loop in which senior experts contribute hard-won industry wisdom while remaining curious and learning from the fresh, cutting-edge perspectives of talented coworkers.
“Knowledge transfer is most powerful when it is a two-way bridge: experience flows from one generation to the next, while new ideas and perspectives flow back,” says Sudeendra Koushik, president of the IEEE Technology and Engineering Management Society and an ILC keynote speaker. “This approach transforms mentorship from simply passing on information into one where the next generation can question, experiment, innovate, and ultimately surpass what came before them.”
Seasoned professionals should encourage independent, disruptive thinkers rather than carbon copies of themselves, Prasad says.
“Legacy leadership is about building continuity,” she says. “We should not simply prepare the next generation to follow the paths we created; we should give them the confidence, knowledge, and networks to challenge those paths, create new ones, and take technology further than we imagined.”
Designing your next chapter
Leadership does not need to stop when one’s job ends; it can evolve. Seasoned, retired professionals can continue contributing meaningful service through pathways that align with their personal passions. They include:
- Advisory boards: steering corporate, technical, or community organizations.
- Civic engagement: applying engineering methodologies to solve community challenges.
- Volunteerism: mentoring the next generation of grassroots innovators through professional networks including IEEE.
Those pathways offer experienced professionals an opportunity to redefine success, not in terms of position, authority, or personal achievement but in terms of sustained impact.
“Retirement from a job should never mean retirement from purpose,” Koushik says. “Our experience becomes even more valuable when we use it in service of the profession, society, and the generation that follows.”
At the same time, the collaborative continuum relies on a proactive younger generation. Emerging leaders need to take responsibility for building their professional connections, Prasad says, advising: “Be bold, stay curious, and build your network early!”
A space for continuity
The conference is designed to combine a drive to cultivate emerging innovators with a deep reservoir of industry stewardship and strategic perspective. Rather than a single classroom session, the conference will feature a dedicated career-readiness and mentorship track where attendees can explore practical frameworks for building strategic professional networks, connecting with peer advocates, and establishing reciprocal knowledge-sharing opportunities across generations.
By participating, seasoned professionals can ensure their decades of expertise continue to yield dividends for generations to come.
“Our professional legacy is not the technology we build, the titles we earn, or the awards we receive,” Ranaweera says. “It is the knowledge we share, the lives we influence, and the future we help others create.”
You can view the agenda, read speaker biographies, and secure your seat at the ILC online.
From Your Site Articles
Related Articles Around the Web
Sports1 minute ago
Kobbie Mainoo decision speaks volumes for Man United as pundits’ favourite frozen out

Tech2 minutes ago
From elections to board games: Washington’s secretary of state does double duty as a tabletop trade envoy
NewsBeat4 minutes ago
Man found with sickening images on Snapchat account told police he had been ‘hacked’




-

 Tech5 days ago
The Latest Weird Thing to Play Doom Is the Mapped-Out Brain of a Fruit Fly
-

 Crypto World4 days ago
Kraken Lets xStocks Holders Earn Yield Through DeFi
-

 Crypto World2 days ago
US Charges Robinhood Engineers Over Crypto Listing Trades
-

 Crypto World6 days ago
Can AI Build a Startup in 72 Hours? Elon Musk's Team Will Livestream the Test
-

 Crypto World3 days ago
What Is the Status of the U.S.-Iran Peace Talks? Here's What Both Sides Are Saying
-

 Crypto World4 days ago
Elon Musk Drops a Bombshell: Grok 5 Could Be the AGI Breakthrough
-

 Business6 days ago
Rivals Sam Altman and Elon Musk Rally Behind Dario Amodei’s Call for a Slowdown in AI Development
-

 Crypto World5 days ago
New Tesla Roadster Uses SpaceX Tech. Will It Impact the Stock Price?
-
 NewsBeat4 days ago
‘Sick conspiracy’: Trump says only guardrails AI needs is ‘a strong and smart (High IQ!) president’ in all-caps rant
-

 Crypto World7 days ago
Robinhood Chain Never Stopped But its Blobs Did Stop Reaching Ethereum For 14 Minutes
-

 Crypto World4 days ago
NVIDIA Analysis: Attempted Rising Wedge Breakout Amid Pressure on the AI Sector
-

 Business7 days ago
Marvell: Most Potent Setup Of The AI Factory Decade
-

 Crypto World4 days ago
Revolut Attackers Warn of Ongoing Daily Customer Data Leaks
-

 Crypto World5 days ago
3 Token Unlocks to Watch in the Third Week of September 2026
-
Crypto World4 days ago
Can Circle’s Arc Repeat Robinhood Chain’s Meme Coin Boom?
-

 Crypto World4 days ago
DOJ Seeks to Seize $61M in Iran Oil Funds From Binance Accounts It Vouched For
-
 Crypto World7 days ago
Bitcoin ETFs lose $462.7M as Ethereum funds gain $196.9M
-
Business4 days ago
SK Hynix ADRs Fall More Than 6% as Memory Rally Breaks on Fears of Slower AI Spending
-
 Crypto World5 days ago
AI Safety Burden Falls on Chief Executives as Trump Prioritizes China Race
-
 NewsBeat6 days ago
Last Night of the Proms pays moving tribute to Dolly Parton as Sheridan Smith wears a gold sequin jumpsuit in memory of the Queen of Country
You must be logged in to post a comment Login