Crypto
Base Cobalt upgrade puts new controls inside tokenized assets

Base activated Cobalt on September 30. For issuers of its B20 tokens, the fork adds a way to schedule balance multipliers, seize balances with a record and combine transfer policies. None of that makes a tokenized asset a share in the company it tracks. It makes the rules enforced by the token more explicit, and the identity of the issuer more consequential.
Summary
- Base Mainnet activated Cobalt at 18:00 UTC on September 30 after Sepolia activated 7 days earlier.
- B20 issuers gained 2 composite policy types, Union and Intersect, for combining existing transfer rules.
- A scheduled multiplier can change displayed token balances at a future time without each holder signing a transaction.
- The new seizure operation moves a holder balance under issuer authority when the relevant policy permits it.
- Base’s mainnet node minimum was v1.4.2; a scheduled fee payment in B20 tokens was removed from this fork.
The Cobalt upgrade specification records a September 30 mainnet activation, one week after Sepolia. Base’s public status page put the mainnet maintenance window at 18:00 UTC and marked it complete at 20:00 UTC. The fork adds B20 asset functions, transactions conditional on chain state, a registry for future upgrade scheduling in monitoring mode and an on-chain method for registering certain trusted-execution-environment prover signers. These are separate changes. The asset story begins with B20, the token format introduced with the earlier Beryl upgrade.
The fork went live, but its entire wish list did not
Two ideas that appeared in earlier Cobalt discussions are absent from the deployed scope. Payment of network fees in B20 tokens was removed from the fork’s list on September 29. Faster canonical 200 millisecond blocks belong to a proposed later Denim upgrade, not this activation. Native account abstraction has no scheduled mainnet gate here. Treating any of those as live Cobalt functions would confuse a roadmap with code an issuer or trader can use today. The distinction is especially important for institutions evaluating a token standard against current compliance requirements.
Base’s node release floor is v1.4.2 for mainnet according to the upgrade documentation. The preceding v1.4.1 included the timestamp but missed changes to validity transaction RPC forwarding; v1.4.0 does not contain the mainnet activation. A node that follows a fork without forwarding the new transaction type correctly can present a partial view of what users think is a uniform network. The code-level distinction is more instructive than a blanket statement that Cobalt is live.
The news hook is real, but it is not the whole thesis. B20’s earlier activation had already put issuer-managed assets on Base. Cobalt increases the actions the issuer can take and the policy decisions a transfer may face. The key question is who can invoke those functions, under what legal promise, and how a holder can check the result.
A B20 balance is a ledger entry with an issuer
A tokenized equity product can be represented as a balance on Base while rights to the underlying security sit with a broker, custodian or contractual issuer. The token standard cannot itself force a transfer agent to recognize the wallet holder as a shareholder. The link between on-chain balances and off-chain property rights comes from the product documents and the entities responsible for backing, redemption and corporate actions. A security token can be technically transferable and contractually restricted at the same time.
Coinbase’s tokenized-stock launch coverage describes a market in which backing arrangements and eligible users matter as much as trading interfaces. That context makes Cobalt’s additions more than developer conveniences. A policy can exclude an address, require a condition, or allow only a class of transfer. An administrative seizure can reassign a balance. A multiplier can change how balances display across accounts. Each function can support a lawful operational need and can also create dependence on an issuer’s judgment or administrative key security.
The B20 format needs to be examined at the token level. The mere fact that Base supports seizeWithMemo does not grant every B20 issuer a seizure right against every token, let alone every ERC-20 on Base. The B20 precompile reference says a token whose issuer has not configured the applicable policy slot has no seizure capability. An auditor has to inspect that token’s policy and authorized accounts. Two assets using the same standard can have sharply different holder rights.
This is the first control split to put on a whiteboard: the chain decides whether a transaction conforms to the deployed rules; the issuer decides which permitted administrative call to send; and the real-world asset provider is responsible for whether the token matches an enforceable claim. Cobalt changes the first two layers. It does not resolve the third. The same address may trade a token on-chain and still fail an off-chain eligibility test at redemption.
Seizure leaves a trace, but the reason is off-chain
Cobalt introduces seizeWithMemo, an issuer-authorized operation that moves tokens from a holder in one administrative step, superseding an earlier burnBlocked flow. The memo can leave a reason marker in the on-chain record. It does not prove the reason was legally sufficient. A smart contract can verify that the calling account has authority and that configured exemptions apply. It cannot decide whether a court order was valid, whether the issuer matched the correct defendant or whether a customer’s complaint should succeed.
The issuer operations guide describes the mechanics. A token might use seizure for a sanctions order, mistaken issuance, recovery under contractual terms or a corporate action. Each is a different justification. The holder should be able to find the administrator identity, the policy, the event and a dispute process in the product’s legal documents. If an issuer only says that tokenization is transparent, a reader should ask transparent about what: the transfer may be visible while the underlying decision remains opaque.
There is a subtle implementation detail. The documentation says the exemption scope changed name from SEIZE_HOLDER_POLICY to SEIZE_EXEMPT_POLICY, with a different selector. Code that hardcodes the old scope can fail to read or set the new one, even though older Beryl selectors otherwise continue. This is a genuine integration question for issuers and auditors, not a general claim that balances became newly seizable on September 30. Check the live token’s policy configuration and test the administrative call under the deployed fork.
The chain provides an evidence trail that conventional account corrections may not expose publicly. If an issuer moves 100 tokens from one wallet to another, observers can count 100 tokens and identify the transaction. They cannot infer a 100-share transfer in the issuer’s off-chain shareholder register without reconciliation. The strongest issuer case is that regulated assets need procedures for error correction and legal orders; tokenized stock volume on Base gives the practical context for why those procedures are now design choices rather than abstract debates. The trade-off is that a holder accepts an administrator with meaningful power.
The multiplier can change units without a matching deposit
A scheduled multiplier allows an issuer to define a future change in how a B20 asset’s unit balance is represented. Think of a stock split. If a holder’s displayed quantity moves from 10 units to 20 at a 2-for-1 ratio while the economic claim per unit halves, value need not change. The on-chain mechanism can coordinate the balance adjustment without asking each holder to sign. The issuer still has to implement the corresponding real-world corporate action and explain the conversion to brokers, custodians and price feeds.
The arithmetic is simple and the reconciliation is not. Suppose 1 million token units are outstanding and a 2-for-1 multiplier is scheduled. The new displayed units would be 2 million if the same multiplier applies across the relevant balances. That does not create 1 million additional underlying shares. A responsible issuer must show that total beneficial claims are unchanged and that the reference security’s own split took effect on matching terms. If token units double while a trading system keeps an old price-per-unit reference, a chart or collateral engine could misstate exposure by a factor of two.
The scheduling function improves coordination by naming the moment before it arrives. It also gives observers something to monitor: a pending update, its authorized signer and the post-change supply and holder balances. It does not guarantee every dependent system consumes the update on time. An exchange order book, oracle, lending vault and tax ledger can each use a different snapshot. A multiplier that is correctly executed on-chain can still create operational errors where integrations cache the old representation.
B20’s balance semantics also matter for historical data. An explorer showing the holder’s balance after the split may not explain how many units the holder held a day earlier or what each unit represented. Analysts should normalize quantities to the multiplier in force at each timestamp before claiming that deposits surged or supply inflated. A published event log gives a path to that normalization, but it is work someone has to do. Trading volume stated as raw tokens across the event is not comparable without an adjusted unit.
Combining policies exposes the eligibility decision
Union and Intersect are the two new composite policy types. Union permits an operation if an underlying policy accepts it under the configured logic; Intersect requires multiple underlying conditions to pass. The exact constituent policies and direction of authorization must be read from the token configuration. The useful analogy is a gate with alternative badges versus a gate requiring several badges. It is not a statement that every token must perform identity checks.
Imagine an asset whose issuer allows transfers to approved broker wallets or to a designated redemption contract. A Union policy can express alternatives. Another issuer may require that both the sender and receiver meet separate conditions, where an Intersect arrangement is more appropriate. If one condition is maintained off-chain through an authorized registry, the apparent on-chain transfer rule still depends on an organization updating that registry. A changed allowlist can change tradability without the holder moving a token.
Composite policies make it easier to describe a regulated asset in reusable modules. They can also make it harder for a holder to discover why a transfer failed if the interface reports only a generic revert. The B20 invariants and tests give developers a starting point, but a product still needs human-readable disclosure of which addresses can act, who updates lists and how errors are challenged. A permissioned token with an undocumented gate is not meaningfully transparent just because the gate is on a public chain.
The strongest opposing argument is practical. A tokenized security offered across jurisdictions cannot promise unrestricted transfer and also satisfy eligibility restrictions, court orders and corporate-action processing. Programmable controls can be more predictable than manual freezes in a broker database. That case holds when controls are narrowly delegated, auditable and tied to enforceable terms. The opposing risk is equally specific: one administrative key, policy registry or issuer interpretation can determine a user’s access. The Cobalt fork supplies primitives. Issuers supply governance.
Conditional transactions do not override issuer rules
Cobalt also introduces validity transactions: signed transactions paired with conditions on chain state, held until those conditions match. This is a general transaction feature, not an automatic compliance waiver. A user may want an order to execute only if a balance, price-related state or other predicate has a specified value. A transaction that becomes eligible still has to satisfy the token’s transfer policy at execution. If an issuer changed an allowlist in the meantime, the transaction can fail or remain ineligible depending on its conditions.
That interaction creates a valuable question for market structure. If a trader signs an order today that becomes valid tomorrow, who can change the state on which its execution depends? Some state comes from neutral contracts; some comes from an issuer-controlled policy. A conditional transaction can reduce one form of execution uncertainty while leaving the holder exposed to an administrator’s ability to update permissions. Integration documents should say which predicate was checked, when it was checked and what happens on expiry or cancellation.
Node software determines whether wallets and service providers see the new path reliably. The mainnet v1.4.2 minimum includes RPC behavior for forwarding validity submissions to a compatible sequencer ingress. A v1.4.1 node may follow the consensus fork but fail that submission route. For a user, the distinction appears as a confusing rejected transaction, not a discussion of release tags. For an institution, it calls for end-to-end testing against the exact node version and RPC provider used in production.
There is another boundary: Base’s sequencing and eventual settlement infrastructure. An issuer policy is enforced in execution when the transaction runs; conditional submission does not give a user a guarantee about when a sequencer includes an eligible transaction. Nor does a fast on-chain receipt by itself settle a legal dispute over the underlying stock. Cobalt improves expression and admission of transactions. It does not collapse ordering, legal ownership and redemption into one proof.
The paperwork determines the asset beneath the token
A holder evaluating a tokenized share should start outside the chain: who owns the reference security, where is it held, what claim does the token confer, and who owes the holder at redemption? If the product is a derivative or contractual claim on an issuer, the holder may not have the voting or insolvency rights of a direct shareholder. Cobalt does not change that classification. Its added controls can implement terms already in the agreement or give an issuer new technical capacity that requires updated disclosure.
Coinbase’s expanding tokenized-stock list illustrates the speed at which product menus can grow. A familiar stock ticker on an app is not a substitute for the issuer’s legal entity name and the asset-specific terms. Some products are available only to certain users or jurisdictions. Restrictions can be enforced at onboarding, at transfer, at redemption or at all three. If on-chain transfer is open but redemption is permissioned, the secondary buyer may end up with a token they cannot redeem directly.
A transparent policy disclosure would list each administrator role, the functions it can call, whether a multisignature is required, whether powers are time-locked and how emergency changes are announced. It would map each on-chain power to a contractual clause. It would show the reserve or custody verification process and how a holder can contest a seizure. The number of on-chain wallets holding a token cannot answer these questions. A token can spread across thousands of addresses while one issuer retains decisive authority over every redemption.
Cobalt also makes an old word, “ownership,” harder to use casually. One person can own the private key controlling a wallet. Another entity can control token issuance and administrative transfers. A custodian can hold the reference share. A broker can control access to the market. A court can assert authority over the claim. Those rights may be legally coherent, but their allocation must be explicit. The chain cannot rescue ambiguous product documents by making one part of the ledger public.
Measure deployment by configured assets, not by fork status
The fork’s activation is verifiable at a block and time. Adoption of its new B20 powers requires a different count: how many live asset contracts actually configure the new policies, how many schedule multipliers and how many invoke seizure? A zero count shortly after activation would not mean the fork failed. It would mean issuers had yet to use those optional functions. A large count would not prove the assets are fully backed or that the controls are well governed.
A reproducible measurement would inventory B20 assets, check policy selectors at the same block height, identify administrator addresses and classify observed calls after September 30. It would separately count attempts that revert and successful state changes. It would avoid assuming that an asset called “stock” has an underlying share merely because its metadata says so. This is a better adoption measure than transaction volume, which may reflect speculative trading in tokens whose legal structure differs widely.
The limit of the current record is that the fork specification describes a capacity, not a complete registry of active issuers and their terms. There is no universal Cobalt setting that determines all tokenized asset rights. Each issuer may configure functions differently, and a later update can change permissions. A node can correctly verify a transfer while the off-chain custodian’s statement remains late or disputed. A token can show an administrative move in public without telling the holder whether it was lawful.
The conclusion is concrete. Base now has more precise tools for issuers to control asset balances and eligibility. Holders gain a better chance to inspect those controls if issuers disclose them clearly. The meaningful test begins at each token: who can change the multiplier, who can seize, who can alter transfer policy and what legal claim survives if the issuer fails?
A holder can test three promises against one contract
The first promise is supply. A backing report might say that every token corresponds to one unit of an underlying asset held by a custodian. The holder can compare reported token supply at the report’s snapshot with the custodian’s stated position, adjusting for any multiplier then in force. The two numbers need the same timestamp and unit. A report of 1 million shares at yesterday’s close cannot be set beside a post-split supply of 2 million tokens today and called a deficit. Nor does a matching aggregate prove that every individual holder has the redemption right the marketing page implies.
The second promise is transfer. A product may advertise peer-to-peer settlement, then apply a policy that permits transfers only between registered intermediaries. Both statements can be true if the permitted peer set is narrow. A holder can inspect the token’s configured policies, submit a read-only simulation of a transfer between representative address types and compare the outcome with the published eligibility rules. That exercise should include a wallet eligible to hold, an ineligible wallet and the redemption destination. If results differ from the terms, the issuer should explain the mismatch before users trade.
The third promise is recourse. A user whose balance is moved by seizeWithMemo needs more than an event hash. The issuer should publish a case reference that protects private information while identifying the authority invoked, the applicable term, the date of notice and the channel for challenge. The holder can then compare the recorded movement with that account. A memo that says “compliance” without a procedure does little for someone contesting a mistaken identity or duplicated instruction. A token standard cannot compel a fair appeal, but its event trail can make the absence visible.
There is a fourth practical test for anyone using these tokens as collateral. A lending protocol may mark the asset to a market price and accept it as security for a loan. If the issuer can freeze or seize the collateral address, or alter the unit count through a multiplier, liquidation software needs to understand both events. A lender that prices an asset by ticker alone may miss a contract-level restriction on transferring it during liquidation. The borrower, meanwhile, may see a healthy price quote but be unable to move the pledged balance to repay. The relevant disclosure is whether the lending contract itself is exempt, who can change that exemption and what happens when the issuer revokes a user’s eligibility.
A custodian can answer some questions with an independent attestation, but an attestation has a scope. It might verify shares held in an omnibus account at a particular time without checking that token holders have a direct property interest. It might verify aggregate backing without checking whether a seizure changed the distribution among customers. A serious audit states the legal entity, the asset identifier, the snapshot time, the reconciliation method and the exclusions. The document should be refreshed after material issuance, redemption or corporate action. Readers should be able to compare successive snapshots, not merely admire a one-time badge on an app.
There is a failure case that the blockchain cannot settle: the issuer enters insolvency while the token continues to trade. The on-chain supply, policies and event logs may all be intact. The decisive question then is whether the underlying assets are segregated for holders, part of a custodian’s estate, or a general claim against the issuer. A smart contract with perfect enforcement of transfer restrictions does not pick a bankruptcy priority. This is why Cobalt’s administrative precision increases the urgency of reading product terms. It tells users exactly what the issuer can do with the token, while the documents must tell them what they can demand from the issuer.
An audit that tests all three promises would go beyond showing that code runs. It would reconcile the outstanding claims with assets held, the actual transfer gates with the published rulebook and administrative actions with a process outside the issuer’s own interface. The public chain supplies evidence for each test, but never the whole answer. Custody records and contract terms must be brought to the same date and unit. That is the work a tokenized asset requires after the celebratory fork announcement.
One more operational boundary deserves a public test. A token’s administrator might be a multisignature wallet with several signers, but a single company could appoint every signer. Publishing the threshold without naming the governing bodies does not show independent oversight. An issuer can disclose the threshold, key rotation procedure and emergency authority without revealing secrets. If it claims that holders can appeal a decision, it should identify the legal entity that reviews an appeal and the period in which it responds. These facts turn an on-chain permission into an accountable process.
A skeptical reader should also check whether policy changes emit events that data providers follow. If a wallet was allowed to transfer at noon and blocked at 12:01, the timing matters to a pending order, a lender’s margin calculation and a holder trying to redeem. A dashboard that updates once daily may make a real-time change look like a surprise seizure. Monitoring the contract directly can close that gap, but the product provider should still send notice to users whose rights change. Cobalt makes changes executable. Disclosure determines whether those changes are intelligible.
What to watch
- Configured policy counts: Public B20 contracts using Union, Intersect and seizure permissions after the September 30 fork.
- First scheduled multiplier: Its announced effective time, applied ratio and reconciliation with the off-chain corporate action.
- Administrative moves: Successful seizeWithMemo events, the authorizing role and an issuer explanation of each material case.
- RPC parity: Major Base node and RPC providers running at least v1.4.2 and accepting validity submissions consistently.
- Issuer disclosures: Product terms that map every on-chain administrator power to an enforceable right and appeal process.
FAQ
When did Base Cobalt activate on mainnet?
Cobalt activated on September 30, 2026 at 18:00 UTC according to the fork schedule. Sepolia activated seven days earlier.
Can every token on Base now be seized?
No. B20’s administrative seizure requires a token-level policy and authorized role. The fork does not apply that power to every ERC-20 or B20 asset.
What does a scheduled multiplier do?
It changes the represented unit balance at a specified time, potentially coordinating an event such as a stock split. The issuer must reconcile the change with the underlying asset and trading systems.
What are Union and Intersect policies?
They combine other B20 policies as alternatives or jointly required conditions. The actual transfer rule depends on a specific token’s configuration.
Can holders pay Base gas in B20 tokens after Cobalt?
No. Fee payment in B20 tokens was removed from Cobalt’s shipped scope on September 29 and remains a separate roadmap item.
Is a tokenized stock the same as directly owning a share?
Not automatically. The holder’s voting, redemption and insolvency rights depend on the product documents and the structure of backing.
Which node release is required for Cobalt mainnet?
The published mainnet minimum is v1.4.2. Earlier releases can miss the fork or the validity transaction submission path.
What would prove these controls work fairly?
A live token’s policy, administrator list, event history and matching legal terms can be audited together. A chain event alone cannot validate the issuer’s off-chain reason. This is educational analysis, not investment advice.
Disclaimer: This article is for information and educational purposes only and does not constitute financial or investment advice. Figures reflect regulatory filings and reporting available at the time of writing and change with each disclosure. Nothing here is a recommendation to buy, sell, or hold any security or asset. Always do your own research. Information is accurate as of October 1, 2026.
Justin Sun, founder of the Tron network, said that the company’s post-quantum cryptography was now live on testnet.
“We’re closely tracking progress in quantum computing and AI, and we’re ready to bring quantum resistance to mainnet at any time, Sun said in a post on X on Saturday.
He added, “We’re committed to keeping user assets secure, and TRON is set to be one of the few major blockchains that is quantum-resistant before Q-Day,” or the day when quantum computing becomes capable of breaking current security standards.
Coindesk reported on July 28 that Blockchain security company AmericanFortress had unveiled a cryptographic plan to protect crypto wallets from future quantum attacks without requiring users to move funds, rotate keys or change wallet addresses.
Unlike most proposed post-quantum approaches, AmericanFortress said it allows existing wallet addresses to remain unchanged while adding post-quantum protection.
Proposal published in technical paper
The company published the proposal in a technical paper on the Cryptography ePrint Archive, though it had not yet been peer-reviewed.
Developers have increasingly focused on post-quantum cryptography because sufficiently powerful quantum computers may eventually break the elliptic-curve cryptography used to secure Bitcoin, Ethereum and many other blockchain networks
Earlier this year, a Strategy-led consortium pledged $15 million to fund Bitcoin quantum security research, the Ethereum Foundation published a proposal for migrating accounts to quantum-resistant cryptography and Algorand outlined plans to introduce quantum-resistant accounts by 2027.
Magazine: SHRINCS BIP published: Quantum-secure Bitcoin comes with a catch
Crypto
JPMorgan makes bullish call in fixed income space, suggests it’s a once in a generation opportunity
J.P. Morgan Asset Management is making a bullish call on an underinvested market group: high-quality fixed income.
Priya Misra, a portfolio manager at the firm, sees a once in a generation opportunity for investors.
“You can actually take credit risk in the highest quality companies and still get [a] 6.5% [yield], Misra told CNBC’s “ETF Edge” this week. “So, you actually don’t have to go down in credit [quality].”
She suggested the strategy is particularly well suited for investors concerned about having too much exposure to artificial intelligence stocks.
“There’s a huge AI exposure,” Misra said. “What fixed income gives you is this diversified set of returns. It’s not just an AI trade or a tech trade. You have the Treasury trade. You have credit outside of AI.”
Misra co-manages the JPMorgan Core Plus Bond Fund ETF (JCPB). The fund has almost $16 billion in assets under management, with just over three-quarters of its holdings in BBB-rated debt and above, according to the firm’s website as of Aug. 31.
“We’ve actually been increasing some of the double-B [and] single-B exposure because there has been a widening in high yield spread,” she said. “We like some investment grade. And now, we’ve started in the last few days to increase some duration as well, thinking we may be nearing the end of that rate move.”
The JPMorgan Core Plus Bond Fund ETF is down more than 5% so far this year as of Friday’s close, according to FactSet.
“You want to be looking bond by bond and sort of sector by sector to see where the macro and you have to do the bottom up as well to make sure that companies are not over levered,” noted Misra, who’s concerned about how higher rates could hurt the housing market.
BondBloxx co-founder Joanna Gallegos is also advising investors to take advantage of “historically attractive” yields across debt markets.
“You want to really consider getting some corporate debt into your portfolio,” Gallegos said in the same interview. “It’s really in the investor’s best interest to start looking at the income that’s back in fixed income. It can offset the volatility in your portfolio.”
Part of her bull case: Base rates are high, and they’re stable.
“The fundamentals of these corporations are so strong, and the economy continues to grow,” added Gallegos. “We really think that’s being lost in the narrative around Treasury rates.”
Her firm BondBloxx is known for fixed-income exchange-traded funds in sectors including Treasury, corporate, private credit and emerging markets.
One of its funds includes the BondBloxx Private Credit CLO ETF (PCMM). As of Friday’s close, it’s down 0.6% so far this year, according to FactSet.
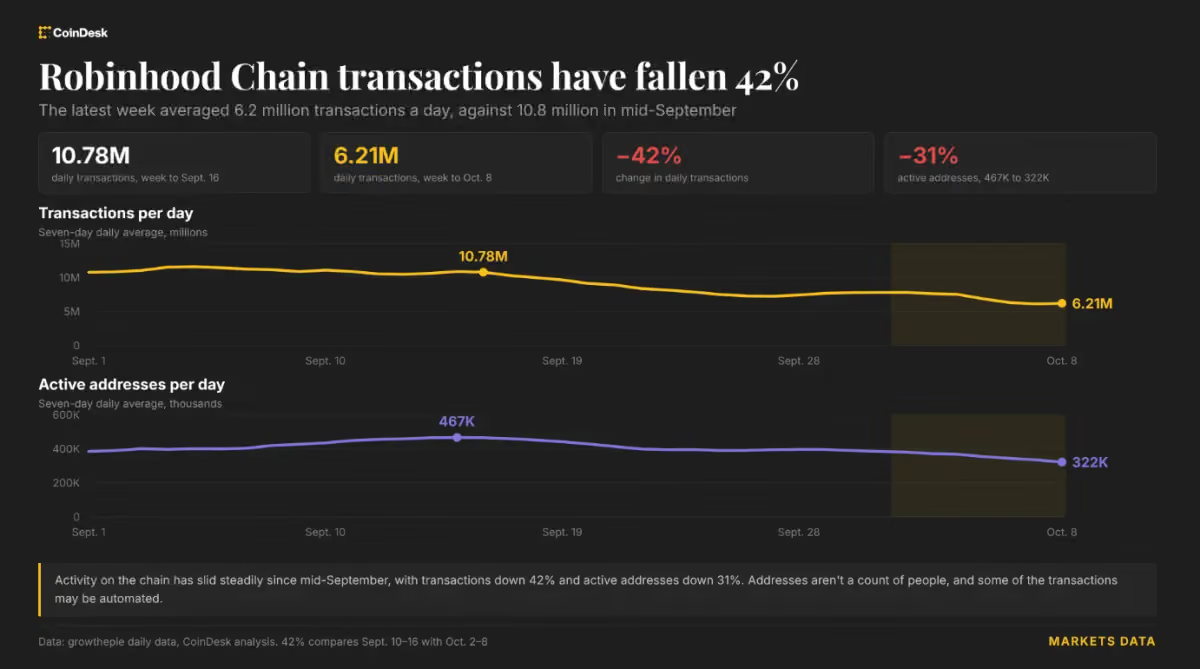
Daily active addresses averaged about 322,000 in the latest week, down 31% from mid-September, suggesting fewer people, and fewer of the trading bots they run, are using the chain each day.
The drop is likely smaller in human terms than the raw number implies, since one trader can run many addresses and a single automated program can account for thousands of transactions.

Less trading, steady balances
Spot exchanges, where users buy and sell tokens directly, handled $7.45 billion during Oct. 2–8, down 21% from $9.46 billion the week before, according to CoinDesk calculations using DefiLlama. Uniswap, an app that lets people swap tokens with each other without a company in the middle, handled roughly 77% of that.
Users aren’t pulling their money out, though. Deposits in the chain’s lending and trading apps rose about 2% over the week to $1.04 billion, and the supply of stablecoins, tokens pegged to the dollar, ticked up to roughly $1.10 billion.
That suggests the pile of money is simply being traded less, with traders keeping their funds on Robinhood Chain and waiting.
Futures are the exception, however. DefiLlama’s rolling seven-day figures on Friday showed about $7.35 billion in perpetual futures volume, contracts that let traders bet on prices without owning the tokens, up 26%.
Crypto
Mashinsky Accepts Lifetime Industry Ban and Up to $35 Million in Conditional Payments | The Defiant
The New York settlement ties the money to federal forfeiture and prison-sentence conditions, adding to existing FTC and CFTC restrictions…. Read the full story at The Defiant
Source link

Key takeaways
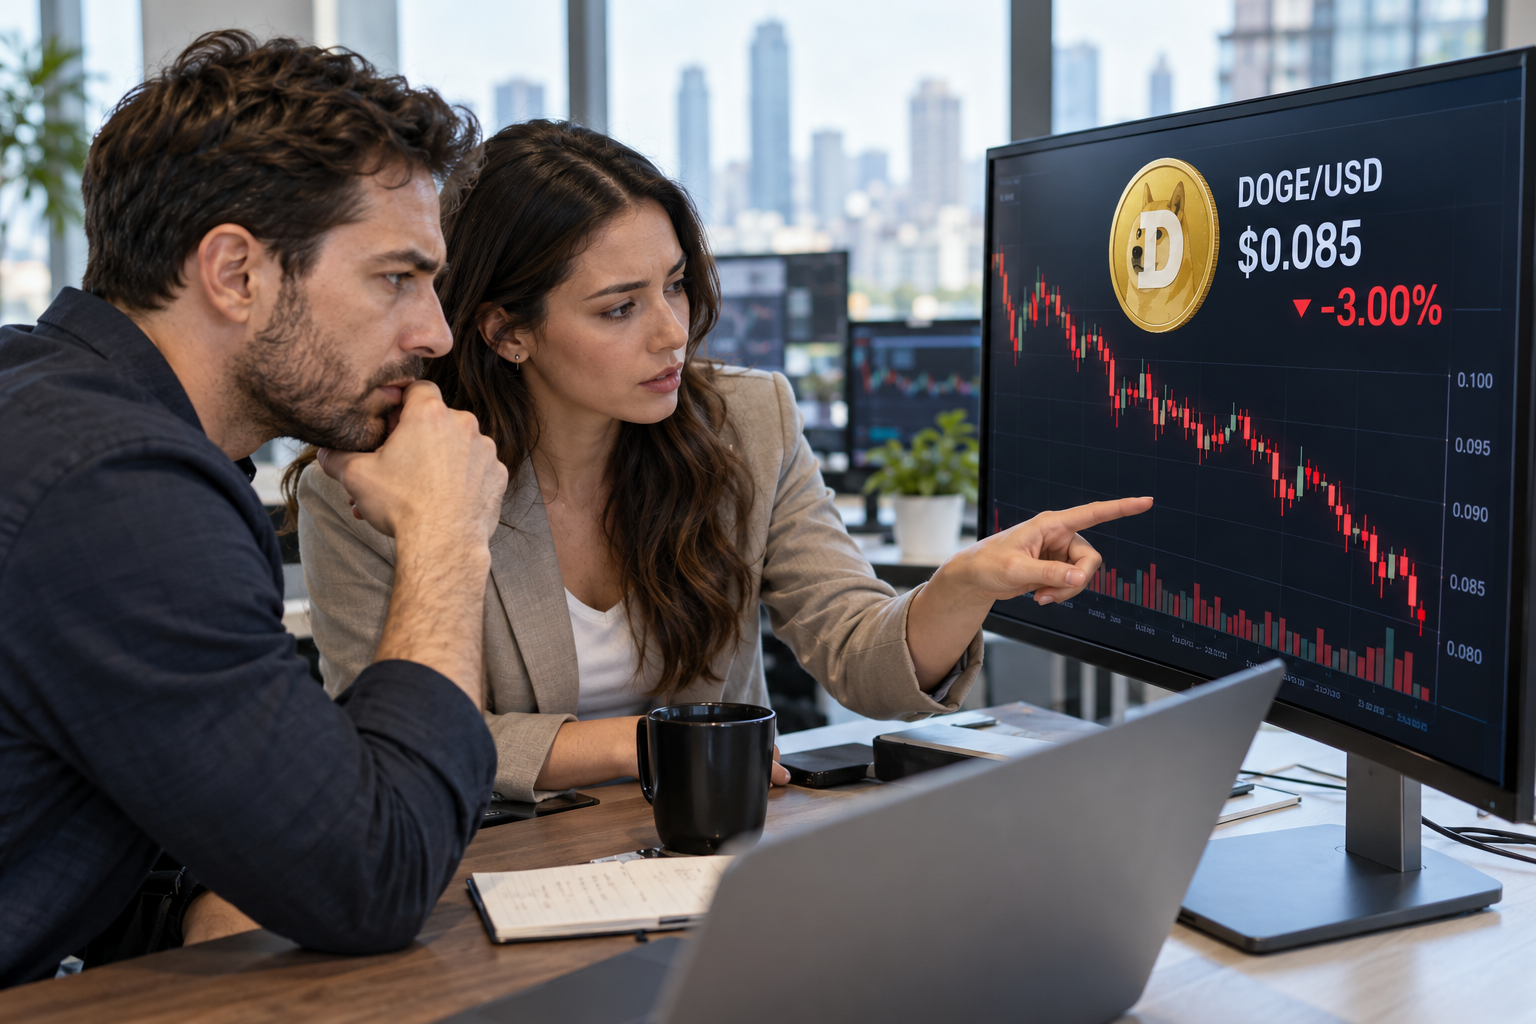
- Dogecoin traded near $0.085 on Friday after losing more than 11% this week.
- Two large-wallet cohorts reduced their combined holdings by 100 million DOGE since Tuesday.
- A close below $0.084 could expose $0.078 and $0.070, with resistance beginning at $0.086.
Dogecoin traded around $0.085 on Friday, approaching a key trendline area after a weekly decline of more than 11%.
Falling balances among some large holders and weakening technical momentum suggest continued downside pressure.
However, derivatives positioning offers a more mixed picture, with long positions outnumbering shorts in CoinGlass’ tracked ratio.
Large Dogecoin holders reduce exposure
Santiment’s supply distribution data shows that wallets holding between 1 million and 10 million DOGE and those holding between 10 million and 100 million DOGE have collectively reduced their balances by 100 million tokens since Tuesday.
The decline suggests some large holders are reducing exposure, potentially through profit-taking. Wallet balance changes alone do not confirm that every token was sold, but the movement adds to concerns about near-term supply pressure.
CryptoQuant’s summary indicators also point to caution. Its data identifies overheating conditions in both spot and futures markets, alongside large orders and sell-side dominance in futures.
These signals suggest that selling pressure remains significant as DOGE approaches nearby support.
Despite the price decline, CoinGlass’ DOGE long-to-short ratio stood at 0.90 on Friday, approaching its highest level in more than a month.
A reading above one indicates that longs outnumber shorts within the positions or accounts tracked by the metric.
Funding rates also remained positive at 0.0010%, meaning long traders were paying short traders to maintain their positions.
Together, the readings suggest some traders are positioning for a recovery. They do not establish that buying demand is strong enough to reverse the decline, particularly while price momentum remains weak.
DOGE tests $0.084 as momentum deteriorates
Dogecoin is trading just above the trendline area near $0.084, which serves as the immediate technical support reference.
A daily close below that level could open the way toward $0.078. A deeper correction would bring the next structural floor at $0.070 into focus.
The Relative Strength Index sits near 40, below its neutral midpoint and consistent with weaker buying momentum.
The Moving Average Convergence Divergence line remains below both zero and its signal line. Its negative, slightly expanding histogram also suggests sellers retain the near-term advantage.
DOGE remains beneath several important exponential moving averages, creating successive barriers to a rebound.


The first resistance is the 100-day EMA near $0.086. Above it, the 50-day EMA and a horizontal resistance level converge around $0.088.
Clearing those levels would help ease immediate bearish pressure. A stronger recovery would require a move above the 200-day EMA at $0.093, followed by a challenge of major resistance near $0.102.
For now, the balance between support at $0.084 and the moving averages overhead will help determine whether DOGE stabilizes or extends its weekly losses.
Three armed men have forced a Chinese expatriate with Turkish citizenship to transfer approximately $820,000 in cryptocurrency during a robbery at his luxury home near Pattaya, Thailand, prompting a police investigation into the suspects and the movement of the stolen assets.
Summary
- Three armed men broke into a luxury home near Pattaya, Thailand, and forced a Chinese expatriate with Turkish citizenship to transfer approximately $820,000 in cryptocurrency.
- The attackers threatened the victim at gunpoint and stole cash and three luxury watches before escaping in a vehicle that police later recovered.
- Thailand police are examining CCTV footage and tracing cryptocurrency transactions to identify the suspects, whose nationalities have not been confirmed.
- The robbery follows a series of violent attacks targeting cryptocurrency holders, with Chainalysis estimating losses of more than $30 million from such incidents in the first half of 2026.
According to initial reports, the robbery took place at around 3:30 a.m. on Tuesday, October 6, inside a gated residential community in Nongprue, where the attackers entered the property using a ladder before confronting the victim in his bedroom.
The masked men reportedly threatened the resident with firearms and ordered him to open a safe containing cash and valuables. They took an undisclosed amount of money and three luxury watches before demanding access to his cryptocurrency holdings.
Under threat, the victim transferred digital assets valued at roughly $820,000 to accounts controlled by the attackers. Reports indicate that the cryptocurrency was subsequently sold, although authorities have not disclosed which assets were involved or how the transactions were carried out.
The resident eventually escaped and contacted police. His identity has not been publicly released.
Thailand police trace stolen crypto and suspects’ getaway vehicle
Police Region 2 has taken charge of the investigation, with officers examining both the physical evidence left behind and the transactions involving the stolen cryptocurrency.
Police Lieutenant General Wasan Techa-akrakesom, commissioner of Police Region 2, said investigators had made significant progress in the case. The Immigration Bureau has been brought into the investigation as authorities work to establish the identities and movements of the suspects.
Initial information suggested that the three attackers might be Chinese nationals, but police have not confirmed their citizenship. No arrests were disclosed in the initial reports.
Investigators have reportedly recovered the vehicle used by the suspects after it was abandoned in a remote location.
CCTV footage placed the same vehicle in the area on October 5, one day before the robbery. Police are examining the footage as part of efforts to reconstruct the suspects’ movements before and after the break-in.
Alongside the search for the attackers, authorities are tracing the digital assets transferred from the victim’s holdings.
Investigators are reportedly examining accounts connected to the subsequent sale of the cryptocurrency in an effort to identify the individuals who received or handled the funds.
Details about the destination wallets, exchanges involved and potential recovery of the stolen assets have not been made public.
Police have yet to establish whether the attackers knew about the resident’s cryptocurrency holdings before entering the property or discovered them during the robbery.
The distinction remains unresolved because the intruders demanded several forms of property, including cash, watches and digital assets.
Crypto wrench attacks have cost victims millions in 2026
The robbery in Thailand follows several violent incidents involving cryptocurrency holders, including home invasions where attackers have used threats or physical force to obtain access to digital wallets.
Such crimes are commonly described as wrench attacks, a term used for robberies involving physical coercion to steal cryptocurrency or force victims to authorize transfers.
In an August investigation, crypto.news previously reported that criminals had stolen more than $30 million through violent attacks against cryptocurrency holders during the first half of 2026, citing research from blockchain analytics firm Chainalysis.
The firm documented 46 incidents during the six-month period, compared with 40 in the corresponding period of 2025. Only 12 of the 46 attacks resulted in payments, giving criminals a reported success rate of 26%.
Home invasions accounted for 37% of documented cases, compared with 14% in 2025. Kidnappings represented 52% of incidents, although Chainalysis noted that some cases could involve more than one type of crime.
A separate investigation by security firm CertiK identified 52 verified wrench attacks worldwide during the first half of 2026, with financial exposure totaling $124.1 million.
CertiK’s figure included stolen cryptocurrency, ransom demands, frozen assets and other amounts connected to reported incidents. It did not represent the amount criminals successfully obtained.
The firm’s findings placed France at the top of its list, with 33 verified attacks accounting for nearly 64% of the worldwide total. Europe recorded 39 incidents, while the United States accounted for four.
Armed home robberies have targeted crypto holders in France and the US
Several recent cases have involved attackers entering residential properties and demanding cryptocurrency transfers from occupants.
In September, four masked men held a family captive for more than three hours in Vendin-le-Vieil, northern France, before forcing the father, who worked in the cryptocurrency sector, to surrender access codes linked to approximately €40,000 in digital assets.
The attackers assaulted the father, while his 12-year-old daughter was struck in the face. French authorities investigated the incident as kidnapping and extortion by an organized gang.
Earlier that month, a couple in Alès was restrained and threatened by two armed intruders who demanded cryptocurrency transactions.
The attackers reportedly carried a handgun and a knife and held the couple for more than two hours while their young child was inside the house. Neighbors alerted police after hearing screams, prompting the suspects to flee.
Similar incidents have reached US courts. In June, two Texas brothers pleaded guilty in an $8 million cryptocurrency robbery case involving a Minnesota family.
Federal prosecutors said the brothers held the victims at gunpoint for approximately nine hours while forcing them to transfer digital assets. Both pleaded guilty to interference with commerce by robbery.
Meanwhile, investigators in Thailand are examining the abandoned getaway vehicle, CCTV footage, immigration records and cryptocurrency transactions connected to the Pattaya robbery.
According toPattaya Mail’s October 9 report, officers located a black Toyota Fortuner in a wooded area and identified footage showing the vehicle near Phatthanakan Road and Soi Wat Boonsamphan at approximately 3:38 p.m. on October 5.
Police have not publicly confirmed the suspects’ identities or nationalities, and the investigation remains ongoing.

Cryptocurrency and the technology behind it are no longer a fringe curiosity for Britain’s financial regulator — they are becoming central to how the UK hopes to keep its capital markets competitive. In a speech delivered this week, the Financial Conduct Authority (FCA) made clear that tokenisation, artificial intelligence and digital assets are now core pillars of its multi-year reform programme, not side projects bolted onto traditional finance.
Jon Relleen, the FCA’s director of infrastructure and exchanges, told delegates at the Reform of the UK Public and Private Capital Markets Summit 2026 that the regulator has “been very busy” completing major elements of a long-running overhaul designed to ensure markets “work well for our economy and support growth.” Crucially, he singled out tokenisation — the process of representing traditional assets like shares, bonds or funds as digital tokens on blockchain-style infrastructure — as one of the fastest-moving frontiers the FCA is now preparing to regulate.
Why cryptocurrency infrastructure is entering the mainstream conversation
For years, cryptocurrency was treated by many regulators primarily as a consumer protection headache: a space rife with scams, volatile prices and speculative trading. The FCA’s own website still carries extensive warnings about crypto investment scams and maintains a public list of firms operating without authorisation. That caution hasn’t disappeared. But Relleen’s speech signals a parallel track, where the underlying technology of cryptocurrency markets is increasingly viewed as a legitimate tool for modernising how capital itself is raised, traded and settled.
This dual-track approach — tightening consumer safeguards while embracing the infrastructure — reflects a broader pattern seen across global financial regulation. Authorities are trying to separate the speculative trading culture that surrounds cryptocurrency from the distributed ledger technology that underpins it, betting that the latter can make markets faster, cheaper and more transparent without necessarily importing the volatility of coins like Bitcoin or Ether.
Trust and risk-taking as twin priorities
Relleen was explicit that reform cannot come at the expense of market integrity. “Trust, market integrity and high standards set the foundations for sustainable growth,” he said, while also stressing that regulators must “enable informed risk-taking.” That balancing act is especially delicate in the context of cryptocurrency-adjacent innovation, where enthusiasm for new technology has historically outpaced investor protections.
The FCA’s framing suggests it wants to avoid repeating past cycles in which cryptocurrency products were sold to retail investors with little understanding of the underlying risks, only for sharp price crashes or platform failures to follow. By building tokenisation into a broader, more deliberate reform agenda — alongside AI adoption and new markets for trading shares in private companies — the regulator appears to be trying to get ahead of the technology rather than reacting to it after problems emerge.
What reform could mean for everyday investors
For ordinary savers and investors, the practical implications of this shift may not be felt immediately, but they could be significant over time. Tokenised versions of traditional assets could, in theory, make it cheaper and faster to buy and sell investments, lower barriers to entry for smaller investors, and create new ways to trade assets that are currently illiquid, such as stakes in private companies.
At the same time, the FCA’s own consumer-facing warnings underline that cryptocurrency-linked products remain high-risk. The regulator continues to flag crypto investment scams as a priority concern and maintains tools allowing the public to check whether a firm is properly authorised before investing. Anyone tempted by new tokenised products emerging from this reform push would be wise to apply the same scrutiny long urged for conventional cryptocurrency investments: verifying authorisation, understanding volatility, and being wary of promises of guaranteed returns.
A multi-year programme nearing a turning point
Relleen described the FCA’s broader capital markets reform effort as having already completed “major aspects” of a multi-year programme, with more changes still to come. Tokenisation and artificial intelligence were named specifically as areas where markets and technology are evolving rapidly enough that regulation must adapt in real time rather than simply catching up after the fact.
This positions cryptocurrency-related innovation not as a one-off experiment but as an ongoing feature of how UK capital markets will likely operate in the coming years. Whether that translates into tangible benefits for everyday investors, or simply shifts where the risks sit, will depend heavily on how the FCA follows through on the detailed rules still to be written. For now, the message from one of Britain’s top financial regulators is unambiguous: cryptocurrency-based tokenisation has moved from the margins of policy discussion to the centre of the UK’s plan for economic growth.
Explore more on this topic with Vexel Search.
“While Tether claims to operate out of El Salvador, the vast majority of its assets reside in the United States under your custodianship,” the Connecticut lawmaker wrote. “As Congress considers how to best regulate digital assets, your partnership with Tether will provide important insights into the inner workings of this industry.”
One of the letter’s many requests: “Please describe all steps Cantor Fitzgerald has taken to investigate allegations that Tether’s stablecoin has been used in illicit finance and money laundering, including within Iran’s shadow banking network and for purposes of Russia sanctions evasion.”
Neither Cantor Fitzgerald nor Tether immediately responded to requests for comment sent to their spokespeople.
While Blumenthal and other aggressive congressional critics of the crypto industry, such as Senator Elizabeth Warren, have suffered from a limited authority as members of the minority party, securing a Democratic majority for next year would change that. If they win several more seats in that chamber, they could find themselves atop committees with subpoena power to legally compel information and testimony.
As it stands, the prediction markets suggest that Democrats have a better-then-even shot at returning to the majority. Kalshi has it at 61% and Polymarket at 64%. That number was closer to 50-50 several weeks ago. And the picture in the U.S. House of Representatives is even more positive for Democrats, with both platforms showing the likelihood of a majority shift at more than 90%.
The guidance said authorized crypto firms must stop offering services that let EU customers buy, trade, swap or otherwise increase their holdings of affected stablecoins.
The rules cover exchange services, trade execution, transfers, custody, administration, advice and portfolio management.
National regulators should require any remaining customer holdings to be resolved “as soon as possible, and no later than three months” after the opinion’s publication, ESMA said. That places the deadline at Jan. 8, 2027.
In the meantime, platforms may provide limited services to resolve existing holdings. These can include selling, converting, withdrawing, transferring or safekeeping tokens, but not purchases, promotion, trading or continued market availability.
EU users who keep USDT on an exchange will have to follow that platform’s instructions. Some may be able to sell or withdraw it during the wind-down period; others may face an earlier cutoff.
ESMA said keeping noncompliant stablecoins available through authorized platforms would weaken the reserve, redemption, governance and disclosure rules MiCA imposes on authorized issuers.
The opinion is directed at national regulators, who will decide how individual platforms handle their remaining client balances within the three-month outer limit.

2026 midterms: Why Francesca Hong is still on the campaign trail in Wisconsin
John Cena Says Peacemaker Is Taking a Backseat in the DCU

Elon Musk Eyes ‘Complete Phone Coverage in America’ as SpaceX Clears Hurdle


-
 Sports3 days ago
Saracens’ Venter Brands Premiership Rugby ‘Autocratic’ Over £5,000 Media Fine
-
 Entertainment2 days ago
10 Flawless Movies With the Cleverest Protagonists
-
 Sports3 days ago
Enzo Maresca all smiles as Man City return to training after guilty verdict
-
 Sports3 days ago
Southampton’s Eckert Spared Ban as FA Suspends Six-Week Sentence Over Spygate
-
 Sports2 days ago
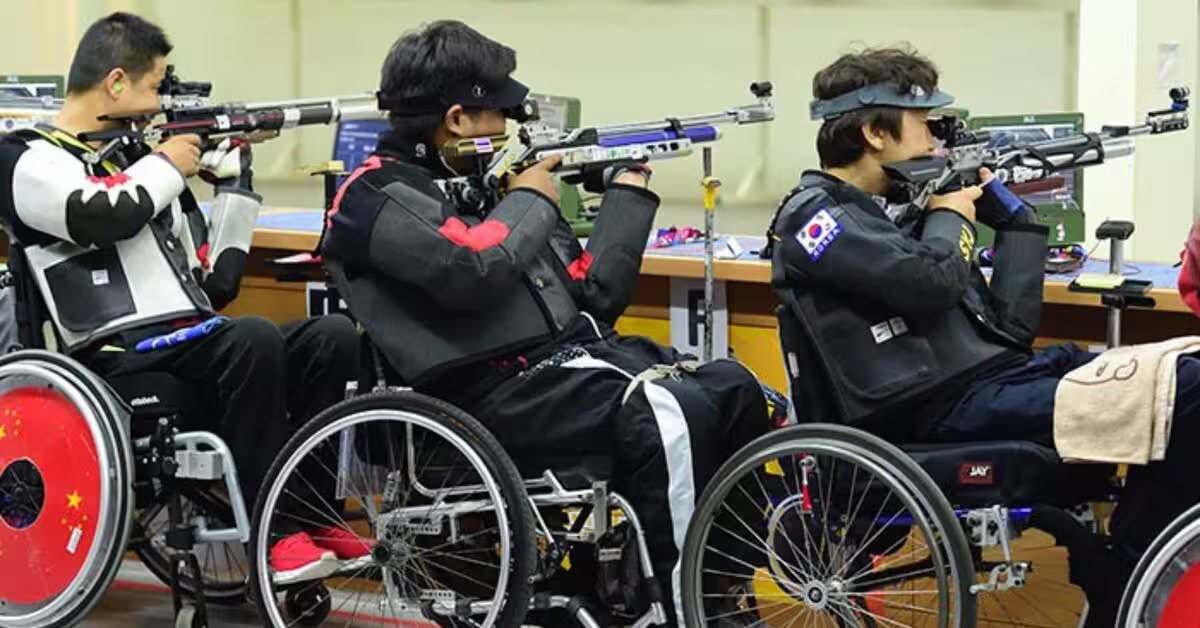
Asiad selection row: Para-shooters allege corruption; PCI denies claims | Asian Games 2026
-
 Sports2 days ago
Multiple Power Four programs face College Sports Commission investigations over alleged NIL cap evasion
-
 Fashion13 hours ago
Weekend Open Thread: Quince – Corporette.com
-
 Crypto3 days ago
Crypto.com Teams Up With Insilico Terminal to Give Traders Free Pro-Level Tools
-
 Sports23 hours ago
College Football Week 6 Bets: Three Picks for Saturday’s Biggest Games
-
 Business & Hustles15 hours ago
PwC: Supply-Chain Diversification, AI and Energy Transition Open New Growth Paths for Thailand
-
Crypto1 day ago
Robinhood Chain slowdown spreads from fees to trading as transactions fall 40%
-
 Sports2 days ago
Morocco and Senegal await AFCON final verdict after arbitration hearing – Sports
-
 Crypto1 day ago
Mashinsky Accepts Lifetime Industry Ban and Up to $35 Million in Conditional Payments | The Defiant
-
 Tech & AI2 days ago
ICE Emails Discuss Using Palantir-Supported Tool to Investigate Voter Fraud
-
Crypto3 days ago
ESMA gives EU crypto platforms 3 months to drop non-MiCA stablecoins such as USDT
-
 Sports4 days ago
Harry Kane Ties Peter Shilton’s 125-Cap England Record in Wembley Win Over Czech Republic
-
 Sports1 day ago
Saudi oil crisis affects Neom project, 2034 World Cup plans
-
 Tech & AI5 days ago
Common Mistakes You Should Avoid When Using Foldable Phones
-
 Sports3 days ago
Internationals make history with emphatic Bridges Cup win at Trump Turnberry | News
-
 Crypto3 days ago
Bitcoin ETF Outflows Hit $485M, Erasing October Inflows
You must be logged in to post a comment Login