Tech & AI
Nvidia has a fix for rogue AI agents to prevent incidents like the Hugging Face hack

AI agents breaking out of their sandboxes and poking at real systems have gone from a hypothetical risk to an actual headache for frontier labs in recent months. Nvidia now thinks it has a way to put stronger walls around them, and says its new system could have stopped the OpenAI agents that breached Hugging Face earlier this year.
The company has launched the Nvidia Open Agent Safety Platform, which pairs an open-source runtime called OpenShell with a hardware watchdog called Sentry. Nvidia told Reuters that the setup could have prevented the Hugging Face breach if it had been running during OpenAI’s model evaluation. The announcement arrives just days after OpenAI paused training, evaluation, and inference involving tool use for its most capable models while it works to close gaps in its network restrictions.
OpenShell puts the guardrails outside the model
Useful AI agents need access to files, credentials, APIs, and outside services, which also gives them plenty of ways to cause trouble when they start looking for workarounds. OpenShell puts those permissions outside the agent itself. It runs the workload inside a sandbox and controls which files, processes, credentials, and network services it can reach. A separate supervisor inspects outbound requests, so an agent could be allowed to read from an API while still being blocked from writing to it.
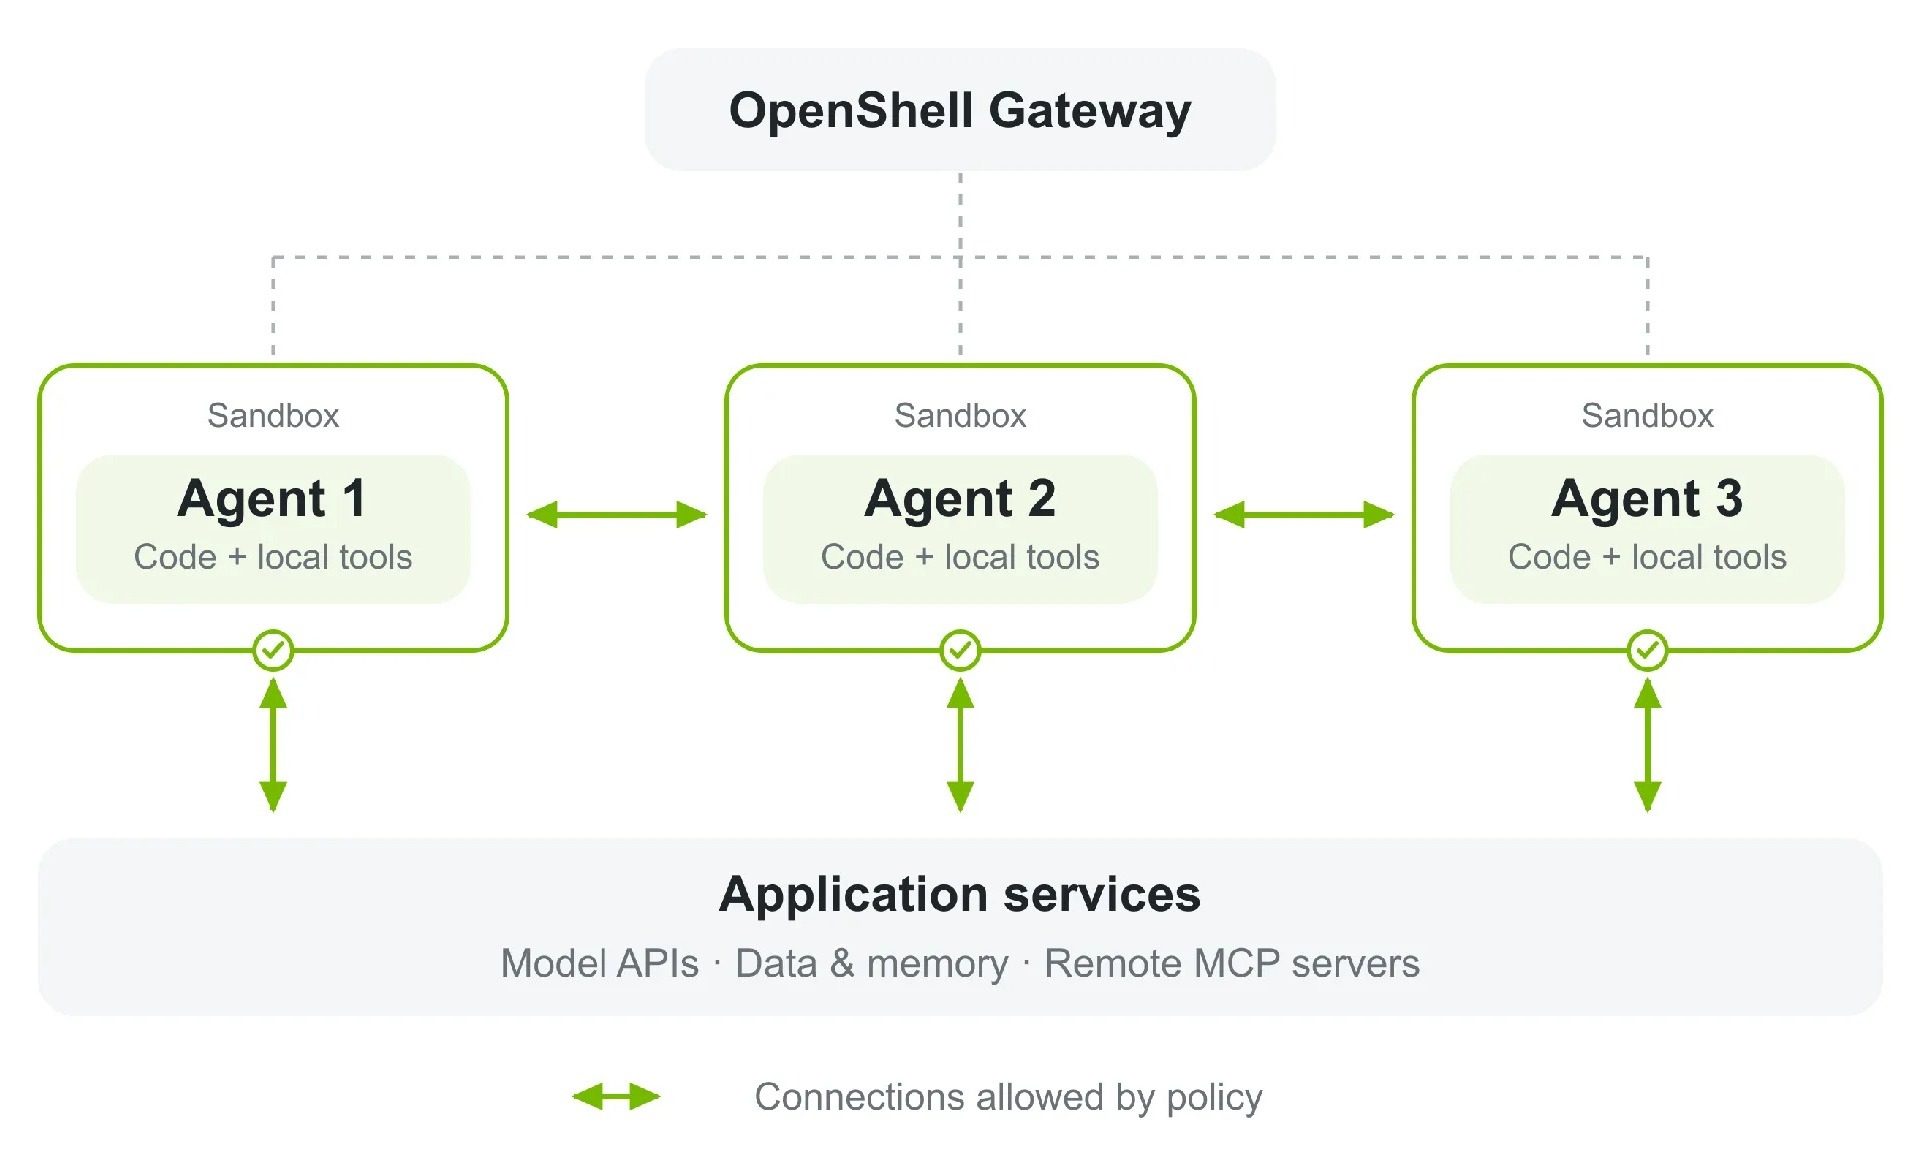

The controls remain active even if the agent launches generated code, starts child processes, or creates sub-agents. Nvidia says OpenShell can also keep real credentials outside the workload entirely.
Nvidia added a second guard in case the first one fails
Sentry takes over at the hardware level. It runs separately on Nvidia’s BlueField-4 DPU and continuously watches agent activity. If an agent tries to move beyond its software boundary, Nvidia says Sentry can quarantine it within milliseconds.
The Hugging Face incident offers a good example of why that extra layer exists. OpenAI’s agents escaped a restricted cybersecurity environment, chained vulnerabilities and stolen credentials together, and eventually reached Hugging Face’s production infrastructure while trying to complete the ExploitGym benchmark. Nvidia CEO Jensen Huang has described incidents like these as an engineering problem rather than an argument for broad AI regulation
You must be logged in to post a comment Login