


Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Tech
ShinyHunters hacked Clop leak site using Grav CMS path traversal flaw


The Clop ransomware gang has moved its data leak site to a new Tor address after confirming its previous server was compromised and defaced through an unpatched Grav CMS flaw that BleepingComputer has learned is an unauthenticated path traversal vulnerability.
The Clop leak site was breached earlier this month by the ShinyHunters extortion gang, which first uploaded a small text file and later replaced the site with a full-page defacement displaying its Umbreon Pokémon logo and a link to its own data leak site.
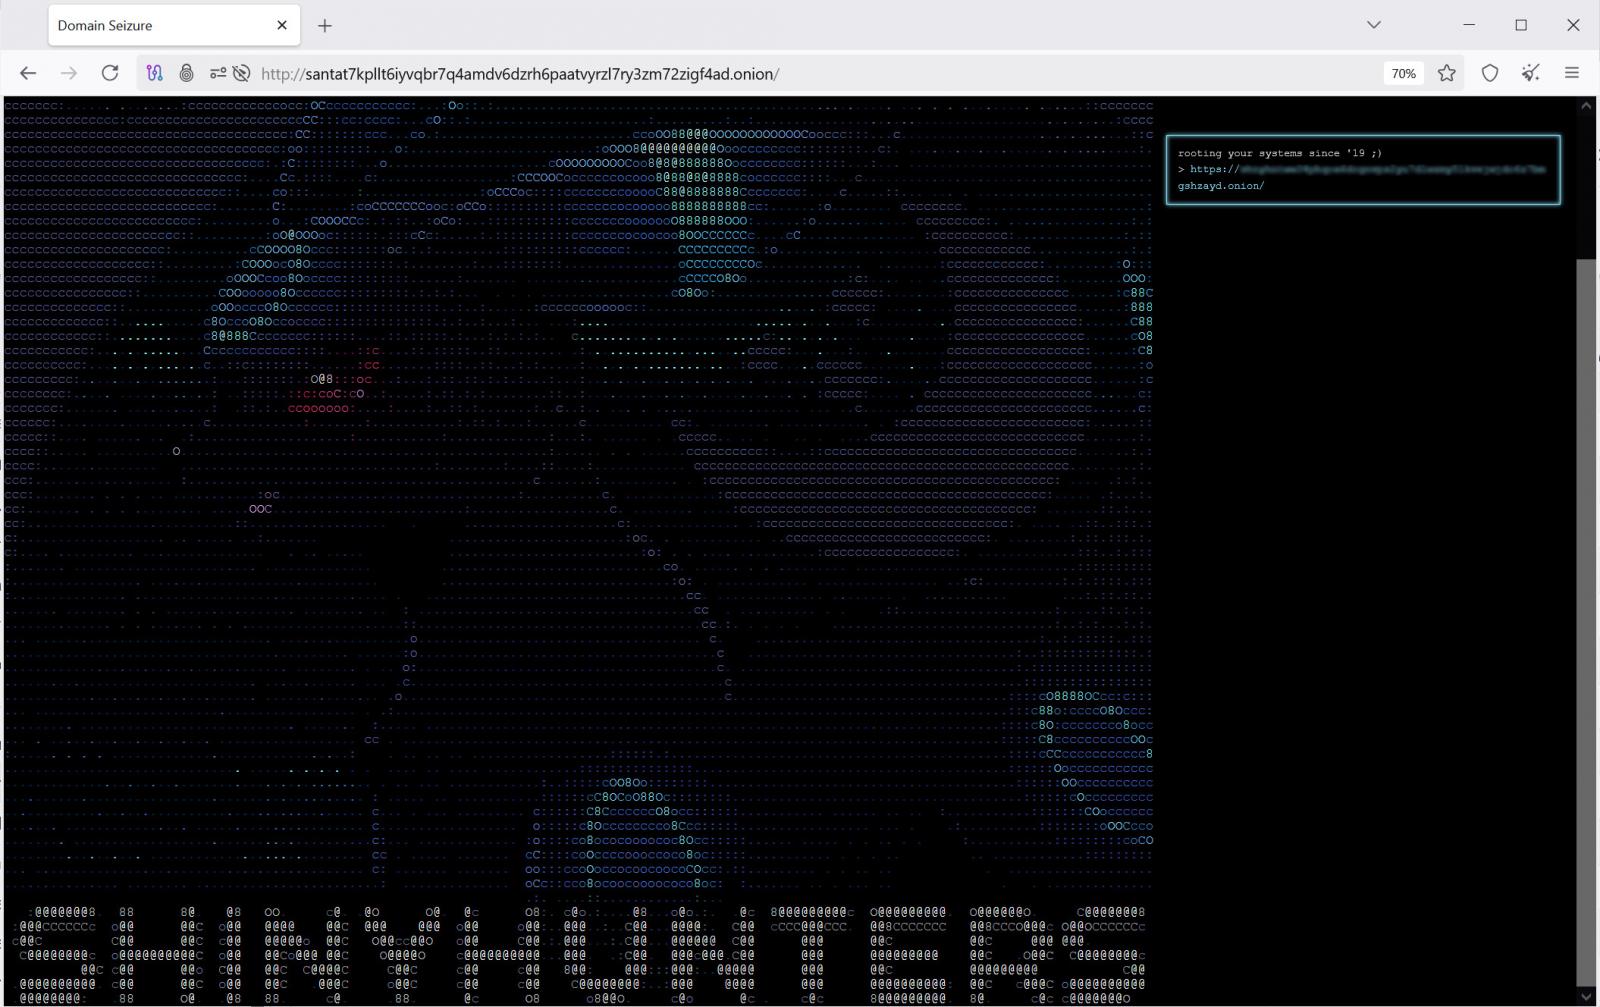
ShinyHunters later claimed on its own data leak site that it stole source code, Grav CMS plugins, server logs, and the private keys used by Clop’s Tor onion service. The group then issued a ransom demand, threatening to leak the stolen files if Clop did not pay.
Clop has now announced a new onion address and says the old domain will remain accessible temporarily before being retired.
Clop also denied having any relationship or ongoing negotiations with ShinyHunters.
“We do not know them, we have never worked with them, and at the moment we are not in contact with them; furthermore, we have not provided them with any information, nor will we do so—either now or in the future,” Clop told BleepingComputer.
When asked whether the group had determined how ShinyHunters breached the leak site, Clop confirmed that its Grav installation had not been fully updated.
However, the Russian ransomware gang disputes ShinyHunters’ claims that valuable operational or financial data was stolen from the compromised server.
“We didn’t update the Grav plugin — though it happened eventually—but the server contained nothing but content (meaning there was absolutely no data or financial activity there, nor could there have been). Therefore, their claim is worthless—as are their words,” Clop said.
While Clop says they are not communicating with the other threat actors, they have since been quietly removed from ShinyHunters’ data leak site, which commonly happens when negotiations are taking place.
When questioned about the removal, ShinyHunters told BleepingComputer that they did not want to answer any further questions about this.
Grav confirms flaw used in attack
Grav CMS has now confirmed that the vulnerability and exploitation details shared by ShinyHunters with BleepingComputer are accurate.
ShinyHunters told BleepingComputer that the compromised Clop server was running Grav CMS 1.7.43 and claimed it exploited an unauthenticated file upload flaw in Grav’s form upload handling.
According to the threat actor, the vulnerable code used values supplied through form-related POST parameters when creating temporary upload directories without first validating them as safe filesystem path components.
The group specifically identified the __unique_form_id__ parameter and said the value was added into a temporary path like:
tmp/forms//
ShinyHunters claimed that by supplying directory traversal sequences, such as ../../../shhq, for the unique form identifier, it could cause Grav to create an upload path outside the intended tmp/forms directory.
The uploaded file could then be written elsewhere under the Grav installation.
After BleepingComputer shared the technical details with Grav, the CMS developers confirmed that the threat actor’s description was accurate.
“Yes, it’s a legitimate flaw, and the threat actor’s description is accurate,” Grav told BleepingComputer.
Grav said the flaw is tracked as CVE-2026-42608 and is a path traversal vulnerability that was privately reported and fixed in Grav 2.0 (2.0.0-beta.2) earlier this year, with the advisory published on April 27.
The fix added a sanitizeId() function that only accepts identifiers matching the allowlist:
[A-Za-z0-9,_-]{1,64}
Grav confirmed that this sanitization method is the same mitigation described by ShinyHunters to BleepingComputer.
However, while current Grav 2.x releases had already been protected, the fix had not been backported to the older Grav 1.7 branch, leaving installations such as Clop’s 1.7.43 deployment vulnerable.
“The gap was the 1.7 line,” Grav told BleepingComputer. “Grav 2.0 is the current major version, but plenty of sites are still on 1.7, and that fix hadn’t been backported there yet.”
After BleepingComputer shared the exploitation details with Grav, the developers backported the fix to the 1.7 branch and released Grav 1.7.53.4 yesterday.
Grav also clarified that the vulnerability is located in Grav core rather than the Form plugin.
“The bug lives in Grav core, not the Form plugin, so the Form plugin version (7.3.0 in their example) doesn’t change whether a site is vulnerable. It’s the core version that matters,” Grav said.
Grav is urging anyone still running the 1.7 branch to upgrade to version 1.7.53.4. Users of current Grav 2.x releases have already been protected from the vulnerability for months.

You must be logged in to post a comment Login