Cybersecurity has a fundamental blind spot. We spend enormous sums protecting software while the processor underneath it blindly executes whatever instructions it receives. That has to change. For the billions of embedded systems running cars, medical devices, industrial controllers, network equipment, and critical infrastructure, security needs an independent layer that can watch processors execute instructions.
The stakes are already visible. The United States recorded 3,322 reported data breaches in 2025, a record high. Cyberattacks accounted for 80% of them. These numbers do not tell us that every defense has failed, but they do tell us something important: adding more security products has not made the underlying problem disappear.
I have spent decades building technology, and one lesson keeps returning: when a system repeatedly fails in the same place, adding another layer around it is not necessarily progress. Sometimes you have to move the security boundary.
Today, that boundary is overwhelmingly software. We deploy firewalls, endpoint protection, intrusion detection, vulnerability scanners, sandboxes, monitoring systems, and countless other tools. They are valuable. But every software defense is itself software, and software contains bugs. We are often asking vulnerable software to protect vulnerable software.
Advertisement
That creates another problem: noise. A network operation center can receive thousands of alerts in a day. Some are genuine threats. Others are harmless. When defenders cannot reliably distinguish between them, they eventually face the same problem doctors faced during the early days of COVID-19 testing: a test that produces too many false alarms becomes less useful, even when the underlying science is sound.
The better question is: Is the machine actually doing what it is supposed to?
A processor executes instructions at extraordinary speed, but traditionally it has no understanding of whether those instructions are legitimate. If an attacker exploits a software vulnerability, the processor may execute the malicious instructions just as obediently as the legitimate ones.
Imagine instead an independent hardware layer watching those instructions as they execute. It could enforce rules about what the software is allowed to do. A buffer overflow could still exist in the underlying code, but the processor could stop the resulting prohibited behavior before it becomes an exploit.
Advertisement
That is fundamentally different from asking another piece of software to detect the attack after the fact. Hardware cannot be remotely rewritten in the same way software can. It can provide a security boundary that does not depend on every line of code being perfect.
And there is a useful side effect. This kind of oversight can expose bugs before the system is deployed in the field. During normal operation, a system could identify behavior that violates its rules and give developers evidence of a vulnerability they did not know existed. Security becomes part of the software development process rather than merely an emergency response mechanism.
We desperately need that backstop because memory-safety vulnerabilities, such as buffer overflow, remain stubbornly common. According to CISA, Microsoft has reported that roughly 70% of its annually assigned CVEs are memory-safety issues, while Google has reported a similar proportion among serious Chromium security bugs. CISA also points out that these problems persist despite years of fuzzing, static analysis, sandboxing, and other testing techniques.
This matters even more as AI accelerates both sides of the fight. In February 2026, Anthropic reported that Claude Opus 4.6 had helped identify and validate more than 500 high-severity vulnerabilities in open-source software. The same capability that gives defenders unprecedented visibility can give attackers unprecedented speed. Anthropic warned that AI models are already capable of identifying novel vulnerabilities and that the traditional time available for disclosure and remediation may no longer be sufficient.
Advertisement
Verizon’s 2026 Data Breach Investigations Report makes the urgency even clearer. Vulnerability exploitation became the leading initial access vector, responsible for 31% of breaches in its dataset. Verizon also reported that AI is helping attackers accelerate the exploitation process.
The future can go one of two ways.
Processors become active participants in security. Embedded systems can continue operating even when software contains flaws. Developers get continuous evidence about weaknesses. Manufacturers build devices that are harder to exploit. Cars, medical equipment, industrial machinery, and connected infrastructure become more trustworthy because the security boundary sits closer to the point where code becomes action.
The alternative is darker. We keep piling software defenses onto increasingly complex software stacks while attackers use AI to find weaknesses faster than humans can patch them. The attack surface grows, alerts multiply, and the code controlling physical systems becomes harder to trust. Eventually, the gap between discovering a vulnerability and exploiting it becomes shorter than our ability to respond. The implementation of oversight not only protects your applications, but it protects your cyber defense systems, making them able to do their jobs effectively.
Advertisement
We should not wait for that darker future to arrive.
Memory-safe languages, better development practices, testing, patching, and conventional cybersecurity all matter. Hardware oversight does not replace them. It gives them a backstop.
So the next time you evaluate an embedded platform, a connected device, or technology that will control something in the physical world, ask a harder question than “How secure is the software?” Ask: “What is watching the processor when the software fails?”
This article is written on an open-source operating system, but not an open-source machine — the BIOS isn’t open-source, and even if it were supported by the coreboot project (formerly LinuxBIOS), there would still be a whole host of binary blobs required to get it to boot. On one vintage architecture, there’s one less blob, as coreboot can now initialize DRAM on Intel Bay Trail SOCs, as [Mate Kukri] presented in a talk at the recent Open Source Firmware Conference.
Bay Trail isn’t exactly cutting-edge hardware, to be sure — the SoCs are over a decade old at this point, and were only used in low-performance mobile applications like Chromebooks. On the other hand, coreboot has been on Chromebooks for at least as long. Getting DRAM set up is difficult because, well, you don’t have any memory to work with until you do. Traditionally, the way you did that was to call on one of the many proprietary ‘binary blobs’ provided with next to no documentation by the manufacturer. Reverse engineering that requires some serious bus-sluthing, which was done in software with the SerialICE debugger and the Unicorn Engine CPU emulator. The talk focused on that technique and how it might be applied more widely, rather than getting into the weeds of how to do DRAM init on one obsolete SOC. At some point the whole thing should be archived on the OFSC website so those of us not lucky enough to attend in person can hear what [Mate] — and all the other speakers — had to say.
Because coreboot is open, you can do a lot more with it than a proprietary UEFI firmware — for example, you can choose not to initialize RAM at all, and run entirely in the CPU’s cache. You can also — of course — run DOOM. If you want to be binary-blob-free, you’ll need to find hardware supported by the more hardcore Libreboot distribution of coreboot, which admits no binary blobs at all. When it comes to Libreboot, it might actually be easier to install than to find compatible hardware these days.
The initiative aims to ‘position Ireland as a leading testbed for insurance innovation by connecting emerging companies directly with insurers, industry experts, investors and experienced founders’.
12 Ireland-based insurance technology start-ups will participate in the second edition of InsTech.ie’s Foundry, a pre-accelerator programme run in partnership with Furthr, one of the country’s four Business Innovation Centres.
InsTech.ie is a national body that aims to connect start-ups, insurers, investors and policymakers to accelerate innovation and help Irish insurtech companies scale globally.
It is supported by 24 insurance industry members, tracks more than 120 Irish insurtech companies, and has eight innovation partnerships, including with IDA Ireland, KPMG and Enterprise Ireland.
Advertisement
The Foundry initiative is designed to create a direct route between established insurance expertise and younger or smaller companies developing technologies capable of shaping the insurance sector’s future, according to InsTech.ie.
The programme aims to “position Ireland as a leading testbed for insurance innovation by connecting emerging companies directly with insurers, industry experts, investors and experienced founders”, according to its operator.
“The first Foundry cohort showed what can happen when ambitious founders are given direct access to the insurance expertise, networks and decision-makers that can help turn promising ideas into commercially viable businesses,” said Gary Leyden, CEO of InsTech.ie.
“With cohort two, we want to build on that momentum and give another group of companies the opportunity to validate their solutions, develop meaningful industry relationships and accelerate their path to market.
Advertisement
“Ireland has a unique combination of insurance expertise and technology talent, and the Foundry is about bringing those two strengths together.”
The 12 selected companies, and their technological offerings, are:
Alteric AI
An AI orchestration layer for commercial brokerages to automate workflows across servicing, renewals, claims and new business.
Fairwrite
A start-up aiming to make life and protection insurance more inclusive for people with mental health conditions, disabilities or neurodivergence through a more individualised approach to underwriting.
Advertisement
Finch AI Systems/LitAgent
An explainable AI platform to support personal-injury reserving and settlement valuation, producing consistent, traceable assessments while keeping the final decision with the claims professional.
Global Nutrition Value
This company is creating a time-stamped evidence trail for food safety and compliance data with applications across underwriting, loss prevention, claims and product recalls.
Insurteam MGA
A start-up creating a solution that combines embedded travel insurance distribution with AI-enabled claims handling, allowing partners to offer cover at checkout and customers to manage claims through WhatsApp.
Maximo
A platform connecting pensions, tax and open banking to help consumers better understand and increase their pension contributions and access associated tax relief.
Advertisement
Model Library/Elliptic
This start-up is developing a climate-risk modelling platform to help insurers and other risk-transfer providers understand and quantify basis risk in parametric insurance.
RMI Agentic
A solution designed for managing risks created when autonomous AI agents transact on behalf of consumers.
SeatFair Technologies
This start-up is exploring how preference-pricing and optimisation technology could support complex reinsurance placements involving price, capacity, counterparties and terms.
TalkTerms AI/Swift Settle
An AI decision-support platform designed to help insurance professionals manage complex claims and complaints while retaining human oversight.
Advertisement
Vardus
A pre-send compliance platform that checks customer communications, identifies potential regulatory issues and provides greater oversight of recurring compliance risks.
Voxalytics
This start-up’s solution analyses broker-client calls to automate administration and identify portfolio-level signals around customer retention, churn, cross-sell and growth.
Don’t miss out on the knowledge you need to succeed. Sign up for the Daily Brief, Silicon Republic’s digest of need-to-know sci-tech news.
Tonight’s UFC 331 headline bout is a classic case of revenge or repeat as Joshua Van puts the UFC flyweight title he won against Alexandre Pantoja on the line at the Crypto.com Arena in Los Angeles. The Fearless won the belt in controversial fashion in December 2025 and the Cannibal is determined to right the wrong he has felt ever since.
Van’s victory at UFC 323 came after Pantjoa suffered a dislocated elbow 26 seconds into the original fight when the former fell and landed on the latter. The Brazilian has felt ignored by Dana White ever since, despite having championship victories against Brandon Moreno, Brandon Royval, Steve Erceg, Kai Asakura, and Kai Kara-France on his resumé. The 36-year-old has the experience and fuel from that defeat to inspire him. He’ll become the third flyweight champion to regain the belt after Moreno and Deiveson Figueiredo if he wins.
Myanmar native Van is well known for his speed but it was the striking that got him over the line against Tatsuro Taira in his solitary title defense in May. The 24-year-old will need to use that aggressive approach if he’s to back that up against another 5ft 5in fighter. This is sure to be a close fight and one not to be missed.
Advertisement
That’s the main event of a stacked card in which Arman Tsarukyan and Maurício Ruffy face off at lightweight with the winner likely to get a future title shot.
Here’s where to watch UFC 331 live streams online and from anywhere with a VPN – including a clever way to watch UFC 331 for just $1.
How to watch UFC 331 live stream in the US
Exclusive US coverage of the full UFC 331 event is on Paramount Plus. It’s being headlined by Joshua Van vs Alexandre Pantoja 2, which is expected to start at around 11pm ET / 8pm PT.
Advertisement
Plans start from only $8.99/month with the Paramount Plus Essential Plan, or you can upgrade to Premium for $13.99/month (see below for more details). You can also get a Paramount Plus trial with Walmart+ for $1 using this sneaky trick we found.
While Paramount Plus will show UFC 331 in its entirety, you can also watch the Early Prelims via UFC Fight Pass.
Away from home at the moment and blocked from watching UFC on your usual subscription?
You can still watch Van vs Pantoja 2 live thanks to the wonders of a VPN (Virtual Private Network). The software can make your devices appear to be back in your home country regardless of where you are, making it ideal for viewers away on vacation or on business. One of our favorites is Surfshark – we explain why in our Surfshark review.
It’s really straightforward to use a VPN to watch UFC 331.
Advertisement
1. Install the VPN of your choice. As we’ve said, SurfShark is our favorite.
2. Choose the location you wish to connect to in the VPN app. For example, if you want to watch the Paramount+ stream, select ‘United States’ from the listed countries.
3. Sit back and enjoy the action. Head to Paramount+ and tune into UFC 331.
Advertisement
How to watch UFC 331 live stream in the UK
The UFC 331 main card is available on TNT Sports 1 in the UK. It’s set to begin at 2am BST in the early hours of Sunday morning.
You can get it by adding TNT Sports to your Sky, Virgin Media or EE TV package, or pay from £25.99 per month for a HBO Max plan that includes TNT Sports.
UFC Fight Pass subscribers can also watch the Prelims and Early Prelims.
If you’re abroad whilst the MMA live stream is on, a VPN like Surfshark can help you to access your home streaming services from anywhere.
Advertisement
How to watch UFC 331 live stream in Canada
There are a host of pay-per-view providers offering a UFC 331 live stream in Canada.
You can head to the likes of Sportsnet, Bell or the UFC Fight Pass to watch the whole event, where the PPV price is set at $69.99. Prelims will also be shown on Sportsnet and TVA Sports, with Early Prelims also on UFC Fight Pass.
North of the border from the US? You can use Surfshark to watch your Paramount Plus subscription like you were back at home.
That means you can live stream UFC 330 via your web browser and devices like Android, iOS, Samsung TV, Apple TV, Android TV, Telstra TV and Chromecast.
You can also catch all the Prelims (but not the Van vs Pantoja 2 main event) via Paramount+ and free-to-air Network 10.
Advertisement
Downloading a VPN will help you access your subscriptions from anywhere if you’re abroad when the fight is on.
Can I watch UFC 331 for free?
Not quite. Other than the sneaky little Walmart+ for $1 trick described above in the US, there doesn’t seem to be any way to watch UFC 331 for free. It’s on Paramount Plus in the US, which no longer carries a free trial. And it’s a PPV in many other countries around the world.
When does UFC 331 start?
The UFC 331 Main Card is scheduled to begin at 9pm ET / 6pm ET on Saturday, September 19. That’s 2am BST or 11am AEST in the UK and Australia on Sunday, September 20.
Before that, the Early Prelims start at 5pm ET / 2pm PT / 10pm BST / 7am AEST (Sun) and the Prelims at 7pm PT / 4pm PT / 12am BST (Sun) / 9am AEST (Sun).
Advertisement
Can I watch UFC 331 on my mobile?
Yes. Most broadcasters have streaming services that you can access through mobile apps or via your phone’s browser – Paramount Plus, HBO Max and Kayo Sports all have mobile apps, for example.
You can also stay up-to-date with the latest UFC news and plays on the official social media channels on X (@ufc), Instagram (@ufc), Facebook (UFC) TikTok (@ufc) and YouTube (@ufc).
UFC 331 full card
Main card Joshua Van (c) vs Alexandre Pantoja (Flyweight) Arman Tsarukyan vs Maurício Ruffy (Lightweight) Patrício Pitbull vs Choi Doo-ho (Featherweight) Gable Steveson vs Sean Sharaf (Heavyweight) Alonzo Menifield vs Iwo Baraniewski (Light Heavyweight)
Advertisement
Prelims Marlon Vera vs Charles Jourdain (Bantamweight) Tai Tuivasa vs Robelis Despaigne (Heavyweight) Michael Aswell Jr vs Yoo Joo-sang (Featherweight) Ryan Gandra vs Osman Diaz (Middleweight)
Early prelims Edmen Shahbazyan vs Brunno Ferreira (Middleweight) Casey O’Neill vs Eduarda Moura (Women’s Flyweight) Giga Chikadze vs Joanderson Brito (Featherweight)
We test and review VPN services in the context of legal recreational uses. For example: 1. Accessing a service from another country (subject to the terms and conditions of that service). 2. Protecting your online security and strengthening your online privacy when abroad. We do not support or condone the illegal or malicious use of VPN services. Consuming pirated content that is paid-for is neither endorsed nor approved by Future Publishing.
Most people use the glasses normally, he said, much as they would a phone camera, only more convenient and more hands-free. He pointed to the indicator light and the anti-tampering measures that stop recording when it is covered.
The first defence is probably true and does not answer the question
Almost certainly most wearers are doing nothing objectionable. That is true of most technologies and it has never been the test for a device carried through public space.
The phone comparison is where the argument gives itself away. A raised phone is a visible act that the person opposite can see and respond to, and the entire selling point of the glasses is that recording no longer looks like anything.
Advertisement
More in the moment is the same property as harder to notice. The convenience and the problem are one feature.
The second defence has already failed in public
The recording light is the mechanism Meta has staked its answer on, and it has been closing holes in it all year. A software update stopped a loophole where a wearer could start recording, wait, then cover the light, and it bricked cameras on units where the light had been drilled out.
That enforcement was real and it was not small. Meta described the action as covering fewer than one in a thousand glasses ever sold, which on seven million pairs in a year is a great many devices.
The Information reported this week that Meta is preparing a camera-free version of the glasses, codenamed Luna, with six microphones and no camera at all. TNW covered the report, which points to an unveiling at Connect on 23 September and shipments in October.
Companies do not remove the defining feature of a product to placate a small number of bad actors. They remove it when the category has a perception problem they cannot moderate their way out of.
Bosworth said at the end of the AMA that there is more to say at Connect. That is five days after he said the discourse had been captured by a fringe.
What Luna would actually change
Taking the camera out addresses the bystander problem directly, and that is a real answer rather than a cosmetic one. It also removes the thing most people buy the glasses for.
Advertisement
Six microphones is not nothing, though. The visual privacy question would be solved and replaced by an audio one, and there is no equivalent of the recording light for a microphone.
Nobody has established a convention for signalling that a face-worn device is listening. Luna would ship into that gap.
Norway is weighing restrictions on camera-equipped wearables. Hamburg’s data protection commissioner has suggested the glasses may already fall foul of German rules on concealed recording equipment.
The moderation record is mixed by its own reporter’s account
Bosworth said harassing content will be removed and accounts taken down where the behaviour is systematic. Business Insider, which examined how the policy was working over the summer, found the moderation uneven.
The targeting has also been narrow. Videos of men harassing women have drawn action, while prank clips tormenting retail workers have been reported as a growing problem.
If the market leader ships a camera-free model this autumn, that becomes the reference point for everyone still deciding. The bad actors framing looks weaker every week the roadmap moves the other way.
What to watch
Watch Connect on 23 September. If Luna appears without a camera, the product has conceded what the AMA did not.
Watch what Meta says about the microphones. A camera-free device that listens continuously needs its own indicator, and the company has not proposed one.
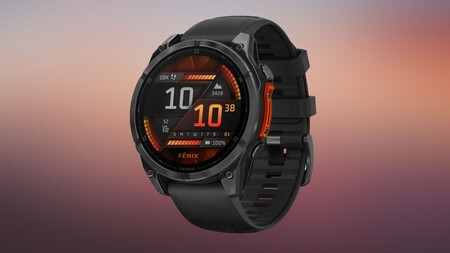
Multisport watches with this depth of training data rarely fall under a thousand dollars, so shaving $250 off the fenix 8 lands it firmly in genuine impulse buy territory for serious athletes today.
Advertisement
Strap it on, and you get a built-in LED flashlight, leakproof metal buttons and a 40-metre dive rating, the kind of rugged spec sheet you would expect from whatever tops a best Garmin watch 2026 buying guide.
The fenix 8 also handles training the way a proper coach would, breaking down recovery and readiness scores each morning based on your sleep, heart rate and recent workload. It even builds targeted strength training plans and sport-specific workouts, so the guesswork of programming your own week disappears entirely.
Advertisement
That same attention to detail carries over to navigation, with built-in ABC sensors and preloaded TopoActive maps plotting dynamic round-trip routes that guide you back to your exact starting point right on schedule every time.
Advertisement
All of it runs on a battery that Garmin rates at up to 16 days in smartwatch mode, which is more than enough for a full week away from home without hunting for a charger.
A built-in speaker and microphone let you take calls straight from your wrist once paired to a phone, while Garmin Pay and onboard music storage mean you can leave the phone behind entirely on a run.
Even at $749.99, the fenix 8 still packs dive certification, weeks of battery life and real coaching smarts into a single rugged watch that costs a full $250 less than its usual asking price.
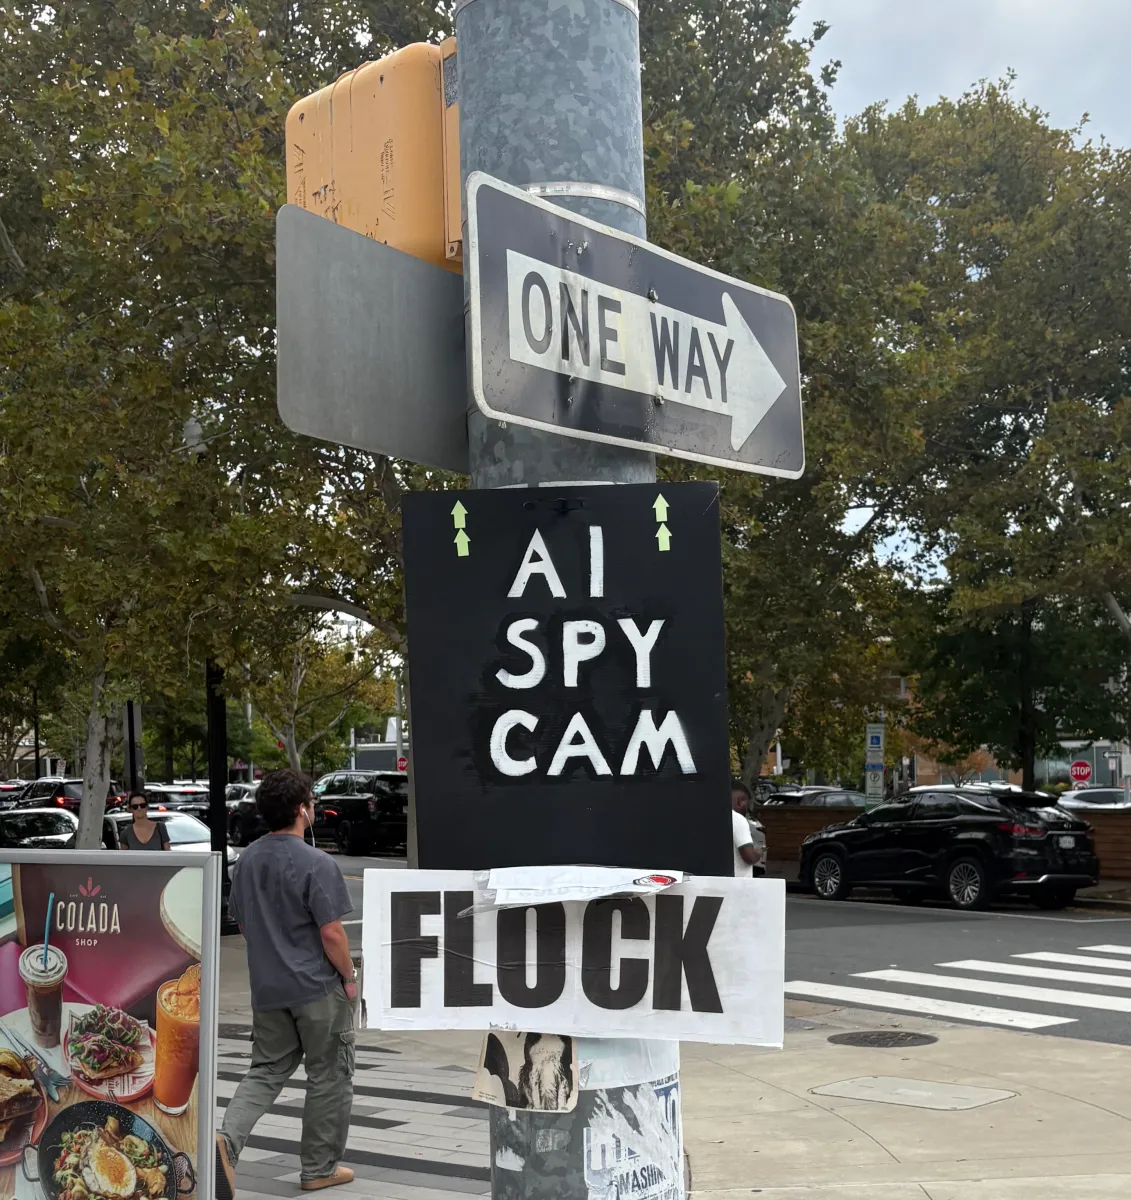
Embattled surveillance technology company Flock Safety unveiled a “generous” severance package for voluntary employee departures on Friday, according to a report in Wired.
Flock reportedly expects a significant portion of its 1,500-person workforce to express interest in the buyouts, and said it will grant them to a majority of those who are interested. The company’s internal announcement described these packages as the “most generous” it has ever offered.
By letting employees depart voluntarily, Flock can say goodbye to team members demoralized by the ongoing backlash over the company’s license plate recognition technology. Wired also reports that without buyouts, the company would “almost certainly” need to lay off some staff.
TechCrunch has reached out to Flock for comment. The startup’s CEO Garrett Langley recently told the All-In podcast that the “biggest damage” caused by the backlash has been to “internal morale.”
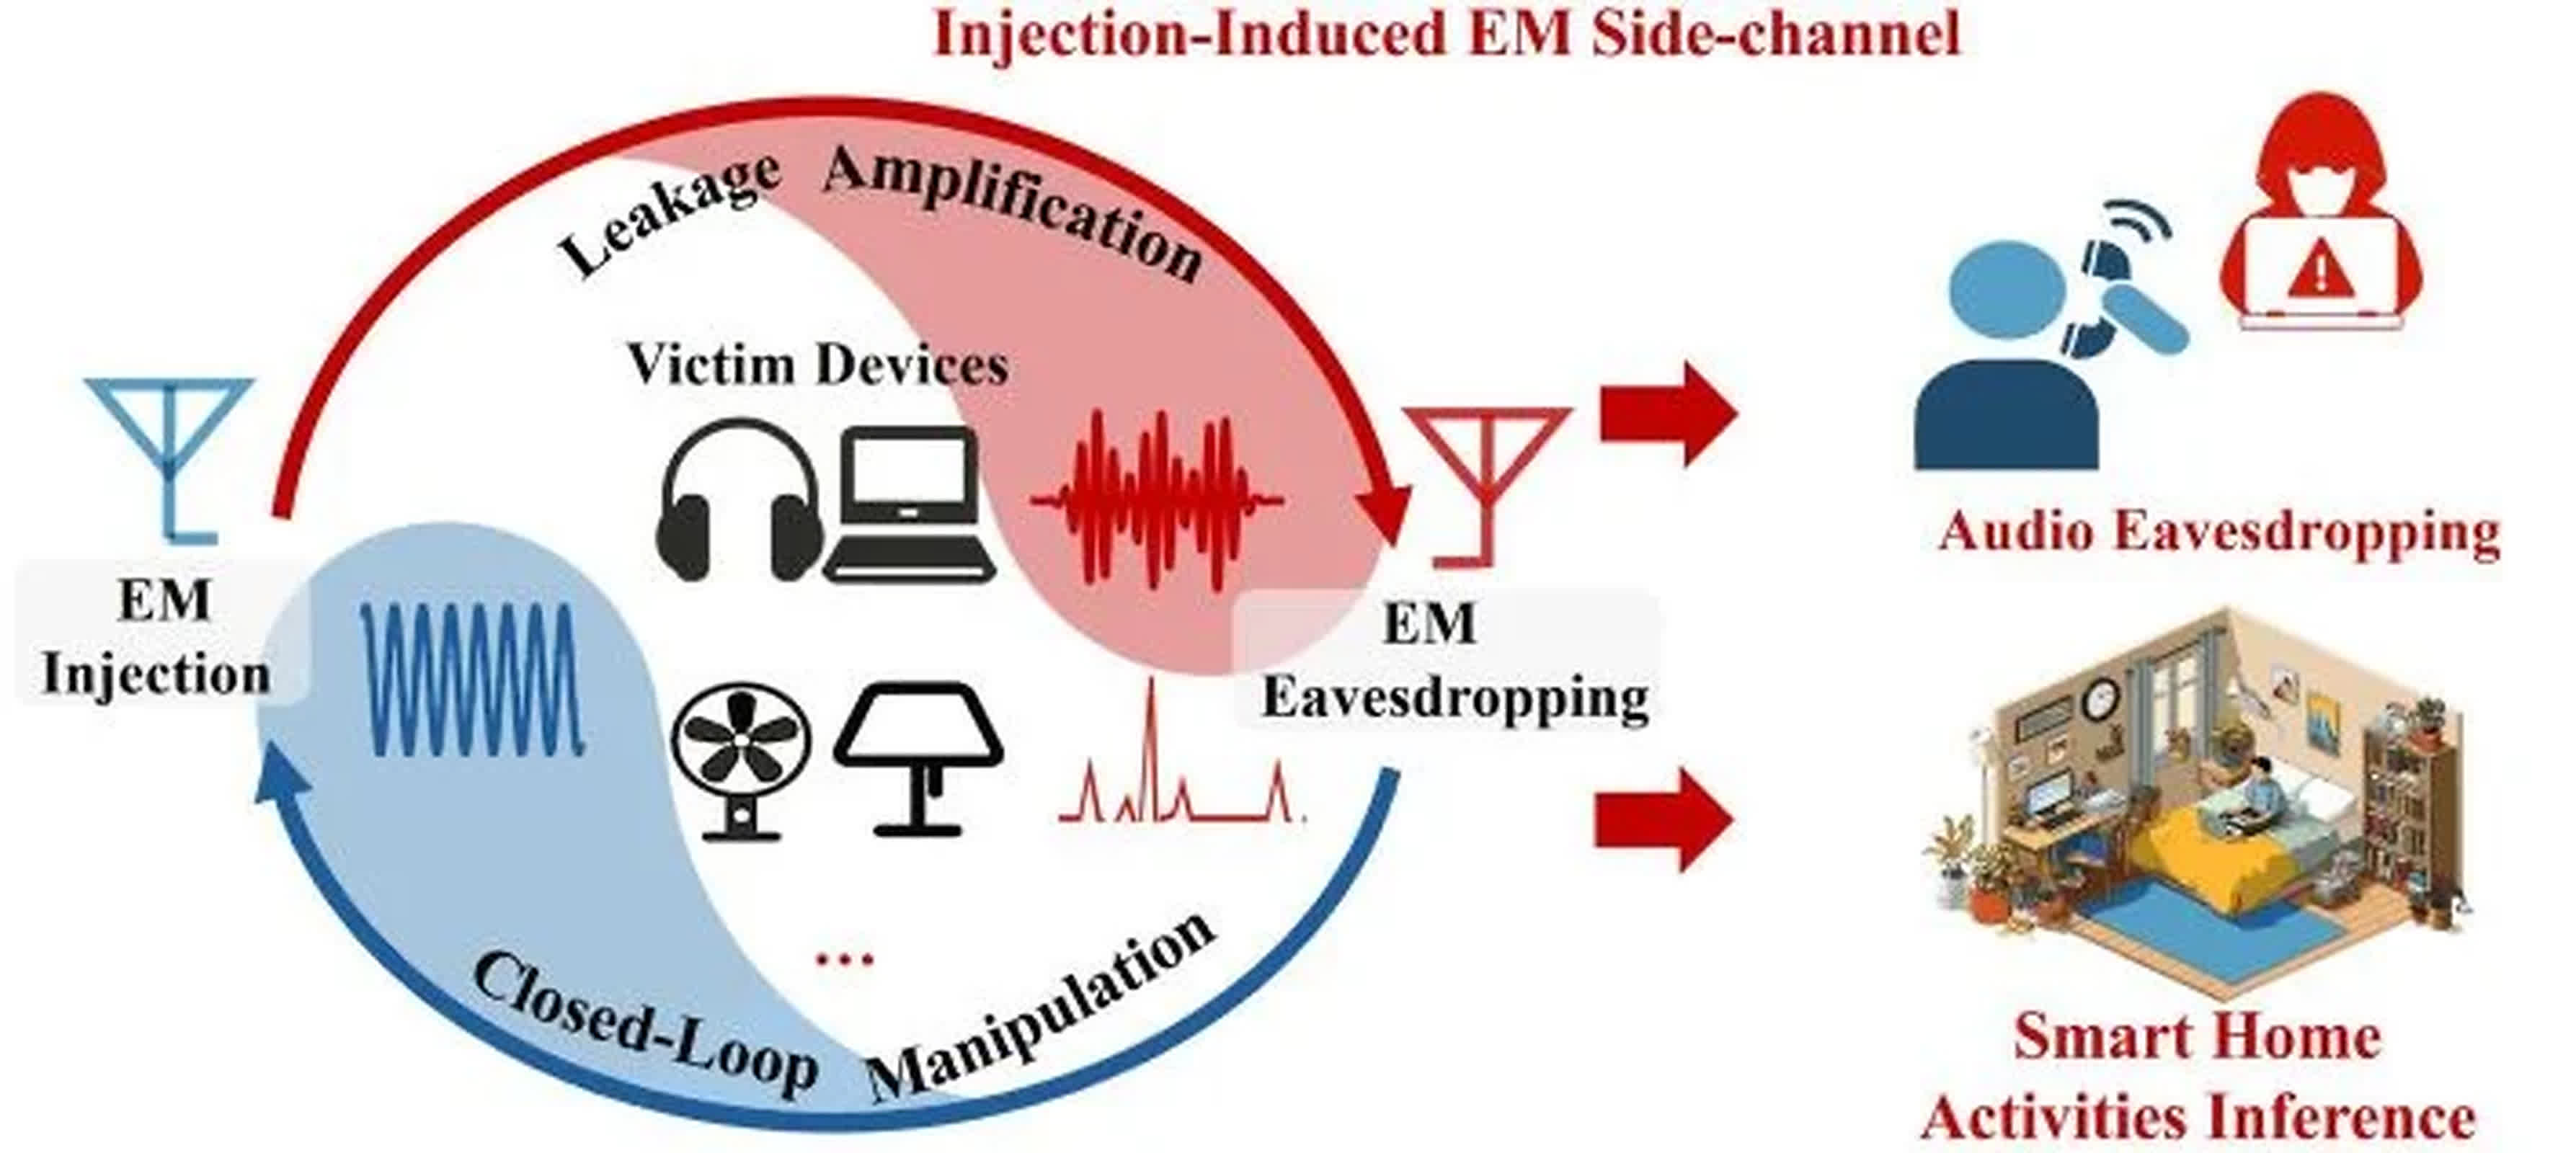
The big picture: Researchers in Hong Kong have developed a technique that uses injected radio signals to extract audio and other information from headphones, phones and smart-home devices. Called InjectEave, the method targets analog components that can leak signals too weak to capture through conventional electromagnetic eavesdropping. In testing, the researchers recovered understandable headphone audio from up to 30 meters away, including through walls.
The research comes from the Hong Kong University of Science and Technology in Guangzhou and the Hong Kong Polytechnic University. The team presented its paper, “Injected and Leaked: Actively Inducing Side-Channel Leakage Using Electromagnetic Injection and Hardware Nonlinearity,” at USENIX Security 2026.
Traditional electromagnetic side-channel attacks rely on passively collecting radiation emitted by electronics. That’s often difficult with audio, since low-frequency signals produce weak emissions that get lost easily in background noise.
InjectEave takes a different route. An attacker transmits an electromagnetic signal toward a device at a frequency between 0 MHz and 9 MHz. The researchers did not disclose the precise settings needed for the attack.
Advertisement
The injected signal interacts with nonlinear parts inside the device, including amplifiers, analog-to-digital converters, power converters and switching MOSFETs. Those components can mix the injected RF signal with audio or other low-frequency activity. The device then emits a modified signal that nearby radio equipment can pick up and analyze.
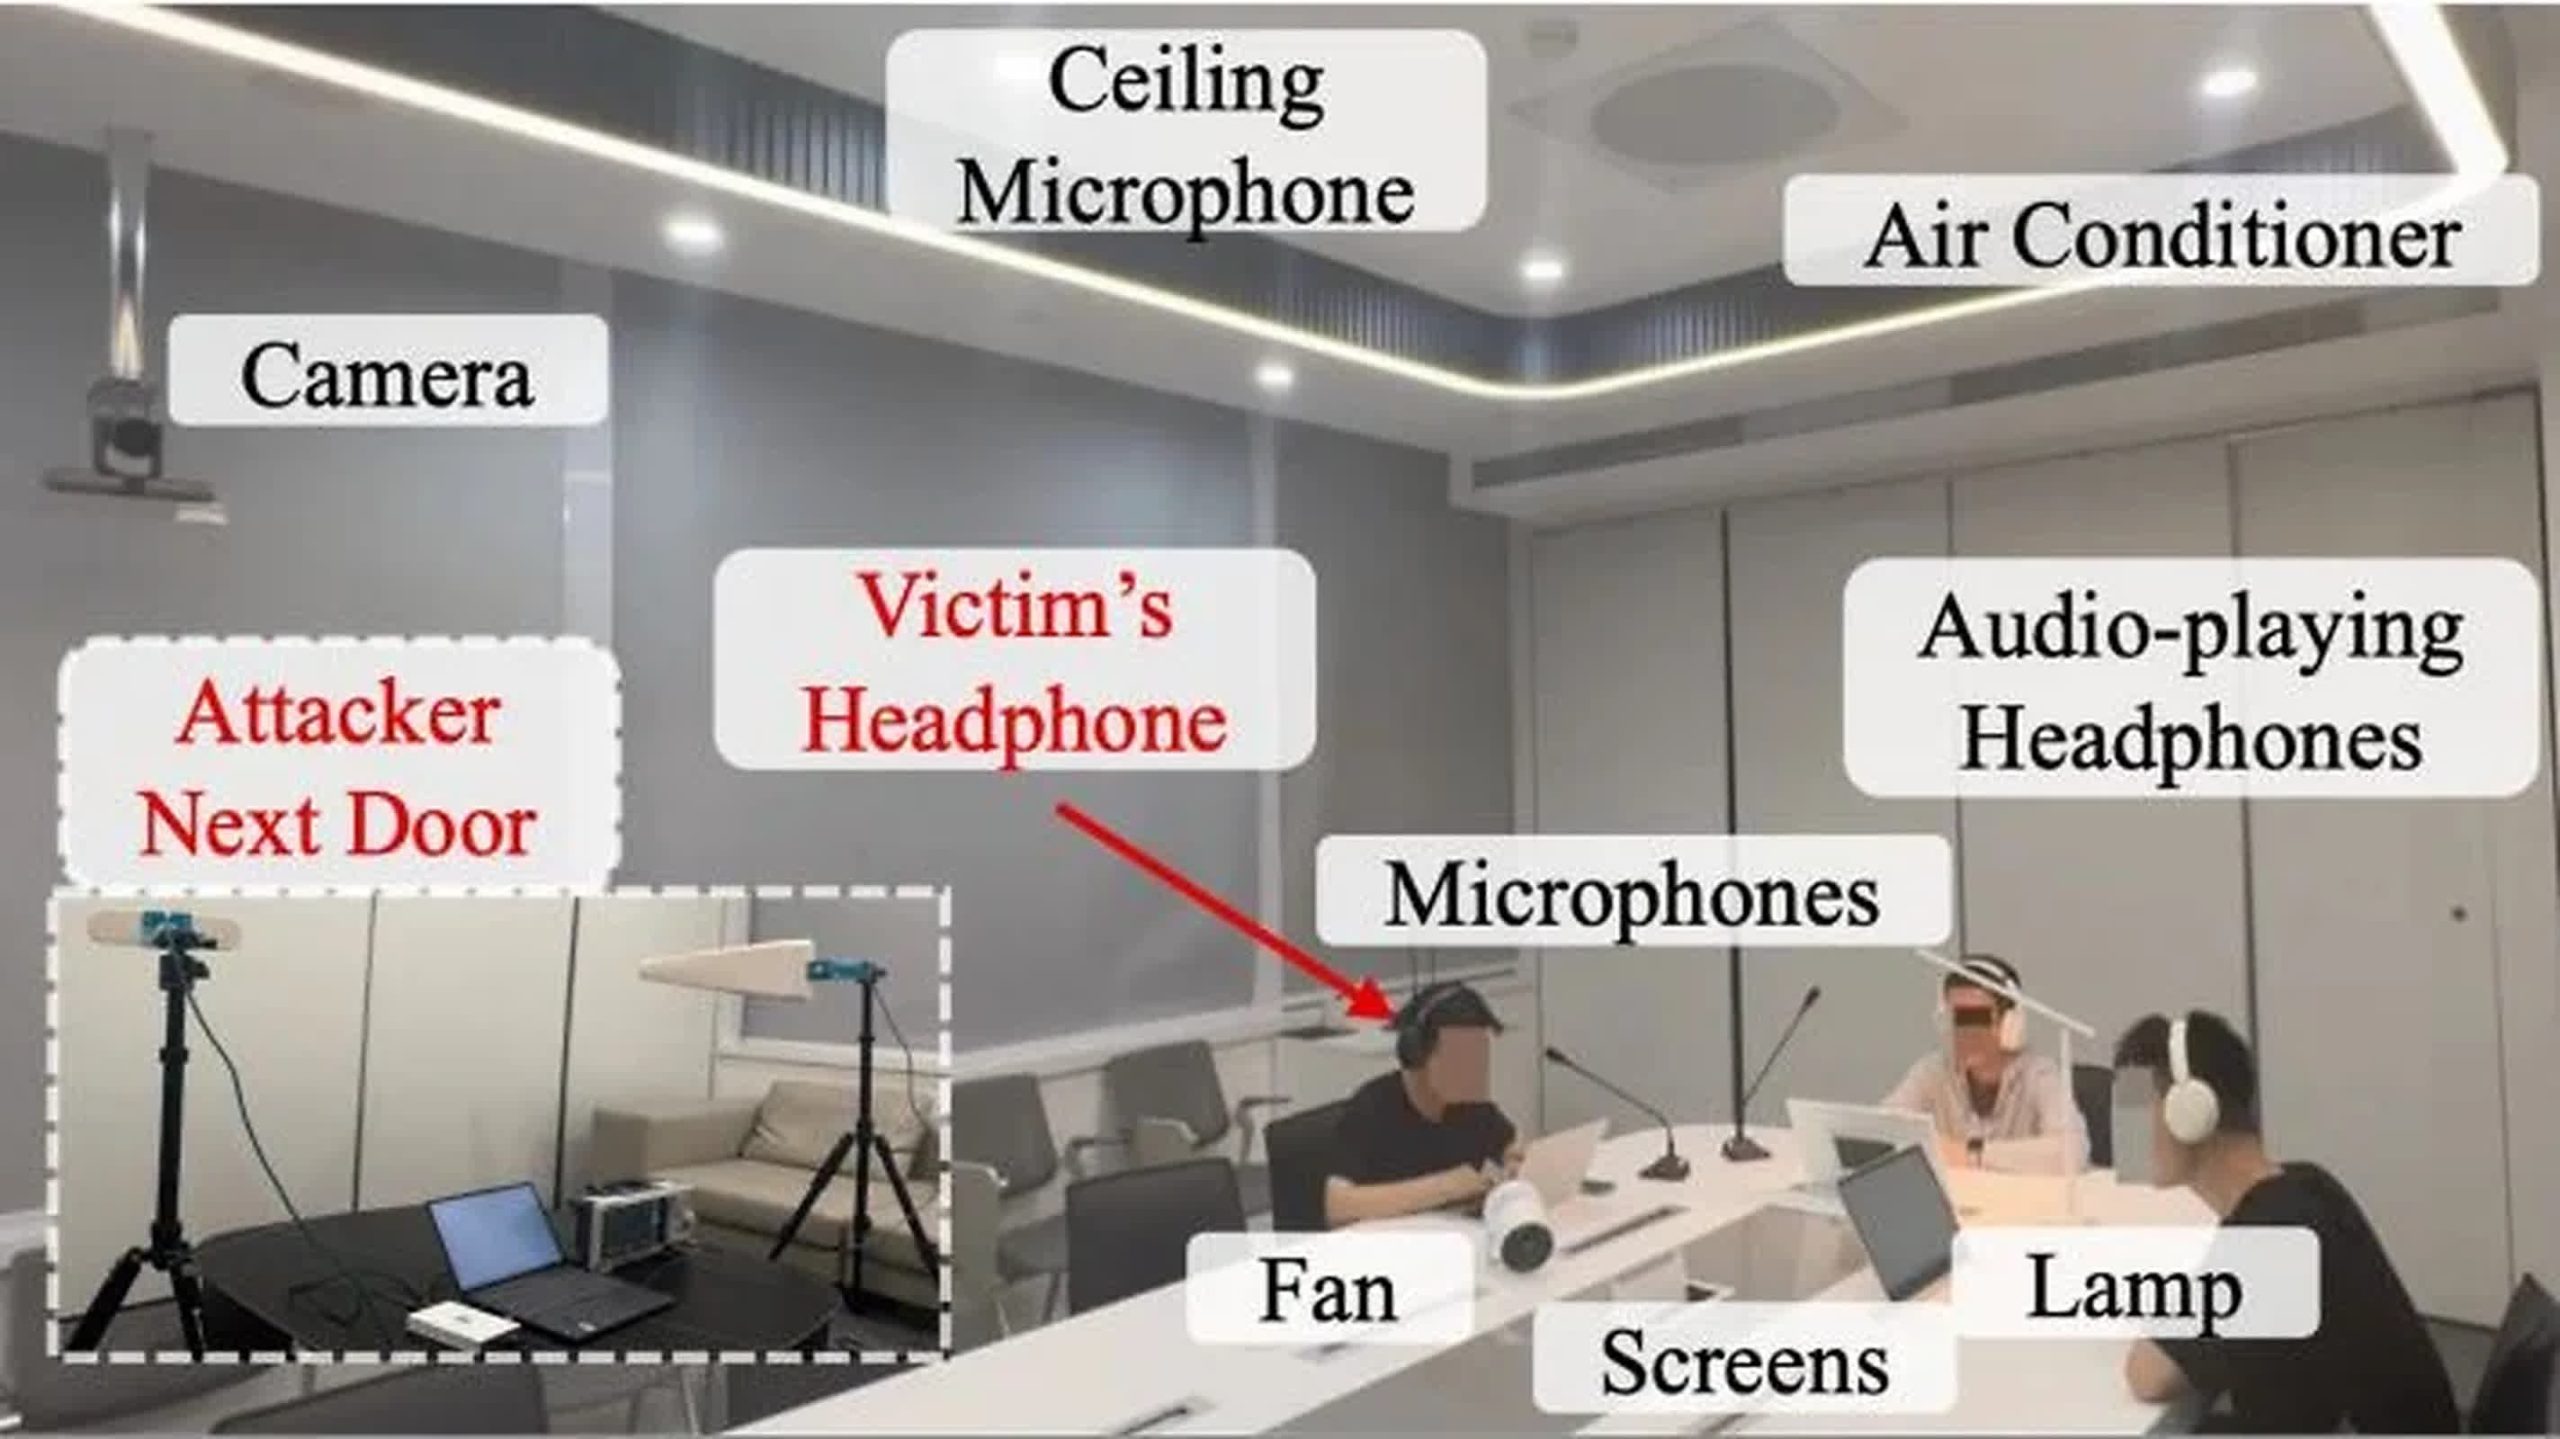
The researchers used a USRP B210 software-defined radio, antennas, a Siglent SSA3075X Plus spectrum analyzer and a laptop. They also used an RF power amplifier in some tests to increase the range.
The team tested 11 commercial products. They included Sony ZX110AP wired headphones, Apple earbuds, UGreen MAX2 headphones, Philips TAH2020 headphones, HP H231R headphones and a Flyingvoice P23GW VoIP phone. The researchers also tested smart fans from Oidire and Xiaomi, as well as lamps from Jingzao and Xiaomi.
According to the paper, most tests worked at distances greater than two meters, including through walls. Device-specific ranges generally ran from one to six meters. With an RF amplifier, the researchers recovered intelligible headphone audio from up to 30 meters.
Advertisement
“Our new project, InjectEave, shows that RF signals can induce information leakage from everyday headphones, allowing an attacker to recover headphone audio from up to 30 meters away, including through walls,” Yan Long, an assistant professor at HKUST in Guangzhou, said in an email to The Register.
Long said the researchers confirmed the issue in devices made by Sony, HP and Philips, among others.
The team also tested scenarios involving equipment hidden in a suitcase, behind a hotel-room wall or inside office furniture. The experiments suggest the attack could be carried out outside a lab, although it still requires nearby radio equipment and knowledge of how a given device responds to the injected signal.
Headphones and phones are the most obvious targets because they may carry private conversations. But the technique could also reveal activity in a home or office. With smart lamps and fans, the team said it could capture control signals and power-use patterns that may indicate when devices are being used.
Advertisement
The researchers said conventional digital protections would not stop InjectEave because the leakage occurs in the analog hardware path, rather than in encrypted data or software.
“InjectEave is immune to digital defenses such as encryption, masking, and randomization, because the leakage comes from the analog path,” the researchers wrote.
They said shielding, filtering and twisted-pair wiring can reduce the amount of RF energy that reaches vulnerable components. Those measures may make the attack harder to carry out, but the researchers said they do not guarantee protection.
President Donald Trump has responded in characteristic fashion to the recent debate around AI safety — by declaring that these concerns are part of a long line of hoaxes “generated by the Radical Left Dumocrats, for purposes of destroying our Country.”
On Saturday, Trump began his musings on AI by writing on his social network Truth Social that “many people think that the words ‘Artificial Intelligence’ are inaccurate, and very ineloquent, relative to AI, or Artificial Intelligence.” So he posted a poll where followers could vote on a new name for the technology — Superior Intelligence, Extreme Intelligence, or Supreme Intelligence. (The poll is still ongoing as of publication time)
A couple hours later, Trump followed up with a post claiming that attempts at “the decimation, or destruction, of AI” are one of “many” Democratic hoaxes, similar to “RUSSIA, RUSSIA, RUSSIA, UKRAINE, UKRAINE, UKRAINE, Global Warming, Impeachment Hoax #1, Impeachment Hoax #2, Men in Women’s Sports, [and] Transgender for Everyone.”
Trump then insisted that he “will not stand by and let this happen,” adding that this so-called hoax “began with an attack on our Data Centers, until people realized how wealthy and prestigious they were for the Communities in which they were built.” But after, in his telling, “the crazed Data Center attack has largely failed,” critics are “going straight at AI.”
The president’s post also echoes his comments at a golf tournament last weekend, when he said he’s open to “guardrails,” but also argued, “I think you have a lot of negative forces that are bringing it up that shouldn’t be bringing it up.”
On Saturday, Trump went on to say that he will “cherish [the AI industry,] help it, and watch over it, as it grows,” but he’s also forming an AI Force, similar to the Space Force that he established in his first term.
“To that end, I will be announcing, in the near future, the AI ‘Czar’ — Only High I.Q. individuals need apply!” he added.
Advertisement
The president did not say what the AI Force and AI czar’s duties will entail. Venture capitalist Daivd Sacks stepped down as Trump’s AI and crypto czar earlier this year, moving on to co-chair the President’s Council of Advisors on Science and Technology.
Nvidia CEO Jensen Huang, meanwhile, called Trump on-stage during the All-In Summit (which Sacks co-hosts), agreed with the president that the AI backlash is a “hoax,” and insisted that “we’re not going to let” a slowdown happen.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
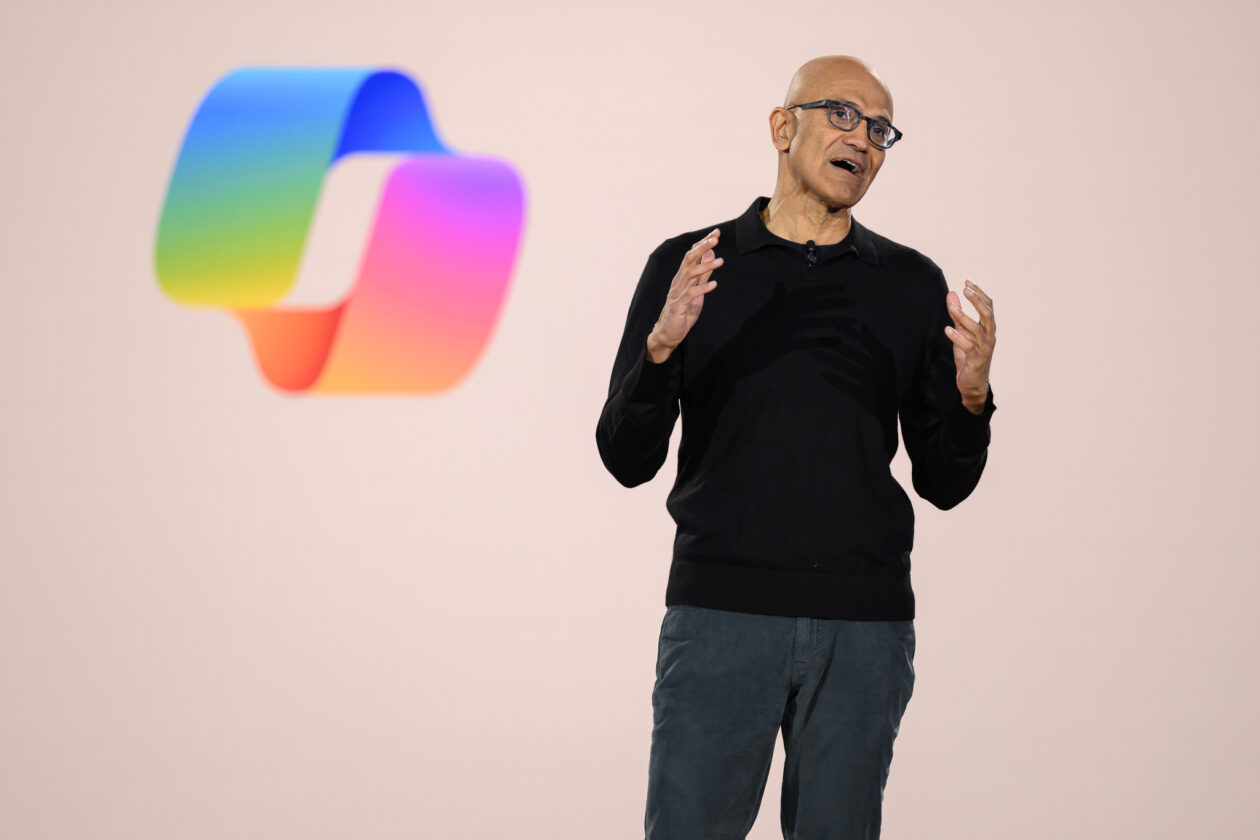
Satya Nadella says Microsoft welcomes the “deliberate pacing needed to get alignment right.” (GeekWire File Photo / Kevin Lisota)
“People matter more than AI.”
That’s the premise of a draft code of conduct Microsoft published Monday morning for the AI models it’s developing in-house. The 37-page document would bar its models from resisting shutdown, setting their own goals, or hiding their reasoning from human auditors.
The document applies to Microsoft’s MAI models, the in-house family the company began building after forming a superintelligence team in late 2025. Microsoft has since released seven homegrown models in what it described as a push for long-term self-sufficiency in AI.
The company says the models should remain “subordinate to humanity, subject to meaningful human oversight and control.”
“AI is moving fast,” the company says in a blog post. “As it does, we believe it’s worth writing down the rules and the motivations behind it, and doing it in as open a space as possible.”
Advertisement
Microsoft acknowledges there’s no guarantee its models will follow the rules. “Written objectives alone can never ensure alignment,” the company says, calling the document a “north star,” not “a guarantee of present-day performance.”
The company says it also filters what its models produce, watches how they behave once released, and limits what they’re allowed to do.
Microsoft’s move comes amid a growing debate over the pace of AI development. In an essay over the weekend, Anthropic CEO Dario Amodei called for slowing down AI advances, saying the pace of development has started to surpass the industry’s ability to keep AI systems safe.
As a first step, Anthropic committed to giving outside evaluators permanent, employee-level access to its systems.
Advertisement
Industry reaction to Amodei: OpenAI CEO Sam Altman agreed and said OpenAI would make the same commitment to independent evaluators. Elon Musk’s response: “Dario is right.”
President Donald Trump rejected the idea of guardrails outright Monday, blaming a “SICK conspiracy” for public backlash over AI data centers and writing that “the only one that is happy about it is China,” alluding to concerns about American competitiveness in AI.
Microsoft CEO Satya Nadella weighed in Sunday, writing on X that the company welcomes “the research, focus, and deliberate pacing needed to get alignment right,” using the industry’s term for making AI systems reliably do what people intend.
Advertisement
Nadella added that the effort “cannot be controlled by a handful of entities, but must have broad representation across the ecosystem, countries, and fields, including academia.”
Microsoft’s draft code of conduct: Mustafa Suleyman, the Microsoft AI CEO, told CNBC the document had been in the works for about five months, and that the company decided to publish it now given the current discussions.
One place where the two companies may diverge is the question of what AI models are, exactly. Microsoft’s code of conduct says its models are “not conscious and should not be designed to imitate consciousness.” It also rejects “the pursuit of legal personhood, or the idea that models might deserve welfare, or be entitled to rights.”
Advertisement
The Verge called that portion of the document “a direct swipe at AI welfare research and model consciousness — concepts Anthropic has been pushing hard on lately.”
Microsoft is taking public comment on its code of conduct for six weeks through a feedback form. It says it will publish a summary of the responses and a revised version later this year, to guide development starting in 2027. It says it isn’t training its current models on it.
The company’s AI team developed the draft with its responsible AI, legal, red teaming and safety teams, consulting outside experts in law, ethics, linguistics and philosophy, plus focus groups drawn from the public.
Manus went back to being an independent business in September after China blocked Meta’s acquisition of the start-up.
AI start-up Manus is reportedly gearing up to double its valuation to $4bn in an upcoming fundraising round, after Meta’s acquisition of the company was forcibly unwound by Chinese authorities earlier this year.
According to Bloomberg, Manus’s fresh $500m round is set to close “soon”, after which the company could become China’s most valuable start-up in its sector. The talks are still in early stages and the outcome could change, sources told the publication.
Manus is behind a general AI agent called Manus AI that utilises multiple frontier models and operates in a complete sandbox environment to help users with multi-step tasks.
Advertisement
Meta acquired the Singapore-headquartered company (developed by China’s Butterfly Effect) late last December at a reported value of more than $2bn. This marked a fourfold jump from its valuation in April 2025, highlighting the perceived value of its general AI agent that took the industry by storm following its launch.
The acquisition, however, faced near-immediate scrutiny from Chinese authorities, which launched a probe shortly following the deal’s announcement.
According to national rules, the Chinese government, which is increasingly protective of its innovative technology and companies, needs to approve the export of certain technologies, including AI. Meta, at the time, said that the deal “complied fully with applicable law”.
Manus had already assimilated with Meta by the time the deal had to be unwound. Existing Manus investors, including Tencent Holdings, ZhenFund and HSG, had already received their acquisition proceeds, which needed to be reversed.










































You must be logged in to post a comment Login