
Connect with us

Tech

Ring Promo Code: 50% Off

Published

on

If you’re a fan of Amazon’s ecosystem, whether that’s asking your Alexa speaker to tell you about the weather or compulsively checking the video feed from your Ring doorbell, then it makes sense to expand and build onto the system. It’s always easier to keep to one ecosystem as much as you can with smart home gear, letting you stick to a single app and single subscription if you decide to invest in one.

While we’ve liked Ring’s cameras and home security products fine enough, they’re hard to recommend at the top of our guides since Ring is reintroducing a policy to enable local law enforcement to request footage directly from Ring users. It’s up to you if that’s something you want to invest in, and if you already have Ring products, it might make the most sense to continue adding onto that ecosystem than diving into a new one.

No matter the reason, if you’re looking to add a Ring product to your home, don’t get one without using our Ring coupon codes to get it for a better price.

Ring Promo Code: 50% Off Ring Cameras, Doorbells, and Outdoor Cameras

Ring is running a deal all month long with up to 50% off different products and bundles. You can get all kinds of Ring cameras and security accessories for a variety of discounts, from Ring’s video doorbell to indoor and outdoor cameras.

Advertisement
Image may contain: Light, Lighting, and Electronics

These locks, lights, and other smart home upgrades let you add automation without messing up your home’s vibe.

Save $150 on Wired Doorbell Pro and Floodlight Cam

If you’re looking for an outdoor combination, you can get both Ring’s Starter Pro Kit, which includes the Wired Doorbell Pro and Floodlight Cam, for $150 off the set. It’s a great option if you want to get a camera feed both at your doorstep and over your garage.

Image may contain: Person, Security, Electronics, and Camera

Ring

Spotlight Cam Pro Battery

Bundle and Save on Ring Whole Home Basic Kit

Looking to deck out your whole home? Ring’s Whole Home Basic Kit is also discounted for $59 off. It includes Ring’s Outdoor Cam Plus Battery, Battery Doorbell, and the Alarm Security Kit, so you can get everything from video surveillance around the outside of your home and sensors to pair with the alarm system for inside of it.

Ring has a variety of subscription plans, which you’ll want since there’s no option to locally store your video footage. That means in order to play any video back to see what set off the camera or who was at the door, you’ll need one of these plans. Here’s a quick breakdown. Basic Ring Plan: Get the basics with video event playback and smart notifications for one camera. $5 per month or $50 per year. Standard Plan: All the core Ring experience with enhanced features for all your devices. $10 per month, or $100 per year. Premium Plan: Ring home the best of the best with our most advanced AI and recording features. $20 per month or $200 per year.

Advertisement
Ring stick up camera

Ring Coupons: $29 Off Pet Basic Kit + Pet Tag

Ring has a pet package you can get for a discount, too. You’ll get both Ring’s Indoor Cam and the Pet Tag, which has a QR code that lets anyone who finds your pet scan it and get your information to contact you. It’s 50% off right now, so if you’re looking for new tags and a camera to keep an eye on your favorite furry companion, this is your moment.

Rectangular cylindrical security camera sitting on a wooden surface

Get $40 Off the Ring Outdoor Cam Plus Battery + Battery Doorbell

If you’ve been looking to upgrade your home security system, now’s a great time to invest in the Ring Outdoor Cam Plus Battery + Battery Doorbell for $30 off (now $160). This discounted Ring bundle includes the Outdoor Cam, plus Battery, Battery Doorbell, and a free 30-day trial of Ring Protect2. With this enhanced Ring bundle, you’ll be able to see all around your home as well as welcome your guests without needing to get up from the couch.

Image may contain: Electrical Device, and Switch

There’s a reason these motion-activated, 1080p HD cameras have become ubiquitous: they’re super simple to setup and use. Just charge the battery, stick it by your door, and keep tabs on your place from wherever you are, day and night, through motion history or a live feed you can watch on an app. Two-way communication lets you chat with visitors or scare away porch pirates, while an optional subscription to Ring’s Protect Plan will let you share videos with your community. 

Secure Your Business With Ring

Having a security camera to protect your business is important. That’s where Ring Business Security Systems come into play. These security and alarm systems are tailored for your business needs, with options like Business Starter Kits, with curated options to fit your needs, and Inventory and Equipment Protection so you can keep an eye on all of your important merchandise and supplies, day or night. Plus, if you want to create your own solution specifically for your business’s needs, you can build your own custom system.

Source link

Continue Reading
Click to comment

You must be logged in to post a comment Login

Leave a Reply

Tech

Arcee AI built Trinity for about $20m, and investors now value it at $1bn+

Published

on

“Organizations should not have to choose between the capabilities of a frontier model and the ability to control the technology at the center of their work,” said Mark McQuade, co-founder and chief executive of Arcee AI.

The San Francisco company builds open-weight AI models. It has raised a Series B round that values it at more than $1bn, according to its announcement on 16 September. Vista Equity Partners, Cambium Capital and Emergence Capital led the round. AI10 Ventures, Hitachi, IAG, Microsoft’s M12, P7 and Wipro also took part.

Arcee did not disclose the amount. A source told Fortune, which first reported the round, that it was at least $150m. Fortune put the valuation at $1bn before the new money.

A frontier model for about $20m

Arcee released the Trinity family of models over the past year. The largest, Trinity Large, has 400 billion parameters, with 13 billion active for each token.

Advertisement

The company says its entire 2025 model lineup, including Trinity Large, cost about $20m to build. That figure covers salaries, compute, data, infrastructure and operations.

McQuade told Fortune the company had $30m in the bank when it decided to build its own models. “I said ‘let’s do it’ and I bet the company on it,” he said. Arcee spent 65% to 70% of its capital on the effort, according to Fortune.

Before that, Arcee worked on post-training, which adapts existing models, Fortune reported. McQuade founded the company in 2023. He previously worked at Hugging Face, which Nvidia is buying.

“Dropped the ball on open source”

McQuade told Fortune the goal is to catch up with Chinese open-weight models. “The U.S. is far ahead in closed source, but kind of dropped the ball on open source,” he said.

Advertisement

He said Arcee is chasing GLM Flash, a model from Beijing-based Z.ai. It is not chasing Poolside’s Laguna, he said.

Monti Saroya, senior managing director at Vista Equity Partners, said:

“Arcee has demonstrated a rare combination of technical execution and capital efficiency, building frontier open-weight models at a pace and cost profile that stands out in the market.”

Where the money goes

Arcee will spend the funding in three areas, according to the announcement:

  • training the next generation of Trinity models, which is already underway
  • expanding its work with the US Department of Energy and its 17 national laboratories on Genesis-Science-1, an open model for scientific computing
  • building products that help organisations customise, test, deploy and run open models

Arcee will also work extensively with Vista’s portfolio companies, Fortune reported.

A day earlier, the software company CIQ said Arcee had chosen its Fuzzball tool to coordinate computing jobs for its next flagship model, according to CIQ’s announcement. Arcee keeps its own training and inference software.

Advertisement

Other open-weight bets

In August, River AI raised $1.1bn to let companies train and keep their own models. The same month, the White House’s technology strategy left open-weight AI off its critical list.

Source link

Advertisement
Continue Reading

Tech

Math Professor Accuses OpenAI of Copying His Work, Says AI Compute Power Makes Racing to Publish 'Pointless'

Published

on

The New York Post wrote that OpenAI “stunned the mathematics world” last week when it announced its AI model “cracked a legendary math problem left unsolved for nearly a century in just 88 hours.”

But a New York University professor “has come forward alleging OpenAI may have copied his work after asking him to collaborate — with one of the company’s scientists allegedly warning he might ‘ruin his career’ if he refused.”

[P]rofessor Tristan Buckmaster, a British-Australian researcher who trained in Germany… had been working with Long Island-raised math prodigy Levent Alpöge, a researcher with OpenAI rival Anthropic, on a different elusive fluid dynamics equation, known as the Euler problem, when he found a solution using AI tools from both Anthropic and ChatGPT. He said scientists from OpenAI approached him and tried to convince him to jointly announce the solution, claiming they had independently solved Navier-Stokes. Buckmaster questioned the timing of their finding the solution in a blog post, noting OpenAI had only done so “in the past few days” — after the company became aware of his work. He asked OpenAI experts whether its AI systems used to solve the equation had been “trained on, or had access to” his research, but said they declined to answer, prompting him to wonder how they had advanced toward the solution so quickly. The puzzle is “not the direction one arrives at in a few days,” Buckmaster wrote incredulously…

In OpenAI’s post on its website sharing the Navier-Stokes proof, which it credited to Astra, the company’s latest AI bot, the firm insisted no user data was incorporated into its model to solve the problem. However, it noted that it “cannot rule out” that anonymized data was used to “improve our models.”

Advertisement

“We congratulate Levent Alpöge and Tristan Buckmaster on their remarkable mathematical work,” OpenAI said in the announcement.

Buckmaster shot back, “Is it ethical to use customer’s data to try to scoop their customer?”

Alpöge’s affiliation with Anthropic “seems to have been a sore point for OpenAI,” writes TechCrunch.

Buckmaster’s public statement says the OpenAI’s Sebastien “twice asserted that he wanted Levent removed from authorship” and also said that “it was so annoying that Levent works at Anthropic” — but that Buckmaster still refused to remove the Anthropic mathematician’s credit.

Advertisement

I said that if OpenAI released its result in the way proposed I would go
public with what happened. The reply was, “Why would you ruin your career?” [OpenAI’s Bubeck said later on X that he’d meant unfounded accusations could damage Buckmaster’s career.] I replied that I am an academic, and asked why he thought going public would ruin my career. The reply was, “If you don’t want me to be nice, then I don’t have to be nice.”

Buckmaster later told Australia’s public broadcaster ABC that the companies building AI “have zero respect for the scientific community. I mean, it’s appalling, honestly.” But he went on to say AI has made the race to publish mathematical breakthroughs pointless.

“I think it’s pointless. Like, I think the game is up….” Professor Buckmaster said he and Dr Alpöge had more research they could publish but questioned the point of racing ahead with it when AI could perform work that had previously occupied researchers for years.

He said there needed to be a discussion about how mathematics should operate in this new environment. Professor Buckmaster said some mathematicians had stopped publicly sharing what they were working on to avoid tipping off AI companies about their plans. He has called on academics and people from OpenAI, Anthropic and DeepMind to discuss ground rules for how they worked together.
He said the companies’ power carried responsibilities that went beyond competing to solve problems before their rivals…

Advertisement

Building on the work of mathematicians Diego Córdoba and Luis Martínez-Zoroa, the pair found a solution to the Euler problem, a stepping stone to the Navier-Stokes problem. Professor Buckmaster said he spent weeks checking and improving the “slop” proofs generated by AI…

For now, Professor Buckmaster said he wanted to finish existing work and support his PhD students and postdoctoral researchers, rather than chase another Millennium Prize. “I think it’s more important to re-evaluate what math is,” he said.

“The New York University professor also warned Australia about the centralisation of resources into the hands of a small number of privately owned foreign companies…”

Read more of this story at Slashdot.

Advertisement

Source link

Continue Reading

Tech

Huawei just laid out its 2027 AI chip plans, and Nvidia is clearly the target

Published

on

Huawei isn’t waiting around for the AI chip race to slow down. At a company event in Shanghai on Thursday, rotating chairman David Wang confirmed that two new AI chips are on the way in 2027, the 960DT and the Ascend 960PR, as the company keeps expanding its AI computing business to go after Nvidia, as Reuters reported. The 960DT is expected in the first quarter of 2027, followed by the Ascend 960PR in the third quarter.

Why does connecting chips matter so much?

Here’s the thing about AI workloads: even the most powerful single chip usually can’t handle the biggest AI programs on its own. That’s why Huawei is leaning so heavily on its UnifiedBus technology, which strings together huge numbers of AI chips so they can operate as a single, much larger computing system.

Wang said Huawei has already built 11 semiconductors around UnifiedBus, and the company’s largest connected setups, known as superclusters, can reportedly handle up to a million AI processors working together. On a smaller scale, Huawei says it has already delivered over 1,000 of these linked systems, called supernodes, to more than 370 customers worldwide. Wang stopped short of saying how many chips a single supernode can hold, who any of the customers are, or how the shipment numbers break down.

Can Huawei actually catch up to Nvidia?

US export controls have limited China’s access to the most advanced chips and manufacturing equipment, and that’s actually worked out well for Huawei, pushing it to the front of China’s domestic AI chip supply. Still, Nvidia remains the one to beat, with its chips and software used by developers everywhere.

Hardware alone won’t close that gap, though. Huawei also needs developers actually building on its chips, and Wang shared that its AI chip ecosystem currently counts 5,270 monthly active developers. That number will need to keep climbing if Huawei wants to be seen as a real Nvidia alternative and not just a backup option.

Either way, the US and China’s chip rivalry shows no signs of slowing down, and Huawei just made it clear it intends to be a major part of it straight through 2027.

Advertisement

Source link

Continue Reading

Tech

Don’t Waste Money On Cheap Portable Air Conditioners

Published

on


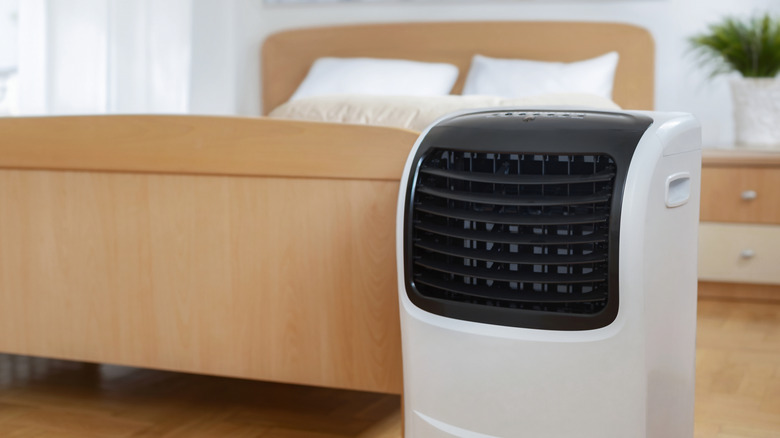
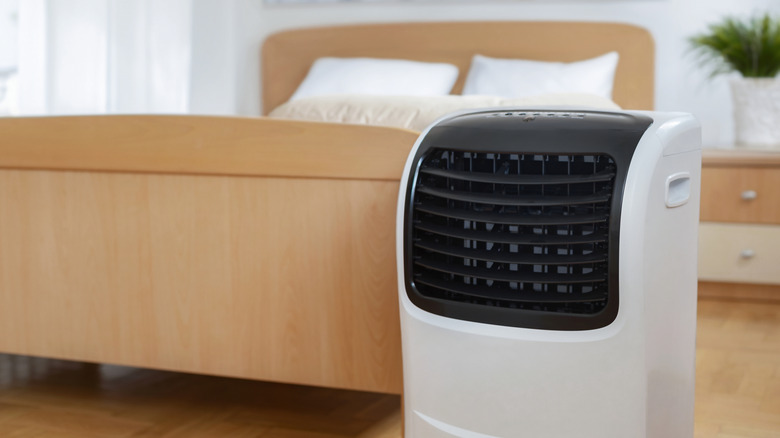
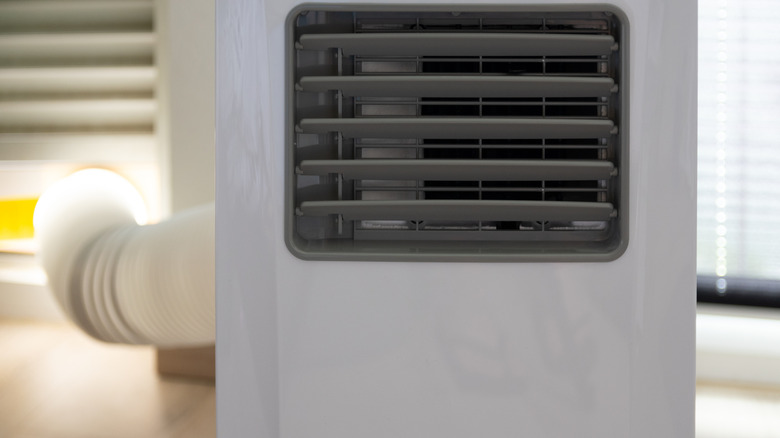
A portable air conditioner is a cooling option you might consider in a variety of circumstances. If you’re trying to cool an individual room, but the room’s design, apartment building rules, or other factors prohibit a window unit, a portable air conditioner may be a viable alternative. However, not all portable air conditioners are created equal. While you might be tempted to save money by purchasing a cheaper, single hose unit, opting for a more expensive dual hose air conditioner can actually reduce costs in the long run and deliver better performance overall.

That said, you first need to decide whether a portable air conditioner is right for you at all.  There are a lot of downsides of portable air conditioners. Despite the name, a portable air conditioner can be relatively heavy, loud, and inefficient. That said, if circumstances prevent you from opting for a superior cooling solution, you at least want to know you’re investing in a portable AC unit that will serve your needs and justify the cost. To that end, buying the more expensive unit might actually be your best bet.

Advertisement

What are the problems with single hose portable air conditioner units?

When you shop for portable ACs, you’ll likely find that single hose models have more appealing price tags than dual hose models. However, purchasing one might ultimately be the less financially sound choice.

A single hose portable air conditioner unit works by pulling air from inside the room and cooling it. The unit is designed to vent warm air and moisture outside the room. However, because a single hose portable AC pulls air from within the room and pushes it outside, the result is negative air pressure within the space you’re trying to cool. This causes the air in the room to be replaced with air that can leak in through other areas through the little gaps beneath closed doors. This naturally counteracts the cooling effect of the unit. Thus, the AC has to use more energy to function as intended.

On top of that, the harder an AC has to work, the more wear-and-tear the unit goes through. This can limit its lifespan and result in the need for early repairs. All these costs add up over extended periods of use. A single hose unit might be acceptable for a small room, but it’s a poor choice for a larger space.

Advertisement

Why a dual hose portable air conditioner is the better option

A portable air conditioner with two hoses typically represents an improvement over a single hose unit. One hose in a dual hose unit draws in air from inside the room, cools it, then sends it back into the room. This process generates heat within the components of the unit. The second hose takes in air from outside, uses it to cool the unit, and sends that warmed air back outside. This addresses some of the efficiency and effectiveness problems that can plague single hose models. The dual hose unit may cost more initially, but it will likely compensate for that with better savings and performance in the long run.

Finally, if you’re not sure whether a portable AC unit is right for your cooling needs, it helps to discuss this topic with a professional. They may be able to point you in the direction of better options. You can research the best portable air conditioners currently available as well. If you decide to purchase one, it’s also wise to brush up on some basic information, such as how much space you should leave between a portable air conditioner and the wall.

Advertisement


Source link

Advertisement
Continue Reading

Tech

EU Kids Act to ban social media for under-13s

Published

on

Big Tech does not decide rules, Ursula von der Leyen says, announcing plans to restrict social media usage for minors.

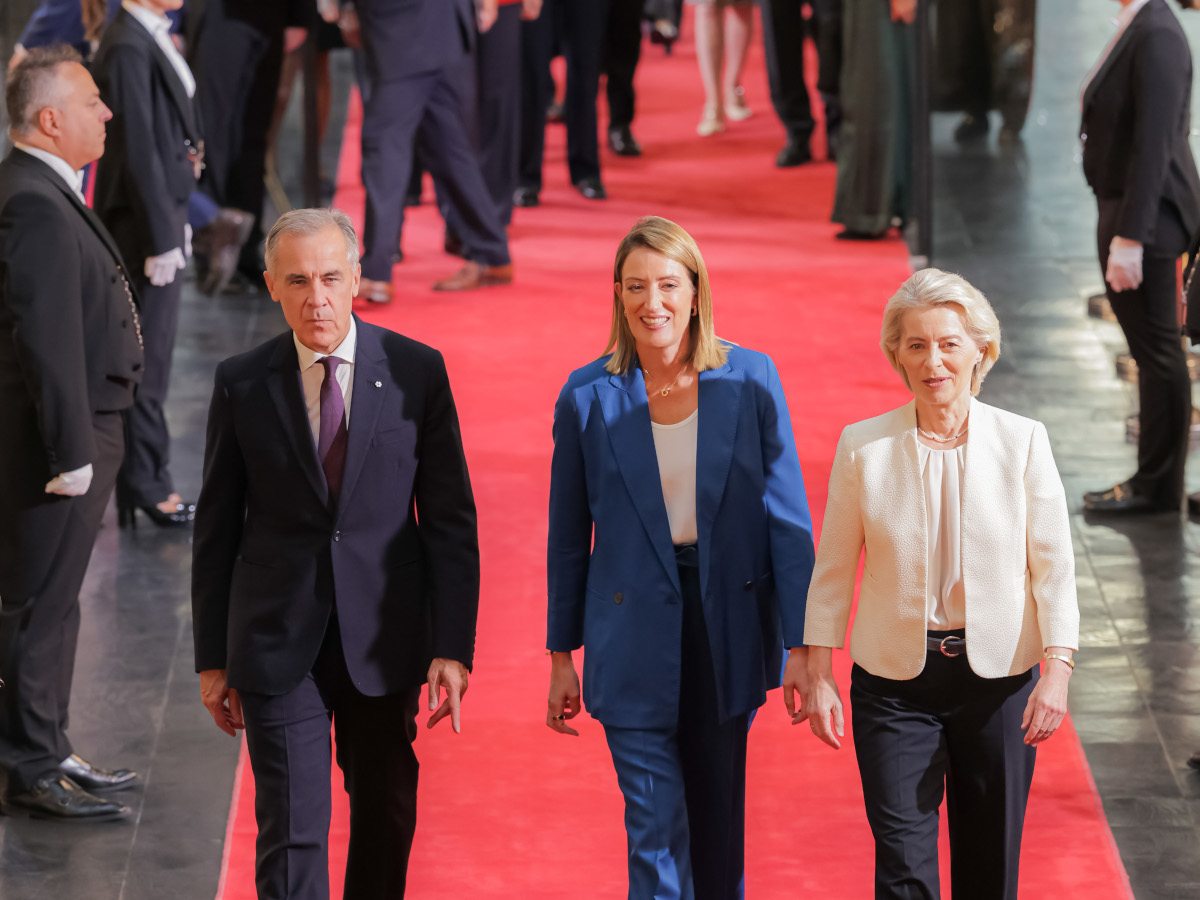
In her State of the Union speech today (16 September), European Commission president Ursula von der Leyen announced the EU Kids Act, a legislative proposal that intends to ban social media for children under 13.

The law takes a tiered approach to social media and video sharing platforms for minors in the bloc, proposing fully guardian-controlled accounts for children between 13 and 15, and a mandatory safe design for all accounts for under-18s.

“What we are witnessing is a great capture of our children. A capture of their attention, their focus, their minds. This is depriving children of their childhood,” von der Leyen said.

Advertisement

Child safety on social media has taken centre stage in recent years as parents and lawmakers grapple with the reality of an increasingly dangerous online landscape, worsened by the proliferation of technology and services such as generative AI and online prediction markets.

Governments across the world are banning popular platforms for younger minors in a bid to shield underage users from their provable harms.

Australia became the first one to ban social media for under-16s last December, though a recent study showed that eight in 10 Australian teens and preteens continued to use social media despite the complete prohibition by their government.

Meanwhile, Brazil rolled out a new law that mandates parentally-controlled accounts for under-16s, and several more countries, including Greece, Germany, Indonesia, Malaysia and Canada, are debating their own restrictions.

Advertisement

Last month, France’s top court blocked a proposed bill that would have banned social media for under-15s, arguing that the legislation was too broad and could infringe upon young people’s freedom of expression.

With the EU Kids Act, the Commission also wants to standardise access to social media across the bloc as part of a major government overhaul aimed at cutting red tape. If the act is passed, France’s under-15s, for example, would still be able to use these platforms.

Limiting access to social media, meanwhile, is only a part of the problem. “Children are pulled ever deeper into feeds designed to keep them scrolling,” von der Leyen said, calling algorithms the “great capture of our children”.

She added: “We do not have to accept addictive features. We do not have to accept children being drawn into ever more extreme content. We do not have to accept that girls have their photos used for AI-generated sexualised images.”

Advertisement

Earlier this year, the bloc greenlit a provisional deal to ban AI systems that generate non-consensual sexually explicit and intimate content or child sexual abuse material.

“Platforms will have to prove that they are safe. Because it is not about our minors accessing social media. It is about when and how do we allow social media to access minors,” von der Leyen continued.

The bloc is also introducing a new Digital Fairness Act this autumn that will aim to tackle addictive features on platforms.

“I am aware that many perceive the power of Big Tech as overwhelming and impossible to roll back. I disagree,” the president said. “Europe has the power to act. It is we who decide our rules, not Big Tech.”

Advertisement

US president Donald Trump, an avid critic of the EU’s strict rules, reportedly considered imposing sanctions on the EU for using its Digital Services Act against US technology heavyweights.

Don’t miss out on the knowledge you need to succeed. Sign up for the Daily Brief, Silicon Republic’s digest of need-to-know sci-tech news.
Source link

Advertisement
Continue Reading

Tech

Malware bypasses browser checks to force install Chrome, Edge extensions

Published

on

Malware bypasses browser checks to force install Chrome, Edge extensions

A banking malware operation active since mid-2025 has been using a toolkit named KREMLIN to install malicious Chrome and Edge extensions that steal credentials, session tokens, and sensitive data.

Researchers at Elastic Security Labs found that the malicious extensions bypass Chromium’s integrity mechanisms and load in browsers as if they had been approved by the user.

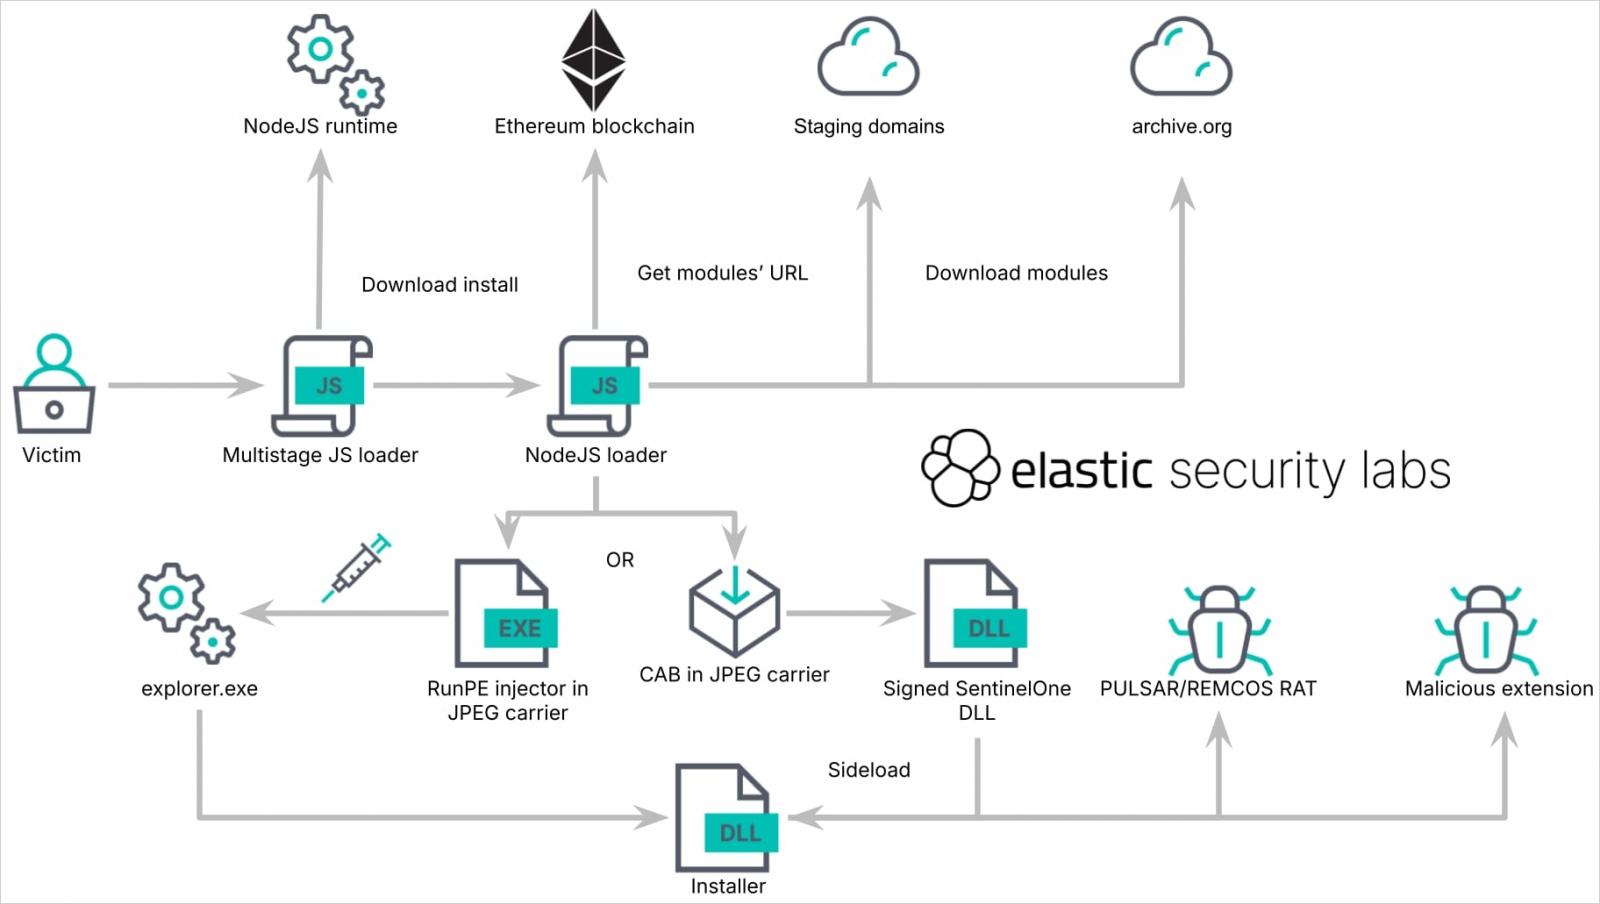
The infection chain starts after the target user opens a JavaScript file disguised as a bank receipt, invoice, payment record, or business document.

After passing anti-sandbox checks, the file triggers a fake error while simultaneously downloading Node.js, establishing persistence through a scheduled task, and retrieving the additional payload location from an Ethereum smart contract.

Advertisement

Despite the name, KREMLIN is linked to a Brazilian operation responsible for at least seven campaigns since May 2025 that use lures impersonating 12 banks.
Installing Chrome and Edge add-ons

A standout feature of KREMLIN is its capability to install extensions on Chrome and Edge browsers without asking the user to approve them.

It waits for the browser to close or terminates it when it detects idle status, and then copies the extension into the app’s profile directories. Next, it enables developer mode and adds the extension to Chromium’s Secure Preferences.

To hide its activity, the malware uses the encryption keys the browser uses to protect sensitive data and then recreates the integrity checks Chrome uses to detect changes in browser preferences.

Advertisement

This makes the malicious extension appear valid to the browser despite never being approved by the user, a documented but rarely used technique according to the researchers.

“KREMLIN uses a documented technique rarely observed in malware: it manually copies the extension into the browser’s profile directories and registers it in the Secure Preferences file,” Elastic explains.

“Because Chromium protects these entries with cryptographic integrity checks, the malware must retrieve the required keys and regenerate the associated HMACs and encrypted hashes.”

Once installed, the extension masquerades as AVSync and performs the following actions:

Advertisement
  • Steals cookies, local storage, and session storage
  • Keylogs text entered into forms, including passwords
  • Captures screenshots and page source
  • Enumerates open tabs and browsing history
  • Intercepts HTTP request bodies and headers
  • Injects attacker-controlled HTML into websites
  • Redirects clicks to attacker-selected destinations
  • Receives commands through a WebSocket connection

Apart from the malicious extension, the KREMLIN toolkit also acts as an info-stealer that can archive and exfiltrate browser databases, cookies, installed extensions, and the App-Bound cryptographic keys needed to decrypt protected data.

Overview of the REF9334 attack chain
Source: Elastic

Disrupting the operation

Elastic Security Labs researchers found that KREMLIN malware campaigns use Ethereum smart contracts as dead-drop resolvers and also abuse the Internet Archive service to host payloads hidden inside JPEG images.

In more recent campaigns, the threat actor deployed the REMCOS remote access tool, but past operations pushed the Pulsar RAT. According to the researchers, the switch was likely due to REMCOS being more feature rich.

By connecting the dots through infrastructure analysis and code artifacts, the researchers found the Ethereum wallet that deployed and updated the smart contracts

According to the researchers, the wallet handled roughly 20,800 USDT (Tether) and 19,000 USDT in incoming and outgoing transfers, respectively. Elastic has confirmed 1,515 infected systems, almost all located in Brazil.

The security firm disrupted the current KREMLIN campaign by registering a domain that the malware used as an anti-sandbox canary, causing the loader to stop due to false flags on systems that would otherwise qualify for infection.

Advertisement

Elastic Security Labs researchers shared the tactics and techniques used in KREMLIN attacks, as well as a set of indicators of compromise.


article image

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

Save your seat

Source link

Continue Reading

Tech

Adafruit's New CircuitPython 'Turbo' Brings Native Code To Tiny Boards

Published

on

Targeting students and beginners, Adafruit released “CircuitPython” in 2017 (as a derivative of the MicroPython microcontroller-optimized programming language).

Now Adafruit managing director Phillip Torrone (also long-time Slashdot reader ptorrone) brings this update:

Adafruit has published CircuitPython Turbo, a workflow that compiles selected Python functions into native machine code on a computer, then loads them onto compatible microcontroller boards.

It builds on MicroPython’s Native and Viper emitters. In a documented Metro RP2040 fixed-point Mandelbrot test, Viper cut computation time from 8.335 seconds to 0.423 seconds, a 19.71x speedup over bytecode. The rest of the application stays in Python. The guide includes benchmarks, source code and hardware demos. The speedup is for the measured computation, not the whole application.

Advertisement

“Turbo support is now included in the latest official CircuitPython builds for RP2040 and RP2350 boards…” explains Torrone’s announcement at Adafruit.com. “The new Turbo in CircuitPython helps when the board spends time calculating: making neopixel effects, drawing fractals, processing audio, filtering sensor readings, or preparing lots of pixels. Those projects can get smoother animation, quicker responses, or room to do more things at once.”

With Turbo, it’s easier, better, and now even faster to make LED light up costumes that also reacts to sound at the same time, a sensor dashboard with animated graphics, or a tiny game doing physics while drawing the screen. Turbo speeds up the busy Python parts. It won’t make a slow sensor or display connection faster… Your computer turns selected functions into instructions the chip can run directly. Python still handles the rest.

We have measured speedups, real display captures, and examples you can pull apart to see what happened. None of this arrived alone. CircuitPython, MicroPython, PyMCU, compiler tools, open hardware, and people sharing their work gave us pieces to connect. The Bao experiments take that idea somewhere else, handing calculations to four helper cores. Now we get to make those paths easier to use, compare results, and find the next useful thing. Maybe that’s smoother animation, a responsive instrument, or an idea we haven’t tried yet.

That’s what I like about open source. Someone shares a piece, someone else sees a possibility, and we get to keep building it together.

Advertisement

Read more of this story at Slashdot.

Source link

Advertisement
Continue Reading

Tech

Apple is reportedly developing an enterprise server built on its own chips

Published

on

Apple is developing an enterprise server built on its own M8 Ultra chips and has discussed using Nvidia’s NVLink Fusion to connect them, aiming at AI developers, companies and governments from around 2029, The Information reported. The European Commission proposed its Cloud and AI Development Act in June, grading public cloud contracts by how far a provider sits outside third-country control.

Apple is working on an enterprise server built on its own chips and has discussed using Nvidia’s networking equipment, The Information reported. It would sell the machine to AI developers, companies and governments.

Two versions are described, one carrying two of Apple’s forthcoming M8 Ultra chips and a larger one carrying four. Nvidia’s NVLink Fusion would connect them, the interconnect it already licenses to Qualcomm, Arm, Fujitsu, Marvell and others.

Nothing would reach the market before 2029. The effort could be cancelled, or proceed without Nvidia’s technology at all. Shares in both companies barely moved on the report.

Advertisement

Apple already builds servers, for itself. Private Cloud Compute ran only on Apple silicon until June, when the company extended it to Google Cloud running on Nvidia GPUs and Intel processors.

It has not sold one since 2011, when the Xserve was discontinued after a run of nearly nine years.

Governments is the interesting word.

The Commission’s June proposal for a Cloud and AI Development Act would grade public contracts by tiers of sovereignty assurance. The highest tier, meant for defence and national security, requires a European cybersecurity certificate and effective control over every software component. No third country may control a provider’s design, development or maintenance.

Advertisement

Europe has already shown what it accepts in practice, and it is less absolute than that sounds.

A six-year, EUR 180M sovereign cloud framework went to four groups in April. One was a Proximus-led consortium including a Thales and Google venture, alongside Mistral AI. American infrastructure qualified.

Non-European technologies, operated within a strict and appropriate framework, can meet the minimum level of sovereignty required, the Commission said at the time. Bidders were judged against eight objectives, from legal exposure to supply chain transparency.

The distinction is between sovereign operation and sovereign technology. A machine a government owns and runs in its own building is an easier argument to make than a service somebody else runs.

Advertisement

The Act covers cloud services rather than hardware, so a server sale would sit outside it altogether. The procurement instinct behind it would not, and buyers write their own conditions.

Europe is short of the thing no regulation conjures. You cannot regulate your way to sovereignty, as Dan Toma argued here last month, when the silicon is American either way.

Source link

Advertisement
Continue Reading

Tech

Providence to receive $1.1B from Nike co-founder to build women’s health hospital in Oregon

Published

on

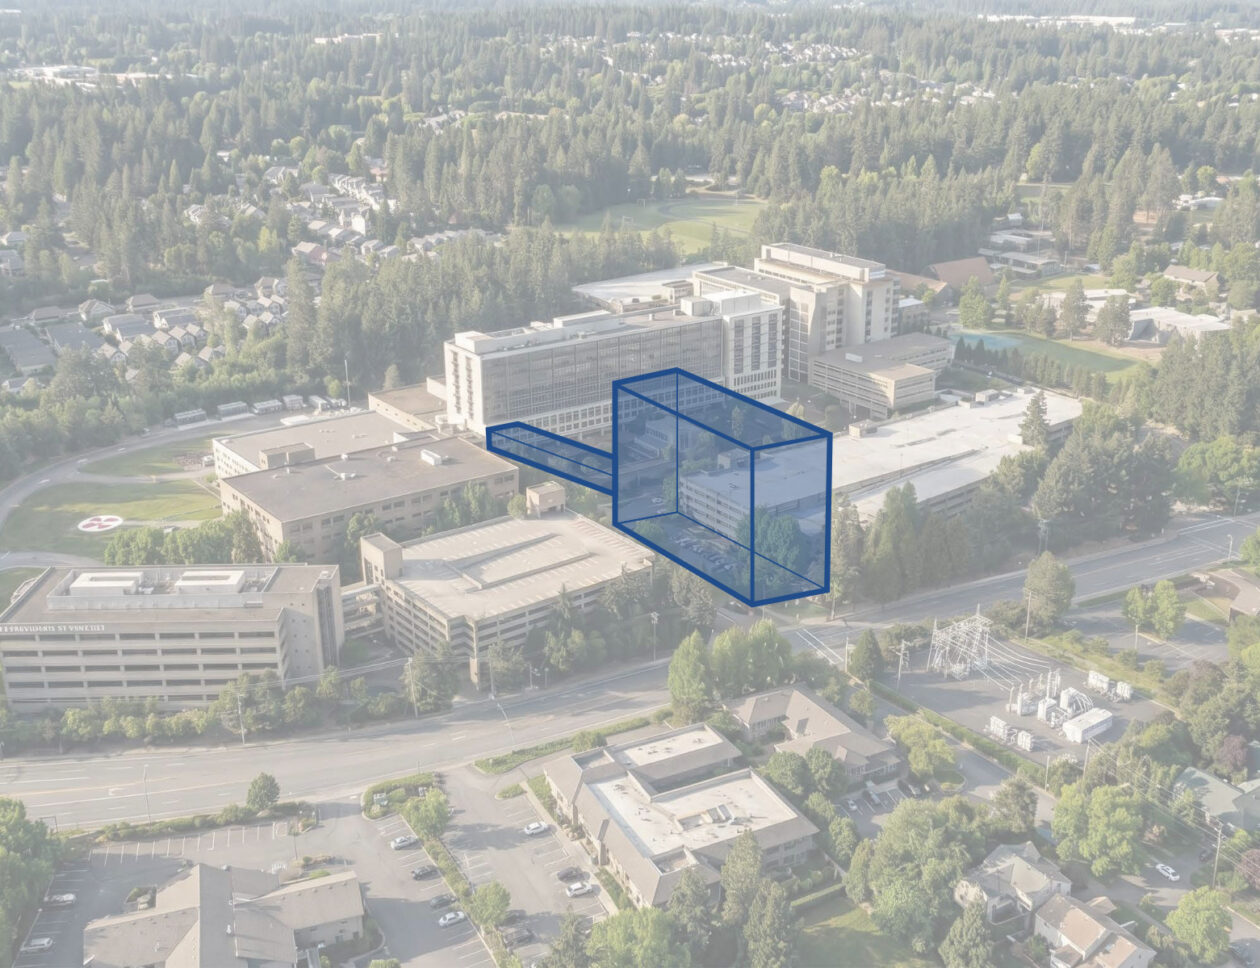
Oregon’s first hospital focused on women’s health will be built on the campus of Providence St. Vincent Medical Center in Portland. (Providence Illustration)

Providence will receive $1.1 billion — one of the largest gifts ever pledged to a U.S. healthcare institution — from Nike co-founder Phil Knight and his wife, Penny. The donation will allow the nonprofit health network to build Oregon’s first hospital focused on women’s health, increase support for cardiovascular services and improve patient care.

“Penny and I have always believed that real breakthroughs come from people willing to take on the toughest challenges,” Phil Knight said in a statement. “Providence has shown that kind of ambition in cardiovascular care, and we see the same opportunity to do something truly distinctive for women’s health.”

The funds are being directed to Portland’s Providence St. Vincent Medical Center and to Providence Heart Institute.

The new women’s hospital will be located on the campus of the medical center and provide care in specialties including gynecology, pregnancy, labor and delivery, menopause and cardiovascular care. Providence leaders note that many pregnant patients are also managing hypertension, diabetes, behavioral health and substance abuse, requiring more specialized services.

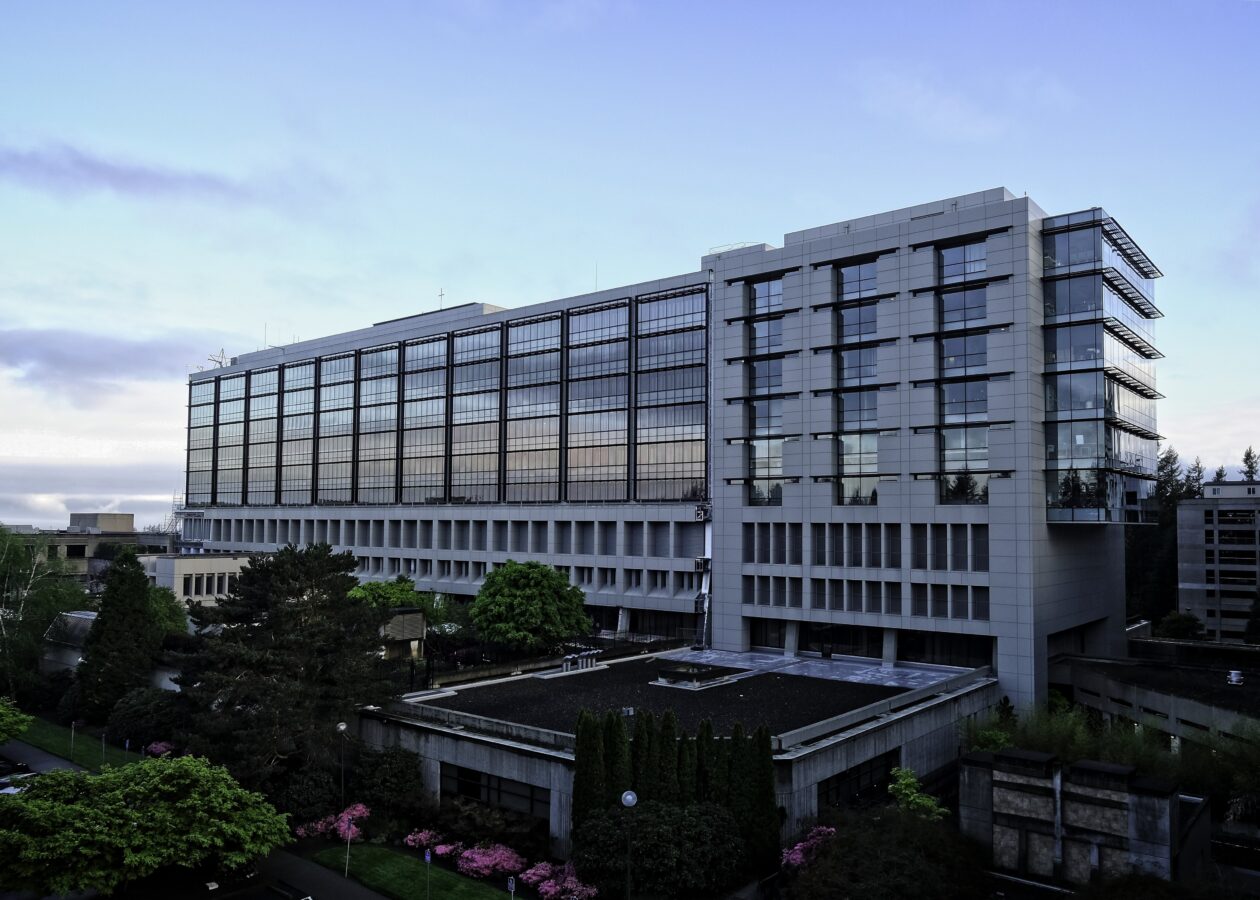
Providence St. Vincent Medical Center in Portland, Ore. (Providence Photo)

The Knights have previously donated $200 million over the course of 10 years to Providence Heart Institute, which sees nearly 63,000 patients each year across the Pacific Northwest, up from 40,000 a decade ago. Cardiovascular disease is the leading cause of death and hospitalization in the U.S.

The added support for the institute will help pay for diagnostic cardiac imaging, additional clinical trials, and the recruitment of leading doctors.

Advertisement

Knight, 88, co-founded Nike with Bill Bowerman in Eugene, Ore., in 1964. The business was originally called Blue Ribbon Sports before rebranding seven years later. Knight is currently worth an estimated $25.4 billion, according to Forbes.

“The Knights’ extraordinary gift is a generational investment, leading to bold and innovative ideas that will shape healthcare in Oregon for decades to come,” said Jennifer Burrows, chief executive of Providence Oregon.

Source link

Advertisement
Continue Reading

Tech

Iranian hackers use CHOSEN BRICK Windows malware to spy on targets

Published

on

Iranian hackers use CHOSEN BRICK Windows malware to spy on targets

Government agencies are warning that Iranian state-linked hackers are using a Windows malware strain named CHOSEN BRICK to target dissidents, activists, and journalists worldwide.

The malware features data theft and espionage capabilities that collect email, Telegram, and WhatsApp communications, take screenshots, and record audio.

The threat actor primarily targeted individuals in the U.S., U.K., and the Netherlands, whose cybersecurity agencies published a joint advisory with the FBI.

A typical attack begins with social engineering messages impersonating trusted contacts or technical support agents, sent to targets via WhatsApp or Telegram.

Advertisement

The threat actor tricks victims into opening malicious files disguised as legitimate applications (e.g., Pictory, RunwayML, Norton Antivirus, Telegram, Adobe Flash Player, KeePass), often suggesting they launch them on personal devices to bypass corporate security blocks.

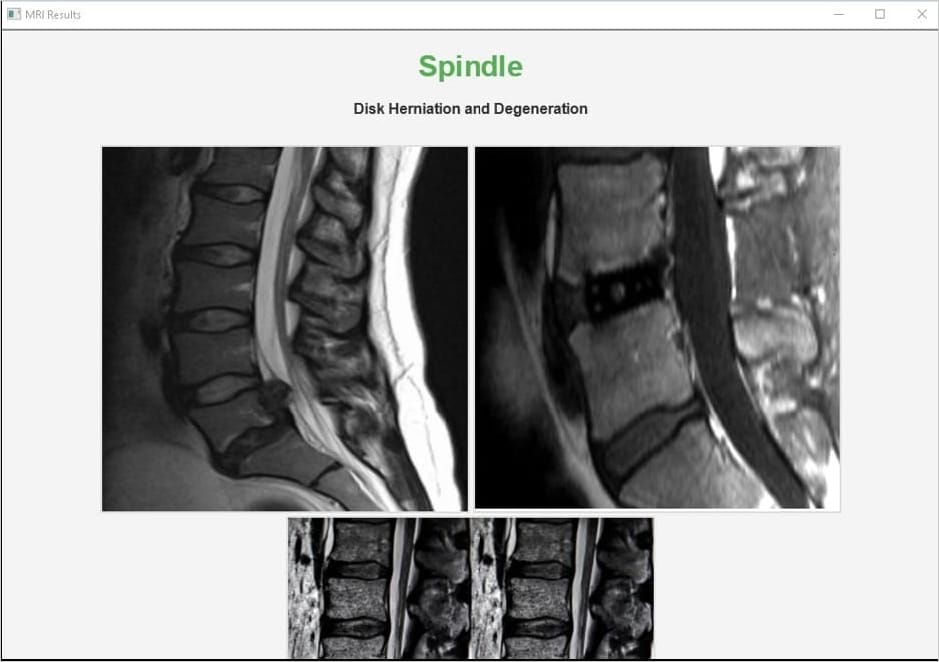
Depending on the pretext used, the hackers sometimes used even medical-related lures, the agencies found.

MRI scan document used as lure
Source: NCSC

The apps display a convincing interface that matches the lure, while silently installing CHOSEN BRICK in the background and securing persistence through Windows Registry Run keys.

The malware adds Microsoft Defender exclusions to evade detection and connects to a unique Telegram bot that matches the victim’s ID and provides command-and-control (C2).

Once launched, CHOSEN BRICK can perform the following actions:

Advertisement
  • Collect system information
  • Enumerate running processes
  • Capture screenshots
  • Record audio through the microphone
  • Steal email content
  • Steal Telegram or WhatsApp browser data
  • Download additional payloads to “C:\Windows \SysWOW64”
  • Delete files
  • Wipe the entire host system

The stolen data is exfiltrated through Telegram or cloud services like VultrObjects and StorjShare, while newer CHOSEN BRICK variants route traffic through SOCKS5 proxies to conceal the activity.

The advisory notes that the stolen data sometimes ends up on pro-Iranian leak sites, serving as a form of harassment and increasing the physical risk for dissidents abroad.

“Iran almost certainly uses cyber activity to support the repression of individuals who are seen as a threat to the regime, such as dissidents, activists and journalists,” the government agencies say.

“In some cases, the Iranian intelligence services have plotted to kidnap or conduct lethal operations against individuals internationally, who they perceive as enemies of the regime.”

Potential victims and organizations should inspect Registry Run entries for suspicious entries, search logs for indicators of compromise (IoCs) shared in the advisory.

Advertisement

Unexpected connections to Telegram’s API, Backblaze B2, VultrObjects, StorjShare, IPRoyal, and LightningProxies should be investigated as suspicious.


article image

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

Save your seat

Source link

Continue Reading

Trending

Copyright © 2025