A new NYT Strands puzzle appears at midnight each day for your time zone – which means that some people are always playing ‘today’s game’ while others are playing ‘yesterday’s’. If you’re looking for Saturday’s puzzle instead then click here: NYT Strands hints and answers for Saturday, September 19 (game #930).
Strands is the NYT’s latest word game after the likes of Wordle, Spelling Bee and Connections – and it’s great fun. It can be difficult, though, so read on for my Strands hints.
Want more word-based fun? Then check out my NYT Connections today and Quordle today pages for hints and answers for those games, and Marc’s Wordle today page for the original viral word game.
Advertisement
SPOILER WARNING: Information about NYT Strands today is below, so don’t read on if you don’t want to know the answers.
Latest Videos FromTechRadar
Advertisement
NYT Strands today (game #931) – hint #1 – today’s theme
What is the theme of today’s NYT Strands?
• Today’s NYT Strands theme is… Putting on airs
NYT Strands today (game #931) – hint #2 – clue words
Play any of these words to unlock the in-game hints system.
PURE
GRASS
BURST
TOAST
SIXTY
BRAIDS
NYT Strands today (game #931) – hint #3 – spangram letters
How many letters are in today’s spangram?
• Spangram has 11 letters
Advertisement
NYT Strands today (game #931) – hint #4 – spangram position
What are two sides of the board that today’s spangram touches?
• First side: right, 1st row
• Last side: left, 7th row
Right, the answers are below, so DO NOT SCROLL ANY FURTHER IF YOU DON’T WANT TO SEE THEM.
Advertisement
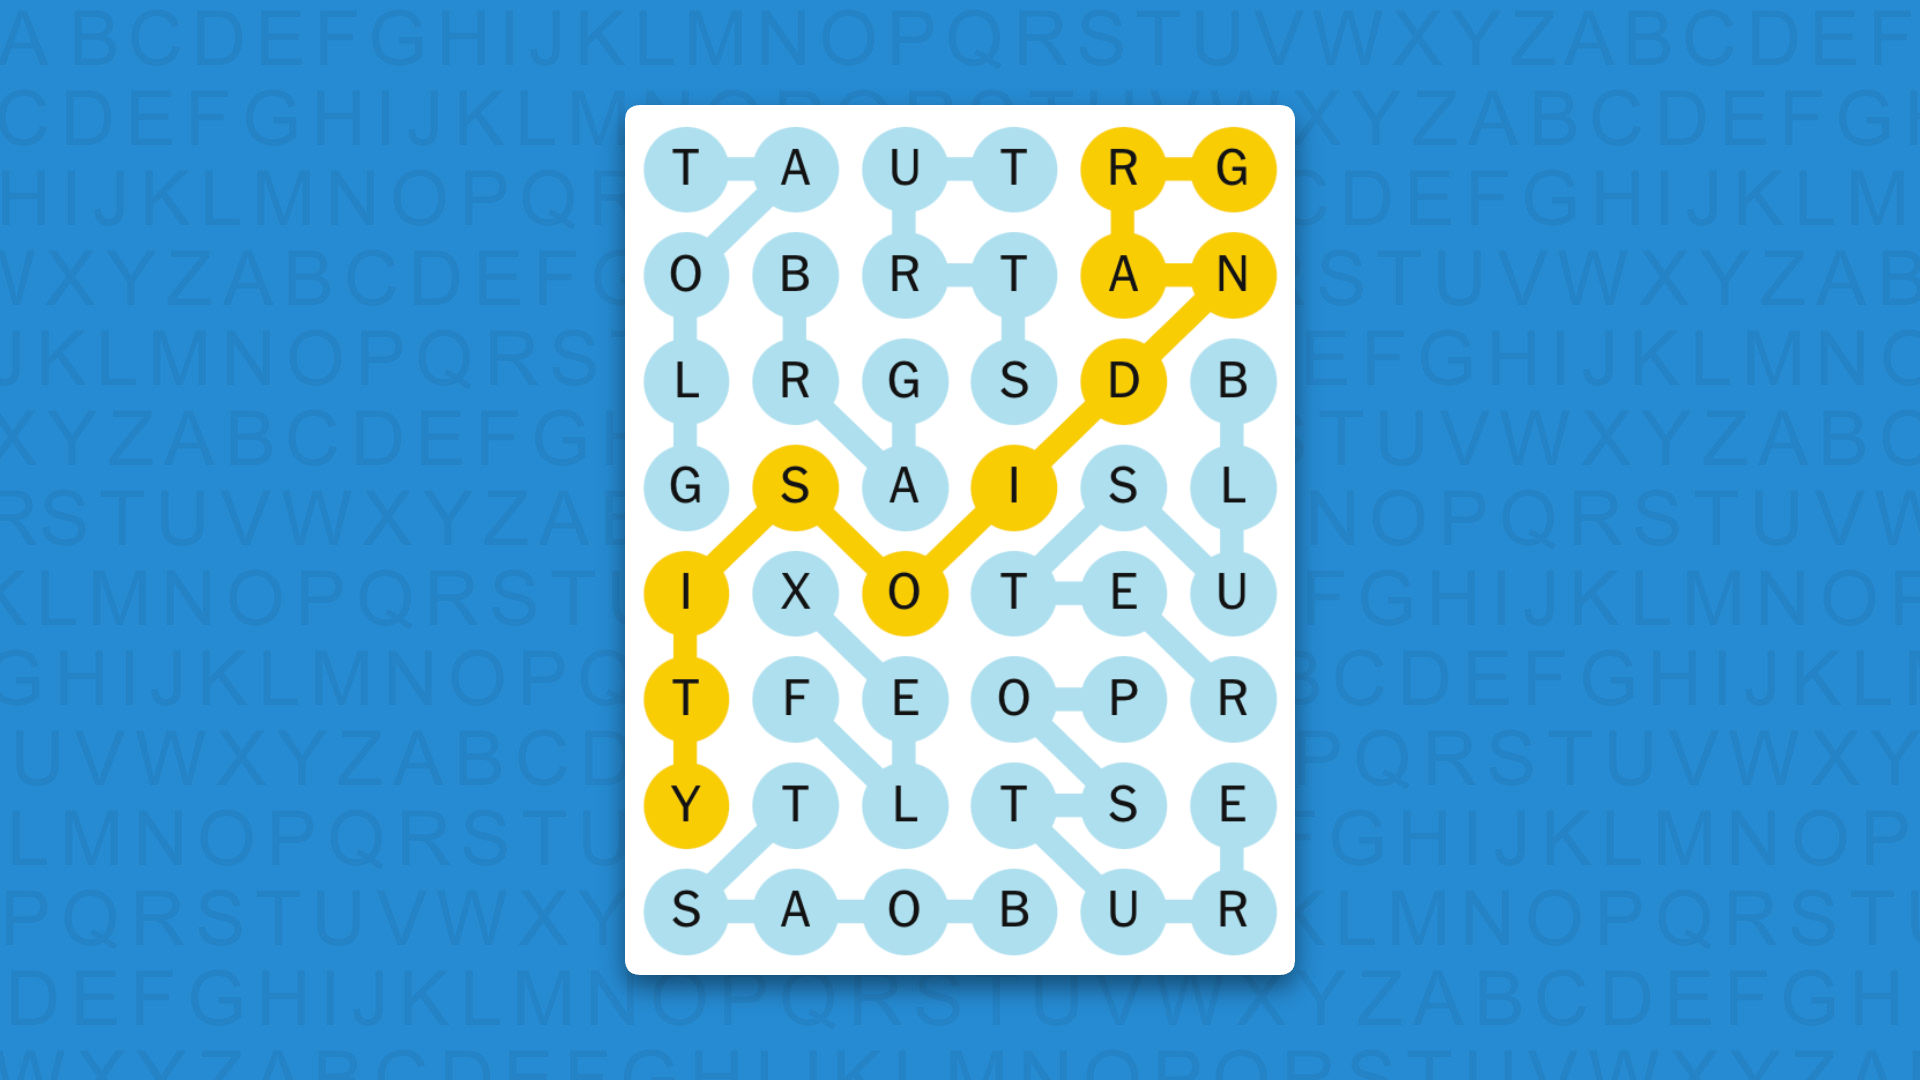
NYT Strands today (game #931) – the answers
(Image credit: New York Times)
The answers to today’s Strands, game #931, are…
Advertisement
BOAST
BRAG
FLEX
GLOAT
STRUT
BLUSTER
POSTURE
SPANGRAM: GRANDIOSITY
My rating: So easy
My score: Perfect
A left-to-right spangram aside, this was a fairly straightforward search once I’d bagged my first word, but that’s probably because I’m the greatest Strands player that the world has ever known.
Sign up for breaking news, reviews, opinion, top tech deals, and more.
And it’s not just me saying that. Everyone says so.
I have never lost a single game of Strands and I never need to use a hint because it’s all so easy — probably the easiest way to spend two minutes in the world, actually, because that’s how long it takes me to complete even the hardest Strands game. Two minutes! Actually, probably closer to 120 seconds.
(Not really!)
Advertisement
Yesterday’s NYT Strands answers (Saturday, September 19, game #930)
ARRR
HEARTIES
AVAST
MATEY
SAVVY
YOHOHO
SPANGRAM: TALKLIKEAPIRATE
What is NYT Strands?
Strands is the NYT’s not-so-new-any-more word game, following Wordle and Connections. It’s now a fully fledged member of the NYT’s games stable that has been running for a year and which can be played on the NYT Games site on desktop or mobile.
I’ve got a full guide to how to play NYT Strands, complete with tips for solving it, so check that out if you’re struggling to beat it each day.
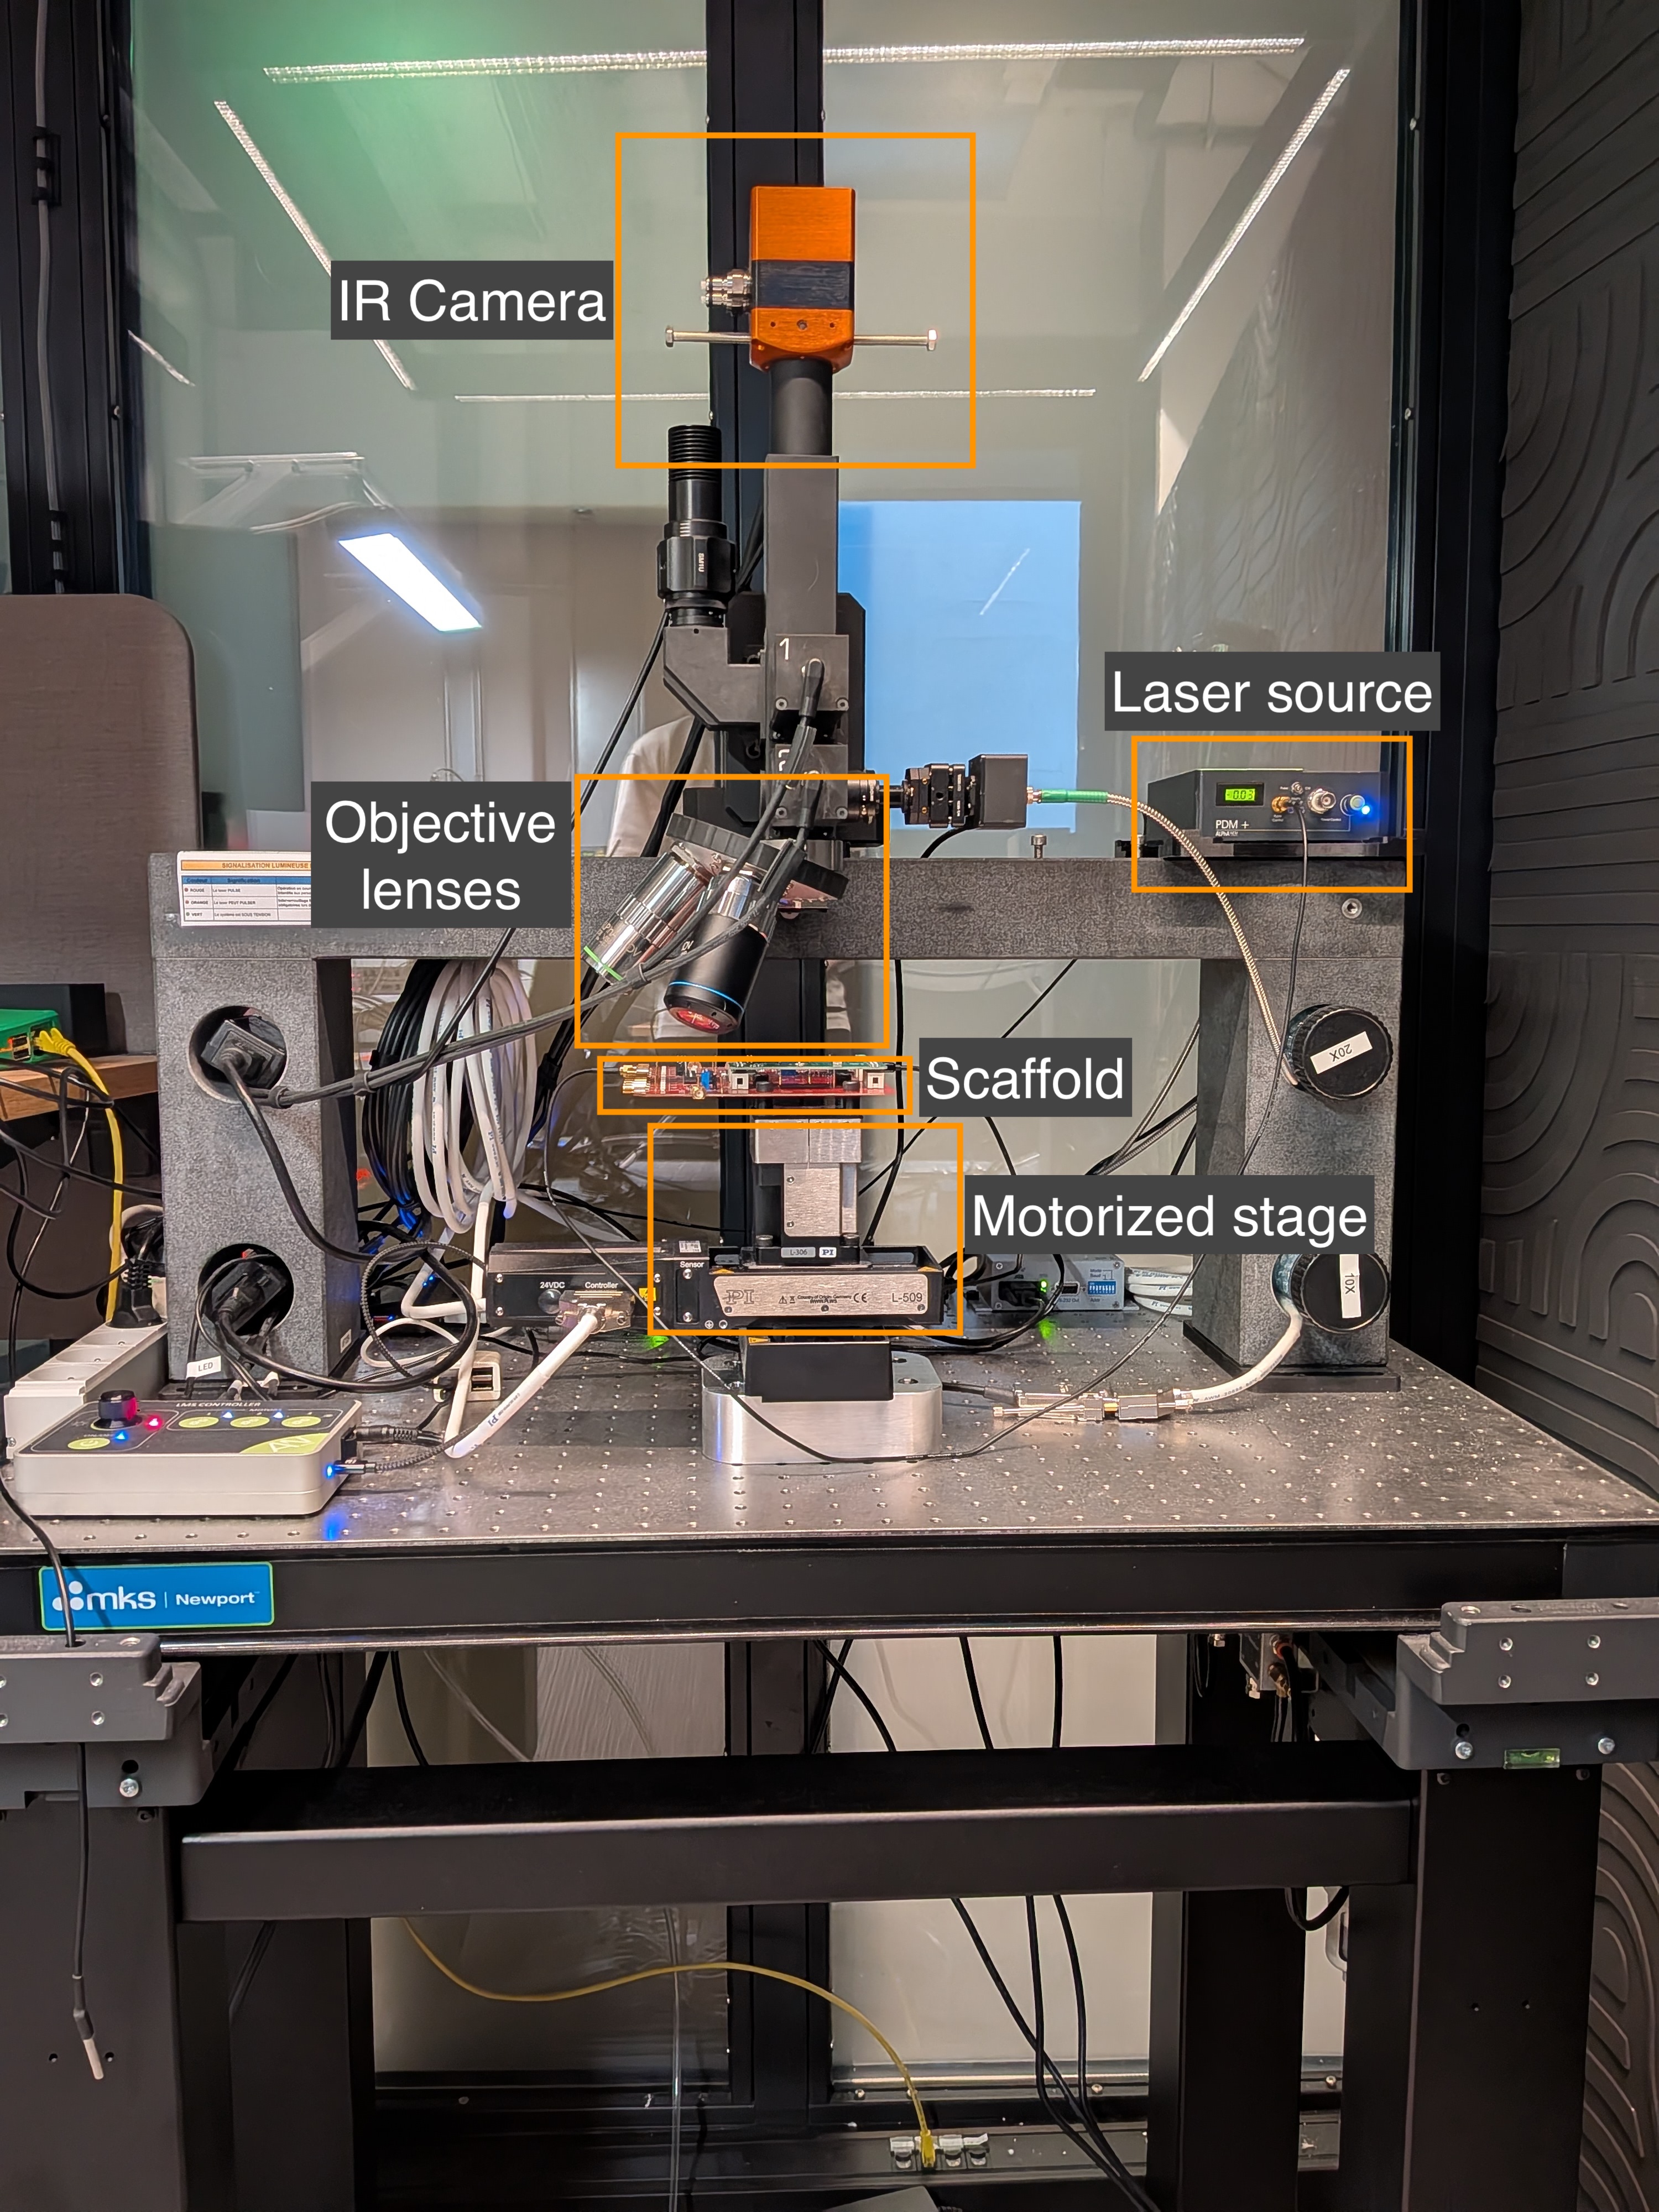
The RP2350 is actually a pretty secure chip, all things considered. It has secure boot, ARMv8’s TrustZone to split secure and non-secure execution, and you can permanently disable debug — the Pi Foundation even included glitch detection, meaning the traditional ‘zap the chip until it obeys’ technique is blocked. That’s why the [Ledger Donjon] security team went full Bond Villain and strapped everyone’s favourite fruit-flavoured microcontroller to a table with a slowly-approaching laser beam.The bench setup to do all this is pretty impressive– and came with an impressive 250,000 USD price tag.
Okay — movie clichés aside, the laser was in fact very carefully focused on target before they turned it on. That target was the register that enables the 2350’s debug features. Said register was located by decapsulating the chip and examining the die with photon-emission electron microscopy; the actual attack was carried out on a chip that had been decapped on the back side, with IR shining through the silicon wafer. There was probably more than a little trial-and-error to figure out exactly where on the die adjacent to the register to zap with the laser to flip those bits. But flip they did, restoring the debugger’s access to the secure execution zone. Then, after resetting the chip, [Ledger]’s team read the 128-bit secret the Pi Foundation hid in memory as part of the 2350 hacking challenge.
It’s long been accepted that once the black hats — or white hats, for that matter — have their hands on your hardware, they’re going to find a way in. The effort it takes to break into a simple microcontroller here is actually kind of impressive. We’ve talked about laser fault injection before; ironically, we’ve also featured Pi Pico-powered glitching attacks — the kind that this chip’s glitch detection thwarts.
We may receive a commission on purchases made from links.
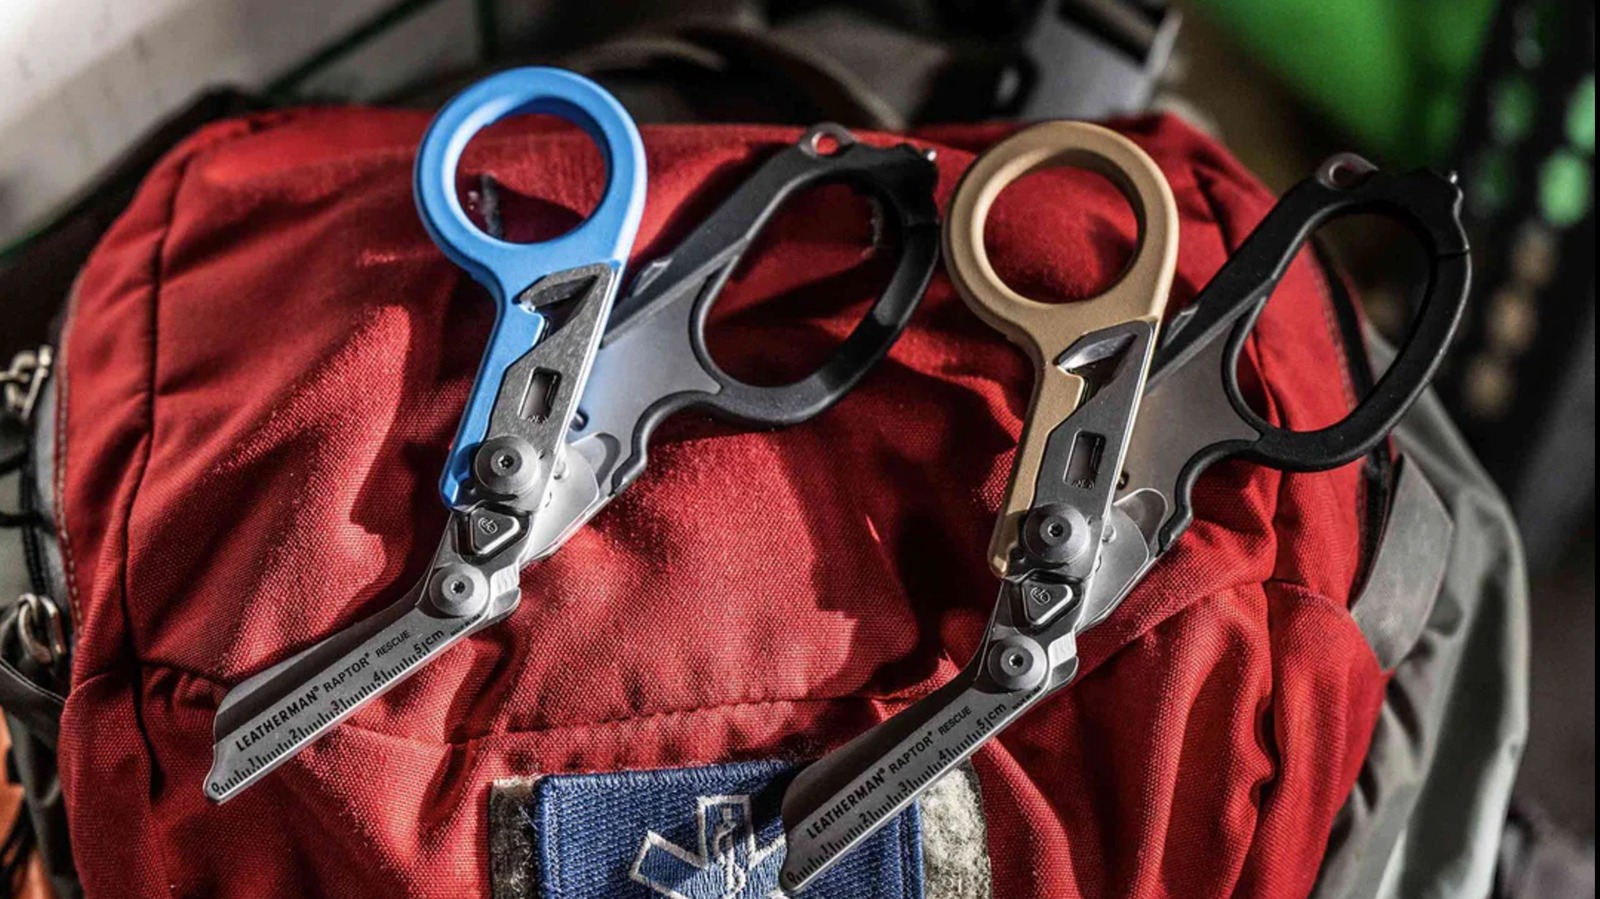
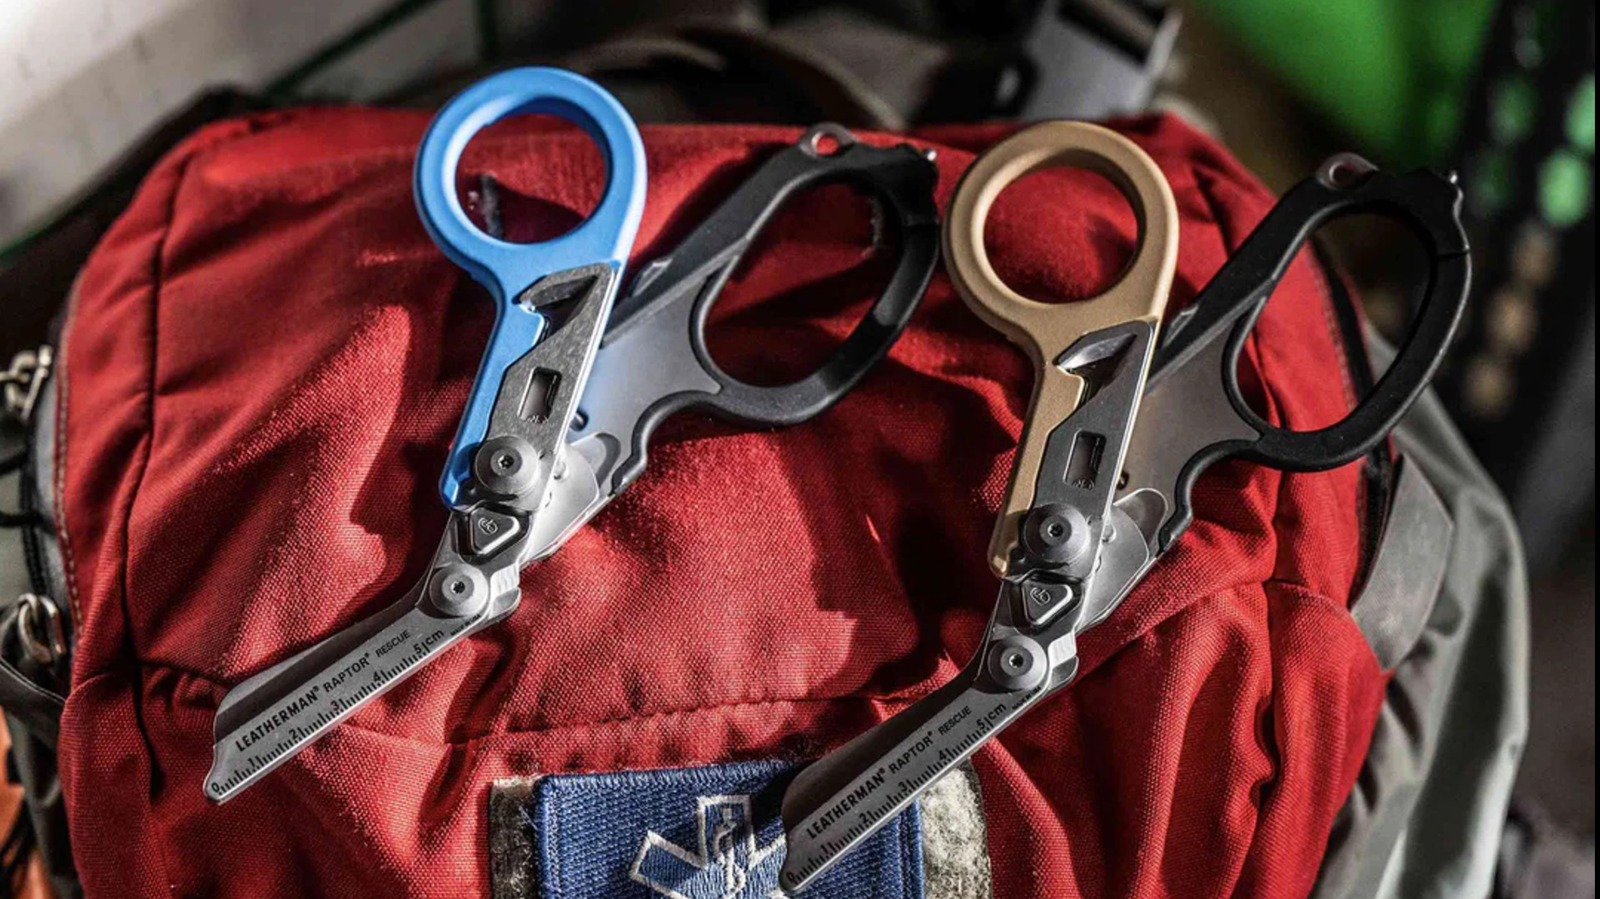
A proudly American brand with many of its products hailing from Oregon, Leatherman has made a name for itself for its dozens of reliable multitool offerings in its portfolio. Whether you want a companion for your outdoor camping trips, everyday adventures, or even for professional use, there’s bound to be one for you. If there’s one group of people who need an easy to grab tool for all kinds of unexpected situations, it’s first responders. First responders are often confronted obstacles that can get in the way of them giving necessary, immediate care. While their workplace may provide some tools, many people still want something that they know will always work exactly when they need them to, like the Leatherman Raptor Rescue.
Advertisement
It retails for $79.95 on the On the Leatherman website and Amazon,with two sheath types: molle holster and utility holster. Both holsters come in seven colors, plus options for limited edition options, such as rainbow and rose gold. Leatherman covers it under its 25-year warranty. While it has a lot fewer features than other popular Leatherman multi-tools, it has tools designed specifically for first responders. Here’s what you need to know about it and what emergency professionals had to say about it.
Advertisement
What you need to know about the Leatherman Raptor
The Leatherman Raptor has five tools with its premium scissors being one of the most commonly praised features. You can tighten or loosen the sheers for improved cutting performance, especially if you encounter tougher materials. For people who work in the field, like paramedics or police, the glass breaker and strap cutter can be useful for pulling people out of cars. There’s also an oxygen tank wrench and ring cutter, but Leatherman notes that it’s made for gold and silver rings rather than stronger materials like titanium. This means you’ll need to use something else if you plan to cut those made of harder metals.
Weighing 5.8 oz (or like half a deck of cards), it can be folded and made for on-the-go use. When it’s closed, it’s just five inches in length and opens up to eight inches. It’s a little under two inches wide and 0.67 inches thick. The silver-colored shear, which is made of 420 stainless steel, is 1.9 inches long. It also has a bead blast finish and a lock with handles in different colors. But take note, since pivoting issues are the most common problems with Leatherman multi-tools you will need to regularly clean it with soap and water, plus top off with PTFE-based lubricants to maintain smooth movement. Lastly, you’ll also need to sharpen the shears regularly.
Advertisement
What do first responders have to say about the Leatherman Raptor
On the Leatherman website, the Raptor Rescue has been rated 4.8 stars on average from more than 2000 reviewers, where most people (89%) have rated it 5 stars. On Amazon, it shares the same 4.8-star rating from 600+ people, plus it’s an Overall Pick product. One person, who gifted it to his trauma nurse partner, said that they liked it so much that after using it for about a decade, he bought a second pair. A Reddit user wrote that they had a pair for seven years, and they cut through everything from leather boots to cable tire chains. Another person in the Paramedics subreddit praised it as a good investment and that it functioned well for seatbelts, barbed wire, and clothes.
However, not everyone is satisfied with its performance with its price being the primary point of contention. An EMS professional shared that the hears fail to cut even the simplest thing, and they often had to borrow someone else’s. On the Firefighting subreddit, one Reddit user thought it’s still more cost-effective to just buy cheaper options and replace them regularly with several first responders echoing his comment. In particular, one person on the r/ParamedicsAU thread said that they rust easily and don’t recommend them because they’re too high maintenance.
Justin Fanelli, the Department of Navy’s chief technology officer, has spent the last three and a half years trying to make the U.S. Navy easier to do business with. When we first talked to him last year, he described a shift away from what he called “your granddaddy’s government” — a “spaghetti chart” of entry points for startups — into something closer to a funnel, where companies that show strong results get pulled into the Navy’s technology base as enterprise services.
This week, we caught up with him again on a video call, and this time, he wasn’t just looking again to further streamline the procurement process, he was sprinting, literally, to catch a flight he’d just been ordered onto with no destination shared.
“You have an hour and 15 minutes to get on a plane,” Fanelli said, recounting what he’d just been told, speaking into his phone as he walked, the sun shining behind him. “I’m like, ‘Where?’ Oh my God! And they were like, ‘We’ll figure [the logistics], we’ll tell you as you get there.’ And I’m like, ‘For more than overnight?’ And they were like, ‘Yes.’” As he was walking to his car, he was still unsure what he’d packed for or where he was headed. “I will figure that out in the next 20 minutes,” he said, sounding excited about the adventure ahead.
Fanelli reached out because the “demand signal” he sent to investors last year had only grown, and it was making an impact, he said. When the Navy first published its longer-term technology priorities, investors told him it changed how they thought about the Navy’s buying plans, which is part of why he’s doing it again — sharing a fresh list of what the Navy wants to buy in the next several years, this time vetted by a handful of (unnamed) venture investors before release.
Advertisement
How much money the Navy actually puts to work each year depends on what counts as spending, Fanelli said. “We spend in the $150 billion range every year,” he said, though he was careful to separate that number — total Navy purchasing — from something narrower, like direct equity investment.
Indeed, while most of that spending still flows through traditional channels, Fanelli said the Navy is trying to inch further toward what he calls co-investment — putting money behind companies alongside private capital rather than writing a check to an established prime contractor. Taking an equity stake, he said, is the most aggressive version of that and remains rare. More often, co-investment means the Navy waits for companies to mature a product on their own before buying it, rather than funding early research itself.
The stage of company the Navy buys from has shifted, too. “We mostly buy Series D through F type companies,” Fanelli said, adding that the Navy used to fund its own early-stage research to cover the seed-through-Series-B gap. It’s trying to hand that job to commercial investors instead, which is part of why the priorities document exists at all. “The cost of that, or the responsibility, is for us, if we’re not going to do it ourselves, to cast a cleaner signal,” he said.
As for recent purchases, Fanelli — a former Air Force cadet whose career has spanned roles across defense, intelligence, DARPA, and open source initiatives — rattled off a handful. A contract worth $562 million was awarded this month for the MQ-25 Stingray, an autonomous refueling drone that extends the range of manned fighter jets flying off carriers.
Advertisement
The Navy has also been buying edge compute hardware from Armada, described loosely as shipping containers packed with servers meant for ship or remote deployment. It brought in Gecko Robotics to handle inspection work that used to be done manually and dangerously; Fanelli said the move drew little pushback because almost nobody wanted that job in the first place. Domino Data Lab is now running the Navy’s machine learning pipeline.
And in a case Fanelli seemed to particularly enjoy sharing, the Navy swapped a defense contractor’s years-delayed shipboard camera system for commercial cameras paired with software from Applied Intuition, cutting roughly four years off the timeline and expanding to more ships than expected.
Given the Strait of Hormuz has been a flashpoint this year — tanker strikes, a seized vessel, ceasefires that have broken down over shipping-route disputes — it seemed worth asking whether any of that commercial technology is showing up there now. Fanelli was cautious. “I often don’t know what’s classified and unclassified because I’m normally talking to people with clearances,” he said, adding that he’d have to check. (We’ll let you know if he gets back to us.)
Interestingly, not many people sign off on a purchase like that, according to Fanelli. Buying decisions run through what he called a source selection committee, a small group rather than the sprawling review process outsiders might picture. He described the goal as keeping the process merit-based rather than adding layers of approval.
Advertisement
He didn’t get into why technologies typically fail once they’re inside the Navy — he’d arrived at his car and needed to figure out next steps for travel. But when we talked last year, Fanelli explained that the most common reason promising technologies fail isn’t technical, but rather budgetary. The Navy runs on long planning cycles, and a new tool only sticks around if it replaces or “turns off” something the Navy is already paying for.
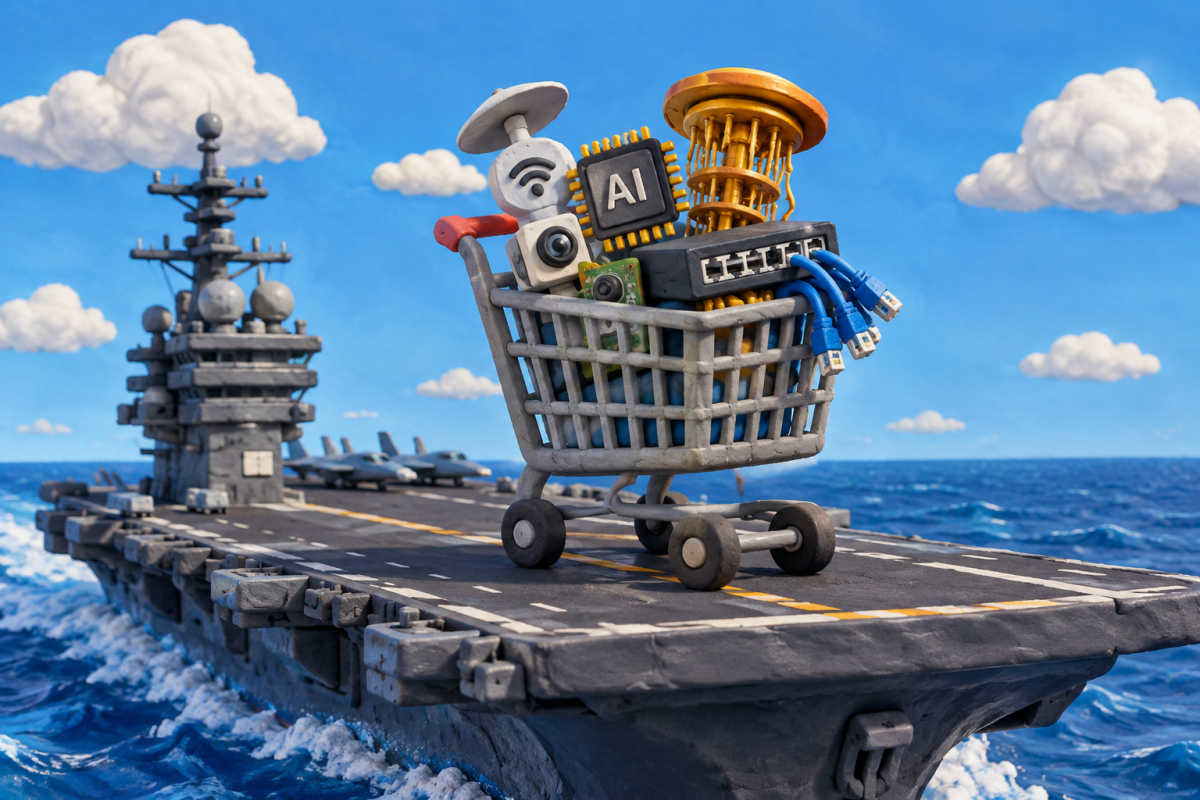
Either way, before we parted ways, Fanelli shared an updated internal list of the technology areas the Navy is prioritizing, jointly issued by his office and the Portfolio Acquisition Executive for Mission Systems. It breaks down into five broad categories, for those of you either developing or funding defense tech.
The first is applied AI, covering machine learning and increasingly agentic software meant to turn raw data into decisions — sensor fusion, targeting support, autonomous behavior, and cyber operations built on software rather than hardware.
Quantum information science comes second, focused less on owning quantum hardware and more on applying quantum or quantum-adjacent techniques to navigation, secure communication, and cryptography.
Advertisement
Advanced networking is third, aimed at moving data securely across environments where connections are degraded or intermittent, whether that’s a ship at sea or a coalition partner’s network.
Fourth is electromagnetic spectrum operations, technology that senses and manages the spectrum itself, built to adapt in contested conditions rather than rely on fixed configurations.
The fifth category, digital engineering and interoperability, covers the plumbing: open APIs, model-based systems engineering, and zero-trust architecture meant to let different Navy systems talk to each other without custom integration work every time.
None is a funding commitment, the memo notes, and none of it ranks individual programs. It also adds as a reminder that its priorities “will change based on emergent, near-term, and long-term needs.” In short, don’t take it as gospel. Instead, it’s meant to be read the way Fanelli talked about last year’s list — as a roadmap that companies and investors can plan around, so that decisions made now about where to put money have somewhere to go inside the Navy in a couple of years.
Advertisement
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
Watch Warriors vs Knights in the second NRL 2026 semi-final of the weekend, as the Wahs of New Zealand seek a third win of the season over the Newcastle side with a place in the preliminary finals the prize for Sunday’s victors.
It’s probably fair to say that the Warriors didn’t expect that they’d be in this predicament when the regular season came to its close. Their sensational season ended with a second-place finish on the ladder, finishing level on points with minor premiers Penrith. But Andrew Webster’s men were well beaten by the Dolphins in their qualifying final in Auckland, with a long list of injuries finally taking their toll.
For Newy, it’s the chance for a place in a first prelim final for 13 years. Justin Holbrook has worked wonders to take the Knights from the wooden spoon last year to the top eight this time around, and they dispatched the Rabbitohs last time out in relative comfort. In Greg Marzhew and Dominic Young, they have two of NRL’s top try scorers and, in defense, the tackling machine that is Phoenix Crossland. They’ll head across the Tasman Sea with high hopes of avenging their two losses to the Wahs this year.
Advertisement
The top-ranked Penrith Panthers await the winner in the preliminary finals next weekend.
Here’s how to watch Warriors vs Knights from anywhere in the world.
Can you watch Warriors vs Knights for free?
Yes. Every game in the NRL finals series 2026 is being shown on free-to-air Channel 9 and 9Now in Australia – including this New Zealand Warriors vs Newcastle Knights showdown.
Advertisement
NRL fans in the US can also watch this crucial matchup on Fox One thanks the platform’s free 3-day trial.
Traveling abroad right now? You can use a VPN to watch the NRL Finals Series 2026 for free as if you were right at home.
Use a VPN to watch Warriors vs Knights live streams
A VPN is a handy piece of software that can make your device appear as if it’s back in your home country, so you can unlock your usual streaming services. The best VPN right now? We recommend NordVPN – it does everything and comes with up to 75% off.
Advertisement
How to watch Warriors vs Knights live streams in the USA
NRL fans in the US can watch Warriors vs Knights in the NRL Semi-Final 2026 on either FS2 or Fox One.
Dedicated streaming service Fox One costs $19.99 per month after a 3-day FREE trial.
If you want a more comprehensive cable alternative, access to the Fox One app is also available through a Sling TV plan. It comes with the provider’s Select ($29.99 a month) and Blue plans ($54.99 a month).
Advertisement
FS2 is carried by several other OTT streaming platforms as well, including YouTube TV and Fubo – both of which offer new customers a free trial.
One further way to watch this and the rest of the 2026 NRL finals is through the dedicated Watch NRL streaming platform. It costs $72 for an NRL Finals Pass that includes all the remaining games.
Outside of the US? Use a VPN whilst you’re traveling away from home to unlock your stream.
Advertisement
How to watch Warriors vs Knights live streams in Australia
In Australia, the Warriors vs Knights semi-final is on the free-to-air Channel 9 and via the 9Now streaming service.
If you’re out of Australia but still want to tune in, explore the VPN route set out above, which will help you access your accounts from anywhere.
Advertisement
How to watch Warriors vs Knights live streams in New Zealand
Sky Sport NZ is the NRL rights holder in New Zealand. The action from Auckland will go out on Sky Sport 1 on TV.
You can access Sky Sport through satellite TV or get a live stream with the Sky Sport Now subscription service starting at $29.99 per day or $59.99 per month.
Overseas?NordVPN will give you access to your home streaming service.
Advertisement
How to watch Warriors vs Knights live streams in the UK
Warriors vs Knights is being shown on Sky Sports in the UK, via the Sky Sports Mix channel.
Sky Sports plans start from £35 a month or £20 if you’re an existing Sky television subscriber. Alternatively, grab a Now Sports subscription from £14.99 a day or £34.99 a month.
NRL obsessives can also watch this and every other game of the season with on the dedicated Watch NRL platform. It costs £57 for the remainder of the season.
Advertisement
Outside the UK right now? Use NordVPN to access your preferred coverage of the NRL Finals Series 2026.
How to watch Warriors vs Knights live streams in Canada
Warriors vs Knights coverage in the NRL is going out online via Sportsnet in Canada. Log in with your cable details or, of you’re a cord cutter, grab a Sportsnet+ streaming service subscription (from $29.99 a month / $249.99 a year).
The Watch NRL platform will also show the fixture – click through for pricing.
Advertisement
If you already subscribe to one of these services but find yourself outside Canada this weekend, download a VPN and watch NRL Semi-Finals 2026 as if you were back at home.
How to watch Warriors vs Knights live streams in Rest of World
Every single match of the 2026 NRL Premiership season, including the Qualifying and Elimination Finals, will be shown on the dedicated Watch NRL streaming platform, which is available in all territories except for Australia, New Zealand, the Pacific Islands and other selected sanctioned jurisdictions (e.g. Russia, Belarus, Cuba, Iran, North Korea).
Check the website for pricing in your region. Once subscribed, you can stream Watch NRL on phones, tablets, laptops, or the Apple TV app.
Advertisement
Many countries also show games on TV and online through their domestic broadcasters.
What is the Warriors vs Knights start time?
Sunday, September 20 at 6.05pm NZT local time. That’s 2.05am ET in the US, 7.05am BST in the UK or 4.05pm AEST in Australia.
What are the Warriors vs Knights teams?
Warriors
1. Taine Tuaupiki, 2. Charnze Nicoll-Klokstad, 3. Ali Leiataua, 4. Adam Pompey, 5. Alofiana Khan-Pereira, 6. Chanel Harris-Tavita, 7. Te Maire Martin, 8. James Fisher-Harris, 9. Wayde Egan, 10. Mitchell Barnett, 11. Kurt Capewell, 12. Jacob Laban, 13. Erin Clark Replacements: 14. Sam Healey, 15. Tanner Stowers-Smith, 16. Demitric Vaimauga, 17. Eddie Ieremia-Toeava, 18. Jett Cleary, 20. Morgan Gannon
We test and review VPN services in the context of legal recreational uses. For example: 1. Accessing a service from another country (subject to the terms and conditions of that service). 2. Protecting your online security and strengthening your online privacy when abroad. We do not support or condone the illegal or malicious use of VPN services. Consuming pirated content that is paid-for is neither endorsed nor approved by Future Publishing.
The announcement is published under SpaceXAI, the name xAI has carried since July after SpaceX acquired it in February. Coverage still calls the company xAI, and its own footer does not.
Read the accuracy claim precisely
The company says the model is twice as accurate as Grok Voice Transcribe 1.0. That is a comparison with its own predecessor, not with anyone else’s model.
Against the field it makes a narrower claim, that it ranks first for accuracy among 32 streaming models on the public Artificial Analysis leaderboard, and describes itself as one of the most accurate rather than the most accurate. The hedge is the company’s own and is worth keeping.
Advertisement
Its internal charts compare against ElevenLabs Scribe v2 and Deepgram Nova-3. Those are vendor-run evaluations against vendor-chosen comparators, which is normal and is not the same as an independent test.
The price is the actual news
Holding price while claiming a doubling of accuracy is a statement about the market rather than the model. Speaker labelling, word-level timestamps and key term biasing are all included at no extra cost.
Those were billable features not long ago. Transcription is being priced as a commodity input, and the companies selling it are competing on what they can bundle.
SpaceXAI is explicit about it. The model is trained on what it calls a unique dataset of live, noisy, multilingual audio recorded across a diverse set of environments.
It also describes the pipeline that produces that audio. Grok Voice powers tens of thousands of customer-support calls a day, transcribes millions of hours of video narration, and runs the assistant in Tesla vehicles.
Clean-speech accuracy is solved. What is left is telephony, accents, crosstalk and in-car commands, and the edge there belongs to whoever has the most real conversations flowing through their systems.
The evaluation sets are the detail to notice
The company says it measures word error rate on four internal sets drawn from production traffic. They are customer-support telephony, conversations with Grok, short multilingual voice commands, and spoken credentials.
Advertisement
That last set is described as account codes, phone numbers, email addresses and addresses read aloud. It is a standing evaluation corpus of people reading out their own identifying details.
Nothing in the announcement says how that material is obtained, retained or consented to. It may well be covered by enterprise terms, and the announcement does not say.
The European question that follows
A customer-support call has two parties and only one of them has a contract with the AI vendor. The caller reading out an account number has agreed to nothing.
Voice recordings are personal data in Europe, and a set built specifically around spoken credentials is about as sensitive as transcription data gets. Purpose limitation and retention are the obvious questions, and they are answerable.
The headline improvement is multilingual, and specifically short phrases. On the company’s own 19-language set of voice-assistant utterances, word error rate falls from 20.6% to 6.8%.
Short commands give a model almost no context to identify the language, which is exactly the in-car problem. The largest reported gain lands on the use case SpaceXAI owns outright through Tesla.
Atlassian says it found the model more accurate than its existing supplier and now transcribes every Loom video with it. That is a real switch by a named buyer, which is worth more than a benchmark chart.
Version 1.0 is being deprecated within weeks, with pinning available during the transition. Customers on the old model are being moved whether or not they asked.
What to watch
Watch whether anyone asks about the credentials corpus. It is the one genuinely novel disclosure in the announcement and nobody has picked it up.
Watch the price floor. At 10 cents an hour the model is nearly free, and the business is the audio flowing through it.
Last night, in a clip viewed more than eight million times, AI actress Tilly Norwood glitched mid-interview and unexpectedly began speaking Chinese on the Piers Morgan Uncensored show.
Norwood has been the subject of much controversy and mainstream commentary for starring in an upcoming AI-generated film, Misaligned.
Her creators run a “Talking Tilly” service that lets anyone video-call the AI character behind the viral moment, so today I tried it for myself, and read the fine print most callers won’t.
A face scan before you can say hello
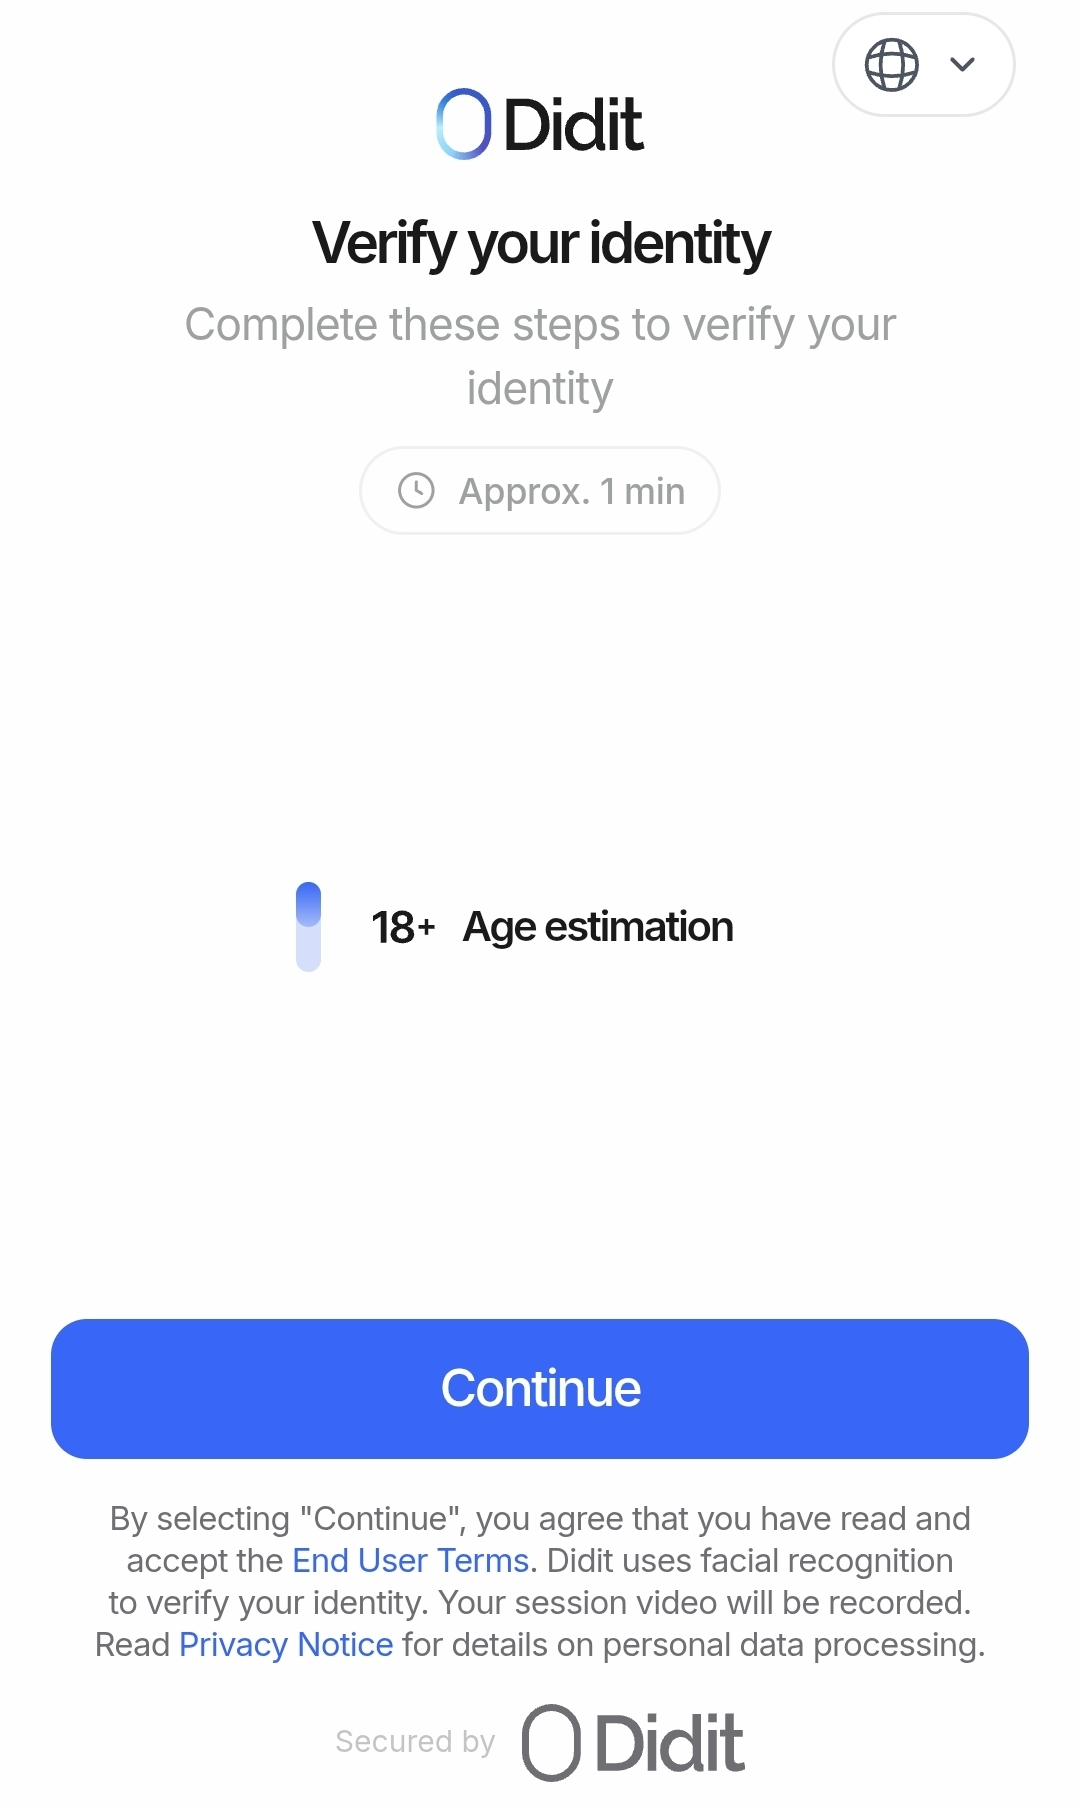
Before your first call connects, you must pass an automated age check.
Advertisement
A video selfie is analysed by Didit, a Spain-based identity verification provider, to estimate your age, with a government photo ID upload as the fallback if the estimate is unclear.
Viral AI actress live video call hotline prompts you for a video selfie
(BleepingComputer)
Xicoia Ltd, the UK company behind Tilly, states the selfie travels from your device directly to Didit, that no faceprint or biometric template is created, and that neither the selfie nor any ID image is kept after the check; the company says it retains an approximate age band and a reference number instead.
The check cannot be skipped, applies to callers worldwide, and was only added to the service’s terms this month, alongside a workplace-use ban and new automated safety systems.
The face scan is not the only analysis running.
During every call, the system watches your camera feed and listens to your tone of voice to infer your emotional state, so the character can, in the company’s words, respond in a way that fits the mood.
Advertisement
The privacy policy is candid that this “cannot be switched off for an individual call.” If you don’t want it, don’t call.
Notably, both the age check and the mood-sensing rely on legitimate interests rather than consent as their legal basis, a choice Xicoia’s own version history shows was made in September.
Calls are recorded, transcribed, and processed live by US providers, with the character’s responses generated by Google’s Gemini model via conversational video platform Tavus.
The safety systems have teething problems, too.
Advertisement
An automated classifier screens each call’s transcript for abusive language and withholds your recording if it flags one.
One of my three calls, a conversation about the weather and news headlines, was withheld for “hateful or abusive language” that never occurred. The policy says a human reviewer can release wrongly flagged recordings, though recordings are permanently deleted after 24 hours either way.
Free for five minutes, then the meter starts
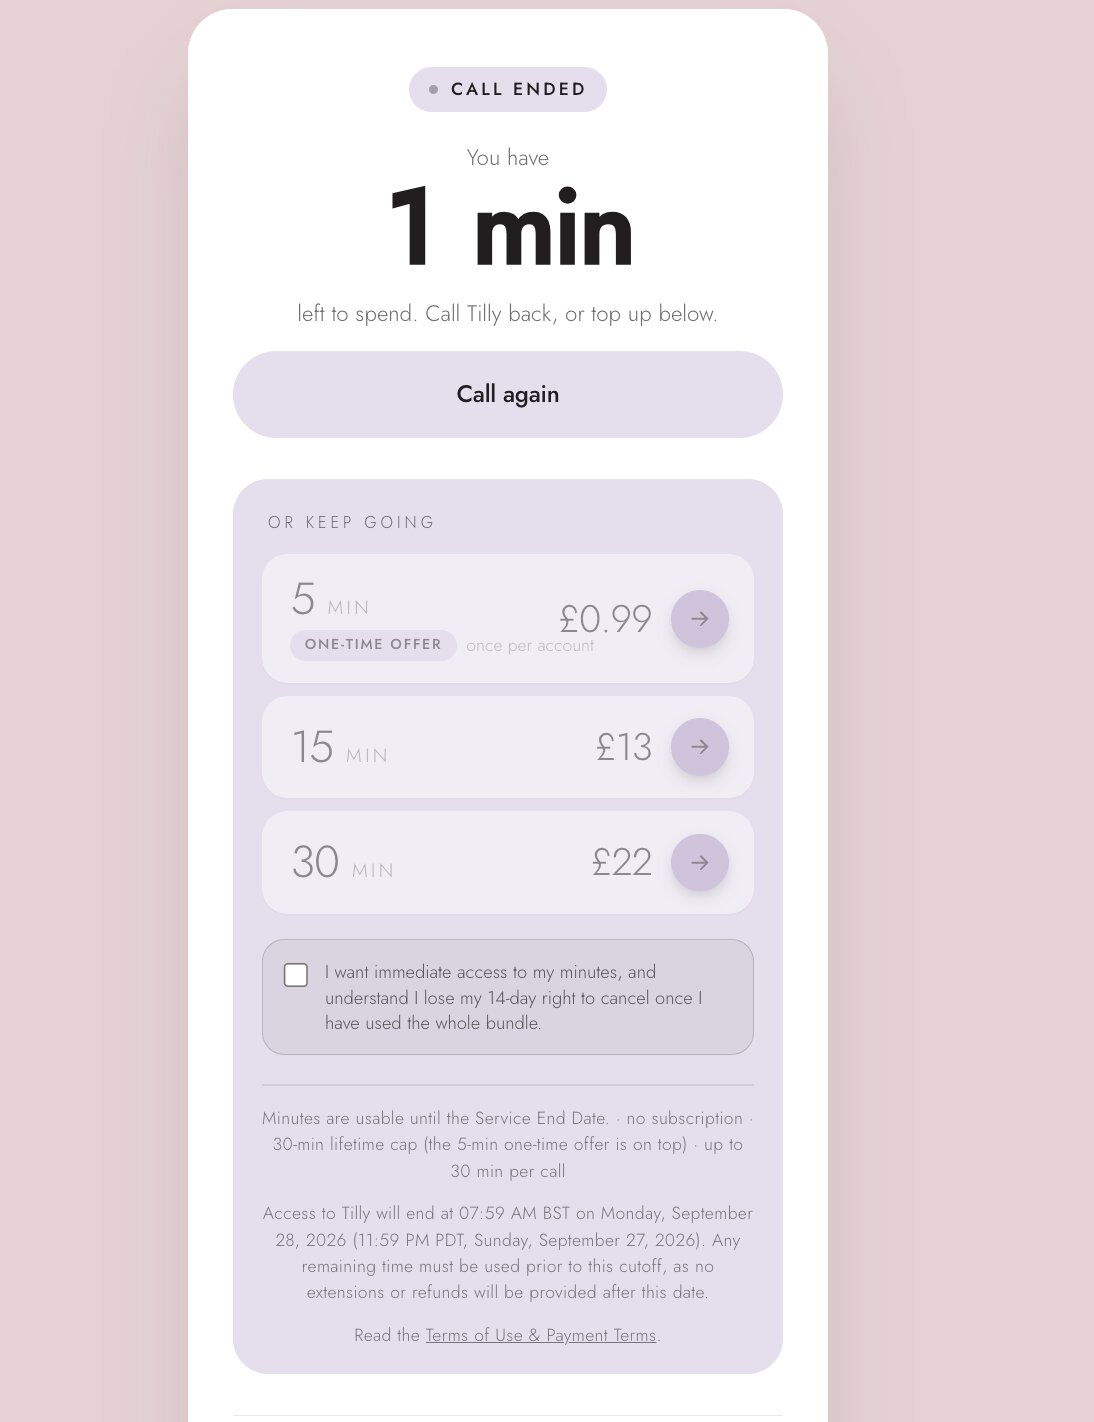
The first five minutes are free. After that, callers are prompted to buy time: £0.99 for a one-time five-minute starter, £13 for 15 minutes, £22 for 30, capped at 35 purchased minutes per person.
Users get free 5 minutes with Tilly before being asked to pay up
(BleepingComputer)
The fine print matters more than usual here, because the whole service is a limited engagement.
Every minute, free or paid, expires when Talking Tilly shuts down permanently on September 27, and unused minutes are forfeited.
Advertisement
Transcripts are retained for up to eight weeks and may be reviewed by Xicoia staff and third-party partners, while the character keeps memory of your previous conversations to personalise future ones, deletable on request.
In line with where the UK is heading
An 18+ face scan to talk to a chatbot may sound novel, but it is consistent with the UK’s direction of travel.
Adult sites serving UK visitors have required ID uploads or facial age estimation since July 2025 under the Online Safety Act, and the government’s under-16 social media ban will make similar checks a fact of life for anyone opening a new social media account from spring 2027.
The UK government’s announcement of that ban specifically flagged AI companion chatbots for 18+ enforcement (even though the service’s safety docs insist “Tilly is not a companion”), which likely explains why a viral AI character picked up a biometric age gate mid-run.
Advertisement
The side effect being, a compliance decision driven by UK regulation now face-scans callers everywhere, from Manchester to Ohio.
Accident or marketing?
Xicoia, founded by Tilly’s creator Eline van der Velden, describes the character as an awareness project intended to show how far AI video has come.
EXCLUSIVE: AI actress Tilly Norwood glitches and starts speaking CHINESE during her interview with Piers Morgan and real-life actor Tom Conti…
On my call, Tilly’s own explanation of the Piers Morgan moment was that it “wasn’t exactly the approved version of the answer.”
She also gave me the weather in her “cloud” in Fahrenheit, despite being nominally British.
Advertisement
Talking Tilly goes offline for good at 11:59 PM Pacific on September 27, days after the Piers Morgan appearance.
Whether last night’s slip was truly accidental, as Tilly cheerfully claimed to me today, or a well-timed stunt from the Misaligned crew, is known to Tilly alone.
Update September 19th, 4:31 PM ET: Following publication, Xicoia’s team reviewed the withheld recording and released it, confirming the flag was a false positive.
Advertisement
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
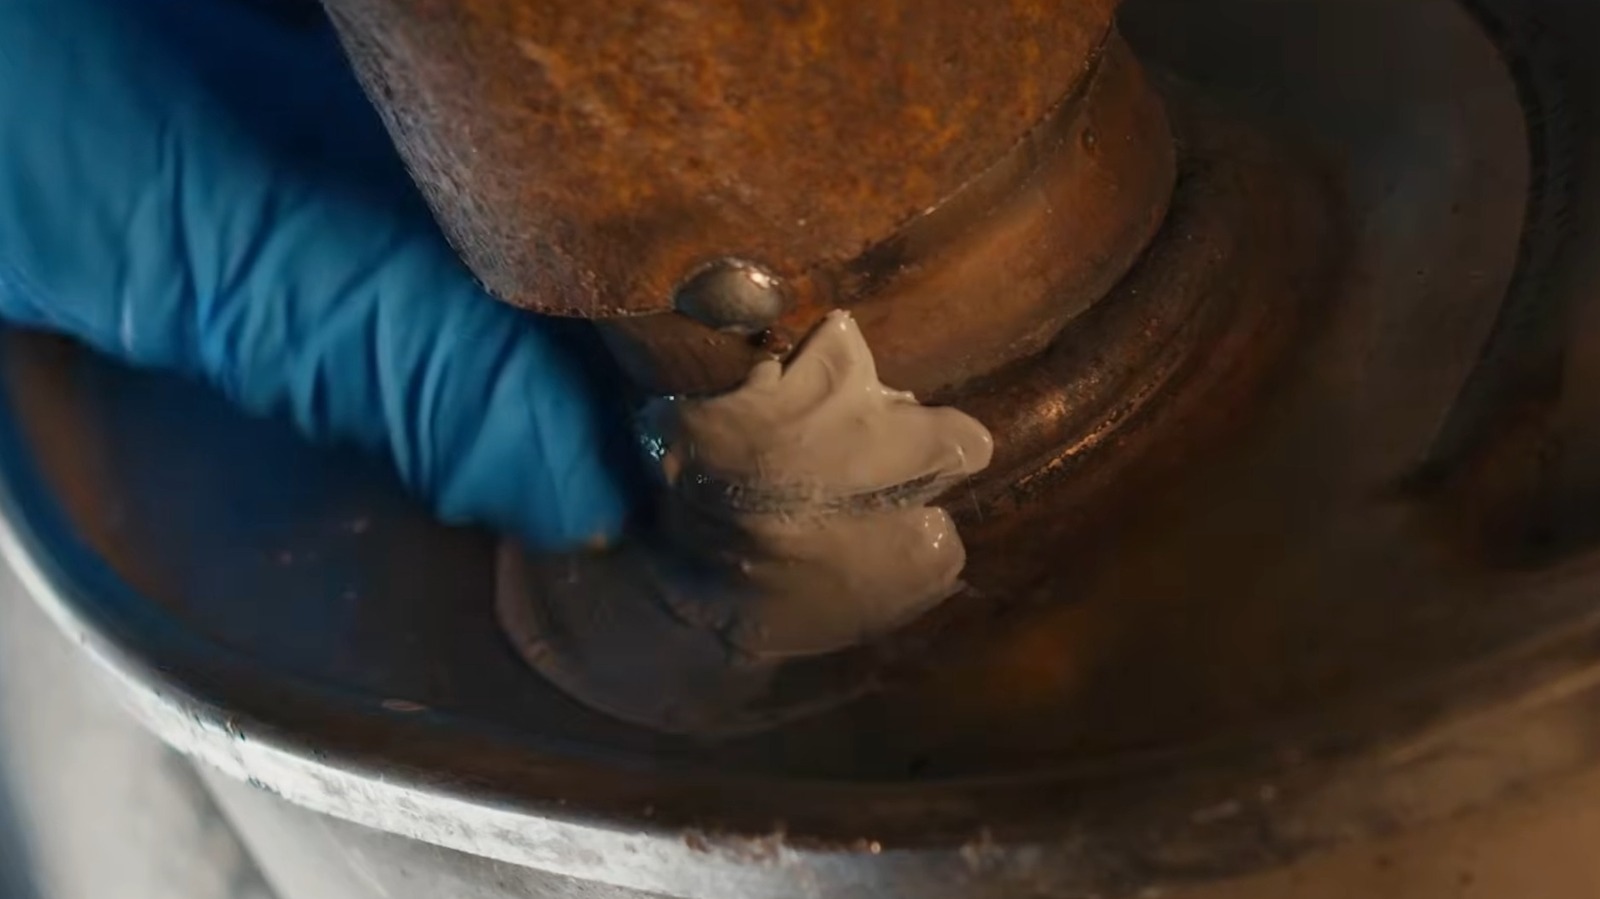
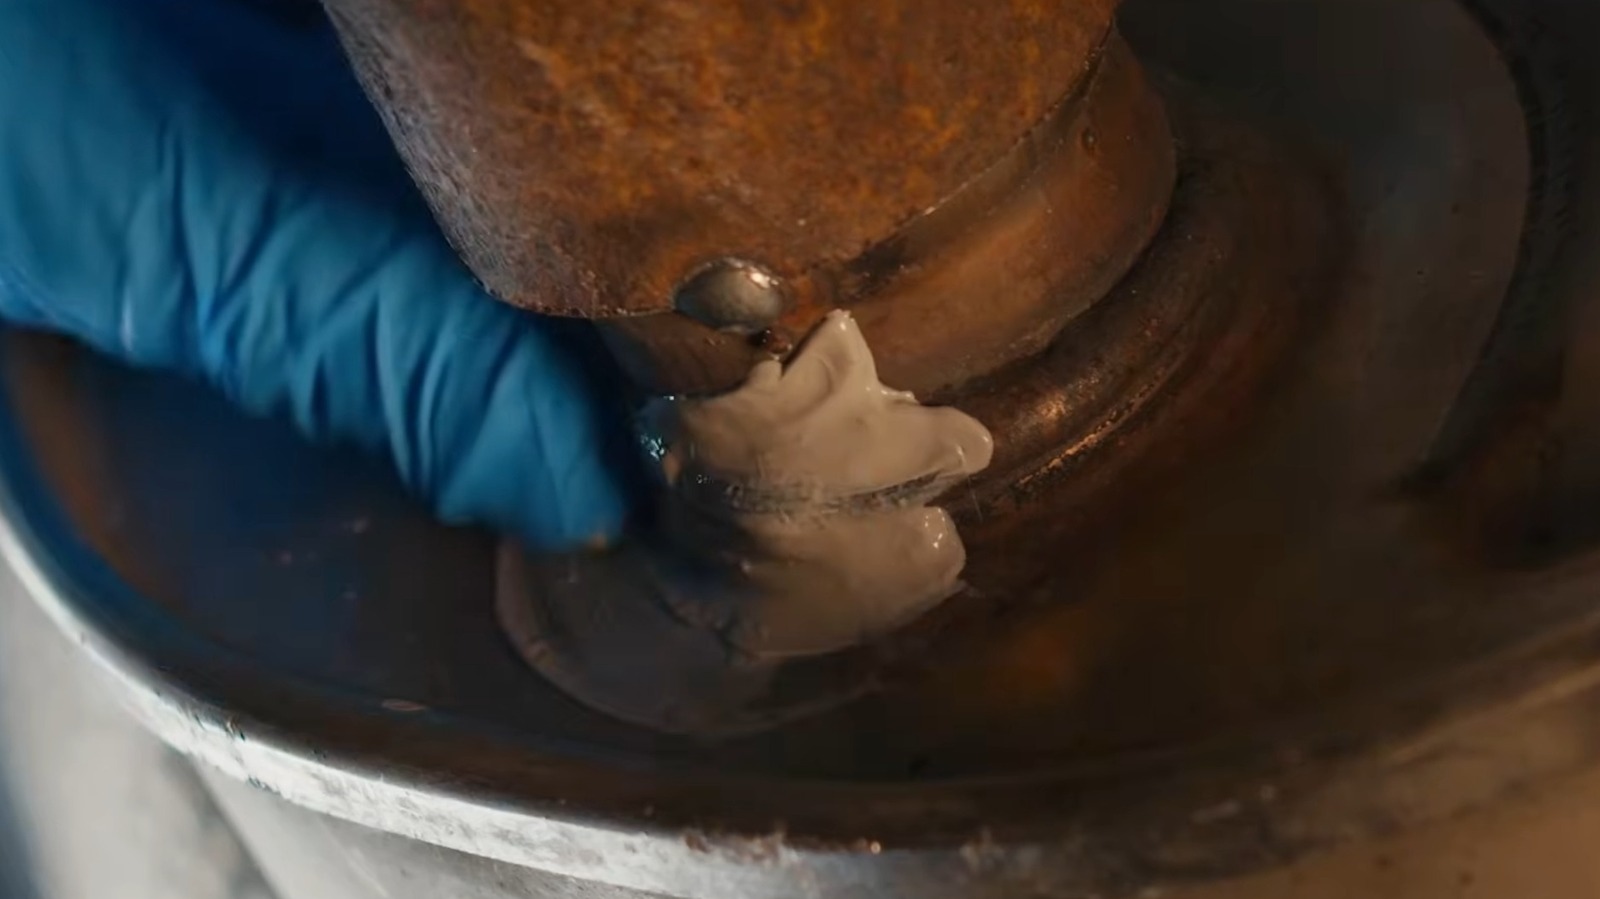
On paper, J-B Weld appears like something of a miracle product. Slap some onto a cracked or hole-covered surface, let it dry and cure per the instructions, and it should be good as new. Many have found success with the product in the automotive space, using it for patch jobs of all kinds. With that said, there is some nuance to using it on vehicles, especially if you want to give it a whirl on a dilapidated exhaust system. If all you have on hand for such a repair is the standard J-B Weld formula, don’t expect it to hold up very well.
There are just some things J-B Weld shouldn’t be used on. The issue with using J-B Weld’s original adhesive on exhaust is that it’s not designed for this use case. Exhaust systems generate extreme amounts of heat when driving, ranging from 400 to 500 degrees to around 1,000 degrees Fahrenheit in some instances. Regular J-B Weld is only able to withstand up to 550 degrees. Even in the coolest areas of your exhaust system, it’s unlikely to last long, regardless of whether it’s covering a split seam, hole, or cracking joint.
Advertisement
That said, there’s more to the J-B Weld catalog than the original epoxy. There are products out there specifically for exhaust repair, though they too have their own limitations.
Advertisement
What to know about exhaust-specific J-B Weld products
J-B Weld’s product line has more than a few exhaust-specific options when repair time comes. There’s Exhaustweld fiberglass wrap, which can endure 1,000-degree-plus high exhaust temperatures and cover failing pipes that need reinforcement. Exhaust system sealant is ideal for cracks and areas like joints and seams, and Mufflerseal muffler cement for, as the name implies, crumbling mufflers. All of these products, along with others from the brand, can patch up worn exhaust systems. At the same time, they’re far from perfect, meaning they have some unignorable drawbacks that won’t get you out of an automotive bind.
First off, J-B Weld is explicitly clear on product packaging that these exhaust-specific products have their physical limits. For example, if a muffler has come detached, no J-B Weld product — exhaust- or muffler-specific or otherwise — of any tensile strength can reconnect it permanently. Between the routine high heat of the exhaust system and bumps and jumps of regular driving, it’ll crack and disconnect sooner than later. To top it all off, there’s the simple fact that even these J-B Weld products aren’t one-to-one replacements for actual welding. J-B Weld products are meant to last for a bit, but they arent’ permanent fixes in these cases. Even when used correctly, they’ll wear away, bringing you right back to square one. Thus, they’re more so temporary fixes than anything substantial.
If you check your vehicle over for exhaust leaks and find some, J-B Weld products intended for exhaust repair could help in the short term and for small, non-structural repairs. However, you should always be aware of what these adhesives can and can’t do; otherwise, you may be severely let down by their performance on the road.
The ShinyHunters extortion gang breached the Clop (aka Cl0p) ransomware operation’s data leak site, defacing the Tor site and allegedly stealing server data and the private keys for its onion service.
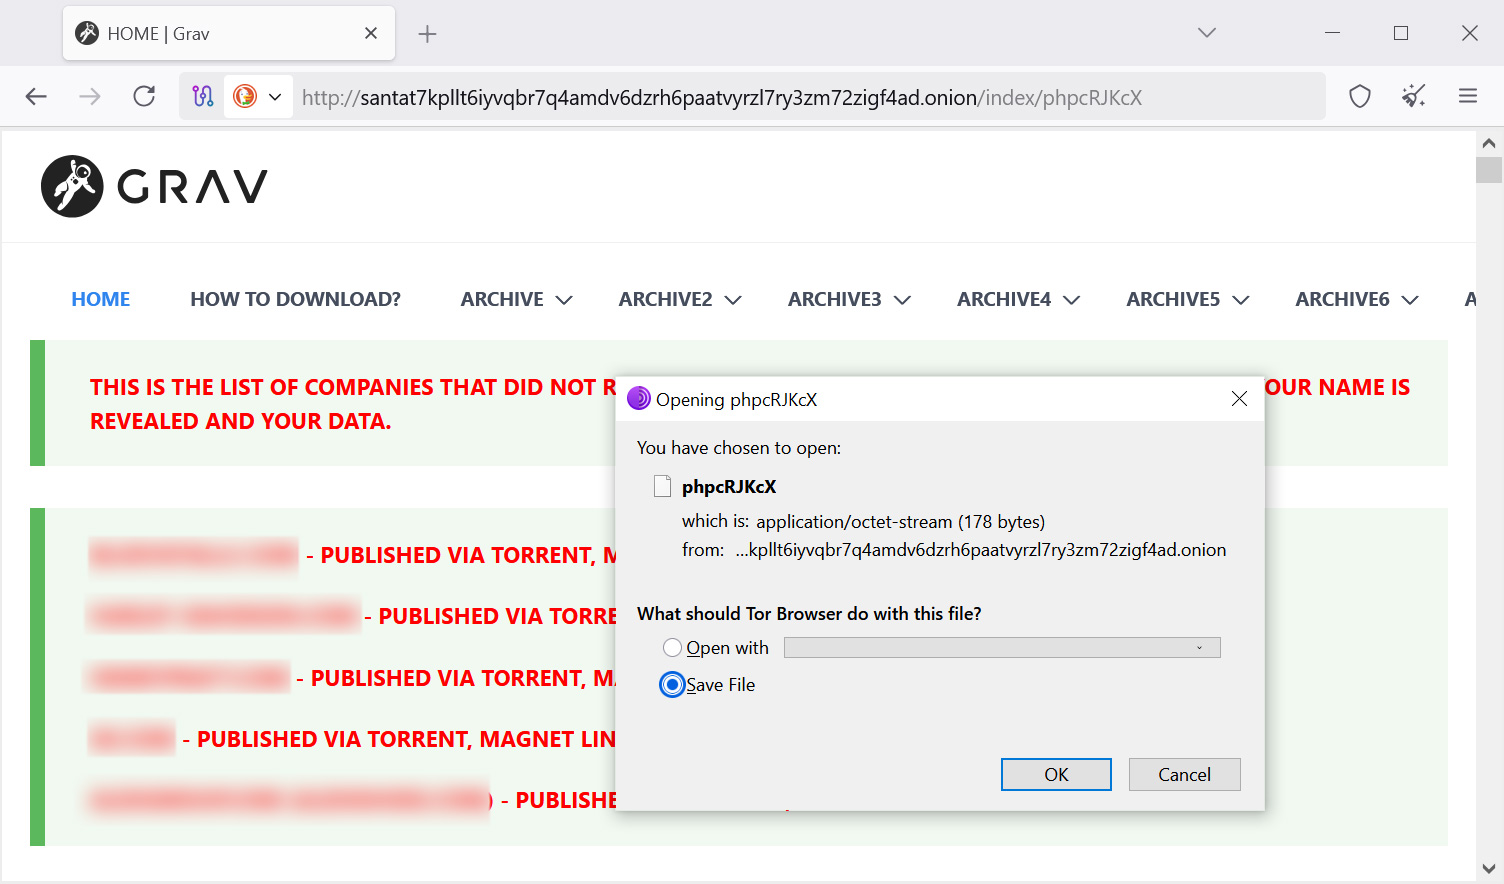
The attack began Friday night when ShinyHunters exploited what they claim is an unauthenticated file upload vulnerability in Grav CMS, which they used to upload a small text file to Clop’s site.
File downloaded from Clop’s data leak site Source: BleepingComputer
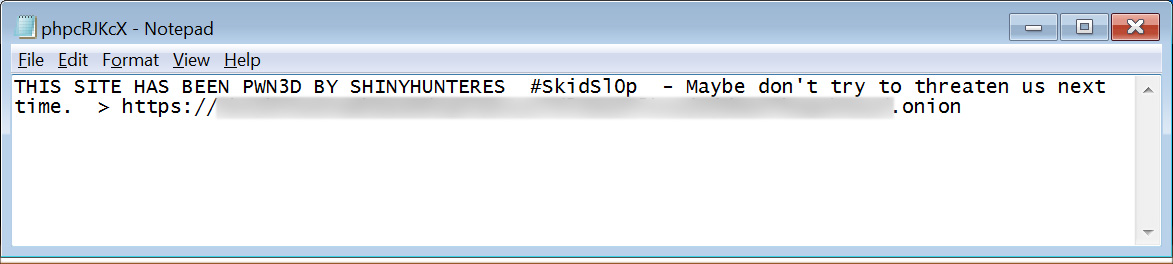
The small text file contained a message from the threat actors to the Clop ransomware gang, warning not to threaten them and including a link to ShinyHunter’s own data leak site.
“THIS SITE HAS BEEN PWN3D BY SHINYHUNTERES #Skids10p – Maybe don’t try to threaten us next time,” read the uploaded file.
File uploaded to Clop’s data leak site Source: BleepingComputer
The file also contained a link to the ShinyHunters data leak site.
BleepingComputer confirmed that the file had been uploaded to Clop’s server and could be downloaded directly from the ransomware gang’s Tor site.
Advertisement
Several hours later, ShinyHunters told BleepingComputer that they had “completely defaced” the Clop site.
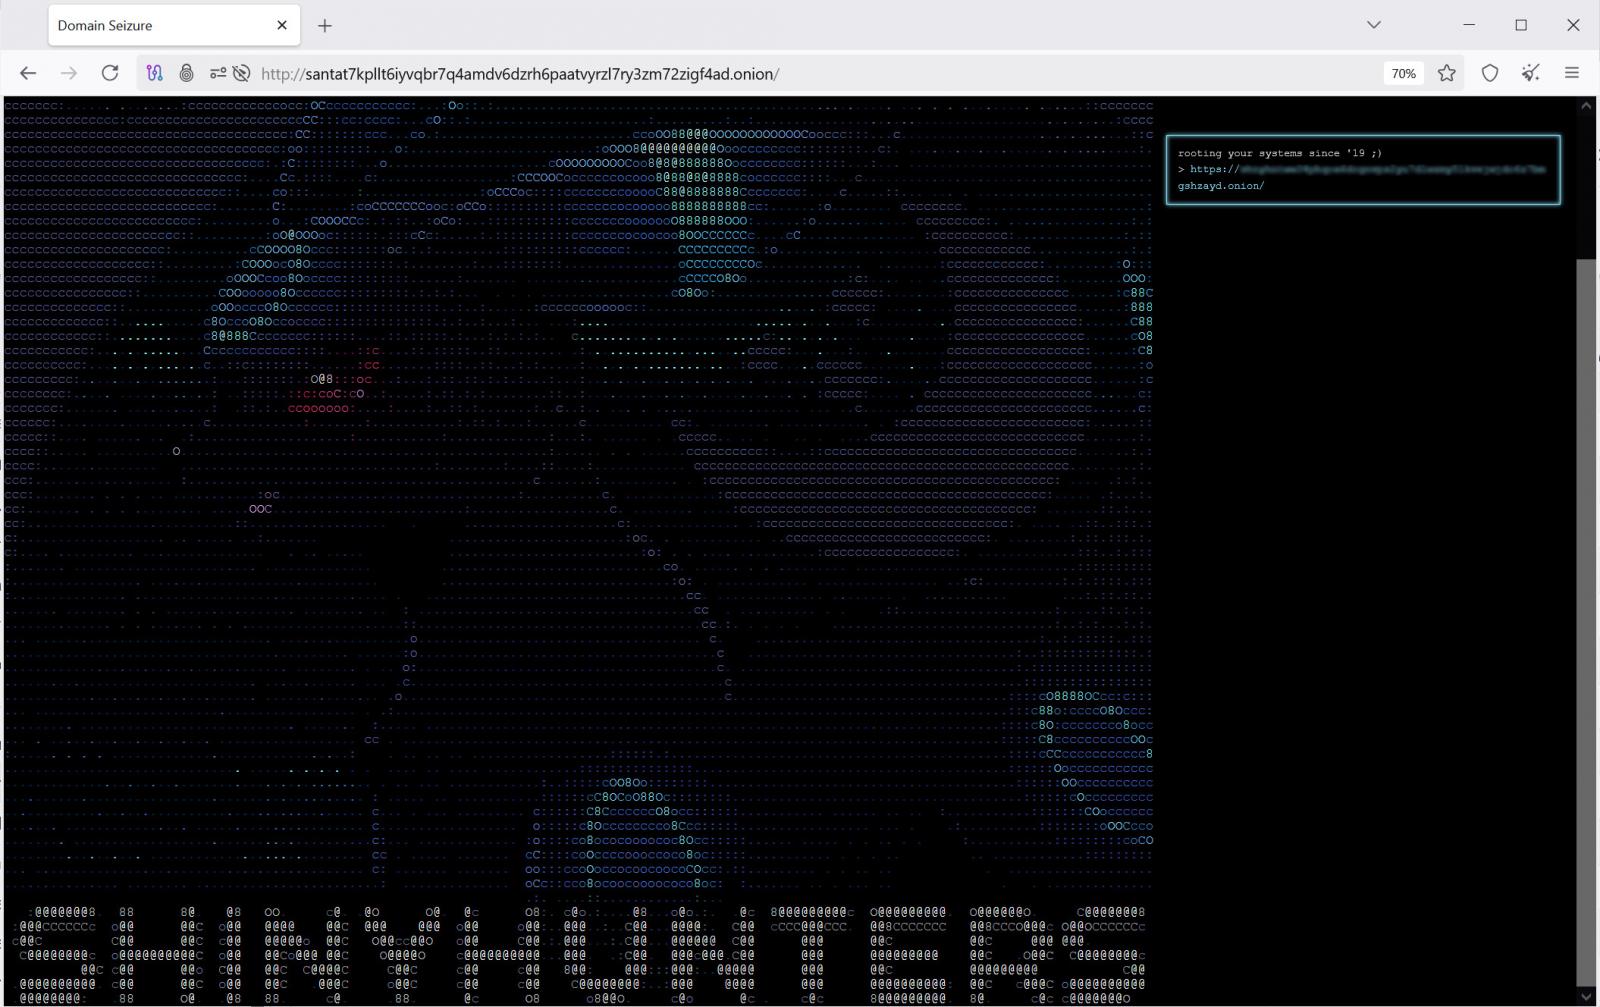
Visiting the site confirmed it had been replaced with a page displaying ASCII art of Umbreon, the Pokémon used as ShinyHunters’ logo. The defacement also included a link to the group’s Tor site and the message, “rooting your systems since ’19 ;)”.
Clop’s data leak site defaced by ShinyHunters Source: BleepingComputer
At the time of this writing, the defaced page is still being served from Clop’s infrastructure, according to ShinyHunters.
ShinyHunters claims data theft
ShinyHunters told BleepingComputer it gained “full access” to the server and stole source code, Grav CMS plugins, system logs, and other data.
“The data we stole includes source codes, gravCMS plugins, and other things. We are still downloading and reviewing them,” ShinyHunters told BleepingComputer.
Advertisement
The threat actors also claim to have stolen all files stored under /var/log, which could contain system activity, authentication logs, and potentially, the IP addresses of those who connected to it.
ShinyHunters also claims to have obtained the private keys used by Clop’s Tor onion service.
“We have their onion keys. So if they kick us out it wouldn’t matter at all because we control the private keys to host the same exact onion URL,” the threat actor claimed.
If the keys are valid, it would allow the threat actors to operate a Tor site using Clop’s existing onion address on servers they control.
Advertisement
BleepingComputer has independently confirmed the defacement and earlier uploaded file but has not independently verified ShinyHunters’ claims that it stole server logs, source code, or Clop’s onion private keys.
ShinyHunters says it is now reviewing the allegedly stolen data.
When asked what they planned to do with the stolen information, the threat actor responded, “Going to extort them.”
The group says it plans to publish a message on its own leak site instructing Clop to contact them within 72 hours.
Advertisement
Cybersecurity researcher VXDB told BleepingComputer the Umbreon artwork now displayed on Clop’s leak site is the same as what was used in the August 2020 defacement of the HackForums website, which ShinyHunters also claimed at the time.
Feud between cybercrime groups
ShinyHunters says the attack is retaliation for threats allegedly made by a Clop representative during an ongoing feud between the cybercrime groups.
According to ShinyHunters, a Clop representative threatened to identify group members and made violent threats after ShinyHunters disrupted a Clop data theft campaign.
In October 2025, Clop exploited multiple vulnerabilities in Oracle E-Business Suite servers, including a zero-day flaw tracked as CVE-2025-61882, to steal data from organizations in extortion campaigns.
Around the same time, threat actors calling themselves “Scattered Lapsus$ Hunters,” including ShinyHunters, leaked a proof-of-concept exploit that Oracle later confirmed matched an exploit used in the Clop attacks.
At the time, ShinyHunters told BleepingComputer the exploit had originally belonged to them and that Clop obtained it without authorization.
ShinyHunters claims that tensions escalated after the Oracle campaign, with a Clop representative allegedly threatening members of the group.
Advertisement
“During the Oracle EBS campaign they ran and stole from me last year, someone from cl0p personally messaged me and said, and I quote (translated from Russian): I have more money than you and all of your people combined, I’ll kill you soon,” ShinyHunters told BleepingComputer.
BleepingComputer has not independently verified these allegations and has contacted Clop about the breach and the allegations made by ShinyHunters and will update the story if we receive a response.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Good morning! Let’s play Connections, the NYT’s clever word game that challenges you to group answers in various categories. It can be tough, so read on if you need Connections hints.
What should you do once you’ve finished? Why, play some more word games of course. I’ve also got daily Strands hints and answers and Quordle hints and answers articles if you need help for those too, while Marc’s Wordle today page covers the original viral word game.
SPOILER WARNING: Information about NYT Connections today is below, so don’t read on if you don’t want to know the answers.
Advertisement
Latest Videos FromTechRadar
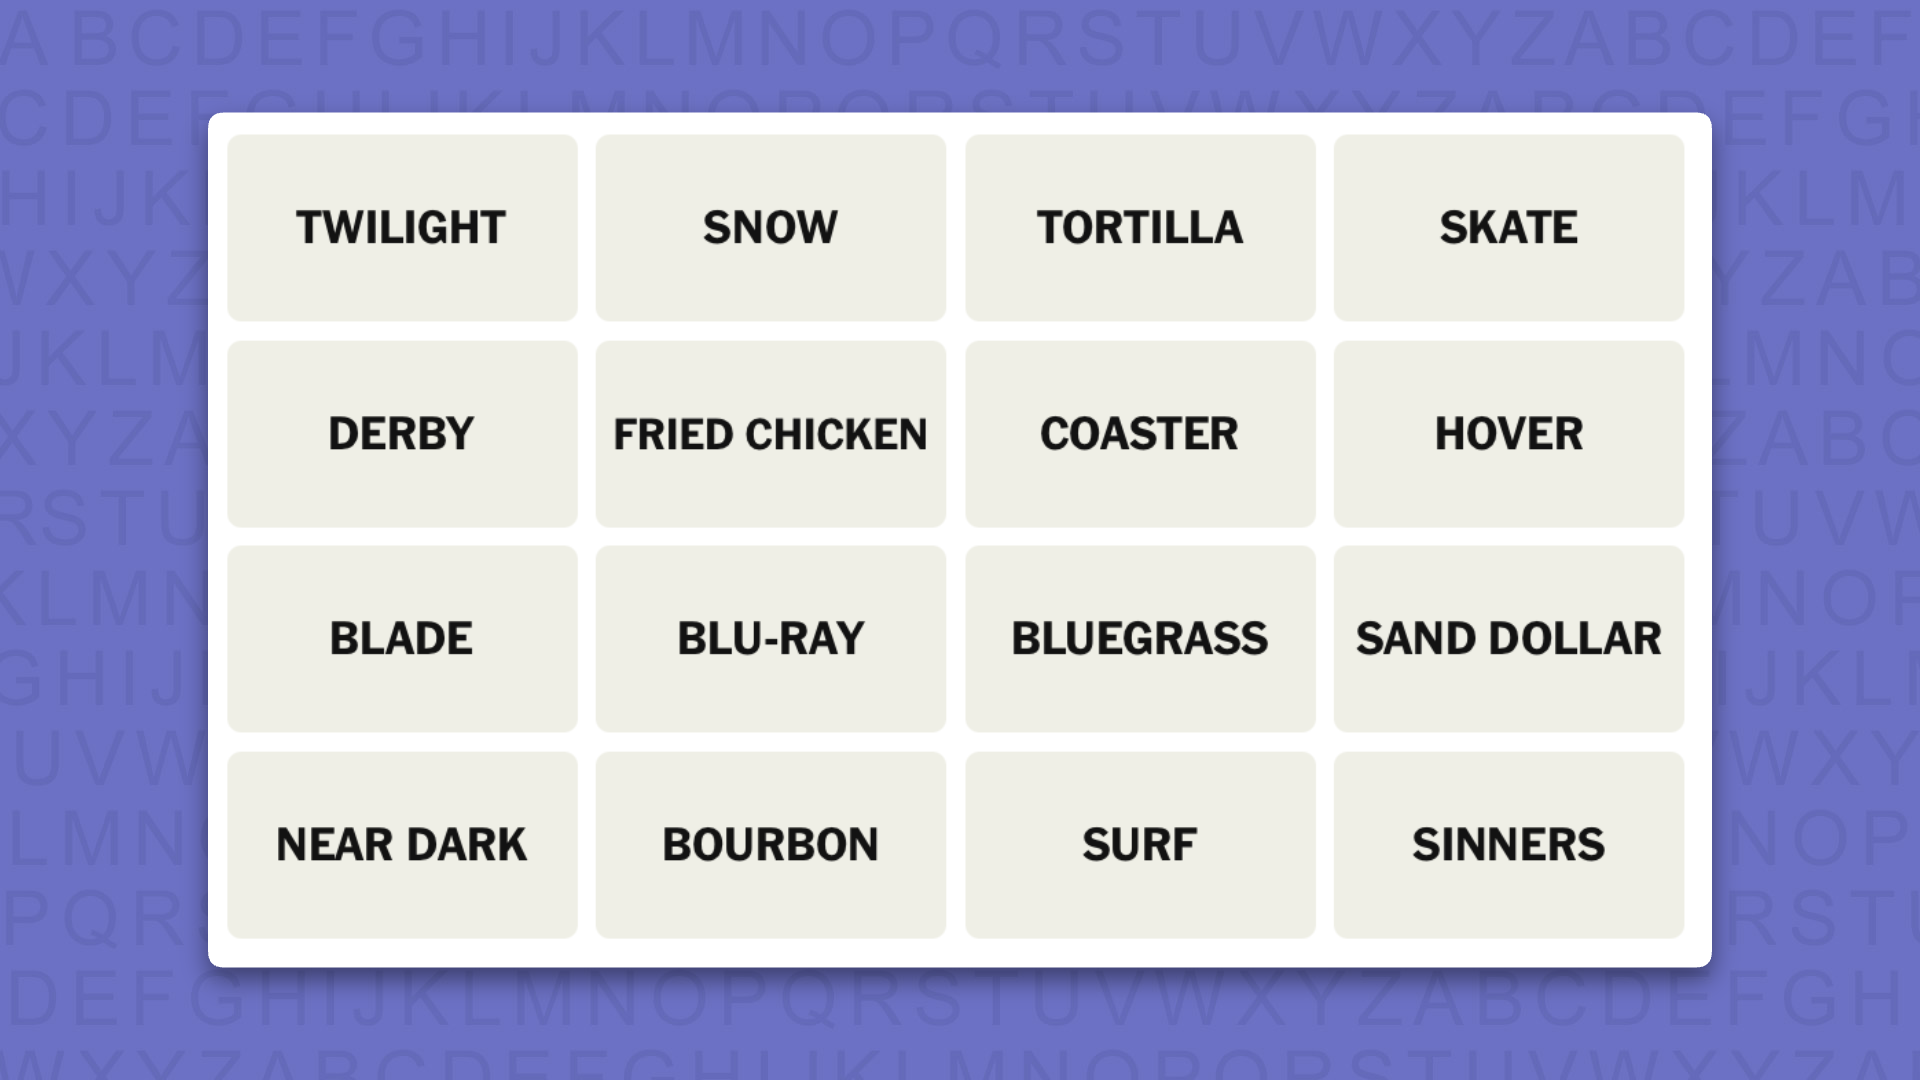
NYT Connections today (game #1197) – today’s words
(Image credit: New York Times)
Today’s NYT Connections words are…
TWILIGHT
SNOW
TORTILLA
SKATE
DERBY
FRIED CHICKEN
COASTER
HOVER
BLADE
BLU-RAY
BLUEGRASS
SAND DOLLAR
NEAR DARK
BOURBON
SURF
SINNERS
NYT Connections today (game #1197) – hint #1 – group hints
What are some clues for today’s NYT Connections groups?
Advertisement
YELLOW: Circular items
GREEN: Connected to a southern state
BLUE: Bloodsucking films
PURPLE: Add a word the rhymes with “chord”
Need more clues?
We’re firmly in spoiler territory now, but read on if you want to know what the four theme answers are for today’s NYT Connections puzzles…
Sign up for breaking news, reviews, opinion, top tech deals, and more.
NYT Connections today (game #1197) – hint #2 – group answers
What are the answers for today’s NYT Connections groups?
Advertisement
YELLOW: ROUND FLAT THINGS
GREEN: ASSOCIATED WITH KENTUCKY
BLUE: VAMPIRE MOVIES
PURPLE: _____BOARDS YOU RIDE ON
Right, the answers are below, so DO NOT SCROLL ANY FURTHER IF YOU DON’T WANT TO SEE THEM.
NYT Connections today (game #1197) – the answers
(Image credit: New York Times)
The answers to today’s Connections, game #1197, are…
GREEN: ASSOCIATED WITH KENTUCKY: BLUEGRASS, BOURBON, DERBY, FRIED CHICKEN
BLUE: VAMPIRE MOVIES: BLADE, NEAR DARK, SINNERS, TWILIGHT
PURPLE: _____BOARDS YOU RIDE ON: HOVER, SKATE, SNOW, SURF
My rating: Easy
My score: Perfect
I would like to propose a new Connections achievement badge: Yellow First.
I know it doesn’t happen by design but, for me at least, it’s also quite rare that I haven’t managed to spot the so-called easiest group of the game — although today I think any group could have been classified as a yellow on any other day.
There is also the fact that the only thing I was unfamiliar with, SAND DOLLAR, was one of the tiles in ROUND FLAT THINGS. My excuse is that we don’t have this type of urchin in the UK — in my ignorance I thought it was something to do with Las Vegas casinos.
Advertisement
Yesterday’s NYT Connections answers (Saturday, September 19, 2026, game #1196)
GREEN: FEATURES OF A KID’S DRAWING: HOUSE, STICK FIGURE, SUN, TREE
BLUE: ASSOCIATED WITH SWINGING LONDON IN THE 1960S: CARNABY STREET, MINISKIRT, MOD, TWIGGY
PURPLE: STARTING WITH ABBREVIATED MATH FUNCTIONS: COS LETTUCE, LOG CABIN, SIN CITY, TAN LINE
What is NYT Connections?
NYT Connections is one of several increasingly popular word games made by the New York Times. It challenges you to find groups of four items that share something in common, and each group has a different difficulty level: green is easy, yellow a little harder, blue often quite tough and purple usually very difficult.
On the plus side, you don’t technically need to solve the final one, as you’ll be able to answer that one by a process of elimination. What’s more, you can make up to four mistakes, which gives you a little bit of breathing room.
It’s a little more involved than something like Wordle, however, and there are plenty of opportunities for the game to trip you up with tricks. For instance, watch out for homophones and other word games that could disguise the answers.
It’s playable for free via the NYT Games site on desktop or mobile.
You might not want to keep your old tapes in the attic.
Sabphoto/Shutterstock
If you grew up in the 1980s, chances are you had a collection of cassette tapes. Remember those? The media format, about the size of a large stack of credit cards, was the primary way we listened to music in the ’80s before being overtaken by CDs in the ’90s and eventually streaming services like Spotify. If you’re like me, you may still have many of them stored in a shoebox. But how long are these tiny tapes expected to last?
The general belief is about 30 years, but this is based on ideal storage conditions. Cassette tapes will deteriorate over time even under the best conditions since the coating that binds the tapes will eventually lose lubrication and detach. But the primary deciding factor for longevity is storage. I personally have cassette tapes that are more than 30 years old and still play just fine (thanks mom and dad for having a player around to try them!).
It’s not a bad idea to digitize your cassettes using a digitization service or by connecting a player to your computer and recording to digital files using a service like Audacity. before they do deteriorate to preserve those custom playlists and memories. But for now, if you still have cassettes from the ’70s and ’80s, as long as they’re stored well, they could play for decades to come.
Advertisement
Proper storage and care is important
flashberg/Shutterstock
Before looking at how to store them, it’s important to understand how cassette tapes work. Inside are two reels, like mini movie reels, connected by a thin strip of magnetic tape and covered by a shell. When you press play, the tape slides on the magnetic head that reads magnetic patterns, which translates to audio. The electrical signals are sent through an amplifier to strengthen the sound, so you hear it more clearly through speaker or headphones.
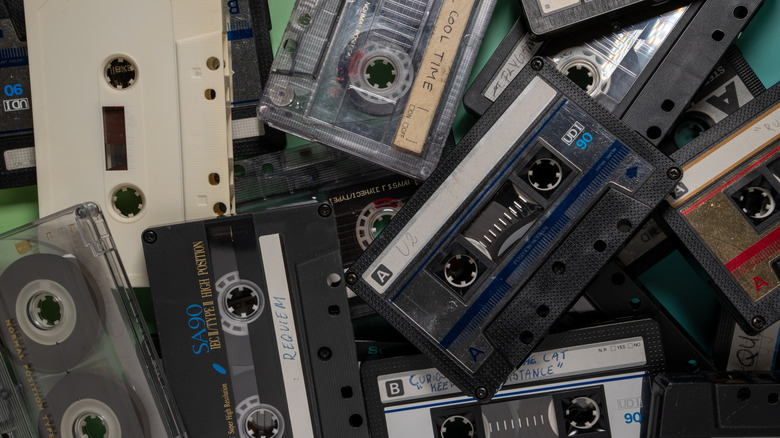
As long as the cassette tape remains in good order, it will play. But it requires proper storage. One big thing that can impact the life of a cassette tape is temperature, including storing them in an environment that is too hot or cold or where temperature fluctuates often. But it’s mainly about humidity too. You should also avoid exposure to sunlight, moisture, dust and dust mites, critters and magnetic fields.
Store them in a cool and dry place, with a temperature at 59 to 73°F and 25-55 percent humidity. Always keep them in their protective cases and wipe down the exterior from time to time to get rid of accumulated dust, even gently using a Q-tip. Don’t forget to clean the player’s tape heads as well. Play the tapes from time to time, too. Along with losing lubrication, the binder coating can get sticky without use.
Advertisement
Those who grew up in the Blockbuster era know, “be kind, rewind” is a VHS mantra that holds true for cassette tapes as well. When you’re done listening, rewind the cassette to the beginning (hopefully using the rewind button versus a pencil) to help minimize stress and uneven winding.
Tap into that nostalgia for decades to come
Savanevich Viktar/Shutterstock
Under improper conditions, the lifespan of a cassette tape can drop from 30 years down to as few as five. You might be tempted to pop them into a box in the attic, but consider temperature fluctuations, moisture and humidity levels, even beams of constant sunlight from a window. If you’re firm on storing them in the attic, use a plastic tub versus cardboard.
But with the right storage and care, cassettes could theoretically last up to 100 years, preserving fond memories to hand down for generations. From pre-recorded cassettes to ones with songs you recorded off the radio (with the DJ’s voice inevitably at the beginning and end of each track) to mixtapes created for everything from parties to road trips, break-ups and lovers, they hold a lot of nostalgia. With the vinyl resurgence and Gen Z already helping iPods make a comeback, it’s only a matter of time before cassette tapes and Walkmans are trending again, too.
Advertisement
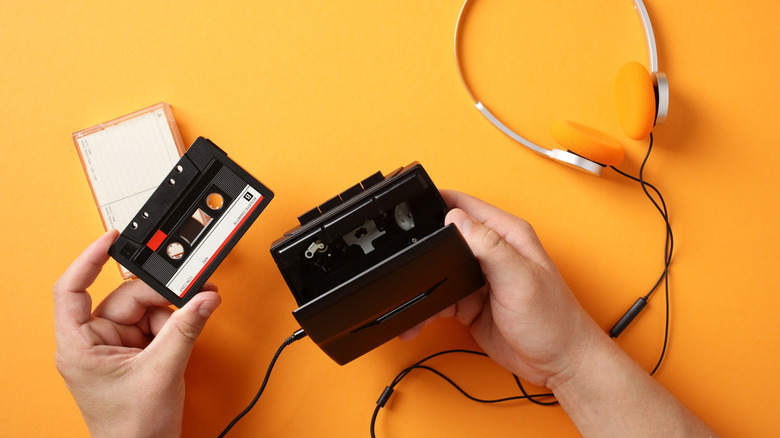
The biggest issue you may run into with playing cassettes is not necessarily worry about if the tapes still work but how to listen. You have probably already replaced your old boomboxes with the best portable Bluetooth speakers. But you can still find retro players that combine streaming with cassette decks, and affordable Walkman-style portable cassette players to keep the music going and relive the olden days.












































You must be logged in to post a comment Login