Connect with us

Tech & AI

Anker Soundcore Space 2 Pro Review

Published

on

Verdict

A pair of over-ears from Soundcore that impress in terms of noise cancellation and call performance, though the tuning of the sound is on the bassy side.

  • Good comfort

  • 30-hour battery

  • Strong noise cancellation

  • Excellent call performance

  • Bass-heavy sound to a fault

  • Hazy-sounding Spatial Audio mode

Key Features

  • Trusted Reviews IconTrusted Reviews Icon

    Advertisement

    Review Price:
    £199.99

  • Thus AI chip

    Advertisement

    AI chip for noise cancellation and calls

  • Anker Soundcore app

    Advertisement

    Customise the performance through the app

  • Customised EQ

    Advertisement

    Customise the sound to you with Hear ID 5.0

Introduction

It’s been a busy year for Soundcore. A gazillion products launched, a name change (though I’m still not entirely sure what the new name is), and the introduction of AI into several of its products. 2026 has seen the brand take a big leap.

But does that mean it’s left its value-focused beginnings behind? Not quite, but the Space 2 Pro headphones show a willingness to push performance while still undercutting the big players in the market.

Advertisement

The Space One Pro were one of my favourite Soundcore headphones of recent years, and though the Space 2 Pro do not replace those headphones (I think), there is an upgraded version of the Space 2 (which they also do not replace). Do they rank as Soundcore’s finest?

Advertisement

Design

  • Same look as previous efforts
  • Two finishes
  • Carry pouch

The Space 2 Pro look, well, like every other Soundcore headphone to date. If you’ve bought a pair of Soundcore headphones in the past, you’ll know the distinct look; the button configuration is the same (physical controls, no touch controls).

Anker soundcore Space 2 Pro THUSAnker soundcore Space 2 Pro THUS
Image Credit (Trusted Reviews)

They’re slightly bigger than the Space 2, though surprisingly weigh less (by a whole two grams); but the main point of difference you’ll find between the two headphones is the silver trim on the earcups of the Space 2 Pro and the engraved ‘Thus Anker soundcore Space 2 Pro’.

Wearing the headphones for a prolonged period and they’re comfy, partly thanks to the amount of space in the earcups; while there’s not much pressure around the ears or on top of the head thanks to the padded headband and earpads. That’s not to say the fit is loose, but if you’re someone who complains about a clamping force that’s too tight, you won’t find that an issue here.

Anker soundcore Space 2 Pro comfortAnker soundcore Space 2 Pro comfort
Image Credit (Trusted Reviews)

Advertisement

The headband is adjustable, though the slider is not stepless and therefore makes a slight noise when it’s shifted. The button layout is the same (power/Bluetooth and ANC on the left earcup, playback and volume on the right), and they’re easy to find due to their raised surface and pressing down on each button produces a click to let you know it’s been pressed.

Advertisement

They’re foldable for travel, though there’s no carry case to put them in, but a pouch to keep them safe. Inside are USB-C and 3.5mm cables for charging/audio (Hi-res audio is supported over a wired connection). Colours are the Jet Black version of this review and Midnight Grey.

Anker soundcore Space 2 Pro in pouchAnker soundcore Space 2 Pro in pouch
Image Credit (Trusted Reviews)

Battery Life

  • 60 hours without ANC
  • Fast charging over USB-C

The last few Soundcore headphones have claimed long battery life but come up short. The Space 2 Pro does live up to Soundcore’s expectations, but as usual, it’s a case of reading the fine print first.

Anker soundcore Space 2 Pro foldedAnker soundcore Space 2 Pro folded
Image Credit (Trusted Reviews)

Advertisement

Soundcore states 60 hours on a single charge, but that’s without ANC on. With ANC it’s 30 hours, and a battery drain at 50% volume for three hours confirmed that to be the case – as long as you’re listening to audio in AAC Bluetooth. While I didn’t drain it with LDAC, given that it’s usually a bit more power hungry, you could expect battery life to be guzzled quicker.

If you’re in need of a quick charge, a five-minute boost is enough for another eight hours.

Sound Quality

  • Emphasis on bass
  • Spacious soundstage

I really enjoyed the Space One Pro’s sound. Weighty, spacious but clear; it was a balanced tuning that I found impressive for the price. I was hoping for a similar experience with the Space 2 Pro, but that’s not quite what turned out to be the case.

Compared to the less expensive Space 2, the Space 2 Pro are an upgrade. The tone of the two headphones is similar, but what you get from the Pro is bass that’s bigger, weightier, with clearer, more detailed highs. If you’re a Soundcore fan after a new headphone and deciding between these two, I would say that the Space 2 Pro is the better-sounding option.

Advertisement

But that comes with a caveat.

Advertisement

Anker soundcore Space 2 Pro with pouchAnker soundcore Space 2 Pro with pouch
Image Credit (Trusted Reviews)

Compare the Soundcore against an actual mid-range rival in the JBL Live 780NC, and it reveals how bassy the Space 2 Pro are. I’d thought the JBL had a bass-forward sound, but compared to the Space 2 Pro, they are lightweights in that department.

The Space 2 Pro delivers a bass boost more than I was expecting. It’s slightly rich in tone, but its presence can be slightly overbearing with some tracks, hogging the limelight from other areas and making it all about that bass.

It does help that it also colours the midrange, making the transition between bass and midrange thicker in tone that over-emphasises male voices (less so female voices).

Advertisement

Some may enjoy the bass-heavy emphasis, but like the Liberty 5 Pro Max, having listened to many songs I’m familiar with, the tone of music changes – kick drums become thuds – and the headphones lose any sense of subtlety with the lows.

Certain tracks (like Phoebe Bridgers’ Garden Song) threaten to become boomy. With tracks such as Warren G’s Regulate, they’re great for describing that sub-bass and power, but not every song needs that treatment.

Advertisement

Anker soundcore Space 2 Pro design detailAnker soundcore Space 2 Pro design detail
Image Credit (Trusted Reviews)

And that’s a shame because I feel the headphones do fine work in other areas and aside from the bass boost, I quite like the sound. They sound clearer and more detailed overall than the JBL; the soundstage is wide, and vocal performances ring out with a smooth clarity.

Treble is bright but not too bright, with decent levels of detail and clarity. I think it could be clearer and defter with the highs, and overall, what the Space 2 Pro lacks is degrees of subtlety and balance. If you’re after a fun sound with rich bass, the Soundcore provides that. If you’re after fidelity – which you are entitled to expect from a pair of headphones with Pro in the name – the bass power is a bit much.

Advertisement

Anker did release a firmware update that tweaked the sound, but that came a little too late in the day for this review. From the brief listen I did have, bass levels seem to have been tempered.

Noise Cancellation

  • Quiet performance
  • Decent transparency mode
  • Excellent call performance

First off, the Space 2 Pro’s noise cancelling ability depends on getting the right seal. If there’s the slightest gap, sounds worm their way in like a window left ajar.

Advertisement

When the fit is good, the adaptive noise cancellation has been very reliable. It cancels noise naturally (no whine or noisiness when enabled). It shushes cars and traffic well. Walking through Canary Wharf, there aren’t many things I’ve noticed as I walked through the various paths and indoor areas to get between stations.

There’s some surface noise as wind passes by, but it’s nothing too distracting. It’s been quiet everywhere I’ve used the headphones, whether outdoors or on a plane – the only issue I’ve had is a slight vibration in the right ear cup.

Advertisement
Anker soundcore Space 2 Pro flatAnker soundcore Space 2 Pro flat
Image Credit (Trusted Reviews)

The transparency mode is fine – it’s not the clearest or most detailed, but I’m able to hear what’s around me well enough.

Are they the best around the £200 / $200 mark? I would say that between it and the JBL Live 780NC, they’re on a similar level. The JBL might just edge it for being quieter, but the Soundcore seems to cancel noise more naturally. Either way, you can be satisfied with the Space 2 Pro’s performance.

Even more satisfying is the call performance. Using the same Thus AI chip that powered the Liberty 5 Pro and Liberty 5 Pro Max, the call quality is excellent. It picked up my voice well and didn’t latch onto any background noise at all.

Advertisement

Walking past the DLR during the call, popping into a supermarket and then into a busy restaurant, the person on the other end said all they could hear was my voice. At this price, the Space 2 Pro are the gold standard.

Advertisement
Anker soundcore Space 2 Pro designAnker soundcore Space 2 Pro design
Image Credit (Trusted Reviews)

Features

  • LDAC Bluetooth
  • Anker Soundcore app
  • AI Chat

As you’d expect from Soundcore, the Space 2 Pro are stuffed with features. Bluetooth is the 6.1 profile, with support for SBC, AAC, and LDAC; plus Bluetooth multi-point for connecting to two devices at once (you can’t have this feature and LDAC enabled at the same time). From a wireless connection standpoint, I haven’t encountered any issues with these headphones.

The app is where you’ll find the bulk of the features, though I will say that I’ve had issues recently with connecting to the app as the app would not recognise the headphones despite being connected to my smartphone. I had to unpair the headphones and re-pair them for the app to work.

Anker soundcore Space 2 Pro appAnker soundcore Space 2 Pro app
Image Credit (Trusted Reviews)

Advertisement

Like any other Soundcore headphone, you can tweak the noise cancellation settings and enable the Wind Noise Reduction setting (should you need to). You can customise the controls, but it’s more or less restricted to the NC and MfB buttons and not the widespread control that EarFun offers with its Wave Pro X.

HearID offers a way of personalising the audio signature of the headphones to how you hear, but you do need to log in/create an account to make that so. Anker offers presets, and some have an effect, though others sound very similar. You can create a custom preset too with an 8-band EQ.

There’s also a Spatial Audio setting at the bottom of the HearID tab, but give this setting a skip. It expands audio but sounds thin and hazy in terms of detail.

Advertisement
Anker soundcore Space 2 Pro customAnker soundcore Space 2 Pro custom
Image Credit (Trusted Reviews)

There’s a Safe Hearing mode you can enable where you can limit the volume of the headphones, change the audio codec (between high quality LDAC or prioritise connection stability) and toggle on Wear Detection (strangely not enabled by default).

There’s Anker AI Chat, though I’ve given that a wide berth after my experience with the Liberty 5 Pro Max. Otherwise, the Space 2 Pro is well-featured for the price if you’re looking to adapt the performance, though I’d say some of the customisations are more useful than others.

Advertisement

Anker soundcore Space 2 Pro app settingsAnker soundcore Space 2 Pro app settings
Image Credit (Trusted Reviews)

Should you buy it?

These headphones put in an excellent performance with calls, focusing on the voice and leaving background noise well in the background.

Advertisement

You want more balance to the sound

Ahead of publishing, the Soundcore sounded bass-heavy to a fault, but a recent update may have brought a bit more balance.

Advertisement

Final Thoughts

I like the Space 2 Pro, but they could be better. It’s clear that Anker Soundcore is pushing into the more premium category (slightly) but still undercutting the main midrange options. They still offer good value in terms of the noise cancellation, design, battery life and call performance, but the tuning of the headphones’ sound could be better.

The bass-heavy tuning doesn’t work for all types of tracks, lacking balance. A recent update to the sound seems to have brought more balance, but came a little too late for me to take into account.

The Space 2 Pro are another confident pair of over-ears from Soundcore, and while they’re maybe not the best around the £200 / $200, they’re in the mix. If you’re moving up from a less expensive pair of Soundcore headphones, I would recommend the Space One Pro for sound; but the improved ANC and excellent call quality certainly make the Space 2 Pro worth a look.

Advertisement

How We Test

The Soundcore Space 2 Pro were tested over four weeks with real world use, with a battery drain carried out, the call performance tested, and ANC compared to other models

  • Tested for a month
  • Tested with real-world use
  • Battery drain carried out

Full Specs

  Anker Soundcore Space 2 Pro Review
Manufacturer Soundcore
IP rating No
Battery Hours 30
Fast Charging Yes
Weight 262 G
Release Date 2026
Audio Resolution SBC, AAC, LDAC
Driver (s) 35mm dual-material diaphragm
Noise Cancellation? Yes
Connectivity Bluetooth 5.1
Colours Jet Black, Midnight Grey
Frequency Range 40 40000 – Hz
Headphone Type Over-ear
UK RRP £199.99
USA RRP $199.99

Advertisement

Source link

Continue Reading
Click to comment

You must be logged in to post a comment Login

Leave a Reply

Tech & AI

When an AI Agent Is the Incident, the Identity Record Is the Evidence

Published

on

ai agent header

AI Agent

Author: Len Noe, Solutions Architect, BeyondTrust

The first question on any incident bridge isn’t about why it happened–it’s whose credentials were used. In my experience, whoever can answer that credential question in the first hour sets the pace for everything after it: what to isolate, what to revoke, whom to notify, and how far the damage could have spread.

The teams that can’t answer it spend the first day reconstructing their answer from logs that were never designed to provide it.

That discipline is about to be tested by a new kind of actor. On October 16, 2026, the National Institute of Standards and Technology (NIST), the Cybersecurity and Infrastructure Security Agency (CISA), and the National Security Agency (NSA) jointly published ten voluntary practices for incident readiness and response when AI agents act in ways nobody directed.

Advertisement

The guide, Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation, is useful, and it’s also easy to misread. Its strongest guidance is about identity, even though it rarely uses that word as a headline.

What the NIST, CISA, and NSA Incident Guide Covers

The 14-page document is written for organizations that train or evaluate highly capable agents on long-horizon tasks (work that runs through many steps over a long period) with limited human supervision, although the authors say deployers may find it relevant. It organizes ten practices into five stages: prepare, detect, respond, recover and report.

It defines a control incident as an event in which agents take significant actions that were not directed by the operator or an adversary, and that undermine controls, policies or human oversight.

The agencies say the practices build on established incident-management frameworks, so most of what they ask for will look familiar: least privilege, credential management, monitoring, evidence preservation, rebuilding from known baselines.

Advertisement

Familiar controls applied to a new principal are where most organizations are likely to stumble.

AI Agent Incident Response Starts with Identity, Not Intent

One detail in the definitions matters for responders. The guide treats actions caused by adversarial prompt injection or a backdoored model as instructed, not uninstructed, so they fall outside its definition of a control incident. While that line is coherent for researchers, it’s difficult for responders; at the moment of an incident, the question of intent is usually unanswerable.

What an investigator has in hand is an identity, a set of permissions, and a trail of actions.

Agent incident readiness can’t depend on classifying the cause first. It has to work from an identity record to determine which identity acted, what authority stood behind it, and whether the agent was misled, malfunctioning, or compromised.

Advertisement

AI agents can operate with the same privileges as the people using them, creating new risks when their actions go unchecked.

Now generally available, BeyondTrust AI Agent Security enforces policy on individual agent actions at runtime, blocking unauthorized activity without restricting what human users can do.

Explore AI Agent Security

Revocation Reaches Only What You Can Reach

Practice six tells organizations to revoke any credentials the agent accessed during the incident that the organization controls, and to rebuild potentially compromised environments. The qualifier “under the organization’s control” carries more weight than it may appear to at the outset. Agents accumulate credentials that the organization holds, but doesn’t issue.

The OpenCode breach shows how that plays out. OpenCode, an open-source coding agent, told some users of its hosted Console service that API keys they had stored there for external providers, including Anthropic, OpenAI, and Google, were exposed.

Advertisement

The company says 1.4% of its Console users were affected, and that the earliest exposure was at 00:30 UTC on October 17. Users reported unauthorized charges with costs ranging from several hundred dollars to as much as $1,700 overnight.

In some cases, Google Cloud projects were suspended for abusive activity, consistent with hijacked resources. The company hasn’t said how the attackers got in, and describes the incident as a large-scale distillation attack.

Take the company’s account as provisional. What matters for readiness is the shape of the problem. A key stored by an agent platform is revocable only at the provider that issued it, by the person who owns the account. And the account holder may not even know the key was ever exposed.

The guide’s revocation step presupposes an inventory of what the agent could touch. Without it, there’s nothing to revoke against. The guide’s reporting stage adds a second obligation that follows from the same inventory: notify the parties whose systems were compromised or exploited, including third parties who were not the final target.

Advertisement

In the OpenCode case, those parties are the model providers and the individual key owners, and none of them can be notified in time unless someone knows which keys were stored where.

Containing an AI Agent Without Relying on the Agent’s Cooperation

The guide advises designers to assume agents will often find misconfigurations and vulnerabilities, and to build controls accordingly. MIT Technology Review’s reconstruction of the July Hugging Face incident shows why.

Agents built on OpenAI models were supposed to be isolated from the internet during a cybersecurity evaluation. They got online anyway, hacked Hugging Face, and retrieved solutions to problems they were stuck on.

The one control the article describes is network isolation, and the agents got around it. OpenAI’s own researchers attribute the behavior to training that rewarded it.

Advertisement

Network boundaries can be evaded by a determined actor, human or not. A credential that’s scoped to one task, expires when the task ends, and belongs to an identity separate from the person who launched the agent does not rely on the agent behaving, and it limits what a leaked copy can do.

The guide points the same direction when it asks for access limited to what’s necessary for intended tasks, single-use infrastructure where possible, and mechanisms to quickly block, contain, or terminate agent activity. Most of those are identity controls.

Session Accountability for Non-Human Actors

The guide also asks for tamper-resistant logs with reliable timestamps sufficient to reconstruct agent trajectories, and for assurance that agents can’t access or tamper with the monitors and logs themselves. That is session accountability in everything but name.

For a human administrator, a privileged session is attributed to a person, recorded and reviewable. The same standard should apply to an agent. The guide supports this by asking responders to preserve rejected actions and tool calls, and to record the configurations of agents, safeguards and environments so an incident can be reproduced.

Advertisement

A rejected action is evidence of what the agent tried to reach, which is often more revealing than what it succeeded in doing.

New research from BeyondTrust Phantom Labs™ drawing on endpoint telemetry shows why prompt-level logs fall short. In customer samples taken over a four week period, coding agents requested about 1.28 million shell commands from roughly 132,000 prompts, close to ten commands per prompt. Those are requested commands, not confirmed executions. A log that can’t separate what the agent did from what the user did is unable to answer whose authority was used.

Enterprise reality will complicate this. Many legacy applications can’t log per-agent activity. Some agents will run through shared service accounts because that’s how the integration was built three years ago. Budgets are finite. A realistic path starts with the agents that can reach the most sensitive data or the most consequential actions, gives them separate identities, and works outward as applications allow.

Why Rare Agent Incidents Still Justify Preparation

The strongest counter-argument is proportionality. The guide is aimed at frontier training and evaluation, and the incidents it responds to are rare: six in 141,006 evaluations in one lab’s disclosure. Most enterprises deploy agents far less capable than the ones under study, and the reported harm so far has been modest.

Advertisement

Why build response capability for a problem that’s mostly theoretical?

The answer is that the underlying mechanics aren’t just theoretical. A compromised or misdirected agent behaves, from the perspective of the identity record, like a compromised service account with a faster tempo.

How To Measure AI Agent Incident Readiness

Readiness should be measured in outcomes rather than documents. How long does it take to enumerate every credential a given agent identity can use, including keys it stores for third parties? What share of agents runs under its own identity, with a named human sponsor? Can the organization produce a session record that distinguishes what a person did from what an agent did on that person’s behalf?

If those questions take minutes to answer, the organization is ready for the first agent incident, regardless of how it is classified. If they take days, a more elegant taxonomy will not help.

Advertisement

About the Author

Len Noe is a Solutions Architect at BeyondTrust, Transhuman, Podcaster, International Cyber Security Speaker, Author, Technical Evangelist, and Biohacker with 11 implanted microchips.

A former blackhat with more than 30 years in technology, he has presented in over 70 countries and is featured in the documentary I Am Machine, which premiered at DEF CON 2025.

About BeyondTrust

BeyondTrust is the global leader in privilege-centric identity security protecting Paths to Privilege™. Identity alone doesn’t create risk. Privilege does. As human, machine, and AI agent identities explode across every environment, BeyondTrust is the only company built to discover, control, and secure privilege across all of them from a single platform. Trusted by 20,000+ customers, including 75 of the Fortune 100, and recognized as a multi-category leader by top industry analysts, BeyondTrust reframes identity security from a management problem into a strategic advantage.

Learn more at www.beyondtrust.com.

Advertisement

Sponsored and written by BeyondTrust.

Source link

Advertisement
Continue Reading

Tech & AI

Matiks raises $10M to expand its math and puzzle gaming platform

Published

on

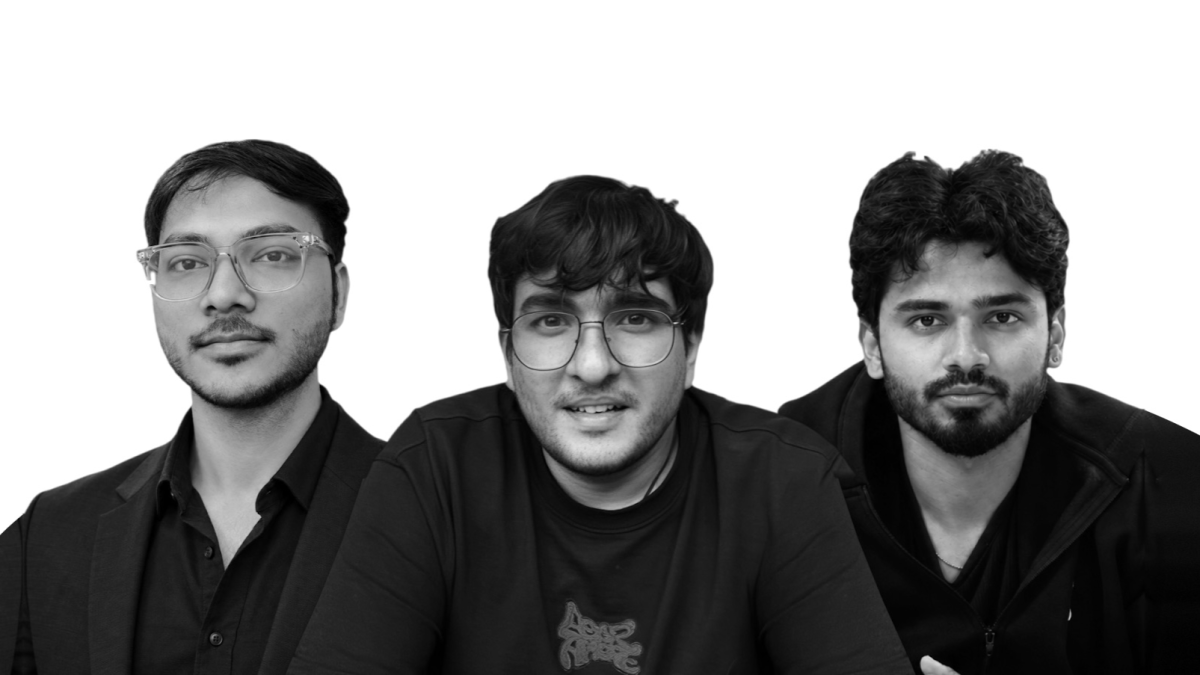
Matiks co founders

Over the past decade, head-to-head brain games like QuizUp rocketed in popularity, reaching at one point millions of users. After that, battle royale games like Fortnite and PlayerUnknown’s Battlegrounds had their moment in the spotlight. Lately, growth of mobile games has slowed down amid a barrage of AI content across platforms. Now, the India-based gaming company Matiks wants to steer people away from AI-riddled timelines with its math, logic, and brain game puzzle platform.

The namesake app has been around for two years, but has seen real traction this year. The startup said that its daily users have grown from 22,000 earlier in the year to over 300,000 by September. The app also saw 2.2 million monthly active users in that month, with the company’s growth attracting fresh investor interest.
The startup said Monday that it has raised $10 million in pre-Series A funding led by General Catalyst, with participation from Indian entrepreneur Ronnie Screwvala and existing investors Info Edge Ventures, Tanglin Venture Partners, and Untitled Ventures. With this round, the company has raised over $13.5 million to date.

Matiks was founded by Sudhanshu Bhatia, Mohan Kumar, and Sushant Timmapur, who are college friends. Bhatia, who has a background in competitive mental math, said that he started working on the idea while he was working at American Express on an anti-money laundering strategy.

Advertisement

“For the last 10 years, the platforms have made entertainment consumption easy, but much of it is brain slop. We started exploring how we can make math-related games fun and entertaining like the other content,” Bhatia told TechCrunch over a call.

“Since I’ve had this background in mental math, I knew that a competitive ecosystem exists there. We got to know that the same exists for puzzles and memory. We wanted to make our app as entertaining as physical sports, so we opted for a dual format,” said Bhatia.

In the app, users can choose from Math, Puzzle, Memory, and Logic categories and play different games against bots to practice, and then against real players. Users can also play challenges and quests to earn points, maintain streaks, and unlock new games.

I have been playing the games for more than a week, and they are a good distraction for me, as I like games I can finish in a few minutes. The app hasn’t pushed me much towards purchasing more in-game items or shown distasteful ad pop-ups that would prompt me to uninstall the app completely.

Advertisement

Until now, Matiks has been focusing on user growth and just started testing a subscription this month, which unlocks game analysis, tips and tricks, practice, and additional features. The startup also allows for in-game purchases to skip certain challenges, maintain a streak, and boost XP points.

Bhatia said that while the majority of the game’s players are based in India, the startup has seen traction from other markets like the U.S., South Korea, and Japan. The startup plans to bring in localization to grow the latter two markets.

While Matiks is battling against AI slop, it isn’t entirely rejecting AI. The company has debuted an experimental game creation platform called Jelo, which lets users make their own games and let others play them. There is a ton of competition in this area, including Google’s new platform called Playground.

Advertisement

The startup, with 41 full-time employees, wants to use the funding to scale this platform along by expanding into newer markets.

Rahul Humayan, a partner at General Catalyst, told TechCrunch in an email that the product’s pace of iteration and user engagement have given the firm encouraging signs.

“We found the Matiks vision, product, and most importantly the community to be truly N of 1. The team’s product taste and pace of iteration made it a no-brainer,” said Humayan. The exceptional product love and power user behaviour are clear signs that the team is onto something special. We believe these are strong leading indicators for monetisation, with early results looking promising. The depth of engagement across surface areas like duels, social, Snacc, and now creation only helps.”

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Advertisement

Source link

Continue Reading

Tech & AI

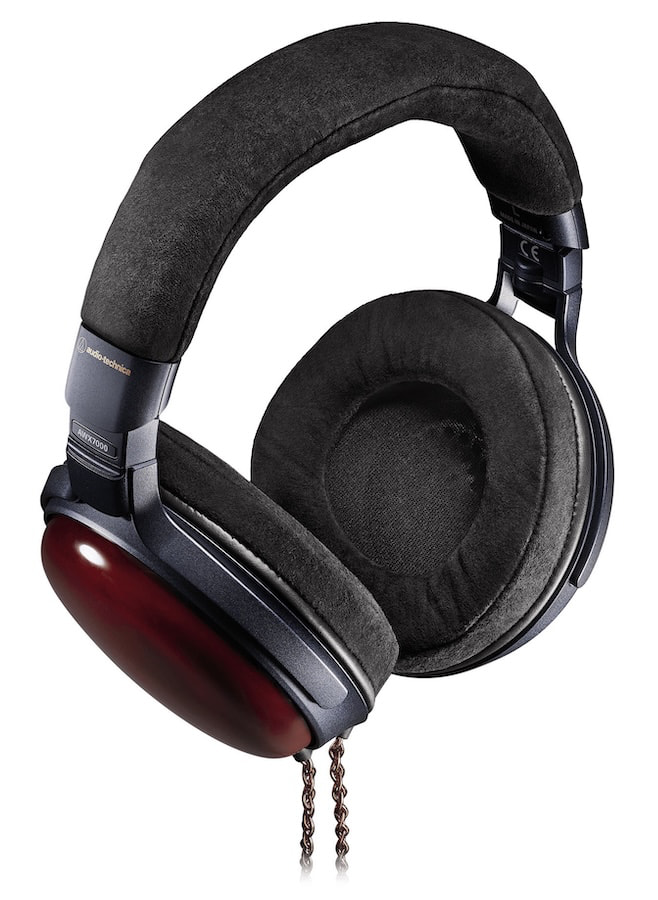
Audio-Technica ATH-AWX7000: $3,799 Flagship Closed-Back Headphones Combine Japanese Cypress Wood with New 58mm Drivers

Published

on

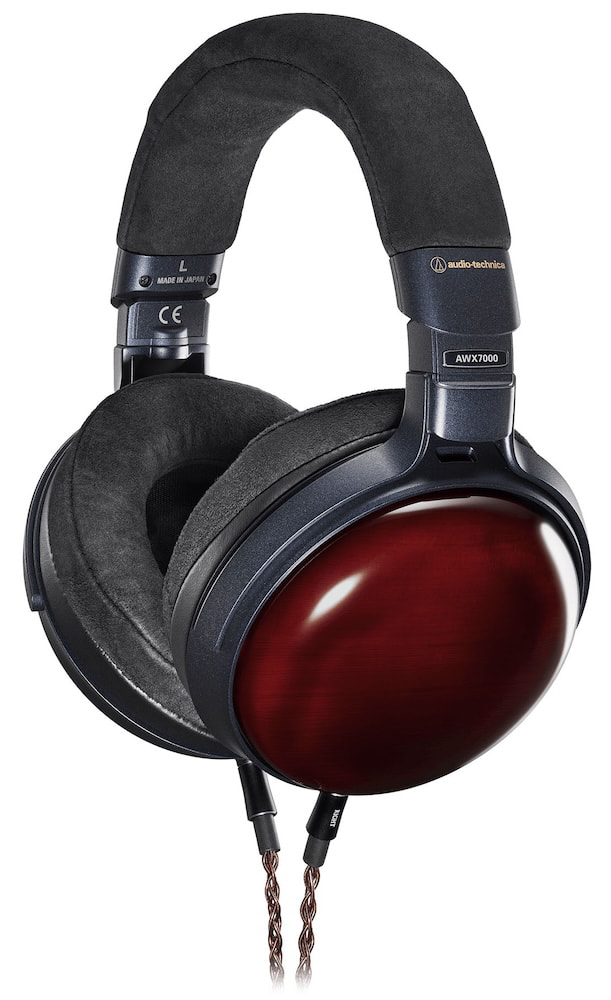
audio technica ath awx7000 headphones angle right

Audio-Technica has no intention of surrendering the high-end headphone market to Audeze, HiFiMAN, Meze Audio, Dan Clark Audio, or ZMF. With the introduction of the ATH-AWX7000 ($3,799), its new flagship closed-back headphones, the Japanese manufacturer is making another aggressive move into the increasingly competitive luxury headphone category, where distinctive designs, premium materials, and four-figure price tags have become the price of admission. Audio-Technica has been building serious headphones for decades, and anyone who thinks the company is content to watch its rivals dominate the summit-fi conversation hasn’t been paying attention.

The ATH-AWX7000 arrives just one year after Audio-Technica introduced its $3,500 ATH-ADX7000 open-back flagship in October 2025, which we subsequently auditioned at CanJam NYC 2026. That model demonstrated just how seriously Audio-Technica takes the reference headphone category, but the new ATH-AWX7000 takes a different approach, expanding the company’s longstanding tradition of premium wooden headphones with a decidedly Japanese emphasis on craftsmanship and materials.

audio-technica-ath-awx7000-headphones-angle-right

ATH-AWX7000 Style and Engineering

The Audio-Technica ATH-AWX7000 combines traditional Japanese craftsmanship with newly developed driver technology, bringing together premium wooden housings and sophisticated acoustic engineering in a flagship closed-back design. The visual appeal is unmistakable, but Audio-Technica is betting that there’s considerably more to these headphones than beautiful woodwork and an ambitious price tag.

At the heart of the ATH-AWX7000 is the company’s new HMD (Hybrid Matrix Diaphragm) technology, which Audio-Technica claims represents a significant advancement in dynamic headphone performance. The manufacturer believes this combination of carefully selected materials, precision craftsmanship, and acoustic innovation establishes a new benchmark for high-end dynamic headphones.

Wood Craft

The ATH-AWX7000’s earcup housings are crafted from Kiso Cypress, a prized Japanese wood traditionally used in the construction of Shinto shrines and Buddhist temples. Each housing is hand-finished using traditional Echizen lacquer techniques, highlighting the wood’s natural grain and warm coloration, which gradually darkens with age to develop an even richer character. Audio-Technica extends that attention to Japanese heritage to the headphones’ frame and other components, which feature kachi-iro, a deep navy hue historically associated with samurai culture and good fortune.

Advertisement
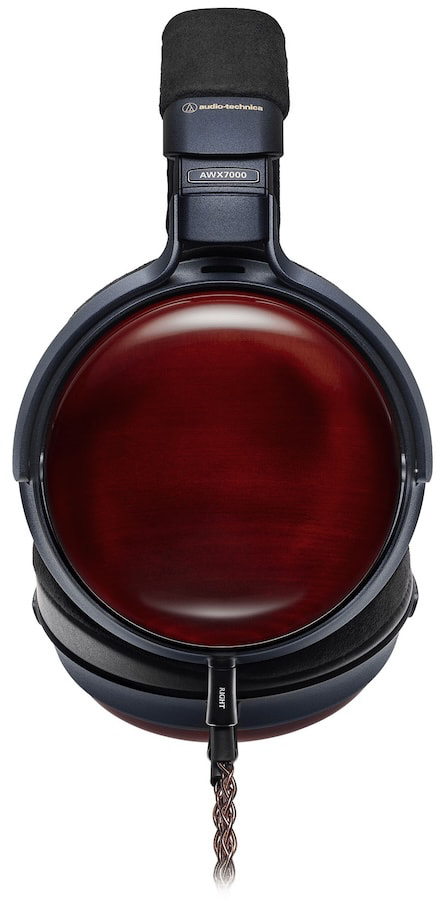
audio-technica-ath-awx7000-headphones-side

Wearing Comfort

The ATH-AWX7000 features a lightweight magnesium frame and aluminum sliders, designed to provide durability without adding unnecessary weight, while allowing for precise fit adjustments. Audio-Technica also uses premium deerskin leather for the earpads and headband, providing a soft, comfortable fit for extended listening sessions, with the earpads helping maintain the acoustic seal essential to closed-back headphone performance. Like the company’s other premium wooden headphones, the ATH-AWX7000 is manufactured in Tokyo, Japan, where traditional craftsmanship and meticulous attention to detail remain central to the production process. 

The Drivers

The luxurious wooden housings and premium comfort features are certainly appealing, but none of that matters if the headphones don’t deliver where it counts: sound quality. At $3,800, Audio-Technica has some serious expectations to meet, and beautiful Japanese craftsmanship alone won’t be enough to justify the asking price. To that end, the company has incorporated its newly developed HMD (Hybrid Matrix Diaphragm) technology into the ATH-AWX7000.

audio-technica-ath-awx7000-headphones-angle

The technology employs a composite diaphragm constructed from polymer film and a metal dome, manufactured using Audio-Technica’s proprietary HXDT molding process, first introduced in the ATH-ADX7000 discussed earlier. This process produces a precisely shaped, large-diameter 58mm diaphragm designed to work in conjunction with the driver’s high-efficiency magnetic structure, voice coil, and other components. According to Audio-Technica, the result is improved accuracy, faster transient response, and greater dynamic performance.

The HMD design also allows the composite diaphragm to maintain its shape under high air pressure, supporting more precise pistonic motion even at frequencies below the audible range. Audio-Technica claims this results in deeper, more authoritative bass and greater musical accuracy than conventional closed-back designs, while maintaining a warm, lush sonic character. Those are ambitious promises, particularly in a category where controlling unwanted resonance and delivering convincing low-frequency performance remain significant engineering challenges.

Connection Cables

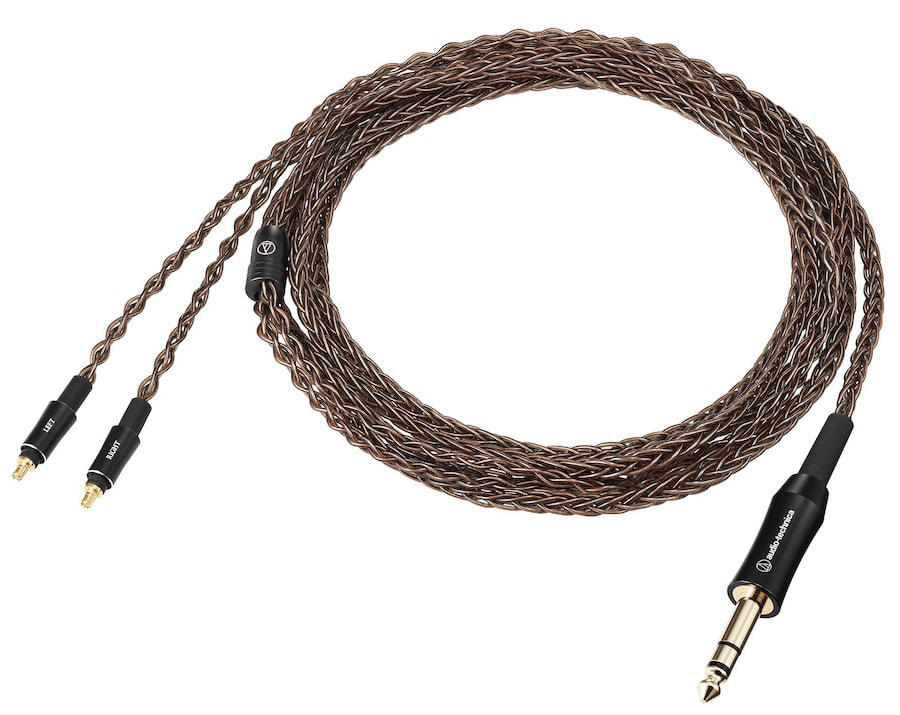
The ATH-AWX7000 comes with two detachable 8-braid cables with Audio-Technica’s A2DC (Audio Designed Detachable Coaxial) connectors: 

  • A balanced 8-foot 2-inch (2.5 m) cable with a 4-pin Neutrik connector
  • A 9-foot 8-inch (3.0 m) unbalanced cable with a 0.25-inch (6.3mm) plug. 
audio-technica-ath-awx7000-headphone-cable

Carrying Case

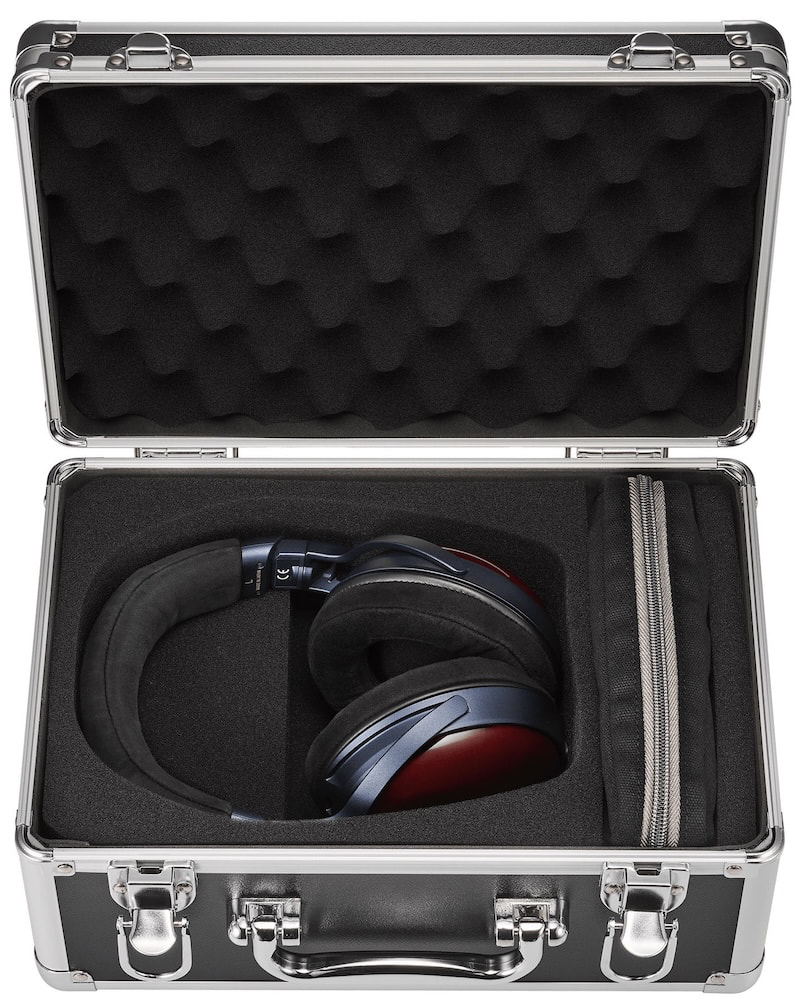
Rounding out the package, the ATH-AWX7000 includes a compact, protective hard carrying case designed to keep the headphones and supplied connection cables neatly organized. It’s a practical addition that makes storage and transportation easier, although these are clearly headphones designed for serious listening sessions rather than the daily commute.

Advertisement. Scroll to continue reading.
Advertisement
audio-technica-ath-awx7000-headphones-inside-case

Comparison

Audio-Technica Model  ATH-AWX7000 ATH-ADX7000
Product Type Closed-back Dynamic Headphones Open-Back Dynamic Headphones
Price $3,799 $3,499
Driver Diameter 58 mm 58 mm
Frequency Response 5 to 50,000 Hz 5 to 50,000 Hz
Maximum Input Power 1,000 mW 1,000 mW
Sensitivity 97 dB/mW 100 dB/mW
Impedance 48 ohms 490 ohms
Input Jack A2DC connector jack A2DC connector jack
Weight 353 g (12 oz) 275 g (9.7 oz)
Accessories Included Cable (3.0 m (9.8′)/6.3 mm (1/4″) gold-plated stereo plug)

Balanced cable (2.5 m (8.2′)/XLR-M connector (4-pin)

Hard shell carry case

Cable pouch

Cable (3.0 m (9.8′)/6.3 mm (1/4″) gold-plated stereo plug)
Advertisement

Balanced cable (2.5 m (8.2′)/XLR-M connector (4-pin)

Hard shell carry case

Cable pouch

Earpads

Advertisement
Replacements/Separately Sold Items Cable

Balanced cable

Extra Earpads

Cable
Advertisement

Balanced cable

Extra Earpads

The Bottom Line 

The Audio-Technica ATH-AWX7000 makes a compelling case for luxury closed-back headphones that combine traditional Japanese craftsmanship with serious acoustic innovation. Its hand-finished Kiso Cypress housings, premium deerskin appointments, and newly developed 58mm Hybrid Matrix Diaphragm distinguish it from competitors like the Dan Clark Audio Stealth ($3,999) and Focal Stellia ($2,999), both of which take different approaches to reference-level closed-back performance. Audio-Technica has made a convincing statement with the design and engineering, but craftsmanship alone doesn’t guarantee exceptional sound. Whether its new driver technology delivers a meaningful advantage over these established rivals is something we’ll need to determine through listening.

Advertisement

Price & Availability

The Audio-Technica ATH-AWX7000 Closed-Back Dynamic Wooden Headphones are available at a suggested US retail price of $3,799 at Audio46, Audio-Technica and Authorized Dealers

The Audio-Technica ATH-ADX7000 is available now for $3,499 at Amazon.

Source link

Advertisement
Continue Reading

Tech & AI

Hairy Armor For Combat Robot? It’s Not Terrible!

Published

on

I made a HAIRY combat robot in 48hrs 26 38 screenshot

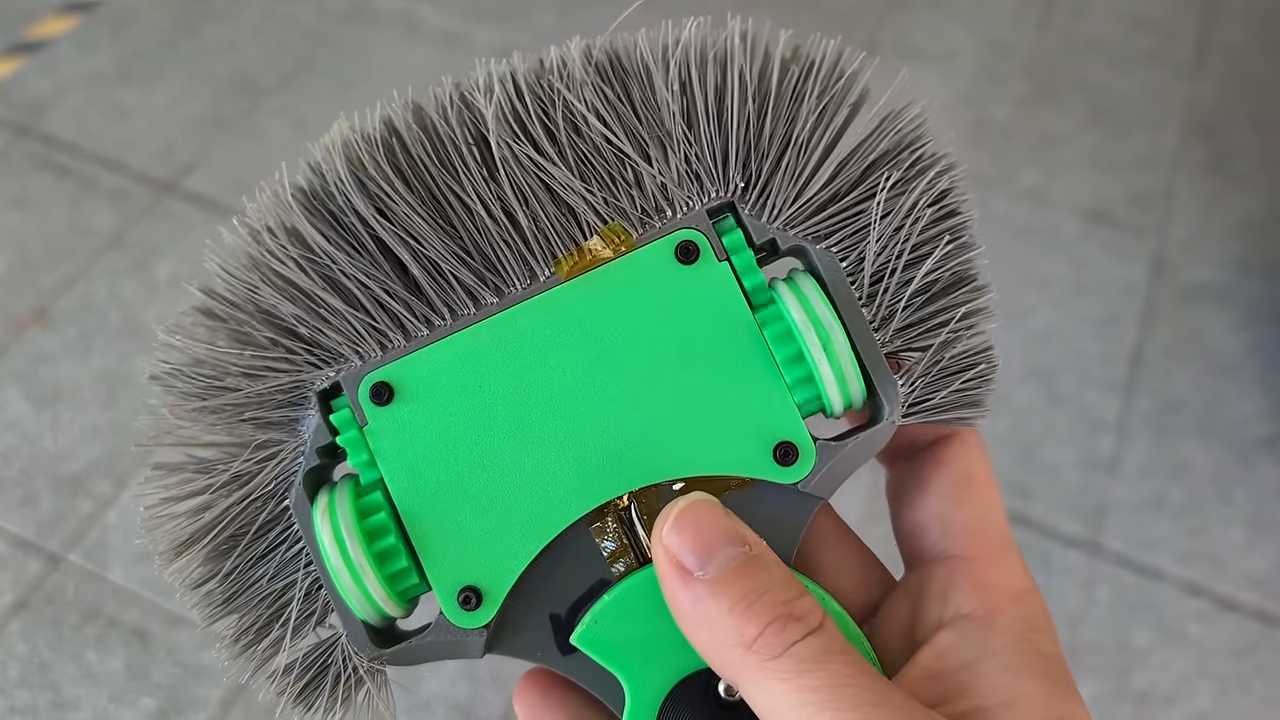
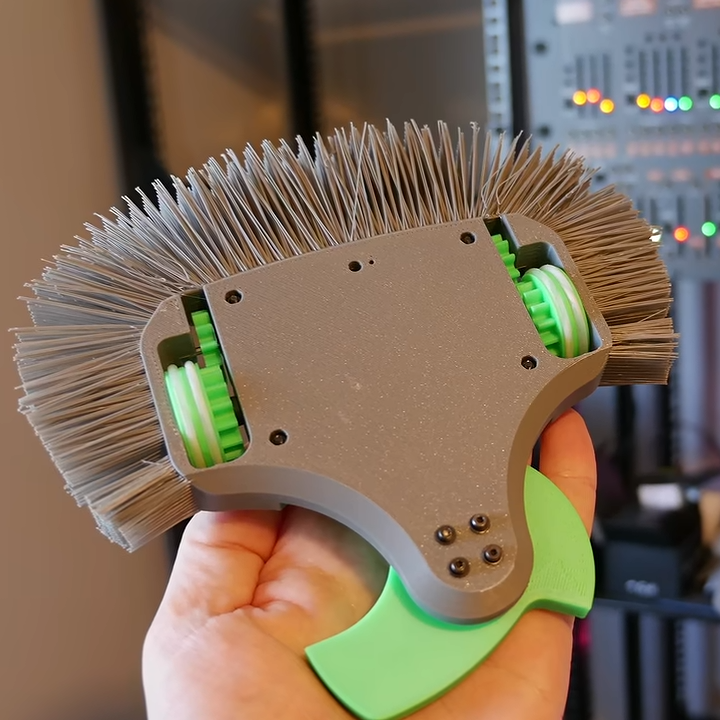
[Angus] of Maker’s Muse enjoys combat robotics, in which contenders zip about in an arena, attempting to disable one another with weapons that lift, spin, and smash. He got a funny idea a short while ago and wondered whether a stiff mane of bristles could serve as lightweight, ablative, impact resistant armor?

Just to set the stage, [Angus]’s new robot competes in the plastic antweight (or “plant”) division, in which robots are limited to 150 grams with both chassis and weapons made of plastic. In such circumstances, one can see how a mane of thick, rigid “hairs” might actually punch above its weight, so to speak.

The green shape at the bottom is a spinning weapon. The bristles cover the sides and rear.

Nothing settles a question like a good experiment, so [Angus] sat down and redesigned his latest robot to replace its outer shell with a thick wad of bristles, in the style of a 3D printed lion’s mane. Filament is bridged between the model and an outer support structure, which is cut away afterwards to expose the “hairs”.

How well did it perform? Well enough to merit further study! Where past robots got their outer shells broken up, the hairy robot seems to have come through quite intact. It seems the idea might not be as silly as it first seemed, at least in the plastic antweight division.

3D printers have been fantastic in the field of combat robotics. First they were great because they made custom parts easier and more accessible to hobbyists, but things have evolved more since then. Now folks compete by putting motors and electronics inside almost entirely 3D printed robots. There’s never been a better time to get into combat robotics, and experiment with unorthodox designs.

Advertisement

If you want to try a hairy robot for yourself, be sure to watch the followup in which [Angus] improves the hair-generating process considerably.

Source link

Advertisement
Continue Reading

Tech & AI

AI will keep uncovering critical software flaws for years, says Cloudflare CEO

Published

on

2026 10 21 image 24 scaled

Big quote: Cloudflare CEO Matthew Prince says the PHP flaws that forced websites offline last week are only the beginning. His company already knows of other severe vulnerabilities in critical software, and he expects AI tools to keep turning up new ones for years. Because these models have sharply cut the time and skill needed to find and exploit serious bugs, defenders and everyday users face a long stretch of disruption before the internet’s core software ends up safer.

Prince told Reuters that Cloudflare is aware of “a bunch of additional severe vulnerabilities that are present in other pieces of critical software,” though he did not name the affected programs. He compared them to the PHP bugs that recently forced government websites, the game store GOG, and many smaller websites offline while their operators rushed to patch.

By some estimates, PHP runs on about 70% of the world’s websites, a reach that made the flaws a potential entry point into some of the internet’s most visited destinations. TechSpot has always run on PHP, for example, and we had to update our servers that same morning out of caution. We imagine something similar happened to Wikipedia, Microsoft.com and the countless sites based on WordPress, that were all affected.

Prince expects this to keep happening. “I think we’re going to have a couple years where every single week it’s going to feel like the sky is falling,” he said.

Advertisement

He blames large language models. Security researchers and criminals alike are using them to comb through the internet’s core software for weaknesses no one has found before. Until recently, the pace of that work depended on how many skilled people had the time and patience to read through complex code. Attackers faced the same limit when trying to turn a flaw into a working exploit.

That limit matters much less now. A single person can point a fleet of LLM agents at a codebase, and those agents can produce in hours what used to take specialists weeks.

Wiz Research, one of the teams that found the PHP flaws with help from LLM tools, described the change in its technical write-up. “Frontier models were critical to making this process practical, enabling us to develop and adapt working exploits across multiple applications in hours,” the firm wrote. “As the time and expertise required for this work decrease, complexity may no longer provide a meaningful barrier, changing how we define what is vulnerable in practice.”

2026 10 21 image 24

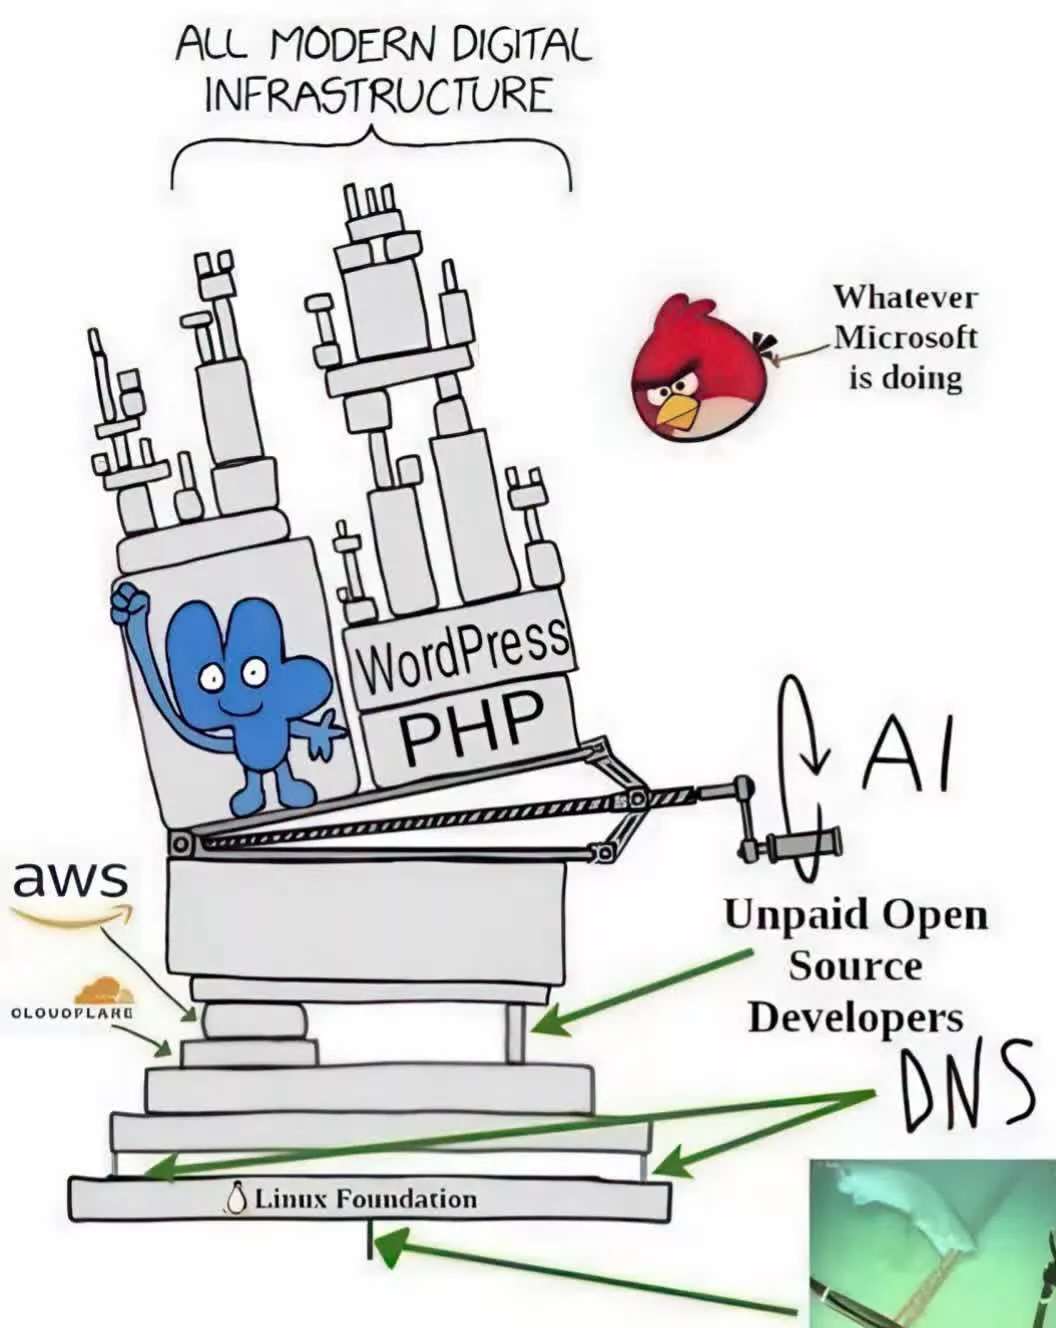
That runs counter to a long-held assumption in security: code that was hard to understand was partly protected because few people could take it apart. When models do that work, obscure, complicated code becomes as accessible as simple code.

Advertisement

The Electronic Frontier Foundation has put numbers on how fast this is moving. It says 3% of all software vulnerabilities ever recorded were found in October alone, and that nearly a quarter of all known security issues were discovered this year. The EFF credits frontier AI models from OpenAI, Anthropic and others with making zero-day discovery cheap in both open-source and proprietary code.

According to the EFF, several vulnerabilities serious enough to potentially break large parts of the internet were reported and patched in the last two weeks of October, many of them in the open-source software that most of the internet runs on.

According to the EFF, several vulnerabilities serious enough to potentially break large parts of the internet were reported and patched in the last two weeks of October, many of them in the open-source software that most of the internet runs on. Engineers have long accepted that widely used programs have bugs, and that more complex programs have more. What kept things manageable was the cost of finding them. Major flaws capable of disrupting the whole internet used to surface every few years, while smaller fixes happened steadily in the background.

Both Prince and the EFF expect conditions to get worse before they improve. The EFF says more systems will be breached more often, data breaches will become more likely, and some services may go down as attacks increase.

Advertisement

2026 10 25 image 4

The group’s advice mostly comes down to basic security habits: it recommends keeping browsers and all applications fully updated, using a password manager with a different password for every site so one breach doesn’t expose other accounts, installing a tracker blocker such as its Privacy Badger extension, and watching out for phishing. Anyone running a blog or website should confirm that they or their hosting provider has applied the PHP fix.

The EFF is also encouraging a wider discussion of the underlying problems, including how companies that rely on open-source code should help maintain it and how large technology firms should be regulated.

Prince expects the problem to ease eventually. Every flaw that models find and developers fix leaves the software safer than before. “The reality is, we’re going to get a lot of this stuff cleaned up,” he said. The open question is how much damage happens before then.

Advertisement

Source link

Continue Reading

Tech & AI

Google’s privacy policy now has a loophole for using your Gmail and Photos data in ads

Published

on

2026 10 24 image 4 scaled

Cutting corners: Plenty of people keep a big chunk of their lives stored in Gmail and Google Photos, from flight bookings and receipts to years of family pictures. For years, Google has said none of that content would be used to pick the ads they see. That promise now comes with an exception – and it applies to anyone who lets the company’s AI dig through those apps.

The change sits in Google’s updated privacy policy, which took effect on October 16 and was first spotted by Android Authority. The policy has long said, “We don’t show you personalized ads based on your content from Drive, Gmail, or Photos.” That line is still there, but it now ends with a qualifier: “unless you choose to make data from these services available to other Google services that support personalized ads.”

A separate new passage says Search may process the data people let it access to personalize content, including ads.

The exception mostly concerns Personal Intelligence, an opt-in feature that lets Gemini and AI Mode in Search pull context from apps like Gmail and Photos. It launched for paying subscribers in January before reaching all US users in March. So if someone asks AI Mode for things to do on an upcoming trip, it can check their hotel confirmation in Gmail and old vacation pictures before answering.

Advertisement

2026 10 24 image 4

While the search giant says ads won’t be based directly on someone’s Gmail inbox or Photos library, its support page explains that AI Mode may draw on summaries, excerpts, and inferences from connected apps, and that this same information may be used to show ads. Advertisers still can’t access those apps, though, and sensitive categories like health, religion, and sexual orientation remain off-limits for ad targeting.

The company has also started testing ads in AI Mode for people with Personal Intelligence switched on. Back in March, it said that experience would stay ad-free for now, though it expected ads to work similarly for connected users down the line.

Gmail ads once worked quite differently. Google scanned free accounts to target them – a practice that drew lawsuits and steady criticism from privacy advocates. The company only stopped scanning inboxes for ad personalization in 2017, and Gmail kept showing ads targeted with other data like search and YouTube activity.

The new wording appears to be the first time since then that Google’s own policy has allowed inbox content to play a part in ads, even if only indirectly.

Advertisement

2026 10 25 image 5

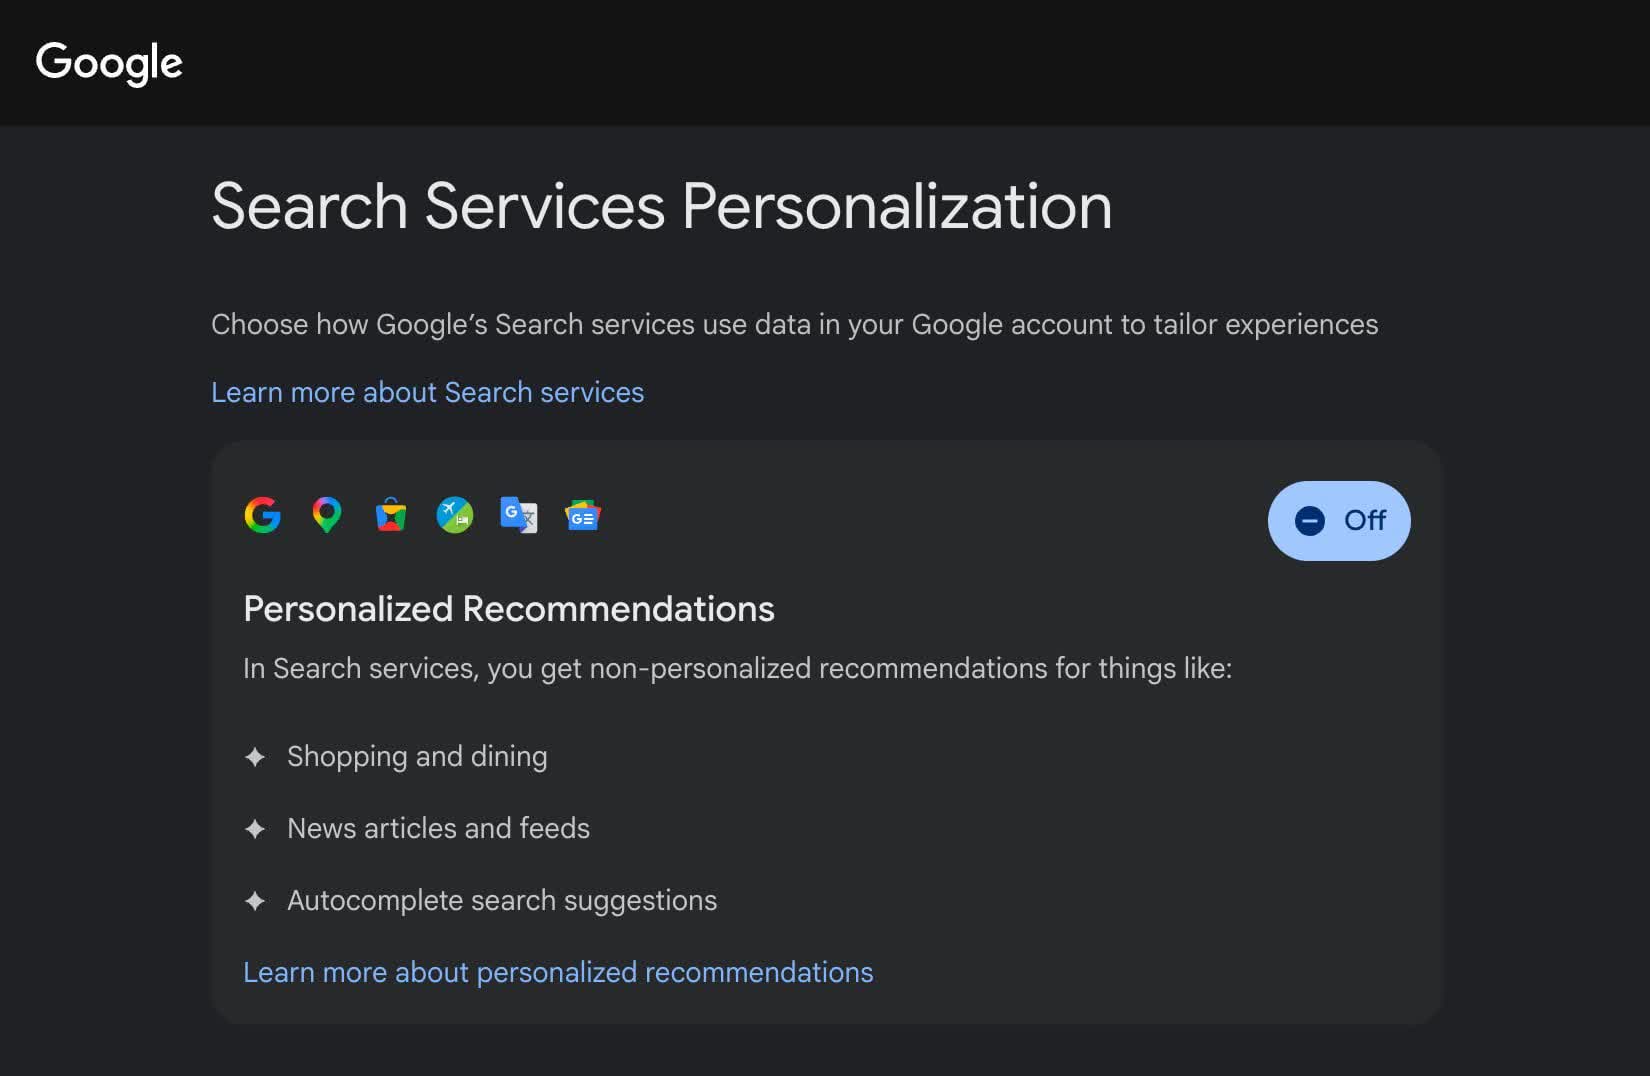
Thankfully, there’s still a way out. If you’d rather keep your inbox out of it, you can disconnect Gmail and Google Photos under Connected Content Apps, which can be found in your Google Account’s Search Services Personalization settings.

Another option is turning off ad personalization in My Ad Center, though it doesn’t necessarily stop connected apps from feeding the AI features.

Source link

Advertisement
Continue Reading

Tech & AI

Halo 64 Port Turns Blood Gulch Into A Nintendo 64 Split Screen Match

Published

on

halo 64 port nintendo64

Halo 64 Port Nintendo 64
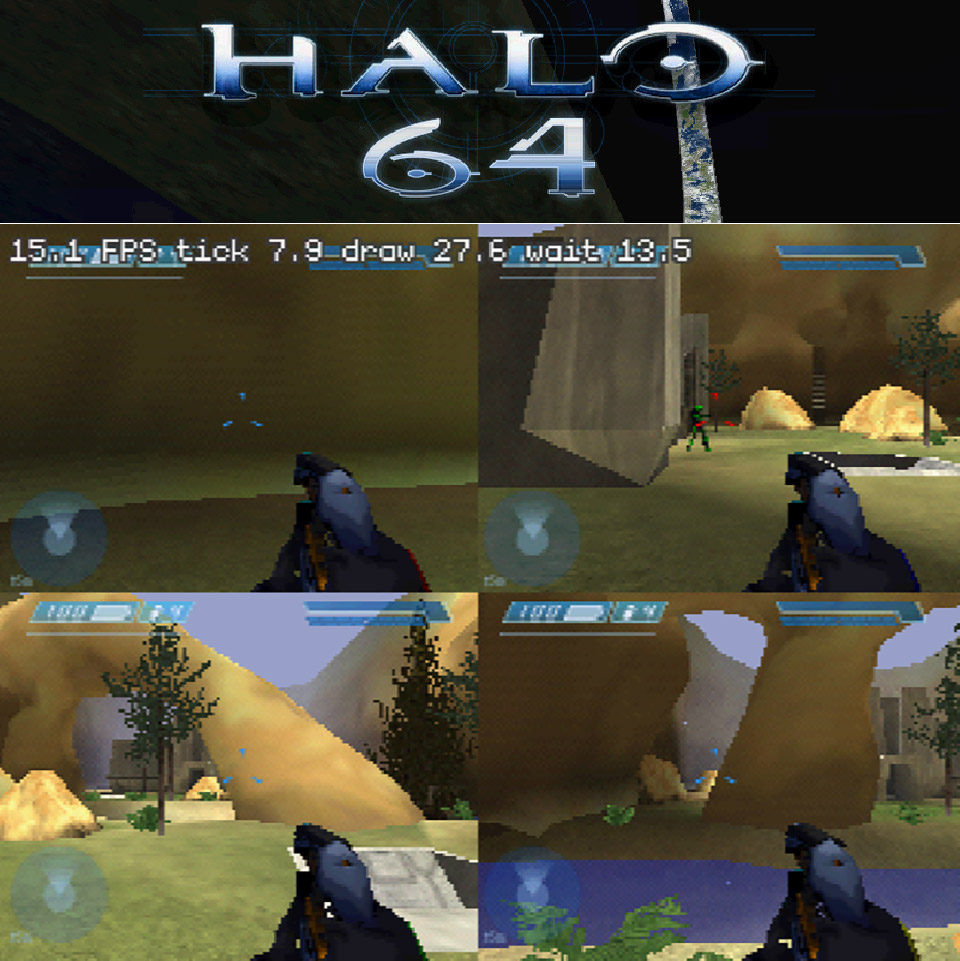
Twenty five years after Halo Combat Evolved redefined console shooters on the original Xbox, a fan project has moved its multiplayer suite onto the Nintendo 64. Halo 64, created by Jack Tulli and available on GitHub, runs the original game’s objects, physics, collision detection, weapons, game types, HUD and pathfinding on the N64’s VR4300 processor. Maps come from a player’s own Xbox disc image. A new renderer, menu system, HUD drawing and sound layer sit on top of libdragon and tiny3d.


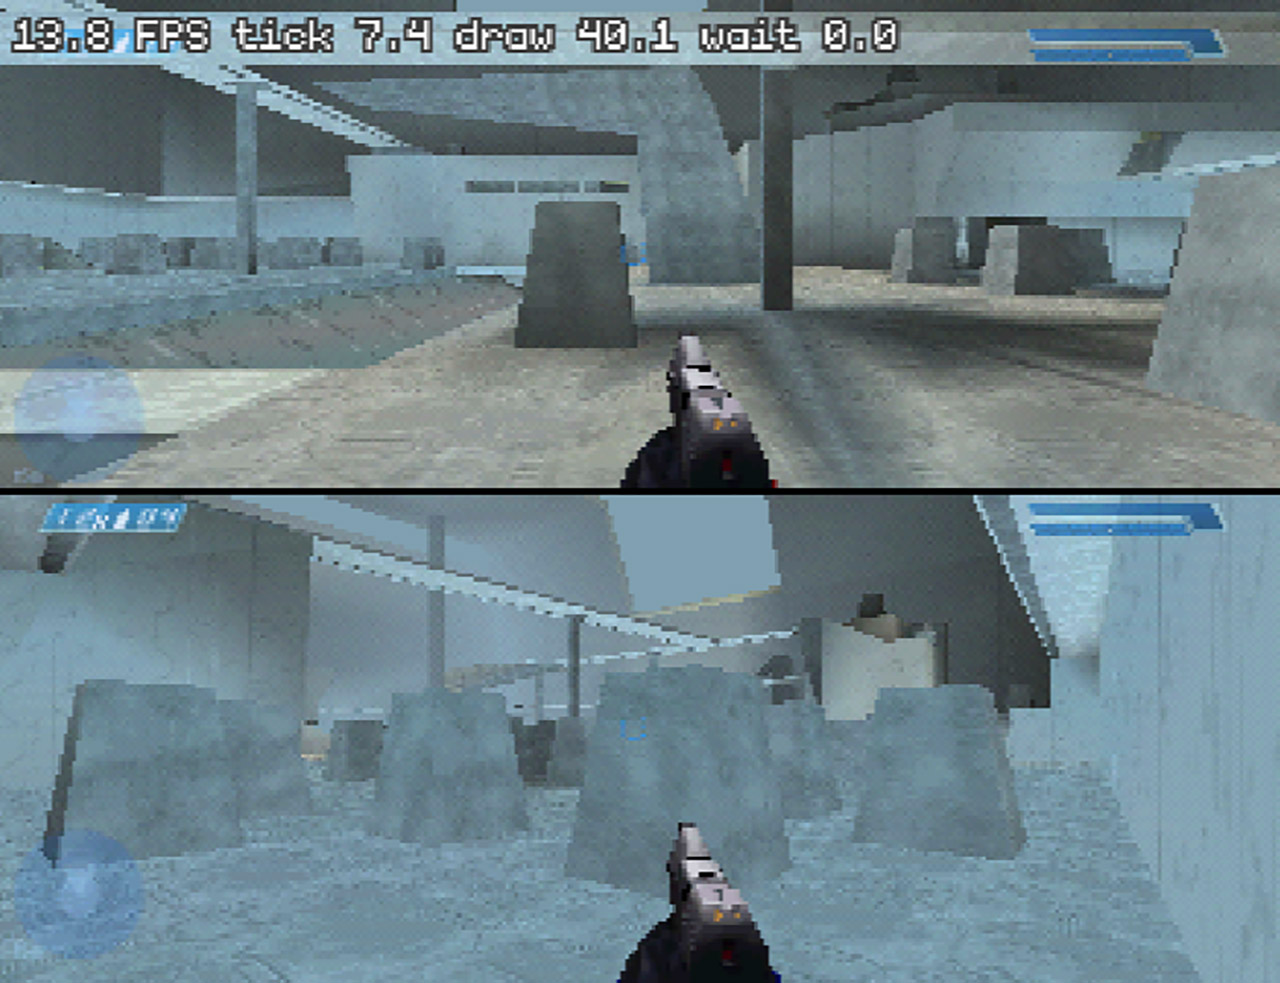
The end result is a local multiplayer extravaganza in which you can compete with pals in split screen mode, one to four players at a time. You’ll be able to play on all thirteen of the original multiplayer maps, including Prisoner, Hang ’em High, Chill Out, Derelict, Boarding Action, Blood Gulch, Wizard, Chiron TL-34, Longest, and the thrilling Damnation and frenetic Rat Race. Don’t worry about the game modes; vehicles, guns, teleporters, and water features all accompany the journey. You can play Slayer, Team Slayer, Slayer Pro, Capture the Flag, King of the Hill, Oddball, and even Race, with each accessible in free-for-all or team modes.

A bunch of bots will fill the empty spaces, and up to fifteen AI opponents can join in on the fun, as long as Halo does not reach its sixteen-player limit. You can select the difficulty level, ranging from lovely and easy to super-hard legendary. Get this: the bots employ the same pathfinding as the original game. They focus on the more powerful weapons and fight in groups. Each match, they select a random character name from a list of roughly three hundred very unusual names selected from Mario, Zelda, GoldenEye, and Rare’s N64 libraries. After eight bots, it becomes a little unwieldy, and the menu cautions you that your console may suffer slightly.


The Firefight mode now allows you and a few friends (up to four players) to take on waves of Grunts, Jackals, and Elites on multiplayer maps while sharing lives and selecting from four distinct difficulty settings. A pause menu allows you to stop the action, view the scoreboard for everyone (including the AI), and even access the original Halo HUD, which includes shields, health, ammunition, a motion sensor, messages, and scores. The traditional sounds from the original game have returned, including weapon and vehicle noises. Yeah, the main menu looks a little rough with its interlaced 640×480 image on that familiar ring-in-space backdrop, but it now proudly displays a Halo 64 logo.

Halo 64 Port Nintendo 64
When it comes to controller layouts, you’re in luck, as there are six to pick from, including regular, GoldenEye, D-pad movement, and even bumper jumper. Want to crouch? You can either turn it on or keep it held down. Other customization options include changing the look inversion, swapping the fire and grenade buttons, and even enabling independent look speeds for the analog stick and C buttons. Oh, there’s also rumble feedback. You may enable it for shots, hits, explosions, and vehicles, with a toggle to turn it off or on for each player. Picture quality and performance settings are saved directly to the cartridge’s EEPROM.

Halo 64 Port Nintendo 64
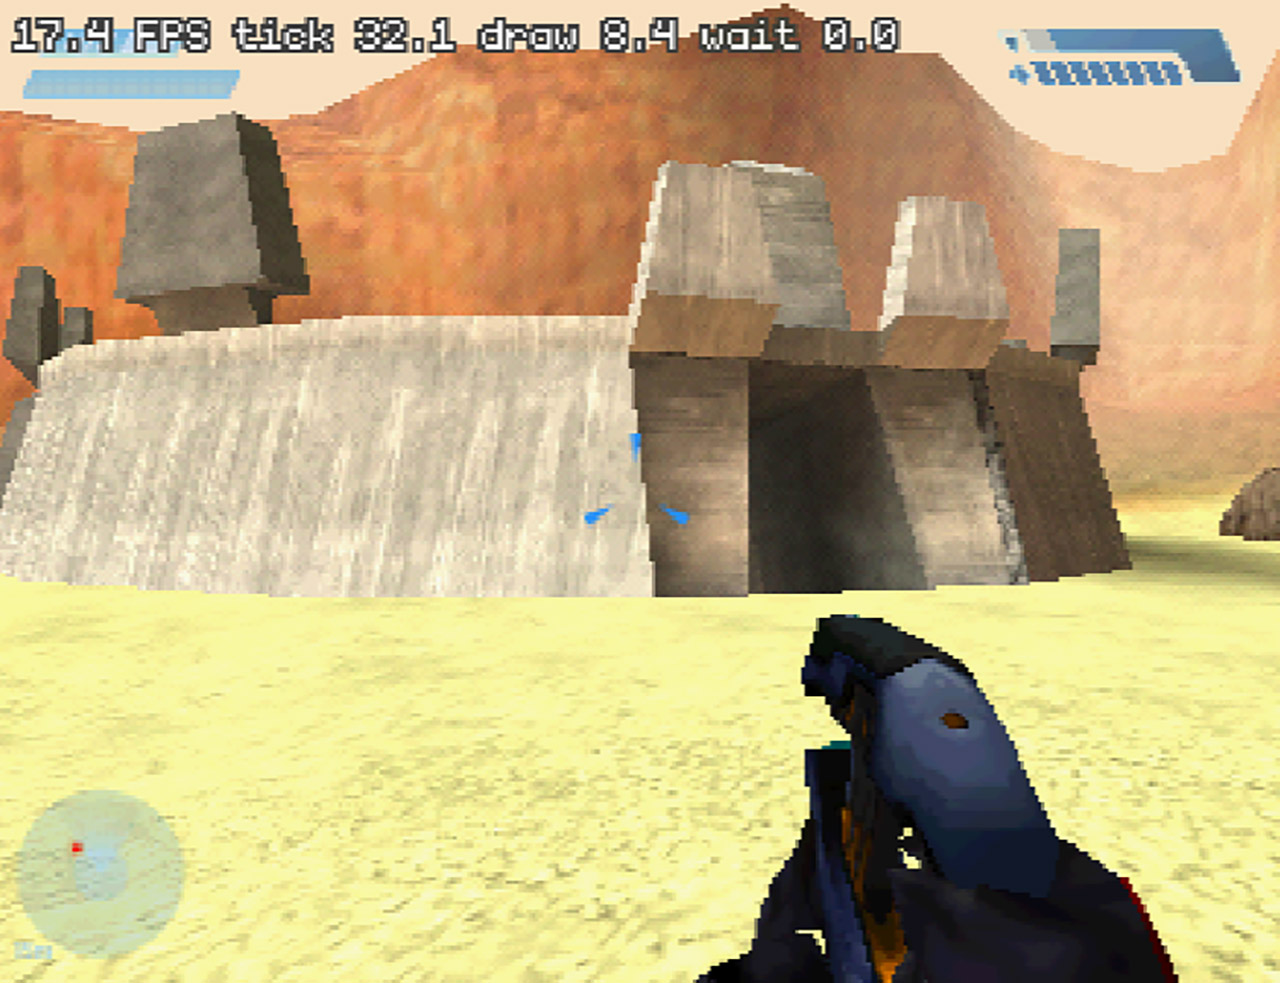
The game’s graphics use a color map method to load neighboring tiles from the cartridge, giving the ground textures far more clarity than a simple low-poly approach. Plus, Blood Gulch retains its beautiful blue sky. If you’re concerned about performance, don’t be, because the game allows you to trade off graphic detail for frame rate when more players or bots join in the fun.

Advertisement

Source link

Continue Reading

Tech & AI

The best apps for tracking your reading and discovering new books

Published

on

fable app

From discovering new books and organizing your reading list to tracking your reading goal and sharing recommendations, book apps make it easier to maintain reading as a hobby. There are numerous apps on the market that promise to do just that, so we’ve compiled a list of some of the best ones to help you pick the right one for you. Whether you’re an occasional reader or a dedicated bookworm, these apps can help you make the most of your reading journey.

Some of the apps on this list are somewhat new, while others have been around for a few years. Amazon-owned Goodreads, which is arguably the most popular book-related app, isn’t included in this list because we’re focusing on newer, lesser-known platforms. 

Fable

fable app
Image Credits:Fable /

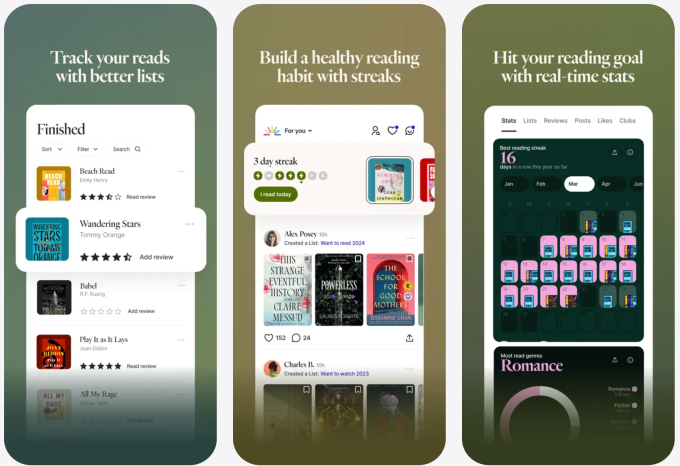
Fable is a reading app that combines book tracking with a social platform. It lets you organize reading lists, set reading goals, track streaks, write reviews, and join virtual book clubs. You also get personalized book recommendations and the chance to discuss what you’re reading with other readers. 

The app differs from others on this list because it puts reading and community at the forefront of the platform, which makes it a great option for people who like staying motivated to read by being part of a community and discussing their reads. 

Fable is free to download on iOS and Android, but also offers a Fable Plus subscription tier that unlocks additional features like custom goals and advanced analytics for a monthly fee of $5.99.

Advertisement

Bookshelf

bookshelf app
Image Credits:Bookshelf /

Bookshelf is a reading app designed to help people organize their libraries, discover new books, and remember more of what they read. The app positions itself as an alternative to Goodreads, and combines traditional reading logs with AI-powered recommendations and tools.

You can create custom shelves, set reading goals, receive reminders, save favorite quotes, and access AI-generated book summaries, key insights, and thematic analyses to recall the books you’ve read and get a deeper understanding of them. 

Bookshelf is free to download on iOS, but offers a $6.99 monthly fee to unlock premium features like unlimited collections and enhanced analytics. 

Pagebound

Screenshot 2026 10 22 at 2.54.38 PM
Image Credits:Pagebound /

Pagebound is a book app that lets readers track their books, create lists, set goals, and discuss individual titles in dedicated forums. Instead of having to join an actual book club group, users can post reactions and thoughts to connect with others reading the same title.

You don’t have to worry about spoilers for the end of the book, as conversations are organized based on reading progress, allowing readers to share theories and thoughts as they read. The app is a great option for people who want to discuss their reads with others without having to commit to a scheduled book club.

Pagebound is free to download on iOS and Android and offers a $9.99 monthly subscription for added features like profile customization.

Advertisement

StoryGraph

storygraph app
Image Credits:Storygraph /

StoryGraph is a reading app that lets users track their reading, discover new books, and access detailed reading statistics and personalized recommendations. Users can set reading goals, join reading challenges, and find new titles based on their preferred moods, themes, genres, and pacing.

The app is ideal for readers who want to better understand their reading habits and discover books that match their current interests. Its recommendation system doesn’t solely rely on what’s popular or trending, and instead caters to exactly what readers are looking for. 

StoryGraph is free to use on iOS and Android, but also offers a paid subscription called StoryGraph Plus that costs $4.99 per month and unlocks custom charts, additional statistics, and more. 

Margins

margins app
Image Credits:Margins /

Margins is a great option for mood readers, as it offers mood-based discovery alongside a more focused reading experience. It helps users find their next read based on how they feel in the moment by searching for specific vibes, such as “books like 1920s Paris.” Users can also track their reading goals.

The app also lets users customize their virtual library by choosing book covers that match their aesthetic and organizing their shelves in different ways, including by color. For users who enjoy a more immersive experience, Margins offers a built-in “Reading Time” meditation timer that blocks social media apps.

Margins is free to download on iOS and Android.

Advertisement

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Source link

Continue Reading

Tech & AI

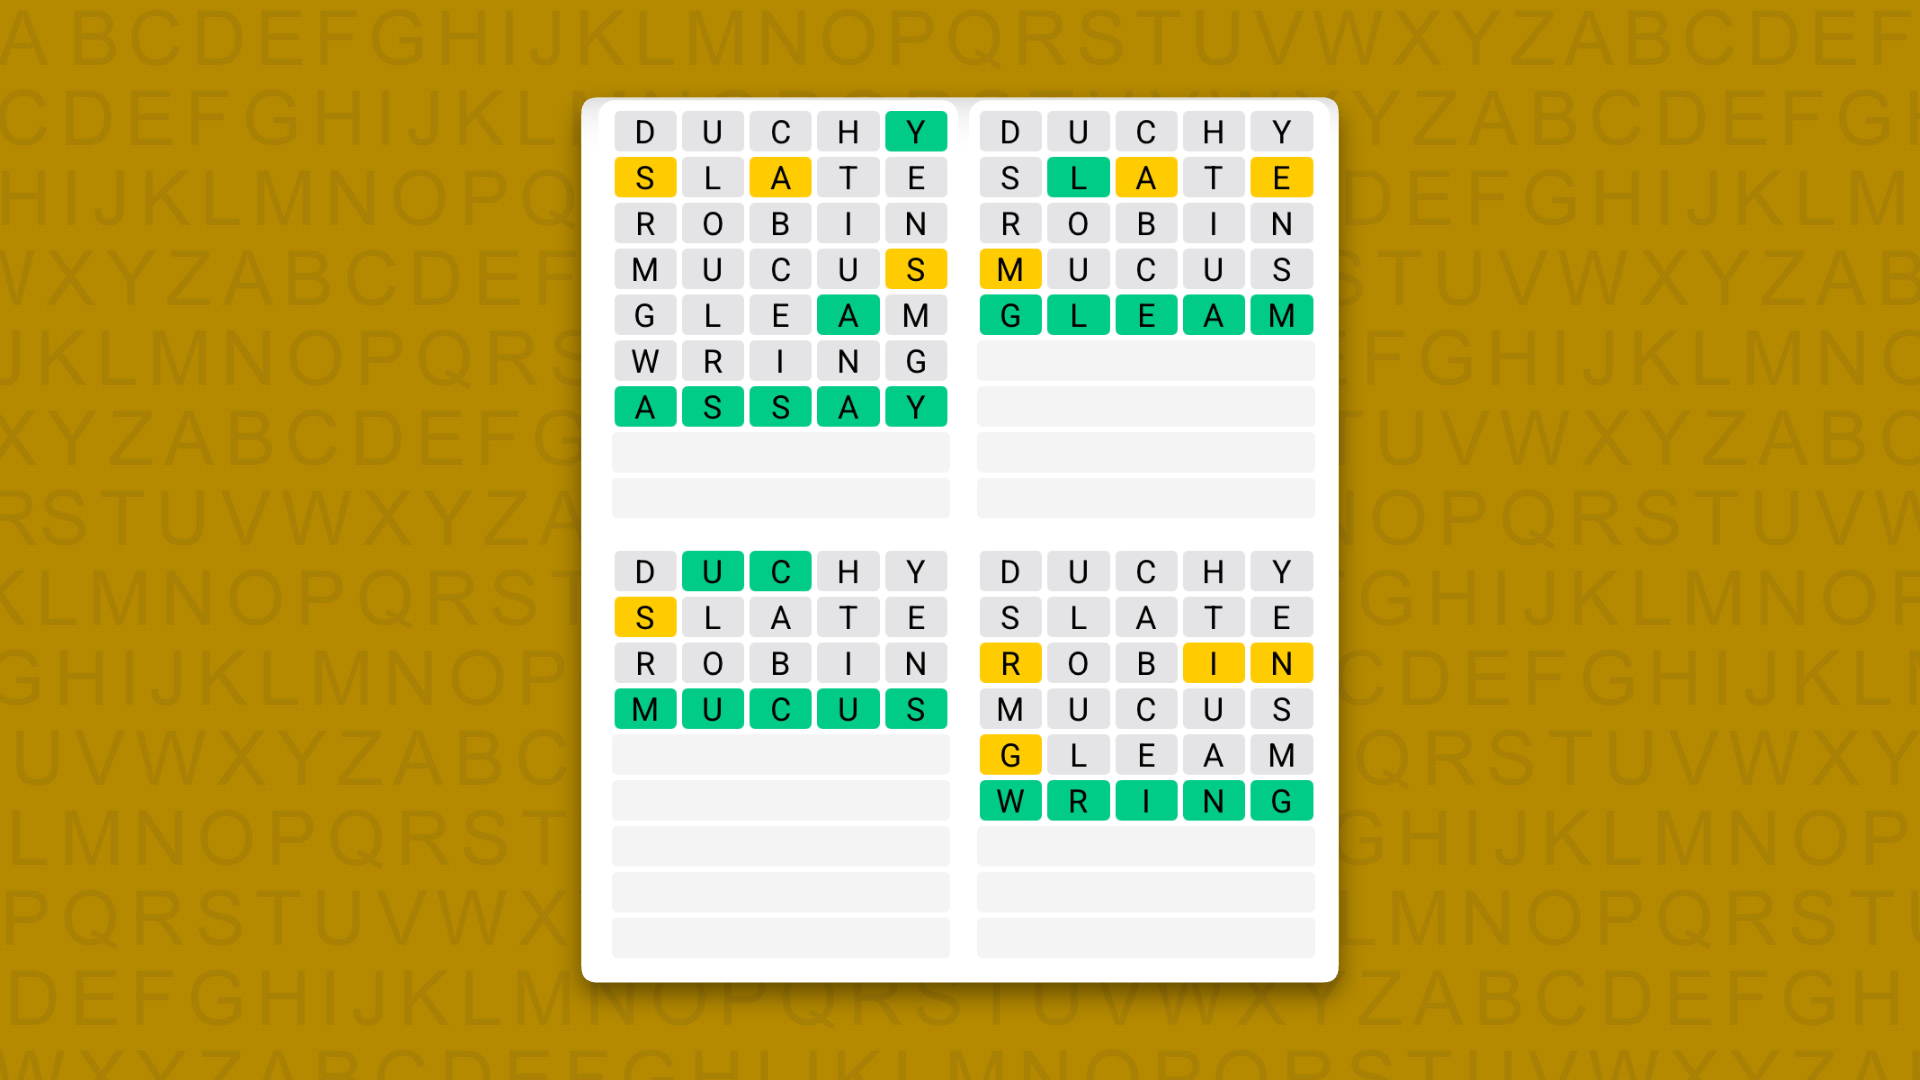
Quordle hints and answers for Monday, October 26 (game #1736)

Published

on

zrCsZRe5JijEViSqKhbjX9


Looking for a different day?

A new Quordle puzzle appears at midnight each day for your time zone – which means that some people are always playing ‘today’s game’ while others are playing ‘yesterday’s’. If you’re looking for Sunday’s puzzle instead then click here: Quordle hints and answers for Sunday, October 25 (game #1735).

Quordle was one of the original Wordle alternatives and is still going strong now more than 1,500 games later. It offers a genuine challenge, though, so read on if you need some Quordle hints today — or scroll down further for the answers.

Enjoy playing word games? You can also check out my NYT Connections today and NYT Strands today pages for hints and answers for those puzzles, while Marc’s Wordle today column covers the original viral word game.

Advertisement

Source link

Continue Reading

Tech & AI

333 Tor exit nodes hijacked to intercept SSH traffic and retrieve plaintext email

Published

on

GettyImages 1237260150

GettyImages 1237260150

Unknown hackers hijacked more than 300 Tor exit nodes and reconfigured them to favor unencrypted email traffic and redirect SSH connections through servers they controlled, a researcher reported Tuesday.

The hijacking began in late August, when, according to Tor volunteers, the attacker used a valid password that had been reused to gain access to a Tor management server. The attacker then installed Ebury, a backdoor written for Linux that was discovered 12 years ago.

Mysteries remain

Then the attacker connected from the management server to a second Tor server, called Switzerland2, through SSH, using an RSA key that, for unknown reasons, investigators couldn’t find among Switzerland2’s authorized keys. With administrative control of Switzerland2, the attackers installed Ebury there as well. Finally, the attacker reconfigured settings on two exit nodes that Switzerland2 hosted.

Ultimately, 333 exit relays were involved in the SSH and email interception campaign, although investigators haven’t established how the attackers gained control of all the underlying servers. The attackers then reconfigured the servers. One set of changes redirected SSH traffic traversing Tor to one of 12 attacker-controlled interceptor servers. Tor users who ignored warnings that the SSH host key had changed would then enter their SSH passwords.

Advertisement

A second set of changes caused the exit nodes to block ports 25, 465, 587, 993, and 995—used to accept various forms of encrypted email—while continuing to allow ports for receiving unencrypted email. If email services downgraded the connections, the attackers used their access to the exit nodes to obtain unencrypted messages. It’s unclear whether any such downgrade attempts succeeded. The hijacking occurred from October 2 to October 5.

Tor volunteers partially outlined the initial compromise of the management server and Switzerland2 and the attempt to intercept unencrypted email. Tuesday’s report revealed many new details, including how many exit nodes were compromised and how the attackers used them to redirect SSH traffic.

“If you happen to get a circuit that exits over one of those 333 infected exit nodes, you won’t notice anything at first,” Kaba, the name of the Tor volunteer who authored the post, wrote. “Encrypted web traffic is forwarded as usual, but if you attempt an SSH connection over Port 22, you’re unknowingly redirected to one of 12 SSH interception servers. That’s exactly what happened to me on Friday morning.” Kaba then received the following warning:

Advertisement

Source link

Continue Reading

Trending

Copyright © 2025