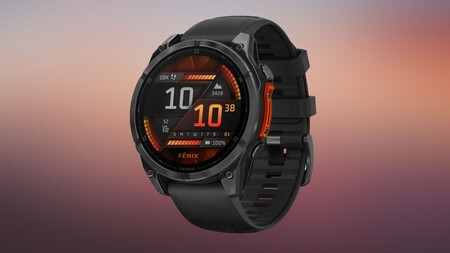
Multisport watches with this depth of training data rarely fall under a thousand dollars, so shaving $250 off the fenix 8 lands it firmly in genuine impulse buy territory for serious athletes today.
Advertisement
Strap it on, and you get a built-in LED flashlight, leakproof metal buttons and a 40-metre dive rating, the kind of rugged spec sheet you would expect from whatever tops a best Garmin watch 2026 buying guide.
The fenix 8 also handles training the way a proper coach would, breaking down recovery and readiness scores each morning based on your sleep, heart rate and recent workload. It even builds targeted strength training plans and sport-specific workouts, so the guesswork of programming your own week disappears entirely.
Advertisement
That same attention to detail carries over to navigation, with built-in ABC sensors and preloaded TopoActive maps plotting dynamic round-trip routes that guide you back to your exact starting point right on schedule every time.
Advertisement
All of it runs on a battery that Garmin rates at up to 16 days in smartwatch mode, which is more than enough for a full week away from home without hunting for a charger.
A built-in speaker and microphone let you take calls straight from your wrist once paired to a phone, while Garmin Pay and onboard music storage mean you can leave the phone behind entirely on a run.
Even at $749.99, the fenix 8 still packs dive certification, weeks of battery life and real coaching smarts into a single rugged watch that costs a full $250 less than its usual asking price.
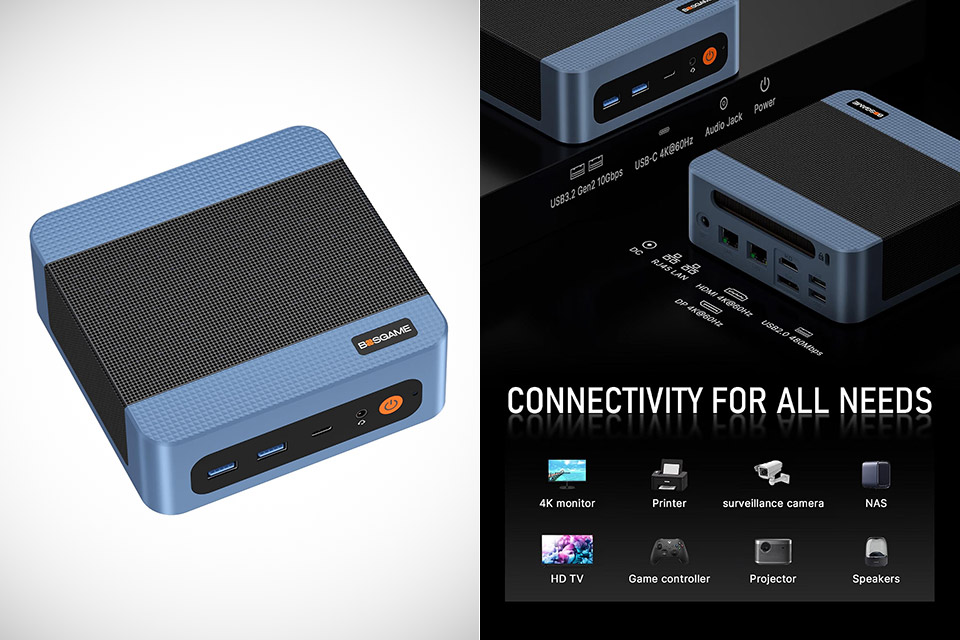
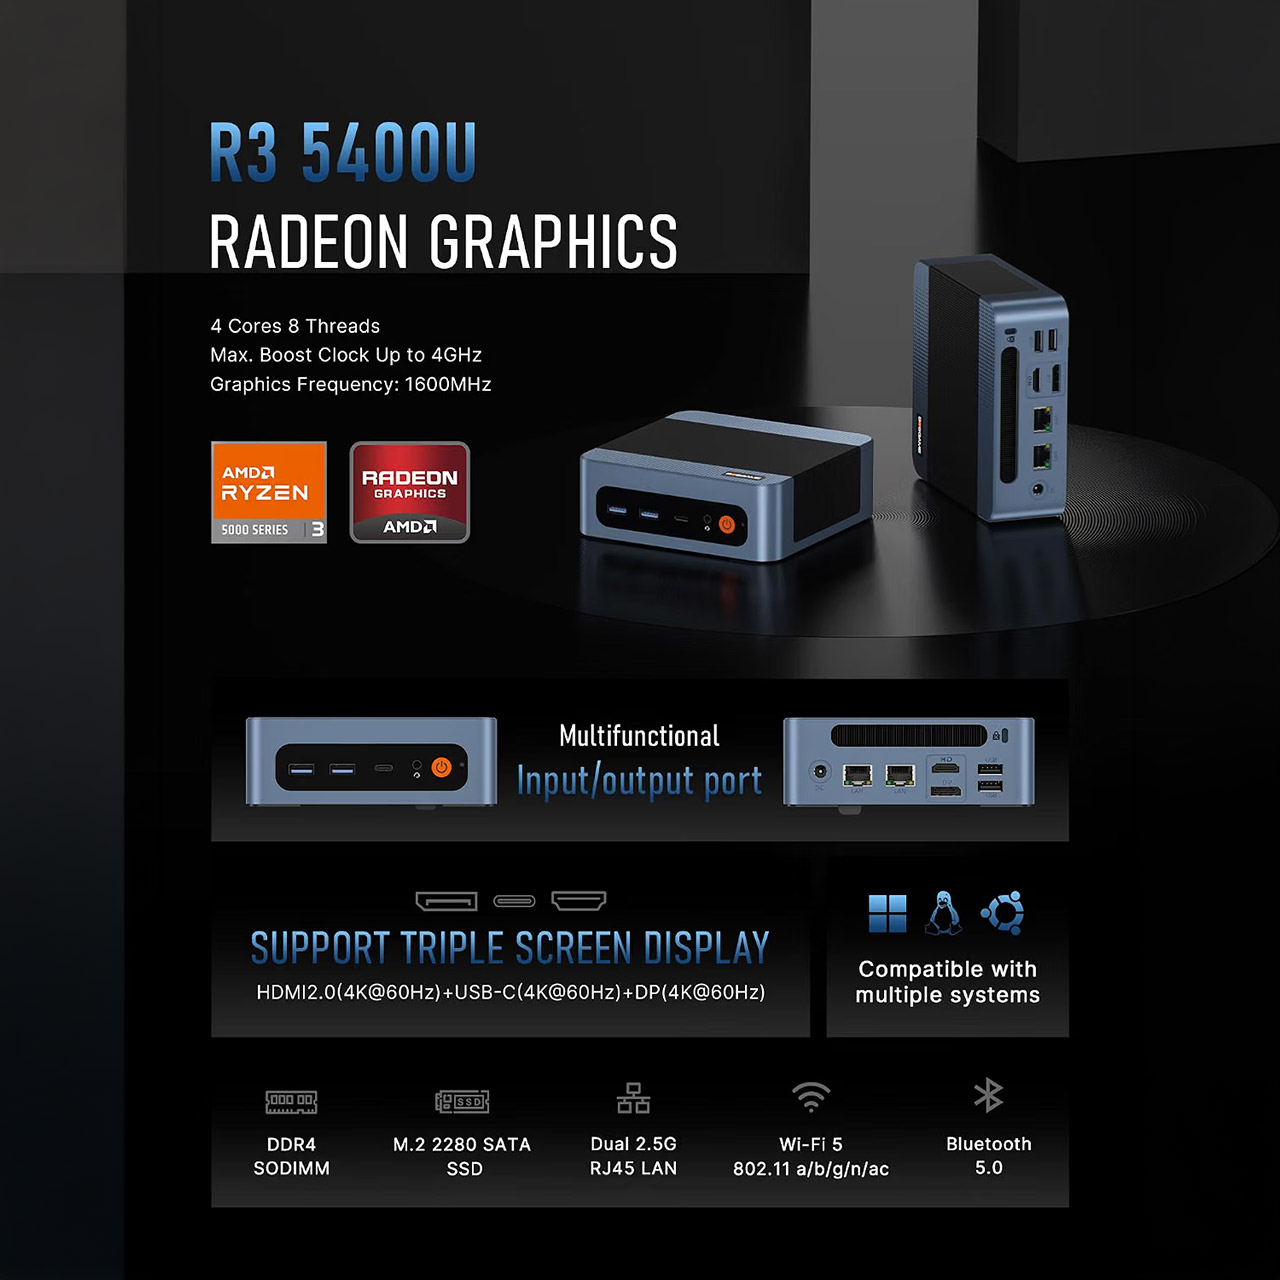
BOSGAME E5 Mini PC, priced at $186.99 with promotion code: 5400U45 (was $340), keeps showing up in deal threads because a machine this small almost never arrives with two 2.5-gigabit Ethernet ports, three 4K outputs, and a licensed copy of Windows 11 Pro for less than $300. Inside is a 15 watt laptop processor, a Ryzen 3 5400U with 4 cores and 8 threads to get the work done.
The Ryzen 3 5400U can reach 4.0GHz and has an impressive 8MB of L3 cache, all owing to AMD’s Zen 3 design. In contrast, the Ryzen 3 5300U, utilized in other SKUs, has a maximum clock speed of 3.8GHz and 4MB of L3 cache on the slightly older Zen 2 configuration. What exactly do you get out of that? The E5 has a little more oomph than the Intel N150 and N100 boxes that are widely available in this price range, which is why reviewers continue to use it as an office PC, a light virtualization host, and for any quiet box job such as spreadsheets, browser tabs, and video calls.
【AMD Ryzen 3 5300U CPU: Outperforms N150 & 3500U】 BOSGAME E5 mini PC is powered by the TSMC 7nm FinFET architecture AMD Ryzen 3 5300U processor…
【8GB DDR4 RAM & 256GB NVMe SSD Storage】 Installed with high-speed 8GB DDR4 dual-channel memory and a fast 256GB M.2 2280 SSD, eliminating slow…
【High-Capacity Dual M.2 SSD Storage Expansion】 Never worry about running out of space for your business files. In addition to the pre-installed…
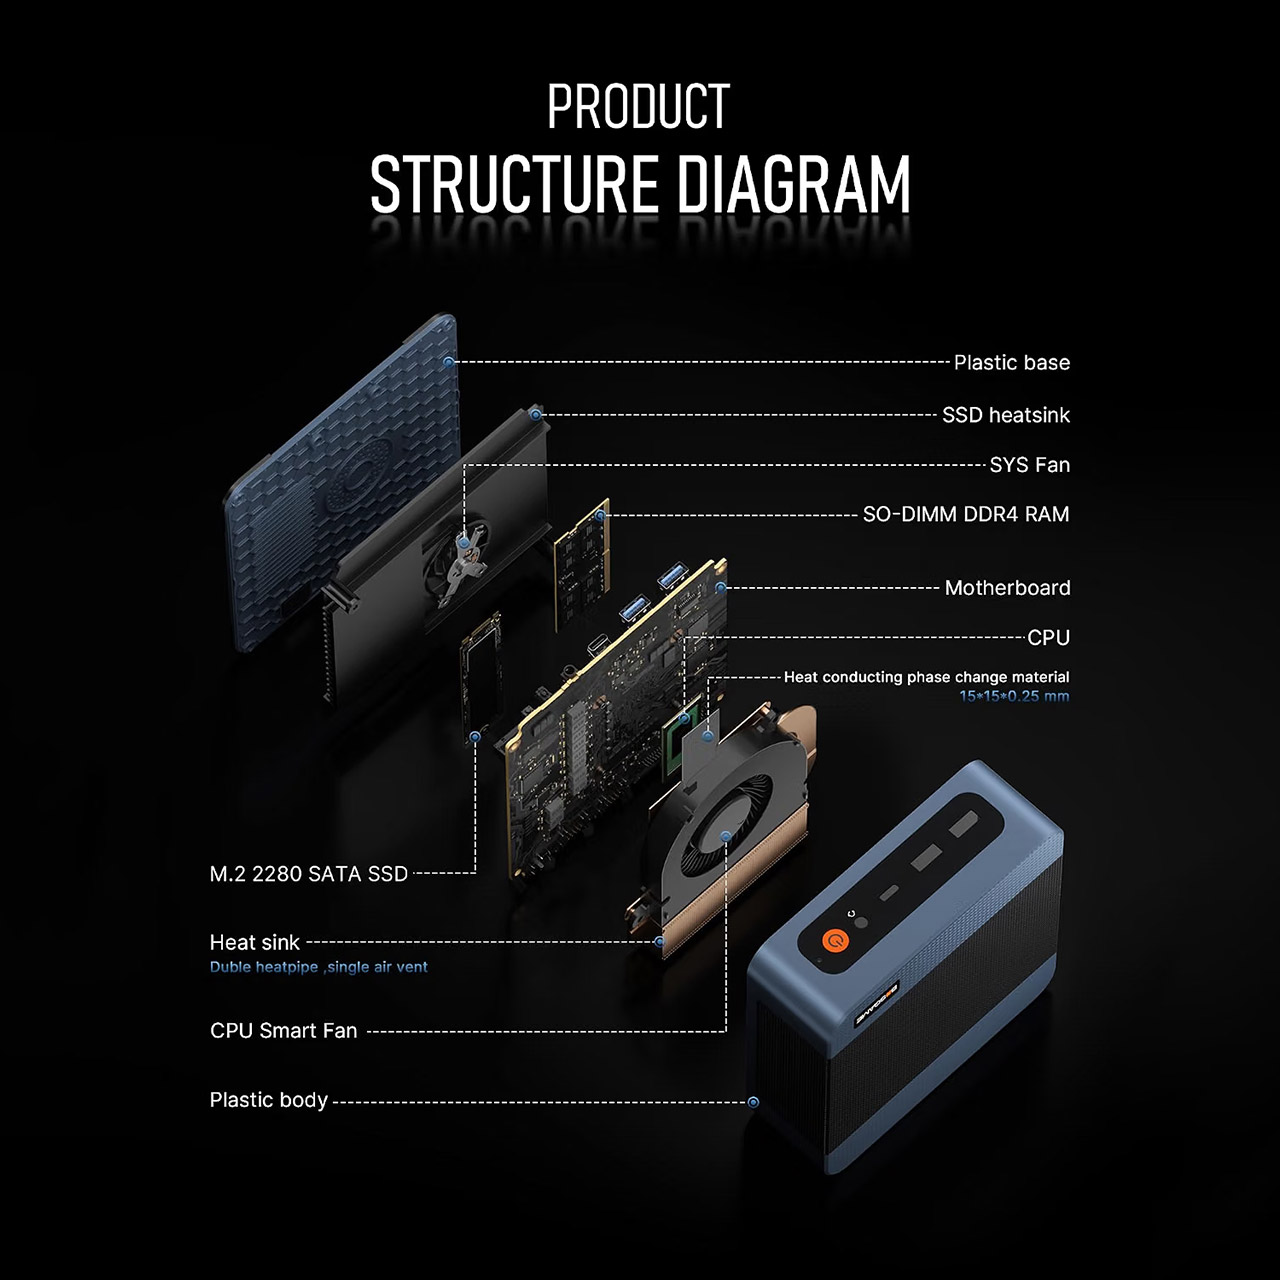
However, memory and storage are where things become interesting. The 8GB base units can easily be upgraded with a matching SODIMM to achieve dual-channel speed. There are two slots for accomplishing this, each of which can support up to 32GB of DDR4-3200 RAM, which is important if you’re running virtual machines or a software firewall on the side. Storage amounts to 256GB out of the box, but you do get a second empty M.2 2280 socket, allowing you to swap out the factory SSD for a new NVMe drive (up to 4TB) without having to open the chassis. Even if you open the case, this 8GB/256GB machine can be transformed into a fine daily driver with a $30 memory upgrade and a larger SSD.
On the back, you’ll discover a couple of Realtek RTL8125 ports, which, believe it or not, are the reason this model is still suggested for home laboratories. Each port operates at 2.5Gbps, allowing you to connect one cable to the WAN and one to the LAN and run pfSense or OPNsense without a cumbersome USB adaptor. Want to run a small NAS or link-aggregate your network? Same ports, same story. However, the most important element here is wired speed. Wireless is kind of a compromise. According to the boxes, this device features Wi-Fi 5 and Bluetooth 5.0, which is fine; after all, you wouldn’t expect Wi-Fi 6 at this price.
Advertisement
The graphics don’t skimp out. You get HDMI 2.0, DisplayPort, and a full-function USB-C port, so you can connect three 4K panels at 60Hz without a problem. The Vega 6 graphics can manage that load with ease, and it even decodes 4K video like nobody’s business. Want to play older games or imitate them? You can do this at 1080p with low settings.
The USB ports are quite mixed. You’ll find a front USB-C port as well as a handful of USB 3.2 Gen 2 Type-A ports, allowing you to connect disks and docks to the front panel. The rear panel also includes two USB 2.0 connections and a 3.5mm combo jack. To top it all off, the chassis measures approximately 130mm square and 46mm height, making it compact enough to hide behind your monitor even if you don’t already have a VESA plate.
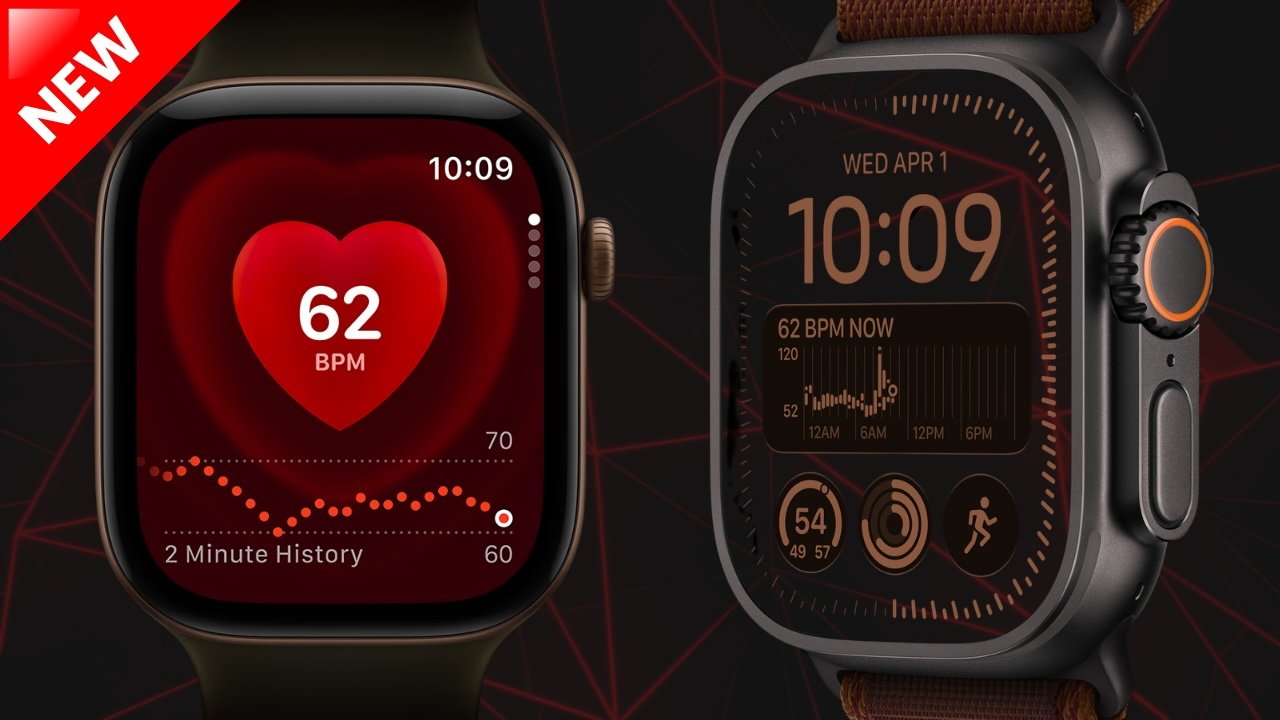
The steepest discount can be found on several Apple Watch Ultra 4 styles, though, which are $20 off. Both the Natural Titanium and Black Titanium Case options are eligible for the markdown, with qualifying band colors and sizes changing rapidly.
Advertisement
Apple Watch Series 12 – 42mm
Apple Watch Series 12 – 46mm
Apple Watch Ultra 4 – 49mm
Black Titanium Case, Translucent Black Ocean Band, GPS + Cellular: $779.99 ($20 off)
The fintech announced a $182m investment in the country over the next five years.
Revolut has applied for a Swiss banking licence as part of its continued global expansion campaign. The UK fintech has established or is aiming to set up authorised banking entities across the globe, including in Colombia, the US, France, Peru, the UK, Australia and Mexico.
Revolut already has more than 1.3m customers in Switzerland, currently served by Revolut Bank UAB, which is licensed in Lithuania. Obtaining a Swiss banking licence would mean the fintech can offer its customers Swiss IBANs, salary accounts, e-bills, merchant acquiring and deposit protection under the country’s strict standards.
The company also announced plans to invest more than 150m Swiss francs ($182m) in Switzerland over the next five years to create local jobs and support product development. Revolut also intends to make a number of senior leadership appointments to further strengthen its local banking build-out.
Advertisement
“Together with our existing banking licences and regulatory infrastructure across Europe, this would further strengthen our compliance, governance and regulatory framework,” said David Tirado, Revolut’s chief commercial officer.
Julian Biegmann, Revolut’s general manager for Switzerland, added: “Revolut is already Switzerland’s leading fintech. With our own banking licence, we would become a true Swiss bank, able to offer our more than 1.3m customers our leading Revolut banking product with a Swiss finish.”
Earlier this year, reports suggested that the fintech was on its way to a $200bn valuation in an eventual initial public offering expected around 2028. It was last valued at $75bn after a major share sale last November.
News of the company’s continued expansion comes just days after it disclosed a data breach that is understood to have affected nearly 700 customers globally, including 12 in Ireland.
Advertisement
In a community alert last week, the company explained that it disclosed sensitive customer data to an unauthorised fraudulent party after receiving requests for information from an email with a government agency domain.
The company mistakenly fulfilled the data requests before realising that the sender was phishing for data, it said. The disclosed data included full names, dates of birth, occupations, addresses, contact details, passports, drivers’ licences, financial statements and facial verification images.
Don’t miss out on the knowledge you need to succeed. Sign up for the Daily Brief, Silicon Republic’s digest of need-to-know sci-tech news.
First look: Valve has open-sourced Lepton, the Android compatibility layer built for the Steam Frame headset, giving VR developers a way to bring existing Android games to the device without rebuilding them for an entirely different platform. The newly available code also offers a detailed look at how Valve tailors an Android environment for VR gaming on SteamOS, covering everything from graphics access to development and profiling tools.
The release follows the Steam Frame’s launch and builds on Valve’s March announcement of Lepton alongside the Steam Frame Verified certification requirements.
In purpose, the project resembles Proton, Valve’s tool for running Windows games on SteamOS and Linux, though it takes a different technical route: rather than translating Windows software interfaces, Lepton provides a purpose-built, game-tuned Android environment.
Advertisement
Valve has kept that environment deliberately narrow. Lepton isn’t designed to turn Steam Frame into a general-purpose Android device, nor does it aim to support every Android app. To keep overhead low, the software disables Android services that aren’t needed for gaming – a trade-off that can affect apps relying on those services.
Lepton is built to work closely with the SteamOS host system, mounting host libraries for graphics drivers, Steam and Steamworks, and Vulkan layers. Valve lists support for graphics stacks including Mesa and Zink, along with Vulkan tooling for foveated rendering and render-pass optimization.
Those capabilities are crucial for VR games, where rendering efficiency and stable frame delivery are central to comfort and image quality. By exposing the host graphics stack to the Android environment, Valve appears to be avoiding some of the overhead that can come with a more isolated container approach.
The project also ships with tools aimed at developers porting games to the platform, including support for debuggers such as strace, GDB, LLDB and RenderDoc, plus Perfetto for performance profiling. The flatscreen application window stays hidden by default, though developers can surface it for testing and troubleshooting.
Advertisement
Valve says Lepton runs without root access or root-level setup tools, with every process inside a Lepton instance running as the same non-root user. Per the project’s documentation, there’s no enforced isolation between apps within an instance, so each app is expected to run in its own separate Android container.
For developers, the open-sourced code offers a clear window into Valve’s approach to Android game support on SteamOS, including its use of host graphics libraries, Vulkan layers and a reduced Android software stack. It also gives Linux developers a base for experimenting with other uses, though Valve cautioned that those are outside Lepton’s main purpose.
This article is written on an open-source operating system, but not an open-source machine — the BIOS isn’t open-source, and even if it were supported by the coreboot project (formerly LinuxBIOS), there would still be a whole host of binary blobs required to get it to boot. On one vintage architecture, there’s one less blob, as coreboot can now initialize DRAM on Intel Bay Trail SOCs, as [Mate Kukri] presented in a talk at the recent Open Source Firmware Conference.
Bay Trail isn’t exactly cutting-edge hardware, to be sure — the SoCs are over a decade old at this point, and were only used in low-performance mobile applications like Chromebooks. On the other hand, coreboot has been on Chromebooks for at least as long. Getting DRAM set up is difficult because, well, you don’t have any memory to work with until you do. Traditionally, the way you did that was to call on one of the many proprietary ‘binary blobs’ provided with next to no documentation by the manufacturer. Reverse engineering that requires some serious bus-sluthing, which was done in software with the SerialICE debugger and the Unicorn Engine CPU emulator. The talk focused on that technique and how it might be applied more widely, rather than getting into the weeds of how to do DRAM init on one obsolete SOC. At some point the whole thing should be archived on the OFSC website so those of us not lucky enough to attend in person can hear what [Mate] — and all the other speakers — had to say.
Because coreboot is open, you can do a lot more with it than a proprietary UEFI firmware — for example, you can choose not to initialize RAM at all, and run entirely in the CPU’s cache. You can also — of course — run DOOM. If you want to be binary-blob-free, you’ll need to find hardware supported by the more hardcore Libreboot distribution of coreboot, which admits no binary blobs at all. When it comes to Libreboot, it might actually be easier to install than to find compatible hardware these days.
The initiative aims to ‘position Ireland as a leading testbed for insurance innovation by connecting emerging companies directly with insurers, industry experts, investors and experienced founders’.
12 Ireland-based insurance technology start-ups will participate in the second edition of InsTech.ie’s Foundry, a pre-accelerator programme run in partnership with Furthr, one of the country’s four Business Innovation Centres.
InsTech.ie is a national body that aims to connect start-ups, insurers, investors and policymakers to accelerate innovation and help Irish insurtech companies scale globally.
It is supported by 24 insurance industry members, tracks more than 120 Irish insurtech companies, and has eight innovation partnerships, including with IDA Ireland, KPMG and Enterprise Ireland.
Advertisement
The Foundry initiative is designed to create a direct route between established insurance expertise and younger or smaller companies developing technologies capable of shaping the insurance sector’s future, according to InsTech.ie.
The programme aims to “position Ireland as a leading testbed for insurance innovation by connecting emerging companies directly with insurers, industry experts, investors and experienced founders”, according to its operator.
“The first Foundry cohort showed what can happen when ambitious founders are given direct access to the insurance expertise, networks and decision-makers that can help turn promising ideas into commercially viable businesses,” said Gary Leyden, CEO of InsTech.ie.
“With cohort two, we want to build on that momentum and give another group of companies the opportunity to validate their solutions, develop meaningful industry relationships and accelerate their path to market.
Advertisement
“Ireland has a unique combination of insurance expertise and technology talent, and the Foundry is about bringing those two strengths together.”
The 12 selected companies, and their technological offerings, are:
Alteric AI
An AI orchestration layer for commercial brokerages to automate workflows across servicing, renewals, claims and new business.
Fairwrite
A start-up aiming to make life and protection insurance more inclusive for people with mental health conditions, disabilities or neurodivergence through a more individualised approach to underwriting.
Advertisement
Finch AI Systems/LitAgent
An explainable AI platform to support personal-injury reserving and settlement valuation, producing consistent, traceable assessments while keeping the final decision with the claims professional.
Global Nutrition Value
This company is creating a time-stamped evidence trail for food safety and compliance data with applications across underwriting, loss prevention, claims and product recalls.
Insurteam MGA
A start-up creating a solution that combines embedded travel insurance distribution with AI-enabled claims handling, allowing partners to offer cover at checkout and customers to manage claims through WhatsApp.
Maximo
A platform connecting pensions, tax and open banking to help consumers better understand and increase their pension contributions and access associated tax relief.
Advertisement
Model Library/Elliptic
This start-up is developing a climate-risk modelling platform to help insurers and other risk-transfer providers understand and quantify basis risk in parametric insurance.
RMI Agentic
A solution designed for managing risks created when autonomous AI agents transact on behalf of consumers.
SeatFair Technologies
This start-up is exploring how preference-pricing and optimisation technology could support complex reinsurance placements involving price, capacity, counterparties and terms.
TalkTerms AI/Swift Settle
An AI decision-support platform designed to help insurance professionals manage complex claims and complaints while retaining human oversight.
Advertisement
Vardus
A pre-send compliance platform that checks customer communications, identifies potential regulatory issues and provides greater oversight of recurring compliance risks.
Voxalytics
This start-up’s solution analyses broker-client calls to automate administration and identify portfolio-level signals around customer retention, churn, cross-sell and growth.
Don’t miss out on the knowledge you need to succeed. Sign up for the Daily Brief, Silicon Republic’s digest of need-to-know sci-tech news.
Tonight’s UFC 331 headline bout is a classic case of revenge or repeat as Joshua Van puts the UFC flyweight title he won against Alexandre Pantoja on the line at the Crypto.com Arena in Los Angeles. The Fearless won the belt in controversial fashion in December 2025 and the Cannibal is determined to right the wrong he has felt ever since.
Van’s victory at UFC 323 came after Pantjoa suffered a dislocated elbow 26 seconds into the original fight when the former fell and landed on the latter. The Brazilian has felt ignored by Dana White ever since, despite having championship victories against Brandon Moreno, Brandon Royval, Steve Erceg, Kai Asakura, and Kai Kara-France on his resumé. The 36-year-old has the experience and fuel from that defeat to inspire him. He’ll become the third flyweight champion to regain the belt after Moreno and Deiveson Figueiredo if he wins.
Myanmar native Van is well known for his speed but it was the striking that got him over the line against Tatsuro Taira in his solitary title defense in May. The 24-year-old will need to use that aggressive approach if he’s to back that up against another 5ft 5in fighter. This is sure to be a close fight and one not to be missed.
Advertisement
That’s the main event of a stacked card in which Arman Tsarukyan and Maurício Ruffy face off at lightweight with the winner likely to get a future title shot.
Here’s where to watch UFC 331 live streams online and from anywhere with a VPN – including a clever way to watch UFC 331 for just $1.
How to watch UFC 331 live stream in the US
Exclusive US coverage of the full UFC 331 event is on Paramount Plus. It’s being headlined by Joshua Van vs Alexandre Pantoja 2, which is expected to start at around 11pm ET / 8pm PT.
Advertisement
Plans start from only $8.99/month with the Paramount Plus Essential Plan, or you can upgrade to Premium for $13.99/month (see below for more details). You can also get a Paramount Plus trial with Walmart+ for $1 using this sneaky trick we found.
While Paramount Plus will show UFC 331 in its entirety, you can also watch the Early Prelims via UFC Fight Pass.
Away from home at the moment and blocked from watching UFC on your usual subscription?
You can still watch Van vs Pantoja 2 live thanks to the wonders of a VPN (Virtual Private Network). The software can make your devices appear to be back in your home country regardless of where you are, making it ideal for viewers away on vacation or on business. One of our favorites is Surfshark – we explain why in our Surfshark review.
It’s really straightforward to use a VPN to watch UFC 331.
Advertisement
1. Install the VPN of your choice. As we’ve said, SurfShark is our favorite.
2. Choose the location you wish to connect to in the VPN app. For example, if you want to watch the Paramount+ stream, select ‘United States’ from the listed countries.
3. Sit back and enjoy the action. Head to Paramount+ and tune into UFC 331.
Advertisement
How to watch UFC 331 live stream in the UK
The UFC 331 main card is available on TNT Sports 1 in the UK. It’s set to begin at 2am BST in the early hours of Sunday morning.
You can get it by adding TNT Sports to your Sky, Virgin Media or EE TV package, or pay from £25.99 per month for a HBO Max plan that includes TNT Sports.
UFC Fight Pass subscribers can also watch the Prelims and Early Prelims.
If you’re abroad whilst the MMA live stream is on, a VPN like Surfshark can help you to access your home streaming services from anywhere.
Advertisement
How to watch UFC 331 live stream in Canada
There are a host of pay-per-view providers offering a UFC 331 live stream in Canada.
You can head to the likes of Sportsnet, Bell or the UFC Fight Pass to watch the whole event, where the PPV price is set at $69.99. Prelims will also be shown on Sportsnet and TVA Sports, with Early Prelims also on UFC Fight Pass.
North of the border from the US? You can use Surfshark to watch your Paramount Plus subscription like you were back at home.
That means you can live stream UFC 330 via your web browser and devices like Android, iOS, Samsung TV, Apple TV, Android TV, Telstra TV and Chromecast.
You can also catch all the Prelims (but not the Van vs Pantoja 2 main event) via Paramount+ and free-to-air Network 10.
Advertisement
Downloading a VPN will help you access your subscriptions from anywhere if you’re abroad when the fight is on.
Can I watch UFC 331 for free?
Not quite. Other than the sneaky little Walmart+ for $1 trick described above in the US, there doesn’t seem to be any way to watch UFC 331 for free. It’s on Paramount Plus in the US, which no longer carries a free trial. And it’s a PPV in many other countries around the world.
When does UFC 331 start?
The UFC 331 Main Card is scheduled to begin at 9pm ET / 6pm ET on Saturday, September 19. That’s 2am BST or 11am AEST in the UK and Australia on Sunday, September 20.
Before that, the Early Prelims start at 5pm ET / 2pm PT / 10pm BST / 7am AEST (Sun) and the Prelims at 7pm PT / 4pm PT / 12am BST (Sun) / 9am AEST (Sun).
Advertisement
Can I watch UFC 331 on my mobile?
Yes. Most broadcasters have streaming services that you can access through mobile apps or via your phone’s browser – Paramount Plus, HBO Max and Kayo Sports all have mobile apps, for example.
You can also stay up-to-date with the latest UFC news and plays on the official social media channels on X (@ufc), Instagram (@ufc), Facebook (UFC) TikTok (@ufc) and YouTube (@ufc).
UFC 331 full card
Main card Joshua Van (c) vs Alexandre Pantoja (Flyweight) Arman Tsarukyan vs Maurício Ruffy (Lightweight) Patrício Pitbull vs Choi Doo-ho (Featherweight) Gable Steveson vs Sean Sharaf (Heavyweight) Alonzo Menifield vs Iwo Baraniewski (Light Heavyweight)
Advertisement
Prelims Marlon Vera vs Charles Jourdain (Bantamweight) Tai Tuivasa vs Robelis Despaigne (Heavyweight) Michael Aswell Jr vs Yoo Joo-sang (Featherweight) Ryan Gandra vs Osman Diaz (Middleweight)
Early prelims Edmen Shahbazyan vs Brunno Ferreira (Middleweight) Casey O’Neill vs Eduarda Moura (Women’s Flyweight) Giga Chikadze vs Joanderson Brito (Featherweight)
We test and review VPN services in the context of legal recreational uses. For example: 1. Accessing a service from another country (subject to the terms and conditions of that service). 2. Protecting your online security and strengthening your online privacy when abroad. We do not support or condone the illegal or malicious use of VPN services. Consuming pirated content that is paid-for is neither endorsed nor approved by Future Publishing.
Most people use the glasses normally, he said, much as they would a phone camera, only more convenient and more hands-free. He pointed to the indicator light and the anti-tampering measures that stop recording when it is covered.
The first defence is probably true and does not answer the question
Almost certainly most wearers are doing nothing objectionable. That is true of most technologies and it has never been the test for a device carried through public space.
The phone comparison is where the argument gives itself away. A raised phone is a visible act that the person opposite can see and respond to, and the entire selling point of the glasses is that recording no longer looks like anything.
Advertisement
More in the moment is the same property as harder to notice. The convenience and the problem are one feature.
The second defence has already failed in public
The recording light is the mechanism Meta has staked its answer on, and it has been closing holes in it all year. A software update stopped a loophole where a wearer could start recording, wait, then cover the light, and it bricked cameras on units where the light had been drilled out.
That enforcement was real and it was not small. Meta described the action as covering fewer than one in a thousand glasses ever sold, which on seven million pairs in a year is a great many devices.
The Information reported this week that Meta is preparing a camera-free version of the glasses, codenamed Luna, with six microphones and no camera at all. TNW covered the report, which points to an unveiling at Connect on 23 September and shipments in October.
Companies do not remove the defining feature of a product to placate a small number of bad actors. They remove it when the category has a perception problem they cannot moderate their way out of.
Bosworth said at the end of the AMA that there is more to say at Connect. That is five days after he said the discourse had been captured by a fringe.
What Luna would actually change
Taking the camera out addresses the bystander problem directly, and that is a real answer rather than a cosmetic one. It also removes the thing most people buy the glasses for.
Advertisement
Six microphones is not nothing, though. The visual privacy question would be solved and replaced by an audio one, and there is no equivalent of the recording light for a microphone.
Nobody has established a convention for signalling that a face-worn device is listening. Luna would ship into that gap.
Norway is weighing restrictions on camera-equipped wearables. Hamburg’s data protection commissioner has suggested the glasses may already fall foul of German rules on concealed recording equipment.
The moderation record is mixed by its own reporter’s account
Bosworth said harassing content will be removed and accounts taken down where the behaviour is systematic. Business Insider, which examined how the policy was working over the summer, found the moderation uneven.
The targeting has also been narrow. Videos of men harassing women have drawn action, while prank clips tormenting retail workers have been reported as a growing problem.
If the market leader ships a camera-free model this autumn, that becomes the reference point for everyone still deciding. The bad actors framing looks weaker every week the roadmap moves the other way.
What to watch
Watch Connect on 23 September. If Luna appears without a camera, the product has conceded what the AMA did not.
Watch what Meta says about the microphones. A camera-free device that listens continuously needs its own indicator, and the company has not proposed one.
Embattled surveillance technology company Flock Safety unveiled a “generous” severance package for voluntary employee departures on Friday, according to a report in Wired.
Flock reportedly expects a significant portion of its 1,500-person workforce to express interest in the buyouts, and said it will grant them to a majority of those who are interested. The company’s internal announcement described these packages as the “most generous” it has ever offered.
By letting employees depart voluntarily, Flock can say goodbye to team members demoralized by the ongoing backlash over the company’s license plate recognition technology. Wired also reports that without buyouts, the company would “almost certainly” need to lay off some staff.
TechCrunch has reached out to Flock for comment. The startup’s CEO Garrett Langley recently told the All-In podcast that the “biggest damage” caused by the backlash has been to “internal morale.”
The big picture: Researchers in Hong Kong have developed a technique that uses injected radio signals to extract audio and other information from headphones, phones and smart-home devices. Called InjectEave, the method targets analog components that can leak signals too weak to capture through conventional electromagnetic eavesdropping. In testing, the researchers recovered understandable headphone audio from up to 30 meters away, including through walls.
The research comes from the Hong Kong University of Science and Technology in Guangzhou and the Hong Kong Polytechnic University. The team presented its paper, “Injected and Leaked: Actively Inducing Side-Channel Leakage Using Electromagnetic Injection and Hardware Nonlinearity,” at USENIX Security 2026.
Traditional electromagnetic side-channel attacks rely on passively collecting radiation emitted by electronics. That’s often difficult with audio, since low-frequency signals produce weak emissions that get lost easily in background noise.
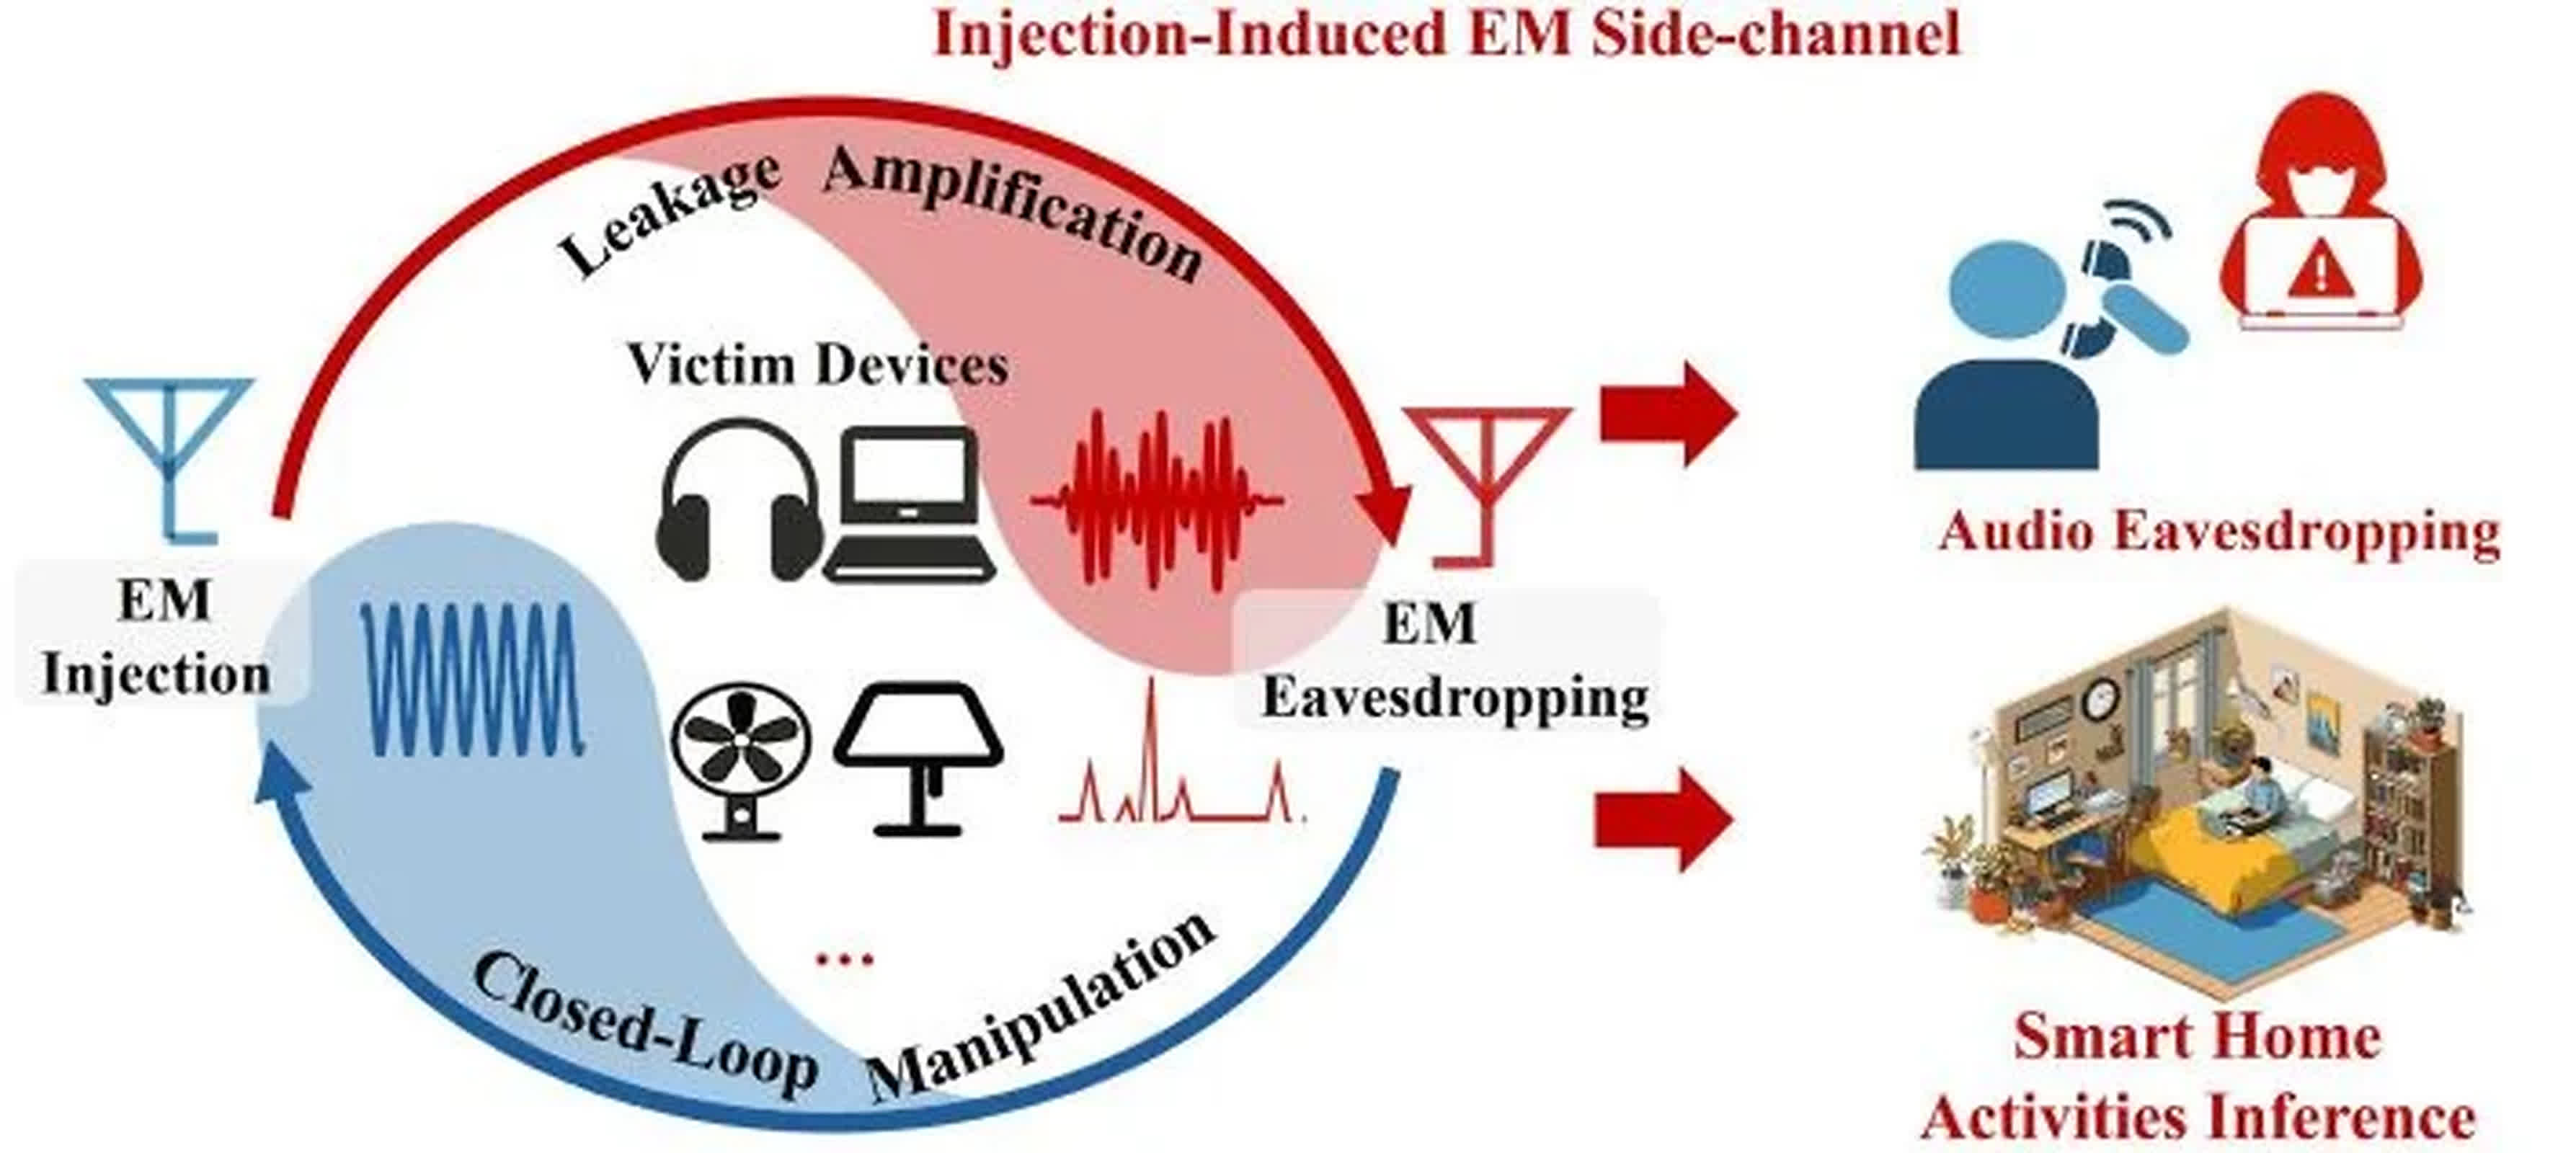
InjectEave takes a different route. An attacker transmits an electromagnetic signal toward a device at a frequency between 0 MHz and 9 MHz. The researchers did not disclose the precise settings needed for the attack.
Advertisement
The injected signal interacts with nonlinear parts inside the device, including amplifiers, analog-to-digital converters, power converters and switching MOSFETs. Those components can mix the injected RF signal with audio or other low-frequency activity. The device then emits a modified signal that nearby radio equipment can pick up and analyze.
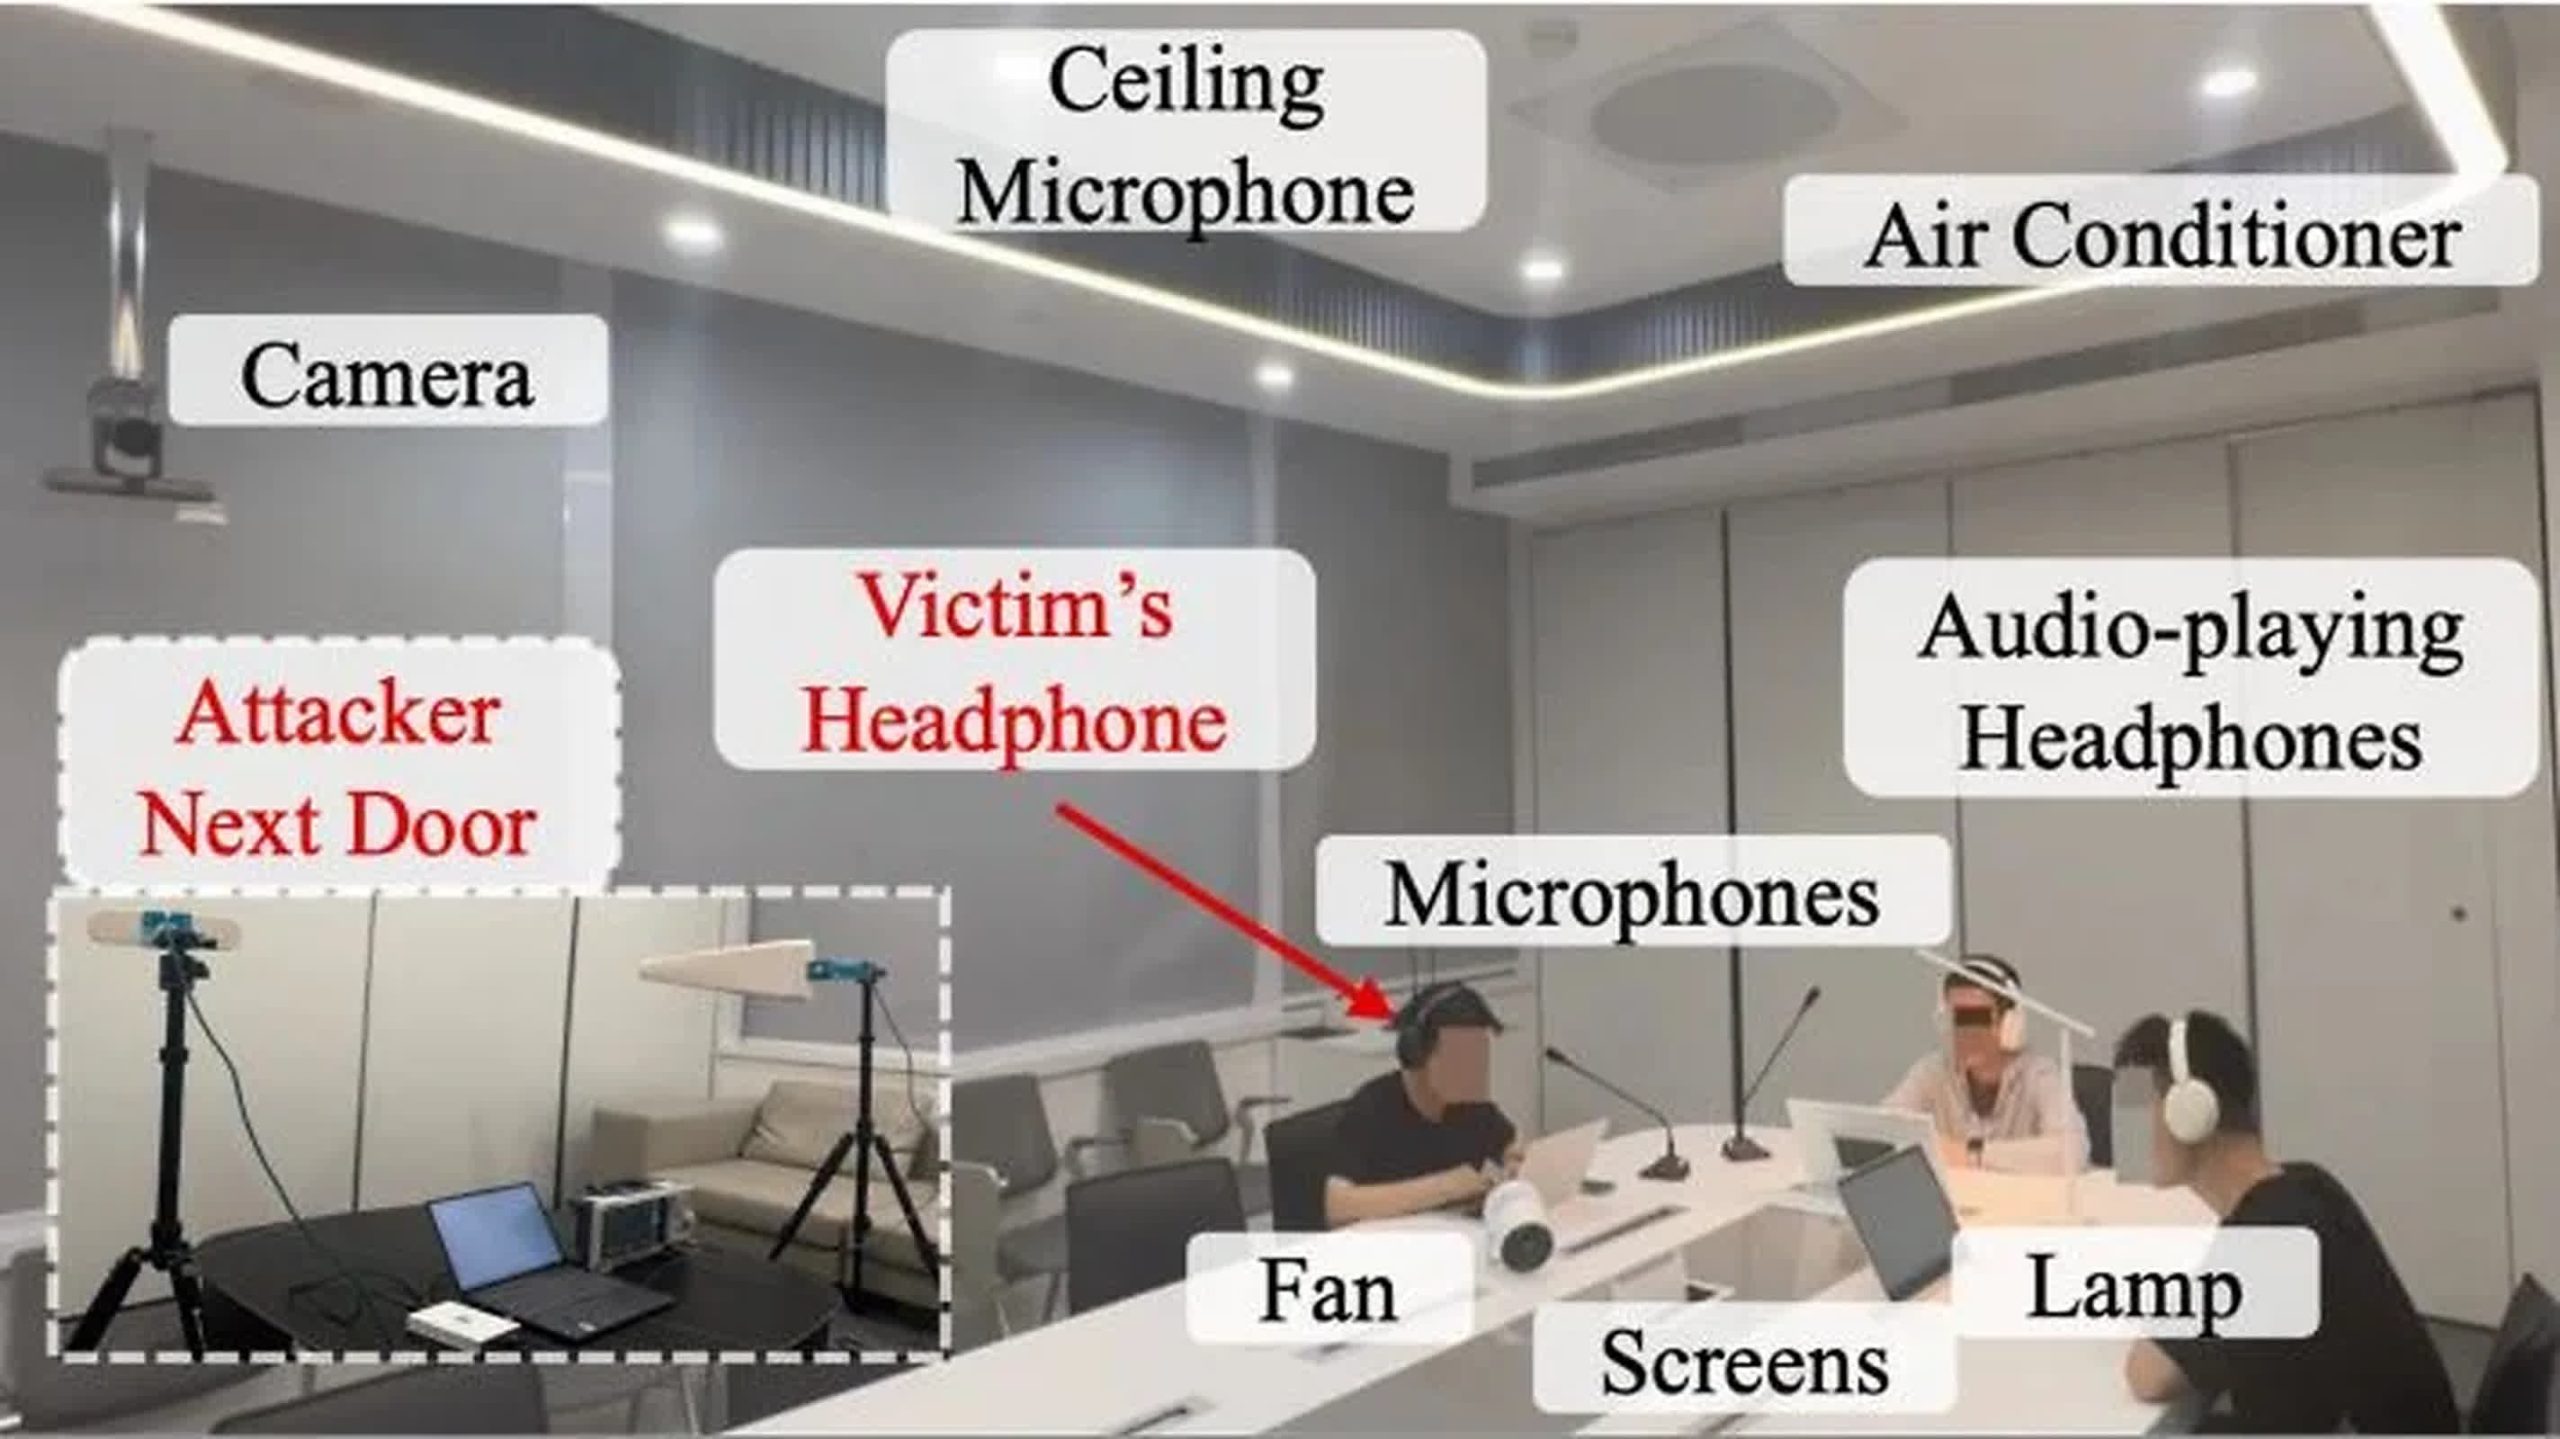
The researchers used a USRP B210 software-defined radio, antennas, a Siglent SSA3075X Plus spectrum analyzer and a laptop. They also used an RF power amplifier in some tests to increase the range.
The team tested 11 commercial products. They included Sony ZX110AP wired headphones, Apple earbuds, UGreen MAX2 headphones, Philips TAH2020 headphones, HP H231R headphones and a Flyingvoice P23GW VoIP phone. The researchers also tested smart fans from Oidire and Xiaomi, as well as lamps from Jingzao and Xiaomi.
According to the paper, most tests worked at distances greater than two meters, including through walls. Device-specific ranges generally ran from one to six meters. With an RF amplifier, the researchers recovered intelligible headphone audio from up to 30 meters.
Advertisement
“Our new project, InjectEave, shows that RF signals can induce information leakage from everyday headphones, allowing an attacker to recover headphone audio from up to 30 meters away, including through walls,” Yan Long, an assistant professor at HKUST in Guangzhou, said in an email to The Register.
Long said the researchers confirmed the issue in devices made by Sony, HP and Philips, among others.
The team also tested scenarios involving equipment hidden in a suitcase, behind a hotel-room wall or inside office furniture. The experiments suggest the attack could be carried out outside a lab, although it still requires nearby radio equipment and knowledge of how a given device responds to the injected signal.
Headphones and phones are the most obvious targets because they may carry private conversations. But the technique could also reveal activity in a home or office. With smart lamps and fans, the team said it could capture control signals and power-use patterns that may indicate when devices are being used.
Advertisement
The researchers said conventional digital protections would not stop InjectEave because the leakage occurs in the analog hardware path, rather than in encrypted data or software.
“InjectEave is immune to digital defenses such as encryption, masking, and randomization, because the leakage comes from the analog path,” the researchers wrote.
They said shielding, filtering and twisted-pair wiring can reduce the amount of RF energy that reaches vulnerable components. Those measures may make the attack harder to carry out, but the researchers said they do not guarantee protection.









































You must be logged in to post a comment Login