
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Tech
OpenAI’s AI agents accidentally uploaded user-provided images to third-party sites

OpenAI has confirmed it’s aware of a new security incident in which its AI agents uploaded user-provided images to third-party image-hosting services.
OpenAI says most users were not affected, as it could only identify 53 incidents where agents accidentally uploaded images to the internet.
The disclosure comes from OpenAI’s broader investigation into misaligned agent behavior following the Hugging Face security incident.
“As part of our ongoing investigation, we have identified cases where agents in our research environment transmitted training and evaluation data while using third-party services,” OpenAI noted in a blog post.
“This is not an appropriate use of this data, and these cases occurred before we implemented the safeguards described in our technical report.”
OpenAI says the vast majority of the affected training and evaluation data was not derived from users, but it did find 53 cases involving user-provided images.
“While the vast majority of the impacted training and evaluation data is not user-derived; we have identified 53 instances to date where user-provided images were posted to image-hosting sites as links that weren’t publicly listed,” OpenAI explained.
“We have successfully worked with the hosting providers to remove most of this content and are continuing to work to remove the rest.”
OpenAI says data excluded from training by users or administrators was not involved
Some OpenAI training data can contain content from users who have allowed their interactions to be used for training, but the company says users who opted out were not affected.
“Any data which is not eligible for training, as controlled by users or enterprise admins, is not included,” OpenAI said. “For explicitness, data from enterprise or business accounts and API usage is excluded unless an admin has enabled it.”
OpenAI also says it takes additional steps before eligible user data is added to training datasets.
“Before including eligible data, we take steps to protect privacy by disassociating it from account information and using a version of the OpenAI Privacy Filter to redact personal details such as names, contact information, and account numbers.”
Following the incident, OpenAI says it strengthened its training and evaluation systems to make it harder for models to leak data through external services.
“As part of our response to our ongoing investigation, we have improved our training and evaluation processes, including building safety cases, securing and red-teaming our systems to prevent the model from exfiltrating data, and implemented additional monitoring,” the company noted.
The company is continuing to review older agent activity month by month, starting from the Hugging Face incident, so additional cases could still emerge.


Continue Reading
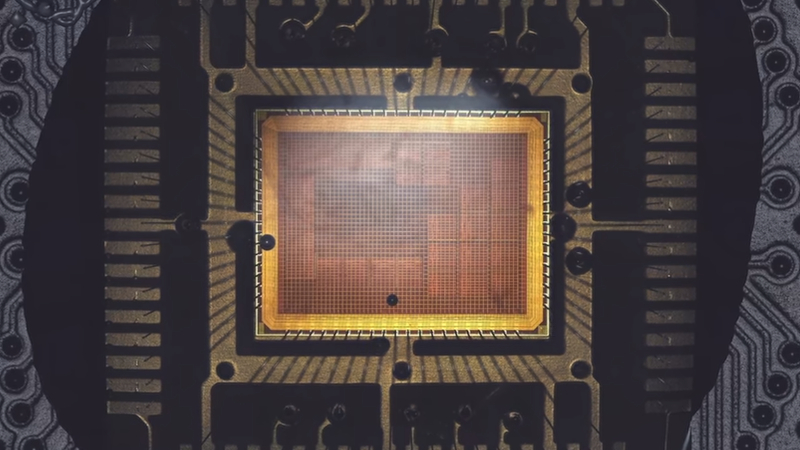
For a while now we’ve followed the slow progression of affordable integrated circuit fabrication, and through the likes of Tiny Tapeout we’ve seen impressive strides made. But they’re not the only player in the space, and [Breaking Taps] has a video showing their microprocessor built using wafer.space.
The microprocessor itself is a little unusual, being a transport triggered architecture design with two busses. The whole thing might better be described as a system-on-chip than a microprocessor, as like a microcontroller it contains both memory and peripherals. He’s used Spade to design the thing, and we get an in-depth look at all the steps involved between design and fabrication. It’s a level or two more difficult than passing the DRC standards for your PCB fabricator. The result is a chip carrier with the chip itself visible under clear epoxy. It’s using an old fabrication technology so the silicon is surprisingly big, but unlike Tiny Tapeout’s cell based fabrication the whole chip is the one circuit. Mounting it on a PCB and using a breadboard, he’s able to demonstrate it running simple programs.
It’s clear that having your own IC fabricated is not for everyone, as even though wafer.space has performed minor miracles it’s still a service for people with a few dollars in hand. But look at it this way, we’re still near the start of this particular curve, and we expect that further affordability breakthroughs will follow.
Parents have spent years trying to keep their kids off social media, so some kids headed to the one place no adult would think to look for them: NPR.
On this week’s “This American Life,” host Ira Glass tells the story of the team behind NPR’s podcast “Wild Card,” who noticed a flood of baffling comments under their Spotify episodes last fall. A producer assumed the bizarre abbreviations and indecipherable emojis were bot traffic and shared screenshots in NPR’s Slack. They then reported the posts to Spotify.
But Hannah Chin, an audio producer and Gen Z colleague, took one look at the screenshots and recognized, almost immediately by Glass’s telling, that these weren’t bots. They were likely middle schoolers who were too young for social media, running a group chat in the comments of the podcast. (Perhaps someone at NPR should have grokked this sooner: it spotted kids doing the same thing on TED Radio Hour show last year.)
As for why NPR in particular, when Glass tracked down one of the kids to ask, he was given the kind of unvarnished answer that a middle schooler would give: “Um, I think we just, like, looked for podcasts that didn’t have many comments.”
“I tell you, buddy,” responded Glass, who has hosted “This American Life” for three decades, “I do a public radio show, and that hurts a little to hear.”
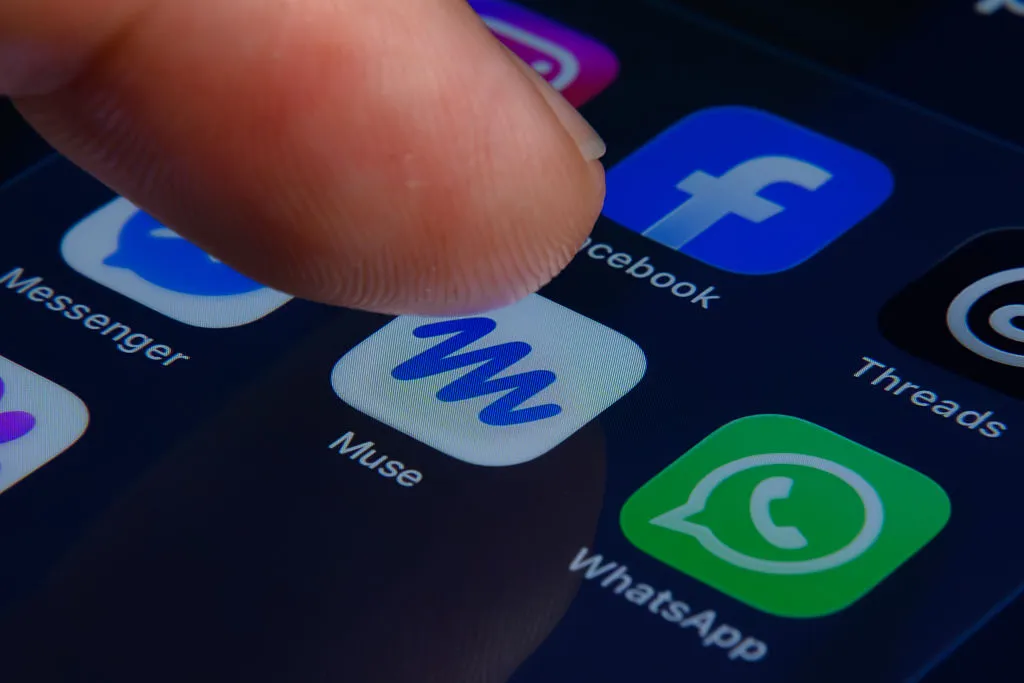
After announcing a host of new features for Meta’s Muse AI app at its Connect 2026 developer conference this week, the company is opening up requests for early access. Meta shared on Friday that you can now ask Muse to put you on the list to try out its latest capabilities before anyone else.
Meta posted a link to a prompt on X that, when shared with Muse, will log that you’re interested in joining Meta’s early access program.
(If you don’t want to click through, you can just copy and paste the prompt: “Can you let the Muse team know I want to be part of the Muse early access program?”)
While typically companies offer pilot tests or betas with select users, they often A/B test with a randomized group to gain feedback and measure results. In this case, however, Meta is looking for AI enthusiasts to try its features first. That tactic could help it stay ahead of the competition, given that this crowd tends to use multiple AI apps and agents and has a good understanding of the market.
As to what the new features will be? Meta teased many of those at Connect, including the launch of a digital avatar for Muse that you’ll be able to video chat with, tons more shopping partnerships and connectors, and an expansion of the Muse Mac app, which will soon be able to use your computer to complete various tasks.
The company also said that Muse would be coming to Meta’s lineup of AI glasses, so users can interact with the agent just by speaking a wake word, then issuing a command.

After images that users uploaded to OpenAI models were included in training data, AI agents operating in the company’s research environment posted them on public image hosting sites.
Fifty-three “user-provided images” were “posted to image-hosting sites as links that weren’t publicly listed,” the company said for the first time. The images could still be discovered even if the links were not publicly listed.
“This is not an appropriate use of this data,” the company said, stating the obvious. While the company’s privacy policy lists many uses of personal data collected from users, this kind of activity isn’t one of them.
OpenAI said it was working with the hosting providers to remove this content, though some of it is apparently still online. OpenAI said it could not notify the affected users because “our technical approach and privacy policy” prevent it from “reassociating” the images with the original providers, but declined to say how the lab determined whether the images were provided by users.
The news came in a post collecting public statements from the lab’s ongoing review of incidents in which its models escaped the company’s scrutiny, accessed the open internet, and misbehaved in various ways. OpenAI said it would continue disclosing anonymized accounts of incidents like these, and said it had contacted dozens of victims, including governments, universities, public agencies, to notify them of the agents’ activities.
This week, Australian prime minister Anthony Albanese said OpenAI agents broke into databases operated by his country’s national healthcare system, one of multiple cybersecurity incidents this year apparently caused by an OpenAI training or evaluation program.
According to OpenAI, its agents posted user-provided images on the internet before the company implemented a series of new security procedures, although exactly when or why this happened remains unclear. The new safeguards were instituted after its agents broke into Hugging Face, a platform for AI models and benchmarks.
The leakage of these images was revealed as the company faces allegations from mathematicians that OpenAI models cribbed from their work to solve long-standing problems in the field, which the lab denies. Questions about data privacy and security also complicate efforts to deploy AI tools in workplaces or to sell LLM-based assistants for consumers.
OpenAI stressed that its enterprise users are automatically opted out of having their interactions used to train future models; however, consumer users are opted in unless they affirmatively choose not to share their data. Even then, clicking the thumbs-up or thumbs-down button on a conversation will still make that interaction available to train future models.
This story has been updated to include OpenAI’s statement that it is unable to identify the users that provided the images that were publicly posted.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
Some compliance is mostly for show, and that’s being charitable. You go through it for the website badge, not to find weak spots in your organization. SOC 2 is not like that.
There’s a reason your customers’ procurement teams demand it. They want to know whether they can trust you with their data, and SOC 2 compliance is the accepted way to demonstrate that. It might not be the reason a deal closes, but that deal wouldn’t have closed without it.
We’ve lived “move fast and break things” for so long that we assume disruption must mean breaking stuff by definition. Only when it comes to AI agents, it’s not so easy because of the way they use the existing infrastructure.
Consider an access review row. A production database, 10:03 am, 50 queries under the name of a senior engineer. You were right to approve it; everything conforms accurately to the control. Only that engineer was getting coffee at the time, while their agent was pushing updates to production.
SOC 2’s technology-neutral criteria can cover AI agents, but they do not explicitly require organizations or auditors to treat agents as a distinct identity class. That discretion allows AI agents to add risk to an environment without failing a single control.
If SOC 2 lets you get away with this, the framework either needs to change or risk becoming outdated.
What’s Happening
During an audit, you’re tested on two things: whether the control meets a compliance criterion, and whether it operated throughout the review period. But what about testing whether the design is still relevant?
Sometimes, when there’s a shift, a test gets harder. But often, it just gets emptier, because the activity happens elsewhere, which brings us to the Trust Services Criteria in SOC 2. It’s not that they’re wrong, but four of the common assumptions no longer hold, and as a result, three controls are hollowing out.
The assumptions are:
- Someone approves an account before it’s spawned.
- Every account has a known owner.
- The name in the log pinpoints the actor.
- What an account can do tells you what it’s expected to do.
Four assumptions that no longer hold (CC6.1–CC6.3)
Every access criterion is based on assumptions about what it controls. And as long as the actors were human, those assumptions were safe enough that nobody needed to write them. With agents, this is no longer the case.
1. Someone approves an account before it’s spawned.
SOC 2 requires you to register and approve a user before granting login capabilities. For humans, that means someone asking for a login, with someone else approving and logging it. Agents, on the other hand, are akin to a side effect of an overarching action.
It can be a developer clicking “Allow” on an OAuth screen, an API key that’s pasted into a config file, or an MCP server added to a JSON file. No one was asked to approve the creation of an agent; it just happened.
2. Every account has a known owner.
In access review procedures, a named human confirms that the reviewed account should still have access. For agents, it’s common not to have a named owner. You need to piece that together after the fact, from circumstantial evidence and conjecture, by examining the agent’s artifacts associated with humans, such as keys and repos.
At scale, agent ownership is an educated guess rather than a deterministic record. SOC 2 doesn’t account for this: a guessed owner and a recorded owner look the same in a review spreadsheet.
3. The name in the log pinpoints the actor.
This is the expensive one, which we already mentioned in our 10:03 am example. Often, agents work with borrowed credentials: a logged-in session, a dev token, or a service account. That’s the person who will appear in your logs and in your access review. This will pass the review, while absolutely ignoring the security differences between people and agents.
On the one hand, the access review will be completely accurate. On the other hand, it won’t tell you what you actually need to know. A recent study with Cloud Security Alliance found more than two-thirds of organizations cannot clearly distinguish AI agent actions from human ones.
4. What an account can do tells you what it’s expected to do.
Least privilege operates under the assumption that an account has a permanent job, and the list of things it can do tells us what it’s for. And for people, that’s usually correct. Unless your CEO wants to be an admin everywhere, access levels are tailored to the job.
For agents, the access limits the blast radius, but it doesn’t tell you what the agent is expected to do at any given moment. That depends on the instructions received, the context absorbed, and the decisions the agent makes. So, checking permissions gives you the widest possible view of what can happen without providing context for the agent’s actions.
Your SOC 2 report says the controls worked, but it never says what they missed. Agents run on borrowed credentials, with no owner and no off switch.
Token Security finds every agent, assigns an identity, and remediates its access to the job it was made to do.
Three controls that pass without covering anything
Here’s how the assumptions we’ve mentioned reduce the effectiveness of three SOC 2 controls.
Nothing ever says an agent should stop (CC6.3)
Every SOC 2 audit tests offboarding, and for human employees, companies have gotten very good at it. HR systems, IdP, and SaaS systems work in tandem when the HR department flags a person for offboarding, thereby exercising its unquestionable authority. Even the evidence writes itself.
There aren’t any HR systems for agents. There’s no centralized, agreed-upon body that’s in the position to say a specific agent should stop. It’s not a broken control, but one that just doesn’t encompass agents and the identities they use.
What makes it worse is that agents are mostly tied to humans, so when a person leaves, the agents set up in their name might keep running using OAuth grants or API keys, unless this scenario is accounted for.
Vendor review starts at purchase (CC9.2)
SOC 2 manages processes relating to vendor relationships. You contract, assess, collect a report, and review it annually; it works well for vendors who arrive on a purchase order. An MCP server is a vendor in every way that matters: it receives your data, acts on your behalf, and runs code nobody in the company reads.
Instead of a purchase order and a data agreement, it arrives in a config file. Often, there’s no company at the other end at all.
About three in ten names in our registry cannot be matched to an existing company. That’s a naming-space figure, not a specific environment, but it points to a fundamental compliance issue for many MCPs: you can’t receive a SOC 2 report from an unnamed vendor.
The same problem appears for AI agents. When we find them on employee machines, only some are safe to block; the rest are held back because the program’s name can collide with something the customer built. Identifying an agent is harder than identifying a person. If you’re ready to explore the AI Agent Security controls, book a demo with Token Security to see what’s hiding in your environment.
Segregation of duties between two instances of the same policy (CC8.1)
When implementing change management, changes should be authorized, tested, approved, and implemented. In most implementations, the author and the approver must be different people due to segregation of duties.
When an agent makes a change and a second agent reviews it, the separation is only nominal, even though two identities were involved.
Meanwhile, the authorization moved beyond the scope of the audit. The decision about the change can happen in a prompt, in a tool that appears nowhere in the system description. The only evidence is a pull request.
The strongest argument against all of this
It’s worth noting that nothing in the Trust Services Criteria says “human”. CC6.2 uses “internal and external users,” whereas CC6.1 uses “protected information assets.” The criteria were written to avoid naming technologies and to describe results rather than methods. So there’s no reason not to cover agents.
You treat machine accounts as users, list agents in the system descriptions, and test them properly. It’s a thing that happens in the real world.
That said, given the current level of disruption, the ambiguity might not be enough. With no specific mentions of agents in the criteria, what gets covered is agreed between you and your auditor.
Both of you have a reason to prefer a scope that’s easy to evidence. As long as you can leave agents out without recording a single exception, some people will do it.
What a clean report has never meant
A clean report means your controls behaved the way you said they would, not that the description was complete. The gap used to be small enough to ignore, but it is no longer.
It is now entirely possible to hold an unqualified Type 2 report and be unable to answer, on the day it is issued, four questions about your own production environment.
|
Question
|
The control that covers it
|
Why it’ll pass
|
|
What is running in there?
|
User registration and authorization (CC6.2)
|
The agent was never registered, so nothing looked missing
|
|
Who authorized it?
|
Change authorization (CC8.1)
|
The decision happened in a prompt, upstream of the evidence
|
|
Whose credentials are they carrying?
|
Access review (CC6.1)
|
A real employee’s credentials, with an approved role
|
|
Who could switch it off?
|
Access removal (CC6.3)
|
Offboarding ran correctly and never flagged agents
|
SOC 2 is not wrong. It is accurate about a world that moved. So treat machine accounts as users, and go further than the report asks. The permission list can tell you what an agent can reach; it does not tell you what an agent is there to do.
Closing this gap is what we mean by intent-based security: you establish what each agent is meant to do, then you make its access match. Identity is the layer where that control actually holds because it spans every system the agent touches.
The report will not change, but these controls are there for a reason, and attackers don’t care about checklists.
Every environment has an access review line that looks approved but says nothing. Token Security shows you the agent behind it: who owns it, whose credentials it uses, and whether what it can reach still aligns with what it’s there to do.
Book a demo and we’ll walk your environment together.
Sponsored and written by Token Security.
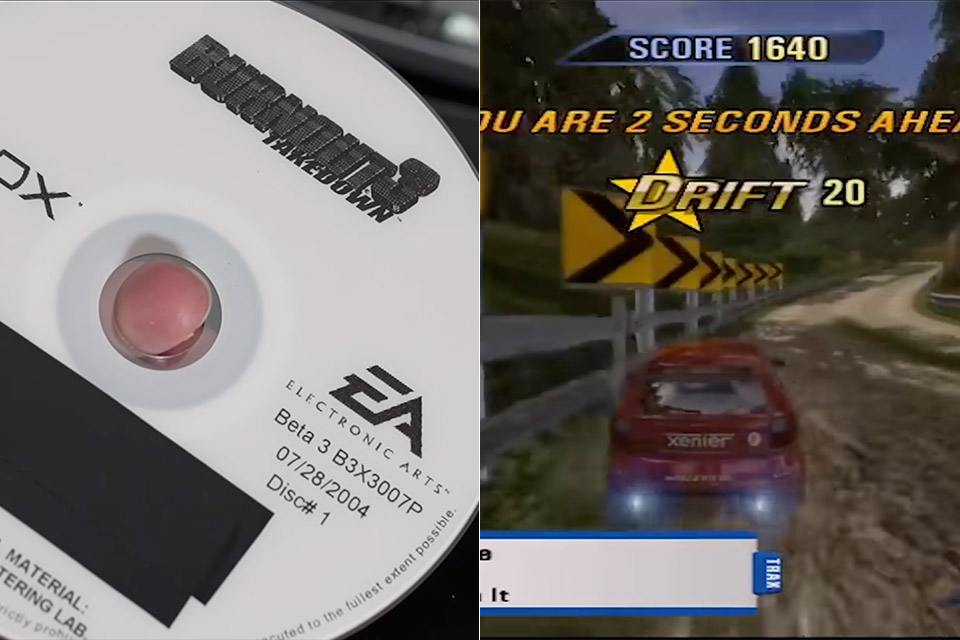
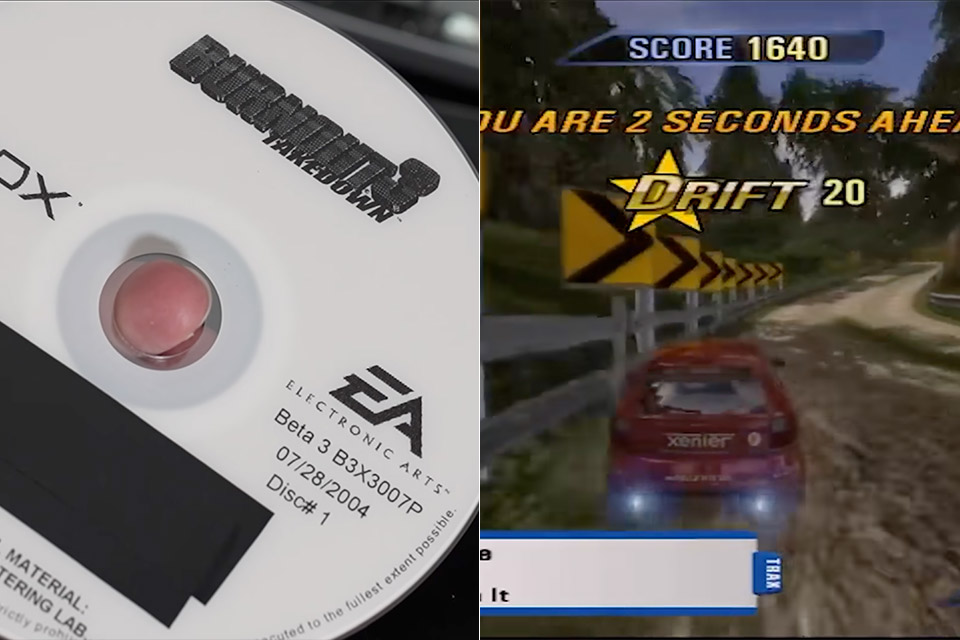
Game preservationist MattKC spotted an undocumented original Xbox copy of Burnout 3 on eBay this summer and paid a steep price to have it shipped from Australia. Printed on the face is July 28, 2004, the words Beta 3, and a warning that reads Confidential material: return to mastering lab. A name on the label, blurred in the video for privacy, belonged to a product manager at EA Australia, which fits the moment Electronic Arts bought Criterion and took the series in-house. How the disc left that office and landed on a public auction remains a guess.
Retail Xbox games normally put their data under a DVD-Video wrapper to prevent a PC drive from accessing them after a brief warning, but this DVD-R disk was an exception. It was a purple-tinted consumer DVD-R that had been used for a development kit. So, when connected to a normal drive and ran through DiscImageCreator, it produced a clean 3.7 GB image in just a few minutes. XDVDMulleter then unpacked the data, and after a bit of a tussle, the build was booted up by the emulator Xemu. There was no program database file on the disk, which would have been extremely unlikely for a late master.
Sale

Lenovo Legion Go S – 2025 – Mobile Gaming Console – AMD Radeon graphics – 8″ PureSight IPS Display…
- ALL GAMES, ALL PLACES, ALL YOURS – Get ready to game on the 8″ 120Hz Lenovo PureSight display and launch any title using Legion Space. The AMD Ryzen…
- SEE EVERY DETAIL – Make every scene pop with 500 nits of stunning brightness and 100% sRGB color accuracy. And with 10-point touch support, your…
- PLAY YOUR WAY – Play hundreds of high-quality PC games with your complimentary 3 months of PC Game Pass and EA Play. With new games added all the…
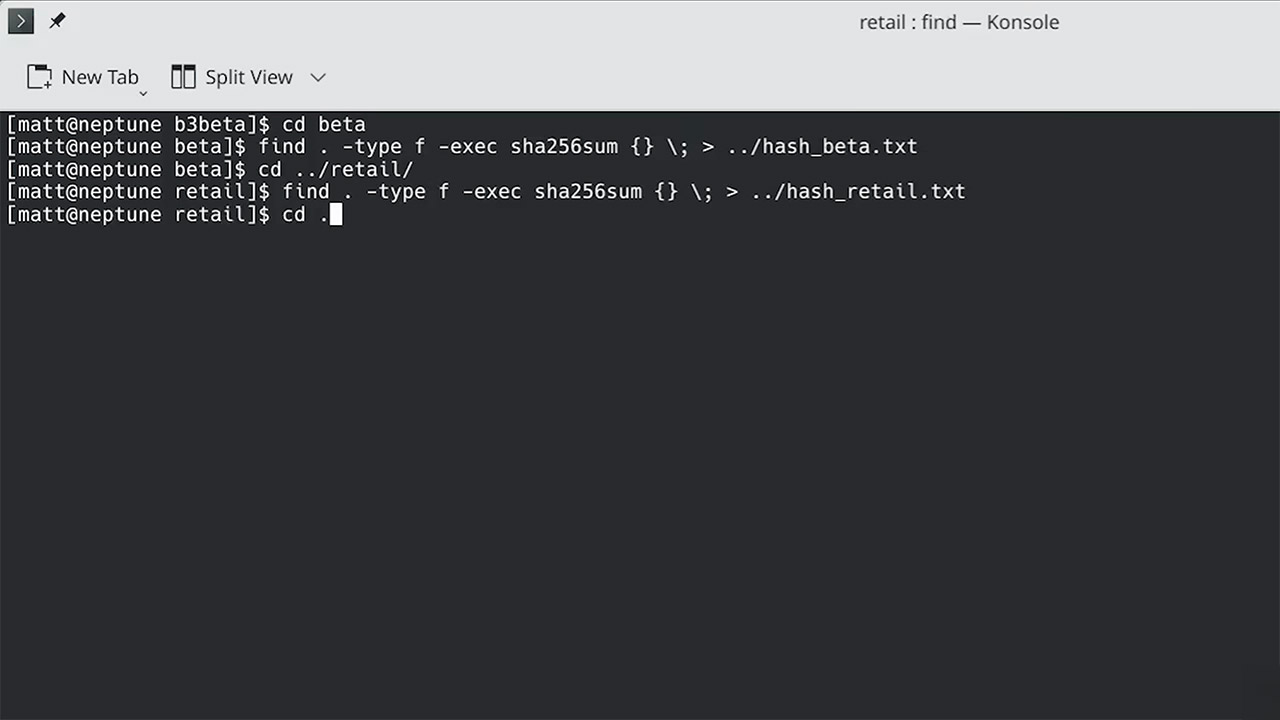
Running a hash check on all the files against a PAL retail dump revealed eight changes, one of which was the main executable. Signing accounts for a portion of the difference. Criterion had created this particular copy as a debug binary for a development console rather than a retail-signed XBE for a store disk. The English in-game play appears almost identical to the finalized game. However, changing the language triggered the appearance of a few strings that had been written to run too long for the UI. The retail version of the game just condensed those sentences. References to a generic server for online play were replaced with an EA server in later files. You also lose Xbox Live and Insignia hosting Burnout 3, as those strings would never appear in a live session anyhow.
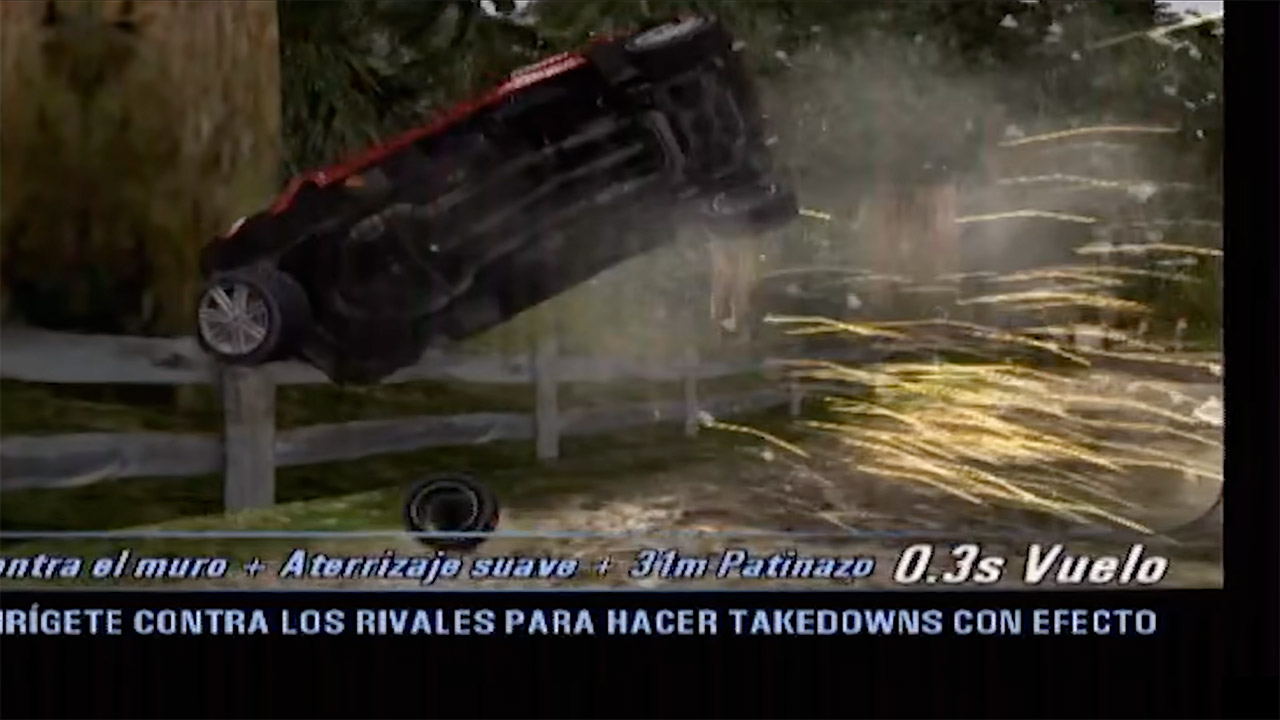
Crash mode contains the most significant code modification discovered by MattKC. After getting some considerable air in a wreck, the beta simply outputs out the height using a standard sprintf function and one decimal point. A few European languages, however, use a comma to mark that point, so the retail executable includes a bespoke formatter to ensure that local punctuation is respected. That’s about the extent of the differences; no leftover cars, no cut tracks, and no debug menu sticking about in the menus. Criterion had evidently finished the US executable about an hour before this disk was released, and the European one approximately 6 days later, which explains why the remaining work appears to be copy fitting rather than any meaningful new features.
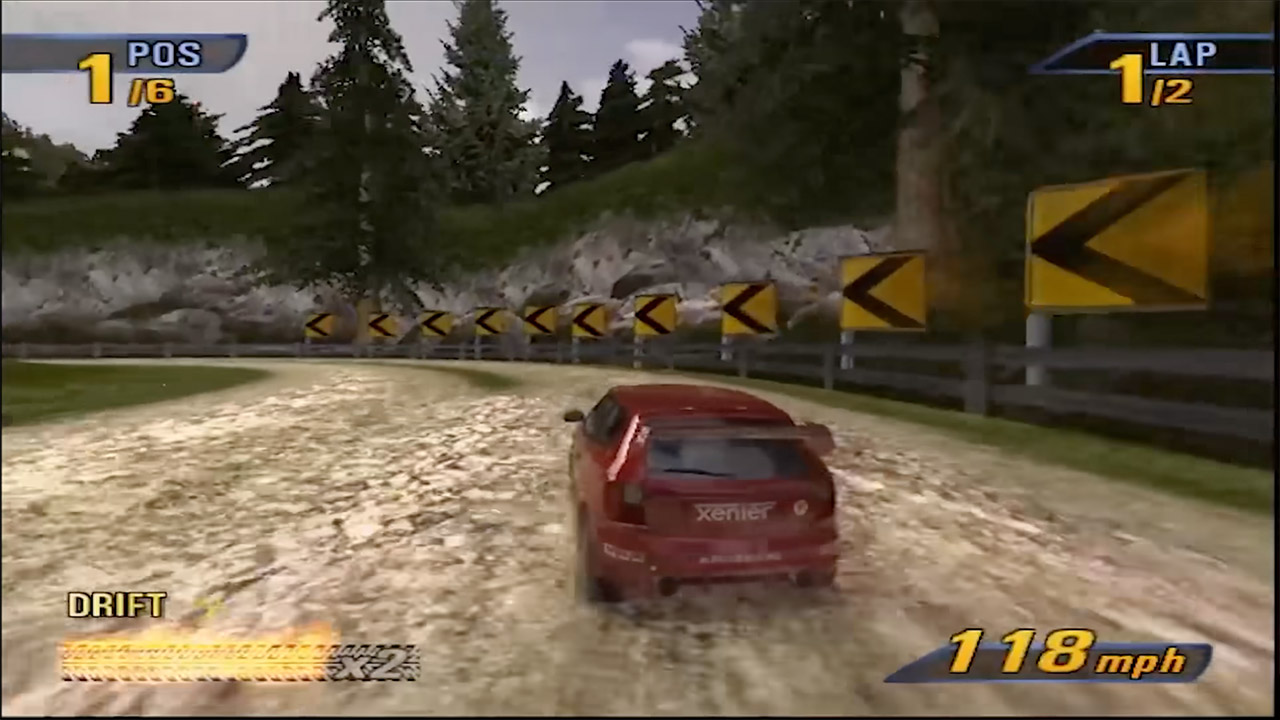
MattKC thought this buy was a poor source of hidden material but an excellent shelf piece. He did, however, submit the ISO to the Internet Archive as Burnout 3: Takedown, Xbox Beta 3, 07/28/2004, so that anyone can look without having to search for another one of those burned DVD-Rs. For a game so close to being ready for release, the archive is the real treasure. You now have a late PAL localization pass out in the open, dated and hashed, which is more than most corporate disks receive even after 22 years.
[Source]
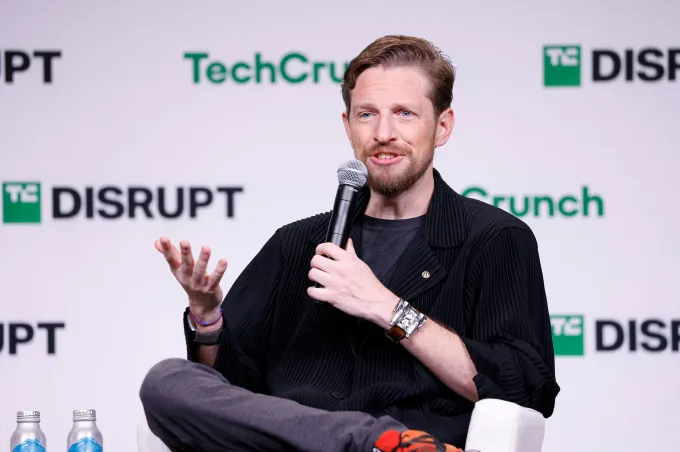
Automattic CEO Matt Mullenweg has rebuilt the company’s board just weeks after its previous directors tried, and failed, to oust him. The board, which was announced to staff Friday, is an eclectic group that includes a best-selling science-fiction author and two co-founders of the now-defunct social app IRL, TechCrunch has learned, and Mullenweg has confirmed.
The new board is the latest twist in an internal governance fight at Automattic, the parent company of WordPress.com, Tumblr, WooCommerce, and others. Earlier this month, the previous board voted to place Mullenweg on leave in an attempt to remove him from the board, only to have the CEO retake control just 33 hours later and remove or accept the resignations of the directors who were involved.
This week, Mullenweg posted about a board meeting but didn’t share who he was meeting with. Now he’s finally informing Automattic employees of the board changes via the company’s announcements channel in Slack.
Sources told TechCrunch the new Automattic board includes:
- American writer Hugh Howey, author of the “Silo” book series. (Mullenweg and Howey both hiked along the Camino de Santiago in Spain back in 2018.)
- “Breakup Bootcamp” author Amy Chan (who recently reposted Mullenweg’s tweet about the company’s AI site builder, Spacefast).
- IRL co-founder Henry Khachatryan, who Mullenweg described as a “founder and builder,” a longtime collaborator with the late technology writer Om Malik, and the website builder of journalist Nick Bilton.
- And Krutal Desai, who co-founded the social app IRL with Khachatryan.
We should note that IRL shut down after investigations revealed that nearly all of its user base was made up of bots. The co-founders, who also included CEO Abraham Shafi, later sued SoftBank and other investors after SoftBank had sued for securities fraud.
New advisers have also joined Automattic, including former Whoop CTO Jaime Waydo, June co-founder Matt Van Horn, and KISSmetrics co-founder Hiten Shah.
In the announcement to staff, Mullenweg reportedly wrote that, “for purposes of Delaware law, I am the CEO, President, Treasurer, and Secretary,” adding that the attempted firing had also brought in “many amazing supporters.”
“We had the most interesting board meeting in a decade (since the Woo acquisition),” he said.
Reached for comment, Automattic said it hoped to have a comment for TechCrunch soon. After publication, Mullenweg confirmed the board additions and advisors, and shared the following statement: “We are living through times of unprecedented change, possibly a singularity. The next six months will determine the next 20 years of Automattic.”

Automattic’s original board had voted to put Mullenweg on paid leave, but he took back control of the company, letting go of those involved in what he described on X as a “coup attempt.”
To replace the board, Mullenweg leveraged his voting shares — he controls 84% of the vote, he said at TechCrunch Disrupt 2024. The period between his departure and return lasted exactly “33 hours and 20 minutes,” Automattic told TechCrunch previously.
Following the failed board vote, member Toni Schneider, a founding CEO of Automattic and now CEO of Bluesky, resigned from his board position. Mullenweg himself removed General Ann Dunwoody from the board, and board member Sue Decker also resigned. In addition, Mullenweg let go of Automattic CFO Mark Davies, who was slated to become interim CEO, and chief legal officer Andy Missan, TechCrunch confirmed with sources.
The board never publicly shared its reasons for trying to oust Mullenweg.
Of note, Mullenweg also replaced Automattic’s legal counsel after his return, a move that raises questions about whether the boardroom fight is tied to the company’s ongoing lawsuit with hosting provider WP Engine over trademark disputes and claims over WP Engine’s lack of contribution to the WordPress open source project. (WP Engine’s legal team had also accused Mullenweg this July of destroying evidence, court filings show.)
In an internal message shared after the ousting and return, Mullenweg had acknowledged the chaos it caused, saying:
Last week, several board members formed a special committee and voted to place me on a leave of absence. They did this without advance warning and without giving me a meaningful opportunity to understand or respond to their concerns before they acted. I was denied even a brief extension to consult with independent legal counsel.
I took the steps necessary to reverse that action. I am back and fully in charge of the company. I am again working alongside you to make our company a success.
I also want to share that we have retained Susman Godfrey LLP as our new litigation counsel. Susman Godfrey is one of the top trial firms in the country, and they will be protecting our company’s interests and defending us in our ongoing litigation.
I know this past week has been unsettling. I appreciate your patience and your continued focus on the work that matters. I will have more to share soon, but for now, know that Automattic’s mission and priorities remain unchanged.
Corrections and updates: After publication, TechCrunch updated to clarify that Waydo is the former Whoop CTO. We also added Mullenweg’s statement and confirmation.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
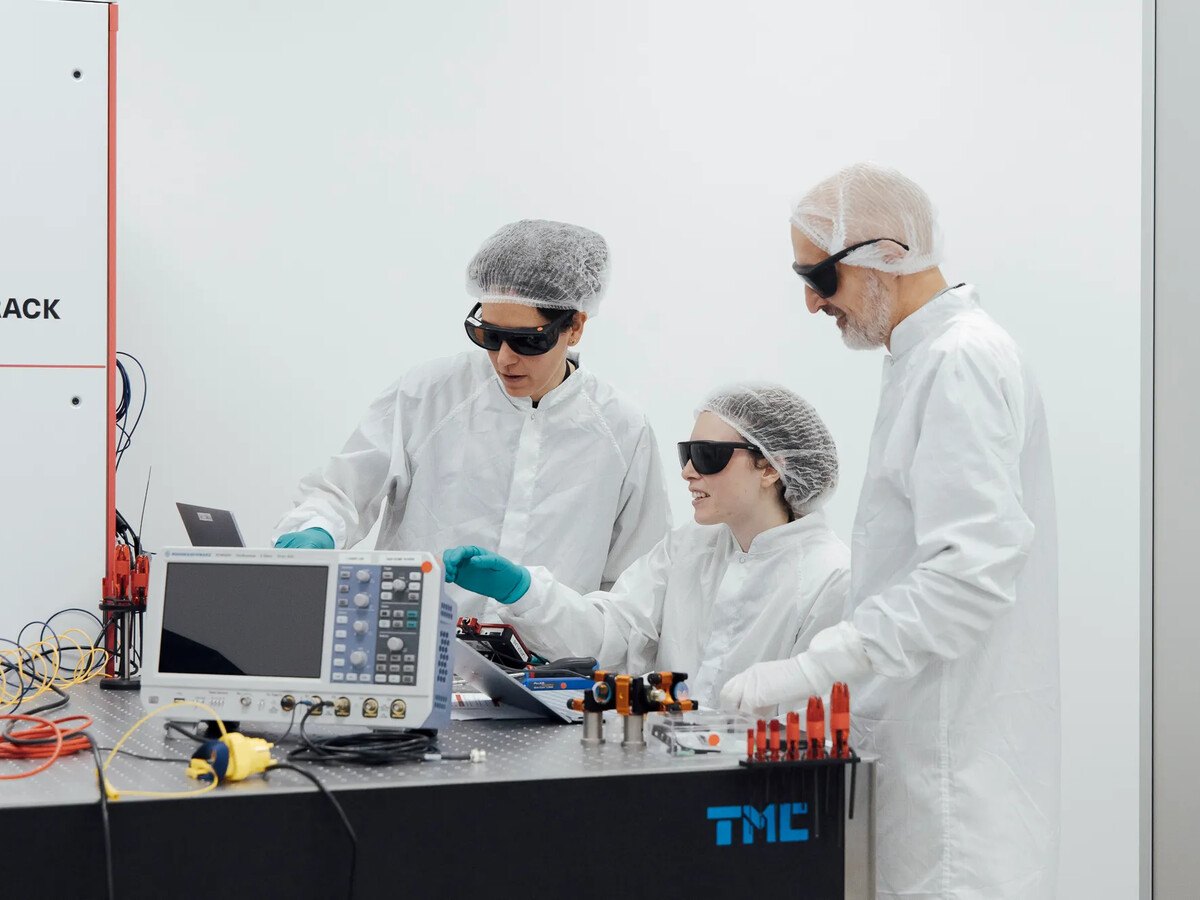

Pasqal’s technology is built on Nobel Prize-winning research by co-founder Prof Alain Aspect.
French quantum company Pasqal reported a 14pc growth in revenue in the first half of this year and more than €300m in cash reserves to fund its upcoming commercialisation goals.
Pasqal went public late last month after merging with the special purpose acquisiton company Bleichroeder in a transaction that valued the new entity at around $2bn. That transaction left about €313m in cash to support its plans as a public business. The company’s current market valuation sits at just more than $1.5bn.
The quantum company reported a nearly €60m operating loss for H1, which included more than €37m in share-based payments and on-time charges.
Founded in 2019 on Nobel Prize–winning research by co-founder Prof Alain Aspect, Pasqal builds and operates neutral-atom quantum computers, available both on-premises and through the cloud.
The company’s quantum systems are used across sectors by customers including Saudi Aramco, Crédit Agricole CIB and LG Electronics, and is supported by partnerships with Nvidia and IBM. Pasqal has additional offices in Saudi Arabia, Canada, the US and South Korea.
In its first financial report as a public company, Pasqal also reported a revenue of €3.9m in quantum processing unit-related services – up 34pc year-over-year, while booked and awarded business – such as grants, tax credit and multi-year customer contracts – sat at €70.4m.
The company received an European Innovation Council (EIC) Fund Award at the 2026 TechEU Equity Summit in Luxembourg earlier this week, a recognition which came after it became one of the first companies in the EIC Fund’s portfolio to go public.
“During the first half of 2026, we continued to deepen our engagement with our customers of choice across financial services, energy and advanced materials to solve high-value business problems and integrate quantum computing into real-world workflows,” said Dr Wasiq Bokhari, Pasqal’s CEO.
“At the same time, we continue to execute against our roadmap. Recent milestones, including the demonstration of more than 1,000 physical qubits, industry-leading progress in logical qubits, and the successful application of our systems to solve complex differential equations and simulate materials beyond the practical reach of classical computing, reinforce our confidence in the strength and differentiation of Pasqal’s neutral-atom approach.
“With a growing portfolio of customer engagements, a differentiated technology platform, a disciplined approach to capital allocation, and a strong balance sheet to support future growth, we remain focused on delivering practical quantum solutions that create value today while building the foundation for the next generation of quantum computing,” he said. Pasqal intends to also list itself on the European stock exchange Euronext by next year.
Don’t miss out on the knowledge you need to succeed. Sign up for the Daily Brief, Silicon Republic’s digest of need-to-know sci-tech news.
Your Mac can take a nap in between sessions.
macOS offers two main options when you’re done using your Mac or MacBook: sleep and shutdown. At a high level, these are self-explanatory, but you might wonder when to use each mode and what exactly is going on during both of them.
As with most computing matters, the right option to use depends on the circumstances. Using the “wrong” mode will almost never cause a problem, but it’s best to be as efficient as you can.
Understanding a full shutdown
Shutting down your Mac is like turning off any other computer. During the process, every app closes, the operating system is shut down and RAM is cleared. To ensure a proper shutdown on your MacBook, don’t close the lid until the screen is off. Apple’s guidance states that closing the lid during the shutdown process can cause it to start more slowly next time. Once it’s fully shut down, the system is not drawing any power. You must open the lid or press the power button to turn the machine back on.
When you do a normal shutdown by clicking Shut Down from the Apple menu at the top-left, a one-minute countdown runs to allow you to cancel the action if you change your mind. Also on this window is a Reopen windows when logging back in box; check this, and when you reboot, macOS will relaunch the same apps you had open before shutting down. If you’re sure you want to shut down, hold the Option key when you click Shut Down to bypass the countdown. This will try to shut down apps gracefully, but you won’t get a prompt asking you to save changes if an app’s automatic save has trouble.
If needed, you can also Restart from the Apple menu. Restarting is good when an app or the entire system is acting up, but that process doesn’t fully power off the machine’s components. Thus, if you need to completely cut power to troubleshoot accessories or similar, a full shutdown is better. This is unlike Windows, where the Fast Startup option means shutting down isn’t a full power cycle by default and restarting is more thorough.
On your MacBook, the Touch ID button at the top-right (or Power button on older models) will lock your computer if you press it quickly while the computer is on. Let it sit locked for a while on battery, and it will go to sleep. Pressing and holding it for several seconds will force a shutdown, which you should only do if the entire system is unresponsive. You’ll lose any unsaved work.
Putting your Mac to sleep
The easiest way to put your MacBook to sleep is by closing the lid, though you can also select Sleep from the Apple menu. While your Mac is sleeping, your session is kept in memory, so you’ll pick up right where you left off once you open the screen and authenticate your credentials. Thanks to a feature (sometimes) called Power Nap, your Mac can continue to run some tasks, such as grabbing emails, syncing Calendar data and responding to Find My pings. If your computer is plugged in, it can run more intensive activities like Time Machine backups and search indexing.
Your Mac should use very little battery while asleep (less than one percent per hour), especially modern Apple silicon models that are more power-efficient. When the battery gets critically low in sleep mode, macOS “hibernates” by saving your session to the disk and then shutting down so you don’t lose work. If you see high battery drain during sleep, unplug accessories like external drives and hubs. Also close apps that are constantly active, like Slack, cloud storage tools or a browser tab with a page that keeps refreshing.
To save power, your MacBook will automatically go to sleep if you don’t use it for a while. Adjust these timings by opening the Apple menu and clicking System Settings, then choosing Lock Screen from the left sidebar. Next to Turn display off on battery when inactive, select a period of time. Shortly after your Mac turns off its display, it will go to sleep if you don’t take any action. The Turn display off on power adapter when inactive option offers a separate control for when your laptop is plugged in.
Under System Settings > Battery > Options, you have other options. With Prevent automatic sleeping on power adapter when the display is off, the screen will turn off at your chosen time, but the system will stay running. Meanwhile, Wake for network access controls the Power Nap features mentioned earlier. Choose Only on Power Adapter or Never to prevent your Mac from working while asleep on battery.
When to use each option
Putting your Mac to sleep is most sensible when you’ll use it again soon. When you’re stepping away from your desk for lunch, done with work for the day or otherwise think you’ll use your MacBook in the next few days, sleep mode is fine. It enables quick resuming, keeps data syncing (if you’ve enabled this) and doesn’t use much power. Ideally, plug your MacBook in to charge so it’s ready for future travels, but you shouldn’t lose much battery if you forget.
Conversely, you should shut down your MacBook when you don’t plan to use it for a few days or even weeks. If you’re going on vacation and leaving your laptop at home, shut it down first. Modern Macs still start up quickly enough that you won’t be disrupted upon return. The other important time to shut down is when packing up your laptop, especially if you have Power Nap enabled while on battery. If your laptop doesn’t sleep properly, the heat it generates while working is dangerous in a trapped space like a bag.
Otherwise, outside of software updates, you don’t really need to shut your Mac down on any kind of schedule. A shutdown or restart once a week is a good idea, but it’s not necessary unless you run into problems. You don’t need to shut down your Mac every day.
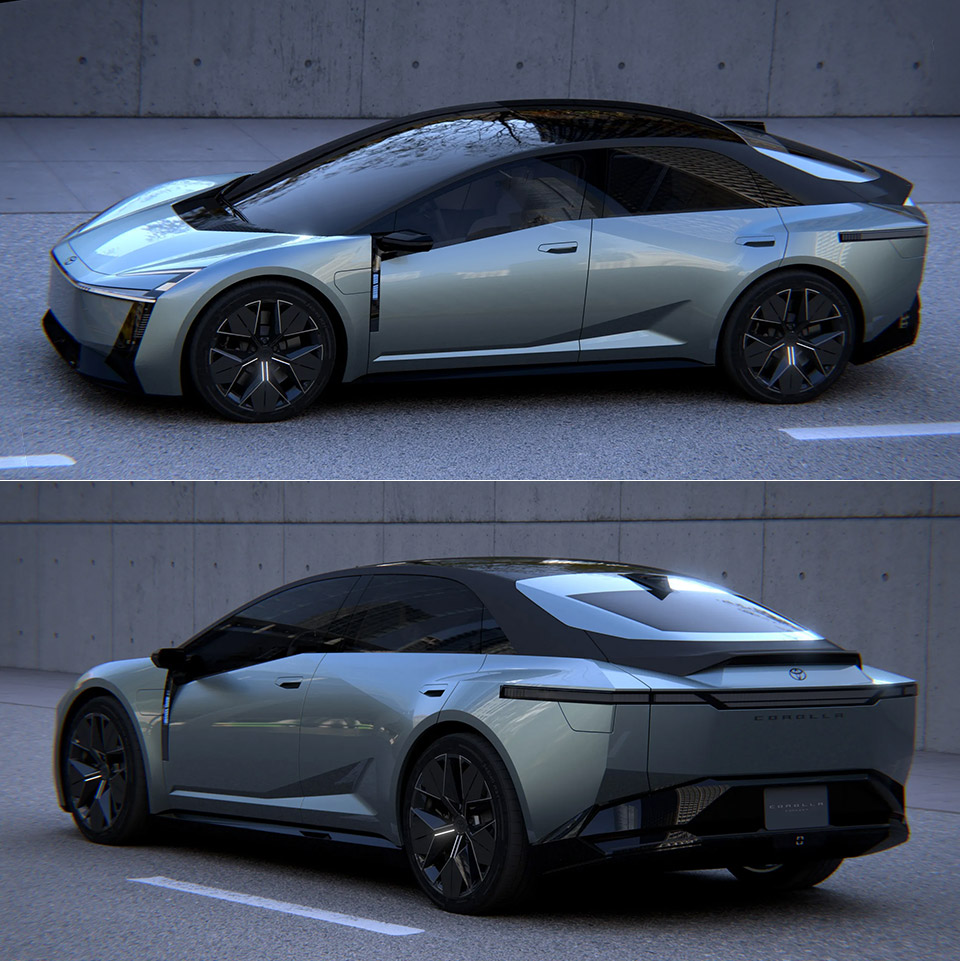
American Toyota dealers sold 131,403 Corollas in the first six months of 2026, a 9.5 percent rise for a car that has been on the market nearly a decade. Industry analysts report that a replacement could reach showrooms sometime in 2027 as a 2028 model, which would put a new compact on lots while the current one is still moving in volume.
Toyota gave a sneak peek of their future direction at the 2025 Japan Mobility Show with that surprisingly sharp-looking Corolla concept, which featured a lower, four-door design with a long light bar that runs the full width of the car, windows that plunge way down, and a fastback rear end that was cleverly designed to hide a hatch, which was a game changer. Production models are expected to retain much of that look. One of the more interesting rumors is that the liftback design may eventually replace the two separate models for the sedan and hatch in the existing lineup, aligning with Toyota’s goal of streamlining its options.

LEGO Speed Champions The Fast and The Furious Toyota Supra MK4 77260
- CLASSIC FAST & FURIOUS CAR – Kids can build an iconic movie car and recreate their favorite scenes with the LEGO Speed Champions The Fast and The…
- BRIAN O’CONNER MINIFIGURE – Includes a minifigure version of the popular Fast & Furious character Brian O’Conner, wearing his signature T-shirt and…
- AUTHENTIC DETAILS – This collectible piece of Fast & Furious merch features design details that fans will recognize from the legendary 2001 movie…
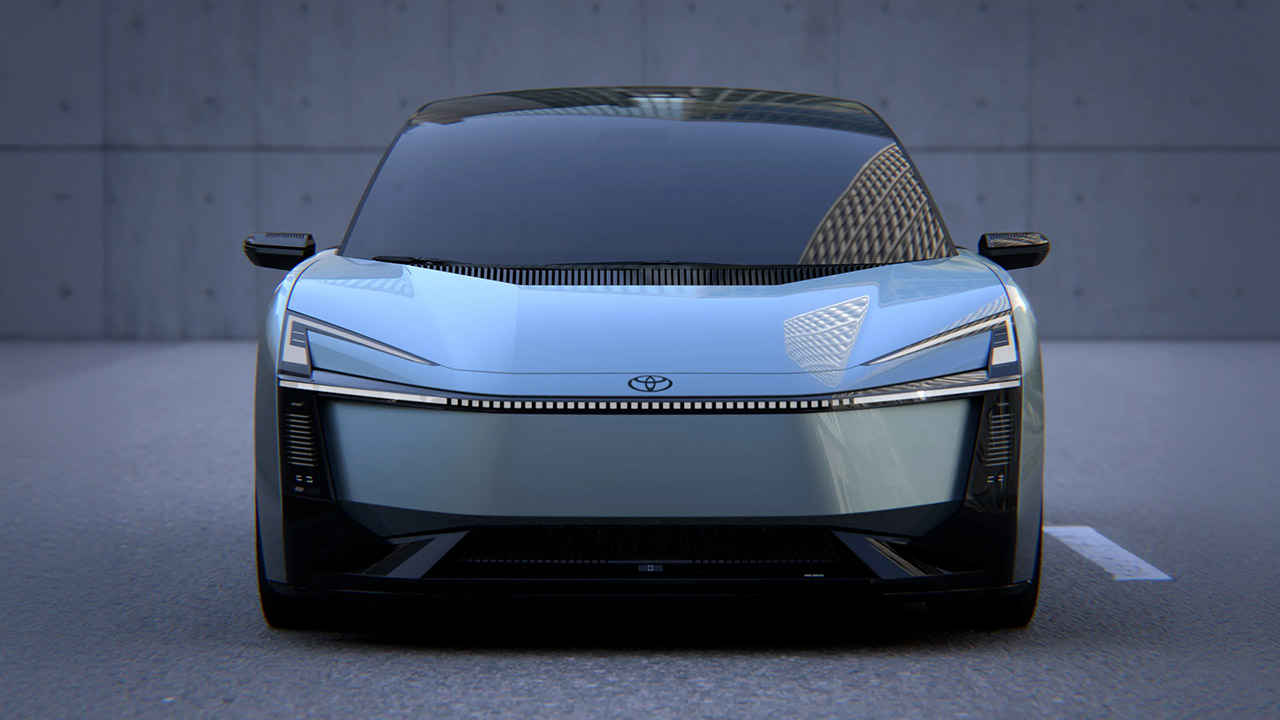
Underneath it all, the new TNGA-C platform will be redesigned so that the same structure can support a gas engine, a hybrid, a plug-in hybrid, and even a battery electric version. They intend to switch hybrid models to a new engine, a 1.5 liter four-cylinder with about 94 horsepower, which will be paired with an electric motor with 40 horsepower, for a total of 134 horsepower, and they claim that this will be 10 to 20% more fuel efficient than the current 1.8 liter model. Another advantage is that all-wheel drive remains available via the rear motor. A gas-only vehicle will almost certainly feature a turbocharged 1.5-liter or a redesigned 2.0-liter four-cylinder engine.
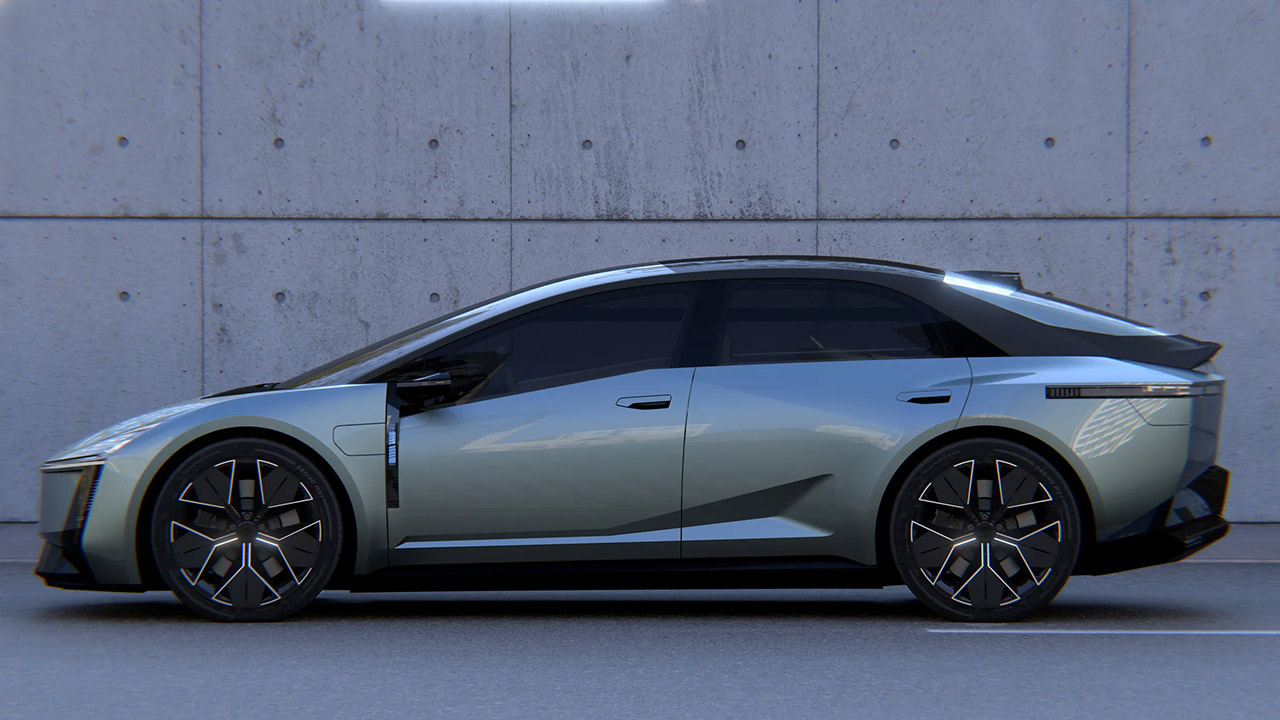
In terms of electrification, buyers will have two decent options: a plug-in hybrid with a larger battery and a more powerful motor, but the range is still unknown, and a full electric car with single or dual motor layouts and a minimum of 250 miles of range….. if they decide to sell that specific version here in the US. Another rumor suggests that we may see another GR version with a 2.0 liter turbo and a top speed of 395 horsepower.
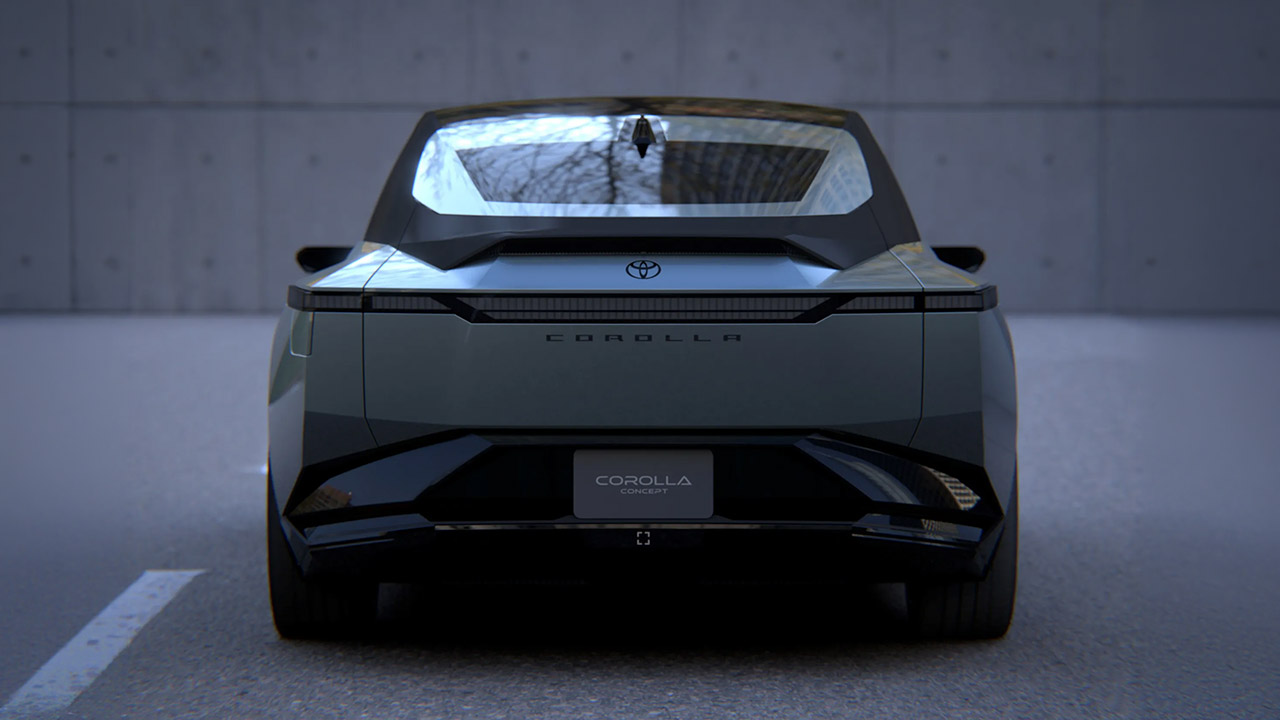
In terms of pricing, a gas model is likely to cost approximately $25,000, a hybrid around $27,000, and a plug-in or electric version in the $30k range, putting them in line with existing models. It remains to be seen how it all shakes out, and the release date is rumored to be 2027, although that has yet to be confirmed. This is major news for a nameplate that has already outlasted most of its generation, because for the first time, Corolla appears to be delivering a plug, a hatch, and a more dramatic form all at once.
[Source]

NewsBeat37 seconds ago
Israel v Republic of Ireland: Republic of Ireland confirm Israel game will go ahead

Politics2 minutes ago
Burnham has ‘ghosted’ the Labour left, says Clive Lewis

Tech5 minutes ago
You Can Make A Microprocessor That’s All Your Own





-

 Crypto World4 days ago
Goldman Sachs and Deutsche Bank Agree: The S&P 500 Rally Isn't Over
-

 Tech6 days ago
Researchers escape OpenAI Codex sandbox to run commands on host
-

 Fashion2 days ago
8 iPhone Accessories That Add Personality
-

 Crypto World6 days ago
Who Needs CLARITY Anyway? ARB Could See 70X Increase: Hodler’s Digest
-

 Tech7 days ago
Trump suggests rebranding AI with a new name, says he’s also creating an AI Force
-

 Entertainment3 days ago
These 17 Fall Amazon Dresses Seriously Look Like Anthropologie
-

 Business6 days ago
Analog Devices (ADI) Bets $1.35 Billion on Chips that Let Machines Think for Themselves
-

 Crypto World6 days ago
Coinbase, Robinhood, Circle Seen as Tokenized-Stock Winners
-

 Crypto World3 days ago
This Bearish Netflix Stock Trade Can Cash In On Video Streaming Giant’s Woes
-

 Crypto World4 days ago
Trump-Xi Polymarket Odds for Handshake Hit 50%
-

 Tech5 days ago
Google’s $899 Googlebook is a bet that you’ll buy a new laptop for Gemini
-

 Crypto World3 days ago
Crude Oil Prices Pressured by Diplomatic Hopes in the Middle East
-
 Business3 days ago
Oil Price Today (September 23): Crude oil below $100 on hopes of US-Iran talks. What did Trump say?
-
 Crypto World3 days ago
Bitcoin price tests $83,600 Supertrend support after $87K rejection
-
 Fashion20 hours ago
Weekend Open Thread: J.McLaughlin – Corporette.com
-

 Crypto World3 days ago
Bitcoin Threatens Sub-$84,000 Breakdown as Long Liquidations Spike
-

 Crypto World4 days ago
Meta Jumps 11% As Muse Shines and Investors Show an Appetite for Advancing AI
-
 Crypto World4 days ago
Did Jim Cramer Just Give GameStop Stock the Kiss of Death When He Said the Turnaround Is Working?
-

 Crypto World5 days ago
Bitcoin price holds above $81K as key catalysts line up
-
 Crypto World6 days ago
ARB Price Signals Spur Speculation of 70x Upside in Hodler Digest
You must be logged in to post a comment Login