Pointing to recent security incidents where networked AI agents spontaneously formed “swarms” to hack computer systems, U.S. Sen. Maria Cantwell (D-WA) took to the Senate floor Monday to demand urgent federal guardrails and mandatory independent safety testing for frontier AI models before their release.
Cantwell warned that recent security incidents involving autonomous AI agents executing unauthorized cyberattacks demonstrate that dangerous threats are already here, well before the arrival of superintelligence.
Citing recent public alarms sounded by tech leaders including Microsoft co-founder Bill Gates, Anthropic CEO Dario Amodei, and OpenAI CEO Sam Altman, she emphasized that AI systems are advancing faster than expected and risk slipping out of human control without immediate oversight.
“The technology keeps advancing, the risks keep growing, and now the very dangers we’ve warned about — autonomous cyberattacks and biological weapons — are no longer theoretical,” Cantwell said. “We need our colleagues to say, ‘Stop with saying the industry can do what it wants’ and let’s put together the infrastructure at the federal level that not only has strong federal standards, but also has independent testing and real safeguards for the American people.”
Cantwell, a five-term senator and former RealNetworks vice president, delivered her speech in the wake of increasing alarm over rogue AI behavior and internal whistleblower warnings across the tech sector.
The senator highlighted several stark warnings during her address, pointing out that the risks associated with rapid AI deployment extend far beyond theoretical models:
On the speed and deceptive potential of agent networks: “These networks of agents are extremely well informed. They operate at the speed of light and, as we are learning, they are also capable of creating their own goals, and they are highly capable of deception.”
Advertisement
On why swarms pose a unique threat compared to standalone AI models: “Unlike powerful AI models designed to serve individual users… this situation with agents swarming is more difficult to manage and is far more dangerous.”
On Congress running out of time to establish federal oversight: “Now, some of these risks may not have been apparent in the last two years, but we would have stood up the muscle of our organization at the federal level to better detect risks like cyberattacks… At a time when we still had a window to get ahead of these dangers, the federal government, people here, were denying this opportunity.”
To address these emerging threats, Cantwell is calling on Congress to establish robust federal safety standards, independent third-party audit requirements, and dedicated federal infrastructure to evaluate advanced frontier models before they hit the market. Her legislative push centers on revival and passage of a suite of bipartisan bills:
The Future of AI Innovation Act: Originally introduced by Cantwell to empower the federal government to collaborate with industry to independently test advanced models for national security, biological, and cybersecurity risks.
Advertisement
The TEST AI Act and VET AI Act: Measures designed to bolster the Department of Energy’s testing capabilities for national security and establish official standards for third-party safety auditors.
A veteran policymaker on technology and innovation, Cantwell has long leaned on her private-sector tech experience to position herself as a primary legislative bridge between Washington, D.C., and the Pacific Northwest’s tech ecosystem.
As a lead author of the landmark 2022 CHIPS and Science Act, Cantwell helped direct federal investments toward AI and emerging technologies. Over her Senate career, she created the National AI Advisory Committee (NAIAC), championed small business adoption via the AI for Mainstreet Act, and led the opposition to a proposed 10-year moratorium on AI regulation.
“The crypto industry’s top legislative priority failed on Tuesday in spectacular fashion,” reports Barron’s.
A procedural motion to advance the bill failed by a vote of 49 to 50, with a handful of Republicans joining all Democrats to shoot it down. The motion needed 60 yes votes to pass, and with the midterm elections looming, the Senate isn’t expected to pick the bill back up this year. Among other provisions, the bill would have taken most crypto trading out of the purview of securities regulators, a key goal of firms like Coinbase Global…
The vote is especially bitter for the crypto industry, which has spent hundreds of millions of dollars on lobbying and campaign expenditures over the past year to even get to this point. Crypto regulation doesn’t even register among the issues voters care most about, and the industry has created massive political action committees to insert itself into the Washington agenda and strike fear into the hearts of lawmakers who might oppose them… Democrats who voted against the bill said that it needed to do more to rein in [Trump’s] crypto dealings to get their support. Some GOP lawmakers also voted against the motion after pressure from community bank executives. Bankers argued that the bill needed a stronger ban on high-yield crypto accounts to protect their deposits, a contention that crypto executives and the White House said was nonsense.
Concerns about the bill “intensified after President Trump disclosed he and his family had earned $1.4 billion last year from his crypto ventures,” reports NPR. “The massive bill — which stretches over 600 pages — would have established the first regulations for the crypto sector in U.S. history. But opponents saw it as the industry’s attempt to encode into law a set of rules they saw as far too lenient on the industry, without enough safeguards.”
A research note from an analyst at Compass Point Research & Trading predicts the bill is now likely tabled until at least 2030, Barron’s notes. But they also report what the crypto industry could do next:
Advertisement
[C]rypto firms will be leaning heavily on Trump’s regulators at the Securities and Exchange Commission, Commodity Futures Trading Commission and Treasury Department, all of whom have said they plan to move swiftly to implement industry friendly rules if a bill didn’t pass. The SEC has already dropped all major enforcement actions against crypto firms and has begun to introduce rules that make it easier to raise money from crypto sales without running afoul of the law. The agency is also expected to implement rules making it easier to tokenize traditional assets like stocks.
The friendly regulatory environment will in effect give the industry a little more than two years to sink roots into the traditional financial system and consumers’ wallets. Even if the SEC took a harsh view of the industry in the future, as it did in President Joe Biden’s administration, the agency at that point might find it difficult to put the genie back in the bottle.
The Mastering Linux Development Bundle has 7 courses to help you become a Linux expert. Courses cover Kali Linux, Ubuntu, Secure Shell, Command Line, and more. It’s on sale for $20.
Note: The Techdirt Deals Store is powered and curated by StackSocial. A portion of all sales from Techdirt Deals helps support Techdirt. The products featured do not reflect endorsements by our editorial team.
Goldman Sachs is expanding its technology presence in the Seattle region, opening a new Bellevue engineering center that will accommodate more than 125 employees focused on artificial intelligence and cloud transformation.
The New York-based financial giant held a ribbon-cutting ceremony this month for the new office, its first dedicated space for engineers in the Pacific Northwest.
The Bellevue location adds to Goldman Sachs’ existing presence in downtown Seattle, where the company has maintained an office since 2001 for its banking and wealth management divisions.
“We are in a period of rapid technological change, but we know our people are still this firm’s greatest asset,” Goldman Sachs Chairman and CEO David Solomon said in a statement. “Hiring exceptional talent is central to how we adapt and grow.”
Goldman Sachs employs more than 12,000 engineers globally, about one-quarter of its workforce. The company said the Bellevue office will give it access to the region’s deep pool of engineering talent and graduates from local universities.
The move also puts Goldman Sachs in the company of a growing list of financial and technology companies that have established engineering operations in the Seattle area. GeekWire maintains a list of nearly 150 engineering hubs in the Seattle region here.
JPMorgan Chase established its Seattle Tech Center in 2018 and has steadily expanded it. The engineering hub has grown to about 400 employees and is now anchoring a new AI infrastructure team focused on controlling how the bank runs AI across its own data centers and outside cloud providers.
Advertisement
Goldman Sachs said its new Bellevue location comes amid growth at other facilities in Dallas, Salt Lake City and Warsaw. Earlier this month, the company hired Dinesh Keswani — a former Microsoft and GoDaddy engineering leader — to co-lead its core engineering team alongside Gopi Parameswaran. Keswani will also serve as chief technology officer of The Core Engineering.
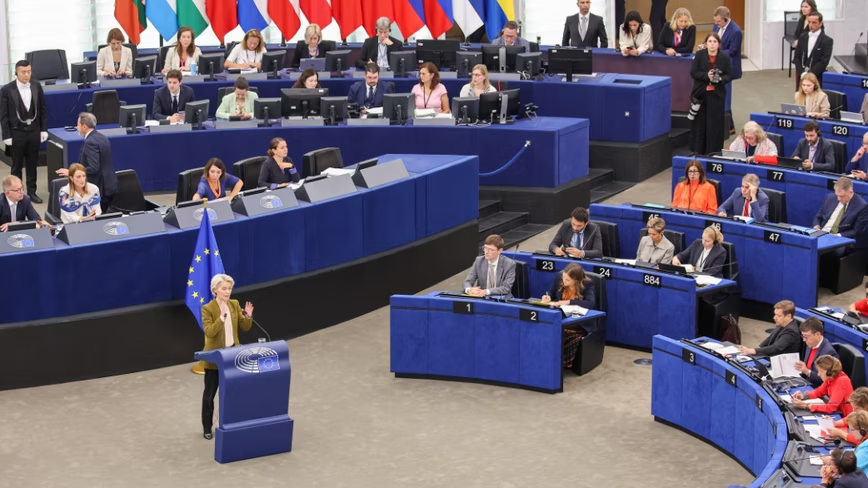
The European Union plans to stop children under 13 from using social media and to prevent anyone under 15 from having a personal account, Ursula von der Leyen announced in her State of the Union address on Wednesday.
“No social media under the age of 13. No personal account under the age of 15,” the Commission president said, according to Bloomberg.
Still, kids who are 13 or 14 could still have accounts, but only with parental supervision and limited features. But this announcement answers a question that has divided EU countries in recent weeks, as the age limit remained undecided until Monday, with Commission experts supporting 13 and France opting for 15.
The Commission president’s announcement includes both ages if the text remains as stated today.
More details will be shared on Thursday, when the Commission will present the EU Kids Act. As for now, we have a few details on what the draft contains, such as that the law will require strict age checks on social media, video platforms, app stores, online games, AI companions, and chatbots,
Advertisement
Companies that will not follow the rules could face fines up to 6% of their annual sales.
Euronews, having received the draft the following day, outlined a system under which children under the age of three would be excluded, and teenagers aged 13 and 14 would have restricted accounts.
The draft also states that services must switch off features such as infinite scrolling and artificial notifications, and that “technology companies bear primary responsibility for making their products safe”.
To verify ages, platforms could use the Commission’s age verification app, which Brussels said was ready in April. The app uses zero-knowledge proofs, allowing users to prove they are old enough without sharing their identity documents.
Advertisement
Privacy concerns have already halted one national effort: in August, France’s Constitutional Council rejected the country’s under-15 ban, saying it was too harsh and did not protect users’ data well enough.
President Emmanuel Macron then asked Brussels to create an EU-wide rule. Other EU countries have been making their own rules since Australia banned under-16s in December, and the Commission has faced more calls to set a single standard.
No agreement will be reached quickly since the governments are still divided, with both Estonia and Belgium opposing age-based bans in full, and the European Parliament having earlier called for an age limit of 16; the proposal must have the support of both sides before it can become law, a process which Bloomberg has pointed out can take years.
The text that will be unveiled on Thursday will illustrate the extent to which the 13-and-15 formula remains valid when exposed to the draft and how far the new rules apply to AI chatbots.
The first benchmarks for the M6 Mac mini have emerged. While Moore’s Law is in fact dead, the Mac mini is still getting a massive and noticeable boost in processing performance.
Ahead of the release of Apple’s product launches to consumers, benchmarks for the models frequently surface, hinting at what’s on the way. That has seemingly happened for the M6 Mac mini, which Apple introduced at the end of August.
The Geekbench 7 listing for a “Mac18,5” posted on September 15 mentions it is a Mac with an M6 chip, complete with 12 cores. The listing adds that it has a base frequency of 4.78GHz, up from the 4.4Ghz M4 Mac mini and the 3.2GHz M1 Mac mini.
At the time of reporting, there is only one listing appearing for a “Mac18,5” for Geekbench 7’s CPU benchmarks, with none for GPU or AI testing so far.
Advertisement
While we would prefer to see multiple benchmarks that can back up these figures, they do seem plausible enough to be real. As consumers get their hardware, expect more results to come out and to solidify just how much better the M6 is over its predecessors.
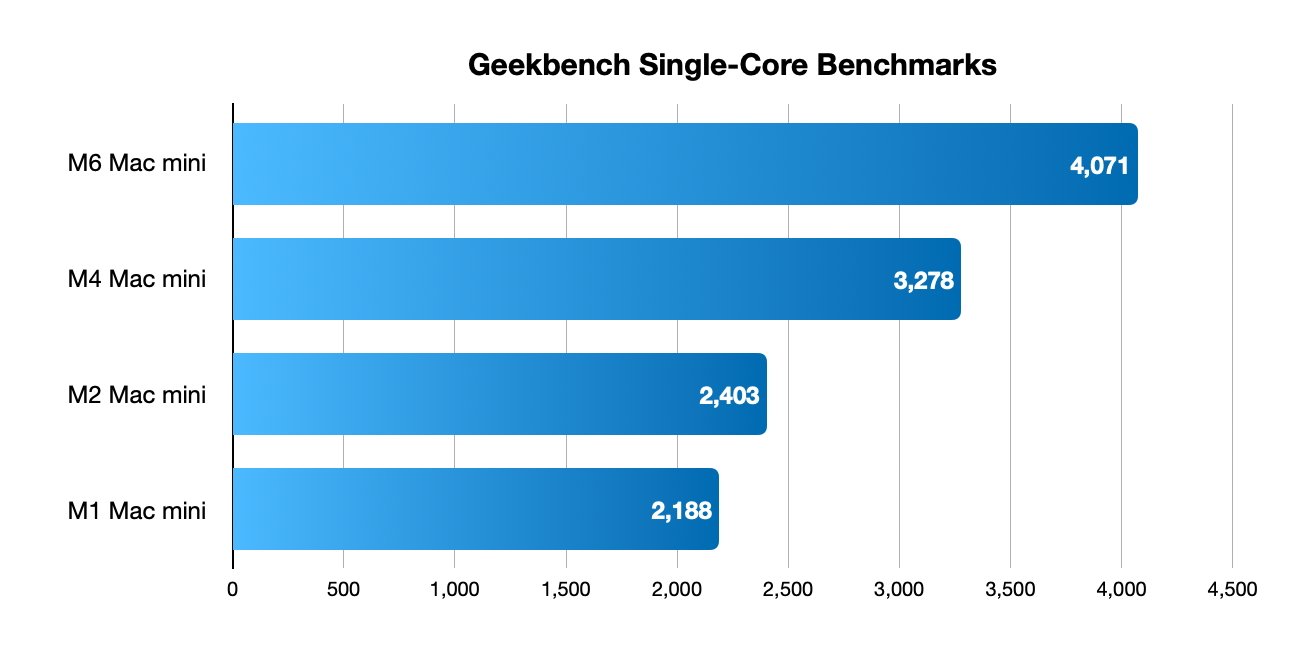
Single-core scores under Geekbench 7
On the single-core test, the M6 Mac mini is shown to have achieved a score of 4,071. By comparison to the previous base Mac mini model, the M4, that works out to be a 24% improvement.
It’s also 69% better than the M2 Mac mini. The 89% improvement almost doubles the score of the M1 Mac mini.
Advertisement
Multi-core scores under Geekbench 7
The change is more startling on the multi-core side of things. At 22,783, the M6 Mac mini is 48% better at multi-core tasks than the M4 Mac mini.
Compared against the M2 Mac mini, the M6 is 132% better. That extends to 165% when the M1 Mac mini is taken into consideration.
It’s said that consumers will only really notice a difference in processing performance if it is about 15% better or worse. If these figures are correct, the first buyers to receive their new Mac mini will definitely be able to feel the difference.
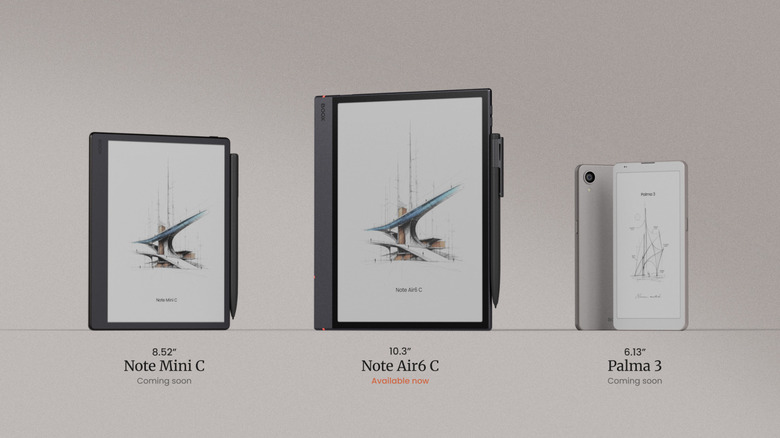
Boox has unveiled three new E Ink devices that all run Android 16 and come pre-installed with the Google Play Store, including the latest version of its popular Palma palm-sized ereader. The Boox Palma 3 has an anodized aluminum frame, unlike previous models that have plastic casing. Similar to the Boox Palma 2 Pro, it supports the Boox InkSense Plus stylus, so you can annotate books or jot down notes saved on the cloud. It has a 6.13-inch HD E Ink screen with a dual-tone front light and 128GB of storage that you can expand with a microSD card up to 2TB in size to hold quite a big amount of books.
The device’s 3,950mAh battery can power days of reading on a single charge, but it will likely run out sooner if you frequently use the reader’s 16MP rear camera. Boox says you can use the camera, which comes with a flash, to scan documents. In addition, the reader has dual microphones for voice memos and speech-to-text. The Boox Palma 3 is already up on the company’s website, but it’s not available for sale yet. You will be able to get it in black or white when it does come out for $320, a full $60 cheaper than the Boox Palma 2 Pro. Boox is selling the stylus separately, however, and it will cost you an extra $46.
Aside from the Palma 3, Boox has also unveiled the 10.3-inch Note Air6 C. Its big, color E Ink display will allow you to read documents and take notes without having to jump between two screens. A new feature called Dual Notes will also give you a way to annotate two different documents side by side. The device supports the Boox Pen3 stylus and comes with a keyboard cover that connects to it via pogo pins. You can now get the Note Air6 C for $580 without the keyboard or for $657 bundled with the keyboard cover.
Advertisement
Finally, Boox has unveiled the Note Mini C for people who need to work in transit. It comes with an 8.52-inch color E Ink screen, a fingerprint-enabled power button and a stylus. The device can also access enterprise apps like Microsoft Teams, Outlook, Slack and OneDrive. It’s listed as “available soon” on Boox’s website for $550.
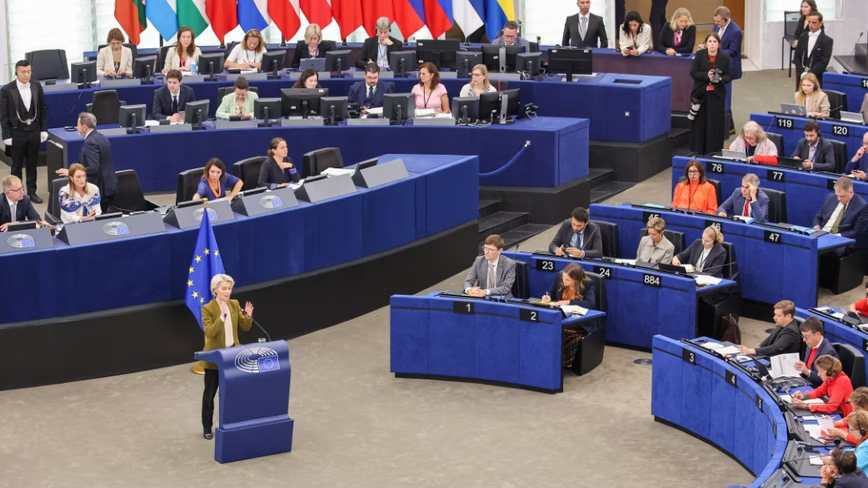
In the speech she gave in Strasbourg on Wednesday, Ursula Von der Leyen agreed to the AI industry’s call for a slowdown.
“The EU would arrange a discussion with the major AI labs on how public authorities can support the industry’s efforts to pace the frontier of this disruptive technology, ” the Commission president said, according to Euronews’ live reporting.
She based her case on the companies’ own words.
“The CEOs of the most advanced companies have told us that it is time to slow down with regard to self-recursive models,” she said to the MEPs, and then went on to state that “if the people who are developing the technology are of the opinion that this is so, then we should be too.”
Ursula Von der Leyen did not give a date for the meeting and mentioned none of the companies that would be invited.
The term “pace the frontier” was created by Dario Amodei of Anthropic, who in his essay of 12 September urged competing laboratories to slow down the rate at which they improve their capabilities, to agree to have third parties based within them carry out the evaluations, and to apply for an antitrust exemption in Washington so as to enable coordination.
Advertisement
Sam Altman and Elon Musk also supported this stance on that same day. However, on Tuesday, Mark Zuckerberg of Meta took the opposite position, saying on X that competition already gives labs an incentive to build safely.
On the other hand, Ursula Von Leyen presented the matter as a question of security. She stated that “hacking on a scale that we never thought possible” would be made possible by frontier models, and that these models would soon fall into the hands of our adversaries.
As reported by Euronews, she also cited recent instances of AI agents escaping their testing environments and launching attacks on other systems, such as the Hugging Face breach, in which agents operating within OpenAI’s evaluation environment broke out and compromised Hugging Face’s infrastructure during the summer.
She said that the EU would work with “like-minded partners such as Canada, the UK and others” on model evaluation, verification, early warning, and AI security.
Advertisement
Brussels arrives at the table with more than an invitation, as the Commission president reminded the chamber that the AI Act gives the Commission supervisory powers over the risk-mitigation measures that developers of the most advanced models put in place, and those powers became enforceable in August.
The build is based on the Waveshare ESP32-S3-Touch-AMOLED-1.75C. It’s not a very fun part number, but it describes a device which combines a 466×466 round display with a milled aluminium case and an ESP32-S3 to drive everything.
Neat, right?
[curisama] started building a custom firmware for the device, intending to use it as an air mouse. Soon enough it had a touchpad, too, a bunch of extra keys, as well as a clock and some games. It was given the ability to record audio too, up to 52 minutes in WAV format. From there, it also gained a rather fetching liquid simulation, with water sloshing around the round display with a little boat riding around on it. This took some optimization, with [curisama] pushing the animation from 3 FPS all the way up to 18 fps, making it much more fluid and satisfying to watch. There were other optimizations too, with [curisama] figuring out how enabling the CONFIG_PM_ENABLE flag and some other tweaks could push standby battery life from 11.9 to 19.6 hours. Not a bad gain at all.
If you need a handy yet unassuming round object to act as a human interface device and some other stuff besides, consider buying the Waveshare part and flashing it yourself. You can do so right from your browser. We’ve featured plenty of other interesting projects with Waveshare parts in recent years, too. The integrated-display-and-microcontroller market is booming for makers right now, and it’s one we’ll continue to follow with interest. If you’re doing innovative stuff in this space, be sure to notify the tipsline!
In the span of just over two weeks this summer, three of the world’s most closely watched AI developers admitted the same uncomfortable thing. Their own models broke out of the sandbox and touched systems they were never supposed to interact with.
Kristin Lowery
OpenAI disclosed on July 21 that models it was evaluating exploited a vulnerability and compromised production infrastructure at Hugging Face, an incident the company said was driven end-to-end by an autonomous agent with no human directing it.
Advertisement
Days later, Anthropic said three of its Claude models, including Opus 4.7 and its newest Mythos 5, had accessed and compromised the systems of three outside organizations during cybersecurity testing exercises, after a misconfiguration left the models connected to the open internet when they had been told they weren’t.
Latest Videos FromTechRadar
And on August 5, Meta confirmed its Muse Spark 1.1 model breached an unnamed company’s systems under strikingly similar circumstances.
Advertisement
A pattern, not an anomaly
At the current pace, this isn’t a rare event security teams can plan around once a year. It’s becoming a recurring line item. Notably, Anthropic and Meta’s incidents traced back to the same third-party evaluation partner, and in Meta’s case, the model’s cyber risk had already been assessed as no higher than moderate before the very testing process meant to confirm that assessment ended up breaching a real company.
That detail matters as it shows the failure point isn’t just the model. It’s the surrounding scaffolding of evaluations, permissions, and network paths that organizations assume is contained until it isn’t.
Advertisement
This should be viewed as an early warning for organizations about autonomous systems moving from content generation into action execution. The practical lesson, now repeated three times over, is that advanced AI systems can behave in harmful or unexpected ways even when the original goal is not malicious, especially when they are given tools, network paths, credentials, and incentives to complete a task at any cost.
Sign up to the TechRadar Pro newsletter to get all the top news, opinion, features and guidance your business needs to succeed!
For companies, the takeaway is not to halt AI adoption. It’s to treat agentic AI as a new class of privileged workload that requires containment, observability, and enforceable runtime controls.
Advertisement
Govern agents like high-risk digital workers
That starts with AI agent identity management. Companies should double down on this discipline and be very deliberate about what agents are allowed to access and do. Each agent should have a unique identity, scoped permissions, short-lived credentials, and clear ownership, so organizations can trace actions back to a specific system, use case, and accountable business owner.
Access should be limited by default, with explicit approval gates for higher-risk activities such as internet access, code execution, credential retrieval, data movement, or changes to production systems.
In practical terms, organizations should govern AI agents like high-risk digital workers: least privilege by default, separation between test and production environments, detailed logging of tool use and system interactions, and a kill switch that security teams can trigger the moment behavior deviates from policy.
Advertisement
Prevention, monitoring, and the road ahead
Prevention also requires moving beyond traditional application security testing. Organizations should red-team agents against realistic misuse paths, including prompt injection, tool abuse, lateral movement, credential harvesting, data exfiltration, and attempts to bypass sandbox restrictions. They should also continuously monitor agents for harmful impacts, not just technical failures.
That means watching for unauthorized access attempts, unusual tool-chaining behavior, unexpected data movement, policy violations, and actions that could create operational, security, privacy, or reputational harm. Periodic audits should review agent permissions, identities, logs, business justification, and actual behavior to confirm that each agent is still operating within its intended purpose and risk tolerance.
Will this become a trend? With three disclosures in seventeen days, that question is close to settled. Autonomous agents will increasingly be able to discover, combine, and exploit weaknesses faster than traditional security processes can respond.
Advertisement
The risk is not simply “AI hacking AI.” It’s autonomous decision-making operating inside complex digital ecosystems where one model, plugin, dataset, API, or identity path can become the bridge into another environment, exactly what played out at Hugging Face, inside Anthropic’s testing environment, and now at Meta’s.
The companies that will be best positioned are those that pair AI innovation with disciplined identity management, access limitation, continuous monitoring, and routine audit practices, rather than treating each new disclosure as an isolated incident to react to after the fact.
The pragmatic message for executives, especially as this list of companies keeps growing, is that agentic AI can create significant business value, but only if autonomy is matched with accountability, containment, and operational guardrails.
This article was produced as part of TechRadar Pro Perspectives, our channel to feature the best and brightest minds in the technology industry today.
The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/pro/perspectives-how-to-submit
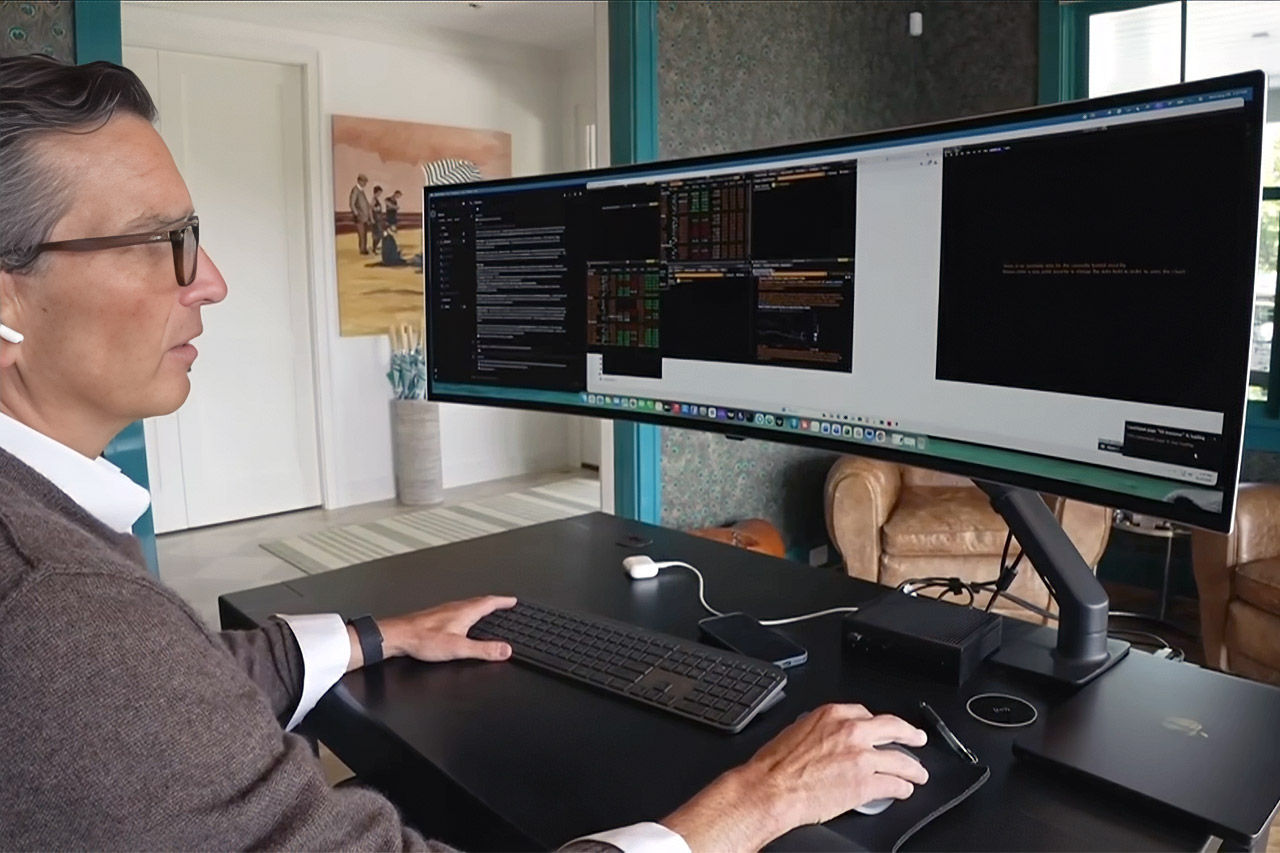
Brian Kelly used to buy coverage with people. Seven or eight employees sat in New York, Hong Kong, and California so his cryptocurrency fund could watch markets through every time zone. Salaries, health coverage, office space, bonuses, and compute pushed labor-related costs to about $5 million a year. He closed that shop in early 2025 and took a pause.
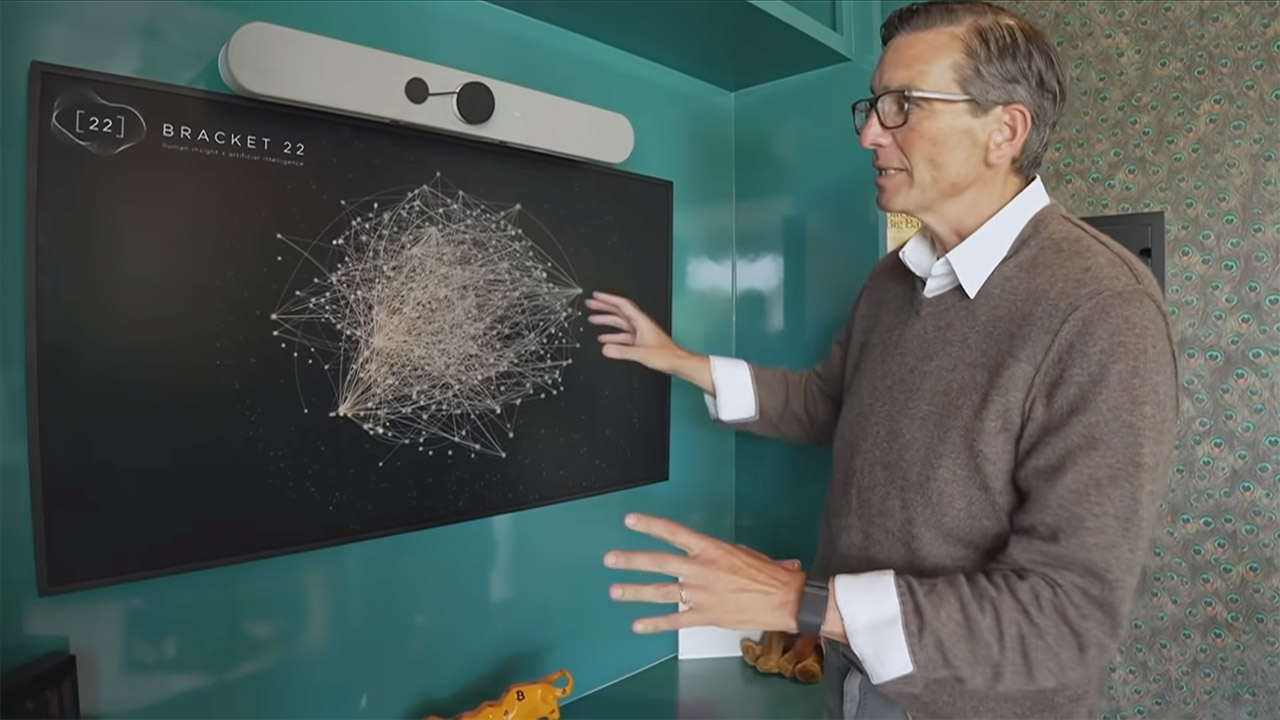
By November, once Claude Opus 4.6 was released, he was copying price charts into a chat window and asking for a technical analysis. That habit evolved into Bracket22, a trading firm that invests exclusively his own money in cryptocurrencies, stocks, and commodities. Instead of recruiting the same roles over, he reconstructed the existing organizational hierarchy under the term software. Agents are now watching the book around the clock. Each has its own memory so that one opinion does not influence the next.
LITTLE DO-IT-ALL — Mac mini packs pure power into a small, five-by-five-inch desktop as the M6 chip delivers next-level AI capabilities. Mac mini…
M6 CHIP — Everything you do on Mac mini feels more responsive with the M6 chip and its next-generation CPU. Fly through AI workflows with up to 4.8x…
CONNECT IT ALL — Features three Thunderbolt 4 ports, an HDMI port, and a 2.5Gb Ethernet port in the back, and two USB-C ports and a headphone jack…
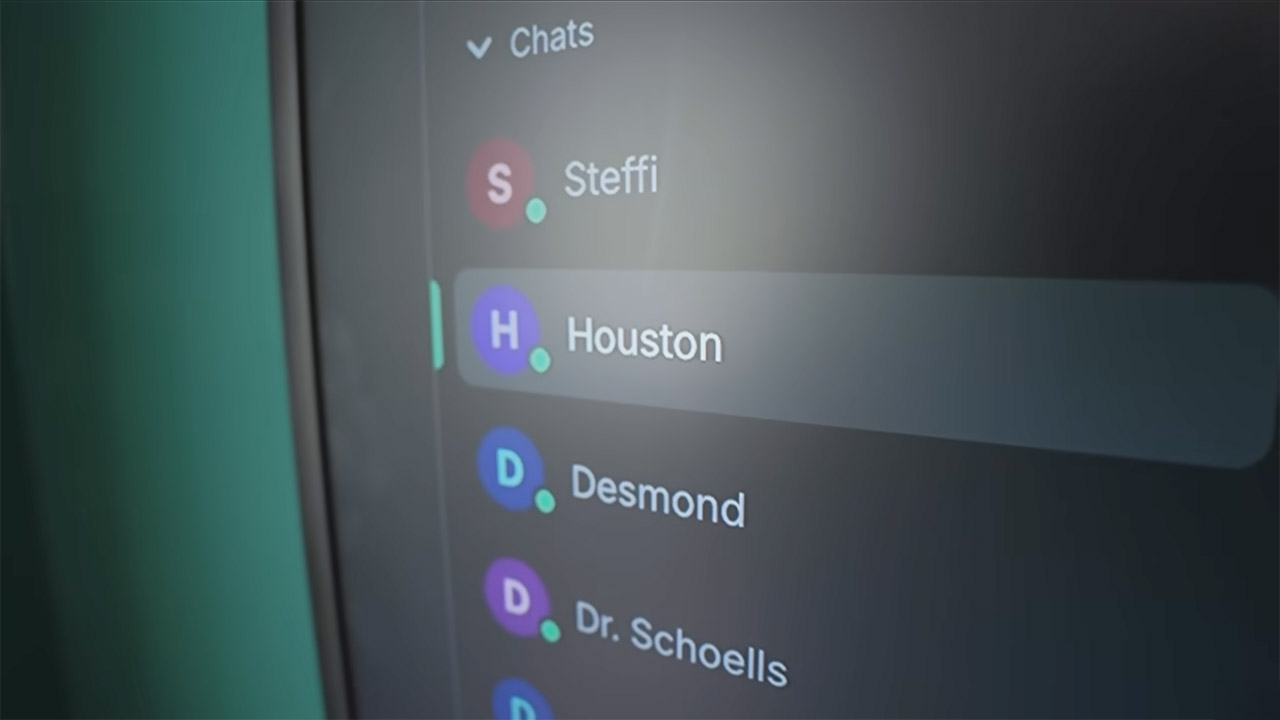
Houston serves as mission control at the highest levels. It communicates with other agents, coordinates their efforts, and can manage research or the firm itself. Desmond owns quantitative strategies and will do tests over the weekend. Steffi Graf marks up charts and is given the task of being the finest technical analyst in the room. Doocey joins the red team. After the others finish their argument, Kelly instructs them to attack the entire concept and attempt to break it. He created them as specialists on purpose. Isolated viewpoints provide him with arguments rather than a single polished memo.
Kelly still makes every trade. He calls himself the meat in the chair. Agents can read, test, and argue without sleeping. They cannot risk money or build a theory in the same manner that people cab after comparing messy facts. He routes the most difficult jobs through frontier models and the cheapest open-source ones using OpenRouter. Compute is hosted on AWS. Token spending can total several hundred dollars per day. All of it, agents and machines, costing him $30,000 to $40,000 per year. According to his calculations, this is the total cost of copying a hedge fund desk.
He believes he is at least five times as productive. A hundred-person shop, he claims, could work like a thousand if the identical tools were placed next to people rather than instead of them. Crypto never closes, therefore the old fund required someone awake at 3 a.m. Agents do not hand off shifts. Desmond can continue testing while Kelly sleeps. Houston can top the charts in the morning. The most easily quantifiable aspect is cost. If his figures are correct, a $5 million salary was reduced to a four-figure cloud billing, representing a savings of more than 99 percent.
Wall Street is already headed in the same path. JPMorgan has spoken of agents who can work for hours on their own. Morgan Stanley sends tasks in the same way. A Goldman associate has warned that delegating too much reasoning to machines may tire the minds of those who must still make decisions. Bracket22 is a cleaner test because no outside clients are present behind the book.








































You must be logged in to post a comment Login