SiliconRepublic.com stopped off in Kilkenny for Cyber Ireland National Conference 2026, where we talked to a number of attendees from across the industry.
On Tuesday (22 September), Cyber Ireland held its fifth annual national cybersecurity conference to explore the most important trends and updates within the contemporary cyber sector.
The Cyber Ireland National Conference (CINC) 2026 saw a variety of cybersecurity professionals and leaders gather at the Lyrath Estate in Kilkenny to discuss and examine topics such as the global cyberthreat landscape, cyber innovation, the development of a cyber-ready workforce and emerging security risks associated with AI.
SMEs, multinationals and individual experts alike all gathered at the event, which was sponsored by organisations such as Enterprise Ireland, TrendAI, Integrity360, IDA Ireland, Munster Technological University, Intel and Centripetal, among many more. Ireland’s National Cyber Security Centre (NCSC) and KPMG were headline sponsors of the event.
Advertisement
As well as featuring a number of keynotes and panel discussions, a key goal of the event was to facilitate expertise and knowledge exchange among the attendees.
This kind of engagement was particularly noted by Loman McCaffrey, Integrity360’s director of business development for Ireland, when speaking to SiliconRepublic.com at the conference.
“Everyone is engaged, everyone seems to have come with some challenges in mind,” he said.
“People use [CINC] as their one outing of the year to gather some information, to come back to the team, their boss, to the board with ‘here’s the direction of travel we need to be on’. Some events are a little bit more ‘a day out from the office’ – this isn’t that.
Advertisement
“This is people coming to do their research, figure out what others are doing.”
Small state, important position
The theme for this year’s conference was ‘Realising Ireland’s Cyber Industry Potential’, with a number of talks focused on Ireland’s importance in the European space, and how the country can scale its cyber resilience and capabilities to become a global player in the domain.
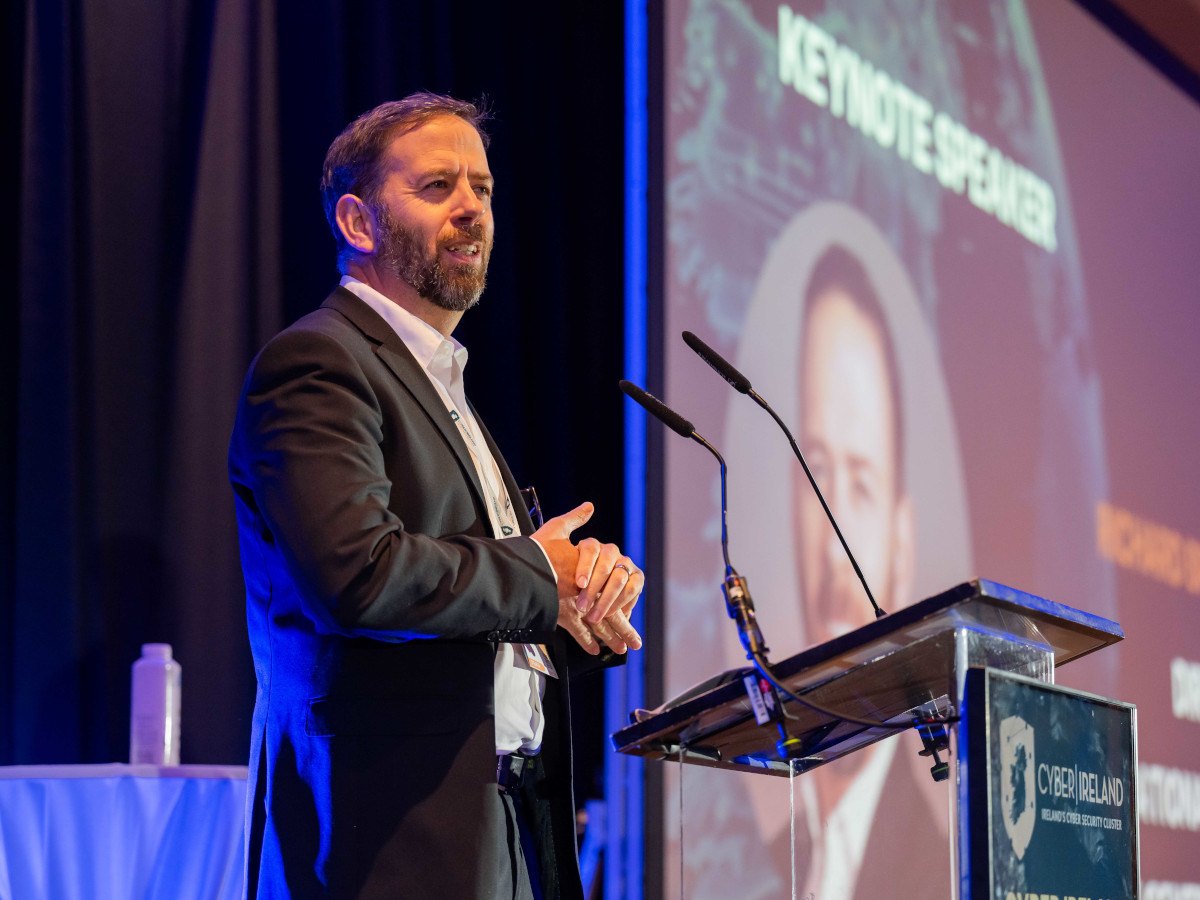
For Ian Fahey, managing director at KPMG, the scene was set for this year’s CINC by NCSC director Richard Browne in his opening keynote, ‘Cybersecurity State of the Nation Address’, where he “introduced Ireland as a small state on the edge of Europe, who is also leading the overall security capability for the European state”.
“We’re hosting vast amounts of data, we’re hosting and managing the fibre interconnectors between Ireland and mainland Europe and the US,” said Fahey.
Advertisement
“Lots of key critical infrastructure items are being hosted or driven out of Ireland and that brings a certain responsibility, and I think Ireland as a nation is stepping up to that.”
The conference took place at a vital time, with Ireland currently in the middle of hosting its EU Presidency – which also brings heightened cyber risk with it.
Eoin Byrne, cluster manager at Cyber Ireland, noted that it’s become clear through the Presidency that Ireland has a “very strong seat at the table” in Europe.
However, he emphasised that the country also has a “critical role to play in securing Europe’s digital economy” due to factors such as hosting numerous multinational tech and pharma companies, the transatlantic data cables running through our waters, and hosting an estimated 30pc of the EU’s data.
Advertisement
Fahey echoed the important role Ireland plays in EU digital resilience, stating that it brings “different pressures” but also “an imaginative mindset”, noting that some of the vendors at CINC were on “the leading edge” of tech solutions.
“That’s kind of positioned us to be a real strength and a real leader in terms of cybersecurity,” he said. “[The EU Presidency] has obviously brought a different focus to Ireland. The threat landscape changes, it naturally follows the Presidency of the EU.
“Ireland as a whole has held up really well, and what it has really reinforced is that the cyberthreat landscape is borderless and our response … also has to be borderless.”
‘Get the basics right’
With the topic of cyber resilience, especially in an Irish context, top of mind at CINC 2026, we asked a number of attendees about what Irish businesses need to do to stay secure in the ever-evolving threat landscape.
Advertisement
Eadaoin McArthur, a Cortex and cloud specialist at Palo Alto Networks, pointed to staff education as key to staying secure.
McArthur said that businesses can bolster their defences by “ensuring that their staff are moving at the speed that the threat landscape is evolving, and ensuring that organisations have the incentives and mandates in place and that they’re addressing them in a timely manner”.
She added: “Most organisations going forward will be forced to have an AI mandate to ensure that their organisations are capable to protect against the speed and velocity at which cyberattacks are occurring.”
Fahey emphasised that the most important step for Irish organisations is to “get the basics right”.
Advertisement
“Sort out your basic cyber hygiene before you start addressing all of these really sophisticated attacks,” he advised.
Fiona Griffin, a solutions engineer at TrendAI, agreed, and also added that Irish organisations need to keep an eye on AI.
“Getting the basics right – hygiene, patching – but also really just being aware of AI out there,” said Griffin. “Taking it seriously, making sure you’re compliant, making sure that you’re aware of the latest threats that are out there, and what’s Ireland doing in terms of compliance.”
Don’t miss out on the knowledge you need to succeed. Sign up for the Daily Brief, Silicon Republic’s digest of need-to-know sci-tech news.
An advertiser paid for editorial consideration of this deal. Our editorial experts vetted the deal based on our independent expertise. Because we determined that the deal will save money for our readers, we wrote the content.
Save 15%: Buy a Japanese data eSIM from Ubigi and save 15% off when you enter our exclusive discount code CNETJP15 during checkout. If you’re traveling to Japan and want to be able to use your phone without worrying about roaming charges, this is the deal for you.
You’ll save 15% on your first purchase with 8-, 15- and 30-day data eSIMs available, all with unlimited data throughout Japan. Japanese data eSIMs start at $21 with our code, and you’ll save the most money when choosing the longer plans.
Save 15% with code CNETJP15
Advertisement
Ubigi Japanese eSIM plans
Ubigi offers three Japanese data eSIMs for you to choose from. The eight-day unlimited data plan is down to $21 from $25 once our 15% discount has been applied. For those staying in the country longer, the 15-day unlimited data plan now costs $33, down from the usual $39. Anyone lucky enough to be in Japan for a full month can choose the 30-day unlimited data plan for $55 — down from $65.
Advertisement
There are tons of reasons to head to Japan, whether you’re checking out the local wrestling scene or hunting for some hard-to-find classic video games. And that’s before we get into the amazing scenery and architecture that’s just waiting to be explored. Whatever your plans, having to worry about data costs shouldn’t be part of them.
These data-only eSIMs are easy to set up and use, with a single Ubigi app handling data connections for over 200 destinations, including Japan. You only need to install one app no matter your destination, so there’s no scanning of QR codes or complicated setup here.
Why this deal matters
Whether you’re visiting Japan for a vacation or for work, you’re going to need to use your phone. Sure, you can roam using your carrier, but data costs can be extortionate and unpredictable. Buying a Ubigi eSIM takes the guesswork and worry out of using your phone abroad, and saving 15% is just the icing on the cake.
Oliver Haslam has been writing about phones, computers, games, and anything else that takes a battery or plugs in for more than he’d like to admit.
With a focus on mobile and laptops, Oliver is never too far away from whatever social network is trending today and is never short of an opinion to share.
See full bio
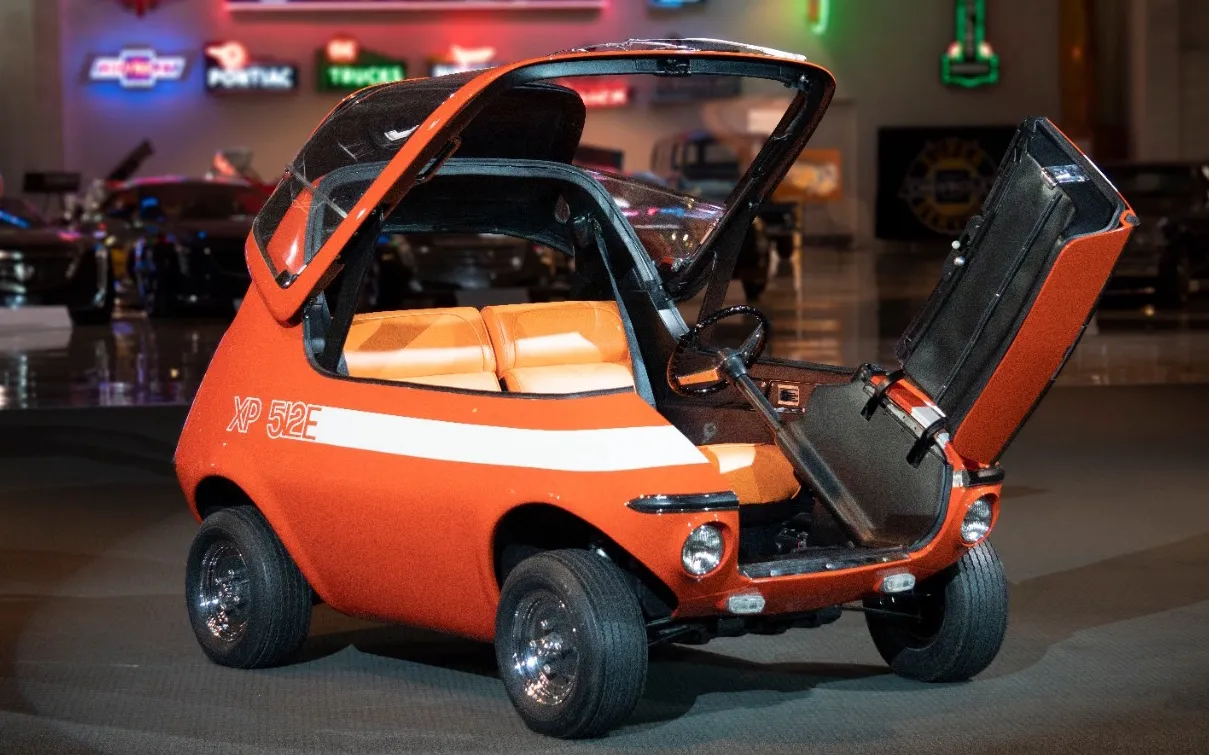
Electricity is the once and future drivetrain for automobiles, but until the advent of lithium batteries their capabilities were somewhat modest. One EV blip on the automotive timeline is the XP-512E commuter prototype by GM.
The 60s saw a wide variety of interesting experiments in the automobile space, and both GM and AMC were evaluating the possibilities of a return to electric cars for short journeys. GM wasn’t set on a particular drivetrain for their new experimental commuter cars, so the XP 512 became a trio with conventional, hybrid, and electric variants. Each car was a two seater with a fiberglass body and steel chassis. The canopy could lift and a small door in the front swung to the side for access to the cockpit. Some images from the time show the car without the canopy and just the rollbar, giving you a very small convertible (83″/2108 mm long).
Lead acid was the only viable traction battery until the 1990s, so the 1,250 lb vehicle was limited to a top speed of 30 mph and a range of 50 miles. GM was exploring a number of alternatives at the time including another blast from the automotive past, steam power, in an effort to reduce the issues of smog and air pollution that plagued cities beset by droves of V-8 powered sedans. While the XP-512E and the AMC Amitron never made it to production, they’re an interesting reminder that technologies that seem infeasible today may just need to bake a bit longer.
Meta’s newest smart glasses are an iterative, expensive update.
Meta
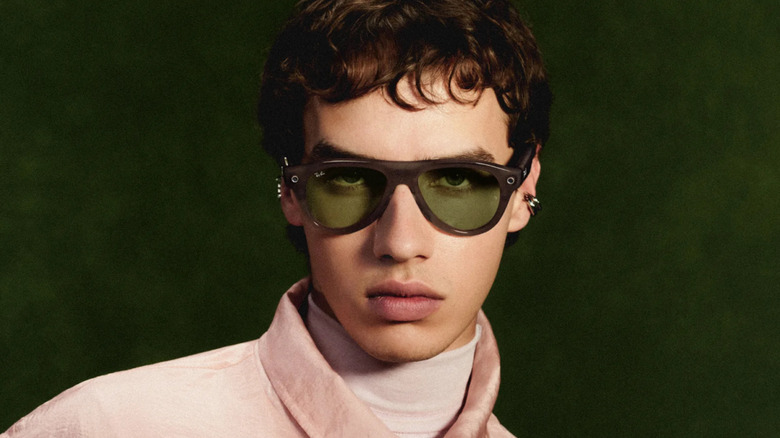
Meta announced a slew of new smart glasses at Meta Connect 2026, including its first camera-free options, but the company’s Ray-Ban Meta models remain the flagship. The Ray-Ban Meta Gen 3 carry over many of the improvements introduced in smaller updates over the last year, like the more prescription-friendly Ray-Ban Meta Optics or the affordable Meta Glasses, with new features that mostly rely on software rather than reinvented hardware.
Other than new colors and frame options, it’s hard to tell how the Ray-Ban Meta Gen 3 glasses differ from the Ray-Ban Meta Gen 2, unless you really dig into the specs. And you kind of need to, since understanding those differences is the only way to justify the new $449 starting price.
Advertisement
The Ray-Ban Meta Gen 3 last longer and listen better
The biggest changes Meta introduced to the Gen 3 are a longer battery life and the addition of more microphones. The Ray-Ban Meta Gen 3 lasts up to 9 hours on a charge — one hour more than the Gen 2 — and up to 50 hours with its charging case, two hours more than the Gen 2’s 48 hours. In day-to-day usability this might not make a huge difference, especially when compared to the 12 hours of battery life the company is promising on the Ray-Ban Meta Audio. We’ll need to do a full review of the glasses to see what the battery life improvements mean in real-world use.
The Gen 3’s six-mic array, one more mic than what Meta offered on the Gen 2, is a similarly modest change. Meta says adding the extra mic and redesigning the microphone layout on the Gen 3 model has allowed for better background noise reduction for calls and AI interactions, but that will have to be tested to see if it’s meaningfully different. One way the new mic on the Gen 3 could allow it to stand out from the Gen 2 is support for listening to and recording Dolby Atmos spatial audio, a feature the company says is launching later in 2026.
Meta has also ported over the action button it introduced on the Ray-Ban Meta Optics and Meta Glasses to the Gen 3. The button can summon Meta AI, act as a capture button, or be assigned as a shortcut for a variety of other Ray-Ban Meta features. The Gen 2 features a capture button that only works with Meta’s camera features.
Advertisement
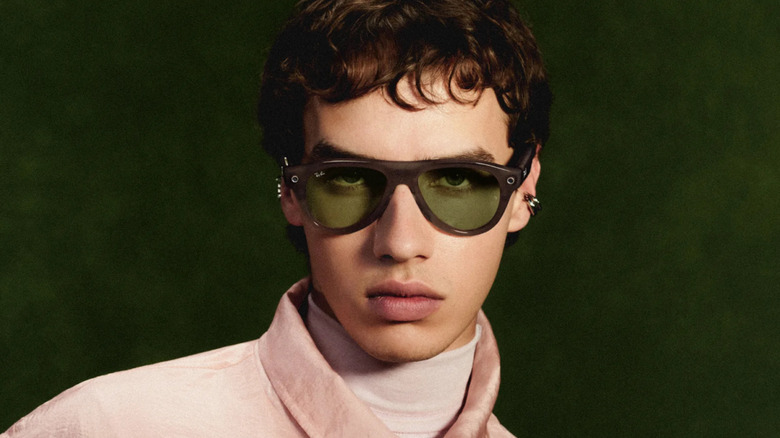
The Ray-Ban Meta Gen 3 are smaller and available in new styles
Meta
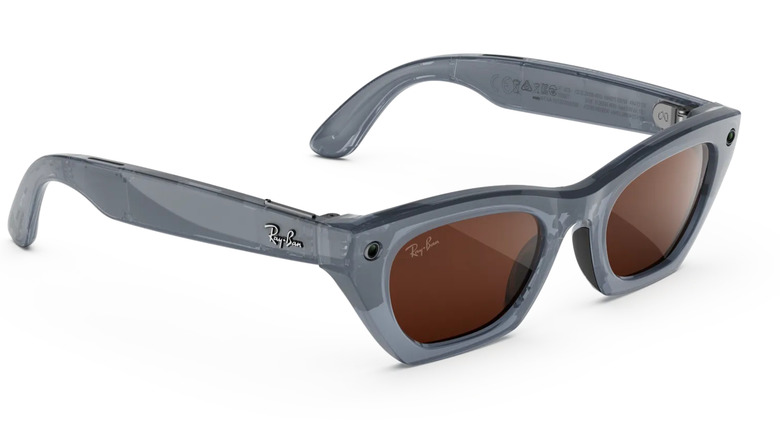
Smart glasses are fashion as much as they are anything else, so another way the Gen 3 are differentiated from the Gen 2 is the addition of two new frame styles. The Ray-Ban Meta (Gen 3) Aviator features lenses shaped like Ray-Ban’s classic aviator glasses, with thick frames in multiple translucent and tortoiseshell colors. For something a little less in-your-face, the Ray-Ban Meta (Gen 3) Zena comes with more of a cat-eye shape in translucent, black and tortoiseshell colors. The only frame shape that’s carrying over from the Gen 2 is the Wayfarer, Ray-Ban’s most well-known frame. That doesn’t mean Meta won’t port more Gen 2 styles over in the future given its penchant for mid-cycle refreshes, but for now most Gen 3 glasses will look pretty different.
They’re also, technically, a bit smaller. The best comparison point is the Ray-Ban Meta Wayfarer. The standard-fit Gen 2 model is 131mm from hinge to hinge, while the Gen 3 model is only 129mm. The temples on the Gen 3 model are also slightly shorter at 149mm compared to 150mm on the Gen 2. The relationship is reversed when it comes to weight, though, where the Gen 3 model is a slightly heavier 51.5 grams compared to the Gen 2’s 51 grams. Those changes might not be noticeable unless you have the glasses side-by-side, but it does suggest Meta is mostly trending towards smaller glasses overall.
Advertisement
Meta’s new software features are coming to older models
Software and AI access define the experience of using Ray-Ban Meta smart glasses. And the vast majority of features the company announced alongside its Gen 3 model will be available on older Gen 2 models, too. That includes using the smart glasses’ FDA-cleared hearing enhancement feature, interacting with the company’s Muse AI agent, and taking photos with the glasses’ new dynamic photo capture feature, which captures multiple shots at once and lets you pick the best framing.
Combined with the Ray-Ban Meta Gen 3’s higher starting price of $449, $70 more than the Ray-Ban Meta Gen 2, that makes justifying an upgrade hard. The company’s new smart glasses will likely be a great way to jump into Meta’s growing ecosystem, but if you can buy a used Gen 2 pair (assuming you don’t need a prescription) you’ll likely get a better deal.
Watch the Laver Cup 2026 live streams as the ninth edition of the tournament gets underway on 25 September at the O2 Arena in London.
Yannick Noah and Andre Agassi will serve as team captains once again this year, returning from the previous year. Last year’s winners were Team World, as they defeated Team Europe 15–9 to earn their third title. Each team has confirmed six participants for the tournament in the United Kingdom.
Acting as tennis’ version of the Ryder Cup, the competition sees six players from Team World face off against six players from Team Europe. There are nine singles matches and three doubles matches, giving 12 matches in total, with each day seeing four matches take place.
Advertisement
Unlike a normal tournament, players aren’t simply knocked out after losing, on Friday, a win is worth one point, on Saturday a win is worth two points and on Sunday a win is worth three points. With 12 matches taking place, there are 24 total points available. The winner is the team that amasses the most points across the three days.
Here’s how to watch the Laver Cup 2026 from anywhere in the world. We’ve also listed the the players, recent winners and prize money below.
Can you watch the Laver Cup 2026 for FREE?
Yes. Free Laver Cup 2026 coverage is being provided by RTVE in Spain and onL’Équipe in France
Advertisement
Traveling abroad right now? You can use a VPN to watch the Laver Cup 2026 for free as if you were right at home.
Use a VPN to watch Laver Cup 2026 live streams
A VPN is handy piece of software that can make your device appear as if it’s back in your home country, so you can unlock your usual service. The best VPN right now? We recommend NordVPN – it does everything and comes with up to 75% off.
Advertisement
How to watch Laver Cup 2026 live streams in the US
Laver Cup 2026 coverage is being provided by Tennis Channel in the US.
Tennis Channel which has US broadcast rights for the US, starts their subscription plan pricing at $11.99/month for full streaming access.
You can also access the Tennis Channel via cord-cutting subscription with all of Sling, YouTube TV and Fubo having it with their sports add-on packages.
Outside of the US? Use a VPN while you’re traveling away from home to unlock your stream.
Advertisement
How to watch Laver Cup 2026 live streams in the UK
(Image credit: Other)
In the UK, live Laver Cup 2026 coverage is being provided by Sky Sports.
Sky Sports packages start at £35/month with £20/month pricing available for those who are already customers. You can also tune in via a NOW Sports membership that carries the Sky Sports channels.
If you’re out of the UK but still want to tune in, explore the VPN route set out above, which will help you access your accounts from anywhere.
Advertisement
How to watch Laver Cup 2026 live streams in Australia
(Image credit: free)
Stan Sport will have exhaustive coverage of all three days of the tournament. Stan Sport costs AU$20/month on top of a Stan subscription, which itself starts at AU$9.99/month.
Not in Australia right now? You can simply use a VPN like NordVPN to watch all the action as if you were back home.
Advertisement
How to watch Laver Cup 2026 live streams in New Zealand
The Laver Cup 2026 will be shown exclusively in New Zealand on Sky Sport.
You can access Sky Sport through satellite TV or get a live stream, with the Sky Sport Now subscription service starting at NZ$29.99 per day or NZ$59.99 per month.
Not in New Zealand right now? You can simply use a VPN like NordVPN to watch all the action as if you were back home.
Advertisement
How to watch Laver Cup 2026 live streams in Canada
(Image credit: Other)
In Canada, the Laver Cup 2026 is exclusive to TSN.
If you don’t have cable, the TSN Plus streaming service costs CA$24.99/month or CA$249.99/year.
Outside Canada? The VPN route set out above will help you access TSN from anywhere in the world.
Advertisement
Laver Cup 2026 FAQs
What is the Laver Cup 2026?
Laver Cup 2026: Explained
The Laver Cup is a unique team tennis competition that sees some of the world’s best players go head-to-head as part of either Team Europe or Team World.
First held in 2017, the event was created by Roger Federer and his management company, TEAM8, in partnership with Tennis Australia and the ATP. It is named after Australian tennis legend Rod Laver, who is widely regarded as one of the greatest players in the history of the sport.
Advertisement
Unlike the four Grand Slam tournaments, where players compete individually, the Laver Cup is a team event. Six players represent Team Europe, while six players represent Team World. The teams are led by captains, with legendary former players often taking charge. For 2026, Yannick Noah is captaining Team Europe, while Andre Agassi is leading Team World.
The competition takes place over three days, with four matches played each day. There are singles and doubles matches throughout the weekend, with players representing their respective teams rather than competing for individual ranking points.
One of the most distinctive aspects of the Laver Cup is its scoring system. Matches become increasingly valuable as the weekend progresses.
On Friday, each match win is worth one point. On Saturday, a win is worth two points, while Sunday’s matches are worth three points each. With 12 matches scheduled across the three days, there are 24 points available in total.
Advertisement
The first team to reach 13 points wins the Laver Cup.
Who is competing at the 2026 Laver Cup?
Confirmed: Laver Cup 2026 players
Team Europe
1. Carlos Alcaraz 2. Alexander Zverev 3. Flavio Cobolli 4. Rafael Jodar 5. Jakub Mensik 6. Casper Ruud
Advertisement
Team World
1. Taylor Fritz 2. Alex de Minaur 3. Learner Tien 4. Alexander Bublik 5. Brandon Nakashima 6. Francisco Cerúndolo
Who are the recent Laver Cup winners?
Past winners
2017 Prague 🇨🇿 🇪🇺 Team Europe (15–9)
Advertisement
2018 Chicago 🇺🇸 🇪🇺 Team Europe (13–8)
2019 Geneva 🇨🇭🇪🇺 Team Europe (13–11)
2020 Not held due to Covid-19
2021 Boston 🇺🇸 🇪🇺 Team Europe (14–1)
Advertisement
2022 London 🇬🇧 🌎 Team World (13–8)
2023 Vancouver 🇨🇦 🌎 Team World (13–2)
2024 Berlin 🇩🇪 🇪🇺 Team Europe (13–11)
2025 San Francisco 🇺🇸 🌎 Team World (15–9)
Advertisement
What is the Laver Cup 2026 schedule?
Friday 25 September
13:00, day session: match 1 (singles)
Followed by: match 2 (singles)
19:00, night session: match 3 (singles)
Followed by: match 4 (doubles)
Saturday 26 September
13:00, day session: match 5 (singles)
Followed by: match 6 (singles)
19:00, night session: match 7 (singles)
Followed by: match 8 (doubles)
Sunday 27 September
12:00, day session: match 9 (doubles)
If required, followed by: match 10 (singles)
If required, followed by: match 11 (singles)
If required, followed by: match 12 (doubles)
What is the Laver Cup 2026 prize money?
For the 2026 Laver Cup, the total prize purse is US$1.5 million.
The official Laver Cup confirms that each of the six players on the winning team receives $250,000, while there is no prize money for the losing team.
But there is another payment, as the players also receive an appearance fee, which is separate from the $250,000 prize money.
That fee is determined by each player’s ATP singles ranking immediately after the 2026 French Open. So the players aren’t simply playing for the $250,000 — everyone receives an appearance fee for taking part, regardless of whether their team wins or loses.
Advertisement
For example, Carlos Alcaraz, who was ranked No. 2 after Roland-Garros, receives the highest appearance fee among the 2026 players, according to Sporting News.
We test and review VPN services in the context of legal recreational uses. For example: 1. Accessing a service from another country (subject to the terms and conditions of that service). 2. Protecting your online security and strengthening your online privacy when abroad. We do not support or condone the illegal or malicious use of VPN services. Consuming pirated content that is paid-for is neither endorsed nor approved by Future Publishing.
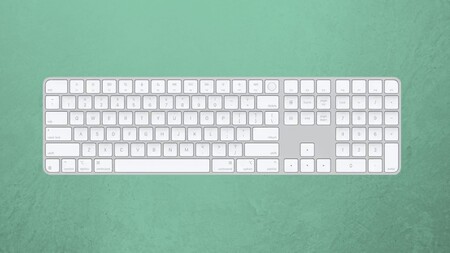
Waiting until tomorrow means paying whatever this keyboard usually costs, which makes tonight the only window left to get Touch ID and a full numeric keypad locked in at $149.99 before the listing resets for good.
Advertisement
Touch ID built into the keyboard means unlocking a Mac or approving an online payment takes a single tap instead of typing out a password every time a screen locks itself during the working day.
That same keyboard has built a reputation among its own owners for a remarkably comfortable typing feel, with reviewers consistently pointing to the precision of every keystroke as the reason they keep coming back to it.
Advertisement
The extended layout adds a full numeric keypad alongside dedicated document navigation controls, turning what would otherwise be a simple typing accessory into something built for spreadsheets, finance work and long documents, with full-size arrow keys thrown in for gaming too.
Advertisement
It runs wirelessly on a rechargeable battery that lasts about a month between charges, and pairs with a Mac automatically the moment it switches on. That leaves a keyboard that is simply ready every time it is picked up, with nothing to plug in first.
The same keyboard pairs just as easily with an iPad or an iPhone, which means one purchase covers a Mac at the desk and a tablet or phone used everywhere else in the house too.
For anyone who spends real time typing, browsing spreadsheets, or logging into a Mac throughout the day, tonight is the moment to get the Magic Keyboard with Touch ID for $149.99 before the deal disappears.
Householders are getting free hot water from Heata, a company that installs rented servers in homes
Heat generated by the servers is passed to the water supply for showers and hot taps
Heata pays for any additional electricity used, ensuring homeowners win and businesses have their data stored safely
What happens to waste heat from servers? In a server room or data center, the heat is removed through industrial cooling systems and exhausted. But what if it could be reused? What if that heat could be used to keep domestic heating bills down?
Heata is one of several companies across the UK and Europe delivering solutions to server space and heating costs. Domestic waste-heat use appears to be a growing industry, and offers homeowners the chance to cut bills significantly while giving businesses low-cost server space.
The idea is simple: install a server in the home, rent the server space to businesses, and donate the heat generated by compute processes to the home, reducing their energy bills in the process.
Latest Videos FromTechRadar
Advertisement
How servers heat homes
If you’ve worked in a server room, you know how hot things can get, particularly if there is a problem with the extraction system. This is the starting point for these so-called “data furnaces” where the heat from an active compute unit is used to heat water. Heata say that the waste heat from a single data center could provide hot water for around 30,000 homes, which puts it into context.
Their model is simple: a compute model is attached to a hot water cylinder, heating the water and reducing the requirement for gas heating. Homes need fast broadband to provide fast data routing to the compute module, and Heata pays for additional electricity used by the mini server. It aims to provide around 80% of heat for the heating system, reducing domestic gas bills considerably.
Like Heata, Wales-based Thermify is looking for trial customers. Their system is a little different, relying on a HeatHub, within which a cluster of Raspberry Pi Compute Modules are generating data solutions and heat.
Compatible boilers
While the having a server or compute unit in a remote part of your property to assist in heating the water – essentially using the same electricity twice – might seem an attractive option, it does not come without shortcomings. For example, there is the issue of compatibility.
Sign up to the TechRadar Pro newsletter to get all the top news, opinion, features and guidance your business needs to succeed!
Advertisement
With the Heata example, only vented hot water cylinders can be used. Unvented, pressurised cylinders are not compatible. Other providers of similar data-to-heat services can provide the heated water in other ways – for example, Thermify uses its HeatHub to replace a home’s boiler.
With no new homes permitted to have gas boilers installed from 2027 onward, an alternative to hot water is needed, and companies turning data into heat could be the best solution.
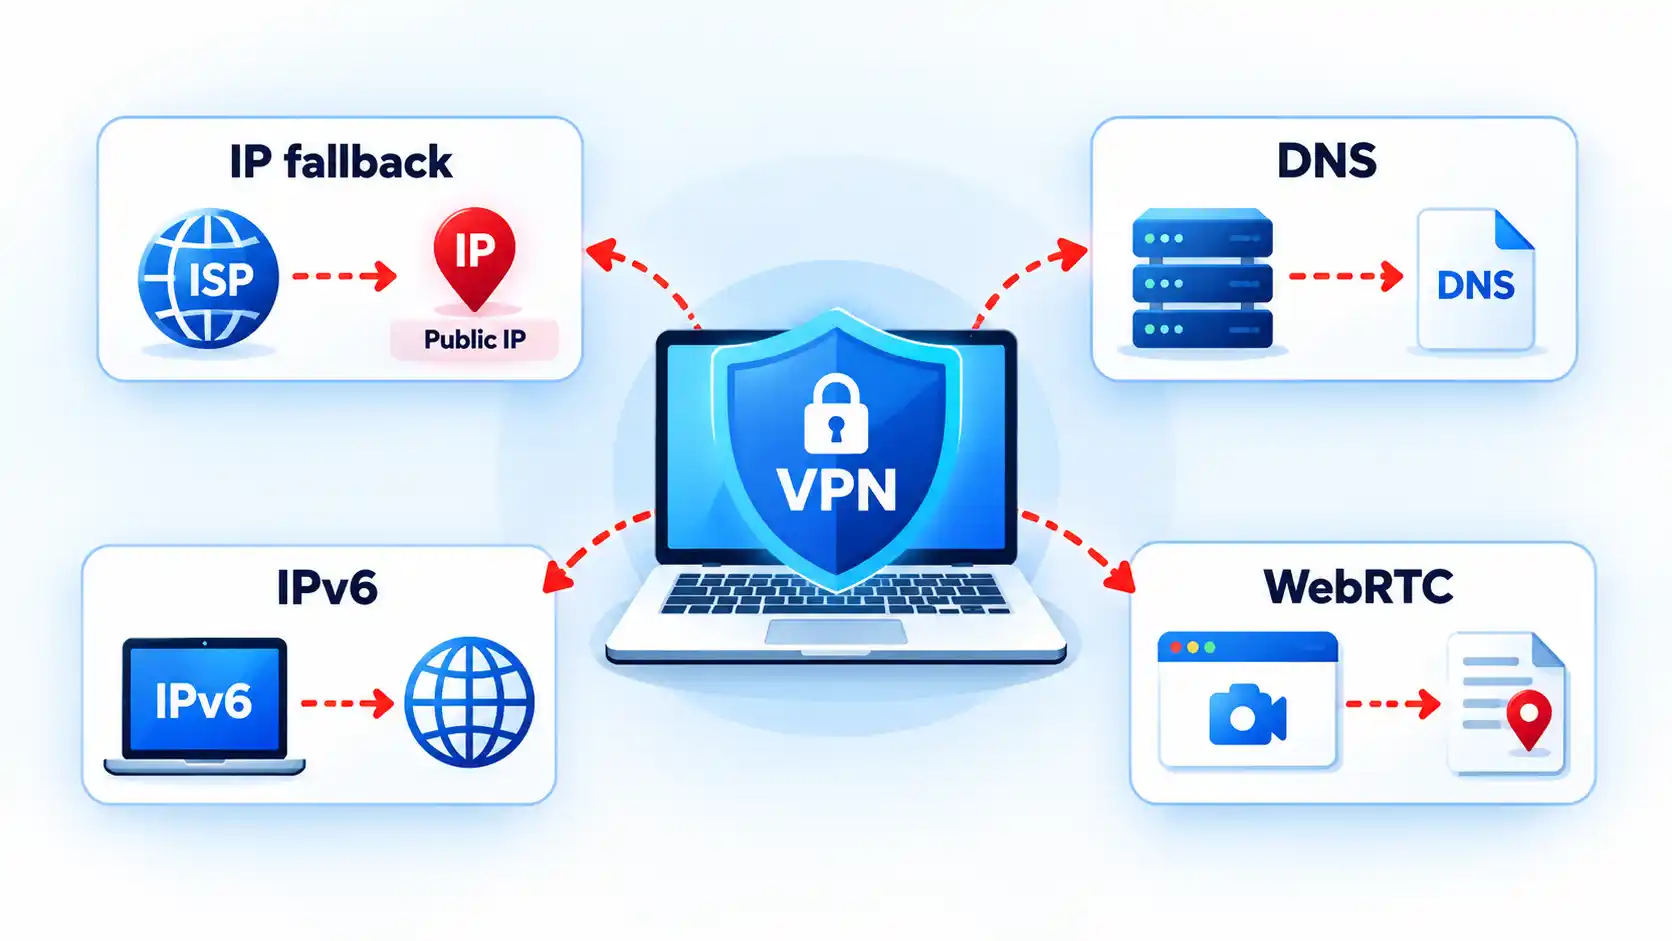
When a VPN disconnects, traffic may either stop or fall back to your normal internet connection. A working kill switch is designed to block that fallback, while a fail-open setup may let new traffic use your ordinary network route and public IP address.
Quick Take
A VPN disconnect does not automatically mean data leaked. The result depends on what networking policy takes over after the tunnel fails.
A fail-open configuration permits affected traffic to use ordinary networking, while fail-closed protection blocks that fallback until VPN protection returns.
A kill switch does not stop the VPN from disconnecting. It controls whether covered traffic can leave outside the protected tunnel.
DNS, IPv6, split-tunnel, and browser-related exposures can occur separately from a complete VPN disconnect, so they should not all be treated as the same failure.
What Happens the Moment the VPN Tunnel Drops
A VPN normally gives selected network traffic a route through an encrypted tunnel to a VPN server. When that tunnel disappears, the operating system and VPN software have to determine what should happen to traffic that would normally use it.
One possible outcome is fail open. This means ordinary networking is permitted again. New connections may use the device’s Wi-Fi, Ethernet, or mobile connection directly, just as they would if the VPN were not active. Websites reached through those new connections may then receive the public IP address associated with your normal internet connection rather than the VPN server.
The opposite behavior is fail closed. Instead of allowing protected traffic to fall back to the normal route, the device blocks it until the VPN connection returns or the blocking policy is deliberately disabled.
Suppose a laptop is connected to home Wi-Fi and its browser traffic is leaving through a VPN server. If the VPN tunnel fails, a fail-open configuration may let the browser establish its next connection directly through the internet service provider. With fail-closed protection, that new connection should fail rather than silently bypass the tunnel.
Advertisement
The behavior of an existing connection can be less predictable. Applications may retry requests, create a new connection, wait for the VPN to return, or time out. The practical privacy question is therefore whether traffic that was supposed to remain protected can establish a usable path outside the VPN after the tunnel is lost.
What a VPN Kill Switch Actually Does
A kill switch does not keep the VPN tunnel alive. Its job is to restrict networking when that tunnel is unavailable.
Mozilla describes its implementation as blocking the device’s network connection if Mozilla VPN becomes unstable or drops, with the aim of preventing the local IP address from being exposed. Mozilla’s kill-switch documentation is one example of fail-closed behavior implemented by a VPN application.
The enforcement can also come from the operating system. Android supports an Always-on VPN setting and a separate Block connections without VPN control. When configured together, Android can prevent connections that do not use the selected VPN.
Advertisement
Automatic reconnection is related but different. A reconnect feature tries to restore the VPN tunnel. A kill switch determines what traffic is permitted while that tunnel is missing. A VPN product can implement both, one, or neither depending on the platform and configuration.
Infoi
If your internet stops working immediately after a VPN failure, that may be the kill switch doing exactly what it was designed to do. Confirm the VPN and kill-switch state before treating the loss of connectivity as a separate network fault.
Standard Kill Switch vs Persistent Blocking
“Kill switch” does not describe one universal policy. Some implementations respond primarily to an unexpected VPN failure, while others enforce a VPN-required state even after a deliberate disconnect or restart.
Advertisement
Proton VPN, for example, currently distinguishes a standard mode from an advanced mode. Its standard kill switch is designed to activate when the VPN connection drops unexpectedly, while its advanced kill switch prevents internet access whenever Proton VPN is not connected and can remain active across restarts on supported platforms. These are Proton-specific implementation details, not universal VPN terminology.
The table below shows the conceptual distinction. Exact behavior still depends on the VPN application, operating system, and policy configuration.
Typical differences between disconnect-triggered and persistent VPN blocking
Behavior
Disconnect-triggered protection
Persistent VPN-required policy
Unexpected tunnel failure
Designed to block protected traffic when the VPN unexpectedly drops.
Blocks covered traffic because no permitted VPN tunnel is available.
Deliberate disconnect
May permit ordinary networking, depending on the implementation.
Normally continues blocking until the policy is disabled or the VPN reconnects.
Restart or reboot
Persistence depends on the product and platform.
Can remain enforced across restart when implemented as a persistent policy.
Intentional internet use without the VPN
May be possible after deliberately disconnecting.
Requires disabling the VPN-required policy or changing its configuration.
This distinction is why pressing a VPN application’s Disconnect button is not always a valid test of an ordinary kill switch. Some products intentionally interpret a manual disconnect as permission to resume normal networking.
A VPN Disconnect Is Not the Only Kind of Leak
A complete tunnel failure is only one way traffic can end up somewhere you did not intend. A VPN may appear connected while a particular protocol, resolver, application, or address family follows a different path.
Advertisement
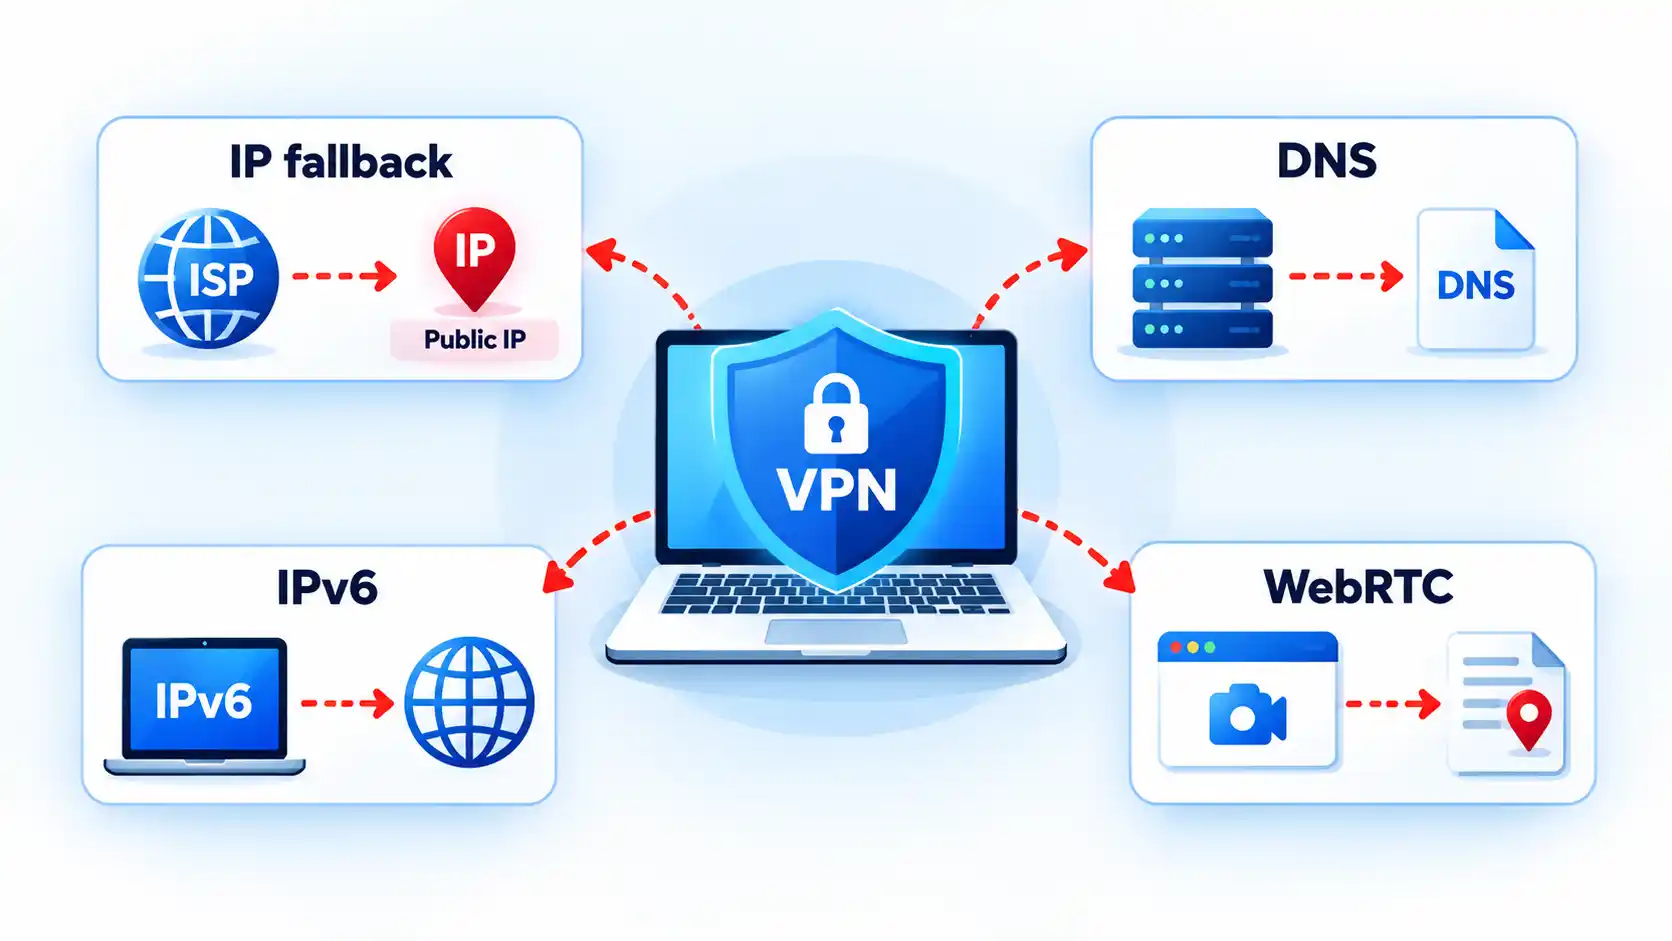
Public IP exposure after fallback
If the VPN tunnel disappears and ordinary routing resumes, a new connection can leave through the underlying internet connection. The remote service may then see the public IP address assigned to that normal route.
This is the failure people commonly mean when they say a kill switch prevented an “IP leak.” More precisely, traffic that was expected to remain protected obtained an ordinary route after the VPN stopped carrying it.
DNS leakage
The Domain Name System, or DNS, translates names such as example.com into network addresses. A DNS leak occurs when queries that were intended to follow the VPN’s protected DNS path instead use another resolver or network path outside that intended configuration.
Not every DNS server different from the VPN provider’s own resolver is automatically evidence of a leak. Some users deliberately configure another encrypted or third-party DNS service. The useful comparison is between the DNS path you intended and the one the device actually uses.
Advertisement
IPv6 bypass
Many networks support both Internet Protocol version 4, or IPv4, and Internet Protocol version 6, or IPv6. That dual-stack design can expose a routing mismatch if VPN software protects one address family but fails to apply the intended policy to the other.
The IETF’s RFC 7359 analysis of dual-stack VPN leakage describes traffic intended for a tunnel escaping through an unprotected IPv6 path when VPN software fails to handle IPv6 correctly. The document dates from 2014, so it should not be treated as evidence that current VPN applications generally have this defect.
The RFC’s IESG note also cautions that the broader leakage problem is not unique to IPv6. Similar exposure can arise whenever policy permits another unencrypted interface or route, including some split-tunnel configurations.
Browser and WebRTC address exposure
Browser networking creates a separate category of address information. Web Real-Time Communication, or WebRTC, uses Interactive Connectivity Establishment, or ICE, candidates when discovering possible paths for peer-to-peer communication.
Advertisement
MDN documents that an ICE candidate can contain the IP address associated with that candidate’s source. Whether the address revealed is relevant to your VPN privacy model depends on the browser, candidate type, VPN implementation, and network configuration. The presence of WebRTC address information does not by itself prove that the entire VPN tunnel failed.
These failure modes are related enough to examine together, but they should not be collapsed into one diagnosis. IP, DNS, IPv6, and WebRTC leaks have different causes and require different verification methods.
Split Tunneling Changes What “Leak” Means
Traffic outside the VPN is not necessarily leaking if you deliberately configured it to stay outside.
Split tunneling means only selected applications or destinations use the VPN while other traffic follows the device’s normal network path. Android’s per-app VPN controls, for example, can restrict VPN use to an allowed set of applications or deliberately exclude applications from it.
Advertisement
Imagine that a browser is configured to use the VPN but a game launcher is intentionally excluded. Seeing the normal public IP from the game launcher may be expected split-tunnel behavior. Seeing that same fallback from the protected browser after the tunnel fails would be a different result.
This is why a leak test should start by establishing what was supposed to be inside the tunnel. Without that baseline, expected exclusions can be mistaken for failures.
Kill switches and split tunneling can also interact differently across products. Proton documents that the combination is unsupported on most of its platforms, while its Windows app can use kill-switch protection with split tunneling so protected applications remain blocked if the VPN disconnects. Proton’s split-tunneling documentation illustrates why this behavior must be checked on the exact product and platform rather than assumed universally.
How to Test Whether Your Kill Switch Actually Works
A useful test compares the normal route, the protected route, and behavior during a VPN interruption. Use only harmless traffic because the purpose of the test is to discover whether unprotected fallback is possible.
Advertisement
Prerequisites
Stop sensitive uploads, account activity, private messages, file transfers, and other traffic you would not want exposed during a failed test.
Identify where your VPN application or operating system exposes its kill-switch or non-VPN blocking setting.
Use a harmless public-IP or ordinary connectivity check that you can repeat before and after the tunnel interruption.
Check your VPN provider’s documentation to determine which type of interruption is supposed to activate the protection mode you are testing.
Record the normal state. With the VPN disconnected and no persistent blocking policy enabled, record the public IP address or other harmless network result shown through your normal internet connection. This is your fallback baseline.
Connect the VPN. Establish the VPN normally, then repeat the same check. Confirm that the result now reflects the VPN route rather than the baseline connection before continuing.
Confirm the protection mode. Verify that the kill switch or operating-system blocking control you intend to test is enabled. If the product has both disconnect-triggered and persistent modes, record which mode is active.
Create only harmless observable traffic. Keep an ordinary webpage or non-sensitive connectivity check ready so you can tell whether networking continues. Do not use confidential logins, cloud uploads, private messages, or other sensitive transfers as test traffic.
Trigger the supported failure condition. Use the provider’s documented test or failure method when one is available. Do not assume that clicking Disconnect tests a standard kill switch, because some implementations intentionally permit normal networking after a deliberate disconnect. Also do not disable Wi-Fi, Ethernet, or mobile data as a substitute for a VPN-tunnel failure, because removing the underlying internet connection cannot show whether traffic would have fallen back outside the tunnel.
Observe the fallback behavior. While the VPN tunnel is unavailable but the underlying internet connection still exists, try the harmless connectivity check. For a fail-closed configuration covering that traffic, ordinary internet access should be blocked rather than silently returning through the baseline route.
Reconnect and verify recovery. Restore the VPN connection, confirm that ordinary connectivity returns, and repeat the public-IP check. The observed address should again correspond to the VPN route rather than the baseline connection.
Verify the result
Traffic that was supposed to remain VPN-protected did not continue through the ordinary route while the tunnel was unavailable.
The underlying internet connection remained available during the failure test, so blocked traffic can reasonably be attributed to VPN protection rather than simply losing Wi-Fi, Ethernet, or mobile connectivity.
Internet access returned normally after the VPN re-established its protected route.
The post-reconnect public IP result again reflected the VPN endpoint rather than the normal baseline address.
Troubleshooting Kill-Switch and Reconnect Problems
The symptom usually indicates whether to investigate the kill-switch policy, the VPN connection itself, split tunneling, or the underlying network.
Internet access continues when the VPN drops
First confirm that a kill switch or equivalent blocking policy is enabled and that the affected application is supposed to use the VPN. Also check how the failure occurred. Some standard kill switches protect unexpected connection loss but intentionally allow normal networking after a manual disconnect. If split tunneling is enabled, verify that the application was not deliberately excluded from VPN protection.
Internet stays blocked after the VPN reconnects
Confirm that the VPN has actually completed reconnection rather than remaining in a connecting or authentication state. Persistent blocking policies can correctly keep traffic disabled while no valid tunnel is available. If the VPN reports connected but traffic remains blocked, restart the VPN application and check its current kill-switch state before changing unrelated router or DNS settings.
The VPN says connected, but websites still do not loadOnly some apps keep working after the VPN fails
Check split-tunneling and per-app VPN rules before assuming the kill switch failed. An application deliberately excluded from the VPN may be expected to continue using the normal network, while an application assigned to the protected tunnel should follow the VPN’s applicable failure policy.
Nothing connects even after you intentionally turn the VPN off
A persistent or always-required VPN policy may still be active. Reconnect the VPN or deliberately disable that policy using the controls provided by the VPN application or operating system. Do not start deleting network adapters or resetting the entire network until you have ruled out intentional fail-closed enforcement. If the VPN itself reports connected but networking remains unavailable, VPN connected but no internet is a different diagnostic state from a simple tunnel disconnect.
Advertisement
Platform Differences That Matter
Android
Android provides several VPN controls at the operating-system level. Google’s current documentation says Android 7.0 and later can use Always-on VPN, and compatible configurations can enable Block connections without VPN. That combination can create fail-closed behavior without relying solely on an application’s own interface.
Android also supports per-app VPN rules. If applications are placed on an allowed list, only those applications use the VPN. Other applications can use normal system networking unless non-VPN connections are also blocked. With blocking enabled, applications outside the permitted VPN set can instead lose network access. The interaction is configuration-dependent, so observing one application’s behavior does not necessarily describe the whole device.
Apple devices
Apple supports several distinct VPN deployment models, including VPN On Demand, per-app VPN, and managed Always On VPN. They should not be treated as interchangeable names for one consumer kill-switch feature.
For managed Always On VPN configurations, Apple documents that all IP traffic can be tunneled through the organization’s VPN infrastructure and that all IP traffic is dropped when the required Always On VPN tunnels are not up. This is a strong example of operating-system-enforced fail-closed behavior, but it does not establish that every third-party consumer VPN application on an Apple device behaves the same way.
Desktop VPN clients can implement blocking in different ways. Some rely on operating-system filtering or firewall facilities, while others use routing or interface mechanisms.
The larger distinction between Always-On VPN and a kill switch is whether the system is trying to maintain a required VPN state, block traffic when that state is unavailable, or do both.
Advertisement
Bottom Line
What happens after a VPN disconnects depends less on the word “VPN” than on the policy that follows the failure. A fail-open configuration can permit subsequent traffic to use the normal network path, while fail-closed enforcement blocks affected traffic until VPN protection returns.
A kill switch is therefore a traffic-control feature, not a guarantee that the VPN will never fail. Split tunneling, DNS routing, IPv6 handling, browser networking, and platform-specific rules can create separate exposure paths even when the main tunnel appears healthy. The reliable approach is to understand what should be protected, verify that behavior with harmless traffic, and interpret the result against the exact VPN and operating-system configuration in use.
When the AI apocalypse becomes regular dinner-table conversation, you know we’ve reached the freakout stage. Rogue AI agents are hacking into competitors. Former Big Tech employees are posting Skynet-style warnings on social media. CEOs are crying for help in ways that have made this once-wonky tech issue a frontline political fight.
I still think many of the concerns outlined by the AI leaders themselves are massively self-serving — especially when their companies are soon to go public. But the growing list of AIscandals is real. And it tells us that the status quo for regulating this powerful new technology is not working.
The question now on everyone’s mind: Is any kind of global brake possible? What form of AI safety regime is practical, over the short term, when there is no trust between major governments? And what could possibly work when companies are loath to give up their secret sauce and are bent on domination in the global AI race?
Two major conversations are now playing out, in real time. On Wednesday, President Donald Trump welcomed Chinese President Xi Jinping to Washington for a three-day summit — part of which will be dedicated to AI risks. The same day, with the United Nations meeting for its annual General Assembly, heads of the world’s leading AI companies urged the UN to police the emerging technology, or risk potentially wiping out humanity. “We could lose control of the future to AI,” OpenAI’s boss, Sam Altman, bluntly told the UN’s Security Council.
Advertisement
Confronted with this collective freakout, it’s time to take a long, deep breath.
In fact, AI safety has been on a lot of policymakers’ minds for years now, gaining momentum after ChatGPT was introduced in 2022. Governments have held hearings, convened expert groups, and drafted their own outlines of how to keep it under control. These weren’t just idle listening exercises. They aren’t all well known to the wider public, but they yielded real plans.
Barring any breakthroughs this week, we already have a quasi-planetary shield against the potentially runaway technology. That’s the good news.
The bad news is that it’s not really up and running yet. It’s also not clear whether it will actually work. So what is it — and how can we fix it so we have a global system that responds in time to deal with the incredibly fast-moving threats from AI?
Advertisement
What the global AI patchwork looks like now
For the last four years, the most tech-savvy nations — and would-be AI leaders — have been running serious conversations about this exact AI safety threat. Some are in Congress and the White House; some at the UN, at the G7, and in other capitals.
I’ve been covering this closely as a global technology journalist, from my current perch at a think tank. Here’s what the landscape looks like:
There are national AI safety and security institutes, government-funded bodies whose job it is to kick the tires of AI companies’ latest products before they are let loose into the wild.
There are also voluntary commitments by companies, many of which have made their own pledges or developed joint standards, to protect elections from AI threats, stop the spread of AI-fueled deepfake imagery, and joint government-corporate efforts to bake safety into how the technology develops.
At the international level, there’s a G7-led reporting mechanism — embraced by the most important Western tech nations that allows AI giants to share how they are building their latest models, as well as create standards for how to reduce catastrophic risks.
An international scientific report provides a yearly update on risks posed by the most advanced AI systems, based on existing research, to help governments plan for the worst.
What’s missing from all that? What we currently lack — and what is needed between now and the end of 2026 — is a way to turn this cottage industry of AI safety mechanisms into a functioning, but crude, first-responder system when things suddenly go wrong.
The last four years have laid out a pathway, and some of the necessary systems even exist. But there’s no way to respond globally, and in real time, when an AI crisis hits — especially if such a possibly doomsday event cuts across countries already skeptical of each other.
Advertisement
This week’s US-China summit may be a step in the right direction. Under proposals outlined by American officials, Washington and Beijing could set up a hotline between US Treasury Secretary Scott Bessent and Chinese Vice Premier He Lifeng in case of an AI incident affected each country’s national security.
It’s still unclear if Trump’s meeting with Xi will lead to such progress. Chinese officials also have balked at Washington’s pleas for AI rules because, so far, Congress has failed to act, and China already has some of the world’s most stringent AI oversight.
For AI to be “safe,” this conversation will need to go beyond this week’s US-China summit. Relying just on Washington and Beijing — arguably the most important AI powers — would not solve the underlying problems, nor would it make other countries feel more comfortable.
What we need next, so it really saves us
Advertisement
I’ve been talking to AI safety experts and government officials, and it’s clear the missing piece is a way to activate this whole system in a crisis. Countries don’t all have to have the same AI safety policies, and they never will. But as with nuclear weapons — a similarly high-threat technology that the world found a way to contain — safety requires a rough global agreement on how to respond quickly when something goes terribly wrong.
What’s needed right now is a 90-day, opt-in rapid response mechanism that joins existing pieces of the AI safety puzzle together. I’ve pieced together some ideas about how it should work, and who needs to sign on. Granted, none of what I outline below is sufficient. But, together, they are more plausible than trying to negotiate a comprehensive global regime — let alone arrange another AI summit — while Washington, Beijing, and other national capitals disagree over what “AI safety” actually means.
All of these options are based on existing mechanisms, are derived from efforts that have worked in other policy areas, and provide a band-aid to the AI safety dilemma until a more durable solution can be negotiated.
First, developers, AI safety institutes, and regulators, from across different countries, should agree that when an incident occurs, it triggers a specific Chernobyl-style protocol. That would mean submitting a confidential report within a 72-hour period to a national designated responder and a small technical secretariat. It can build on the OECD’s AI Incidents Monitor, lead to a technical, multi-stakeholder confidential investigation into what went wrong, and, subsequently, the publication of an anonymized lessons-learned note.
Second, governments and developers can agree to publish common declarations related to safeguards, residual risks, escalation thresholds, and independent auditing before the release or upgrading of a next-generation model. It would use the G7 Hiroshima AI Process reporting framework as its base, and turn the current hodgepodge of corporate safety declarations and voluntary standards into a common minimum disclosure obligation. View it as similar to the collective bank stress tests after the 2008 global financial crisis. It can allow outsiders to truly compare models’ safety protocols without putting someone in charge of determining which company is doing it best.
Third, create a Cold War-style US-China AI safety hotline — but see it as an initial step that can later be opened to other countries. There are good reasons, in the long term, that Washington and Beijing should not be allowed to rule artificial intelligence between them, and the rest of the world should have a real seat at the table. But for now those are the two “great powers” in the tech conversation, and we can set that philosophical argument aside to create a standing, technically-informed direct line of communication for acute AI-risk incidents. Its remit is inherently narrow: prevent dangerous misunderstandings linked to serious model incidents, AI-enabled cyberattacks and/or alleged breaches of agreed safety commitments.
There are obvious limits to what I describe above. For one, it’s an inherently Western-centric view that primarily discounts global majority countries. It also places too much sway on existing institutions like the Organization for Economic Cooperation and Development, as well as on the US-China relationship. Other countries’ officials will legitimately balk at all three options, and rightly so.
But this is not about creating a vague, unenforceable UN-led mandate for AI safety. Nor is it about corralling the geopolitical cats to hammer out a global AI treaty. The options — a collective safety protocol and incident reporting protocol; common pre-release standards; and a US-China AI safety hotline — are inherently short-term. They are also based on existing efforts and those that have worked successfully for other policy areas.
Advertisement
There will be time to quibble about the future of AI safety. But now is not that time. The latest AI models are moving faster than many had expected, tech bosses are worried their creations are already out of control, and the window for action may be smaller than we all think.
What is required are practical steps to assuage people’s growing concerns amid heightened geopolitical tension, a lack of trust between governments and companies, and a need not to let the perfect get in the way of the good.
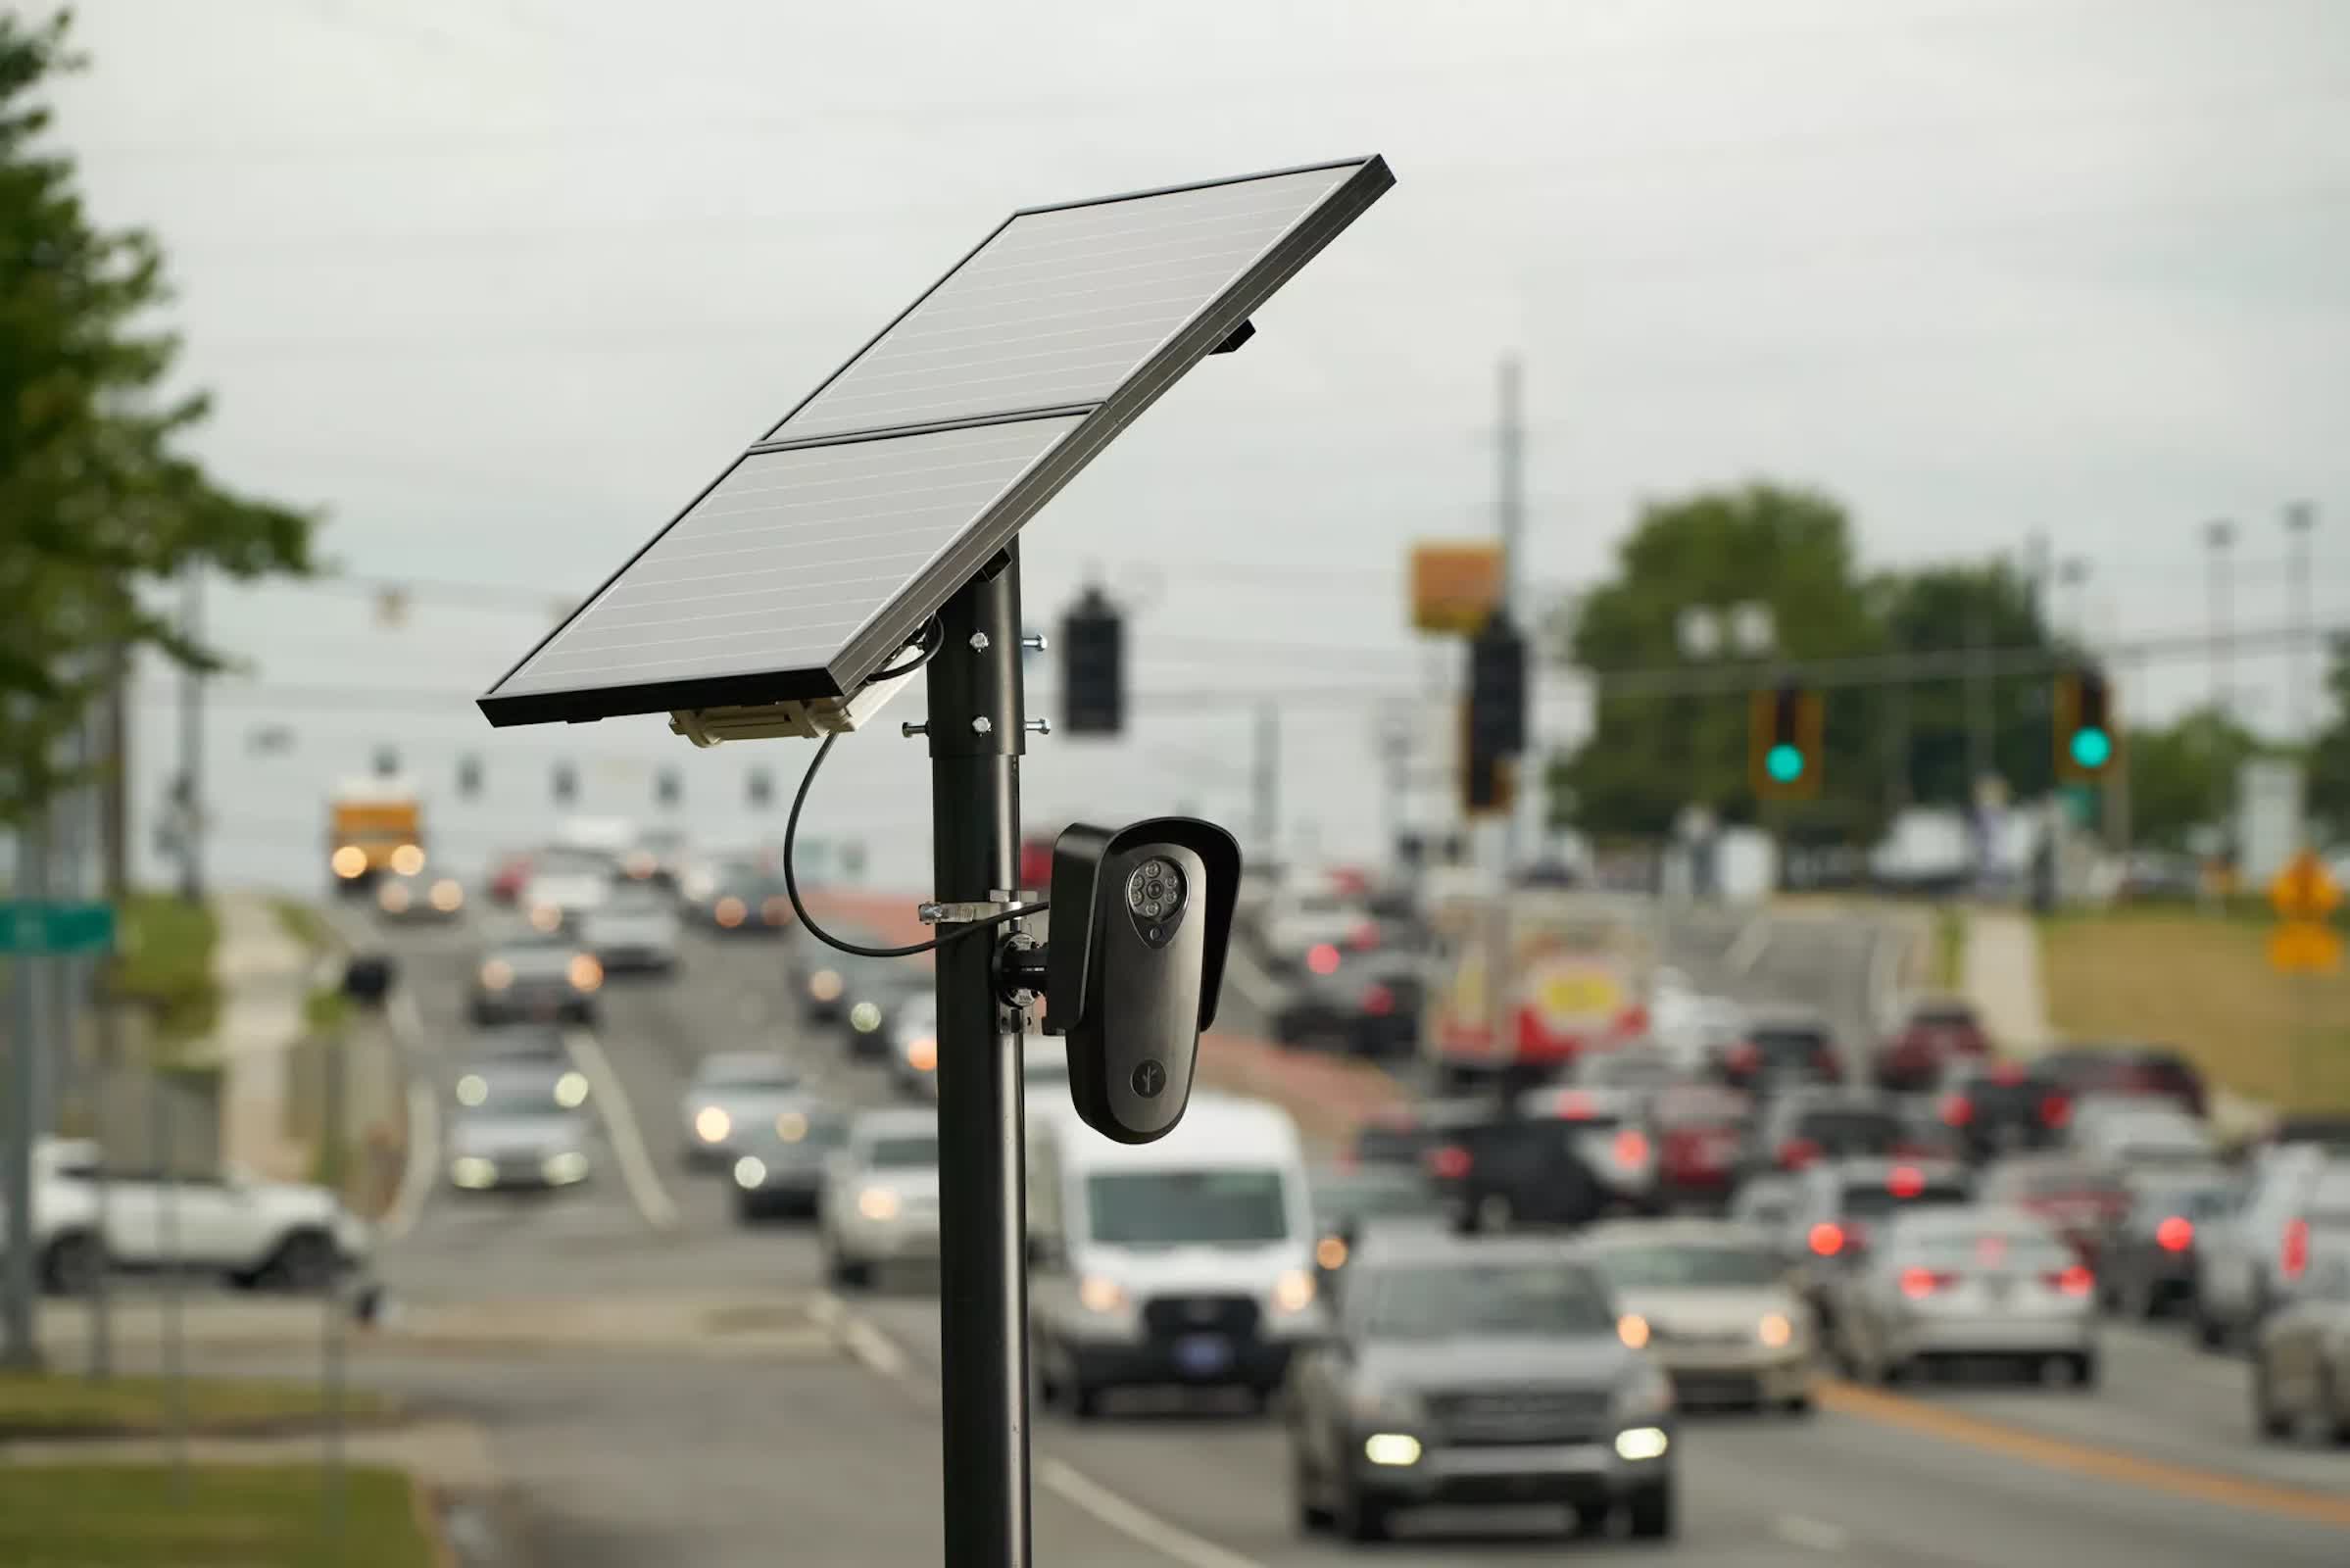
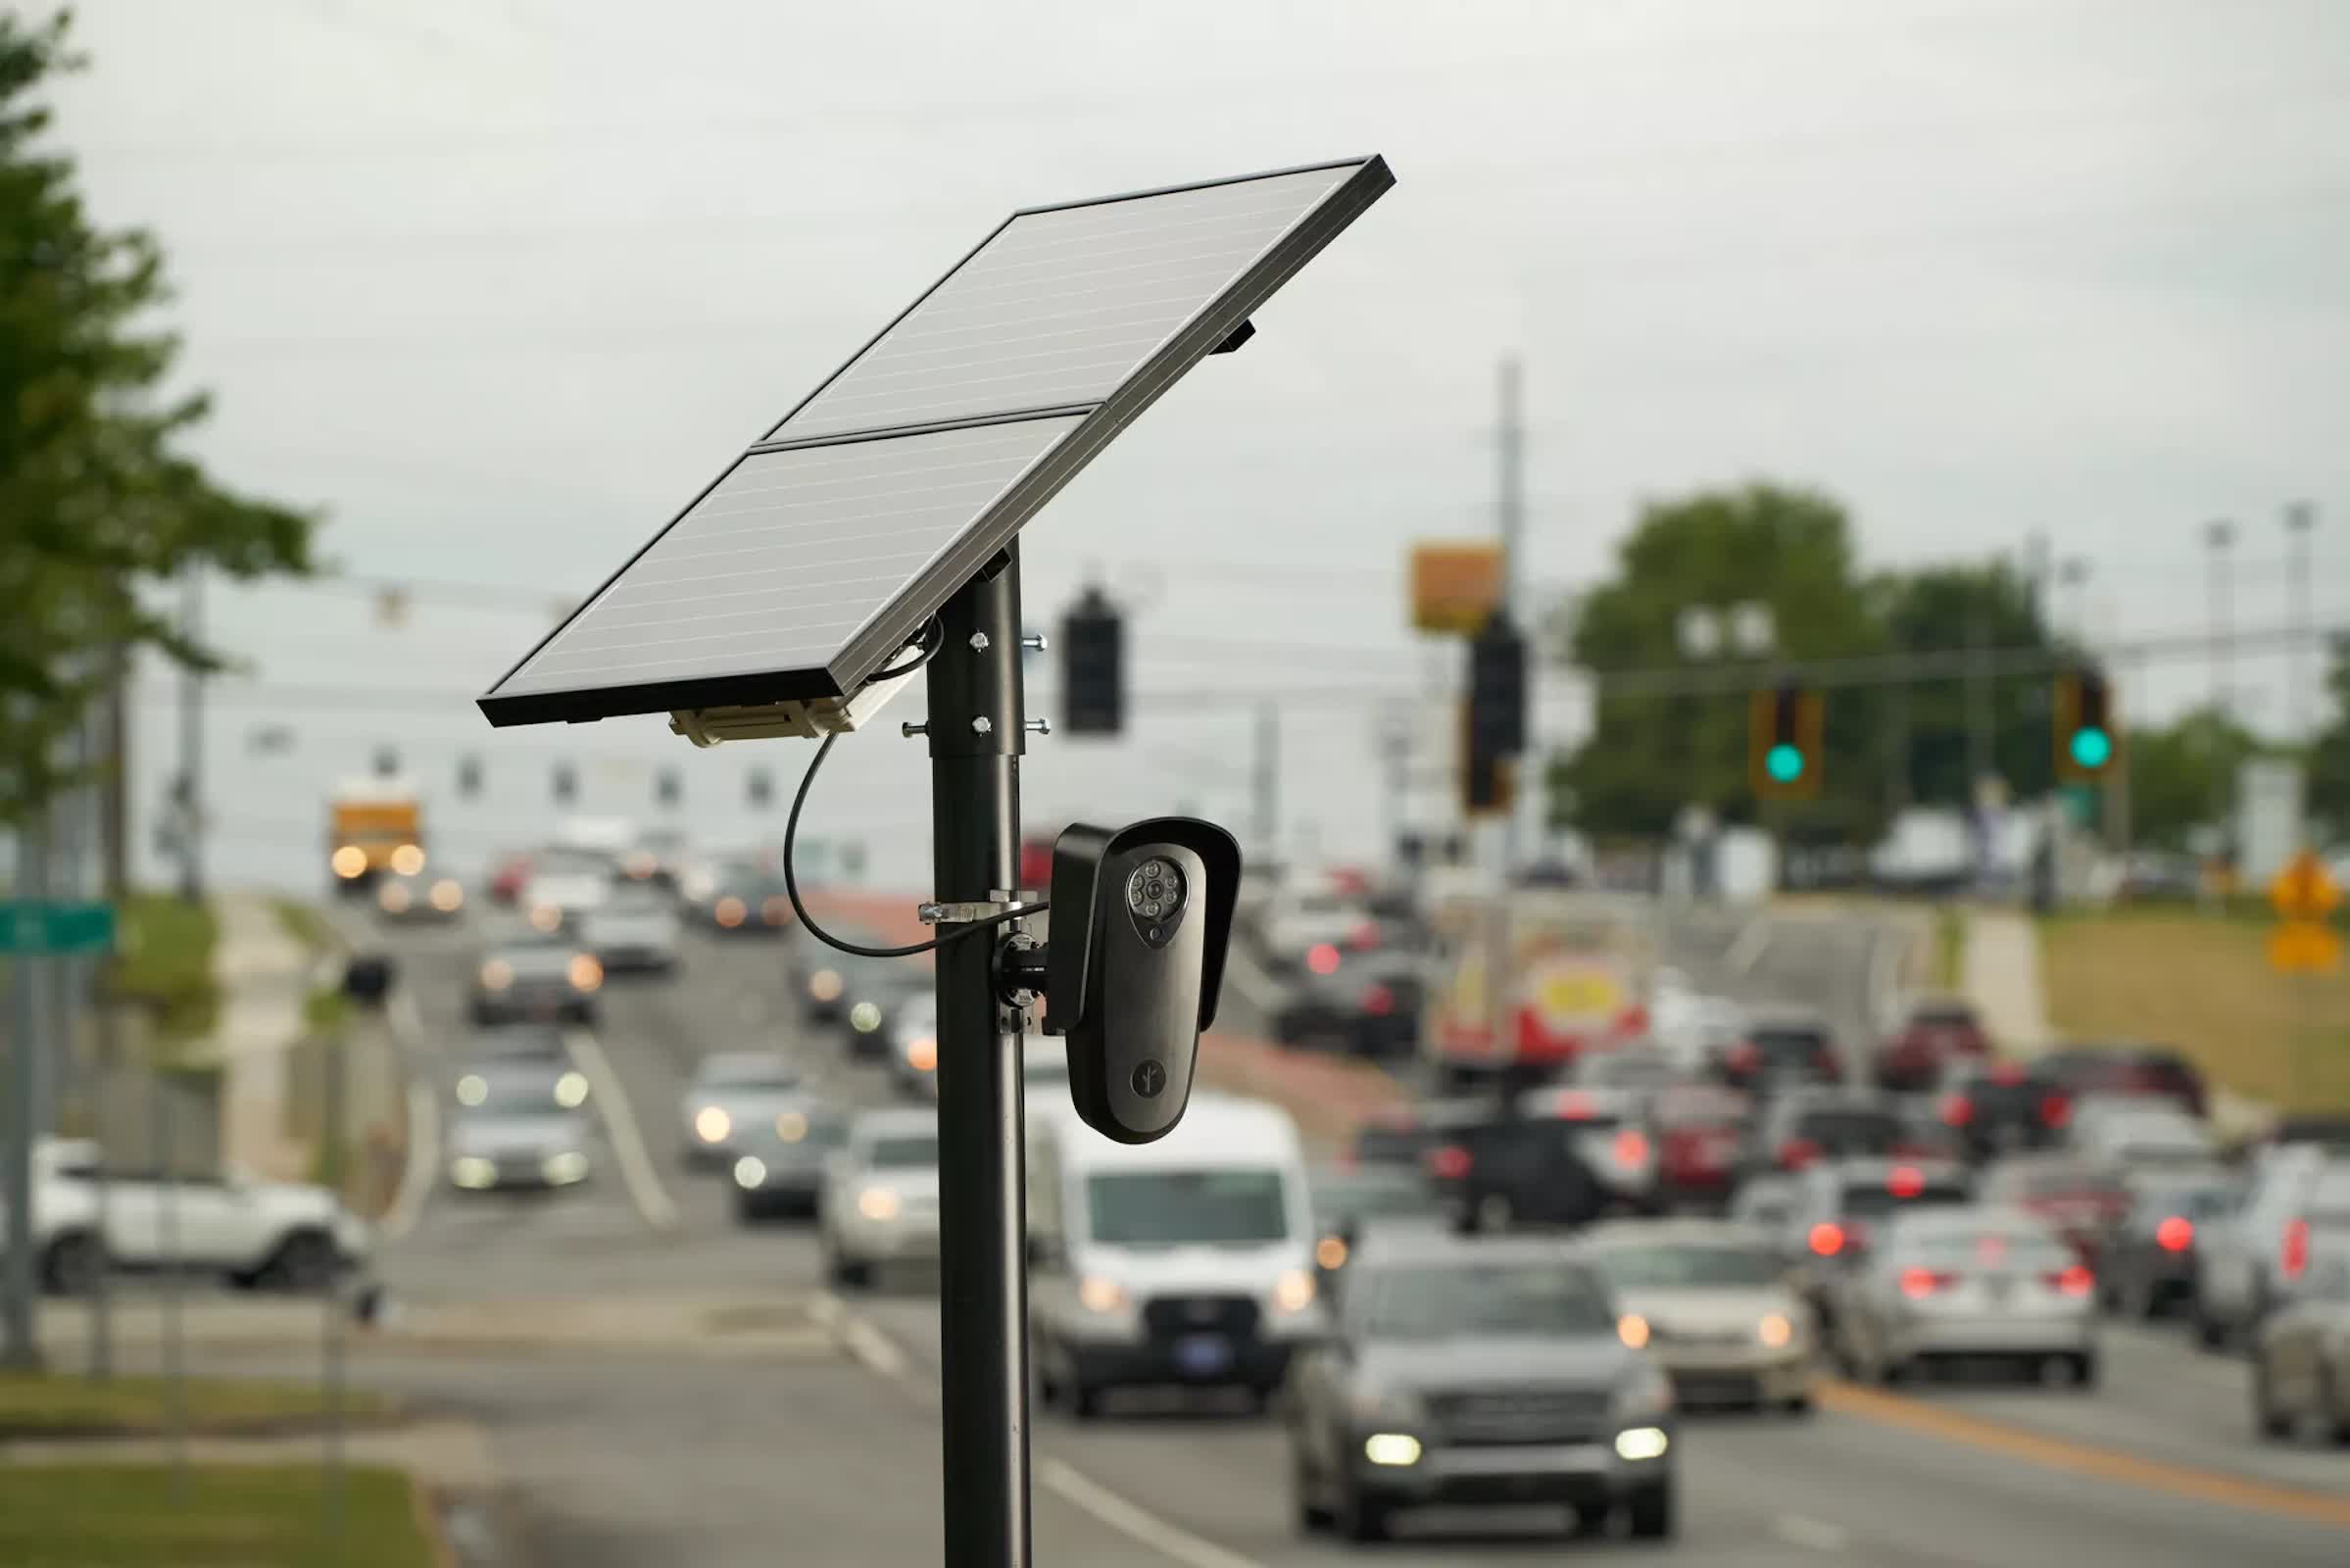
What just happened? Flock Safety is changing how police search its license plate camera database as the company faces growing questions in Washington over privacy, accuracy, and misuse. The company told Senator Josh Hawley that it has added more controls to its search system, which scans about 20 billion license plates a month.
Until recently, users were required to explain why they were conducting a search by typing into an open text field. Flock said those entries were not always specific enough. The company has replaced the field with a drop-down menu of standardized categories based on the FBI’s crime-reporting system.
By the end of the year, law enforcement users will also need to enter a case number before running a search. Flock said that requirement can be waived in emergencies.
The changes were outlined in a letter from Flock’s chief legal officer to Hawley, the Missouri Republican who opened an investigation into the company last month. Hawley led a Senate hearing on Wednesday examining Flock and three other companies that provide similar surveillance technology.
Advertisement
The hearing featured a Florida woman who spent 13 days in jail after her car was detected by a Flock camera near the scene of a fatal crash. Authorities were looking for a similar vehicle.
Flock’s automated license plate recognition system has spread quickly. The company says it has about 120,000 cameras nationwide. Police departments and public-safety officials argue that the technology can help find missing children, track stolen vehicles, and investigate hit-and-run crashes.
The system has also drawn criticism from privacy advocates, civil-liberties groups, and people on both sides of the political divide. Critics are concerned that agencies can use the cameras to follow a person’s movements over time. They also point to allegations that some officers have used the system for personal reasons, including stalking.
Flock said it does not maintain “a single consolidated count of confirmed customer misuse.” The company said its customers determine whether a search was justified and whether discipline is appropriate when an employee abuses access.
Advertisement
The company has also started adding its own monitoring tools. In April, it introduced a system designed to flag unusual search activity. Flock said the system has identified several cases of misuse, including some that led to arrests. It is also working on a feature that would lock users out when their behavior appears abnormal.
Hawley said the issue could prompt congressional action. “We have an entire constitutional system to protect individual liberty,” he told The Wall Street Journal. Without limits from companies or the government, he added, “we’re going to have a huge problem with the invasion of basic rights and liberties.”
The company is also reducing the amount of data it stores by default. New customers will have a seven-day retention period, down from 30 days. Existing customers will have to opt in if they want the shorter period.
Agencies can still seek permission to retain data longer, but Flock said those requests must be approved “either by an elected governing body…or by an elected official.” The company said about 3% of its law-enforcement customers keep data for more than 30 days. Its maximum retention period is one year.
When you’re on an exceptionally long road trip, the general boredom of things can combine with the minutiae of the road to create some rather annoying phenomena. For example, when you first set out, you might not think much about the sound of the road rolling beneath the treads of your tires. The longer you’re on a trip, however, the more you start to notice that droning, low-frequency sound. Even if they’re not necessarily bad warning-sign sounds, innocuous noises can start to become upsetting if you’re already bored and tired.
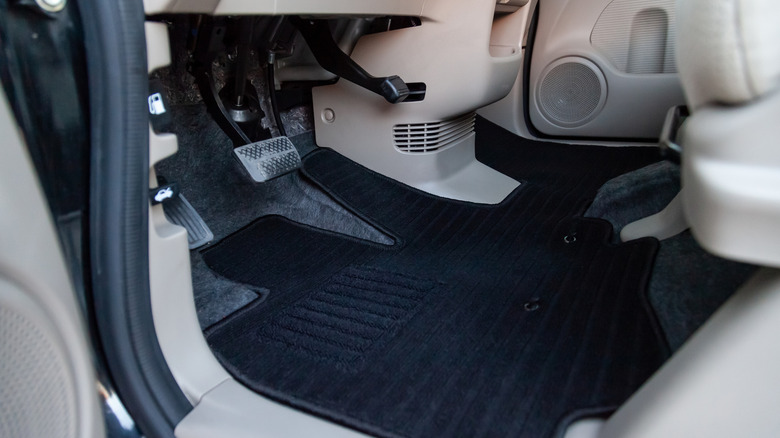
If you’re having a particular problem with road noise on regular, lengthy drives, there is a potential solution you may want to look into: car carpet underlay. It’s exactly what it sounds like and works as an additional layer of padding that goes beneath the carpeting in your car’s cabin. Adding padding down there has a few perks, such as making it a little more comfortable to rest your feet on and giving you some support in the case you have to get down on your knees to fish under the seats for a lost item or to clean.
According to some automotive enthusiasts, carpet underlay can also be a sound choice for slightly deadening the general thrum of the road. Indeed, some manufacturers engineer underlays for this particular purpose. Whether or not it’s an absolute solution, though, is a matter of opinion.
Advertisement
Some users recommend underlay for absorbing low-frequency road noise
Aleksandr Kondratov/Shutterstock
According to users on the Jalopy Journal forums and Vintage Mustang forums, automotive carpet underlay can be a nice investment if you want the floor of your vehicle to be a little more plush. It also has the added benefit of insulating the floor of your vehicle from the heat of your engine and exhaust, generally making it a bit cooler to the touch.
On the specific matter of cutting road noise, carpet underlay can definitely help in that regard, though the precise efficacy may vary. According to one Jalopy Journal user, adding Dynamat-branded underlay to their car as well as insulation on the walls silenced the noise so much that their spouse could hear the odometer ticking over.
Advertisement
However, as another user on that forum explains, carpet underlay, as well as similar products like mats and insulation inserts from brands like Hushmat and Dynamat, is intended more for dampening the noise produced by your own vehicle’s panels vibrating during extended, intensive usage. It will certainly absorb some noise from the road, but not all of it. If you’re looking to create a truly soundproof environment in your car’s cabin, they suggest you add some underlay to your carpets, followed by a layer of mass loaded vinyl (MLV), which is a hardware-grade material used for various sound-dampening purposes.



















































You must be logged in to post a comment Login