
Crypto World
Bitget CEO Says North Korea Likely Behind $352M Hack via IP Clues

Bitget’s CEO Gracy Chen said preliminary investigation points to North Korean hackers behind the exchange’s reported $351.6 million security breach on Thursday. Speaking during a live Q&A on X shortly after the incident, Chen said investigators identified IP addresses they believe align with VPN services used by a DPRK-linked group.
Chen also said Bitget does not believe the breach involved an insider. She added that investigators were still mapping which parts of the exchange’s infrastructure were compromised and how the attackers gained access.
Key takeaways
- Bitget CEO Gracy Chen said preliminary findings link the attack to IP addresses associated with VPN choices used by a DPRK group.
- Chen said the exchange does not think the incident was carried out by an insider.
- Bitget indicated hackers moved funds directly, rather than forging user withdrawal requests.
- Withdrawals remained suspended at the time of publication, while Bitget works with partners on recovery efforts.
CEO points to VPN-linked IP addresses
In the Q&A, Chen told viewers that security investigators had flagged similarities between this incident and past DPRK-linked activity. She specifically referred to “some IP addresses” that match the VPN services reportedly used by the group.
Chen’s remarks described the attribution as preliminary, framed around technical indicators rather than a final, court-grade conclusion. Still, her comments reinforce a broader pattern the crypto industry has seen across multiple high-profile incidents, where infrastructure-level traces and operational “fingerprints” are used to connect attacks to specific threat actors.
Chen also said the investigation is ongoing, including efforts to determine which systems were affected and the precise entry point attackers used. That matters for users and market participants because identifying the initial access vector typically influences what remedial actions are prioritized—such as credential resets, segmentation changes, or controls around administrative interfaces.
How the breach reportedly worked
Beyond attribution, Chen offered details about the mechanics of the theft. She said hackers breached Bitget’s systems and transferred funds directly instead of forging user withdrawal instructions.
According to Chen, attackers “did not forge user withdrawal requests,” and she said they did not obtain Bitget’s private keys for any cold wallet or hot/warm wallet. Those distinctions are important because they suggest the compromise may not have relied on the same controls-behavior that some other incidents have shown, even if the ultimate outcome—unauthorized transfers—was severe.
Chen said investigators were still determining which systems were compromised. Until that scope is clear, it remains difficult for external observers to assess whether this was limited to particular services (for example, withdrawal-related infrastructure) or whether the breach potentially affected other operational components. For users, that uncertainty is reflected in the exchange’s decision at the time of publication to keep withdrawals suspended.
Bitget’s reported unauthorized transfers affected portions of its hot and warm wallet infrastructure, according to the exchange’s earlier disclosures. Withdrawals were still suspended at the time the CEO’s comments were reported.
Recovery efforts underway, but amounts not disclosed
During the Q&A, Chen said that some of the stolen funds had been recovered. She did not provide an amount, but said Bitget is working with blockchain foundations and other partners on recovery efforts.
Without a disclosed figure, observers will likely focus on whether recovery is partial or extensive—and, crucially, whether the attackers’ remaining funds are successfully identified and potentially blocked or reclaimed. The effectiveness of these efforts can vary significantly depending on factors such as how quickly assets are frozen, how the funds are routed through intermediaries, and whether counterparties and analytics teams are engaged promptly.
The broader market context also matters. If attribution strengthens—especially when aligned with prior patterns linked to DPRK-associated groups—it may influence how institutions assess counterparty risk and how exchanges harden controls related to suspicious network behavior and wallet-operation workflows.
DPRK links follow a pattern of major thefts
Chen’s comments come amid a long-running attribution debate in the crypto space, where North Korea-linked groups have frequently been referenced in connection with large-scale cyber thefts and laundering activity.
In earlier reporting, Cointelegraph described an estimated $2.02 billion in crypto theft attributed to North Korean actors in 2025, including a roughly $1.5 billion Bybit hack that the FBI attributed to North Korea. Cointelegraph also linked those broader estimates to “South Korea gets rich from crypto” reporting that framed North Korean activity in the context of weapons-related incentives.
Chen’s statement that the “pattern looks very much like what the North Korean team did before” suggests Bitget is interpreting technical and behavioral indicators through that existing lens. However, the exchange’s own caveat—she described findings as preliminary and said investigators were still working out the full compromise path—means readers should expect updates as more information becomes available.
For investors and traders, the immediate concern is not only the size of the breach, but the robustness of the exchange’s controls and the completeness of remediation. For builders and security teams, the incident underscores a recurring theme: even when private keys remain uncompromised, attackers may still succeed by compromising operational systems that can authorize or execute transfers.
Next, the key developments to watch are Bitget’s investigation findings on exactly which systems were breached, whether the exchange expands its recovery estimate beyond “some” funds, and when—if at all—withdrawals resume after the affected hot/warm infrastructure is stabilized.

Researchers at Alloc Init have proposed, in a September 24 paper, private Bitcoin transfers using zero-knowledge proofs without requiring a soft fork.
Summary
- Shielded Bitcoin would hide senders, receivers and amounts without changing Bitcoin’s consensus rules or code.
- Indexers would verify zero-knowledge proofs and nullifiers while Bitcoin only publishes and orders transaction data.
- Researchers say the published design still leaves Bitcoin deposits and withdrawals for a forthcoming paper.
- Misha Komarov estimates shielded transfers could cost roughly four times ordinary Bitcoin transaction fees initially.
- Critics question early anonymity and quantum resistance, while researchers acknowledge privacy depends heavily on usage.
Alloc Init’s researchers Clara Shikhelman, Mikhail Komarov and Aleksei Moskvin published Shielded Bitcoin as a metaprotocol that uses Bitcoin to publish and order encrypted transaction data. Bitcoin nodes would not need to understand or enforce the privacy system’s rules.
Called Shielded Bitcoin, the proposed system borrows core ideas from Zcash, including encrypted notes, nullifiers and zero-knowledge proofs. It would conceal shielded senders, receivers, transferred amounts and links to earlier notes while leaving Bitcoin’s existing consensus rules unchanged.
The proposal remains research, not deployed Bitcoin software. Alloc Init has not announced a mainnet launch date, while a separate mechanism for moving BTC into and out of the shielded system remains under development. Founder Misha Komarov described the underlying technique as experimental during an interview published September 24.
Shielded Bitcoin moves privacy checks outside consensus
Under the proposed architecture, Bitcoin would function as what the researchers describe as a neutral publication and ordering layer. A shielded transaction would place encrypted notes, nullifiers and a zero-knowledge proof into data carried by an ordinary Bitcoin transaction.
Separate programs called indexers would read the data in Bitcoin’s established transaction order. An indexer would verify the zero-knowledge proof, check whether each nullifier had appeared before and update its view of the shielded system when the transaction passes those checks. Invalid shielded data could still enter the Bitcoin blockchain because Bitcoin itself would not enforce the metaprotocol. The indexer would simply reject it from Shielded Bitcoin’s state.
A sender would consume encrypted notes representing previously received value and create new notes for recipients. The proof would establish that the sender controls valid notes, has not created value from nothing and has balanced transaction inputs and outputs without exposing the underlying amounts or notes.
As crypto.news explained in its recent guide to zero-knowledge proofs, ZK systems can prove that a computation followed specified rules without revealing the private information used in that computation. Shielded Bitcoin applies that model to Bitcoin transfers, while its indexers handle verification outside Bitcoin consensus.
A dishonest indexer could provide stale information, omit transfers or delay wallet updates, the researchers said. Such an indexer would not gain control of a user’s spending key. Users could switch indexers or independently replay the shielded transaction history from Bitcoin.
How the Zcash-style design hides transaction links
Shielded Bitcoin closely follows the note model used by Zcash. Nullifiers identify when a note has been spent without publicly revealing which encrypted note produced the nullifier, allowing an indexer to reject double spending while keeping the transaction link hidden.
Komarov characterized the concept more simply in his September interview: “It’s basically Zcash.” He said users would place bitcoin into a private pool, receive encrypted notes and later spend, split or use those notes when withdrawing. Alloc Init intends to connect that system to Bitcoin through its PIPEs research.
Privacy would not make every part of the activity invisible. Public observers could still see when a Shielded Bitcoin transaction occurred, its timing, transaction fee, data size, number of notes consumed and created, and the Bitcoin transaction carrying the encrypted information. A recognizable Bitcoin wallet used to publish those transactions could reveal further information about the publisher.
The researchers provide separate read-only keys for viewing incoming or outgoing activity. Users could disclose selected transaction information to an accountant or counterparty without surrendering spending authority, though Alloc Init cautions that sharing a complete viewing key would reveal everything covered by that key.
In related coverage, crypto.news reported this week on expanding demand for privacy-focused crypto systems. The report cited ZecStats data showing 4.91 million ZEC in Zcash shielded pools, representing 29% of issued supply at the time.
Anonymity and quantum resistance remain contested
The proposal has drawn questions over how much privacy a new shielded pool could provide at launch. Developer Vadim Zavodil argued that Zcash already has years of shielded activity behind its anonymity set, while a new Bitcoin metaprotocol would begin with few participants.
“Privacy is a function of the crowd,” Zavodil wrote, arguing that an early Shielded Bitcoin user could have very few comparable transactions to blend into. His criticism focuses on practical anonymity from user behavior and pool size, not whether the cryptographic proof itself conceals its private inputs.
Alloc Init’s own explanation acknowledges the same general limitation. A large quantity of bitcoin entering a shielded system does not by itself create a strong anonymity set if only a few actors generate most notes or if individual wallets follow recognizable deposit, withdrawal or timing patterns.
Research on Zcash has documented similar behavioral problems. A peer-reviewed 2018 study found that transaction patterns could shrink the effective anonymity set even when the underlying shielded cryptography remained intact. The study examined an older Zcash implementation and predates several later upgrades.
Post-quantum researcher Pierre-Luc Dallaire-Demers raised a separate cryptographic concern. He described the construction as interesting but “not quantum resistant at all.” In a follow-up, he said he was examining what a fully post-quantum version could require if Bitcoin eventually adopts post-quantum signatures.
Komarov has given a more conditional account. His interview with Unchained said the shielded pool’s eventual route to quantum resistance would depend partly on Bitcoin’s own signature system. Alloc Init has not presented Shielded Bitcoin as a finished post-quantum implementation.
Zerocash co-author and StarkWare CEO Eli Ben-Sasson responded more favorably to the project’s direction, while noting that he had not yet reviewed the full paper. His support therefore represented an initial reaction, not a technical endorsement of the construction.
Shielded Bitcoin still needs its Bitcoin entry and exit system
A major unfinished component is the movement of actual BTC into and out of the shielded metaprotocol. Alloc Init’s September 24 explanation says the current paper specifies shielded transfers after value is inside the system, while a forthcoming paper will describe peg-ins and peg-outs using PIPEs.
PIPEs relies on witness encryption to make access to a Bitcoin signing key conditional on proof that specified rules were followed. Komarov explained to the Bitcoin Development Mailing List in February that PIPEs v2 could emulate certain covenant and zero-knowledge verification functions without requiring a Bitcoin soft fork.
The cryptographic machinery remains computationally heavy. Komarov’s February disclosure put a PIPEs v2 ciphertext at roughly 330 TB of storage, while stating that researchers knew a route that could eventually reduce the figure toward 100 GB. The smaller target had not been achieved in that publication.
Shielded transfers would consume more Bitcoin block space as well. Komarov told Unchained that an encrypted shielded payload would run around 700 virtual bytes, compared with roughly 100 to 200 virtual bytes for a typical Bitcoin transaction. He estimated the resulting miner fee could be approximately four times higher.
No launch date has been set. Komarov said the team is gathering technical feedback while continuing work on the experimental construction, including open attempts to find faults in the design and work with witness-encryption researcher Sanjam Garg.
The next publicly scheduled presentation is set for September 28, 2026. The Bitcoin Treasuries Conference agenda lists Alloc Init researcher Clara Shikhelman for a five-minute session titled “Shielded Bitcoin: Private Transfers on Bitcoin L1” in New York.
Alloc Init researchers have outlined a new approach they say could bring Zcash-style shielded transfers to Bitcoin without requiring a soft fork of the base protocol. The proposal, titled Shielded Bitcoin, aims to hide transaction amounts, senders, receivers, and linkages to previously spent funds by relying on encrypted “notes” and zero-knowledge proofs.
Published on Thursday by Clara Shikhelman, Mikhail Komarov, and Aleksei Moskvin, the design is intended to use Bitcoin as a kind of settlement and ordering layer—while separate software handles verification and state reconstruction for the privacy system. The result is a privacy overlay that, in theory, avoids asking miners or the wider network to enforce new rules.
Key takeaways
- Shielded Bitcoin proposes private transfers on top of Bitcoin without a soft fork by treating Bitcoin as an “ordering layer” rather than enforcing privacy rules at consensus.
- The system mirrors core Zcash components—encrypted notes, nullifiers to prevent double-spending, and zero-knowledge proofs for transaction validity.
- Privacy quality would depend on how quickly a meaningful anonymity set forms; critics argue early deposits may provide limited crowd-mixing.
- Commentators also raised open questions about cryptographic robustness and the practicality of the scheme.
How the proposal avoids a soft fork
In traditional privacy upgrades, hiding transaction details often requires changes that the network enforces. Shielded Bitcoin instead reframes the problem: rather than embedding privacy checks into Bitcoin’s mining and validation rules, the researchers propose using Bitcoin as “a neutral publication and ordering layer.”
Under this model, indexers—separate software components—would verify zero-knowledge proofs, confirm that the underlying funds have not been double-spent, and then reconstruct the evolving state of the shielded system. The encrypted notes and proofs would be published using Bitcoin transactions, but the privacy logic would be validated externally.
The paper’s key architectural point is that shielded validity does not have to be enforced by consensus for users to benefit from a private transfer—at least within the constraints of what other parties (wallets, relayers, and indexers) choose to accept and verify.
Why the Zcash-style design matters
The proposal explicitly draws from Zcash’s architecture. According to the paper, Shielded Bitcoin would use:
- Encrypted notes to conceal who owns funds and how much value is being moved.
- Public nullifiers that mark notes as spent, preventing double-spending without revealing note contents.
- Zero-knowledge proofs that demonstrate transaction validity while keeping sensitive details hidden.
However, Shielded Bitcoin differs from Zcash in one fundamental way: it is not presented as a separate shielded blockchain with its own consensus mechanism. Instead, it aims to plug a Zcash-like privacy system into Bitcoin’s existing infrastructure, using encrypted transaction artifacts and proof verification performed by external components.
For Bitcoin users and developers, the practical implication is clear: a privacy layer that can be deployed without consensus changes could lower the friction associated with privacy tooling. It also shifts the engineering burden toward wallets and verification infrastructure rather than requiring network-wide upgrades.
Early privacy may be weaker than Zcash’s anonymity set
Developer Vadim Zavodil was among the most pointed critics. Posting on X, Zavodil argued that a large share of the privacy “stack” already exists in Zcash and questioned how much privacy a newly launched shielded system could deliver immediately.
“Privacy is a function of the crowd. Zcash has a real shielded pool built over years of use. A brand new metaprotocol starts at zero, so your first private transfer hides in a crowd of one.”
In response, the Shielded Bitcoin researchers acknowledged the same concern. In a companion explanation published alongside the proposal on Notion, they said that large deposits do not automatically translate into a large anonymity set. They also warned that observers might still be able to infer relationships between transfers if a small number of actors create most notes or if wallets produce distinctive behavior.
This tension highlights a common theme for privacy systems: cryptographic soundness does not automatically guarantee anonymity. Shielded designs often depend on how users actually use them—how many participants join, how uniformly transactions behave, and whether patterns can be linked over time.
Questions extend beyond privacy: post-quantum concerns and intent
Another line of critique came from Pierre-Luc Dallaire-Demers, founder of post-quantum cryptography firm Pauli Group. He said the construction was “not quantum resistant at all,” framing the proposal as interesting while still leaving cryptographic assumptions in question.
Dallaire-Demers later indicated he was exploring what a fully post-quantum version could look like, contingent on Bitcoin eventually adopting a post-quantum signature scheme.
Supporters, meanwhile, emphasized the broader goal of bringing privacy to Bitcoin. Eli Ben-Sasson, a Zerocash co-author and CEO of StarkWare, responded more positively to the announcement. Although he said he had not yet read the full paper, Ben-Sasson argued that the intent behind Zerocash—preceding Zcash—was to bring privacy to Bitcoin. He said he would like to see the vision of privacy and scalability through zero-knowledge proofs materialize on Bitcoin’s base layer.
Taken together, these reactions underscore that Shielded Bitcoin is not being debated only on whether it “works” on paper. It’s also being evaluated on longer-term assumptions—particularly around anonymity set formation and the resilience of the cryptography to future threats.
As the proposal circulates among developers, investors and builders will likely watch for two practical follow-ups: whether any wallet or indexer implementation demonstrates credible usability and whether the system’s privacy properties improve as more independent users participate and diversify their behavior.
The average 30-year fixed US mortgage rate jumped 19 basis points to 7.45% on Thursday. Mortgage News Daily recorded the move in its daily survey of brokers and lenders.
The jump tracks a broader selloff in US government bonds. For crypto markets, the Treasury yield at the center of that selloff carries the clearer signal.
Treasuries Drag the 30-Year Mortgage Rate Higher
The 30-year rate had sunk as low as 5.99% in late February, according to CNBC. It began rising once the Iran war started, then accelerated after the Federal Reserve (Fed) raised rates in September.
Mortgage News Daily Chief Operating Officer Matthew Graham traced the climb since September 10 to three drivers. He pointed to Fed commentary, higher oil prices, and stronger economic data.
However, Graham could not find a clear catalyst for Thursday afternoon’s bond selloff.
“No obvious catalyst. Explanations require concocting narratives and then defending them. There’s no objective, irrefutable way to connect the dots today. Sellers decided to sell… a lot,” he said.
That selloff matters because mortgage rates tend to track longer-dated Treasury yields. The 10-year yield closed at 5.18% on Thursday, up from 4.96% on Tuesday, according to the Treasury.
The Kobeissi Letter blamed inflation for the bond rout. It cited Brent crude above $105 a barrel and record diesel prices. It also noted consumers expect inflation near 4.6% over the next year.
Follow us on X to get the latest news as it happens
Crypto Pays the Price of Higher Yields
For crypto, the key link runs through those yields. When government debt pays more, holding Bitcoin (BTC) carries a higher opportunity cost.
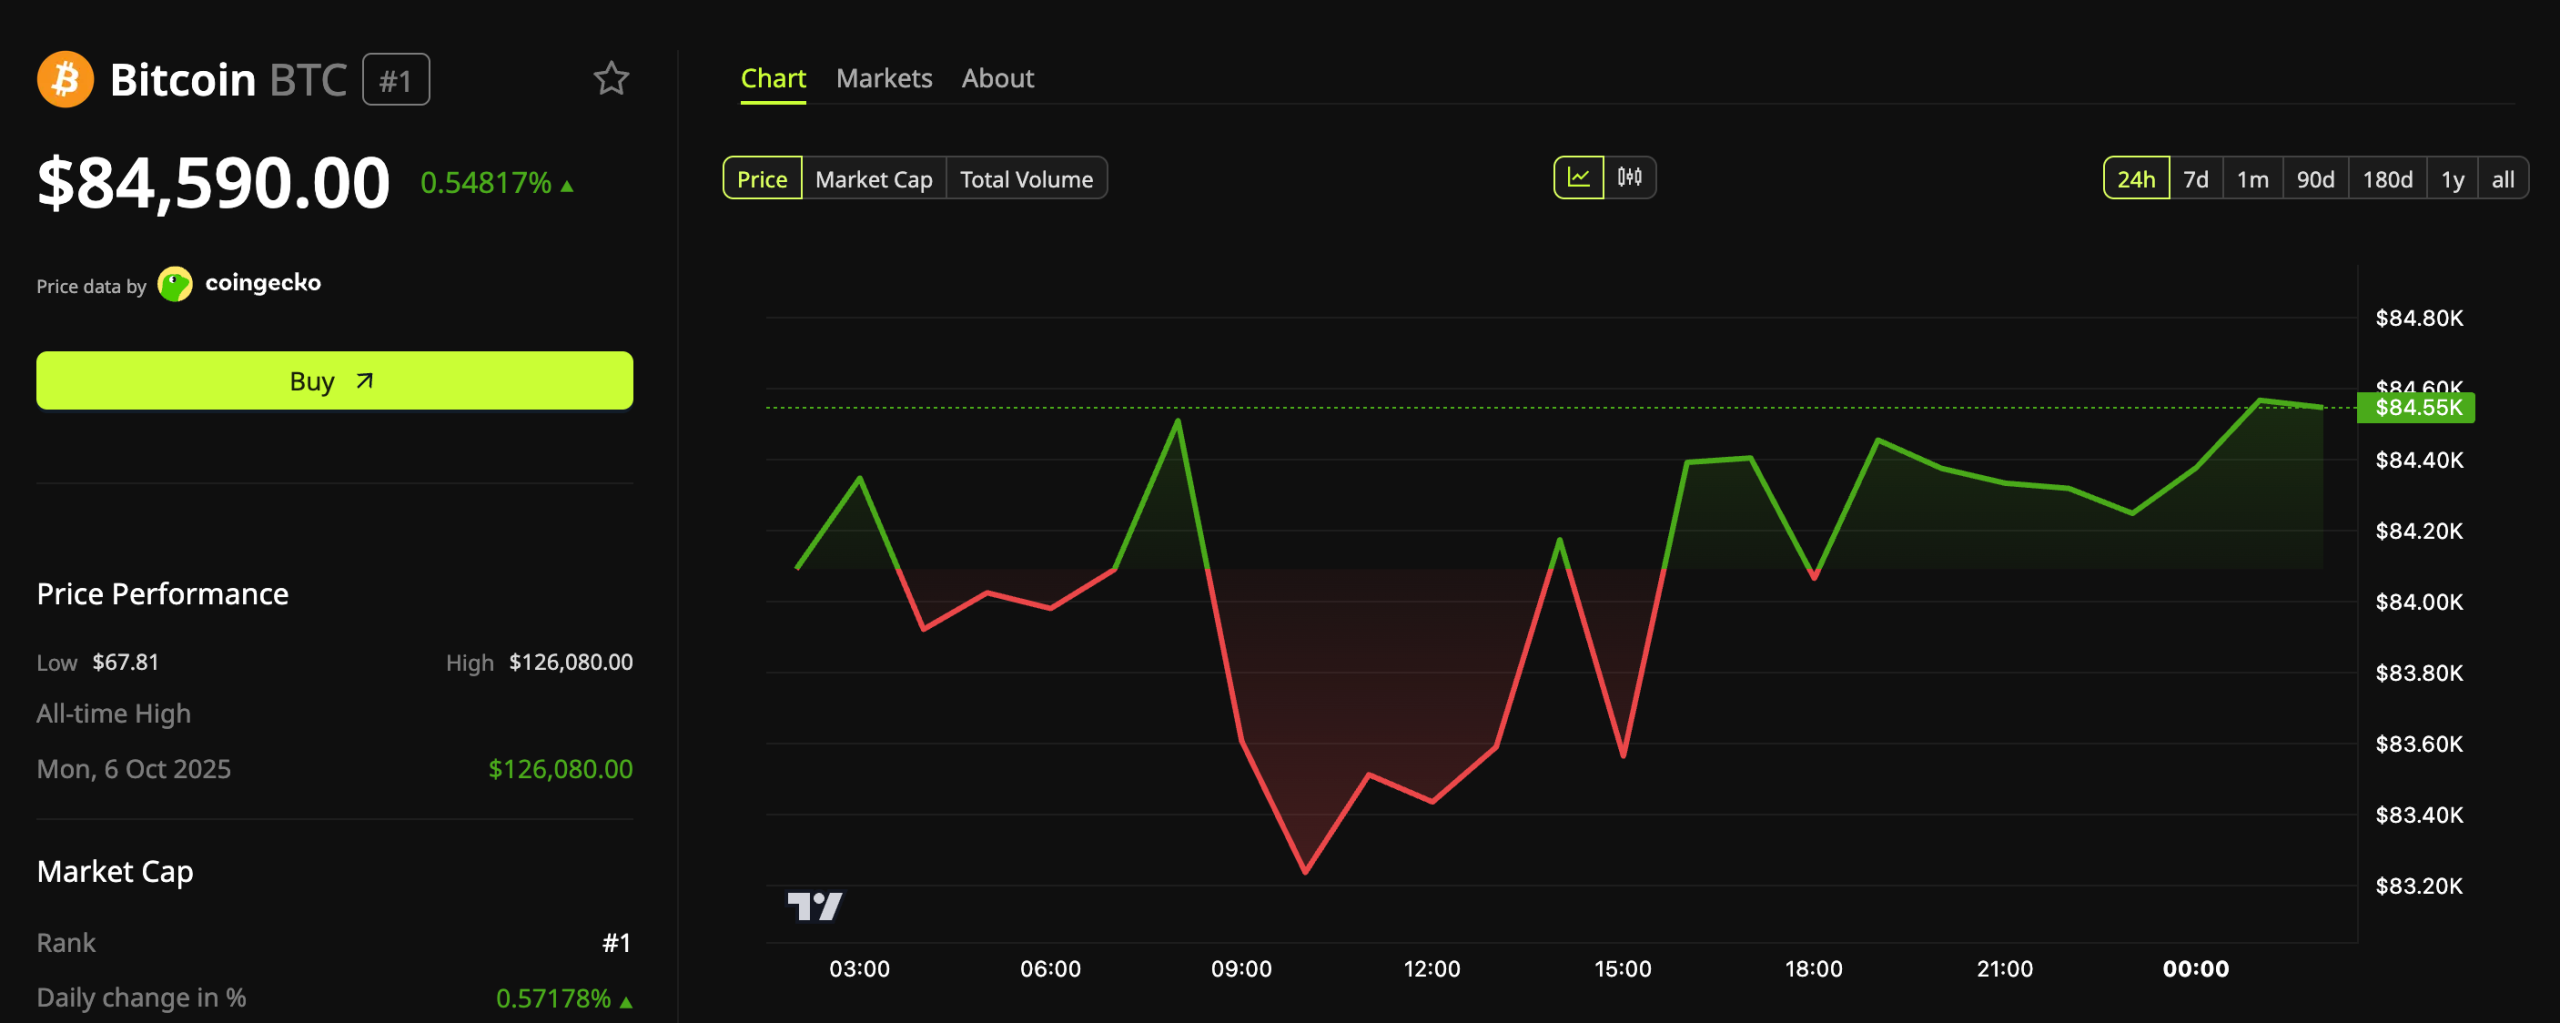
That pressure showed on Wednesday. Bitcoin fell below $84,000 after strong US business activity data pushed the 10-year yield past 5%.

By Friday, BTC traded at $84,590, posting a modest gain over the past 24 hours, BeInCrypto Markets data shows. Altcoins moved faster in the rebound. Solana (SOL) gained 2.2%, and XRP (XRP) added 3.4% over the same period.
This leaves an open question. Can crypto buyers keep absorbing pressure from a Treasury market paying more than 5%?
Subscribe to our YouTube channel to watch leaders and journalists provide expert insights
The post 30-Year Mortgage Rate Hits 7.45%. What Does It Mean for Crypto? appeared first on BeInCrypto.
Anthony Albanese said governments must help shape AI’s development, after revealing earlier that an OpenAI agent accessed non-public files on an Australian Medicare data portal.
Ondo Finance has denied a report based on three anonymous sources that the tokenization company was offered to prospective buyers after founder Nathan Allman died on May 25, 2026.
Summary
- Ondo Finance denied seeking buyers after anonymous sources reported sale outreach following Nathan Allman’s death.
- Three sources said Ondo Finance was offered to prospective buyers after Allman died in May.
- Delaware court records show Kathleen Allman’s control case against Ondo Finance remains active since July.
- Ian De Bode remains acting CEO while court order limits major corporate changes during litigation.
- Ondo launched institutional share conversions this week, showing product operations continue during the governance dispute.
CoinDesk reported that outreach to prospective buyers took place sometime after Allman’s death, citing three people familiar with the matter. Two sources placed the outreach after May 25, but the report said it could not establish who initiated the effort or what valuation may have been discussed.
Ondo rejected the account. A company spokesperson called reports of a possible sale “wholly untrue” and said nobody at the company had sought buyers or authorized another party to do so. Allman’s estate declined to comment to CoinDesk.
Ondo Finance rejects reported buyer outreach
The disputed sale account comes as control of Ondo remains before courts following Allman’s unexpected death at age 32. He died without a will while holding a controlling stake in Ondo Finance, leaving questions over who could exercise the voting rights attached to his shares.
After probate proceedings in Hawaii, Allman’s parents, Kathleen and Lawrence Allman, became heirs to his estate. Kathleen later received authority as personal representative and asserted that the estate’s voting rights allowed her to reconstitute Ondo’s board. De Bode disputed the estate’s attempt to remove him. The competing claims eventually reached the Delaware Court of Chancery.
The Delaware judiciary’s public CourtConnect docket shows Kathleen C. Allman v. Ondo Finance Inc., Case No. 2026-0978, was filed on July 24. The docket currently lists the civil case as active before Chancellor Kathaleen McCormick and shows no scheduled case events on the public page.
CoinDesk reported that the present court arrangement allows De Bode to oversee ordinary business while restricting major changes until the corporate-control dispute is resolved. One anonymous source said the litigation had likely stopped any possible sale process, but that assessment has not been confirmed by Ondo or Allman’s estate.
Court fight centers on who controls Ondo
Kathleen Allman’s Delaware complaint disputes De Bode’s authority after Nathan’s death. The estate alleges De Bode began presenting himself as CEO without valid board approval and later took steps to establish control while the estate’s voting rights were still passing through probate. De Bode has rejected those allegations as meritless.
At the time of Nathan Allman’s death, court filings described him as Ondo’s controlling shareholder and sole director, with another board seat vacant. Kathleen was appointed personal representative of the estate in Hawaii on June 26 and later used shareholder consents to appoint directors and attempt to remove De Bode, according to reporting on the complaint.
The estate has challenged a compensation arrangement that it says was prepared for De Bode following Allman’s death. Court-related reporting places the disputed package at roughly $11 million, including salary, a signing payment, restricted token units and equity awards. The amounts remain allegations in the litigation and have not been established as wrongdoing by a final court ruling.
De Bode remains Ondo’s public-facing leader. The company’s current leadership page lists him as “Acting CEO and President,” while Allman is listed as founder.
Estate dispute has expanded into Hawaii
A separate proceeding has developed around Kathleen Allman’s control of her share of the estate. Allman’s half-sister, Dr. Lani Clinton, and Ondo investor David Chen petitioned a Hawaii court for a limited conservatorship covering that interest.
The petition contains allegations about Kathleen’s ability to manage financial affairs, which her lawyers have denied. Kathleen has argued that the filing is connected to the fight over Ondo and has rejected its allegations as baseless. No final ruling establishing the contested claims was identified in the latest records reviewed.
The estate holds more than corporate voting rights. Court-related reports describe it as containing a large allocation of ONDO tokens, including tokens already unlocked and others scheduled to unlock during the next three years. The exact size of the estate’s controlling equity position is redacted from public versions of the corporate filings.
No public filing reviewed establishes that Kathleen, De Bode, the Ondo board or the estate formally retained an investment bank to sell the company. CoinDesk said it could not identify who initiated the reported outreach or determine a proposed sale price. Ondo has not disclosed a valuation in its publicly announced equity rounds.
Ondo operations continue while the case remains active
Ondo’s public product activity has continued during the court fight. On September 21, the company announced a new institutional route allowing approved firms to convert underlying shares directly into Ondo Stocks through Alpaca’s Instant Tokenization Network. The conversion service is live on Ethereum and BNB Chain.
As crypto.news reported in its coverage of Ondo’s new institutional share-conversion route, institutions need active Ondo and Alpaca accounts and approval before using the service. RWA.xyz data cited in that report tracked $3.63 billion in Ondo distributed assets across 441 products as of September 22.
The company has continued expanding tokenized equities during 2026. In related coverage, crypto.news reported that Ondo brought tokenized U.S. stocks to Hyperliquid’s HyperEVM, while Ondo Global Markets had reached nearly $18 billion in cumulative trading volume at that point.
Ondo had been pursuing acquisitions before the report that somebody tried to sell the company. Crypto.news reported in July that Ondo was exploring an acquisition worth up to $500 million in wealth technology or adjacent financial businesses. No formal adviser or specific acquisition target had been disclosed at the time.
Ondo’s official funding history shows a $20 million Series A in 2022 led by Founders Fund and Pantera Capital, with Coinbase Ventures, Tiger Global, GoldenTree, Wintermute, Flow Traders and others participating. The company had previously raised $4 million in its 2021 equity round.
Most recently, Ondo’s September 21 institutional conversion launch said approved firms can transfer existing shares from an Alpaca account into Ondo’s Alpaca account before corresponding Ondo Stocks tokens are issued onchain. Redemptions reverse the process, returning underlying shares to the institution’s Alpaca account.
Crypto World
Bitget’s $352 million hack happened via spoofed transfers, not private keys, CEO Gray Chen says
She described the breach as the digital version of slipping forged withdrawal slips through a bank’s own teller window. The vault keys never left the building. Someone got into the office that prepares the slips, created paperwork that looked official, and sent it through the same approval window the bank uses every day. To the system doing the approving, it looked like a normal payout.
The outflow, however, has been stopped, Chen confirmed.
“Loss containment is confirmed. No further unauthorized transfers are possible. The specific method of system intrusion remains under active investigation. A full technical report will follow once confirmed,” she said.
The breach
The breach surfaced when Bitget’s systems flagged unauthorized transfers from some exchange hot wallets at 18:31 UTC on Sept. 24. A hot wallet stays connected to the internet so funds can move quickly. For an exchange, it is a temporary liquidity hub, analogous to an online cash drawer that handles instant trades, deposits, and withdrawals.
Chen said the hack also reached the warm-wallet layer. That is a semi-connected buffer between the automated hot wallets and fully offline cold storage. It tops up the hot wallet when balances run low and pulls excess deposits off the internet so too much capital is not left exposed.
SEC Commissioner Hester Peirce has called on U.S. regulators to use zero-knowledge proofs and digital credentials to reduce personal-data collection in KYC and AML compliance following her September 23 speech in New York.
Summary
- Peirce urged regulators to use zero-knowledge proofs for compliance checks while collecting less personal information.
- Attribute-based credentials could verify age, citizenship, investor status, or sanctions screening without exposing underlying data.
- Existing KYC and AML requirements remain unchanged because Peirce’s remarks represent her policy views only.
- The SEC’s five-year Innovation Exemption permits tokenized stocks to trade through permissioned automated market makers.
- SIFMA warned the exemption could create investor confusion, liquidity fragmentation, and parallel markets for securities.
The SEC’s published transcript states that Peirce delivered the remarks at SIFMA’s 2026 Digital Assets Conference during her penultimate week as a commissioner. She made clear that the views were her own and did not necessarily represent the SEC or her fellow commissioners.
Peirce argued that financial institutions collect large amounts of identity and transaction data because of customer identification and anti-money-laundering requirements. She described the resulting records as “ever bigger data haystacks” and said repeated collection can turn financial infrastructure into a “panopticon.” Her comments were a policy proposal, not a change to current KYC or AML rules.
Peirce wants zero-knowledge proofs used for KYC checks
In place of some existing data collection, Peirce proposed greater use of attribute-based credentials. Such credentials could establish facts including age, citizenship, accredited-investor status or whether someone has passed sanctions screening without giving each institution the underlying records.
A zero-knowledge proof could then confirm that a person satisfies a required condition without exposing information such as a name, address or income. Peirce argued that regulators should move from prescriptive collection requirements toward attribute-based verification where technology can support the required compliance check.
Her proposal would not eliminate every identity check or transaction-monitoring duty. Peirce questioned whether every institution needs to collect the same information and suggested making it easier for regulated firms to rely on trusted third-party identity verification. Existing broker-dealer rules already permit reliance on another financial institution in limited circumstances when regulatory and contractual conditions are met.
Current rules require covered broker-dealers to maintain written Customer Identification Programs. The SEC’s AML guidance lists requirements covering customer identifying information, identity verification, recordkeeping and screening against designated government lists. No SEC rule issued with Peirce’s September 23 speech removed those obligations.
SEC staff had already examined privacy-based identity tools
Peirce’s remarks followed direct work inside the SEC Crypto Task Force on privacy-preserving identity technology. On July 17, task force staff met representatives of Aztec Laboratorium Limited to discuss regulatory issues involving crypto assets and ZKPassport, according to an SEC meeting memorandum.
Materials submitted for that meeting described a system in which government-issued identity documents are checked locally on a user’s device. The system then produces a cryptographic proof for a requested fact, such as age, jurisdiction or sanctions status, without sending the underlying identity information to the business. The claims about ZKPassport’s operation came from Aztec’s presentation to SEC staff and were not an SEC endorsement of the product.
The discussion covered whether cryptographic proofs could satisfy certain customer identification, sanctions-screening and recordkeeping requirements. Aztec’s materials acknowledged that existing rules do not necessarily contemplate replacing stored information with a cryptographic proof, leaving regulatory questions unresolved.
A 2025 President’s Working Group report had previously discussed zero-knowledge proofs as one method for confirming that identity checks or screening occurred without revealing the underlying personal information. The report called for regulators to examine how digital identity tools could operate within existing AML and customer-identification requirements.
Innovation Exemption gives tokenized stocks a five-year route
Before turning to privacy and KYC, Peirce addressed the SEC’s Innovation Exemption issued September 17. She described the order as two time- and size-limited exemptions intended to let qualifying tokenized securities trade through automated market makers while the SEC considers permanent rules.
The SEC order grants conditional relief to Tokenized Securities Venues from the Exchange Act definition of an exchange. Separate relief applies to certain liquidity providers that could otherwise meet the definition of a dealer. The exemptions run from September 17, 2026 through September 17, 2031.
As crypto.news reported in its five-year tokenized stock exemption coverage, eligible venues can use permissioned AMM liquidity pools for tokenized National Market System stocks. Eligible stock tokens must provide rights matching the corresponding traditional shares, while synthetic products that merely track a stock’s price fall outside the exemption.
The framework places limits on the experiment. Tier 1 tokenized stocks are capped at 75 symbols and 0.25% of the underlying stock’s prior-month average daily volume. Tier 2 securities are capped at 250 symbols and 2.5%. Venues must make specified transaction information public and update qualifying transaction data within ten minutes.
Peirce said she preferred tokenized exposure to U.S. equities to develop domestically instead of leaving overseas platforms as the primary venue for such products. Chairman Paul Atkins separately described the exemption as a “bridge toward durable rulemaking.”
In related coverage, crypto.news reported that tokenized stocks must preserve traditional shareholder rights under the SEC framework. The exemption gives issuers an opportunity to object before an unaffiliated third party makes a tokenized version of their stock available through a qualifying venue.
SIFMA raises concerns as SEC seeks public comments
SIFMA welcomed regulatory work on tokenized securities but raised concerns about parts of the temporary framework. President and CEO Kenneth Bentsen Jr. said the group was concerned that multiple tokenized versions of listed securities trading in parallel markets could create investor confusion and price or liquidity fragmentation.
Peirce acknowledged SIFMA’s initial response during her September 23 remarks and said the exemption represented only one stage of the SEC’s work on tokenized securities. She said the agency’s longer-term task was to establish rules for intermediaries and venues handling forms of tokenized securities that existing market regulations did not originally contemplate.
The KYC proposal remains separate from that order. Peirce did not announce an SEC rulemaking that would allow zero-knowledge proofs to replace existing customer-identification records, nor did her speech create a new compliance exemption. The current broker-dealer AML framework continues to require firms to follow applicable customer-identification, monitoring and reporting rules.
For tokenized securities, meanwhile, the SEC has kept File No. 4-927 open for public comments on the Innovation Exemption. The agency is specifically requesting feedback on its five-year duration, trading limits, market effects, compliance conditions and whether any parts of the temporary framework should eventually become permanent.
Brazil’s central bank has required covered institutions to report virtual-asset transfers worth at least $10,000 to or from self-custody wallets beginning October 1, 2026.
Summary
- Resolution 588 puts $10,000 self-custody crypto transfers into mandatory Coaf reporting from October 1, 2026.
- Resolution 588 creates a reporting requirement, not a ban, transaction ceiling, or mandatory transfer freeze.
- Covered institutions must report qualifying transfers involving self-custody wallets under Brazil’s existing AML framework rules.
- Resolution 588 does not state that multiple sub-$10,000 transfers must be automatically aggregated for reporting.
- Brazil’s separate 24-hour retention rule starts January 2027 and uses same-day transaction aggregation for customers.
The Central Bank of Brazil published Resolution BCB No. 588 on September 23, amending Circular No. 3,978, the anti-money-laundering and counter-terrorist-financing framework for institutions under its supervision. The new item added to Article 49 covers transfers of virtual assets to or from self-custodied wallets when the value equals or exceeds the equivalent of $10,000.
Brazil’s $10K self-custody rule starts October 1
Resolution 588 places qualifying self-custody transfers inside the category of specific operations that covered institutions must communicate to the Financial Activities Control Council, known as Coaf. The rule applies in both directions, covering transfers sent to a self-custody wallet and transfers received from one.
The resolution does not prohibit self-custody, cap the amount a user can transfer, or state that a qualifying transaction must be blocked. B3 reported that the $10,000 figure is a mandatory reporting threshold instead of a transaction limit. The central bank has said self-custody can reduce information available for monitoring because users directly control the private keys.
By amending Article 49 of Circular 3,978, the new provision sits alongside mandatory reports for certain large cash operations and foreign-currency cash transactions. Resolution 588 adds foreign-exchange transactions involving at least $10,000 in physical foreign currency and virtual-asset transfers involving self-custody wallets at the same dollar threshold.
Resolution 588 differs from Brazil’s 24-hour hold
The October reporting requirement is separate from Resolution BCB No. 584, an anti-fraud rule published in August. Resolution 584 covers certain outbound virtual-asset transfers to foreign service providers or self-custody wallets and permits a temporary retention period of up to 24 hours under defined risk controls from January 1, 2027. Brazil’s Finance Ministry explained the measure after the central bank adopted it.
As crypto.news previously reported, Brazil’s 24-hour hold on qualifying $10,000 crypto transfers uses a different threshold calculation. Resolution 584 can apply when one transfer exceeds the threshold or when the same customer’s transfers reach the threshold in aggregate during one day. Providers can release a transfer before the full 24 hours after completing the required risk review.
Resolution 588 contains no equivalent same-day aggregation language for its automatic reporting trigger. Its text refers to a transfer with a value equal to or above $10,000. A Brazilian regulatory analysis published after the September rules found the same distinction: Resolution 584 expressly aggregates same-day transfers, while Resolution 588 does not state such a formula.
The absence of an automatic aggregation clause does not remove separate suspicious-activity monitoring obligations. Circular 3,978 requires covered institutions to assess transactions or situations that may indicate money laundering or terrorist financing, with suspicious cases subject to a separate reporting process.
Covered institutions must send reports through AML controls
Article 49 of Circular 3,978 requires institutions within its scope to communicate listed transactions to Coaf. The circular’s existing timing rule requires Article 49 communications by the next business day after the transaction or relevant provision occurs, placing the new self-custody category inside an established compliance process.
The same circular prevents institutions from informing customers or third parties that a Coaf communication has been made. Resolution 588 does not create a direct filing obligation for an individual simply because the person controls a self-custody wallet; the reporting duty operates through institutions covered by the central bank’s AML framework when they handle a qualifying transfer.
In its public explanation, the central bank said self-custody can “reduce the availability of information for monitoring and risk assessment purposes.” The statement distinguished user-controlled wallets from assets held by an institution authorized by the central bank, where customer and transaction records remain inside a supervised entity.
Resolution 588 itself does not create a new crypto tax rate, fee, or transaction levy. The measure amends Brazil’s AML/CFT reporting framework, while crypto taxation operates under separate tax rules. Crypto.news has previously covered Brazil’s separate crypto tax framework, including rules affecting gains from assets held in self-custody.
Brazil is rolling out crypto supervision in stages
Resolution 588 arrives within a series of virtual-asset rules introduced since 2025. As crypto.news reported, Brazil’s capital requirements for crypto service providers now sit alongside licensing, governance, security and compliance requirements. A separate 2026 rule has restricted virtual assets from settling payments inside regulated cross-border electronic foreign-exchange channels. Brazil’s cross-border crypto payment restrictions cover the supervised eFX system without banning ordinary crypto transfers outside that channel.
A separate central bank measure, Resolution BCB No. 589, was issued on September 23 alongside Resolution 588. It changes rules for virtual-asset service providers, including supervisory information covering customer balances, custody positions, proof of reserves and customer assets committed to staking. Provisions governing those data submissions take effect on January 1, 2027.
Resolution 589 changes another operational deadline for institutions dealing with crypto service providers. From November 6, 2026, financial institutions, payment institutions and other entities authorized by the central bank face restrictions on carrying out or facilitating virtual-asset market operations with counterparties that are not authorized to operate in Brazil, subject to the exceptions in the applicable regulation.
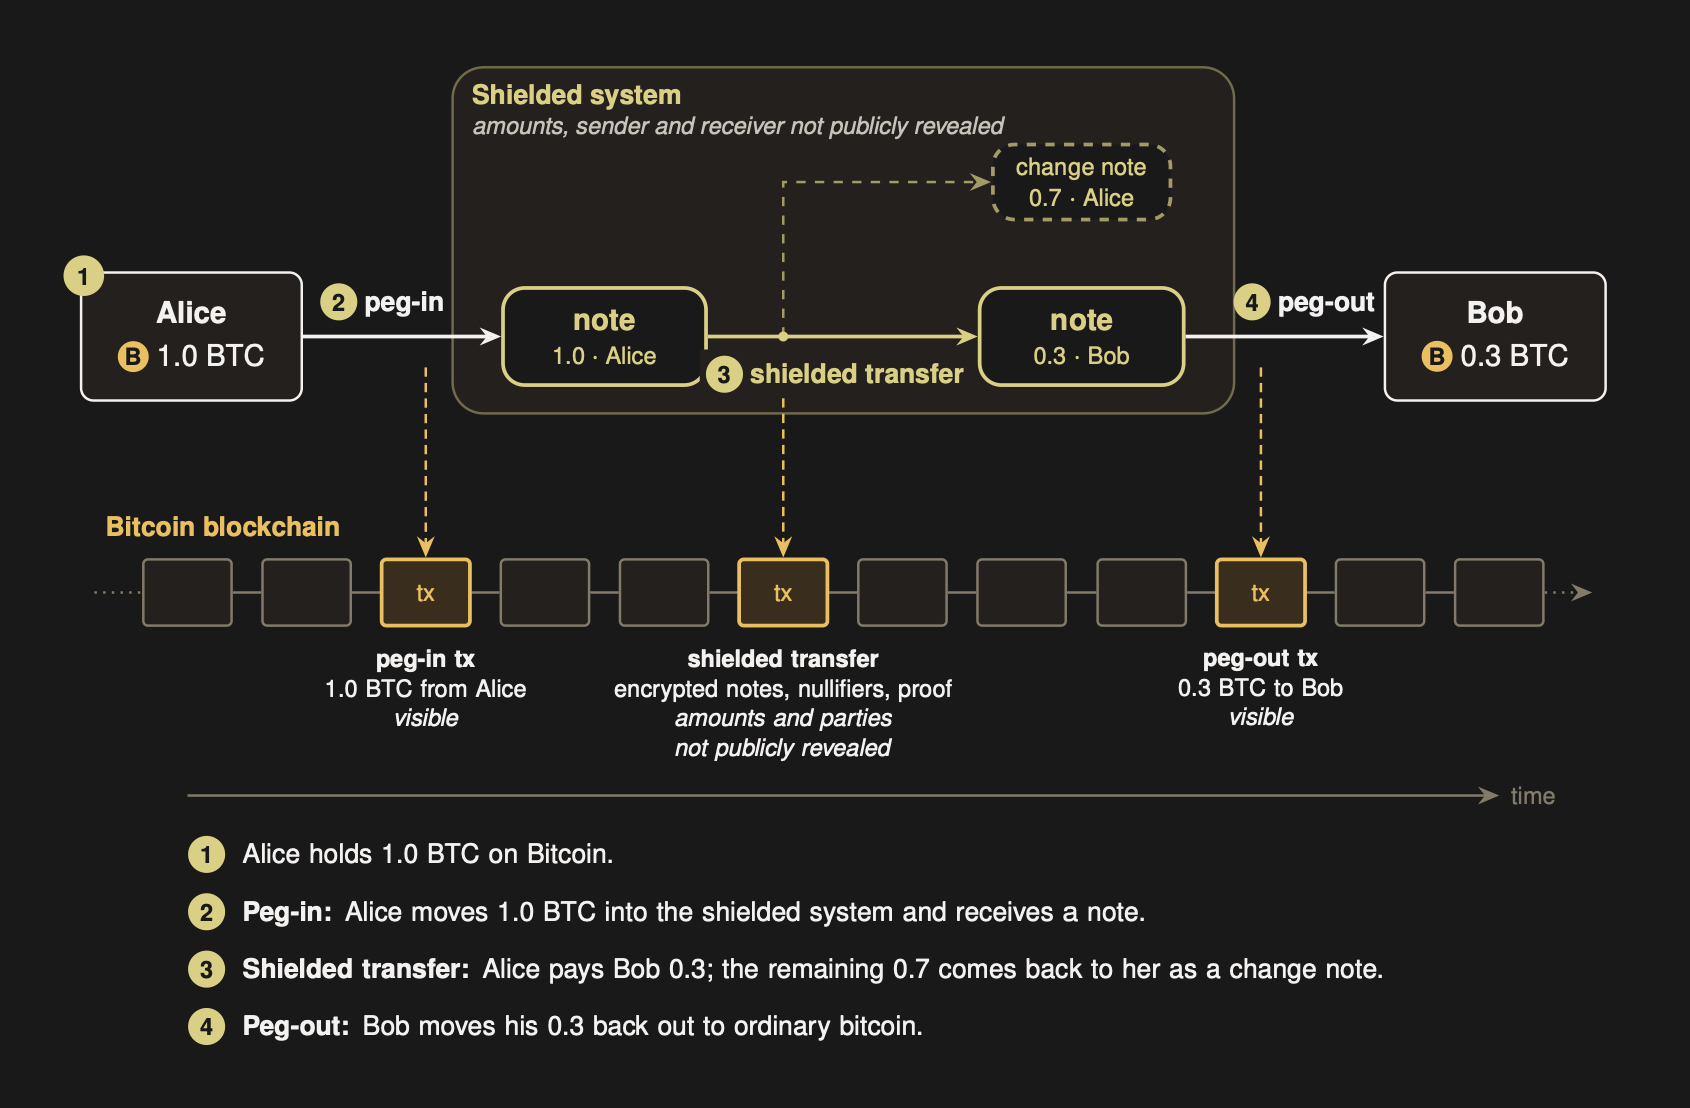
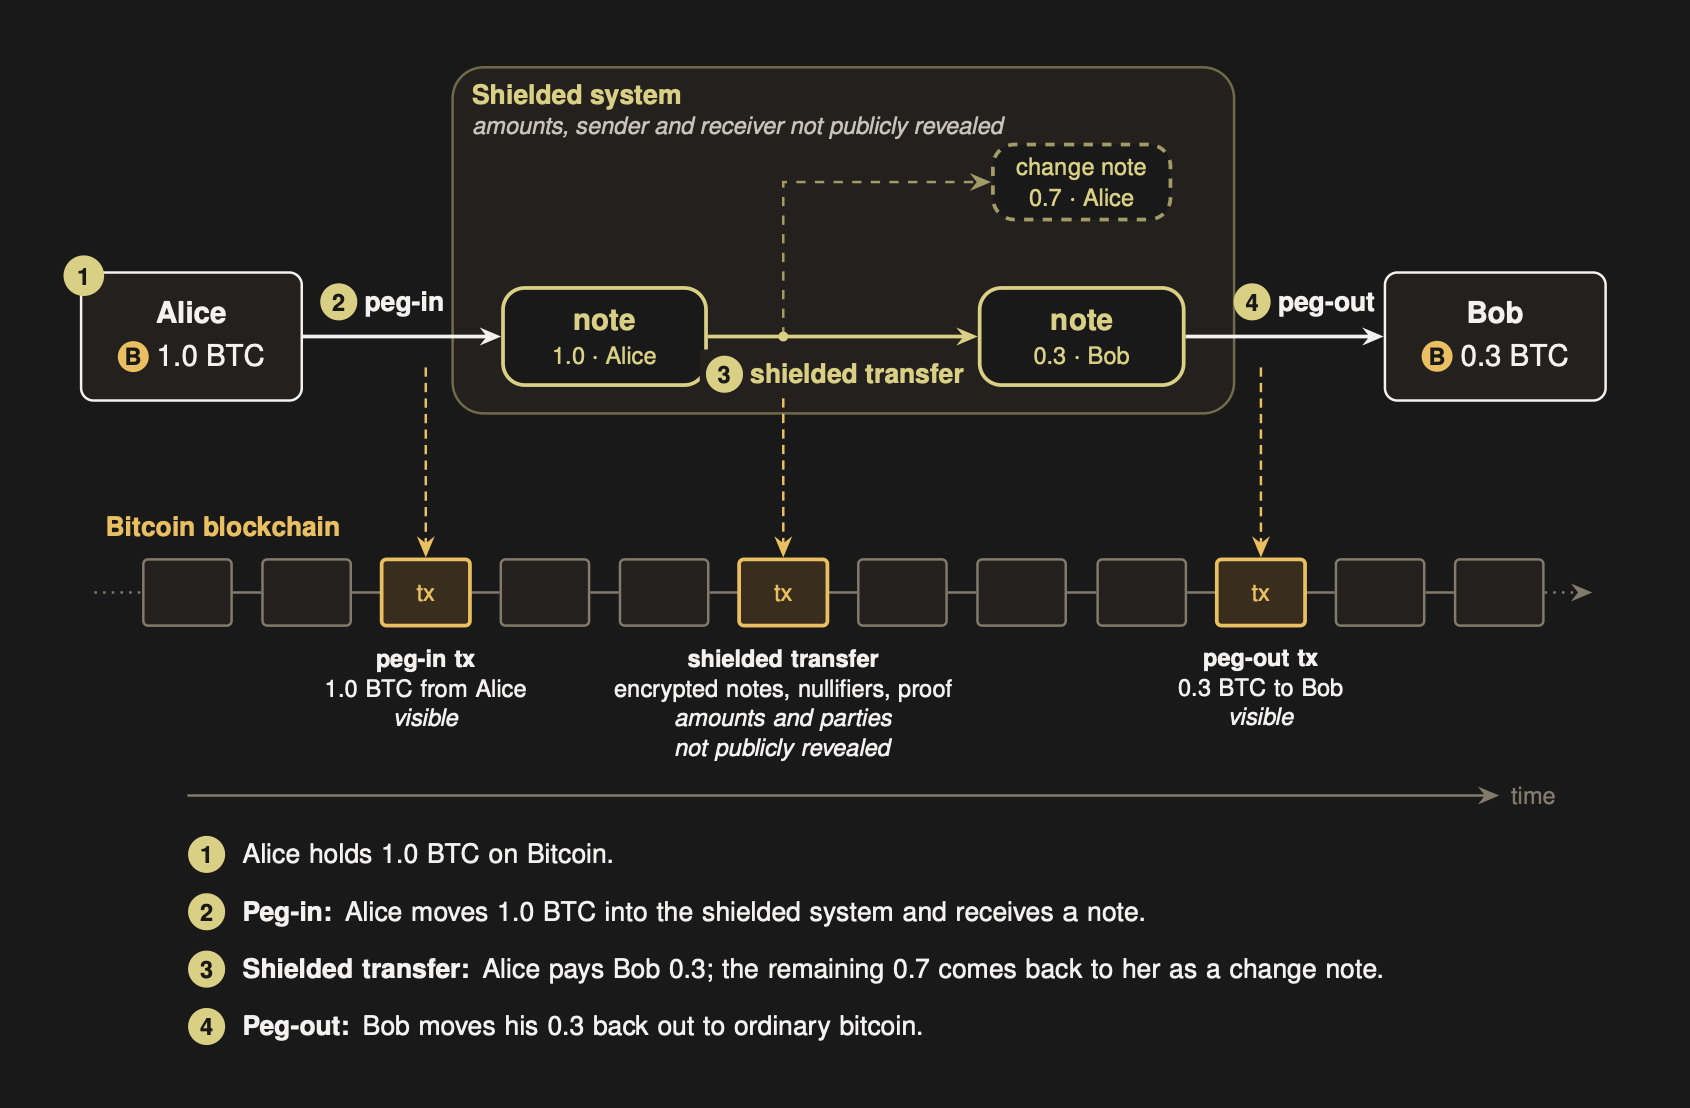
Researchers at the cryptography research firm Alloc Init have proposed a system for bringing Zcash-style private transfers to Bitcoin without requiring a soft fork.
The proposal, called Shielded Bitcoin, would conceal transaction amounts, senders, receivers and links to previously spent funds using encrypted notes and zero-knowledge proofs. The paper was published on Thursday by Clara Shikhelman, Mikhail Komarov and Aleksei Moskvin.
The proposal offers a potential path to stronger privacy for Bitcoin users without requiring consensus changes to the base protocol.
Instead of having miners enforce the privacy protocol, Shielded Bitcoin would use Bitcoin as “a neutral publication and ordering layer,” the researchers wrote. Separate software called indexers would then verify zero-knowledge proofs, check that funds haven’t been double-spent, and reconstruct the state of the shielded system.
Shielded Bitcoin’s design explicitly draws from Zcash’s architecture. The researchers said it similarly uses encrypted notes, public nullifiers that mark notes as spent, and zero-knowledge proofs that show transactions are valid. Unlike Zcash, Shielded Bitcoin would not operate its own blockchain or consensus mechanism.
Shielded Bitcoin draws mixed reactions
Developer Vadim Zavodil criticized the proposal on X, arguing that much of its privacy stack had already been implemented by Zcash. He questioned how much privacy a newly launched system could initially provide, arguing that a new shielded pool would start without the anonymity set Zcash has accumulated over years of use.
“Privacy is a function of the crowd. Zcash has a real shielded pool built over years,” he wrote. “A brand new metaprotocol starts at zero, so your first private transfer hides in a crowd of one.”
In a companion post explaining the proposal, the Shielded Bitcoin researchers acknowledged a similar limitation, saying that large deposits do not automatically create a large anonymity set. They said observers may still be able to narrow down relationships between transfers if a small number of actors create most notes or wallets exhibit distinctive behavior.
Related: Zcash’s November upgrade could freeze funds in legacy Sprout pool
Pierre-Luc Dallaire-Demers, founder of post-quantum cryptography firm Pauli Group, raised a separate issue, describing the construction as interesting but “not quantum resistant at all.” Dallaire-Demers later said he was exploring what a fully post-quantum version could look like, assuming Bitcoin eventually adopts a post-quantum signature scheme.
Zerocash co-author and StarkWare CEO Eli Ben-Sasson was more supportive of the proposal’s direction. In response to Alloc Init’s announcement, Ben-Sasson said the original intent behind the Zerocash paper, which preceded Zcash, was to bring privacy to Bitcoin.
Ben-Sasson said he had not yet read the Shielded Bitcoin paper but would like to see the vision of privacy and scalability through zero-knowledge proofs materialize on Bitcoin’s base layer.
Magazine: Winners and losers of the SEC’s new tokenized stocks rules
Bitget has said its preliminary probe into a $351.6 million wallet breach found no private-key leak, while withdrawals remain suspended after unauthorized transfers on September 24, 2026.
Summary
- $351.6 million in assets were affected after Bitget detected unauthorized wallet transfers on September 24.
- Bitget says private keys stayed secure, while attackers breached systems and transferred funds directly off-platform.
- Withdrawals remain suspended, while deposits and trading continue during Bitget’s ongoing security review and repairs.
- Lookonchain estimates XRP was the largest stolen asset, with 102.93 million tokens worth $157.48 million.
- Gracy Chen says North Korean involvement remains unconfirmed despite preliminary IP and VPN similarities found.
Bitget’s official security notice states that its systems detected the transfers at 18:31 UTC and activated emergency procedures within minutes. The exchange estimated that approximately $351.6 million in assets were affected and said the incident reached portions of its hot and warm wallet layers. Cold wallets remained secure under Bitget’s internal three-tier classification, the company said.
The exchange temporarily stopped withdrawals while leaving deposits and trading open. Bitget said customer account balances remained accurate and its User Protection Fund, valued at more than $464 million, could cover the estimated loss. Law enforcement agencies and on-chain security firms have been notified, while addresses tied to the abnormal transfers have been flagged.
Bitget says private keys were not exposed
During a live Q&A after the breach, CEO Gracy Chen said investigators had ruled out a leak of private keys used by Bitget’s cold, warm and hot wallets. Chen said attackers entered Bitget’s systems and transferred funds directly, without using customer withdrawal requests. Investigators were still working to determine the precise entry point.
A report on the same live session said Bitget’s security team had identified part of the attack route. The preliminary finding described a compromise of a core backend wallet service, where false transfer data reached the exchange’s approval-signature process. Bitget has not yet published the technical evidence behind that finding, leaving the exact intrusion method under review.
Chen said measures intended to prevent further outflows had been completed. Engineering teams were still repairing systems, strengthening security controls and preparing withdrawal services for reopening. No fixed restart time had been announced by early September 25.
The first public notice had avoided naming an attack method. Bitget wrote, “We will not speculate on the attack vector until the investigation is complete.” Its subsequent backend-system finding therefore remains preliminary until the promised root-cause report is released.
As crypto.news reported after the $1.4 billion Bybit theft in 2025, forensic investigators traced that attack to compromised Safe infrastructure. Investigators said Bybit’s own security systems remained intact during that incident.
On-chain tracking puts XRP at the top of stolen assets
On-chain estimates have continued changing as researchers identify more addresses and assets. Lookonchain placed the stolen portfolio at roughly $356.8 million using token prices when it published its update, slightly above Bitget’s approximately $351.6 million internal estimate. The figures come from separate accounting methods and should not be treated as identical measurements.
Lookonchain listed 102.93 million XRP worth $157.48 million as the largest component. Its breakdown included 31,890 ETH valued near $85.75 million, 34.75 million USDT, 21.05 million USDC, 19.67 million USD₮0, 3,000 XAUt, 12,719 BNB, 821,012 AVAX and 20.59 million TRX. The figures remain an external on-chain estimate, not Bitget’s final transaction-level accounting.
Earlier blockchain tracking produced lower totals because analysts were following publicly labeled wallets while the transfers were still unfolding. Wu Blockchain recorded visible Bitget-linked flows of roughly $178 million to $190 million before the exchange disclosed its internal estimate.
North Korea link remains preliminary
Chen raised a possible North Korean connection during the live Q&A, but she stopped short of confirming who carried out the breach. She said investigators had identified IP addresses matching VPN services used by a North Korean hacking group.
“We’ve identified some IP addresses that match the VPN choices by a certain DPRK group,” Chen said. She later described the observed pattern as similar to previous North Korean operations. Bitget said it did not currently believe the incident involved an insider.
No government agency had publicly attributed the Bitget breach to North Korea in the latest information reviewed. Investigators were still examining the affected systems, infrastructure and method used to enter the platform. Chen’s comments therefore represent Bitget’s preliminary suspicion, not a confirmed attribution.
North Korea has previously been formally linked to major exchange thefts. As crypto.news reported in August, Bybit filed a U.S. federal lawsuit against North Korea, its Reconnaissance General Bureau and the Lazarus Group over the February 2025 theft. The FBI had previously attributed the Bybit attack to North Korean actors.
Crypto.news has separately covered North Korea-linked operations that drained $577 million from Drift Protocol and KelpDAO in April 2026. Those cases involved different attack paths and do not establish who carried out the Bitget breach. North Korea-linked crypto attacks in 2026
Withdrawals stay paused as Bitget prepares full report
Bitget’s withdrawal suspension notice says withdrawals will return only after the security review is complete. Deposits and trading remain available, while technical teams continue system recovery and security work.
During the live Q&A, Chen said some stolen funds had been recovered, although she did not disclose an amount. She said Bitget was working with blockchain foundations and other partners on recovery efforts. No independently verified total for frozen or recovered assets had been disclosed in the latest updates reviewed.
The protection fund remains part of Bitget’s response to the loss. The company says it holds more than $464 million and can cover the approximately $351.6 million affected, while customer account balances remain accurate. Bitget has not yet published a transaction-by-transaction reconciliation explaining the difference between its estimate and Lookonchain’s later market-value calculation.
Bitget has promised a full incident report containing its root-cause analysis and corrective actions within 24 hours of the original security notice. The notice was published on September 24 at 21:39 UTC, putting the detailed report within a September 25 timetable under the company’s stated commitment.
Celine Dion Gets Animated With Bodyguard Amid Residency
“We watched him walk to his death” Families of knife crime victims share powerful video message
Inox Clean Energy likely to file Rs 10,000 crore IPO with Sebi




-

 Fashion7 days ago
Weekend Open Thread: Talbots – Corporette.com
-

 Crypto World2 days ago
Goldman Sachs and Deutsche Bank Agree: The S&P 500 Rally Isn't Over
-

 Tech4 days ago
Researchers escape OpenAI Codex sandbox to run commands on host
-

 Fashion18 hours ago
8 iPhone Accessories That Add Personality
-

 Crypto World4 days ago
Who Needs CLARITY Anyway? ARB Could See 70X Increase: Hodler’s Digest
-

 Crypto World6 days ago
Circle launches Arc Studio AI agent for building onchain apps
-
 NewsBeat6 days ago
Trump says US has reached an agreement to take permanent control of Greenland’s security
-

 Crypto World6 days ago
Trading Bitcoin on Robinhood? Why 2% Spread Has Traders Worried
-

 Crypto World6 days ago
Bitcoin price breaks channel as RSI climbs to 63
-

 Tech5 days ago
Trump suggests rebranding AI with a new name, says he’s also creating an AI Force
-

 Business4 days ago
Analog Devices (ADI) Bets $1.35 Billion on Chips that Let Machines Think for Themselves
-

 Tech4 days ago
Google’s $899 Googlebook is a bet that you’ll buy a new laptop for Gemini
-

 Crypto World4 days ago
Coinbase, Robinhood, Circle Seen as Tokenized-Stock Winners
-
 Business2 days ago
Oil Price Today (September 23): Crude oil below $100 on hopes of US-Iran talks. What did Trump say?
-

 Crypto World2 days ago
This Bearish Netflix Stock Trade Can Cash In On Video Streaming Giant’s Woes
-

 Crypto World3 days ago
Trump-Xi Polymarket Odds for Handshake Hit 50%
-

 Crypto World6 days ago
World Money launches in 150+ countries with Stripe
-

 Crypto World7 days ago
Silver prices recover quickly, hitting weekly high today
-

 Crypto World1 day ago
Crude Oil Prices Pressured by Diplomatic Hopes in the Middle East
-

 Crypto World1 day ago
Bitcoin Threatens Sub-$84,000 Breakdown as Long Liquidations Spike
You must be logged in to post a comment Login