
Crypto World
Bitget hacker swaps USDC for ETH as Circle faces renewed freeze questions

The Bitget hacker has converted stolen USDC into ETH after a breach that the exchange valued at about $351.6 million, renewing questions about when Circle freezes funds linked to an attack.
Summary
- Security researcher Taylor Monahan flagged USDC transfers and swaps tied to the Bitget attacker.
- Bitget estimated the theft at $351.6 million and temporarily suspended withdrawals.
- Circle says it freezes USDC when legally compelled, while researchers have criticized its response time in past hacks.
- A U.S. lawsuit over the Drift exploit has raised similar questions about stolen USDC moving across chains.
Security researcher Taylor Monahan flagged the attacker’s activity on X, pointing to USDC moving through wallets as stolen assets were converted into ETH. Monahan questioned why the funds remained movable despite Circle’s ability to block transfers from specific USDC addresses.
The transactions show the attacker using USDC during the conversion process, according to Monahan’s account. Her criticism concerns Circle’s response to identifiable funds, although the public account of the transfers does not establish whether Circle received a legal order concerning those addresses or when it learned their identities.
Bitget attacker moves USDC after $351.6 million breach
Bitget said its security systems detected unauthorized transfers from some hot wallets at 18:31 UTC on Sep. 24. The exchange activated an emergency response, suspended customer withdrawals and estimated the affected assets at approximately $351.6 million. Deposits and trading remained available, while Bitget said account balances were accurate and its cold wallets were secure.
In its initial report on the breach, crypto.news covered Bitget CEO Gracy Chen’s account of the preliminary investigation. Chen said investigators had ruled out a leak of wallet private keys and believed the attackers had entered the exchange’s systems to move funds directly, without submitting customer withdrawal requests. Bitget was still investigating the entry point and had not released a final account of the attack.
The theft involved several assets, leaving investigators to follow more than one route for the stolen funds. On-chain tracker Lookonchain estimated the stolen portfolio at roughly $356.8 million using prices at the time of its update. Its breakdown included 102.93 million XRP worth about $157.48 million, 31,890 ETH worth about $85.75 million, and 21.05 million USDC. Lookonchain’s changing on-chain estimate and Bitget’s internal loss figure use different measurements.
Bitget said it had flagged addresses linked to the abnormal transfers and notified law enforcement and on-chain security firms. Chen said measures to prevent further outflows had been completed as engineers worked on repairs and the return of withdrawal services.
Monahan’s concern centers on the portion of the stolen assets held in USDC. Circle’s USDC terms say the issuer reserves the right to block transfers to and from certain on-chain addresses under its blocklisting policy. Once an attacker swaps USDC for ETH, however, a block on a USDC address cannot freeze the ETH received in that trade.
Circle’s freeze policy draws a response-time dispute
Circle has described a narrower standard for using its technical controls than the one its critics seek during a live exploit. In an April statement on lawful intervention, published after the Drift Protocol hack, the company said it exercises its freeze ability when legally compelled by an appropriate authority. Circle argued that letting an issuer decide on its own whose assets to block could put legitimate holders’ property rights at risk.
Its USDC terms also say Circle may be required to freeze tokens after receiving a legal order from a valid government authority. The terms separately reserve the right to block certain addresses that Circle determines may be associated with illegal activity or a violation of its terms. They state that an on-chain USDC transaction cannot be reversed or recalled once initiated.
Those provisions matter to U.S. holders because Circle issues a dollar-backed stablecoin used across exchanges and decentralized applications, while its freeze decisions can affect access to tokens at a particular address. Circle’s stated policy places lawful process at the center of that decision. Monahan’s criticism focuses on the time available to intervene before a suspected attacker finishes moving or swapping the USDC.
Circle said in its April statement that tools for faster intervention exist, but legal frameworks for quicker, coordinated action while protecting users’ rights remain incomplete. The company called for clearer rules and for security measures across protocols, wallets, exchanges and stablecoin issuers.
ZachXBT documented 15 earlier USDC cases
On-chain investigator ZachXBT alleged in April that Circle had taken minimal action or failed to act quickly enough in 15 cases involving more than $420 million in suspected illicit USDC flows since 2022. His list covered hacks and fraud cases in which he said stolen funds remained movable despite time to identify the activity.
As previously covered by crypto.news, ZachXBT cited about $9 million in USDC linked to the July 2025 GMX hack and said wallets involved in the Cetus hack were blocked only after the stolen USDC had been converted into ETH. He also alleged that attackers in the Drift case moved roughly $232 million over about six hours and more than 100 transactions before converting the funds.
The Drift transfers became the subject of a U.S. civil case. In April, a claimant sued Circle over transfers following the exploit, alleging that the issuer failed to stop roughly $230 million in stolen USDC routed through its Cross-Chain Transfer Protocol. The complaint, filed in a federal district court in Massachusetts, argues that earlier intervention could have reduced the losses. Those are the claimant’s allegations, rather than a court finding against Circle.
In that case, the claimant also pointed to Circle’s freeze of 16 USDC-linked wallets tied to a separate sealed U.S. civil matter as evidence that the issuer could block addresses. Circle’s April public statement, issued after the Drift attack, said freezes require lawful authority and called for legal structures that would permit faster action during future incidents.

Crypto World
Another appeals court rules against prediction market provider Kalshi, says sports contracts are subject to state regulations
States have tried to wrangle prediction markets offering sports-related contracts under their regulatory frameworks since they started taking off after the 2024 election, arguing that these markets are competing with state gambling platforms and offering identical products to gambling sites and apps. For many states, the issue is that federally regulated platforms do not pay state taxes, while still competing with state-regulated platforms. Another major point of contention is the fact that prediction markets often offer their products to people as young as 18, rather than 21, like most state gambling operators.
In Friday’s ruling, the three-judge panel said it agreed that Kalshi did have the right to bring a case, but disagreed that the products in question were federally regulated swaps.
“While we agree with Kalshi that its sports-event contracts are conditioned on the occurrence of ‘event[s],’ we conclude that Kalshi’s contracts do not depend on events that are ‘associated with a potential financial, economic, or commercial consequence’ within the meaning of the statute,” the ruling said.
The ruling used the New York Giants winning a Super Bowl as an example case, saying the result could depend on how the “event” in question is defined. If the event is the Giants winning, then that victory would be described as “that event having occurred.”
Her crypto work included a wide range of policy statements and guidance that clarified the agency’s position on various aspects of the industry, including mining, staking, memcoins and — most importantly — a series of definitions for classifying different types of crypto assets and which regulator would have dominion. More recently, the agency began proposing formal rules, beginning with one known as Regulation Crypto Assets, which set up a system for offering crypto assets without triggering stringent securities regulations.
The agency’s biggest splash, though, may have been its recent opening of the pathway for tokenizing securities. The effort known as the “innovation exemption” is meant to launch the tokenized securities era in a limited, five-year approach that will inform plans for eventual agency rules that make it more permanent.
“Maximizing people’s freedom to choose what is best for themselves and their families within sensible regulatory parameters designed to give them the confidence to transact with others is a delicate and vitally important task for the regulator,” Peirce, who’s going to be an associate professor at Regent University School of Law, wrote in her resignation.
Peirce acknowledged her nickname, “Crypto Mom,” in a 2019 speech during the industry-resistant era at the agency, and she also noted the agency had “hindered innovation and growth,” saying, “The only guidance out of the SEC is a parade of enforcement actions and a set of staff guidance documents and staff no-action letters.”
Google has disclosed that its PageBreak AI security agent has found over 500 cross-site scripting vulnerabilities across the company’s web applications.
Summary
- Google says PageBreak tests suspected flaws against running applications before sending reports to product teams.
- The agent uses Gemini models for most scans and separate tools to confirm whether an exploit works.
- Applications built on Google’s high-assurance frameworks had two XSS findings as of Sep. 4.
- Google plans to connect PageBreak more closely with CodeMender, which generates security fixes.
The Google Product Security team said PageBreak began as a pilot in November 2025 and became a formal project in January 2026. It tests Google’s own web applications and has found cross-site scripting, or XSS, flaws even on sensitive company domains. Google did not identify the affected applications in its announcement.
XSS occurs when an application allows an attacker’s script to run in another user’s browser. Depending on the application and the attacker’s access, the flaw can expose data or let someone act through an affected user’s session. Google reported more than 500 findings across its applications, but did not give a breakdown by product or severity.
How PageBreak confirms suspected flaws
Rather than sending every suspected bug to a product team, PageBreak passes each candidate to a specialized validator. For an XSS finding, the validator inserts a JavaScript payload, loads the affected page, and checks whether the script runs. Google said the validation step has kept the system’s false positive rate close to zero.
The agent can also test other types of flaws. According to Google, its validators check whether an injected input changes a database query, whether an application exposes a file through path traversal, or whether it can be made to execute code. A separate check looks for requests that an application sends to internal services.
Most PageBreak scans use Gemini models, including Gemini 3.1 Pro and Gemini 3.5 Flash, although Google said the agent can work with different models. The validators themselves are not written by the AI agent. Google also runs agents through repeated attempts because a model can follow an unproductive path before finding a workable exploit.
Google built the validation process in response to a problem its security staff had encountered: AI-generated reports can describe convincing attack paths that fail when tested. Under PageBreak’s process, unverified candidates stay within the security team’s workflow. They can guide later scans or help engineers build new validators, but Google said they are not sent to product teams as confirmed bugs.
PageBreak found two flaws in protected applications
Among hundreds of applications built on Google’s high-assurance web frameworks, PageBreak identified two XSS vulnerabilities as of Sep. 4, Google said. Both were confined to internal applications or debug endpoints with gaps in their security protections. The result covers that group of applications; Google’s figure of over 500 findings covers its first-party web applications more generally.
The framework result gives Google a way to test how its application design holds up against repeated scans. PageBreak also has access to company tools that help it inspect applications at scale. Google said its code repository lets the agent follow paths across services, while security data from live web traffic can connect a requested page to the relevant source code. Existing scanners give it authenticated access to internal sites that can be difficult for an outside researcher to examine.
Those resources help explain the scope of Google’s findings without suggesting that another organization could obtain the same results simply by running a Gemini model. PageBreak’s reported count comes from scans of Google’s applications with access to Google’s code, traffic data and testing systems.
Crypto teams face the same verification workload
The problem of checking AI-generated security reports has also surfaced in crypto software. In July, Ethereum Foundation security research described a process in which agents develop potential findings and separate reviewers try to reproduce them. The foundation reported one confirmed flaw in libp2p, later disclosed as CVE-2026-34219, while warning that plausible reports can involve unreachable code or attack conditions that do not hold in practice.
For teams that handle crypto users’ funds, the difference between a candidate issue and a working exploit affects how quickly a report can lead to a fix. An August Bitcoin Red Team scan logged 7,958 findings across 501 open-source projects after 108 hours. At that point, 24.7% of the findings had reproducible proofs; the full tally did not represent 7,958 confirmed exploitable vulnerabilities.
Earlier reporting on crypto bug bounties described a similar review burden. Cosmos Labs co-CEO Barry Plunkett said in April that submissions to its program had risen 900% from the previous year, including both valid and invalid reports. PageBreak is an internal Google tool, and Google has not said it is available to crypto projects.
Google plans to pair findings with fixes
Even after limiting reports to verified findings, Google said its product teams still receive a high volume of security work. PageBreak is therefore working with other Google projects, including CodeMender, an agent that generates bug fixes. Google plans to deepen that connection so product teams can review proposed fixes alongside confirmed vulnerabilities.
OG.com Markets is seeking US regulatory approval to offer perpetual futures tied to individual stocks, as trading platforms push to bring the popular derivatives product to US equity markets.
In a Thursday filing with the Commodity Futures Trading Commission (CFTC), OG.com proposed new rules allowing it to list cash-settled single-stock futures that never expire and can trade 24 hours a day, five days a week.
OG.com was recently spun out of crypto exchange Crypto.com as an independent prediction markets and derivatives platform valued at $5 billion. At the time, CEO Kris Marszalek said the platform planned to expand beyond prediction markets into futures and perpetual contracts.
Shortly after the spin-off, Robinhood took an equity stake in OG.com as part of a multi-year deal to use its CFTC-regulated derivatives exchange and clearinghouse for prediction markets.
Unlike traditional futures contracts, perpetual futures, or “perps,” have no expiration date, allowing traders to maintain exposure without periodically rolling into new contracts. The product was pioneered in crypto by BitMEX in 2016.
Related: President Trump’s media company to terminate Crypto.com deal
Perpetual futures push expands into US stocks
Crypto trading platforms and prediction markets are increasingly looking to bring one of the digital asset market’s most popular derivatives products to US stocks, with OG.com joining a growing group seeking regulatory approval.
On Sept. 18, Coinbase, Kraken parent Payward through its Bitnomial exchange, and prediction market Kalshi all filed to offer perpetual futures tied to individual US stocks.
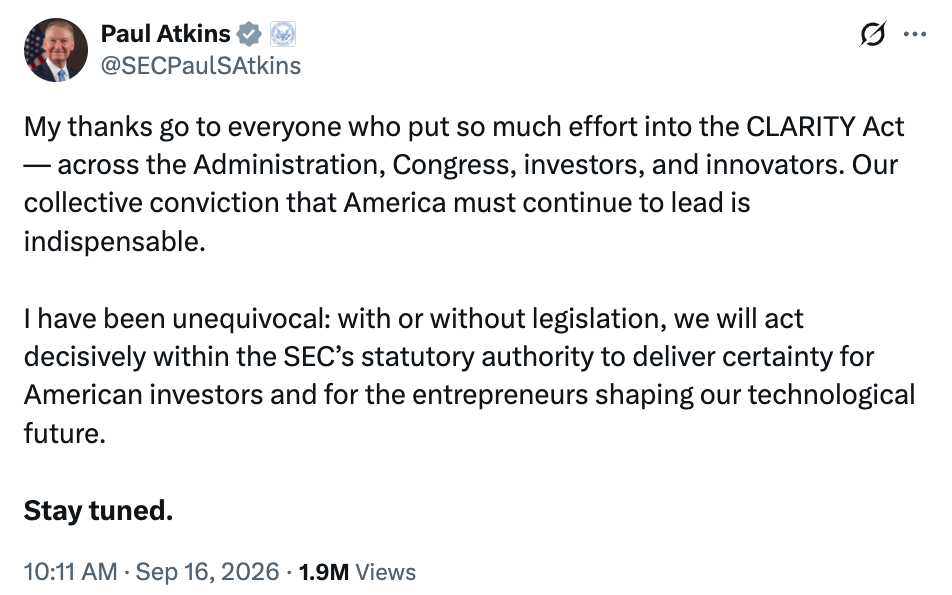
The filings came after US regulators, including the Securities and Exchange Commission (SEC) and CFTC, pushed ahead with crypto initiatives despite the CLARITY Act failing to advance in the Senate on Sept. 15.
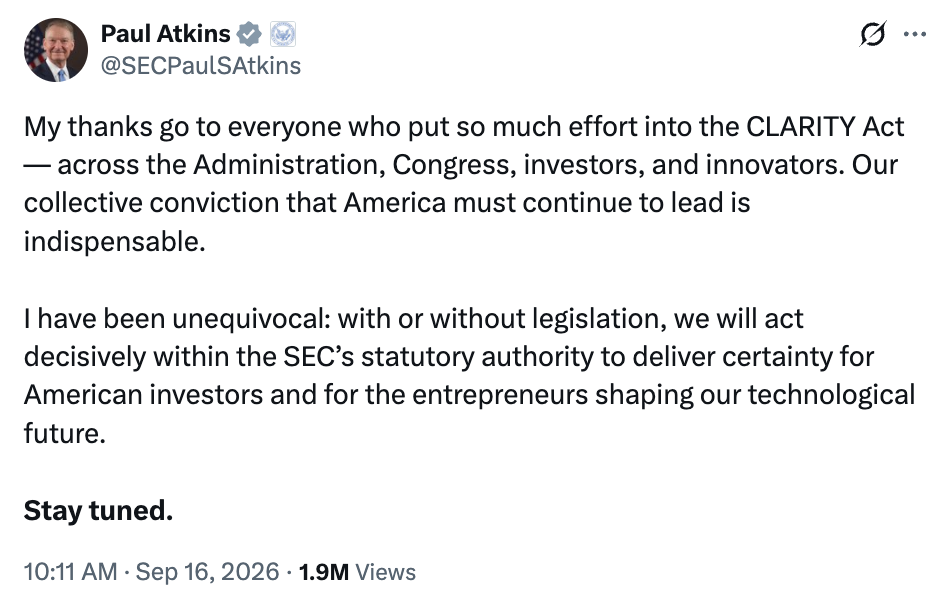
Source: Paul Atkins
Just days after the vote, the SEC cleared limited onchain trading of tokenized US stocks under its Innovation Exemption, while the CFTC expanded regulatory relief for software providers connecting users to regulated derivatives platforms, including those offering perpetual contracts.
The CFTC had already begun laying the regulatory groundwork for perpetual futures months earlier.
In May, the agency established a case-by-case review process for perpetual contracts and approved Kalshi’s Bitcoin perpetual futures product, followed in June by temporary relief allowing certain registered exchanges to convert existing crypto futures into contracts without expiration dates.
Magazine: Exchanges reporting crypto gains to IRS becomes tax nightmare
Crypto World
Appeals court rules that states can regulate Kalshi’s sports prediction markets, dealing another legal blow to platforms
The 6th U.S. Circuit Court of Appeals ruled on Friday that states have a right to regulate sports-related event contracts on prediction market platforms, marking a second major legal defeat for the industry as a fight at the U.S. Supreme Court looms.
In a unanimous decision, the three judge panel said that Ohio and Tennessee are permitted to apply their state gambling laws to Kalshi’s sports-related event contracts.
“We hold that Kalshi has not shown that its sports-event contracts satisfy the statutory definition of a ‘swap’ so as to fall within the scope of the CFTC’s ‘exclusive jurisdiction,’” the opinion said.
Kalshi and other prediction market platforms argue all event contracts are swaps, a type of financial derivative that is regulated by the Commodity Futures Trading Commission. However, states assert that platforms’ sports-related offerings amount to gambling, and thus should be regulated by their laws related to sports betting.
This disagreement has spawned a legal battle across the country as states sue platforms for operating what they often claim are illegal gambling operations, while exchanges also sue states to block them from enforcing local laws on what they argue should be federally-regulated financial exchanges.
The CFTC has sued nine states to defend what it believes is its exclusive right to regulate event contracts, given to it by the Commodity Exchange Act. But the 6th Circuit panel rejected that notion.
“Even assuming that Kalshi’s sports-event contracts are swaps, we alternatively hold that the CEA neither expressly nor impliedly preempts Ohio’s or Tennessee’s gambling laws,” the opinion said. The decision overturns a Tennessee federal district court ruling that sided with Kalshi, and reaffirms a decision by a federal district court in Ohio that sided with the states’ argument.
“Kalshi attempted an end run around Tennessee law to avoid any of the rules or taxes associated with sports gambling. They failed,” said Jonathan Skrmetti, Tennessee’s attorney general.
“Sports wagering is heavily regulated because it can do a lot of harm, and I’m glad we thwarted Kalshi’s efforts to remove every safeguard and put Tennessee sports bettors at risk,” he added.
Kalshi nor the CFTC immediately responded to requests for comment. CNBC has also reached out to the Ohio attorney general’s office for comments.
The latest ruling now means prediction market platforms have notched two losses in legal fights at the appeals court level. The 9th U.S. Circuit Court of Appeals ruled last month that Nevada has a right to regulate sports-related event contracts, stating that they were sports bets and not swaps. Meanwhile, the 3rd U.S. Circuit Court of Appeals ruled against New Jersey in April and said the CFTC has the exclusive right to regulate all swaps, no matter the contract type.
New Jersey appealed that decision in a petition to the Supreme Court earlier this month. It is not clear whether the Supreme Court will take up the case now, or wait until further decisions from circuit courts on the issue of sports-related event contracts are delivered.
Disclosure: CNBC and Kalshi have a commercial relationship that includes customer acquisition and a minority investment.
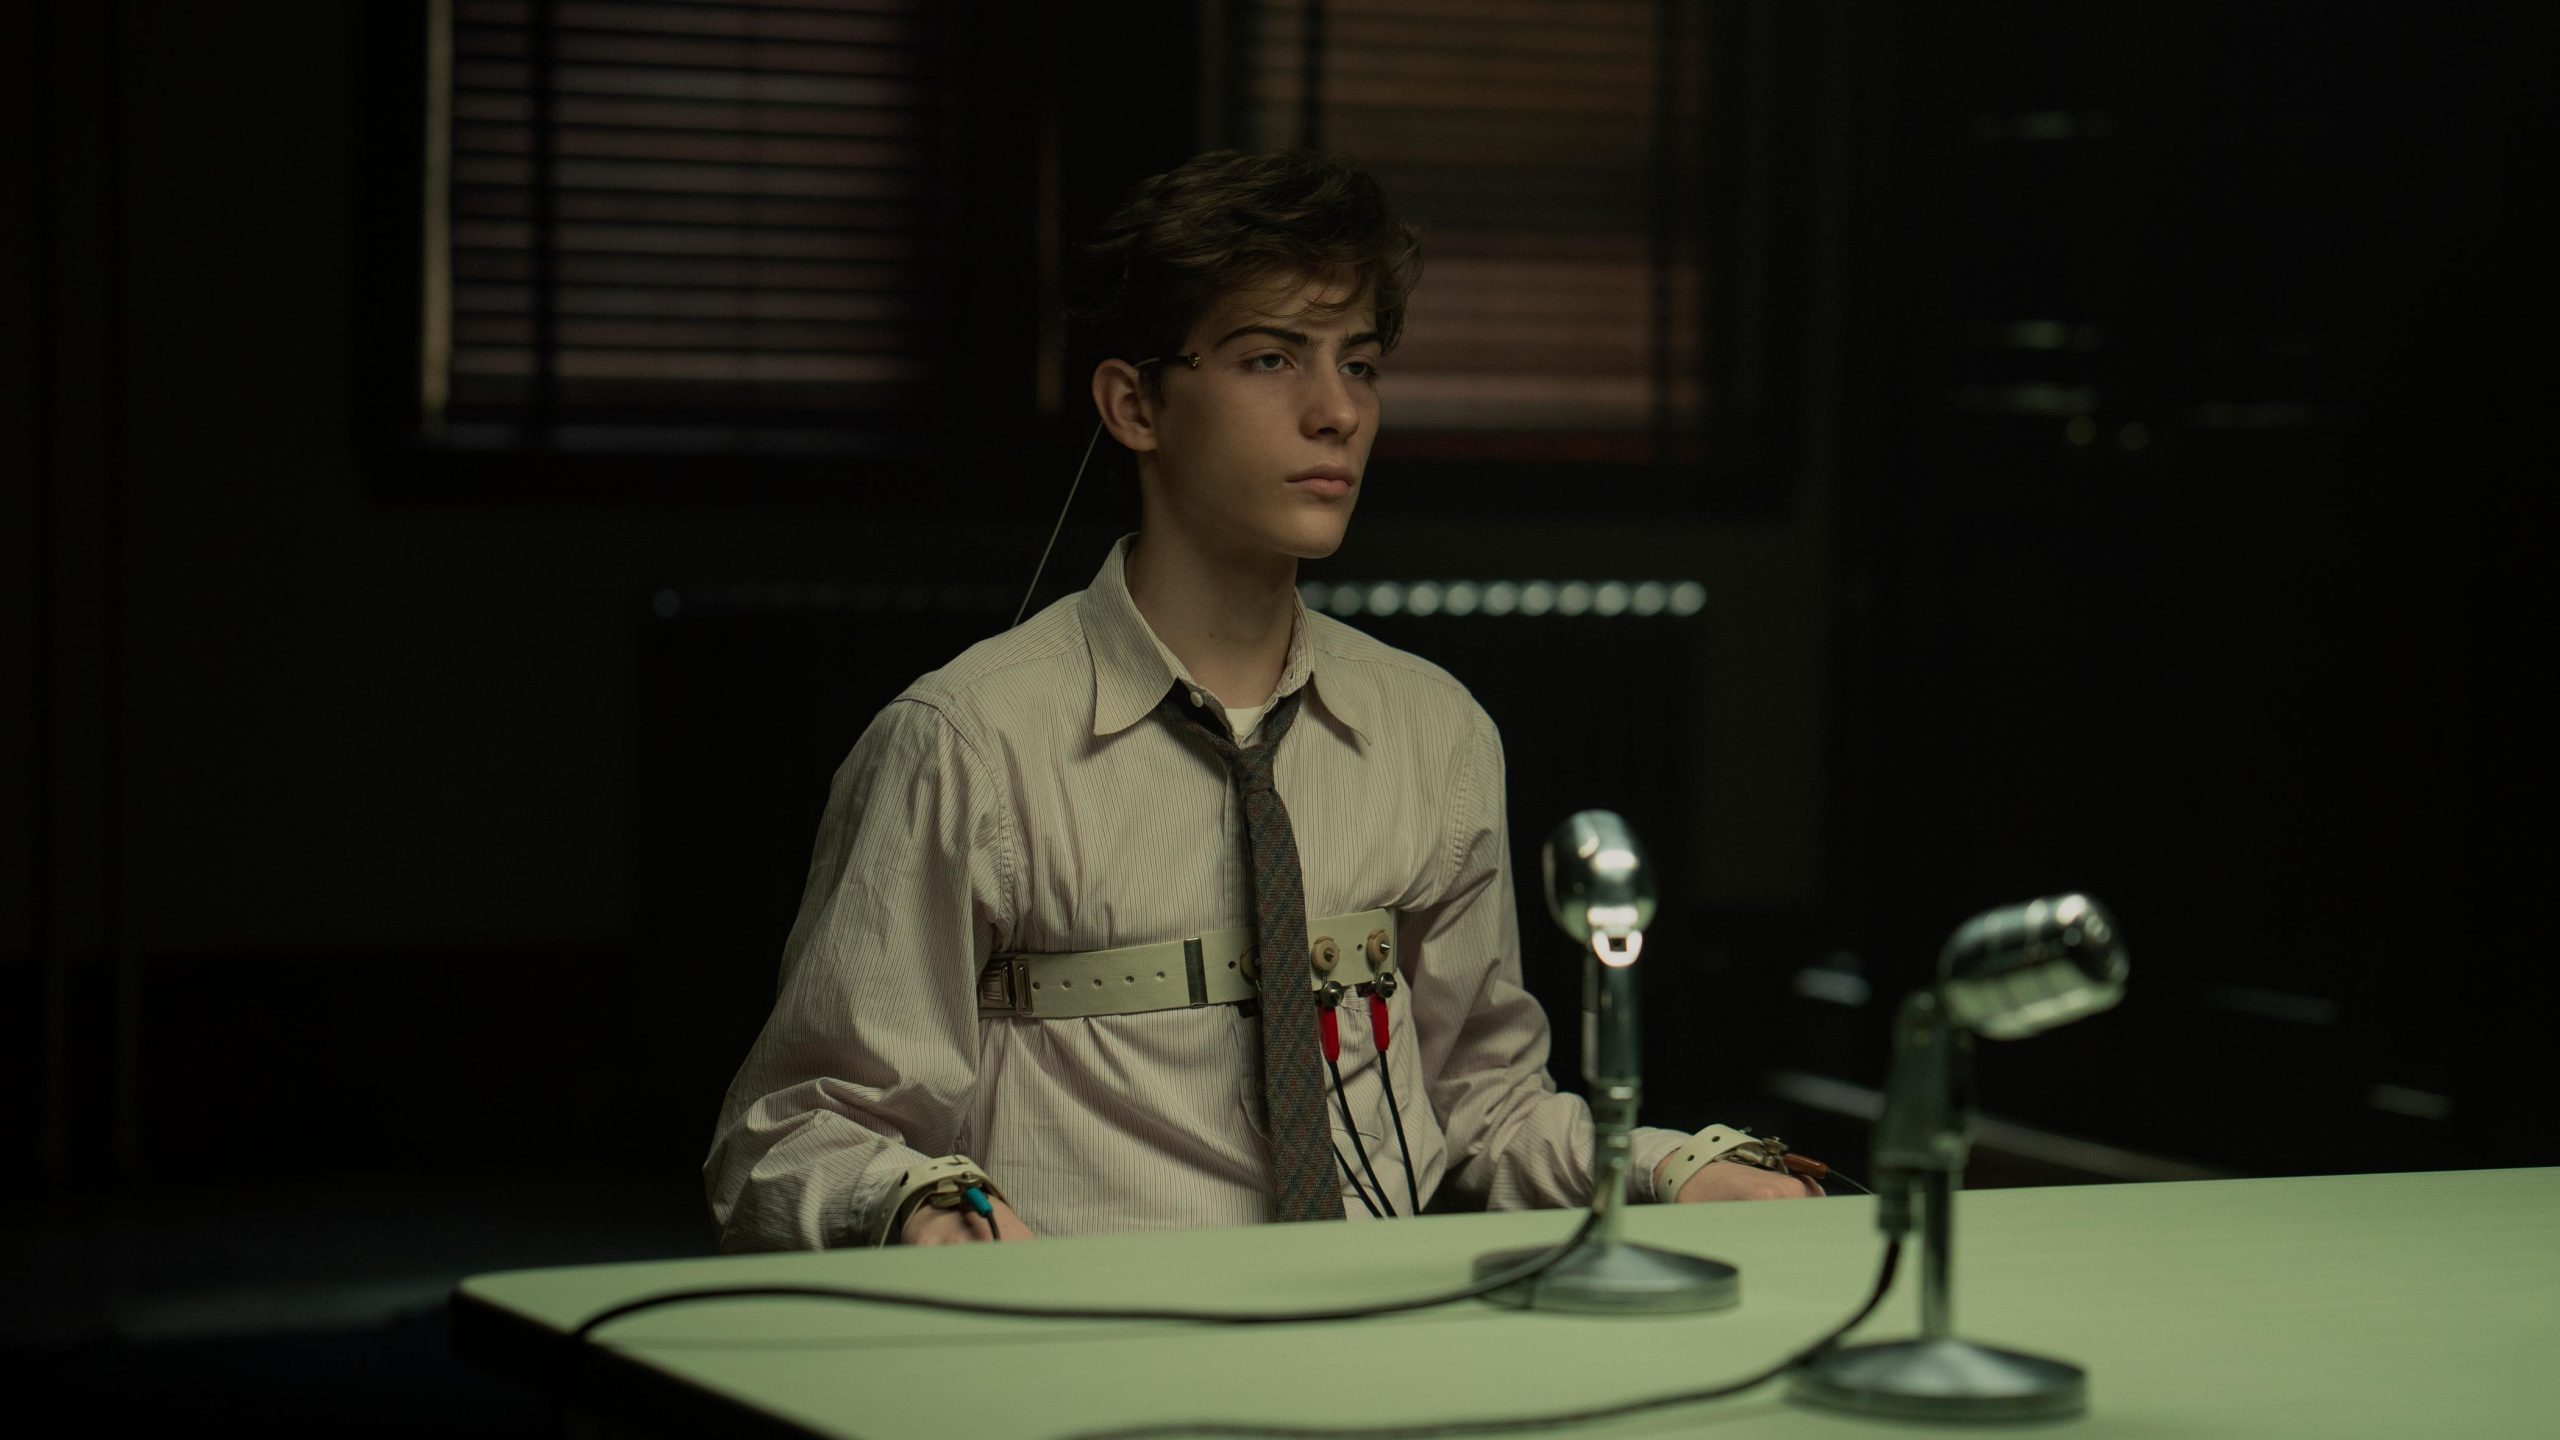
The psychological experiment scenes presented a different challenge. Tremblay was strapped to a chair, limiting his movement and expressions. “I learned to utilize that unfamiliar and uncomfortable environment to my advantage,” Tremblay says. “Because Ted himself in that moment is also experiencing that discomfort and unfamiliarity at the same time.”
How accurate is the Netflix movie?
Unabomber is grounded in documented events from Kaczynski’s life, but the film also takes creative liberties with gaps in the historical record.
“But that was fun for the filmmakers and us actors as we got to create something unique from the story we pieced together and that excited me because it distinguishes our film from other tellings of the Unabomber’s story,” Tremblay says.
For Metz, the film was also an opportunity to explore parts of Kaczynski’s story that are less familiar to audiences.
“In developing the film, we found that the psychological experiments conducted on Ted Kaczynski during his time at Harvard were unknown to most people, some were not even aware he attended Harvard,” Metz says. “While our film doesn’t offer a complete biography, we chose to present a filmic take on his story and a narrative opening into the mind of Ted Kaczynski.”
OG.com Markets has submitted a filing to the U.S. Commodity Futures Trading Commission (CFTC) seeking approval to launch cash-settled perpetual futures linked to individual stocks—an effort to bring a product format widely used in crypto derivatives into traditional equity markets.
According to the CFTC filing released Thursday, the proposed rules would cover single-stock futures that do not expire (“perpetuals”), trade around the clock, and are designed to offer continuous exposure without requiring traders to roll positions into new contract months.
Key takeaways
- OG.com Markets is pursuing CFTC approval for perpetual futures tied to specific U.S. equities.
- The product is described as cash-settled and perpetual, with continuous trading for five days a week.
- Regulatory momentum comes as other major crypto trading and prediction-market players also seek permission to offer similar stock-linked perps.
- The CFTC has been building a framework for perpetual contracts through approvals and temporary relief tied to specific arrangements.
OG.com’s CFTC filing outlines stock-linked “perps”
In a Thursday filing with the CFTC, OG.com Markets outlined a proposed rule set intended to enable the listing of cash-settled single-stock futures that never expire. The proposal also calls for trading to operate 24 hours a day, five days a week.
Perpetual futures differ from traditional futures by removing the need for contract expiration. For traders, that structure can reduce the operational friction of rolling between dated contracts, while for markets it can support more continuous liquidity and positioning.
The concept is not new in crypto. Perpetual contracts were pioneered in digital-asset derivatives, with BitMEX introducing an early version of the model in 2016—helping make “perps” one of the most actively traded derivatives formats in the sector.
How OG.com ties into the wider prediction-markets and derivatives shift
OG.com Markets recently emerged as an independent prediction markets and derivatives platform after being spun out from crypto exchange Crypto.com. At the time of the separation, OG.com was described as being valued at $5 billion, and CEO Kris Marszalek said the company planned to expand beyond prediction markets into futures and perpetual contracts.
Shortly after the spin-off, Robinhood acquired an equity stake in OG.com as part of a multi-year agreement. The deal includes the use of OG.com’s CFTC-regulated derivatives exchange and clearinghouse for prediction markets. That backdrop matters because it places OG.com’s U.S. equity-derivatives ambitions directly within a set of business relationships already aligned with regulated derivatives infrastructure.
Importantly, while OG.com is now aiming at stock-linked perpetual futures, its current positioning originates in prediction markets—where the mechanics of cash settlement and continuous trading can be attractive to participants who want to express views over time without physical delivery.
Not alone: Coinbase, Kraken’s parent, and Kalshi have also filed
OG.com’s move fits into a growing cluster of filings from platforms attempting to introduce perpetual futures tied to individual U.S. stocks. Earlier coverage noted that Coinbase, Kraken parent Payward through its Bitnomial exchange, and prediction market platform Kalshi all filed to offer similar stock-linked perpetual futures.
The timing also reflects a regulatory environment that has been more permissive toward certain crypto-adjacent activities than some market participants expected. The shift gained attention after U.S. Senate action failed to advance the proposed CLARITY Act on Sept. 15—yet regulators continued moving forward on crypto initiatives through other channels.
In particular, after the Senate vote, the SEC cleared limited onchain trading of tokenized U.S. stocks under its Innovation Exemption, and the CFTC expanded regulatory relief for software providers that connect users to regulated derivatives platforms, including those offering perpetual contracts.
The CFTC’s groundwork for perpetual contracts
The CFTC’s approach to perpetual futures has not been confined to one company or one application. The agency previously began laying out a path for perpetual contracts through a combination of case-by-case review and targeted relief.
In May, the CFTC established a case-by-case review process for perpetual contracts and approved Kalshi’s Bitcoin perpetual futures product. It then followed in June with temporary relief allowing certain registered exchanges to convert existing crypto futures into contracts without expiration dates.
That incremental regulatory scaffolding helps explain why the market is converging on perpetual structures now. Even without a single comprehensive rule that automatically covers every new product variation, firms can structure applications around how the CFTC has already evaluated perpetual contracts—making the approval process feel more navigable than it might have been in earlier years.
For investors and traders, the key question is how quickly the CFTC can translate precedent from crypto perpetuals and targeted relief into approvals for cash-settled, stock-linked perps. Watch for updates on the OG.com rulemaking process and whether regulators request changes to trading mechanics, settlement terms, or operational guardrails as these filings move through review.
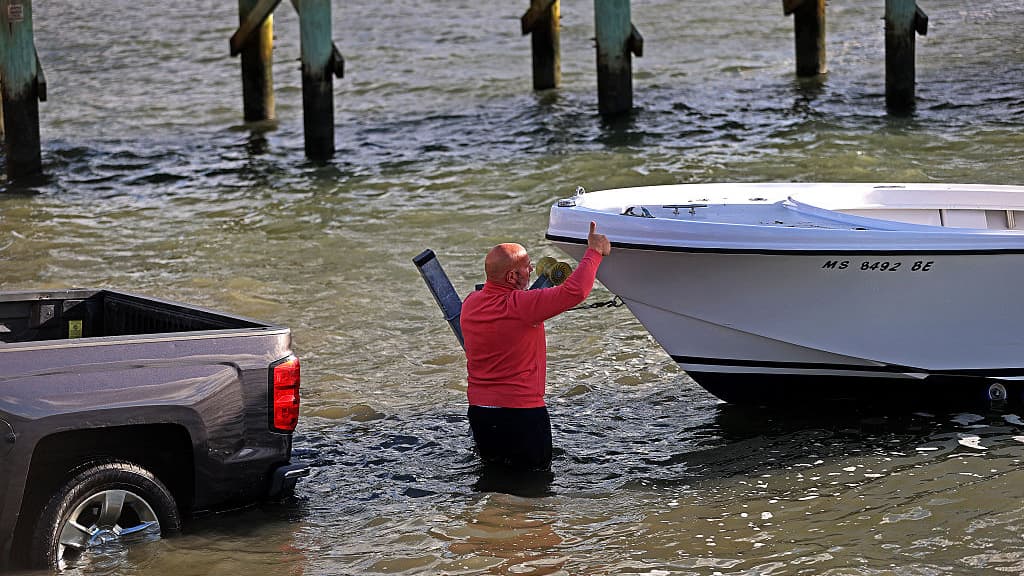
“Not every storm is becoming more intense, but the intense storms are becoming more intense—whether that be a thunderstorm, a hurricane, one of these nor’easters,” Barlow says.
One thing that doesn’t seem to be changing is the number of storms, Barlow adds. “We’re not seeing any changes in the overall average, and the total number of storms might actually be going down a little bit,” he notes.
In an ever warming world, storms are only going to continue to intensify. Climate change is increasing the number of “billion dollar disasters,” disasters that top at least $1 billion in damage, that take place in the U.S. each year. The average length of time between billion-dollar disasters has fallen—from 82 days during the 1980s to 16 days during the last 10 years. In 2025, the U.S. experienced a billion-dollar weather or climate disaster once every 10 days.
“Until we stop increasing the amount of greenhouse gasses in the atmosphere, the intensity of rainfall, the intensity of these storms, will continue to increase as well,” says Barlow. “Until we stop making things worse, things are going to keep getting worse.”
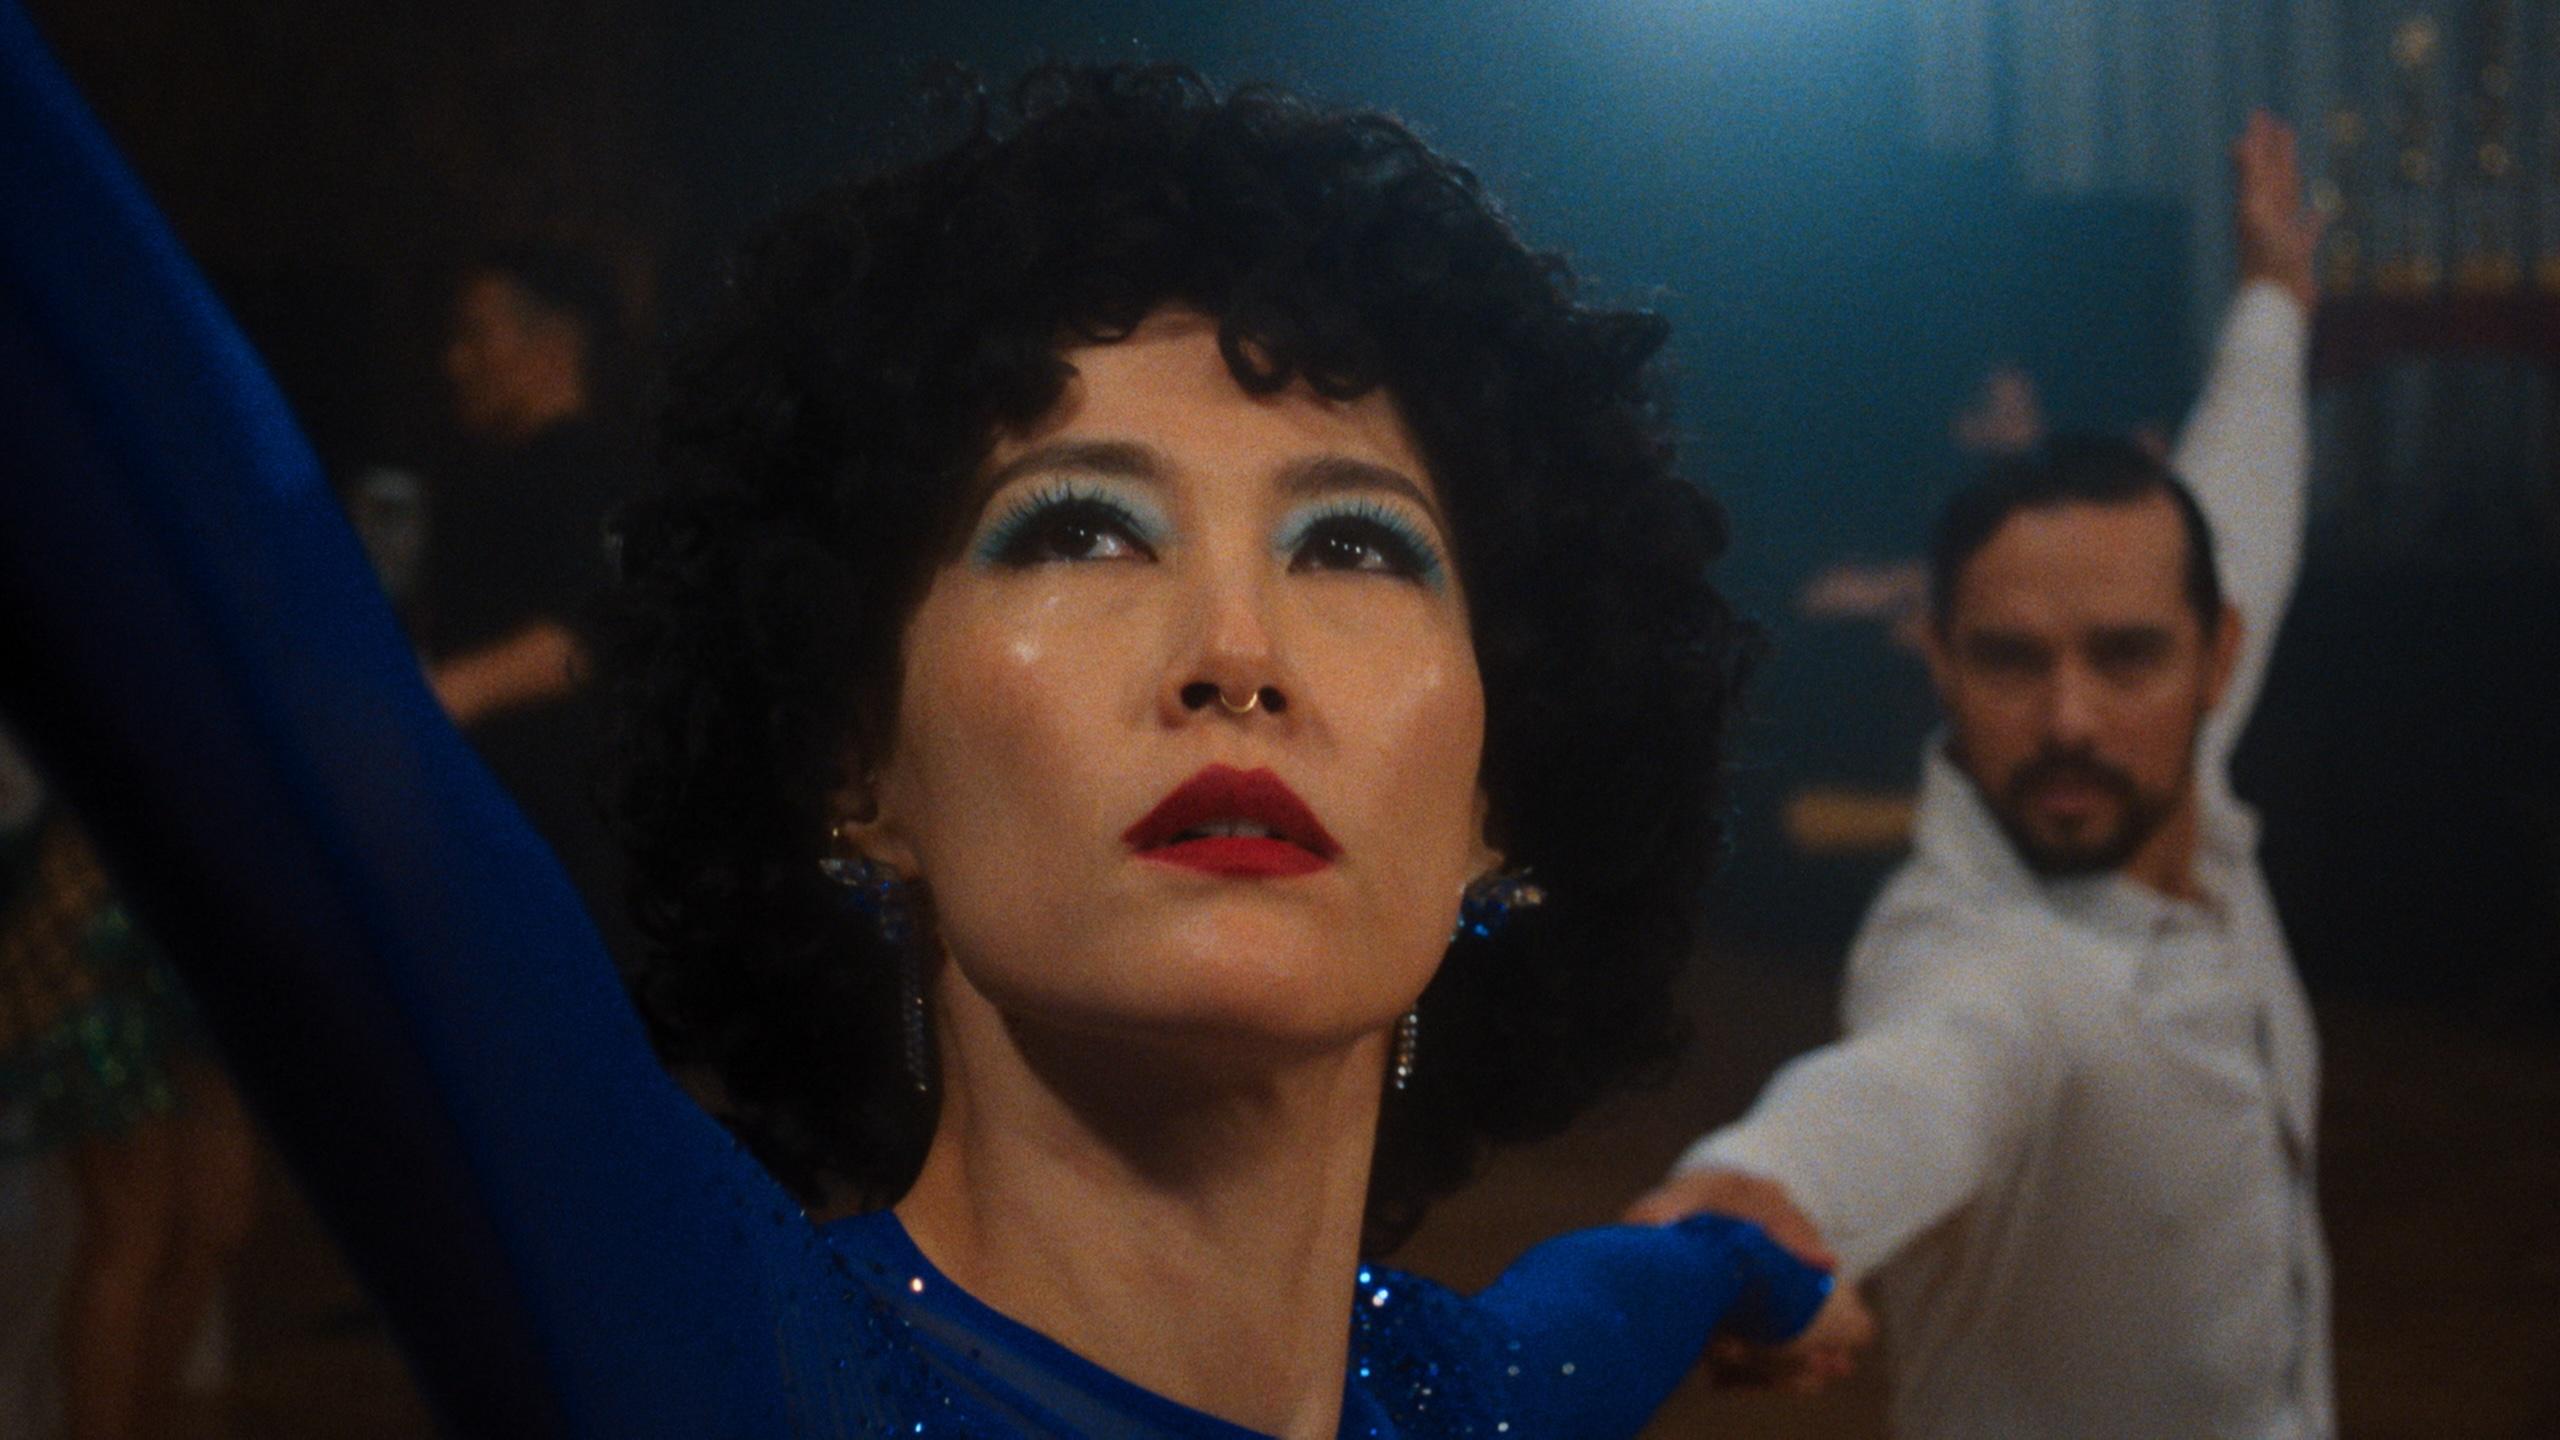
When Haru meets Fedir—whose wife is a Paris-based dance champion, though the marriage is an open one—she glimpses fresh possibilities, or at least just an adventure. In an early scene, after she and Fedir have had a pleasant, platonic dinner together, they’re ready to part ways in the street. A crew of drunken businessmen jostle Haru, and Fedir stands up for her. What follows is a cleverly choreographed dream ballet—though the genre is actually the bachata, one of the dance forms Fedir teaches, its movements an expression of longing and heartache—in which Fedir defends Haru’s honor against this gang of boorish men. Other passersby join in, and the scene becomes a metaphor for the act of rejoining life. By the end of the evening, Haru and Fedir have tumbled into bed.
Their two hookups are enjoyable and tender—until the wife shows up, and Haru realizes she has feelings she can’t control. Kikuchi shifts gears smoothly: One minute, she shows how Haru is nearly deadened by sorrow. The next, her exhilaration becomes a kind of artificial sunshine. But a flash of anger and jealousy causes her to act out, in a scene that makes you recoil a bit even as you laugh. Kikuchi is perhaps best known for her roles in movies like Babel and Pacific Rim, as well as HBO’s Tokyo Vice, several episodes of which Wladyka directed. Here, she captures the spirit of a woman who longs to get back to being herself, if only she could remember who that self was. Haru is both breezy and cautious, and totally lost. By the movie’s end, she has found her way forward, because she realizes there’s no going back. She’ll have to be a new person, encompassing the experiences and memories of the old one. Kikuchi captures that difficult butterfly transition as it unfolds; it’s both painful and funny to watch. But in the end, she shows us how Haru finds her way back to the music, which is the only way she can move into the future, one note, and one dance step, at a time.
Summer Mersinger is leaving the helm of the Blockchain Association, one of the crypto industry’s leading advocacy groups, a week after the sector weathered a major legislative setback in the loss of the Digital Asset Market Clarity Act.
Mersinger will be replaced — for now — by Kristin Smith, the organization’s original CEO who ran the association from its launch in 2018 until 15 months ago, according to a Friday statement. The handover is set for October 16, closing a tumultuous era that saw major crypto wins in Washington and a significant defeat last week, when the U.S. Senate failed to advance the Clarity Act in a wide loss in which all the Senate’s Democrats and some Republicans declined to support it.
“I’m proud of how far we’ve come together, from the GENIUS Act to real regulatory clarity at the SEC and CFTC,” said Mersinger, who’d taken the job after leaving her post as a member of the Commodity Futures Trading Commission, in a statement. “Kristin built this association from the ground up, and BA is in good hands. I’ll be cheering them on.”

VITURE Pro 2 Packs a 146-Inch Screen Into 63 Gram XR / AR Glasses for $299
Another appeals court rules against prediction market provider Kalshi, says sports contracts are subject to state regulations
Wales breaking news plus weather and traffic updates (Friday, September 25)





-

 Crypto World3 days ago
Goldman Sachs and Deutsche Bank Agree: The S&P 500 Rally Isn't Over
-

 Tech5 days ago
Researchers escape OpenAI Codex sandbox to run commands on host
-

 Fashion2 days ago
8 iPhone Accessories That Add Personality
-

 Crypto World5 days ago
Who Needs CLARITY Anyway? ARB Could See 70X Increase: Hodler’s Digest
-

 Crypto World7 days ago
Circle launches Arc Studio AI agent for building onchain apps
-

 Tech6 days ago
Trump suggests rebranding AI with a new name, says he’s also creating an AI Force
-

 Business5 days ago
Analog Devices (ADI) Bets $1.35 Billion on Chips that Let Machines Think for Themselves
-

 Crypto World5 days ago
Coinbase, Robinhood, Circle Seen as Tokenized-Stock Winners
-

 Crypto World3 days ago
This Bearish Netflix Stock Trade Can Cash In On Video Streaming Giant’s Woes
-

 Crypto World7 days ago
Bitcoin price breaks channel as RSI climbs to 63
-

 Crypto World3 days ago
Trump-Xi Polymarket Odds for Handshake Hit 50%
-

 Tech4 days ago
Google’s $899 Googlebook is a bet that you’ll buy a new laptop for Gemini
-

 Entertainment3 days ago
These 17 Fall Amazon Dresses Seriously Look Like Anthropologie
-

 Crypto World2 days ago
Crude Oil Prices Pressured by Diplomatic Hopes in the Middle East
-
 Business3 days ago
Oil Price Today (September 23): Crude oil below $100 on hopes of US-Iran talks. What did Trump say?
-
 Crypto World2 days ago
Bitcoin price tests $83,600 Supertrend support after $87K rejection
-

 Crypto World7 days ago
World Money launches in 150+ countries with Stripe
-
 NewsBeat7 days ago
Ed Sheeran protegees Katseye UNFOLLOW star… days after Macklemore was dropped from his tour over Free Palestine remarks
-

 Crypto World2 days ago
Bitcoin Threatens Sub-$84,000 Breakdown as Long Liquidations Spike
-

 Crypto World4 days ago
Meta Jumps 11% As Muse Shines and Investors Show an Appetite for Advancing AI
You must be logged in to post a comment Login