Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Tech & AI
ChatGPT is taking ads into image generation, and your conversations could decide what you see

I’ve never loved ads turning up where I go to think, so this one makes me wince.
OpenAI is testing visual ads in ChatGPT image generation. The software will decide whether you should actually see one.
How doChatGPT’ss new Image ads work?
OpenAI says the ads show products in use or the experiences they unlock, carry clear labels, and sit apart from the imageyou’ree creating.
The more interesting part is thatOpenAI’s guardrails determine whether a chat is emotionally vulnerable or sensitive before placing ads. In technical terms, automated guardrails analyze the chat context before triggering a personalized ad. In simpler terms, OpenAI wants to be safe.
DoubleVerify and Integral Ad Science (third-party firms) will check how brand safety rules get applied, in a controlled setup without real conversations. I’d say an outside check matters, since I’d want any system that seems fragile to be audited first before it starts showing me targeted advertisements.
The business logic is quite simple as well. Ads let OpenAI monetize beyond subscribers among 1.2 billion weekly users.
Why isEurope’ss rulebook part of this story?
Ads have run across 31 European countries since late August, but only for free and Go users, while Plus, Pro, and Enterprise subscribers see none. That same week, the European Commission labeled ChatGPT a very large online search engine (focus on the term) because its 159.1 million monthly EU users dwarf the 45 million threshold.
The consequence: by January, OpenAI must publish a year of ads, with advertisers, run dates, targeting, and reach. That matters because Europe’s rulebook forces OpenAI to leave a paper trail for its growing ad business. At least in the EU, ChatGPT must disclose who paid, when the ads ran, whom they targeted, and how many people they reached.
This will give users and regulators a clearer view of howChatGPT’ss advertising business operates. ChatGPT already shows text-based ads, and visual ads take that further.
RELATED COVERAGE:
Continue Reading
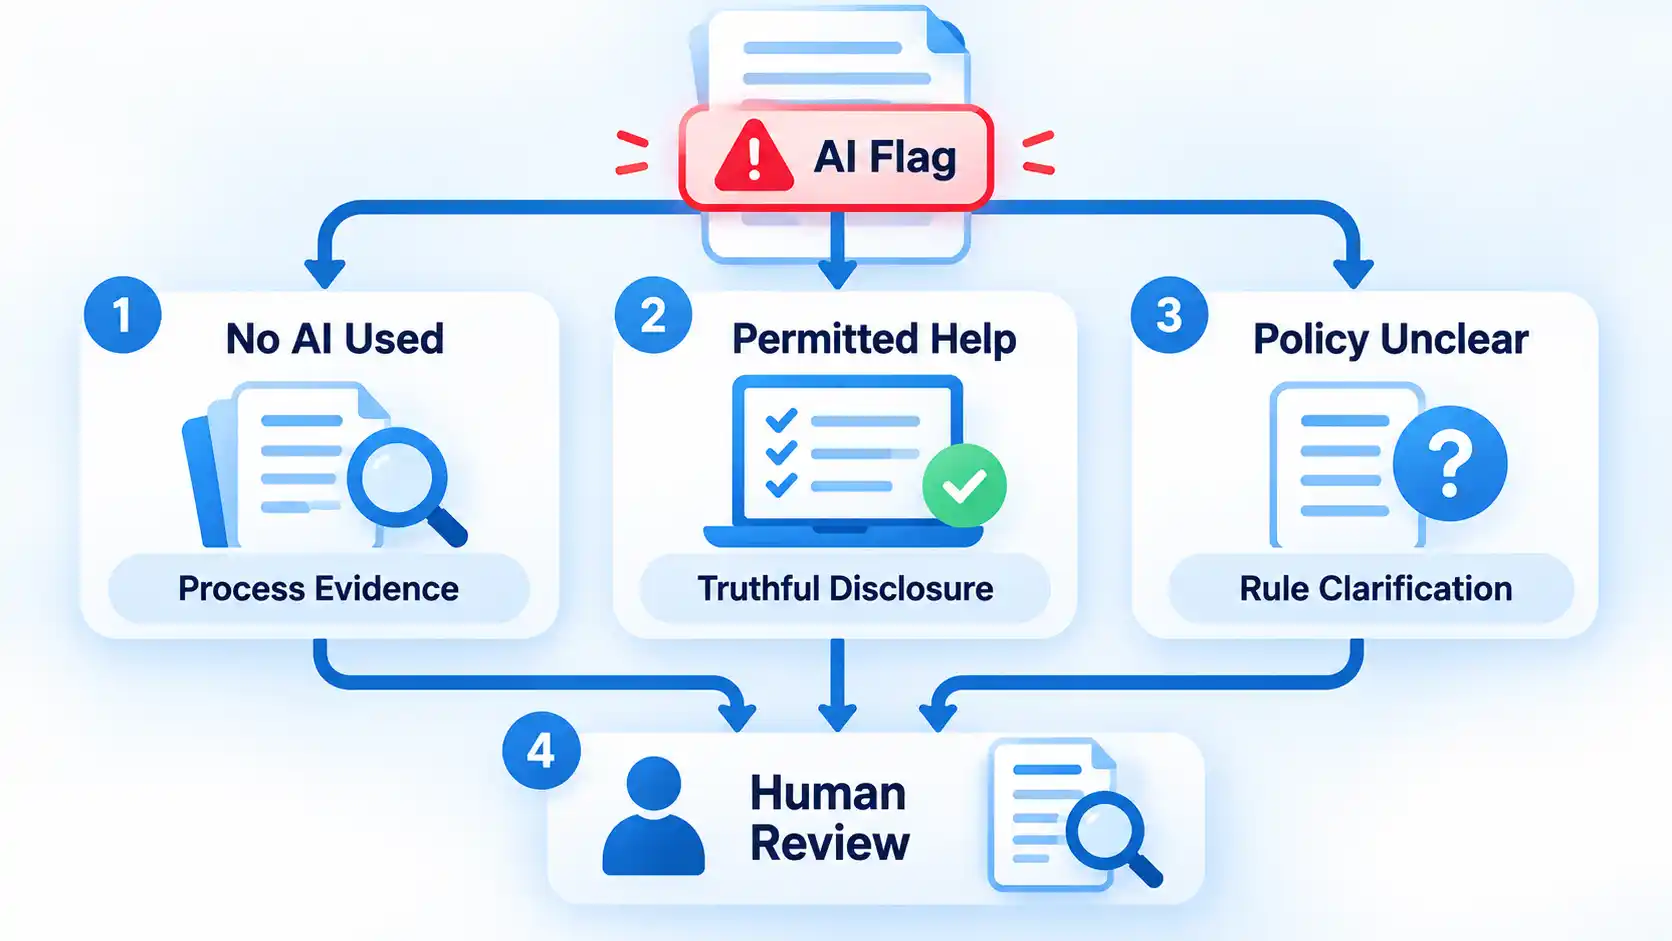
If human-written content is flagged as AI, do not immediately rewrite it to chase a lower score. Preserve the exact document and detector result, collect genuine records of how the work was created, check the rule that applies, and ask for a human review based on the full evidence.
An AI detector can be useful as a signal, but a result by itself does not record who actually wrote a document. The safest response is therefore evidence-first rather than score-first.
What an AI Flag Actually Means
An AI detector looks at patterns in text and estimates whether those patterns resemble generated writing. A false positive happens when human-written text is classified as AI-generated.
Do not assume that a percentage means the same thing across different detectors. For example, Turnitin says its current AI Writing Report does not show a numerical percentage for results from 1% to 19% because that range has a higher incidence of false positives. Instead, those results are shown as *%. For displayed results of 20% or more, its percentage refers to qualifying text that the system identifies as likely AI-generated or likely AI-generated and then modified with an AI paraphrasing tool.
That matters because a detector percentage should not automatically be read as “the percentage of this document that a machine wrote.” The meaning depends on the particular detector and how it defines its result, so even a high score still needs context.
When deciding whether content was written by AI, a detector result is only one signal. Draft history, source records, factual accuracy, the writing process, and other evidence can provide information the detector cannot see.
AI detector accuracy depends on the specific tool, text, language, and testing conditions rather than one universal accuracy figure.
Before You Respond: Preserve the Original Record
Before changing the disputed document, preserve what actually existed when it was flagged. If you rewrite the only copy first, you may make it harder for a reviewer to compare the detector result with your drafts and editing history.
Prerequisites
- Keep the exact version of the document that was submitted or scanned.
- Save or screenshot the detector report, including the visible score, highlighted passages, detector name, and date when available.
- Preserve existing drafts, outlines, notes, source records, comments, and relevant correspondence.
- If you need to edit the document later, work from a copy rather than overwriting the only preserved version.
If you cannot see the detector report yourself, ask the reviewer which text was flagged and what result they received. Knowing what was actually assessed is more useful than arguing against a percentage you have not seen.
How to Build an Authorship Evidence Pack
Version history is useful, but it is only one part of the record. A stronger response combines several genuine pieces of evidence that show how the document developed.
Check Google Docs version history
On a computer, open the Google document and click Last edit, the Version history control near the top right. Choose an earlier version in the panel to inspect changes and, where available, who updated the file.
Google notes that you need edit permission to browse earlier versions. It also warns that revisions may occasionally be merged, so an incomplete revision trail does not necessarily mean earlier editing never occurred.
If an earlier state is important, you can make a copy of that version instead of replacing the current document. This lets you keep both states available for comparison.
Check Word or Microsoft 365 version history
For a Word file stored in OneDrive or SharePoint in Microsoft 365, open the file, select the file title, and choose Version history. You can then select an earlier version and open it separately for comparison.
Microsoft makes an important limitation explicit: Microsoft 365 Version History works for files stored in OneDrive or SharePoint. A document that existed only as a local file should not be expected to have the same Microsoft 365 cloud revision trail.
The distinction between Google Docs and Word version history matters when you are trying to reconstruct how a file changed over time.
Add drafts, notes, sources and prior work
Do not stop at revision history. Earlier drafts, outlines, research notes, saved source material, comments from collaborators, emails about the work, and earlier writing on similar subjects may all help a reviewer understand the process behind the final document.
In academic disputes, for example, Cornell recommends looking beyond initial suspicions and considering tangible evidence. Relevant evidence can include outlines, drafts, prior discussions, previous submitted work, and whether the student can explain the submission. The exact standard will differ outside education, but the broader point is useful: several consistent pieces of evidence are more informative than a detector score alone.
No single item below should automatically be treated as conclusive proof.
| Evidence | What it can show | Important limitation |
|---|---|---|
| Detector report | What one detector classified and which passages it highlighted. | It does not directly establish who authored the text. |
| Version history | How a document changed across saved versions and, where available, who edited it. | History may be incomplete, merged, unavailable, or dependent on where the file was stored. |
| Earlier drafts | How wording, structure, examples, and arguments developed. | A draft alone does not prove who created every part of it. |
| Notes and outlines | The planning and reasoning that preceded the finished document. | Many writers do not keep complete planning records. |
| Sources and citation notes | How research material connects to the finished work. | They support the research trail, not authorship by themselves. |
| Prior comparable writing | Whether the document is consistent with the writer’s established knowledge or style. | People naturally change style across topics, audiences, editors, and assignments. |
| Process explanation | Whether the writer can explain source choices, revisions, examples, and conclusions. | It should be assessed with the rest of the evidence rather than treated as a standalone test. |
Your response should separate two questions: what did the detector report, and what does the available evidence say about how the document was produced? Work through the issue in order instead of rewriting the document simply to change a score.
How to Respond to the Flag
If you did not use generative AI
Keep the response simple and evidence-based. State that the disputed writing was produced by you, explain the basic process you followed, and provide the records that best support that account.
You do not need to prove that every sentence looks unlike machine-generated prose. The goal is to give the reviewer better evidence than a style-based classification alone.
If you used permitted editing, translation or AI assistance
“Human-written” does not always mean “produced without any software assistance.” A person may write the original material and later use spelling, grammar, translation, rewriting, or generative features.
The important question is whether the actual assistance complied with the rule governing the work. If the policy permitted a tool or required disclosure, state what you used and provide the required disclosure. Do not turn a legitimate detector dispute into an inaccurate claim that no automated assistance was involved.
If the policy is unclear
Ask which rule is being applied and which kind of assistance the reviewer believes violated it. A detector result and a policy violation are separate questions.
This is particularly important in education because rules can vary by instructor and assignment. Cornell’s current guidance says generative-AI rules may be set on an assignment-by-assignment basis and advises students to ask when the policy or tool classification is unclear. Other organizations may define acceptable assistance differently.
The procedure has reached a useful stop point when the responsible reviewer has the exact disputed material, the applicable rule, your truthful description of any assistance, and the relevant process evidence. A particular detector percentage is not the stop condition.
What to Do If You Have No Version History
No version history does not automatically mean you have no evidence. A document may have been written offline, imported from another application, saved as separate local files, copied between systems, or created somewhere that does not preserve a detailed revision trail.
When revision history is missing, other ways to show how a document was written can include:
- earlier local copies of the file;
- handwritten or digital outlines;
- research notes and saved source material;
- citation-manager records;
- emails or messages discussing the work;
- comments from editors, teachers, colleagues, or collaborators;
- earlier writing on the same subject; and
- your ability to explain why particular sources, examples, arguments, or revisions were used.
Even detector vendors acknowledge this limitation. Originality.ai’s current review guidance says that absence of document history is not proof of AI use and recommends using other evidence when history is unavailable.
File dates and metadata can add context, but they should not be presented as unquestionable proof. Files can be copied, exported, restored, or moved between devices and services. Use metadata as one supporting clue alongside stronger process records.
What Not to Do After a Flag
A disputed detector result can make it tempting to keep changing the text until a different tool gives the answer you want. That approach solves the wrong problem.
- Do not fabricate drafts, notes, timestamps, or screenshots. False evidence creates a separate credibility problem and can be more damaging than the original detector dispute.
- Do not delete the disputed version. Keep the material that was actually assessed before creating revised copies.
- Do not treat a second detector as automatic proof. Different systems can produce different results, so disagreement adds uncertainty rather than establishing authorship.
- Do not repeatedly rewrite legitimate prose solely to lower a score. Rewriting changes the evidence and may also make the prose less natural.
- Do not hide assistance that was actually used. If editing, translation, paraphrasing, or generative tools were involved, describe them accurately and compare that use with the applicable rule.
- Do not assume a detector percentage is a plagiarism percentage. AI detection and source-matching or plagiarism systems answer different questions.
- Do not upload confidential work everywhere just to collect more scores. Before sending sensitive academic, client, employer, or unpublished material to another service, check whether you are authorized to share it and how that service handles submitted content.
A controlled rescan can help investigate an inconsistent result, but it should compare like with like. When possible, use the same text, detection model, language settings, and citation treatment. A different result under different conditions does not automatically invalidate the first scan.
How to Protect Future Work
The simplest protection is to keep ordinary records while you work instead of trying to reconstruct them only after a dispute. You do not need an elaborate surveillance system. A normal revision trail, retained drafts, research notes, and accurate disclosure records are usually more useful.
For important work, consider drafting in a system that preserves revision history, keeping meaningful intermediate copies, and retaining the notes and sources that shaped the document. Google Docs also lets you name important versions, which can make major milestones easier to find and helps prevent those named versions from being merged.
If a school, employer, client, or publisher permits some use of AI, translation, grammar, or rewriting tools but requires disclosure, keep a simple record of what was used and for what purpose. That is easier than trying to remember the exact workflow months later.
Verify the result
- Important documents are being created or stored somewhere that retains useful revision history when feasible.
- Meaningful drafts, outlines, and research notes are not all discarded when the final copy is completed.
- Source and citation records are kept with high-stakes research or publishing work.
- Any AI, translation, rewriting, or editing assistance that must be disclosed is recorded accurately.
- You could explain how the document developed without depending on an AI detector to validate your authorship.
The aim is not to make human writing “pass” every detector. It is to keep enough genuine context that an important authorship question can be reviewed using more than one automated score.

South Korea’s Financial Services Commission (FSC) held an emergency meeting following a series of cyberattacks targeting financial institutions in the country.
During the meeting, officials confirmed a data breach at Shinhan Bank and said other cybersecurity incidents affected other South Korean banks, including Kookmin Bank.
Shinhan Bank and KB Kookmin Bank are large private South Korean commercial banks, each holding more than $400 billion in assets.
Authorities said they launched on-site investigations after receiving incident reports and shared all actionable information with relevant agencies, including KISA (Korea’s data protection agency).
Financial companies in the country are now instructed to:
- Inspect all externally accessible IT systems and services, including those that are not customer-facing.
- Reduce unnecessary information exposure and check for missing or inadequate authentication and access controls.
- Quickly share threat information and coordinate their responses.
- Submit their internal security inspection results as soon as possible.
Authorities also pledged to oversee consumer protection and compensation, and analyze the incidents to identify necessary regulatory improvements.
Yesterday, local media outlets reported that South Korea’s President Lee ordered a thorough investigation into personal data leaks at financial and public institutions.
At the same time, Hana Bank was also found to have suffered a limited-scope breach after its sales-support system was compromised.
According to the same reports, Shinhan Bank leaked the details of 25,000 customers, while Kookmin Bank leaked credit card information of 119,000 clients.
AI-powered attacks suspected
While official channels provided no details about the perpetrators, Korean news agency Yonhap reported that a server used in the attacks had an HTML page title containing a Chinese-language string associated with ARTEX AI.
ARTEX AI is an open-source penetration-testing system that uses agents to automate information gathering, vulnerability discovery, attack-path planning, security-tool execution, and vulnerability verification.
The bank and financial authorities have not confirmed its use in the Shinhan breach, and the Chinese-language string doesn’t link the attacks to any particular threat actor.
However, Moon Jong-hyun, the head of the Genian Security Center, posted on LinkedIn that several threat analysts believe that the breaches involved AI-based attack automation tools.

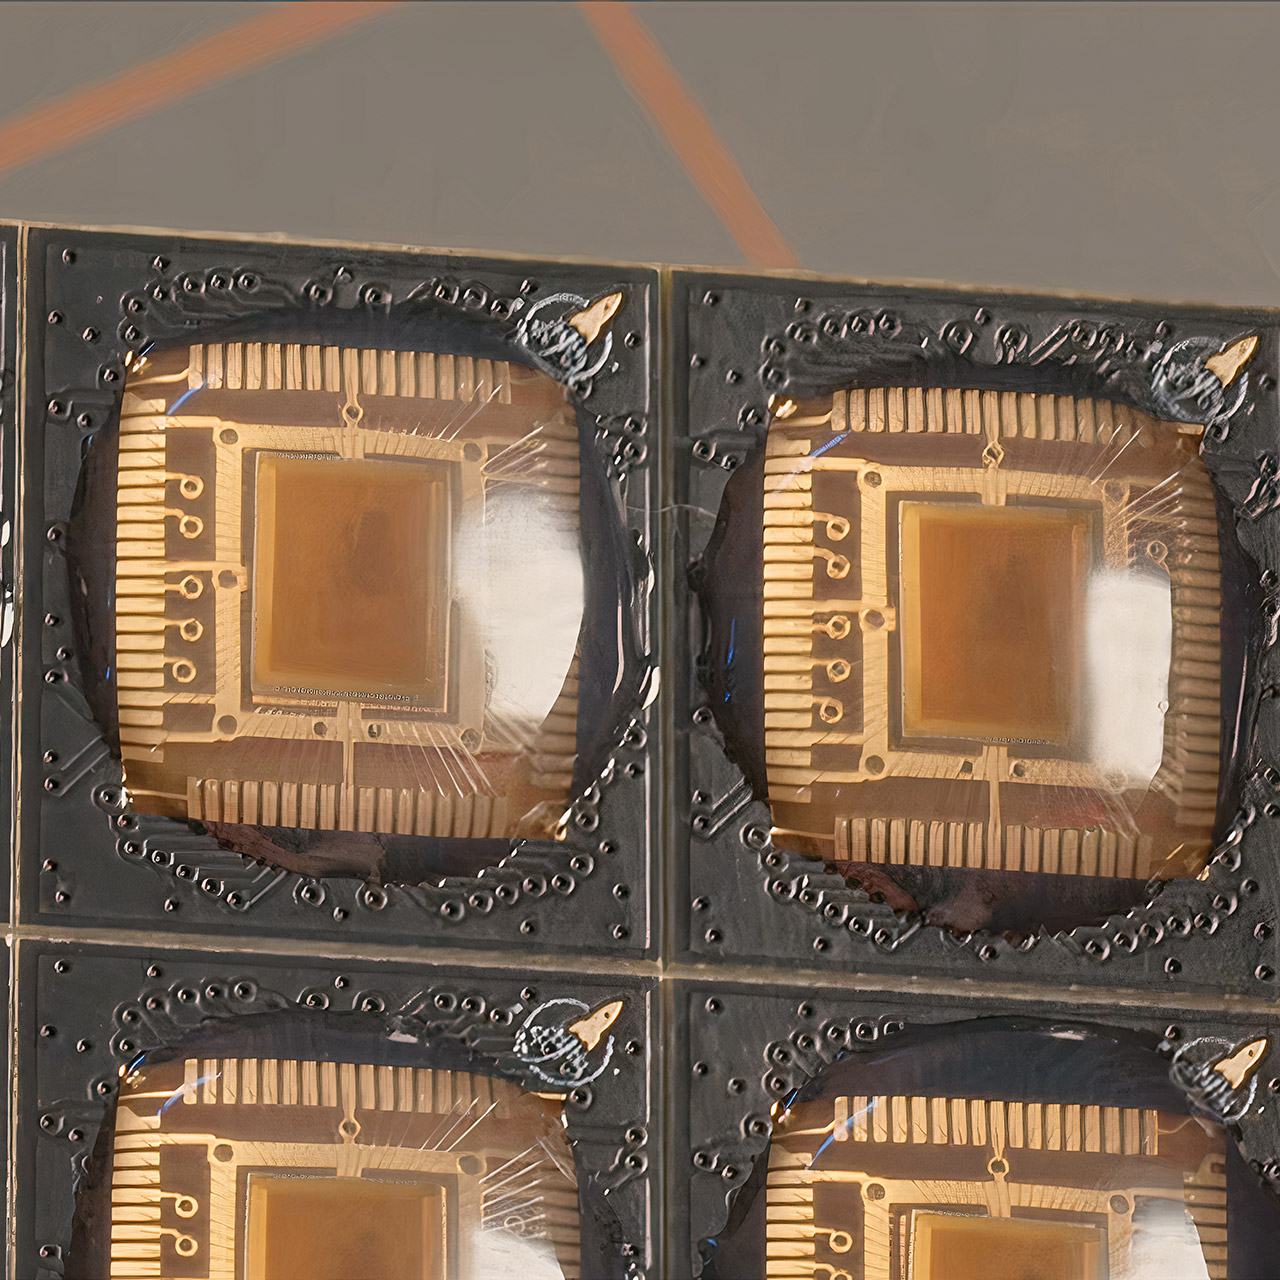
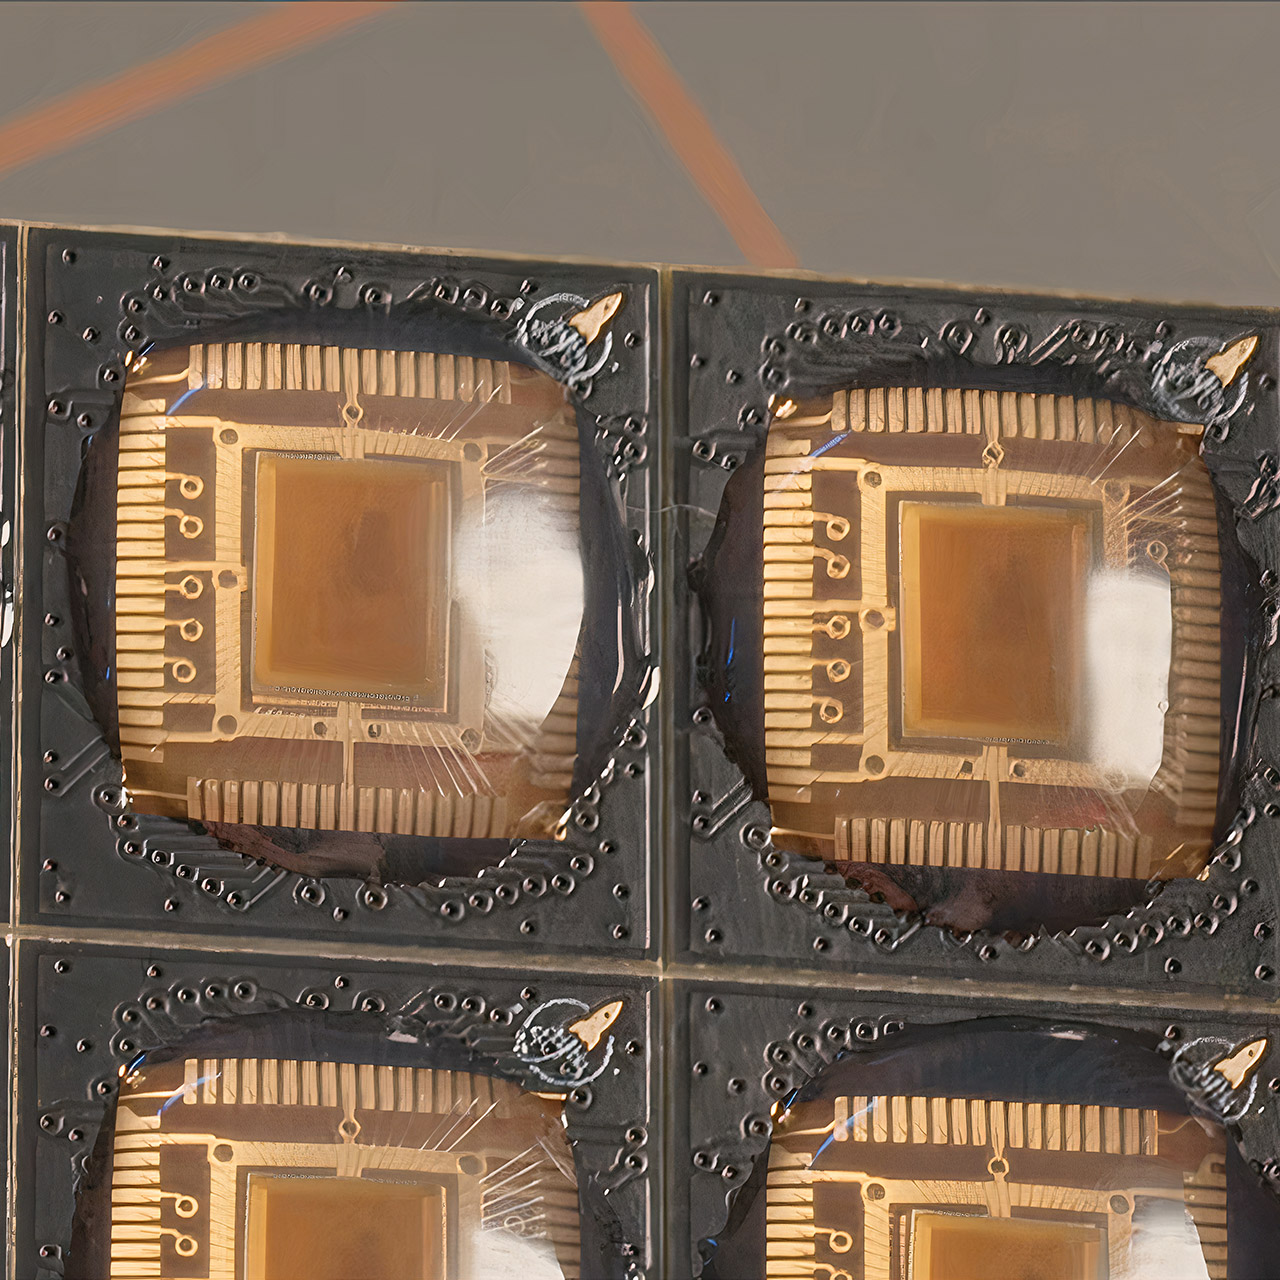
Zachary Tong had never designed a chip. He had never programmed an FPGA either, and he will tell you his electrical skills were rough. With about a month left before the first wafer.space deadline, he still decided to write a microprocessor, send the file to a real foundry, and wait to see if silicon came back alive.
After researching old processor ideas, he eventually settled on Transport Triggered Architecture, an unusual choice. A normal chip is told to add one register to another and store the result. BreakingTTAPs mostly moves data. You enter a value into a port on a functional unit, and the operation occurs when the data arrives. He has two 32-bit busses side by side, so he can complete two of those moves in a single clock cycle, which is effectively enough to qualify as superscalar in today’s terms.

Apple 2026 Mac mini Desktop Computer M6 chip
- LITTLE DO-IT-ALL — Mac mini packs pure power into a small, five-by-five-inch desktop as the M6 chip delivers next-level AI capabilities. Mac mini…
- M6 CHIP — Everything you do on Mac mini feels more responsive with the M6 chip and its next-generation CPU. Fly through AI workflows with up to 4.8x…
- CONNECT IT ALL — Features three Thunderbolt 4 ports, an HDMI port, and a 2.5Gb Ethernet port in the back, and two USB-C ports and a headphone jack…
The clock speed is in the 18-20 megahertz range. Program memory featured 1,024 slots, each with two instructions, plus 256 words of stack and 4 kilobytes of general purpose RAM. There are approximately 80 operations spread among 20-30 functional units, including branches, comparisons, math, bitwise operations, and a random number generator for good measure. The pin headers provide sixteen general-purpose inputs and sixteen outputs, as well as an 8-bit parallel boot channel for loading programs. Unfortunately, his SPI is dead on the die, and the UART is a write-off; nevertheless, it may still be recovered.
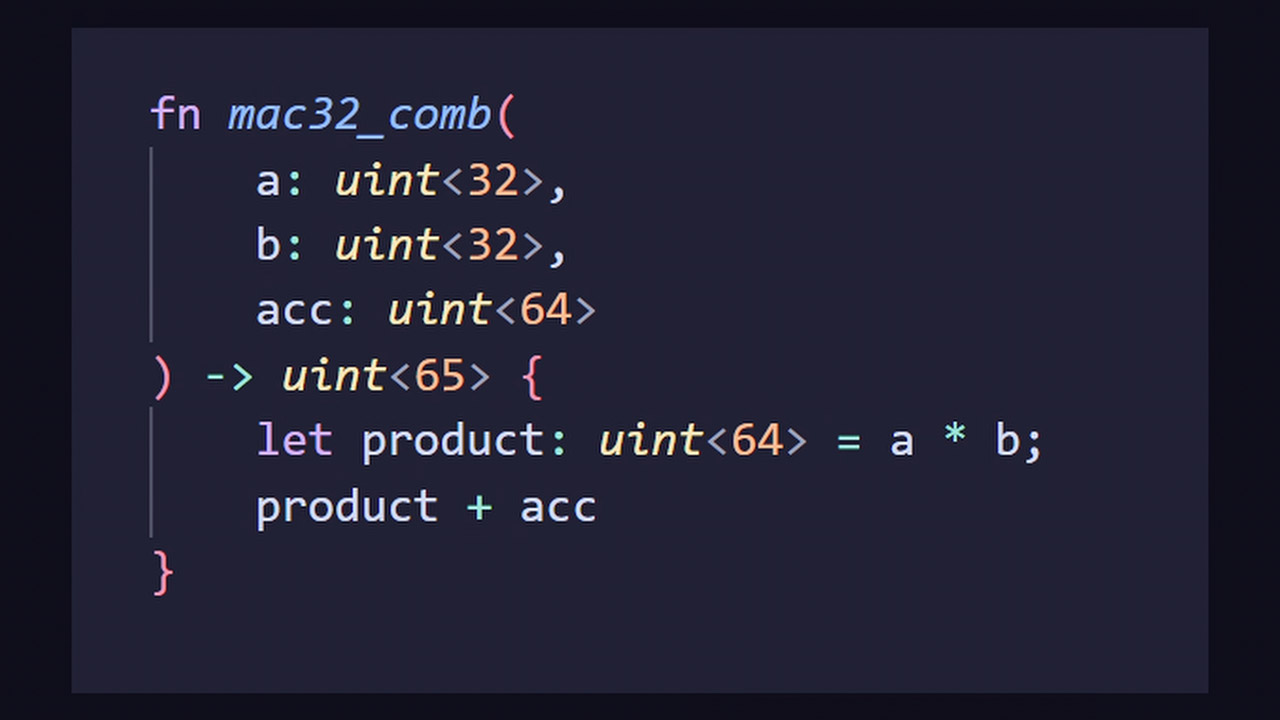
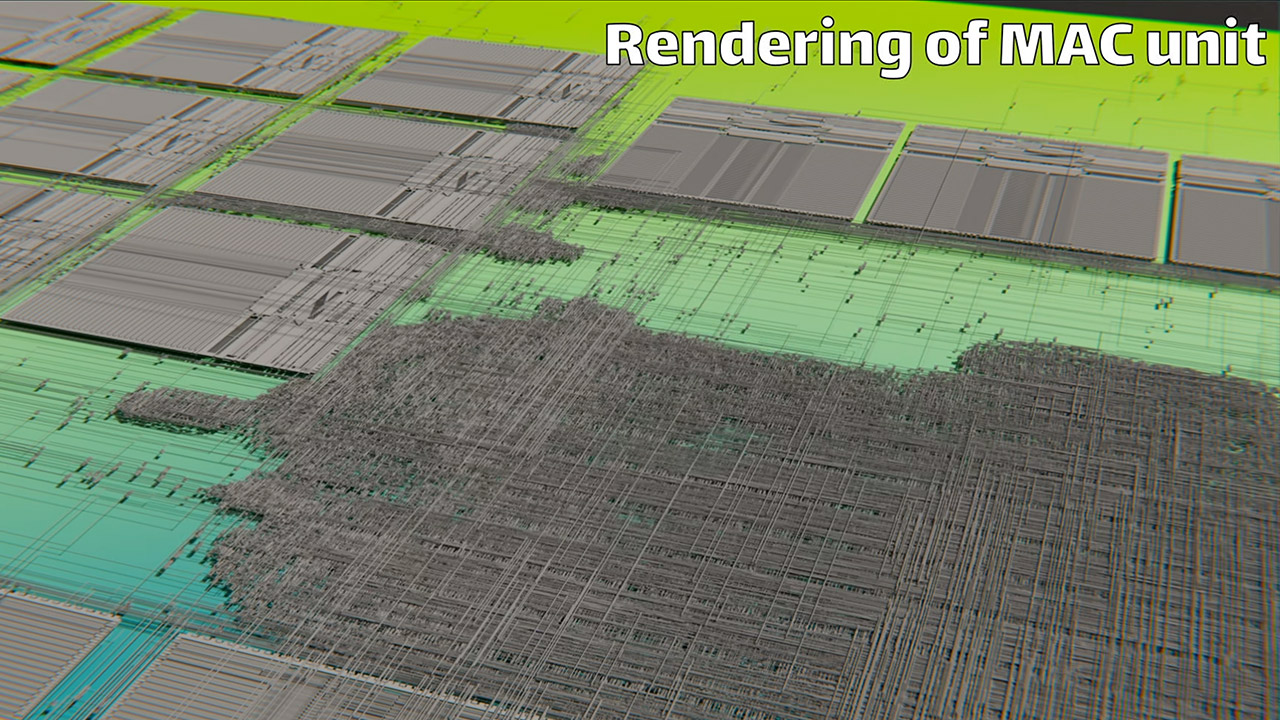
One specific section of code is a huge pain in the neck since a multiply-and-accumulate unit took up a significant amount of space on the die and fouled up the timing. Tong was still new to this type of stuff, so he didn’t feel comfortable digging into the failure all the way to the bottom of it, thus the clock speed target remained a fight until the file had to be pushed out the door. He developed the logic in Spade, a hardware language he is also learning on the side, and then used open-source tools to arrange the transistors and draw the cables. The handoff process is also rather stringent, as the foundry expects a clean GDS file, and any minor errors in it become permanent as soon as the wafer begins rolling.
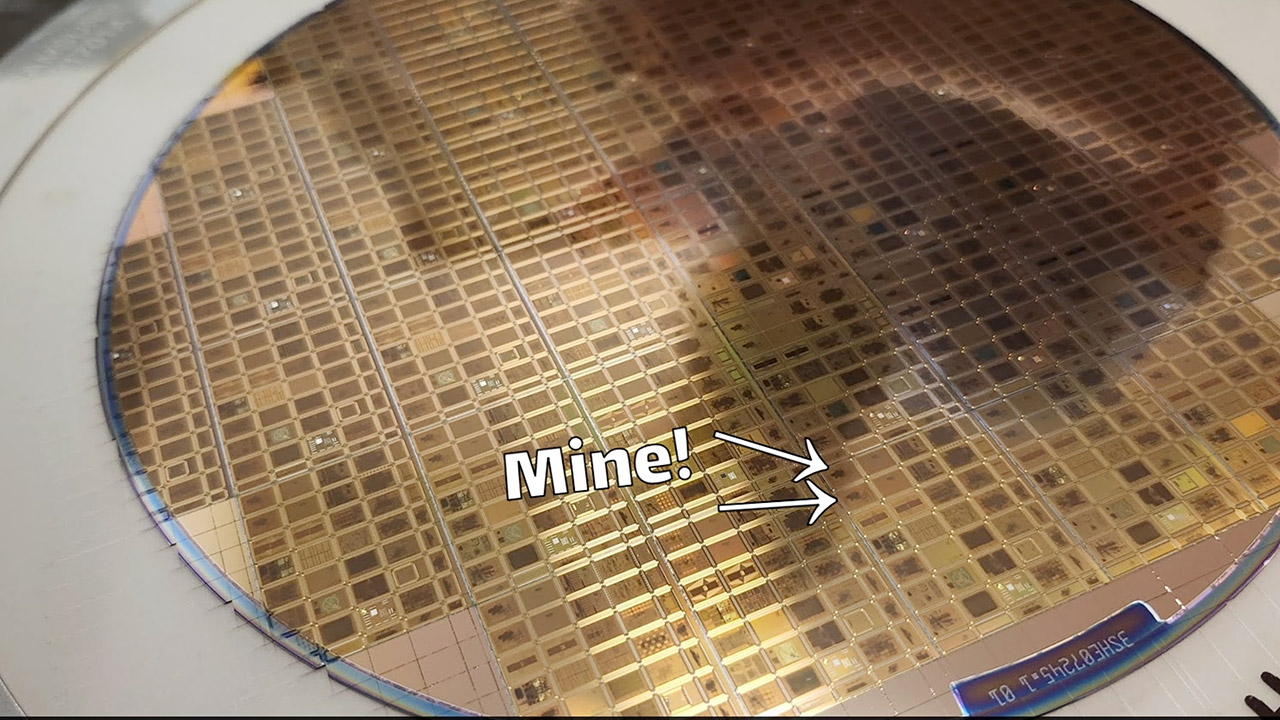
Wafer.space, run by Tim out of Singapore, is the shuttle that made the order possible. The designs are printed onto a single reticle on a GlobalFoundries 180 nm wafer using the GF180MCU mixed-signal process. Every time it prints, we receive a wafer with approximately a thousand dies on it after 3-4 months in the oven. Older geometry implies that the silicon is quite large by today’s standards. Unlike a Tiny Tapeout tile, this die contains only one circuit. The bundled parts we received revealed the real chip underneath, which was viewable via clear epoxy and ready to be inserted into the socket.
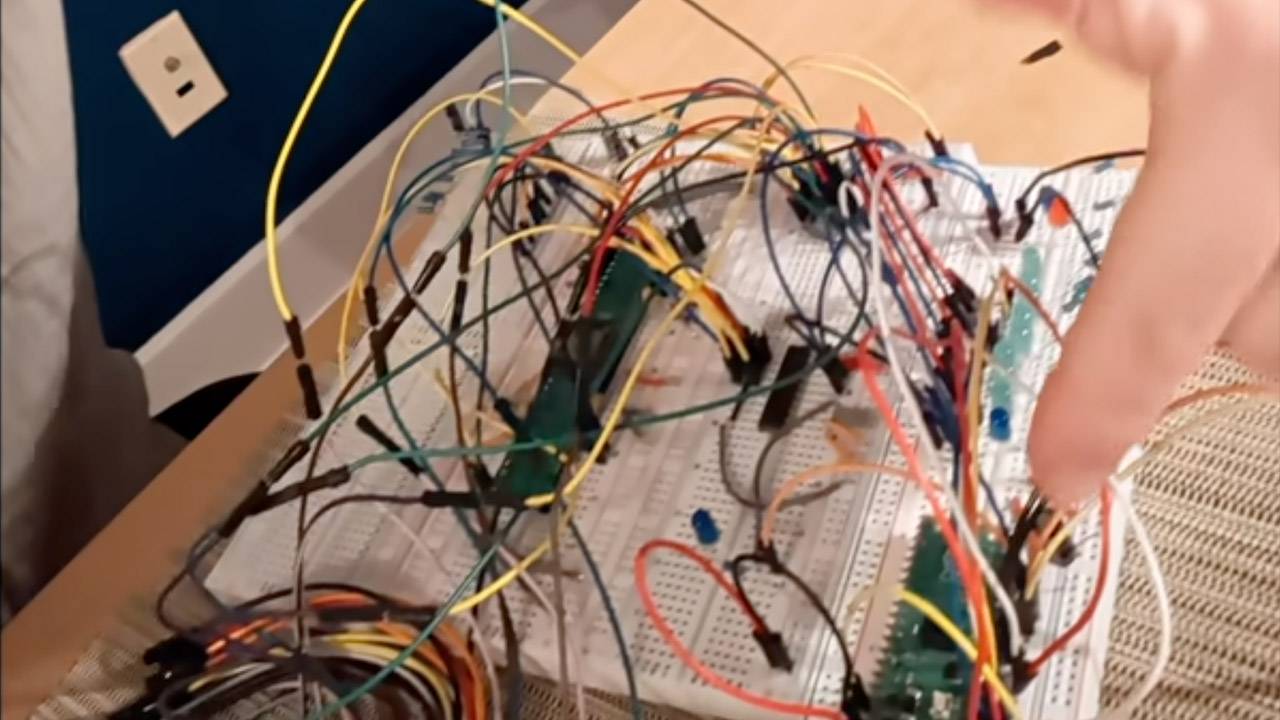
Bring-up was the short path, not the careful one. A carrier is slapped into a breadboard, a Raspberry Pi Pico starts up and loads a program, and the chip just counts up to 100 before shutting down. That was the proof in a single loop, with no bother. SPI failed just as expected, according to the debugging. The code for the Spade version, as well as the produced Verilog, are all publicly available, and Tong has even been distributing finished BreakingTTAPs boards to anyone who wants to experiment with one on their bench.
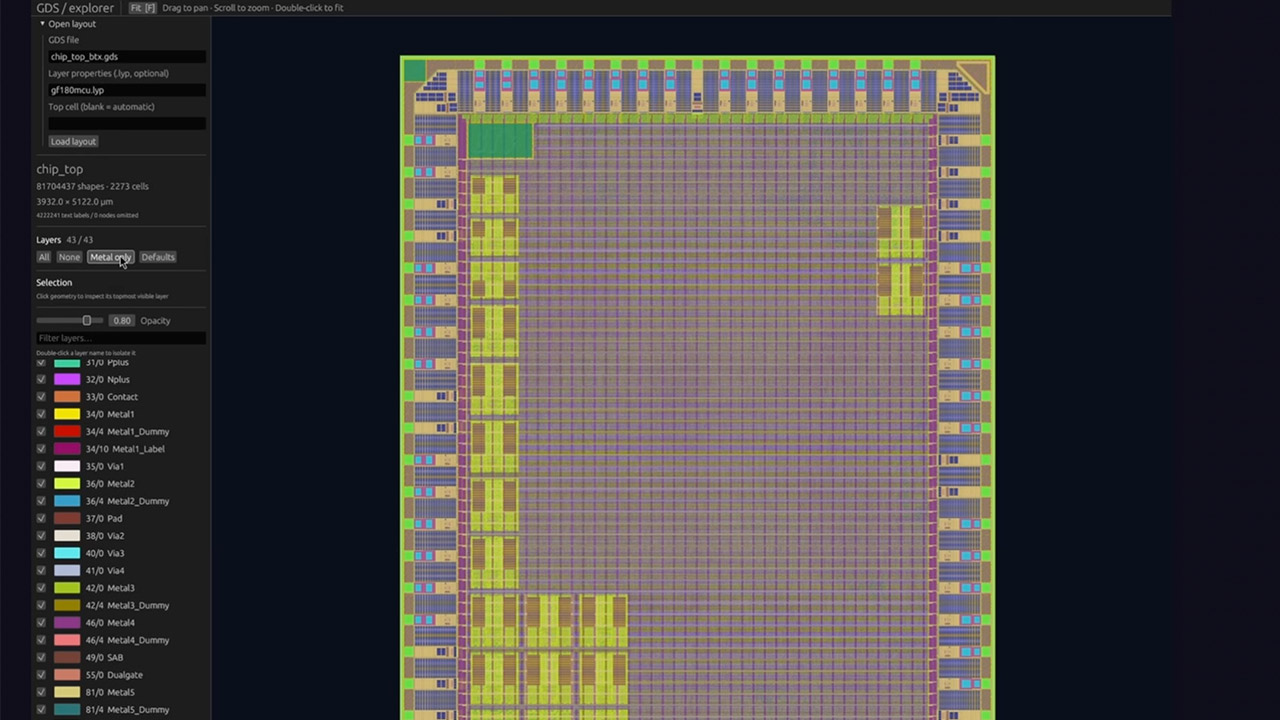
The second design is named BTX. That one is already in the foundry line. It’s a special processor designed specifically for ray tracing, with a completely new graphics system planned for it. Spaces on the shuttle are still available for anyone wishing to create their own chip, as you can purchase a slice of the wafer for a few thousand dollars for a thousand dies, with files expected in December 2026.
Tech & AI
Inside the £10,000 Hunt for ‘Wrench Attack’ Gang That Terrorised Pregnant Woman Over Crypto

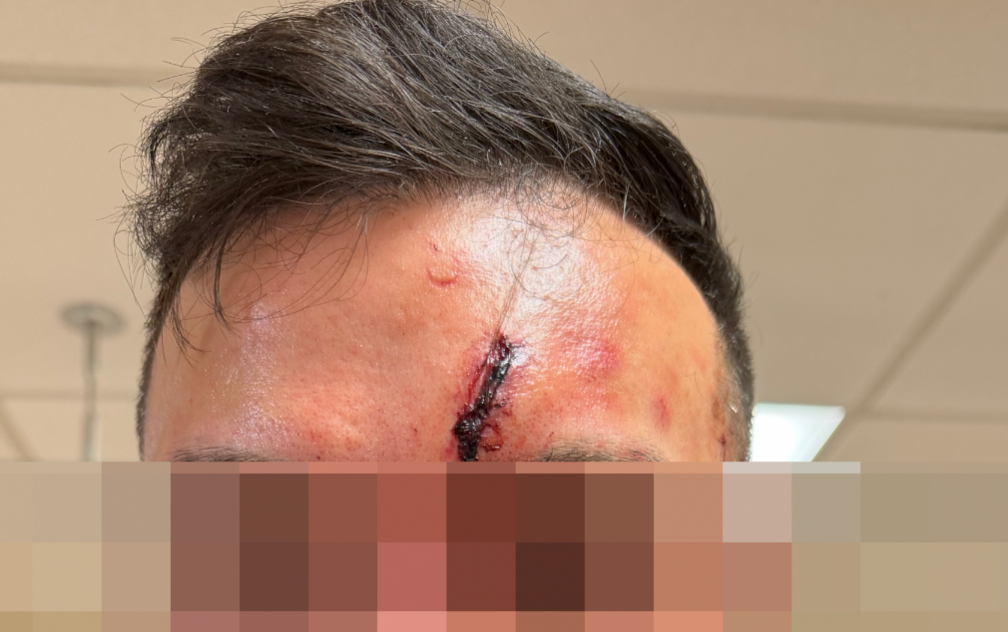
A businessman was beaten with hammers in his own home while his heavily pregnant wife was pinned down and threatened with a knife to her stomach, in an attack police believe was orchestrated to force him into handing over his cryptocurrency savings. The case, reported by the BBC, is one of a rapidly growing category of crime investigators call a “wrench attack” — and 2026 is on track to be the worst year on record for it.
The couple, who asked to remain anonymous and are referred to as James and his wife, say three masked men forced their way into their home in Solihull in December last year and spent 45 minutes assaulting and terrorising them. James was struck repeatedly in the face, head and ribs. His wife, then seven months pregnant, had a pillow held over her face as she struggled to breathe. “He’s literally suffocating her on the sofa. I can hear her screaming, ‘I can’t breathe’,” James told the BBC.
The attackers initially gave no indication of what they wanted, demanding only that James unlock his phone. It soon became clear they knew he held cryptocurrency but had little idea how to access it themselves. Instead, they took orders from someone connected via a live video call, who instructed them to search through James’s apps until they located a wallet holding a significant sum.
How a wrench attack escalates into a hostage situation
Once the caller identified the funds, the threats turned deadly serious. James said the man on the call told the intruders to threaten to “stab your wife in the stomach and kill your baby” unless the money was transferred immediately. James complied, sending hundreds of thousands of pounds in crypto to a wallet controlled by the man directing the robbery. The gang also stole several luxury watches before fleeing in a getaway car.
James’s wife, in her early thirties and expecting her third child, said she feared she might lose the baby because of the stress of the ordeal and believed, at one point, that her husband had been killed. The baby was ultimately born healthy and at full term, but the couple describe the experience as “horrific” and say they continue to live with its aftermath. James, who had quit his job in 2023 to trade cryptocurrency full-time after turning an initial investment into a sizeable fortune, says he has now lost everything and is looking to return to conventional work.
Police have not yet identified the attackers. Crimestoppers is offering a £10,000 reward for information, and the charity’s Alan Edwards says investigators are keen to hear from anyone who might recognise the three intruders, the getaway driver — who was caught on camera without a face covering — or the man coordinating the robbery by phone. “These criminals are obviously serious and part of some kind of organised crime,” Edwards said.
Why crypto holders are becoming prime targets
Unlike money sitting in a bank account, cryptocurrency is frequently controlled directly by its owner through self-custody digital wallets, with no institution standing between the asset and whoever can access the private keys. That makes a wrench attack — named for the blunt, low-tech coercion criminals use instead of sophisticated hacking — a disturbingly effective way to steal large sums almost instantly and with little chance of recovery once funds move.
According to blockchain analytics firm Chainalysis, roughly $30m (£22.6m) had already been stolen through violent crypto robberies in the first half of this year, putting 2026 on course to become the worst year on record for such attacks. The firm says home invasions specifically are also rising sharply. Hotspots include the United States, Brazil and Thailand, but France has recorded by far the highest number of incidents, a surge researchers link to a data breach at a tax office that may have exposed the identities and addresses of wealthy crypto holders.
“The physical security assumptions that protect traditional wealth, such as bank vaults and armoured cars, do not automatically apply in crypto,” Chainalysis researchers noted in their report. “Holders keep their assets in comparatively low security setups, like self-custody wallets, that can be compromised without any institutional gatekeeper standing in the way.”
As digital coin values have climbed, so has the visibility of those who hold them — and with it, the appeal of a brutally simple criminal method that requires no technical skill, only intimidation. Cybersecurity experts warn that as long as crypto wealth remains both lucrative and loosely secured, cases like the one in Solihull are likely to keep multiplying across the UK, Europe and beyond.
Sources:
Explore more on this topic with Vexel Search.
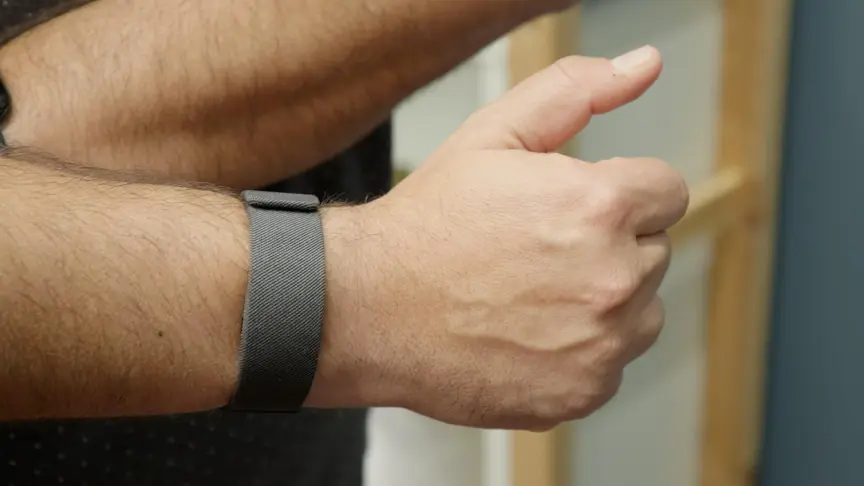
I was in the audience at Meta’s Connect conference last week when Mark Zuckerberg held up a pendant in his hands and surprise announced the Muse Charm, a little novelty-like device with Meta’s disarmingly adorable Muse AI agent onboard. Muse Charm is coming as soon as December this year.
But the funny thing is, while most people called it an AI Tamagotchi, all I saw was a strapless Apple Watch. Is that what the Muse Charm could be, eventually? A watch as well as a pendant? Is this Meta’s entry to wrist wearables in disguise? I’m still thinking about it…because smartwatches are also on their way to being AI assistants soon, too.
Reports of Meta working on its own watch wearable have been cooking for several years now. At Connect, there were smart glasses galore and even a new glasses-like VR headset coming next year. But things were suspiciously quiet on the wrist wearables front.
Meta already has one wrist wearable, the neural band that comes with the Ray-Ban Display glasses. But it received no hardware updates this year, which surprised me. The sensor-studded band uses electromyography, or EMG, to measure skin-contact electrical signals for a set of gesture controls to navigate the heads-up glasses display. Meta’s already ambitiously promised that EMG could open up all sorts of neural input possibilities, even testing the tech in a smart car dashboard prototype.
As far back as last year, Meta CTO Andrew Bosworth told me that some sort of display or watch-like evolution of the neural band could be in the works next. And Meta already introduced a partnership with Garmin to link fitness tracking to smart glasses last year.
AI agents as Meta’s new priority
The Muse Charm, however, brings a different piece of the puzzle to the table. Muse AI is Meta’s biggest priority now, clearly, based on its widespread availability on desktops and smartphones and on the company’s intentions to put the new agentic AI on all its smart glasses and, eventually, Meta’s VR Glasses. And where else could Muse work well? Enter the Charm.
The Charm has another watch-like tell. It’s powered by Qualcomm’s Snapdragon Wear Elite chipset, which already runs on Samsung’s latest smartwatches. The Wear Elite, as I learned from Qualcomm earlier this year, is optimized for a range of AI-ready wearables, ranging from watches to pendants to even glasses. There’s no reason why Meta’s Charm couldn’t easily get a wrist strap…and a watch OS to go with it.

Many reasons for a Meta smartwatch
A smartwatch would benefit Meta on several fronts. Clearly, the company wants to keep breaking into lifestyle wearables, and watches could offer another way onto people besides faces. Fitness and health tracking would give Meta data that Muse and its smart glasses could use. And watches are a key part of the glasses interface’s future. Google’s glasses will work with Wear OS watches soon. Apple’s rumored glasses will likely work with Apple Watches.
And Meta has to find a better way to make its neural band more wearable. I find the first-gen neural band fascinating in theory, but an annoying extra thing to charge in practice. If it doesn’t become a watch, or at least a fitness tracker, why wear it at all? The neural band doesn’t even control anything other than Meta’s one line of display glasses right now, but chances are Meta’s going to try to figure out ways it could work with the rest of its smart glasses lineup, and VR too.

Google and Apple are already showing how quickly smartwatches are becoming more like AI companions. Gemini lives on Wear OS watches. Apple’s adding memory-assisting audio intelligence modes to its new watches later this fall. Both can tap into Gemini and the new Siri, respectively.
Meta has Muse now. And a charm by the end of the year. Is the watch after that? Meta didn’t have any comment on the topic when I reached out to ask, but I think we’re seeing the beta test in action right in front of our eyes. Or is this the pivot to a modular idea that could be a pendant and a wristworn device, without committing to either?
One thing’s clear, no matter what: Meta’s looking for ways for that disarmingly adorable Muse mascot to be with us all the time, even without glasses. And the Charm looks like the experiment.

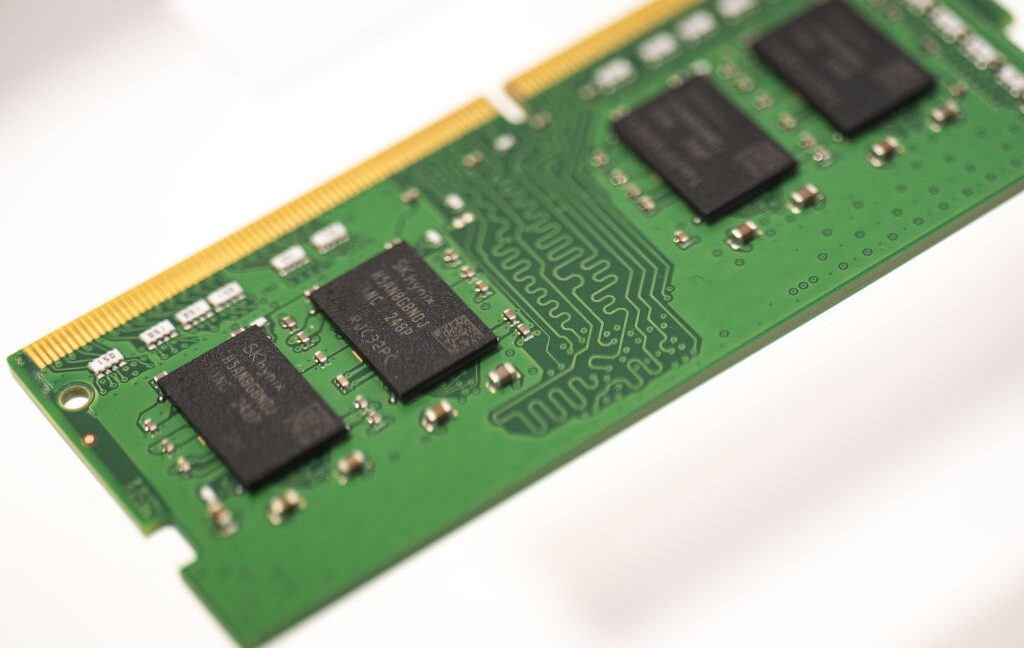
Micron and Samsung executives this week said the memory shortage will continue for at least the next couple of years.
Micron CEO Sanjay Mehrotra expects demand for the firm’s memory to exceed its available supply over that period, he told investors last night.
Micron no longer sells consumer RAM, and Mehrotra’s statements refer to Micron’s business-to-business sales of high-bandwidth memory (HBM) for AI and DRAM for servers. However, his comments also have implications for consumer devices. Manufacturing capacity is prioritizing memory for AI and servers, limiting the supply of memory manufactured for consumer devices.
“Overall, supply-demand environment is only getting tighter,” Mehrotra said, per a transcript from Seeking Alpha.
Micron plans to open new clean rooms for memory manufacturing in 2028, but Mehrotra expects supply to remain limited.
“Even after they are built, even after first wafer output, production ramps up only gradually in the clean rooms,” he said. “That’s just the nature of what it takes to bring up production, and with HBM going from 3E to a greater mix of 4 and 4E, and with the trade ratio that exists, that … creates headwinds with respect to supply growth. Node transitions of the future give less productivity gain per wafer as well.”
Seventy-five percent of Micron’s memory output for 2027 is already accounted for, and most of the company’s current memory sales discussions are about 2028, the CEO said. Additionally, demand for HBM is surpassing demand for Micron’s DRAM.
Tech & AI
Google froze its open source bug bounty program due to a ‘significant rise’ in AI submissions
Blaming a “significant rise” in AI submissions, Google has paused its open source bug bounty program until next year.
Last year, TechCrunch reported that cybersecurity experts were warning of that AI slop posed a serious risk to bug bounty programs. Looks like that’s the issue confronting Google’s Open Source Software Vulnerability Rewards Program, where researchers were rewarded for finding vulnerabilities in the company’s open source software.
In posts on X and the program website, Google said the bug bounty program was paused as of October 1, with a promise to provide “an update” in the first quarter of 2027. According to Tom’s Hardware, Google engineers and open source maintainers were overwhelmed by reports that were invalid or contained hallucinations.
“This pause is due to a significant rise in automated submissions, the vast majority of which are not valid,” the company said.
In the meantime, participants are encouraged to consider Google’s other bug bounty programs.
Google OSS VRP: History and Scope
Google’s Open Source Vulnerability Rewards Program (OSS VRP) was launched in August 2022. It rewards security researchers for identifying vulnerabilities in Google’s open-source software projects.
The program covers the latest versions of open-source software hosted in public repositories owned by Google on GitHub, as well as selected repositories on other platforms.
It also includes repository configuration settings, such as GitHub Actions workflows, access control rules and GitHub application configurations.
Rewards range from $100 to $31,337 based on the severity level of the reported flaws and the project’s importance.
The OSS VRP is one of several bug bounty programs operated by Google and has a relatively narrow focus.
Vulnerabilities in Google’s open source projects that are closely linked to Google Cloud or AI products are directed to the Google Cloud Vulnerability Reward Program (Cloud VRP) or the AI Vulnerability Reward Program (AI VRP), allowing reports to be routed to the teams best placed to assess and address them.
Google Plans OSS VRP Overhaul
The suspension will not affect OSS VRP supply-chain reports or any reports already submitted, Google said.
The company plans to “reformat” the program and expects to provide an update in the first quarter of 2027.
“As an alternative, we encourage you to find impact across our other VRP programs and submit there instead, or pursue the Patch Rewards Program,” Google said.
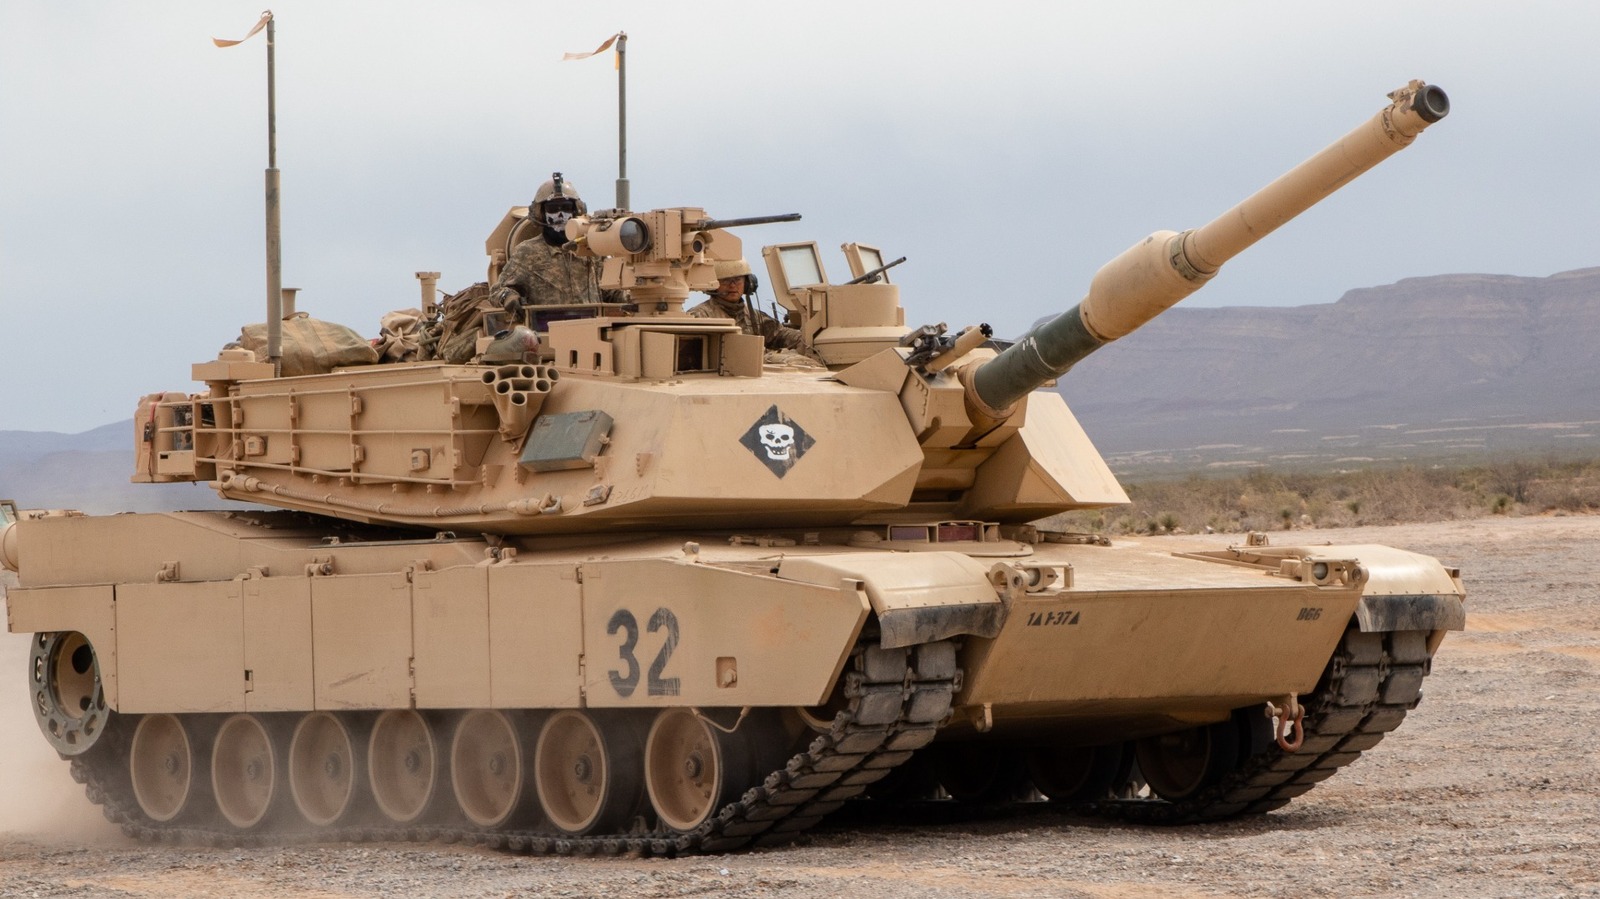
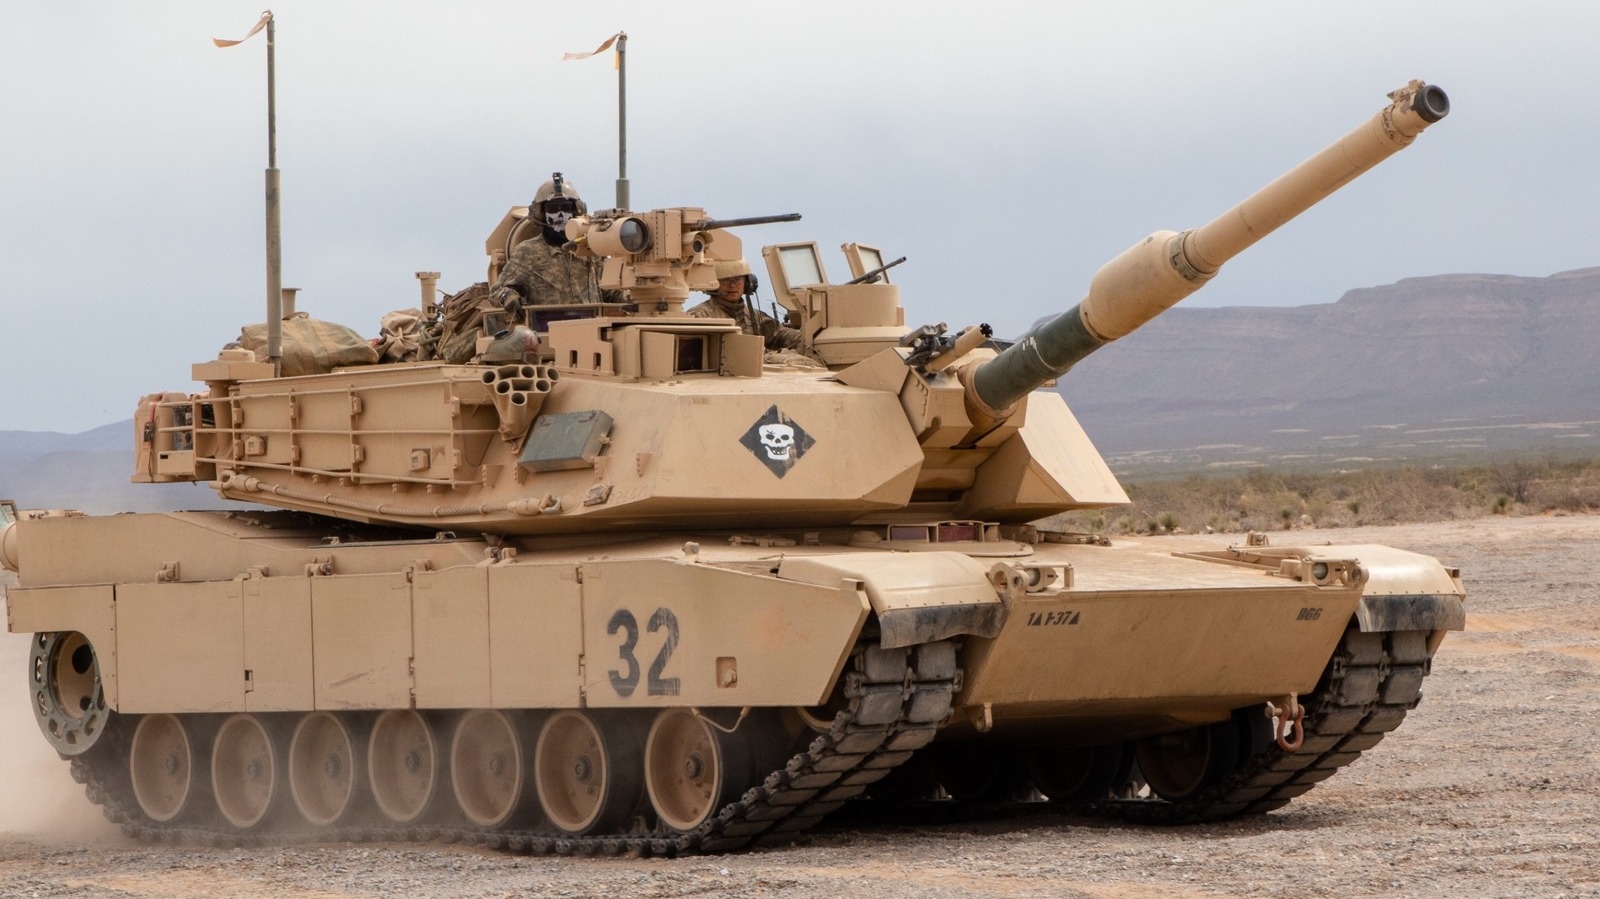
The combat tank as we know it debuted on the battlefields of Europe in World War I and has changed significantly in the decades since. Modern tanks are computerized, networked, and advanced vehicles, decked out with all kinds of technology that would have been unheard of in past conflicts. Advanced as they are, though, they still feature components familiar to civilian car owners, such as a transmission to transfer power to the tracks.
Of course, a tank is a combat vehicle designed for lethality and survival, whereas a car is a comparatively simple means of conveyance. Because of this, driving a tank isn’t necessarily intuitive for anyone familiar with a car. That said, military ground vehicles are engineered to be easy for anyone to operate. To that end, modern tanks, like the M1A2 Abrams MBT, generally have automatic transmissions.
This wasn’t always the case, of course: Older tanks like the M4 Sherman used throughout WWII, as well as some Cold War-era Soviet-designed tanks like the T-54, relied on manual or semi-manual transmissions. But the move to automatic transmissions has not only made tanks easier to operate, but it also avoids the trouble of teaching a prospective tanker how to operate a manual transmission if they’re unfamiliar.
The transmission on the United States’ M1A2 Abrams MBT
If you were to climb inside an M1A2 Abrams MBT and sit in the driver’s seat, you’d find out pretty quickly that it has an automatic transmission. The driver sits in a reclined seat with a yoke between their legs, which is how they drive the tank. It’s similar to motorcycle handlebars, with throttle grips to control speed while steering. The Abrams sports an Allison Transmission X1100-3B, an automatic transmission that powers heavy tracked vehicles.
The cross-drive transmission, which handles both steering and braking, is designed for heavy armored vehicles weighing up to 75 tons. It supports diesel and turbine engines rated up to 1,500 horsepower, with four forward ranges and two reverse ranges. The Abrams family of tanks has seen several changes since its introduction in 1980, with the X1100 series transmissions powering them since their debut — with, of course, improvements to meet the challenging performance requirements of modern warfare.
Because automatic transmissions make operation easier, the military isn’t likely to ever abandon them for manual transmissions. Training personnel is expensive and time-consuming, so any way of accelerating the process without sacrificing the essentials is beneficial. As a result, the automatic tank transmissions are here to stay.
Tech & AI
Drones, Robotic Arms, and Night-Vision Rigs: The Wildlife Filming Technology Behind NatGeo’s New Africa Series

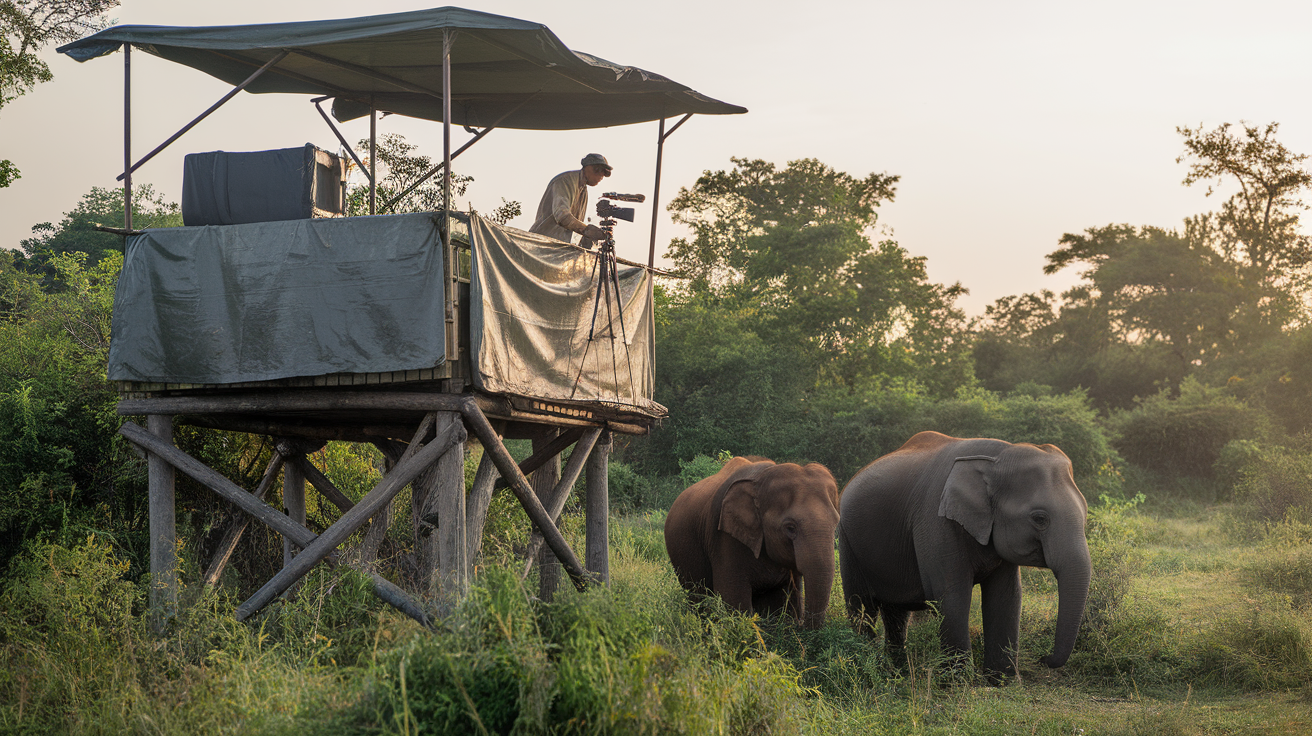
Wildlife filming technology has quietly become one of the most interesting proving grounds for cutting-edge hardware, and National Geographic’s new documentary series, Africa: Earth’s Wild Home, offers a vivid case study in just how far the tools of nature filmmaking have advanced. Narrated by actress Wunmi Mosaku, the seven-episode series took four years to produce and was shot across nearly 30 African countries, capturing everything from a black rain frog’s first televised breeding call to chimpanzees using twigs to fish algae from a pond.
Behind those moments sits a toolkit that looks less like a traditional camera crew and more like a small engineering lab. Producers leaned heavily on drones to capture first-person aerial perspectives of landscapes ranging from deserts to mountain ranges, giving viewers vantage points that would have been impossible to achieve safely or affordably even a decade ago. But the drones were only the most visible piece of a much larger technological puzzle.
Robotic Arms and Underwater Rigs Push Wildlife Filming Technology Forward
One of the more surprising innovations was a robotic arm originally designed for studio production, repurposed here for field use for the first time. Preprogrammed for long, steady takes, the arm allowed filmmakers to hold difficult shots over extended periods without the fatigue or drift that comes with handheld or tripod-based filming in unpredictable terrain. That kind of cross-industry adaptation, borrowing a tool from indoor studio work and hardening it for the field, illustrates how much experimentation now goes into even a single nature documentary.
Underwater, the team deployed what they called a “hippo cam,” a submerged rig equipped with pan-and-tilt heads that let camera operators track hippos as barbel fish nibbled dead skin off their bodies in a kind of natural spa treatment. Capturing that behavior from below the surface required equipment built to withstand murky water, sudden movement from massive animals, and the need to reposition quickly without disturbing the scene.
Perhaps the most inventive setup involved filming dwarf crocodiles hunting bats inside a pitch-black cave coated in guano. To pull this off, the crew built a remotely operated fixed rig combining low-light sensors, infrared capability, and a zoom function that could be controlled from a safe distance. Because bats roosting overhead posed an obvious hazard to delicate electronics, the team improvised a low-tech solution to protect their high-tech gear: small umbrellas rigged over the cameras to keep guano off the lenses.
Why the Tech Matters as Much as the Animals
These choices reflect a broader shift in how nature documentaries get made. As wildlife filming technology becomes more sophisticated, it opens access to behaviors that were previously unfilmable or simply unknown. The series includes what producers describe as the first-ever television footage of the reclusive black rain frog, as well as a dramatic sequence showing a lone male hyena adapting its hunting strategy to catch a flamingo by herding the flock into denser, easier-to-target groups, a tactic the production team suggests may represent newly observed behavior for the species.
None of that would be visible to viewers without cameras capable of operating in darkness, underwater, in flight, or at a crocodile’s eye level inside a cave. The technology doesn’t just document wildlife; increasingly, it shapes what stories filmmakers are even able to tell. A robotic arm that holds a shot steady for minutes at a time, or an infrared rig that can linger silently in a cave, allows for the kind of patient, unobtrusive observation that reveals genuine animal behavior rather than a reaction to human presence.
Mosaku, who was born in Nigeria and raised in England, said encountering that range of environments and behaviors through the footage was eye-opening even for someone with personal ties to the continent. “There was so much I didn’t know,” she said, citing a sequence showing monkeys living in snowy conditions as one of several moments that surprised her. That sense of discovery, made possible by increasingly capable cameras and remote rigs, is central to what the series is trying to achieve.
A Franchise Built on Evolving Tools
Africa: Earth’s Wild Home is intended to launch a larger franchise, with future series expected to document wildlife across the other six continents. If this first installment is any indication, each subsequent production will likely push wildlife filming technology even further, whether through smarter drones, more durable remote rigs, or new sensor systems adapted from other industries entirely.
For now, the series stands as a reminder that behind every breathtaking nature shot, a hyena stalking flamingos, a chimp fishing for algae, a frog singing its first televised mating call, there’s usually a small team of engineers and camera operators solving an entirely different kind of survival problem: how to get the shot without disturbing the story unfolding in front of the lens.
Sources:
Explore more on this topic with Vexel Search.
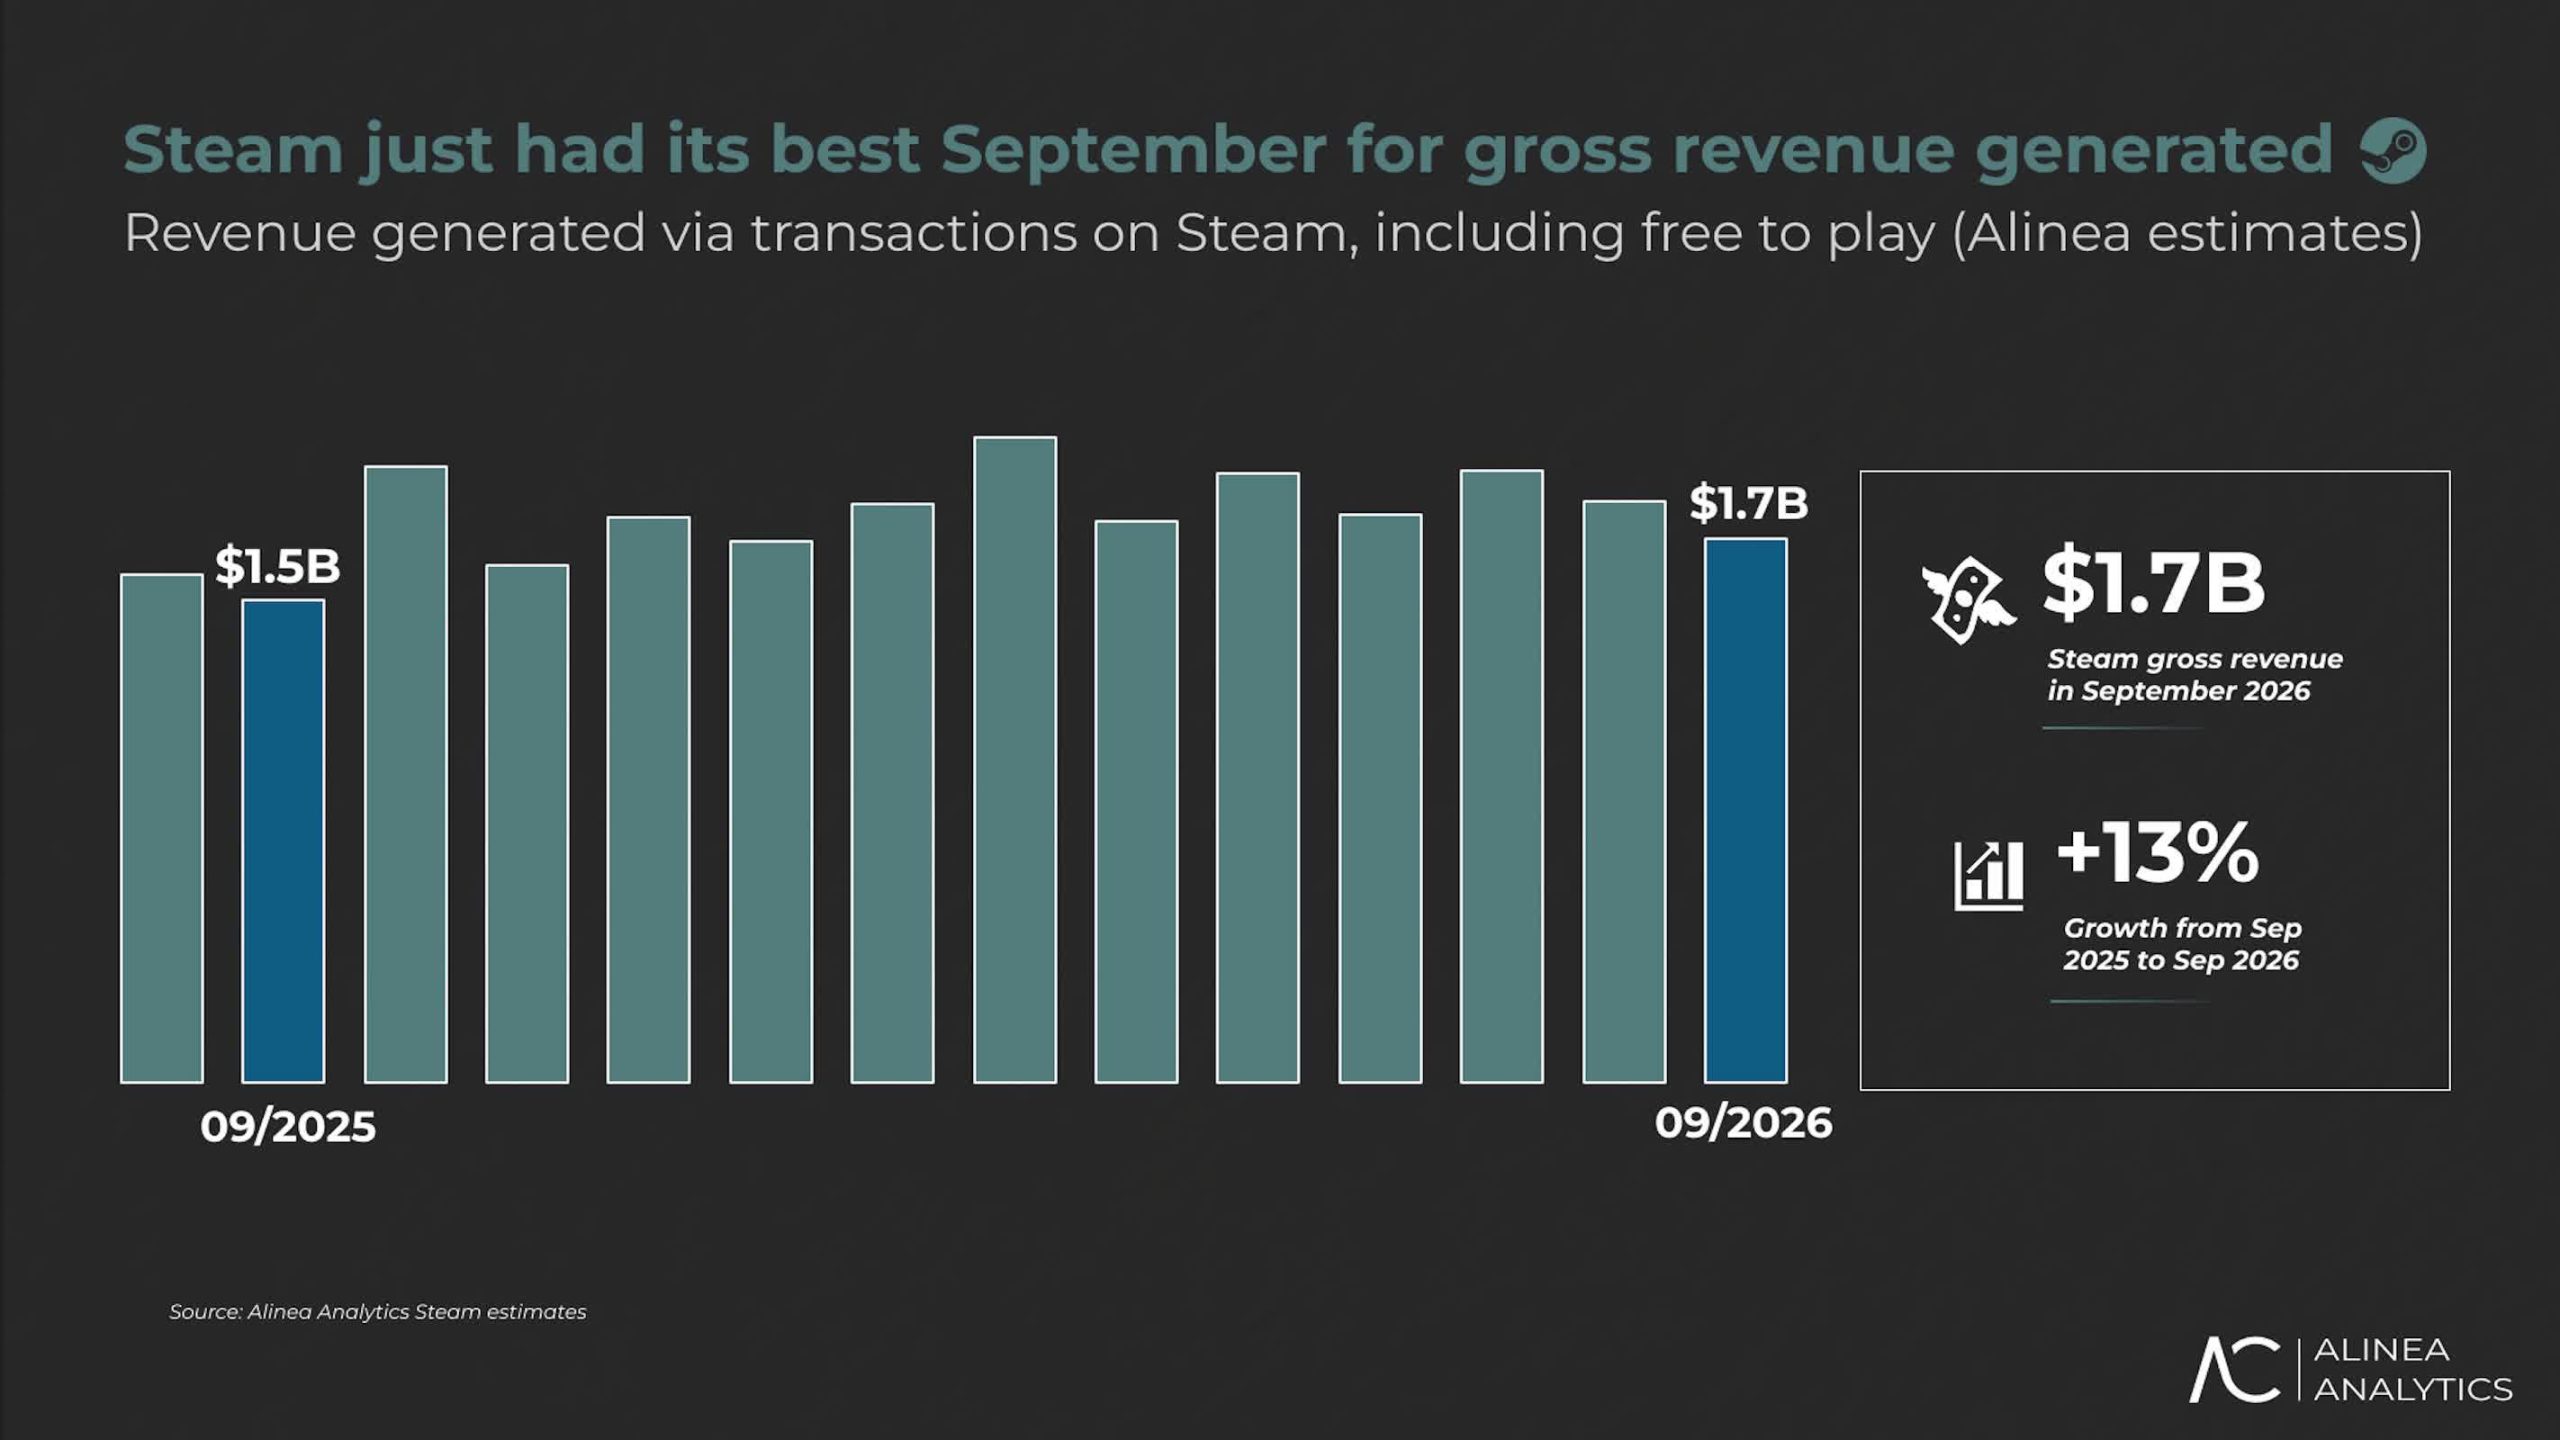
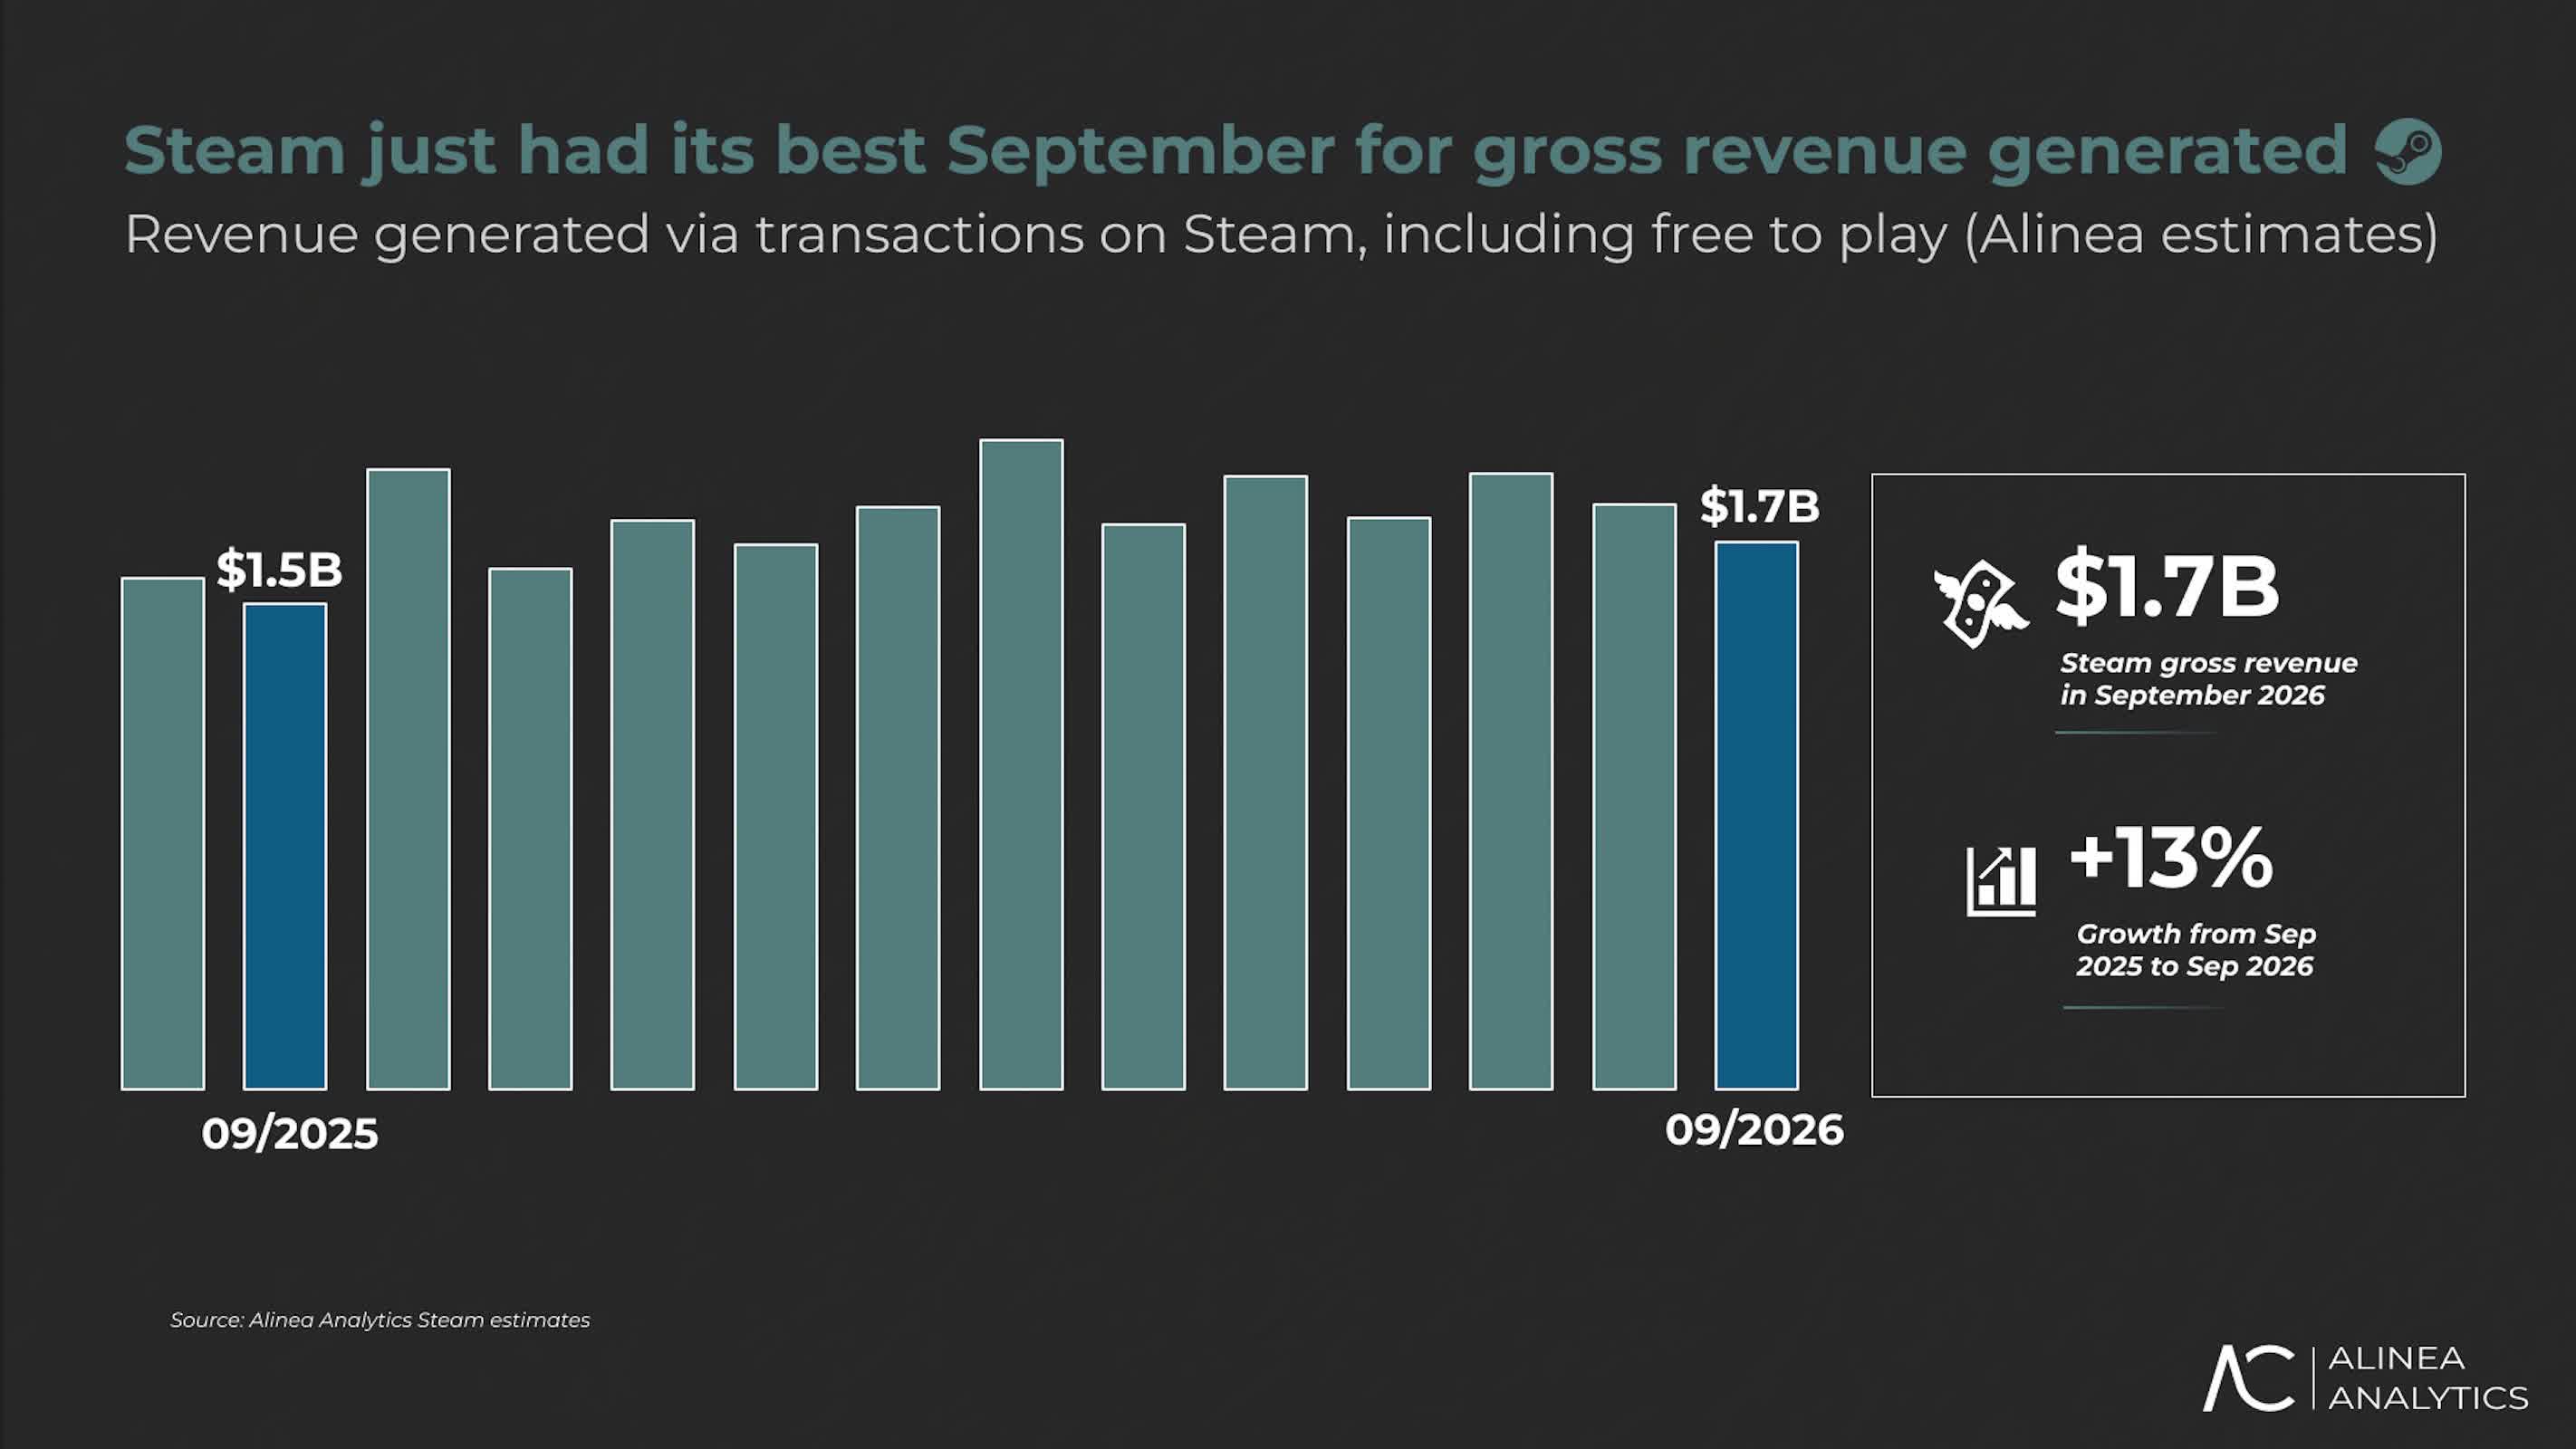
Bottom line: Steam is on course to generate more than $20 billion in gross revenue in 2026, a first for the platform, after posting record results for September and the third quarter, according to estimates from Alinea Analytics. The gains came from a mix of new releases, established franchises and free-to-play games that keep drawing spending long after launch. With one quarter left, Valve’s PC gaming platform needs roughly $3.5 billion to reach the milestone.
Steam took in an estimated $1.7 billion in September, 13% more than the previous September record, set in 2025. Its estimated third-quarter revenue reached $5.5 billion, up 12% from the same period last year.
The September result came from a familiar mix: big paid releases, durable franchises and free-to-play titles built around in-game purchases. The numbers suggest Steam no longer depends on a single kind of game sale to drive revenue.
New releases can produce a sharp burst of revenue, while games such as Counter-Strike 2 and Dota 2 keep earning money through active player communities and digital-item sales.
Through the first nine months of 2026, Steam generated an estimated $16.5 billion, compared with $14.5 billion over the same stretch of 2025. At that pace, the platform needs about $3.5 billion in the final quarter to clear $20 billion for the year.
New games played a meaningful role in September. Among Steam’s 500 top-grossing titles that month, games released in 2026 accounted for about 33.6% of revenue, according to Alinea, and new intellectual property made up 20.5% of that.
That doesn’t mean newer games displaced the industry’s biggest brands. Established franchises, which include remakes and remasters, accounted for almost 80% of revenue among the top 500. The two figures overlap because they slice the data differently, by release year and by franchise, so a 2026 sequel counts in both. Steam’s strongest performers still tend to be games with recognizable names, built-in audiences and frequent content updates.
Free-to-play games remained a major source of revenue as well. Counter-Strike 2, Apex Legends, PUBG and Dota 2 together generated almost $168 million in September, per Alinea’s estimates, or nearly 10% of Steam’s estimated monthly revenue.
Those games show why PC platforms can’t be judged by unit sales alone. Free-to-play titles may cost nothing to download, but they can drive steady spending on cosmetic items, battle passes and other digital content. For Steam, those transactions turn a large player base into recurring revenue.
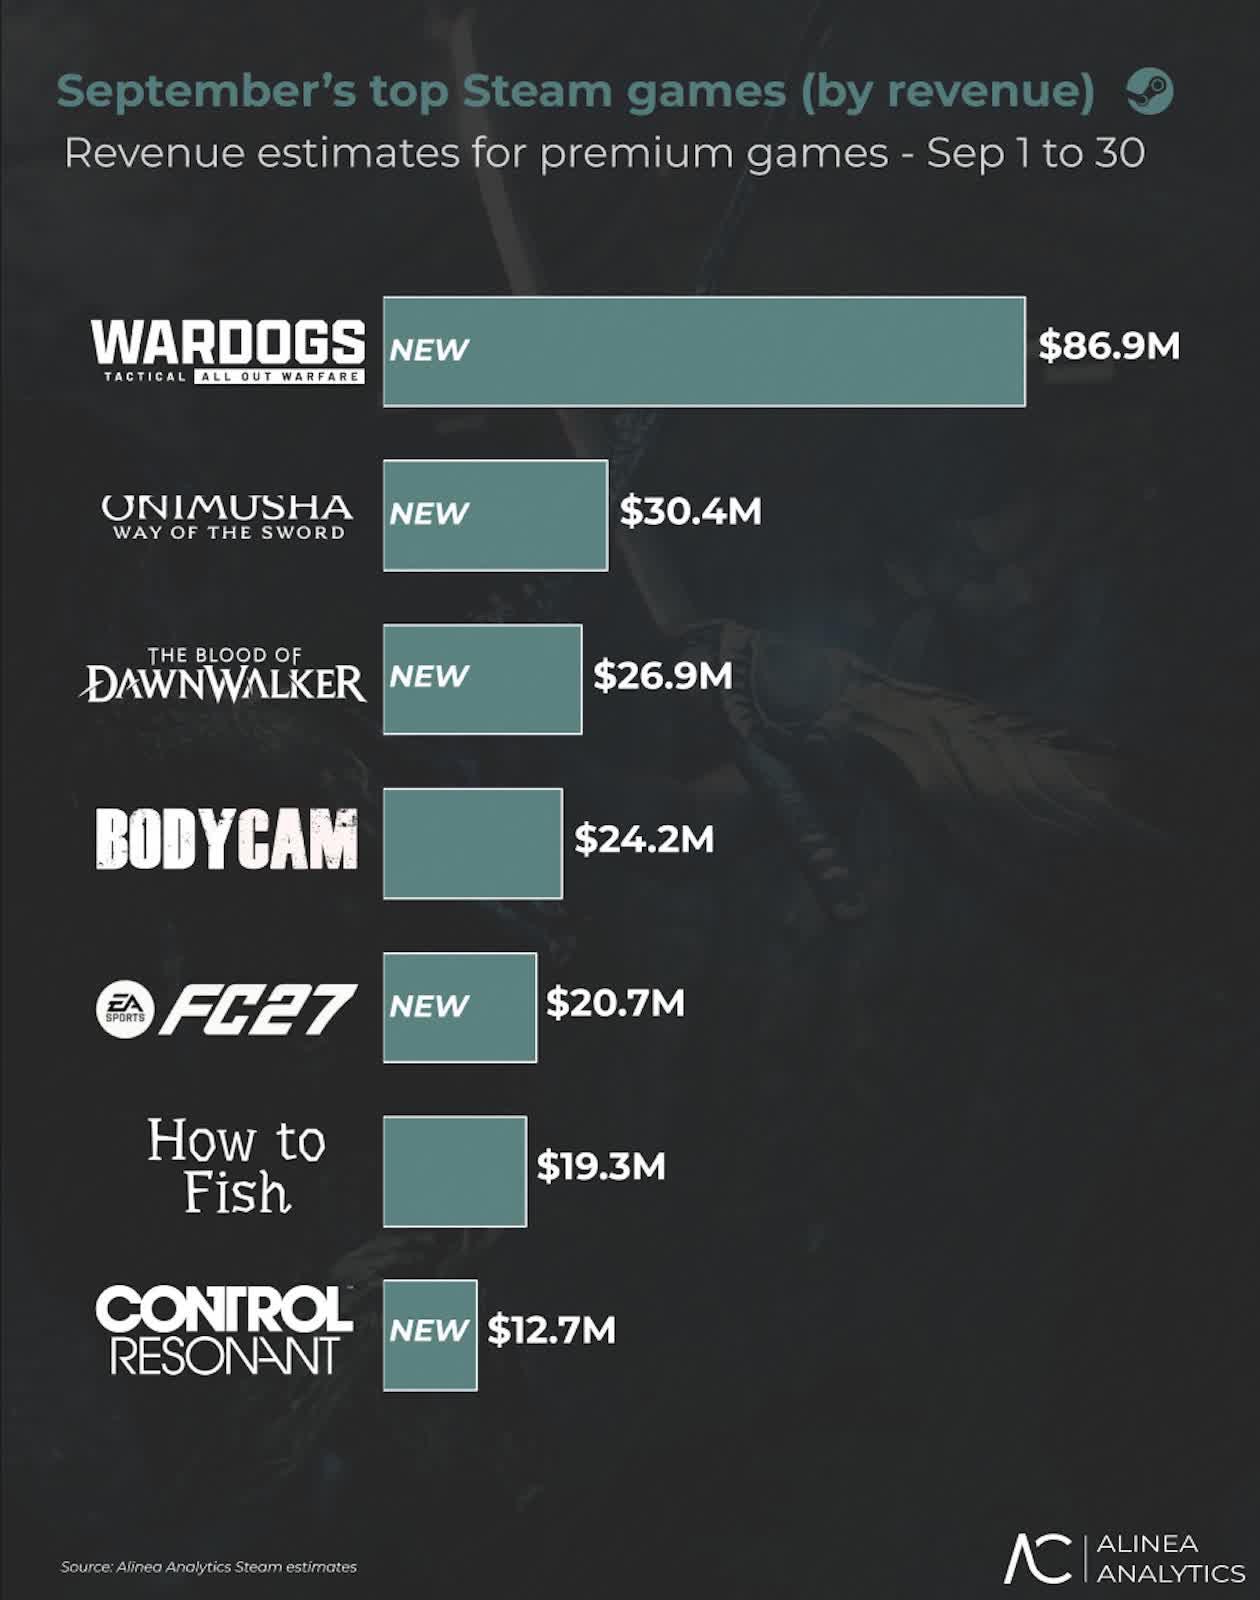
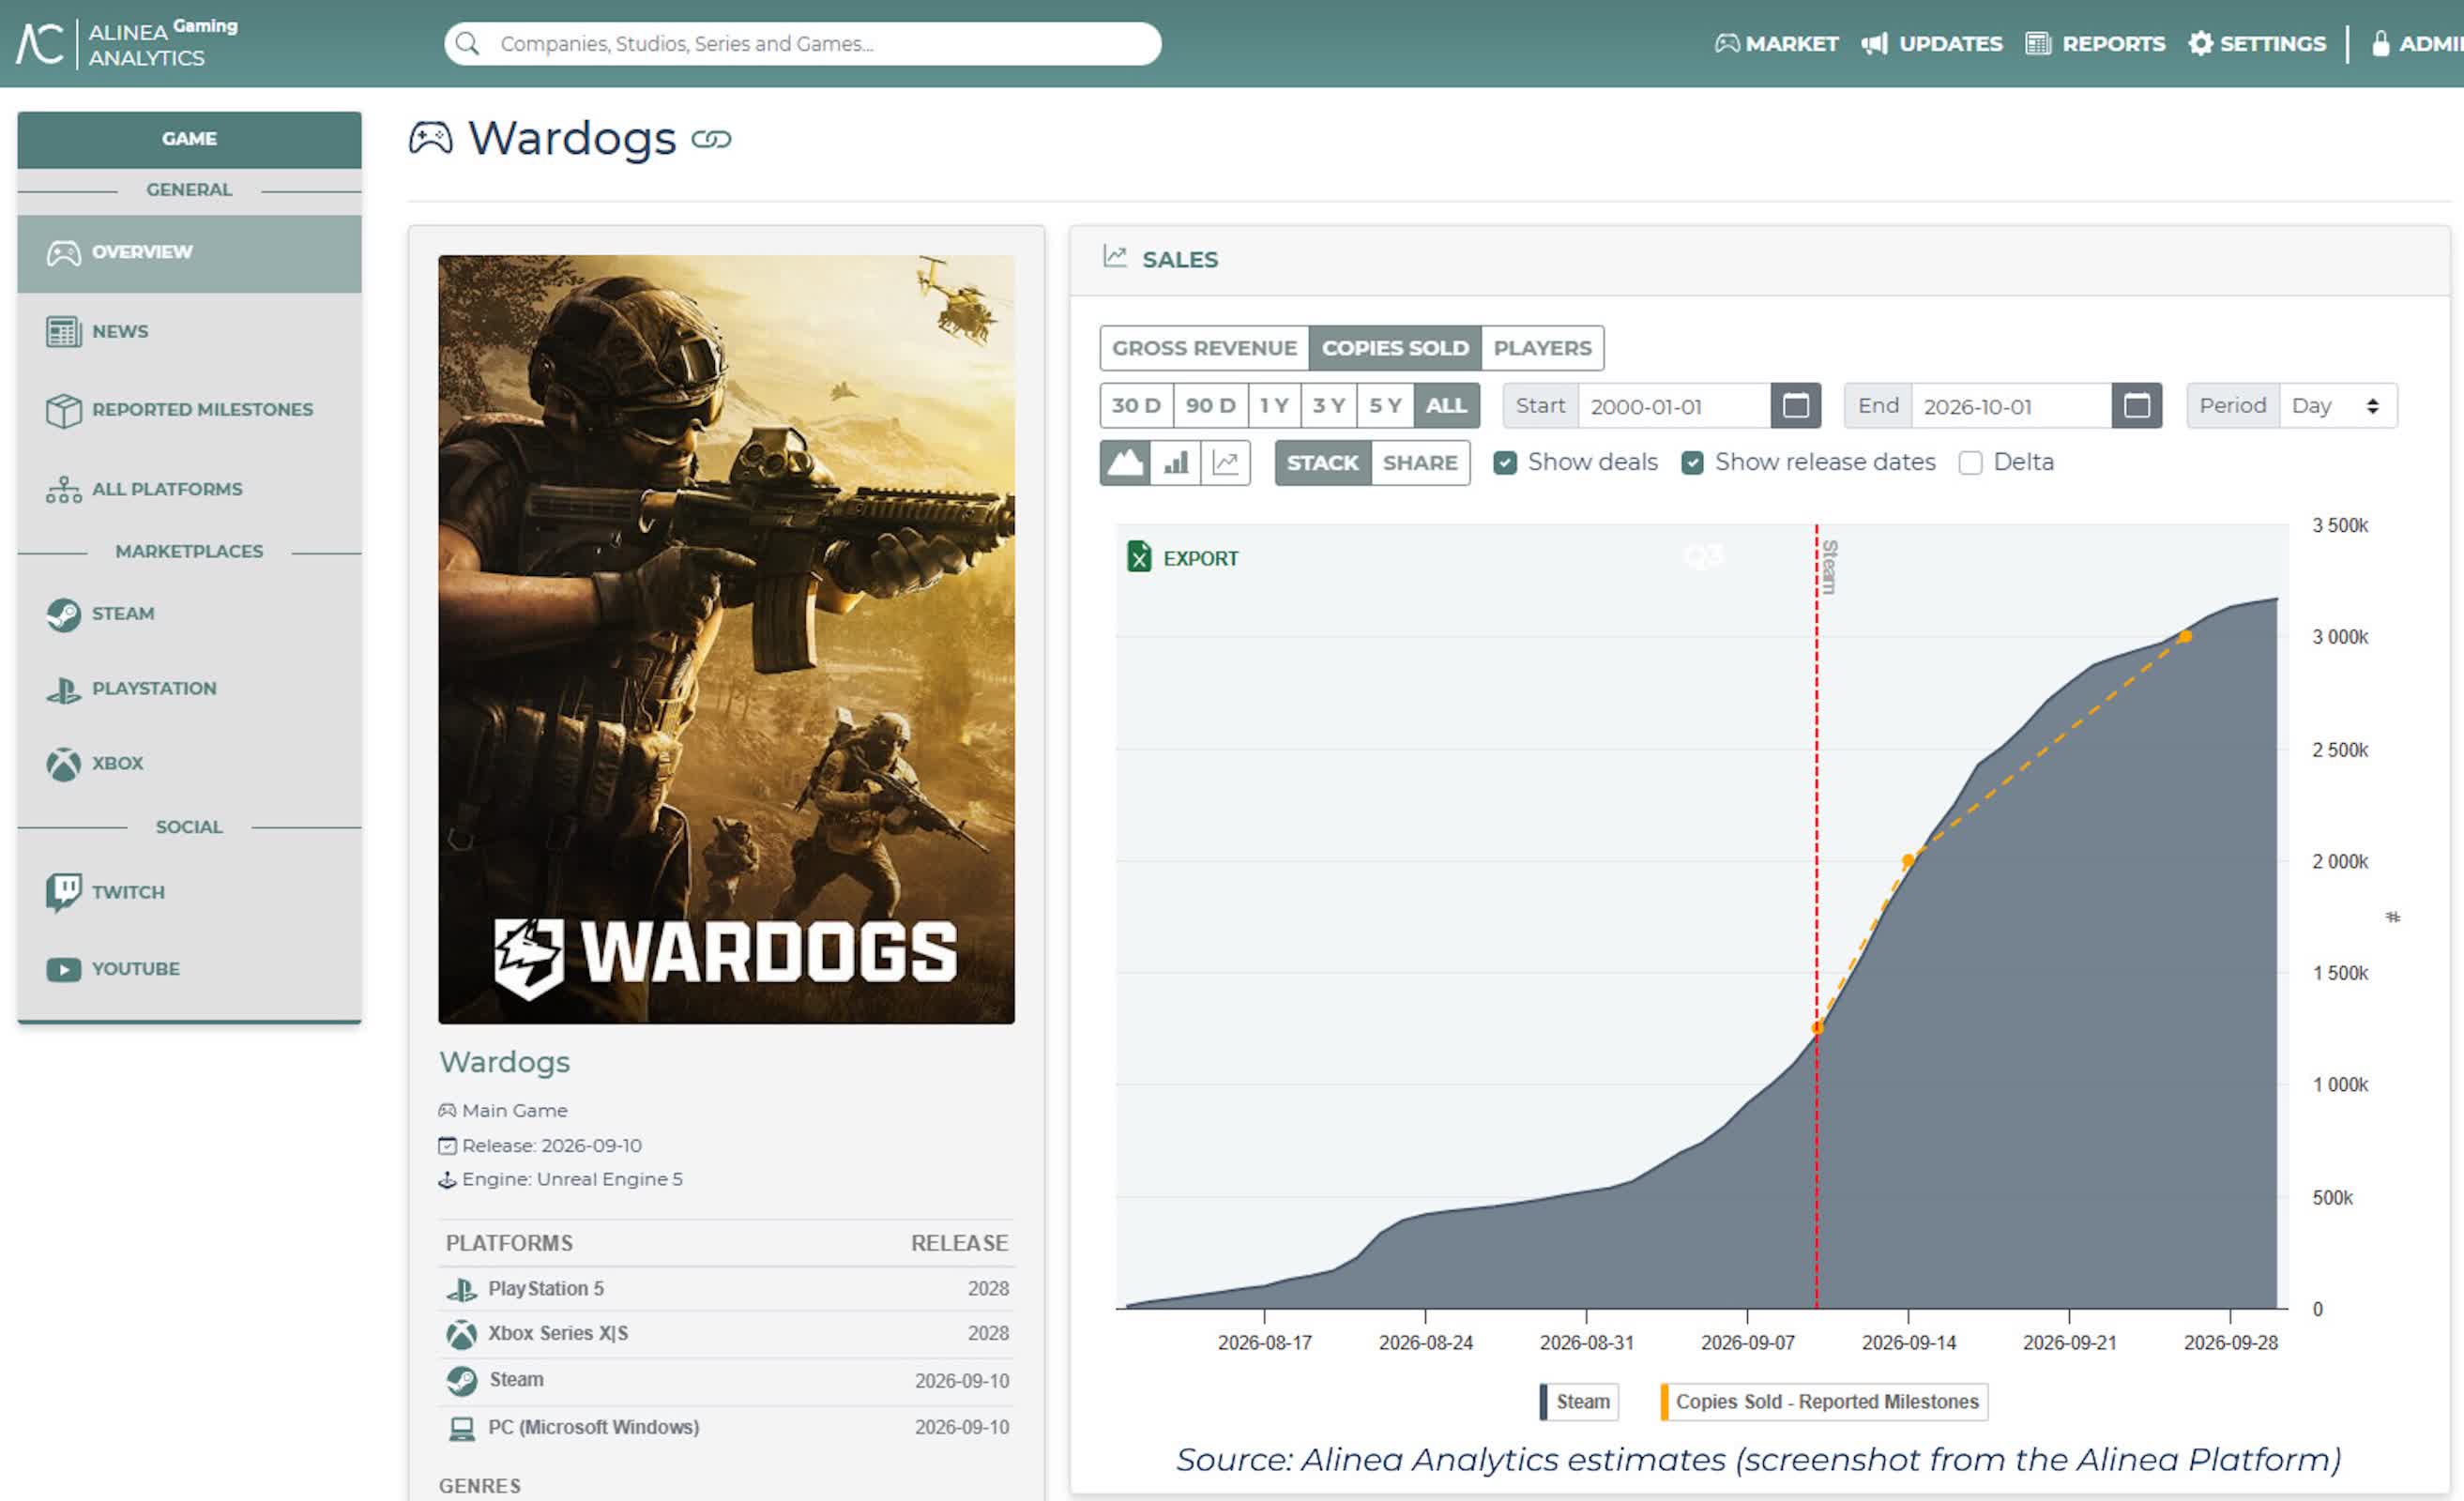
Paid games accounted for several of the month’s biggest individual performances. PvP shooter Wardogs brought in an estimated $86.9 million in the roughly three weeks after it entered Early Access on September 10. Onimusha: Way of the Sword generated $30.4 million during the month, and The Blood of Dawnwalker added $26.9 million.
EA Sports FC 27 contributed another $20.7 million from Steam copies, though most of its sales were on consoles.
Wardogs’ Early Access performance is notable because it shows how large a role the model now plays on Steam. Developers can release a game before it’s finished, collect revenue early and use player feedback to shape updates. For multiplayer games, that can also help build a community before a full launch.

Tech & AI1 minute ago
Human-Written Content Flagged as AI? What to Do Next

Gaming8 minutes ago
No Video Games Headlines Today: Our Source Material Was Actually About the Avatar-Endgame Box Office Battle

Tech & AI1 hour ago
ChatGPT is taking ads into image generation, and your conversations could decide what you see


-
 Fashion2 days ago
Weekend Open Thread: Veronica Beard
-
Business & Hustles7 days ago
Perpetua Resources at Mining Forum Americas 2026: shift to construction
-
Business & Hustles7 days ago
Greatland Resources at Mining Forum Americas 2026: cash-rich growth push
-
 Tech & AI5 days ago
Figure F.02 Robots Meet Molten Steel as Arnold Schwarzenegger Watches in Finland
-
 Tech & AI6 days ago
Alternatives to Animal Testing Are Finally Taking Off
-
 Business & Hustles6 days ago
OpenAI rebrands AI agents as ‘dots’ amid security fears
-
 Business & Hustles6 days ago
Develop sets $458 million growth capital budget
-
 Business & Hustles6 days ago
UK chancellor uses bitcoin to mock Nigel Farage
-
 Business & Hustles6 days ago
Market veterans favour value plays over crowded, expensive themes
-
 Tech & AI7 days ago
These Extremists Are Running for Election in November
-
 Tech & AI3 days ago
Fireflies.ai Launches Fireflies Talk for Free, Unlimited Voice Dictation
-
 Business & Hustles7 days ago
Accountancy firm Hazlewoods move to larger offices in Cardiff to support expansion
-
 Tech & AI7 days ago
Jet Megatextures Demo For ESP32-S3
-
Business & Hustles6 days ago
Dave & Buster’s interim CFO Cory Hatton buys $25,999 in stock
-
 Tech & AI3 days ago
Sony’s new PS5 Pro lottery requires 60 hours of playtime just to apply
-
 Tech & AI7 days ago
SpaceX’s Latest Starship Mission Reached Low-Earth Orbit
-
 Tech & AI5 days ago
OpenAI Pulls Plug on New AI Model as Industry’s Safety Cracks Widen
-
 Crypto4 days ago
OpenPayd’s MiCA Approval Signals Europe’s Stablecoin Infrastructure Is Going Mainstream
-
 Crypto4 days ago
NEAR Intents hacked days after freezing stolen Bitget funds
-
 Crypto7 days ago
Strategy buys 1,665 BTC and repurchases $152M STRC
You must be logged in to post a comment Login