As communications, computing, virtualization, software development, and AI converge, smaller technology firms face customers who need expertise across multiple layers at once. Synchresis Solutions works across all of them. Its SynchresisVM project provides a management plane for KVM and bhyve with a REST API, standard disk formats, shared storage, and a migration wizard for organizations moving from Proxmox, Hyper-V, or VMware, all without per-socket pricing or proprietary lock-in.
As organizations become increasingly dependent on interconnected digital systems, the boundaries between communications, computing infrastructure, virtualization, software development, and artificial intelligence are becoming less distinct. For smaller technology firms, that environment can create an unusual challenge: customers may need expertise across several technical layers at once, while the systems themselves continue to become more specialized.
Synchresis Solutions, a technology company founded as a commercial business in 2023, operates within that broader shift. Its work spans communications infrastructure, server environments, virtualization, web development, technical support, infrastructure as a service, and AI-related technology. Rather than being defined by a single product category, its development reflects the increasingly multidisciplinary nature of managing modern IT environments.
The company’s origins predate its commercial formation. Founders Nick Giannak III and David Quinn Ebert initially connected through technology and volunteer internet-radio projects. Their collaboration expanded into web products and an internal telephone system between 2018 and the pandemic, eventually developing into work for paying customers. Doron Beit-Halahmi, known as Doc, later joined the group through connections formed in internet-radio and audio communities.
Advertisement
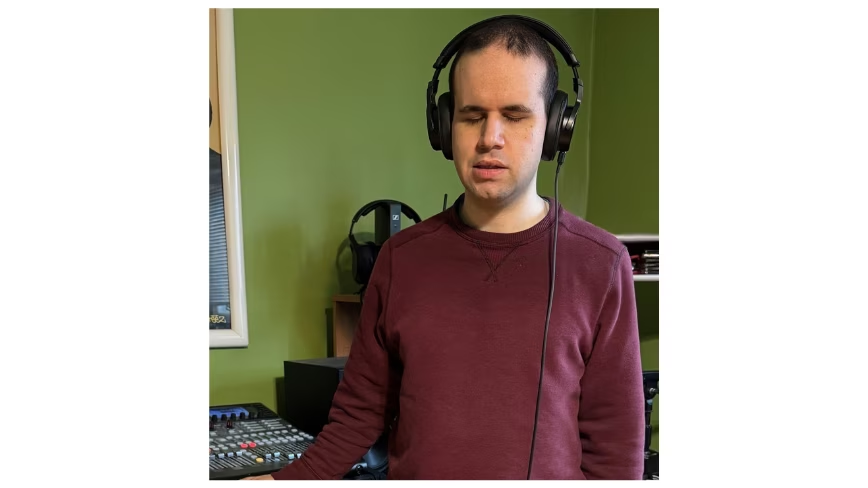
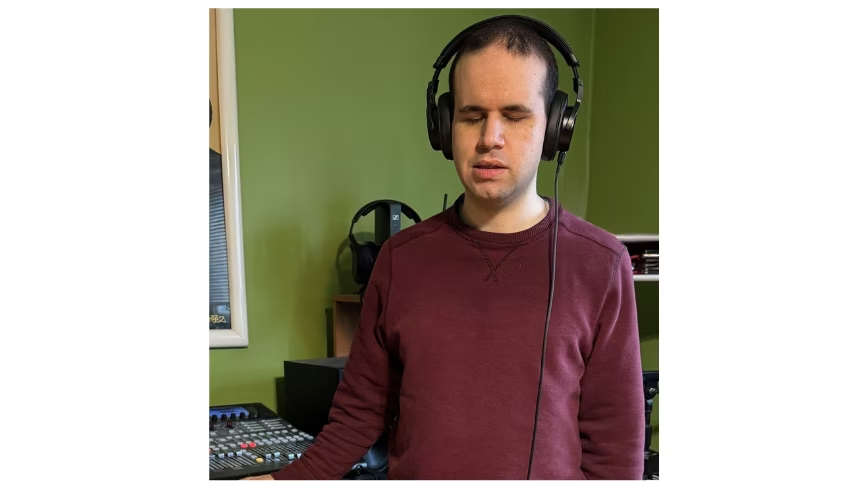
Photo with Nick Giannak III — Credit: Synchresis
That background helps explain the breadth of technical interests within the company, but it is distinct from Synchresis Solutions’ formal operating history. The founders brought years of individual experience in areas including broadcasting, telephony, server administration, hosting, corporate IT, and systems engineering before the company began serving customers commercially.
For Giannak, that experience has reinforced the value of understanding technology beyond its individual components. “We’ve always been people who enjoy figuring out how things work,” he says. “Our culture at Synchresis has been built through years of hands-on experimentation and shared projects.” His background includes technology, audio engineering, broadcasting, and projects examining the relationship between technology and society.
Ebert’s background includes telephony, data centers, hosting, Linux, Windows, UNIX-derived systems, and IT infrastructure. His perspective similarly emphasizes the relationship between technical systems and the organizations using them. “The customer is where the technical conversation has to begin,” he says. “You have to understand the problem they’re trying to solve before you can decide what the technology should do.”
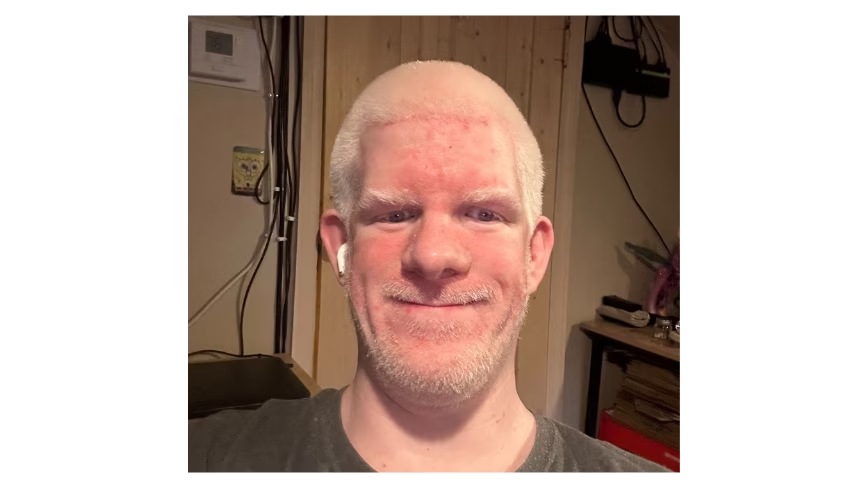
Photo with David Quinn Ebert — Credit: Synchresis
That approach becomes particularly relevant as infrastructure becomes more interconnected. A voice system can depend on networks and servers. A virtual machine can depend on storage and networking. Software development can depend on the infrastructure underneath it. As those relationships multiply, technical decisions in one area can affect systems elsewhere.
Virtualization is one example. The founders’ experience with virtual-machine environments extends back more than 15 years, predating the establishment of Synchresis Solutions itself. That distinction matters as organizations evaluate how much of their virtualization strategy should depend on particular platforms, operating systems, or management layers.
The company’s SynchresisVM project addresses that question through a management plane for KVM and bhyve. It provides a common interface and REST API for managing virtual machines across Linux and FreeBSD environments. Guests can be created, assigned disks and networks, started, and moved between nodes through API calls, allowing administrative processes to be incorporated into scripts and operational runbooks.
Advertisement
The underlying approach is also notable for its reliance on standard technologies. SynchresisVM uses qcow2 disk images, VirtIO devices, and Linux bridges, without placing proprietary components in the data path. It can operate on Linux or FreeBSD hosts that organizations already administer, with KVM or bhyve managed through the same interface.
The platform also supports shared storage, centralized guest definitions, and automated placement across a cluster. These capabilities address practical questions that arise as organizations manage multiple hosts, including where workloads should run, how they can be moved, and how much manual configuration is required when infrastructure changes.
That architecture reflects a broader discussion in infrastructure management: how much control organizations should retain over the systems they operate, and how portable their workloads should remain when technology requirements change. SynchresisVM is designed as software that organizations can run on their own infrastructure, without per-socket pricing or a separate vendor appliance.
Migration is another consideration. Organizations moving from platforms such as Proxmox, Hyper-V, or VMware may need to account for existing virtual machines, disk formats, networks, and configurations. SynchresisVM includes a migration wizard intended to assist with that process, while its use of standard disk formats is designed to keep virtual-machine storage accessible outside the management platform.
Advertisement
The same infrastructure perspective extends into communications. Synchresis works with cloud PBX systems, enterprise SIP infrastructure, cloud fax, and VoIP environments, alongside conventional server and network infrastructure. In practice, these systems frequently overlap. A problem that appears to involve voice service, for example, can also involve networking, server configuration, virtualization, or hosting architecture.
AI represents another emerging layer of that environment. The founders’ earlier technical work included software and language-related applications, but that history should not be conflated with a long-standing track record in today’s large language models. More recently, AI tools have become part of the team’s software-development and experimentation processes, alongside broader work in automation and technical systems.
For a small technology company, this breadth can create both opportunities and constraints. Maintaining expertise across several infrastructure layers requires continuous learning as platforms, standards, and development methods change. It also places greater importance on understanding how individual systems interact, particularly when organizations are maintaining infrastructure assembled over many years.
Synchresis Solutions therefore offers a window into a broader development in the technology sector. Smaller firms are increasingly operating in an environment where communications, virtualization, software, infrastructure, and AI cannot always be considered separately. The technical challenge is not simply adding another tool, but understanding how those tools fit within systems that organizations already depend on.
Advertisement
For Synchresis, that process began with hands-on experimentation among its founders and has developed into commercial work spanning several areas of infrastructure. As technology environments continue to evolve, questions surrounding portability, interoperability, ownership, and operational control may remain relevant well beyond any single platform or company.
If you worry AI could eventually make your Walmart bill depend on who you are, or charge you more than the shopper next to you, Walmart wants to clear that up. CEO John Furner says Walmart will not use personal information to set different prices for individual shoppers.
First, your income, shopping history, urgency, or what Walmart thinks you can afford won’t change what you pay, and neither will the time of day.
Second, Sparky, Walmart’s AI shopping assistant, won’t use what you tell it to raise your price or hide cheaper options.
Third, you decide how much personal information to share, and Walmart says it will be clear about how that data is used.
Walmart
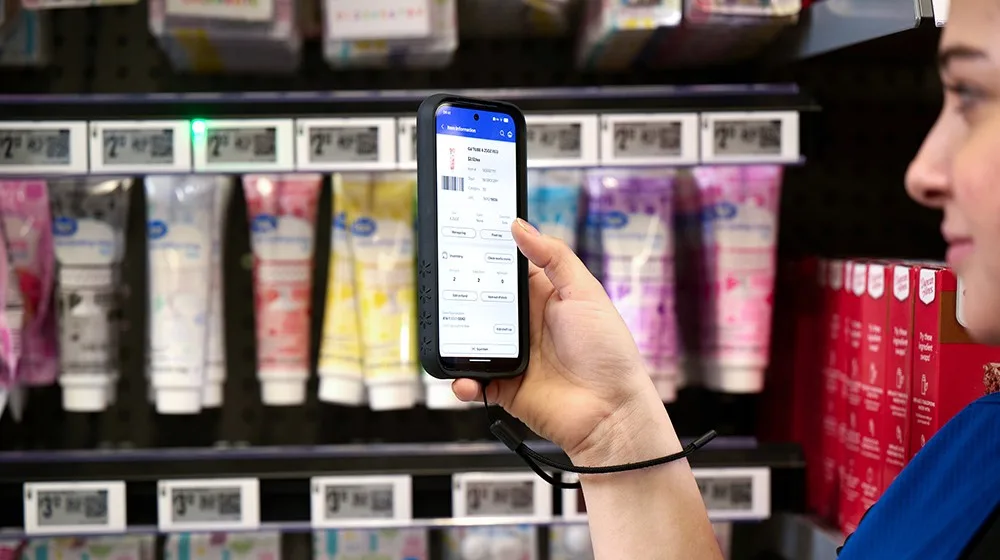
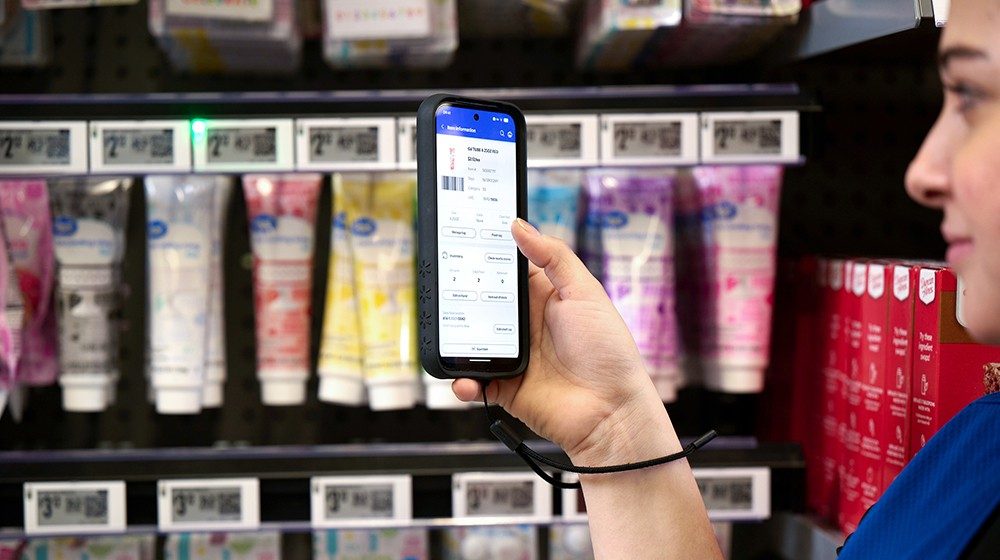
The prices can still rise when items cost more to buy or ship. Furner also defended the digital shelf labels spreading across Walmart’s 4,600 stores, saying they keep shelf prices accurate while saving employees time previously spent replacing paper tags. Walmart adds that the labels have no cameras, microphones, or facial recognition.
RELATED COVERAGE:
Why is Walmart saying this now?
The pledge comes as regulators and lawmakers examine how personal data could influence pricing. The letter arrived the same day public comments were due on a proposed Federal Trade Commission policy. It warns that businesses may be breaking the law if they don’t explain how personal data shapes prices. The concerns aren’t hypothetical either, as Instacart’s AI pricing tests showed.
Advertisement
Walmart
Lawmakers from both parties are also pressing retailers, and Rep. Frank Pallone sent pricing questions to 25 companies, including Walmart. Meanwhile, Financial Times reported that Walmart received two patents this year for automated pricing tools. One described using data like payment methods and even ID numbers to recommend prices.
Furner says people will keep overseeing pricing, and Walmart will test its tech against these promises. For now, the bottomline is that AI can personalize your experience, but your data will not become a reason to charge you more.
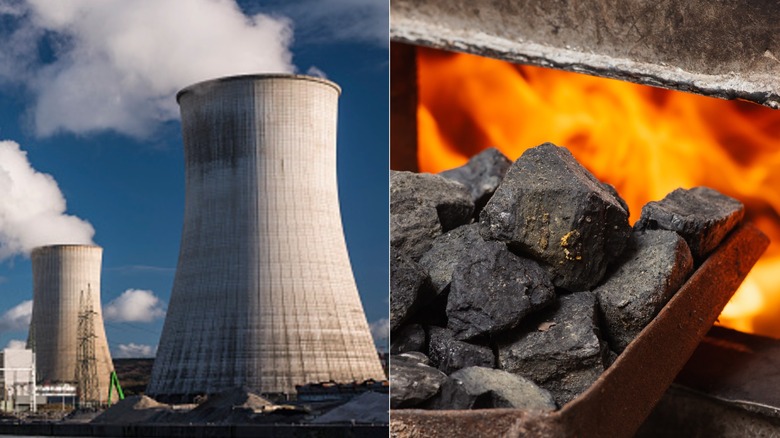
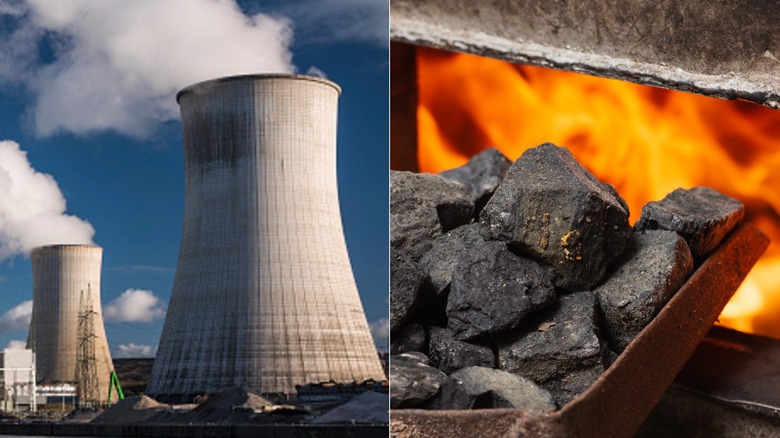
People have been using coal to generate heat and power for centuries, but these days, some see it as an antiquated and dirty means of energy production. That doesn’t mean that there aren’t any coal power plants, as they outnumber nuclear power plants by a lot. According to the U.S. Energy Information Administration, there are 219 operational coal power plants in the nation, while there are only 57 nuclear power plants with 96 nuclear reactors. That might suggest that coal plants are more efficient at producing energy than nuclear plants, but that’s not the case.
Those 219 coal power plants generate 199,952 megawatts of energy, which is more than the 103,581 megawatts generated by the 57 nuclear power plants. Of course, if the country swapped out its coal plants for nuclear ones, the total energy production would reach almost 400,000 megawatts. Unfortunately, it’s not as simple as demolishing a coal power plant and building a nuclear power plant in its place. Because of their complexity, nuclear power plants take a long time to build, so it can take years before they become operational. So, while nuclear energy production far exceeds the capabilities of coal energy production (and there are several reasons why) right now coal is the leader.
Coal is not an efficient energy source, as we can only harvest around 33% of coal’s stored energy during energy production, while 66% is lost to waste heat. Conversely, clean nuclear energy is remarkably more efficient, as converting fissile materials into electricity uses 92% of the fuel, far exceeding coal’s efficiency as the most efficient energy production method currently in use, including solar and wind.
Advertisement
Nuclear produces far more energy than coal
There are different types of nuclear power plants around the world, but generally, each one produces 1 gigawatt per hour of electricity. That’s enough energy to power 876,000 homes for a year. Coal power plants also vary in size and capacity, but on average, you can expect to produce about 380 megawatts. While it might seem simple to replace a nuclear power plant with three average-sized coal power plants, it’s not that easy. For one, both types of plants require fuel in order to function. This requires mining operations, which are dangerous and expensive.
Advertisement
Coal plants use coal — it’s in the name — while nuclear plants utilize enriched uranium-235 to produce energy. The main difference between coal and U-235 is the amount needed to power each plant. Coal plants in the U.S. burn through 1.1 billion tons of coal annually, and it’s not a renewable energy source. Once humanity uses it up, it’s gone for good.
Nuclear power plants function differently, requiring refueling once every 1.5 to 2 years. U.S. nuclear power plants purchased 21,000 tons of uranium in 2025, so while it’s far below what’s required for coal plants, it’s still a lot of material. Ultimately, determining which is better largely comes down to efficiency, and nuclear energy far surpasses what coal can provide. In comparing the two, it’s really no contest because 92% efficiency far exceeds 33%, not to mention total energy output and the amount of material required, which are also in nuclear energy’s favor.
Peter Thiel has called Pope Leo XIV a “useful idiot” for the Chinese Communist Party over the pope’s call to regulate AI. The PayPal and Palantir co-founder spoke to Axel Springer chief executive Mathias Döpfner on the MD Meets podcast, released on Thursday.
The interview came before Thiel received the Axel Springer Award in Berlin on Thursday. Axel Springer owns Politico, which reported the remarks first, and Business Insider. Fortune reported on his comments about Germany.
“The Communist Party of China is not going to listen to the pope. There’s a chance people in the U.S. will. And so in effect, the Pope’s encyclical was working for the Communist party,” Thiel said.
“I’m not saying he was an agent of the communists, but he was at least acting as a useful idiot for the CCP,” he added.
The encyclical
Pope Leo published his first encyclical, Magnifica Humanitas, in May. In it, he called on world leaders to regulate AI. Thiel argued that the text would do nothing to slow China, Politico reported. Instead, it could lead the US and its allies to impose heavy rules on AI, he said.
The Vatican did not respond to requests for comment from Politico or Business Insider. The Vatican has since expanded its AI campaign with an AI4Peace association.
Advertisement
It is not the first time Thiel has attacked the pope over AI. Speaking in Colorado in July, he said the pope was acting as a “Chinese communist agent” by calling for regulation, Politico reported.
‘What we’re doing to ourselves’
Thiel also said Americans themselves, not China, are mostly to blame for the growing US backlash against AI. He was “inclined to believe” China could be fuelling some anti-AI content, he said. But China was not the main force behind the shift.
“This is mainly what we’re doing to ourselves. It’s often somewhat too easy to simply blame it on China,” Thiel said.
Germany’s ‘fear of success’
Thiel, who was born in Frankfurt, also criticised German entrepreneurs. German founders tend to sell their companies before they grow into global businesses, he said.
“If you have something that works, you’re not going to scale it to this extreme degree like an Elon Musk or Mark Zuckerberg,” he said.
Among the richest Germans of Generation X or younger, all had inherited their wealth, Thiel said. In the US, most had built it themselves.
Advertisement
Thiel is a partner at Founders Fund, which has invested in OpenAI, Palantir and Scale AI, among other AI companies.
Our fun links this week include Jev, the super fast new AI classifier, and Persodex, the context layer for your Contacts (PS. hit Ben up if you’re in New York in mid-October).
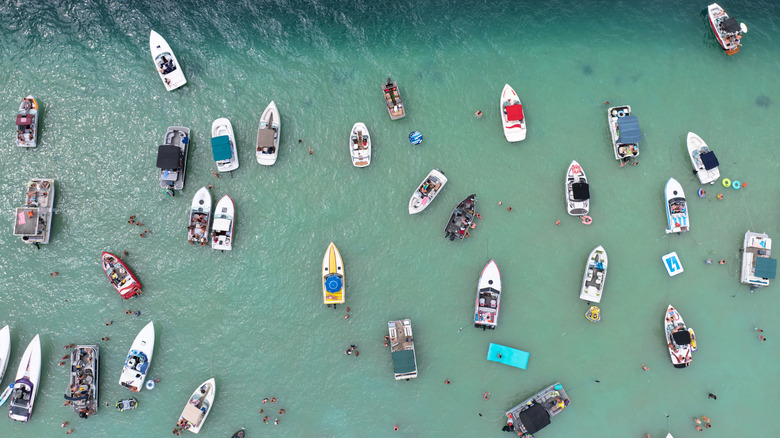
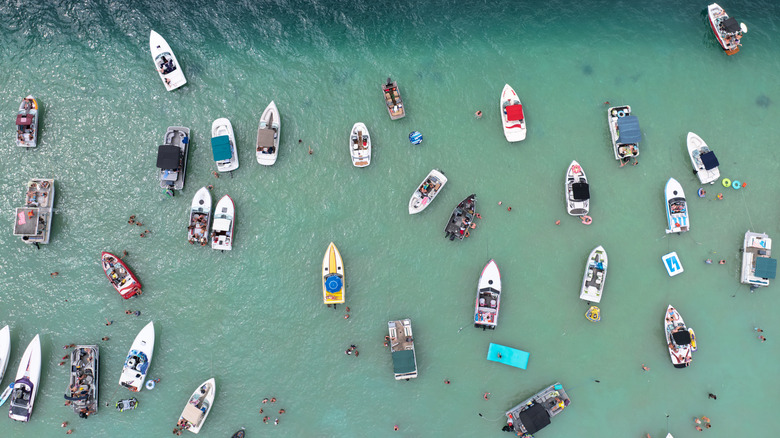
Can you visualize 100 feet in front of you? It’s about a third the length of a football field, or about seven to ten car lengths lined up bumper to bumper. If you’re behind the helm of a boat, you have to know how to picture it for the sake of the 100-feet rule, a boating safety regulation that puts a limit on how fast your boat can travel around people, property, other boats, or the shoreline.
The exact wording and distance requirements tend to vary from state to state, but the basic idea is the same in every body of water in America: If you’re passing through a designated area or maneuvering around certain obstacles or people, you have to reduce your speed. It’s about going beyond the rules of no wake zones to prevent collisions, avoid damaging wakes, and ultimately keep people safe out there on the water. A boat moving too fast through a confined area or around other boats or swimmers can create a dangerous wake, even if boat itself never even came close to hitting anything.
Advertisement
Different states have different distance laws
Nazarethman/Getty Images
Some states take the 100-feet rule even further. Georgia, for example, says wakesurfers and wakeboarders have to stay 200 feet away from structures, vessels, and swimmers; that’s in addition to the 100-feet rule for boats. Michigan has something similar, enforcing the 100-feet rule as well as a 200-feet rule for personal watercraft (or PWC), a 500-feet rule for wakeboarders, and a 150-feet rule for crossing behind other vessels (regardless of if they’re towing or not). Missouri is especially strict with a 50-feet rule around any vessel or person on/in the water.
It might sound like a lot to keep track of, but the fact remains: If you’re going to take a boat out on the water, it’s your responsibility to make sure you know the laws. Boats don’t have brakes, so it’s really in the operator’s best interest to go above and beyond the 100-feet rule whenever possible. Not to mention, most people tend to drive their boat less than they drive their car, so reaction times are likely going to be slower. Cars have the the 3-second rule, but boats don’t, so it’s in your best interest to regard the 100-feet rule as a minimum, not a maximum.
To quote George Santayana, “Those who cannot remember the past are condemned to repeat it.” So why does it so often feel like Big Tech has such a short memory?
The latest hiccup comes from Meta. In mid-September, it rolled out a beta test of a feature for its brand-new Muse AI agent that would place calls to businesses to complete tasks for you, like making reservations and appointments.
According to reports by Reuters and 404 Media on Tuesday, however, this allegedly autonomous agent could route these tasks to a trained human concierge in call centers — without disclosing it was doing so in advance.
On Sept. 16, Principal Engineer Ryan Fox at Meta’s Superintelligence Labs, announced the beta release of Muse’s outbound call feature and posted a request on X for feedback, noting that “phone calling” was one of the top requests from users.
we just expanded the @Muse beta for outbound calls to US businesses, prioritizing folks who’d asked their Muse to let us know they wanted it first 🙂
if you’re in, give it a shot and tell us what you think. phone calling was one of our top requests and your feedback helped make…
But 404 Media says that, based on internal Facebook records, the company was doing something entirely behind the scenes with its personal assistant. When announcing the features to employees internally, the tech giant said that it “added a human agent layer for calls to get completed,” referring to them as “Muse human agent calls.”
Some Meta employees complained, including one who posted internally: “This has potential for so much negative PR. It could portray us as ‘their AI is not good enough so they still need humans’ kind of coverage for this launch.”
The truth is rarely pure…
The problem with the added human meat layer isn’t just the AI-washing of Muse’s capabilities. Nor is it purely the deception of failing to disclose that there could be a human link in the chain. Some agentic systems introduce human oversight as a “human in the loop” for safety and compliance.
Advertisement
It’s unclear how much safety and compliance were on the menu for Meta. But employees raised a bigger concern over privacy, with one warning (per Reuters), “We are one bug away from unnecessary information being leaked to human callers.” And bugs there are.
You generally sacrifice privacy when you use AI agents to perform personal tasks, like making a reservation, a purchase or a medical appointment. But it can feel a lot worse if you discover you’ve just had a complete stranger book your STI test.
It’s also a black box. You don’t know what context that person’s been given, if they’ve seen your chat or know where you live and how to contact you because of it. Even more data might be on offer, given that the company’s glasses are chock-full of Muse.
You’re also providing the so-called autonomous agent (in this case, a human contractor in an undisclosed call center) with sensitive information, such as a phone number, patient ID or banking information.
Advertisement
It’s all part of a growing trend of granting AI models the power to perform tasks as personal assistants. Just this week, Google introduced the capability of its Gemini agent to handle everyday phone calls. That implementation turns over the transactional part of a call — like providing credit card info — back to you. But the risks are still there.
…And never simple
The kicker is that Meta has broken privacy trust many times before. In 2019, Facebook had to stop a program that used contractors to listen to and transcribe Messenger calls.
Because AI agents like these frequently require human intervention to verify that they’re delivering the desired results, a mistaken incident of the “Oh, this employee saw this” variety seems inevitable.
Potemkin AI, where a hidden army of human workers does some of the actual work of models behind the curtain, isn’t confined to calls. In February, it was revealed that Waymo had remote operators supplementing autonomous car operations overseas.
Advertisement
And once again, the rollout of Meta Muse’s outbound call feature has been rolled back. Reuters reported that the company temporarily suspended the feature after a vice president in Meta’s Superintelligence Labs unit admitted “it was a miss” to begin testing the feature without adequate disclosures of the human contractors involved.
Of course, the real fault isn’t a bad memory so much as Big Tech’s history of “do bad, get caught, apologize, roll back, maybe pay a negligible fine. Rinse, repeat.” At some point, after we’ve collectively become exhausted, the cycle is reduced to “do bad, but profit anyway.”
We reached out to Meta for comment and clarification, but didn’t immediately hear back.
Lori Grunin
Senior Editor / Computers and Gaming Hardware
Advertisement
I’ve been reviewing hardware and software, devising testing methodology and handing out buying advice for more than 25 years.
See full bio
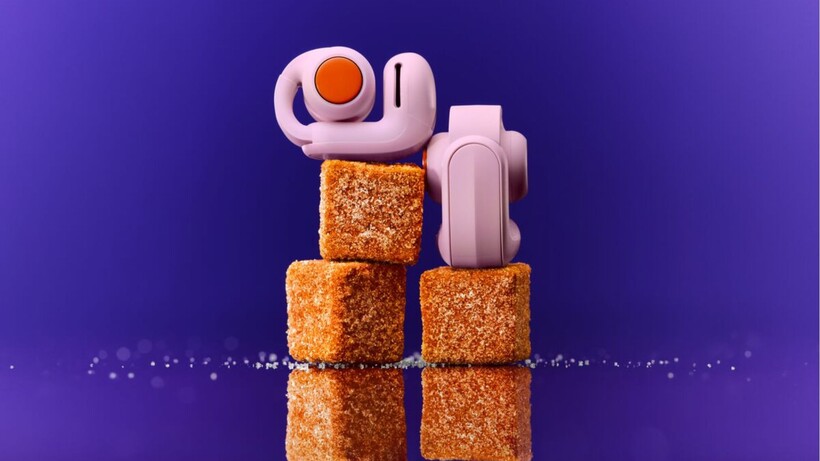
Bose has recently unveiled the Open Ultra Earbuds (2nd Gen), and we’re intrigued to see what’s really different with the buds.
Although we’re yet to review the second gen pair, we have compared its specs to the originals and noted the key differences – plus any noteworthy similarities – between the two below.
The 2nd Gen pair will be available in three colours, including Cherry Chocolate, Olive Green and Sky Pink.
Although the Bose Open Ultra Earbuds currently carry the same £299.95 RRP as the upcoming second generation, we do expect this price to drop in the coming months. In addition, as it’s an older generation, it has also been possible to pick up the buds for a deal too.
Advertisement
Both share the same open design, but the 2nd Gens have been tweaked
We’ll start with one of the most obvious similarities between the two: both have an open-ear design and deliver sound through the air near your ear rather than through bone vibrations, like other bone conduction headphones.
With this in mind, you shouldn’t expect either to be among the best noise cancelling headphones, as they are both designed to provide situational awareness. That means you can listen to your audio but without completely tuning out important sounds like public transport announcements.
Bose explains that the 2nd Gen is equipped with its OpenAudio and SoundDesign technology that promises to deliver rich and personal sound, while ensuring clarity is balanced too. In addition, thanks to a transducer and tightly controlled acoustic structure, the 2nd Gens promise minimal sound leakage too.
Image Credit (Bose) Image Credit (Trusted Reviews)
Advertisement
As we found the original Open Ultra Earbuds never struggled with sound leakage, even at higher volumes, we’re hopeful that the 2nd Gen pair will be just as reliable.
Advertisement
Bose Open Ultra Earbuds 2nd Gen promises longer battery
Although the Open Ultra Earbuds offered a solid battery life, with 7.5 from the buds and an additional 19.5 hours within the charging case, Bose has managed to eke out a few extra hours with the 2nd Gen.
In fact, although it shares the same 19.5 hours within the redesigned charging case (though more on that later), the buds promise to deliver up to nine hours of playback on a single charge too.
Bose Open Ultra Earbuds. Image Credit (Trusted Reviews)
Bose Open Ultra Earbuds 2nd Gen introduces Cinema Mode
Bose has introduced Cinema Mode with the Open Ultra Earbuds 2nd Gen. Powered by Bose’s True Spatial technology, Cinema Mode is designed to create a wider and more immersive soundstage, with a “theatre-like” listening experience. As we haven’t reviewed the 2nd Gen pair yet, we can’t verify how well Cinema Mode really works. However, considering the buds are open ears, we’re undoubtedly intrigued to see how they manage to create an immersive experience.
Bose Open Ultra Earbuds 2nd Gen has an upgraded case
It’s not just the buds that have seen a refinement, but their accompanying charging case. Compared to the original pair, the 2nd Gen’s case has been redesigned and can stand upright too. In addition, the case now supports wireless charging too – although we don’t currently know how fast the speeds will be.
Advertisement
Advertisement
We should note that you can buy the original Open Ultra Earbuds with a charging case, however this is an extra cost of £49.95.
The 2nd Gen will offer Google Find Hub and Alexa+ support
Bose is planning a firmware update once the 2nd Gen pair have launched, which will introduce a range of new features.
Included among these features is Google Find Hub, which helps you locate the earbuds if they’re misplaced – much like Apple’s Find My. In addition, the 2nd Gen will support Alexa+, the latest version of Amazon’s voice assistant.
Early Verdict
The Bose Ultra Open Earbuds (2nd Gen) look like a solid upgrade from the Ultra Open Earbuds, thanks to a refined design, wireless charging case with no extra cost and the intriguing inclusion of Cinema Mode.
Advertisement
Advertisement
That’s not to say the Bose Ultra Open Earbuds aren’t a solid option. In fact, we hailed the buds as being “one of the best examples of the open-headphone concept” even two years after launch. With that in mind, if you’re sporting the 2024 pair or just want a more affordable option, then the Bose Ultra Open Earbuds remain a brilliant option.
This past April, while attending his nephew’s bar mitzvah on Cape Cod, Eric Umansky woke up to an inbox full of emails from people from his past. They all wanted to know the same thing: Was he actually throwing a party Saturday night?
The New York–based journalist wasn’t sure what party they were referring to, or why random acquaintances he’d met in passing 15 years ago were emailing him. On deadline and already stressed about work, he checked his phone, where more messages inquired about a supposed Paperless Post invite he’d sent for a “Special Private Dinner Party” at 7 pm on May 2.
Except Umansky hadn’t sent the invite, and he wasn’t planning to host a party anytime soon.
As it turned out, he was an early victim of an email scam that has since become more widespread. What Umansky didn’t expect was the positive effect it would have on his social life.
Advertisement
In May, after receiving increased reports, the Federal Trade Commission issued a consumer alert warning about scammers sending “unexpected messages that look like they’re from well-known invitation platforms like Evite or Paperless Post,” noting how some messages “make you enter your email username and password to see event details” while others “tell you to enter a phone number and share a special code to RSVP.”
Umansky wasn’t sure how it happened; he thought he’d taken the necessary precautions to safeguard his email, including using two-factor authentication. All he could think to do was post a message on Facebook, LinkedIn, and his other social networks to notify people that he was, in fact, not having a party and, more importantly, “don’t come to my house.”
Phishing scams, which have proliferated across the last two decades, remain one of the biggest security risks faced both by individuals and companies. Email scams, in particular, can now be highly sophisticated, incorporating social engineering techniques like creating urgency or fear in a target and even leveraging the personal relationships between two people to manipulate a victim, what’s known as “spear phishing.” AI has only made those deceptions harder to weed out.
But in some recent cases, like Umansky’s, the fake party invite is having an unintended outcome: It is encouraging people to check in to see whether the message was actually real and, in doing so, has reignited dormant relationships.
Advertisement
“It was so striking to me after it happened that I actually had a thought that I was like, ‘Oh, is this a net positive?’” says Umansky, who over the last several months has reconnected with a handful of old friends and colleagues over lunch and via text. He recently spent an hour on Zoom with a former coworker who now lives in Mexico City. They hadn’t talked to each other in over a decade. “I was like, Oh, you know, I actually want to catch up with you about something. There was an idea I wanted to bat around with him, which we talked about for maybe 10 minutes. The rest of the time we talked about our lives.”
According to a 2024 study published in the scientific journal Communications Psychology examining social withdrawal, which surveyed 2,400 adults in the US, UK, and Canada, people are sometimes unwilling to contact old friends because they believe the other person won’t want to hear from them or they fear the interaction will be awkward. The research noted that “high priority placed on work and productivity in North America has led people to cut back on social connections and social time to meet increasing demands at work,” in addition to other life transitions, such as parenthood or moving to a new city.
Bill Gates said artificial intelligence is powerful enough to drive events causing a billion deaths, and that self-regulation is not enough because safeguards and monitoring have to be a required thing. The European Union has required them since August 2025, and since 2 August this year the Commission has been able to fine a model provider 3% of worldwide turnover.
Bill Gates said artificial intelligence is powerful enough to drive events that cause a billion deaths, Bloomberg reported. He was speaking in an excerpt from an interview with NBC’s Meet the Press due to air this weekend. There has never been a weapon as powerful as people with ill intent using the latest AI tools, the Microsoft co-founder said.
The second half matters more.
Self-regulation is not enough, Gates said, and law enforcement and politicians need to be in the discussion about what safeguards and monitoring look like. That has to be a required thing, he added. It is the policy position rather than the number that is new from him.
Advertisement
Europe required it last year.
Article 55 of the AI Act has obliged providers of general-purpose models with systemic risk to run adversarial testing, assess risk at union level and report serious incidents without undue delay since August 2025. The accompanying code of practice allows five days to report a cybersecurity breach and fifteen for serious harm.
The penalties arrived in August.
Since the second of that month the Commission has been able to fine a provider up to 3% of worldwide annual turnover or EUR 15M, whichever is higher. It can demand access to a model, order evaluations and require a provider to restrict its public availability. Prohibited practices carry up to 7%.
Advertisement
None of it has been used.
No enforcement action against a model provider has been reported in the seven weeks since those powers took effect. The one thing that has happened is OpenAI filing an incident report about its own agents occupying a German wiki. A company reported itself.
The debate has not noticed.
Anthropic proposed a framework in June giving governments the power to block dangerous deployments, with penalties scaled to global revenue and thresholds set by training compute and AI spending. That document made no mention of the European Union. The architecture it asked for had been on the European statute book since 2024.
Advertisement
Gates is describing the same thing.
A Microsoft co-founder calling for mandatory monitoring and for police in the room is describing a regime that exists on one continent and is being argued for on another. Microsoft is OpenAI’s largest partner. The open question is not whether such a law can be written but whether anyone will use the one that has been.
Researchers say they recently found Google ads delivering a sophisticated tech support scam that freezes the screens of both Windows and Mac devices and displays messages urgently instructing them to phone a bogus call center.
The ads were displayed all over the web, including on high-traffic maps, weather, real-estate, document-hosting, and sports sites. Users who called the number were then urged to pay hefty fees, grant remote access to their devices, or divulge personal information. From August 31 to September 14, security firm Netskope observed users from 619 customer organizations click on the malicious ads, although none of them were actually scammed because Netskope blocked the content.
Roughly 62 percent of the organizations were based in the US, with Japan and Australia accounting for the Nos. 2 and 3 spots. Since the firm has visibility into only a tiny sliver of Internet activity, the number of people exposed to the ads—including those who fell victim to it—is likely much higher. Netskope tracked more than 250 Google Ads campaign IDs across at least 284 legitimate publisher sites.
So, what about Uncle Louie?
“For the victim, that tradecraft turns an ordinary ad click into a browser that appears to seize up on a fake security warning,” Netskope said. “The locker fills the screen, hides the cursor, swallows the usual exit keys, and lags the browser, all to manufacture the sense of a broken machine and pressure the person into calling the number on the screen. Nothing on the computer is actually locked, but in the moment it is convincing enough to push people toward the scam.”
Advertisement
By now, many people, including a fair number of readers of this site, ridicule and shame people who fall for such scams. These criticisms fail to account for a sizable portion of Internet users who have little or no understanding of how computers and the Internet work. Combined with their need to get things done quickly and the growing difficulty of navigating the web, this lack of awareness makes a sizable portion of users prime targets. There’s little doubt that some critics have close friends and family who are among those who simply don’t know enough to be wary.















































You must be logged in to post a comment Login