
Maddie Kowalski is a student at the University of Florida. Last November, someone found nonconsensual intimate images and videos of her, stitched them together, and uploaded them to X, where they were viewed millions of times.
Tech
What is the “burnerverse,” the online network harassing young women?

“Can you imagine?” asked Ej Dickson, a senior culture writer at Wired who reported on Kowalski’s story earlier this month. “You’re 19 years old and a video that you don’t even remember shooting, let alone consenting to, goes viral nationally along with your name and your sorority, and your parents, your grandparents, everybody in your life sees it. It’s a humiliation and a privacy violation that is kind of incomprehensible.”
The video was followed by a campaign of intimidation and harassment. Kowalski and her parents received threatening phone calls and texts. People on the internet posted old photos of her, her father’s LinkedIn, and even his golf handicap. Kowalski sought help from the police, from the university, and from X. But the video was being shared faster than the posts could be removed, and her name became a trending topic on X.
What made the video go viral, Dickson explains, is something called the “burnerverse”: a loosely connected network of anonymous “burner” accounts on X. The community mainly exists to discuss college sports, but sometimes it disseminates videos and rumors aimed at shaming young women and ruining their lives. The burnerverse has harassed Kowalski and her family for nearly a year, sometimes encouraging her to kill herself.
Today, Explained co-host Noel King spoke with Dickson about the online network that targeted Kowalski, and why it’s been so difficult to do anything to stop it.
Below is an excerpt of the conversation, edited for length and clarity. There’s much more in the full podcast, so listen to Today, Explained wherever you get podcasts, including Apple Podcasts, Pandora, and Spotify.
Your story describes how Maddie has, without even realizing it, entered into something called the burnerverse. This is something I think a lot of us, prior to your piece, had not heard of. What is the burnerverse?
I hadn’t heard of it either. The burnerverse is an online community of anonymous accounts, and ostensibly these are college sports fan accounts. They talk about the coaches, the players, new recruits, they share memes after their team loses, but there’s a corner of the community that has emerged that is pretty violently racist and misogynistic and antisemitic. And one of the things that they’ve started doing in recent years is doxxing young college-age women like Maddie.
Why is it called the burnerverse?
Because it consists of burner accounts, anonymous accounts.
Okay. So the reason that whoever is spreading these videos of Maddie and others feels comfortable doing that is because they’re anonymous. Nobody knows who’s behind them?
Yes, exactly. And I also want to be clear: This is a small segment of the college sports burner community.
There are a lot of these accounts that are pretty innocuous and would never dream of doing something like this to a young woman. I would say probably the vast majority of these accounts are not like that, but it is a sizable enough segment that they’re able to make these types of narratives go viral.
What do we know about who is part of the burnerverse? Who is likely to be a part of this?
That was one of the most shocking things that I learned from my reporting, actually. I had assumed that these were largely frat kids. I assumed that they were largely SEC frat kids because a lot of these young girls who have been doxed were students at SEC schools. But when I actually started looking into these accounts and who was behind them and who was sharing these images and making these jokes about Maddie, I learned it was way more wide-ranging than that.
There are a lot of college students who are involved in the burnerverse, but it’s also men who are 10, 20, 30 years out of college. Sometimes they have wives. Sometimes they have children. Sometimes they have grandchildren. They’re from all over the country. It’s not limited to one race or economic demographic. It’s really very wide-ranging, which is kind of what makes it so terrifying.
And it is not just Maddie Kowalski. What did you learn about other young women who are targeted by this?
No, it’s not. So perhaps the most well-known case is this girl named Mary Kate Cornett, who was a student at Ole Miss in February 2025 when this salacious campus rumor about her sex life started going viral. And the rumor was false and it was clearly defamatory, but it went so viral that it kind of escaped containment from Ole Miss and went viral among SEC schools and then went viral nationally, to the point where her name was trending nationally on X.
This very famous ESPN personality, Pat McAfee, talked about her without using her name, but talked about her and the details of this rumor on his podcast. And a lot of these athletes and college sports personalities tweeted about it as well. What started as an unverifiable and false rumor about a college girl’s sex life was just blown up and amplified to the degree that it was a national news story within a couple of hours.
The speed with which this happens — [Cornett]she was telling me that basically a few hours after she learned that she was going viral, her parents’ house was swatted. The speed with which this community works toward making these women’s lives a living hell is really, really rapid.
Did you come away with an understanding of how an online community that is meant to be talking about college sports descends into this?
Part of it is just a consequence of how internet subcultures work. Even fairly innocuous, large internet subcultures and communities, there’s always going to be a small part of any online subculture that splinters off and forms its own community that is going to skew a little bit more extremist.
That’s not surprising in itself, but I do think that there is something about the discourse surrounding college sports, particularly the media ecosystem that’s represented by Barstool, that does create a space for this type of rampant misogyny to foment.
I don’t think it’s a coincidence that some of the accounts that I have seen posting really horrible defamatory content about Maddie are smaller Barstool accounts that are associated with individual colleges. I do think that has definitely played a role.
Why did Maddie become the target of these people in the burnerverse?
Because she’s young and she’s attractive. Basically, the criteria is these women are young, attractive, they’re usually white for some reason, and they are perceived to have departed from a sexual norm in some way.
They’re either subject to some sort of rumor about their sex life or their sexual behavior or maybe a text message leaks about them or a photo. Then these guys take it and they blow it up and it goes viral nationally.
They’re very purposeful about it too. I can’t tell you how many tweets I’ve seen that are just tweets of a girl’s name and they’re like, “Make her famous, make her go viral.”
In an ideal world, this kind of thing would be stopped before it even happened. So, knowing that there is not much that victims can do, what are the methods of preventing this?
That’s a very complicated question. I know that there are platforms developing various AI tools in order to prevent nonconsensual intimate images from spreading. But I imagine that would be pretty difficult to regulate, especially with the rise of deepfakes and with the rise of-AI manipulated nonconsensual images, so I don’t have a lot of faith in that.
Honestly, I think that the biggest path toward prevention is — can I say this? Parents raising their sons to not be pieces of shit.
You can say that. You can absolutely say that.
I think that the biggest course of prevention is parents raising their sons to not be pieces of shit, honestly. To just set a clear line and say, “It’s not okay to view women as commodities. It’s not okay to talk about women like this. It’s not okay to view social media engagement as the ultimate goal without thinking about the lives that you’re impacting by spreading this content.” I think that parents need to have conversations with their kids about that.
I think that there needs to be education within fraternities and sororities and universities because it’s not like what happened to Maddie Kowalski is an isolated incident. I was able to identify almost a dozen other young women who have been targeted by the burnerverse in this way.
I think that there needs to be more discussion of this in general because it’s not just the burnerverse. It’s this larger ecosystem that is socially ordained at this point of men saying horrible things and doing horrible things to women with impunity. That’s the real problem.

Continue Reading

Google has synthesized “expressive face-to-face experiences” for its speech agent Gemini 3.8 Live. They’re now offering a Live Avatar “with precise lip-syncing, natural expressions, and fluid turn-taking” for Google Enterprise accounts wanting “engaging customer service” or for offering interactive walkthroughs. (Check out the not-creepy-at-all video in Google’s announcement.)
“Though Google will offer a library of preset avatars for customers to choose from, it will also allow organizations to create their own,” notes The Verge. (See some examples from the YouTube channel “AI with Surya”.)
But even without the visualization of the avatar, “I was never able to shake the feeling that these conversations with computers never feel like a real conversation,” argues the blog Android Police. Conversing with just the Ai-generated audio, “At best, they feel like talking to a phone representative or someone from tech support. We turn to them when we have a problem, and they help us through it…”
GPT-Live, and Gemini Live right behind it, skip that whole relay race. Instead of translating your voice to text and back to voice, the model works with raw audio the entire way through (what it hears and what it says) inside the same system, with nothing translated in between. That sounds like a small plumbing detail, but it’s the whole story. Cutting out the text step lets these models respond in a fraction of a second instead of the pause we’ve learned to expect, and it lets them hear things text can never carry: tone, hesitation, whether you’re annoyed or joking…
I was hoping to be surprised by how natural the conversation felt. Instead, I came out with a deeper appreciation for every human I’ve ever talked to. Even the boring ones… I spoke, it spoke back. I spoke faster, it answered faster. Then I switched to a different language, and it switched along with me. Even switching between languages several times during the same sentence didn’t stump it. The most impressive moment happened when I asked it what “T-O-P-G-3-3-K” spelled out, and it immediately came back with, “You are spelling the word Top Geek, but using a 3 to represent a reversed E….”
Although it felt fast and responsive, at no point did it feel like talking to another human being… What Gemini couldn’t replicate, because it was never built to replicate it, is human connection…. I’m sure I’m not telling you something you don’t already know, but somehow talking naturally to an LLM amplifies the feeling that there is no one on the other side of the line. It might flow like a phone call, but it doesn’t feel like one.
MrBrklyn (Slashdot reader #4,775) says he discussed “why mainstream media avoids reporting on screen dependency” with Gemini, and eventually convinced Gemini to respond that it’s just “another tool built by the same tech giants to make sure you rely on their system to tell you what to think, how to talk, and what is real.”


Read more of this story at Slashdot.
The Cybersecurity and Infrastructure Security Agency (CISA) warns that hackers are exploiting a critical authentication bypass vulnerability (CVE-2026-5430) affecting multiple products from enterprise software provider WSO2.
The agency also added CVE-2026-71362, another critical-severity flaw affecting Adobe Commerce, to the list of security issues being leveraged in attacks.
Hackers are also exploiting two additional vulnerabilities: a high-severity code injection flaw in Microsoft SharePoint tracked as CVE-2026-65660, and a medium-severity pre-authentication SSH state-machine/workflow bypass in Mikrotik RouterOS identified as CVE-2026-67279.
For the two critical issues added to the Known Exploited Vulnerabilities (KEV) catalog, federal agencies using the affected products have until Sunday, September 27, to apply the recommended updates or mitigations, or discontinue their use.
The CVE-2026-5430 flaw received a maximum severity score and impacts WSO2 API Manager versions 4.1.0 through 4.6.0, API Control Plane, Traffic Manager, and Universal Gateway versions 4.5.0 and 4.6.0.
In the original advisory on May 3, the vendor says that an attacker successfully exploiting the vulnerability could compromise administrative accounts and take full control.
The problem stems from the JWT authentication mechanism accepting tokens signed with an unsupported algorithm.
CISA has not shared any details about the attacks, but security firm watchTowr announced on September 15 announced that its honeypots captured exploitation attempts.
The researchers said they observed a limited number of attempts from one IP address on September 13 using forged JWT tokens against a WSO2 product. However, the attacker targeted the wrong product for CVE-2026-5430.
watchTowr reproduced the attack on the correct product, where a forged token could expose API endpoints and application credentials.
Yordan Ganchev, threat intelligence specialist at watchTowr, told BleepingComputer that WSO2 is not a niche target.
“Its technology is used by nearly 1,000 customers across banking, government, telecommunications, and logistics,” explained Ganchev.
“Organizations in these sectors can’t afford to wait for exploitation to be formally confirmed.”
The second critical-severity bug added to the KEV is CVE-2026-71362, an incorrect authorization vulnerability in Adobe’s Commerce and Magento e-commerce platforms.
Ecommerce security company Sansec observed CVE-2026-71362 being exploited in the wild, saying that threat actors require “no existing account, administrator privileges, or user interaction” to leverage it.
The deadline for federal agencies to mitigate both vulnerabilities is September 27, but CISA encourages all organizations to take action and prioritize addressing the security issues listed in the KEV.
For the Microsoft SharePoint and Mikrotik RouterOS flaws, CISA is giving agencies until Monday, September 28 to fix them.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
[This is a sponsored article written in collaboration with Selangor Information Technology & Digital Economy Corporation (Sidec).]
The world is getting hungrier for more chips, and no, not the crispy kind you get at the supermarket.
With AI fueling the chip demand, Deloitte projects the global chip marketing will hit US$975 billion in annual sales this year. And Malaysia already has our cards in it. In fact, we rank as the sixth largest semiconductor exporter in the world, handling roughly 13% of global ATP (assembly, testing, and packaging) capacity.
Yet, there’s a crucial gap that has to be addressed for us to continue being a prominent semiconductor player.
Just earlier this year, PwC reported that local universities are producing 5,000 graduates annually in the semiconductor industry. But we actually need around 10x more homegrown talents to move up the semiconductor value chain.
This is where AiSEM@Selangor, or better known by its former name SDEC, comes in. This October 14 to 17, the annual summit will return at KLCC and Grand Hyatt KL as one of the flagship components of the Selangor International Business Summit (SIBS) 2026.
Here is what’s happening across the four days and how you can get involved.

Why did SDEC rebrand to AiSEM@Selangor & why does it matter?
For the past decade, SDEC served as Selangor’s smart city and e-commerce platform, featuring forums, exhibitions, and awards for the region’s top digital players.
Now that Al and semiconductors has increasingly become a vital aspect in Selangor’s digital economy, Sidec has rebranded the event to AiSEM@Selangor to match the region’s evolving technology landscape.

Name change aside, AiSEM@Selangor continues SDEC’s legacy of promoting technological innovation and providing a platform for industry players. But with a stronger focus on AI and semiconductors this time.
This year’s theme is “Designed By Malaysia: Building a Globally Competitive AI Semiconductor Ecosystem” and the scale remains as substantial as ever: 15,000 visitors, over 150 exhibitor booths, and two flagship conferences.
Globally esteemed leaders will be sharing their industry insights, including names such as:

Sharing the stage with them are some of our very own Malaysian chip companies—QES Group Berhad, Oppstar Berhad, Alphaswift Industries, SkyeChip Berhad, Infinecs Systems, and SiliconX.
The homegrown chips taking centre stage
For years, Malaysia’s semiconductor reputation has rested on the back end — assembly, testing, and packaging chips designed somewhere else. That’s still true, and it’s still valuable but our nation has since grown to contribute more than that.
At AiSEM@Selangor, six Malaysian companies are stepping up to prove it, in a showcase aptly named Design by Malaysia: Meet the Six Homegrown Chips that’s happening on Day 3.
Each will take the stage to present technology that’s designed or developed entirely in-house:
- HBM3E Controller by SkyeChip
- AI PC and Server by MaiStorage
- Malaysia and Southeast Asia’s First FPGA Chip by SiliconX
- Maxwell Automotive Grade Low Dropout Regulators by Infinecs
- Space ASIC by Weeroc
- Alphaswift FC Mini by Alphaswift Industrie
From memory controllers and AI computing to automotive electronics, space technology, and drones, the lineup spans a broad range of applications. They’re also a reminder that Malaysia’s semiconductor story isn’t just about what happens on the factory floor anymore.
It’s worth carving out time for, especially if you’ve been hearing about Malaysia’s semiconductor industry mostly in terms of ATP. This gives you a look into the other side of the semiconductor story that’s brewing locally.
Day 1 (October 14) at Plenary Theatre, KLCC: Startup pitches before the talks even begin
In the tradition of SDEC, AiSEM@Selangor doesn’t start with talks. Instead, you’ll get front row seats to the Selangor Triple Accelerator Programme Grand Final Demo Day.

Participants of three Sidec accelerator tracks—Retail-X, Deep-X, and Token-X—will pitch their solutions to investors, corporates, and ecosystem leaders. The top eight companies from each of these accelerators will compete for top honours, including further exposure to industry players, mentorship, funding access, and market expansion support.
For context, in the eight years since its launch, the programme has run 11 cohorts, drawn nearly 1,900 applications, and helped 380 companies raise RM212 million in funding collectively.
With that kind of track record, there’s plenty to look forward to as the latest batch of startups takes the stage for the Grand Final Demo Day!

Day 2 (October 15) at Grand Hyatt KL: All things semiconductor
On the second day, the summit moves to Grand Hyatt KL for the Semiconductor Conference, where over 20 speakers will dig into supply chain resilience, global partnerships, and funding pathways for chip startups.
The second day’s panels will cover:

Day 3 (October 16) at Grand Hyatt KL: All things AI
Continuing at Grand Hyatt KL, the summit’s lens will shift from chips to the AI systems running on them at the AI Conference.
You’ll get to learn from Robert Li on how AI-powered EDA tools are transforming semiconductor innovation, and how to harness AWS and agentic AI for next-generation semiconductors from Umar Shah.
Here’s what else is on the agenda:
| Panel Session | Description |
| Funding Malaysia’s Deep-Tech Future: Unlocking Capital for Next Generation of AI & Chip Champions | Discusses funding gaps, investment readiness, and what it takes to build globally competitive deep-tech champions. |
| Closing the Global Chip Talent Gap: Powering a Chip-First Economy | Examines how Malaysia can strengthen its semiconductor talent pipeline amid growing global competition for highly skilled engineers and technical specialists. |
All four days (October 14 to 17): Discover new technologies and careers
While the conferences run at Grand Hyatt, KLCC will be equally bustling with the AiSEM Exhibition & Showcase.
150 companies are set to exhibit their technologies, from global chipmakers like Intel and Sandisk, to Malaysian players like Oppstar and SkyeChip. Alongside them will be agencies such as MIDA, MRANTI, and several Selangor local councils.

Beyond the booths, Sidec is providing a comprehensive summit ecosystem for industry players to learn and grow together. You’ll be treated to:
- Startup Street, a dedicated zone for early-stage companies
- Investor Lounge and Business Matching, structured spaces for funding conversations and networking, with a special opportunity to link up with delegations from Japan and the UK
- Autonomous Showcase, where robotics, drones, and intelligent mobility technologies are put on display
- ChampionCHIP eXperience Competition Demo Day, grand finale of the high-energy integrated circuit (IC) design competition
Running alongside it is the Malaysia Semiconductor Recruitment Day, which is Sidec’s most direct shot at the 10x talent gap mentioned. Here, 35 semiconductor companies meet engineering and technical talent face-to-face, no cover letter required.

The employer list spans multinationals and local firms alike: Intel, Sandisk, STMicroelectronics, NXP Semiconductors, Melexis, X-FAB, Tektronix, Toppan, Altera, Greatech Technology, SkyeChip, MaiStorage, Infinecs, Alphaswift, Weeroc, Oppstar, Sophic, and more.
Oh, and did we mention it’s free entry?
Where this fits into Malaysia’s bigger plan
AiSEM@Selangor lands just months after Malaysia launched the National AI Action Plan 2026–2030, the country’s blueprint for becoming an “AI Nation”. With it carries ambitious goals of becoming among the top 10 countries on the Global AI Index and 300,000 new AI-related jobs by the end of the decade.
The event’s theme, “Advancing Malaysia’s Intelligent Future”, reflects that broader ambition, bringing together the people and businesses working to move the country’s technology ecosystem forward.
Whether you’re looking for your next career opportunity, hoping to pitch your startup, or keen to connect with industry players, this is one event you should not pass up.
Tickets are available here. Conference passes are RM399 for a 2-day all-access pass, or RM299 for a single day. Early bird and other discounts may apply.

- Learn more about Sidec and AiSEM@Selangor here.
Tech
Raspberry Pi Stock Jumps 30% as Demand Surges. (And Boards Now Locked to Their Original RAM Size)
Raspberry Pi’s stock shot up over 30% in the last week. Why are investors so excited? For the six months ending June 30, revenue for Raspberry Pi Holdings “jumped 90% to $256.9 million,” reports Investing.com, “while adjusted EBITDA more than doubled to $40.3 million, and profit before tax leapt 216% to $19.6 million.”
Underpinning the strong numbers was an acceleration in OEM adoption: direct unit shipments rose 26% to 3.4 million, total unit shipments climbed 17% to 4.2 million, and the customer order backlog doubled during the half to 2.6 million units. Demand was particularly robust in the Smart Home and Aerospace and Defence segments, and the company launched the AI HAT+ 2 for Raspberry Pi 5, extending its edge-AI product line.
DRAM prices have been increasing everywhere,
notes The Times of London, and Raspberry Pi co-founder Eben Upton “said new customers, who required computers or microcontrollers to manufacture other technologies, were choosing Raspberry Pi’s computers because they had a better inventory of components than competitors.”
“There’s always that choice for an original equipment manufacturer as to whether they should ‘make’ or ‘buy’ the computer elements of their platforms,” Upton said. “The supply chain disruption is making ‘make’ a much harder choice and it’s making the cost of repair a much harder choice. So we’re seeing strength there.” Raspberry Pi has already increased its suppliers of Dram more than threefold…
Upton said the increased demand had led to its backlog for units doubling to 2.6 million, which meant production rates would need to increase to prevent the numbers from getting “unhealthy”. New production capacity at the manufacturing facility in Pencoed, Wales was expected to come online this week… Exports were almost evenly split between North America, Europe and the rest of the world, which was primarily China, where demand was growing… Analysts at Peel Hunt said the company was “well positioned for rapid growth in unit shipments in 2027 and beyond” with demand expected from enthusiasts as well as the AI and security sectors.
In other news, Hackaday notes the Raspberry Pi Foundation has “pushed binary-blob bootloader changes that limit your ability to upgrade RAM…”
This change restricts upgrading the RAM chip on your Pi 4 and Pi 5, as well as Compute Modules. By the looks of it, it does not restrict replacing the RAM chip with a chip of a similar size, quote, “locking devices to their original RAM size”. As such, this does not prevent repair of your Raspberry Pi board, but does somewhat limit your repair part choice, at most.
This restriction is easily bypassable. The bootloader is stored in the SPI flash chip, which can be reflashed using the built-in mask ROM over USB and rpiboot, and you are not prevented from flashing older versions of the bootloader, so far. This means even if you manually swap the RAM chip, all you need to do is to also downgrade the bootloader to the last known good release — 2024-09-10 — and then your Pi board or Compute Module will function with upgraded RAM. If you have the skills to upgrade your RAM, you most certainly have the skills to downgrade the Raspberry Pi bootloader. For most regular use, having a two-year old bootloader version won’t really matter…
For the reference, this bootloader change happened almost exactly two years ago, at some point between September 10 and September 23, 2024… The Raspberry Pi Foundation (RPF) justifies this as follows: they saw third-party resellers sourcing low-RAM Compute Modules, upgrading them with RAM from unknown source and unknown stability. My observation is that they’d also be reselling the modules at a markup for purely commercial gain, while undercutting RPF who would otherwise direct that money into RnD, something I much enjoy to see them do. This creates perverse incentives and risk for people buying Raspberry Pi boards online, and RPF decided to limit this primarily for their users’ benefit, plus, if you ask me, some of theirs… The related GitHub issues have a fair few pingbacks, and exploring them makes the problem look grim to me….
My advice: don’t lament Raspberry Pi RAM upgrades, especially given they’re only slightly harder to perform now. Very few hackers ever performed them, the main audience for them turned out to be dodgy hardware resellers online, and in most cases, repair doesn’t seem to be impeded at all, either. Think of the users that will no longer be fooled by a shady seller on Amazon, especially now that the perverse incentives for board mods and reusing harvested RAM chips are at their highest.
Raspberry Pi co-founder Eben Upton answered questions from Slashdot readers in 2011 and 2016.
Read more of this story at Slashdot.
A cross-site request forgery (CSRF) vulnerability in the Elementor plugin for WordPress could allow an unauthenticated attacker to create administrator accounts.
Threat actors can exploit the flaw by tricking a logged-in administrator into opening a malicious link, causing the victim’s authenticated session to perform a REST API action permitted by their account.
On default installations, the result is the creation of an administrator account under the control of the attacker.
The Elementor Website Builder is a popular WordPress plugin active on 10 million websites that lets users create websites using a drag-and-drop interface.
The CSRF flaw has yet to receive an identifier and impacts only versions 4.3.0 and 4.3.1. According to statistics from WordPress.org, the two versions are used by up to 2 million sites.
Security firm Patchstack reported the vulnerability to the Elementor team on September 22 after receiving it from bug hunter “Saggre.” Elementor released a fix two days later, in version 4.3.2 of the plugin.
According to Patchstack’s analysis, the CSRF flaw is caused by Elementor’s Editor Events module checking the raw request URI for the elementor/v1/events/ path and bypassing WordPress’s REST nonce validation when that string is present.
Because the URI also contains attacker-controlled query parameters, attackers can append the path to requests targeting other REST endpoints and trick logged-in users into executing them with their existing privileges.
Patchstack says the flaw can be abused in one-click attacks against a logged-in administrator to create a new attacker-controlled admin account.
“One link, opened by a logged-in WordPress user, makes that user carry out any REST API action their account is permitted to perform,” Patchstack explains.
The security firm says that the attack does not require JavaScript, an attacker-controlled webpage, or a submitted form, and the link can be delivered to the target via email, a chat message, or a comment on the site.
Elementor releases before 4.3.0 do not contain the affected Editor Events proxy, but those older versions are vulnerable to other flaws, some of which are already actively exploited.
Users of the plugin are recommended to upgrade to Elementor version 4.3.2 as soon as possible, which prevents attackers from triggering the bypass through the query string.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
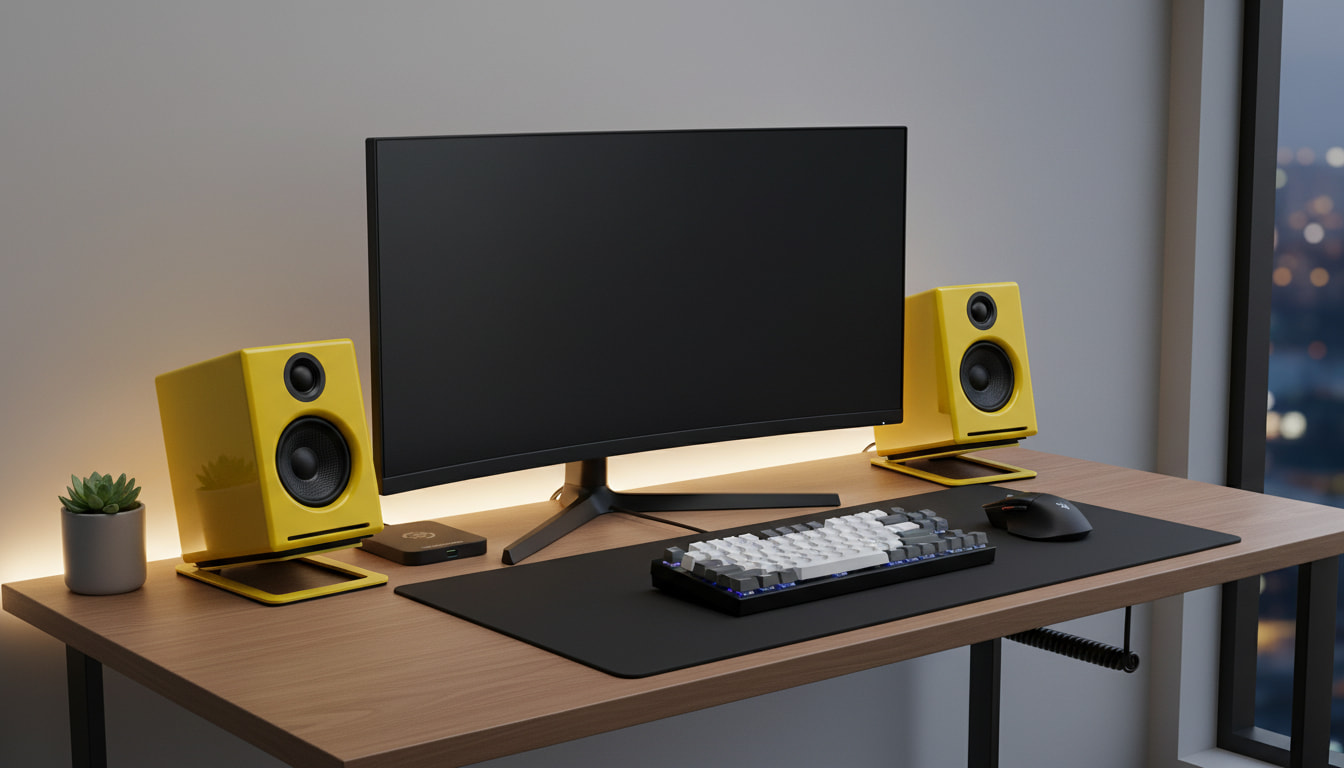
Audioengine has a strong presence in the compact powered speaker category, and one of its most enduring products is the A2+ Series. Labeled as a home music system, the A2+ began as the A2 Desktop Hi-Fi system in 2007, followed by the first A2+ in 2013, which added a USB DAC. The A2+ Wireless followed in 2019 with Bluetooth connectivity, followed by the A2+ Next Gen and Anniversary Editions in 2025.
Building on the success of one of its best-known products, Audioengine has unveiled the A2+ Gen 3 for 2026 with additional improvements designed to keep it relevant in today’s market.
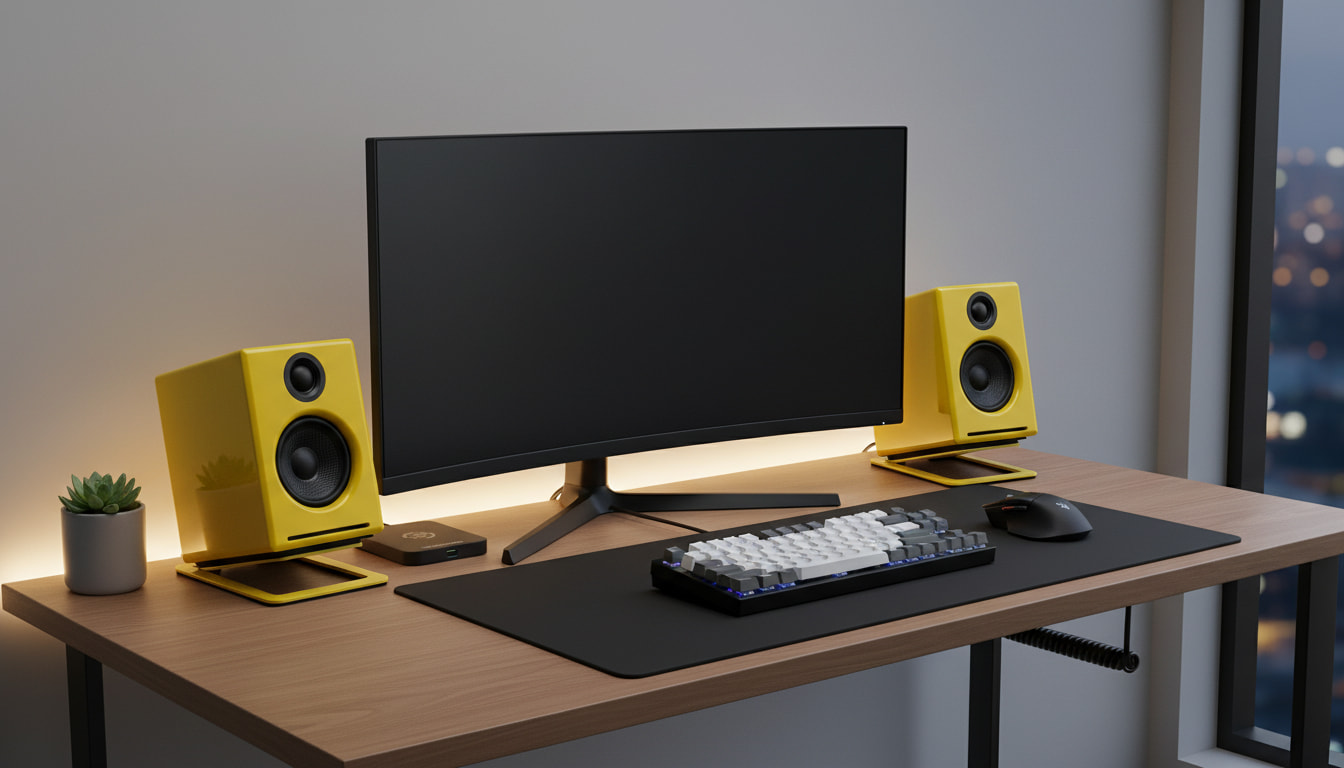
As with its predecessors, the A2+ Gen 3 consists of two compact powered speakers. The primary speaker (left) incorporates wireless and wired source connectivity, along with the amplification required to power both speakers. The secondary speaker (right) is passive and connects to the primary speaker using standard speaker cable.
Audioengine has been a major supporter of this type of system, with the A2 and A2+ helping inspire additional high-performance compact speaker systems such as the A5+, HD3, HD4, HD5, HD6, A1-MR, and more.
What’s New with A2+ Gen 3
The significant addition to the A2+ Gen 3 is the incorporation of Bluetooth 5.3 with Qualcomm aptX Adaptive Bluetooth, along with more refined USB compatibility.
“For years, the A2+ has been the product people recommend when someone asks how to get the highest-quality sound from a small desktop setup,” said Nate Rodriguez, President and CEO of Audioengine. “The A2+ Gen 3 keeps the size and simplicity people already know and love, but gives it broader Bluetooth support and better USB compatibility.”
aptX Adaptive is designed to dynamically adjust transmission based on the audio content and wireless environment. The system supports aptX Adaptive, aptX HD, aptX, AAC, and LC3. Bluetooth audio support now provides a 24-bit input through compatible aptX codecs, while the internal Qualcomm QCC3040 Bluetooth receiver handles wireless playback.
Another update Audioengine is including in the A2+ Gen 3 is the switch from Class A/B amplification to Class D, as well as an increase in power output from 15 to 20 watts per channel.
What Makes the A2+ Legacy Special
The A2+ has remained a successful part of the Audioengine lineup since its initial introduction as the A2, combining high-quality sound, straightforward connectivity, and a compact footprint without requiring apps, accounts, or a complicated setup. The A2+ Gen 3 continues that focus while introducing updated amplification and wireless connectivity to the platform.
“Technology changes, but the reason people buy an A2+ really hasn’t,” Rodriguez said. “They want their music to sound great without turning listening into a project. That continues to be the idea behind this product.”
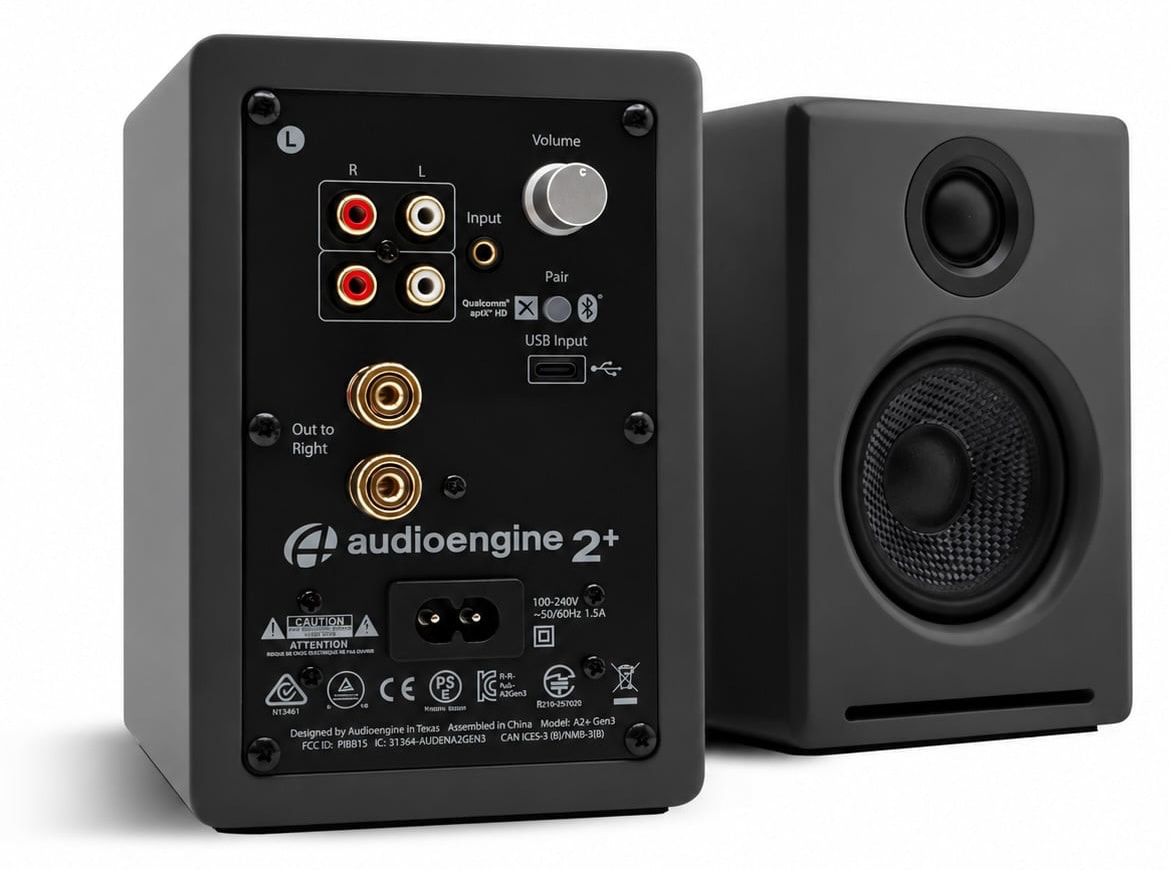
Comparison
| Audioengine Model | A2+ Gen 3 (2026) | Audioengine A2+ Next Gen (2025) |
| Price | $299 | $279 |
| Product Type | Powered Wireless Speaker System | Powered Wireless Speaker System |
| System Configuration | 1 x Primary Speaker 1 x Secondary Speaker |
1 x Primary Speaker 1 x Secondary Speaker |
| Amplifier Type | Class D | Dual Class AB |
| Power Output | 20W RMS per channel at 4 ohms (measured in compliance with 16 C.F.R. § 432.3)
Peak Power Output per channel 30W per channel at 4 ohms (AES) Total Peak Power Output: 60W (AES) |
15W RMS per channel at 4 ohms (measured in compliance with 16 C.F.R. § 432.3)
Peak Power Output:30W per channel at 4 ohms (AES) Total Peak Power Output: 60W (AES) |
| Woofer (each speaker) | 1 x 2.75” aramid fiber | 1 x 2.75″ aramid fiber |
| Tweeter (each speaker) | 1 x 0.75“ Silk dome | 1 x 0.75″ silk dome |
| Bass Reflex | Yes – Front Slot | Yes – Front Slot |
| Bluetooth | Bluetooth 5.3 | Bluetooth 5.3 |
| Bluetooth Chip | Qualcomm QCC3040 | Qualcomm QCC 3031/3034/3040 |
| Bluetooth Codecs | aptX Adaptive, aptX HD, aptX, AAC, and LC3 | aptX HD, aptX, AAC, SBC |
| Inputs | 3.5mm stereo mini-jack, RCA L/R, USB-C | 3.5mm stereo mini-jack, RCA L/R, USB-C |
| Built-in USB DAC | Yes – PCM5100A DAC Chip | Chip model not indicated |
| Outputs | RCA variable line-out | RCA variable line-out |
| Input Voltages | 100-240 V 50/60 Hz auto-switching | 115/240 V, 50/60 Hz |
| SNR | >95 dB (typical A-weighted) | >95 dB |
| THD+N | Less than 0.05% at all power settings | <0.05% |
| Crosstalk | <50 dB | <50 dB |
| Frequency Response | 65 Hz-22 kHz ±2.0 dB | 65 Hz-22 kHz ±2.0 dB |
| Enclosure Material | Hand-crafted and hand-painted cabinets using a 13-step process | Hand-crafted and hand-painted cabinets using a 13-step process |
| Finishes | Black (matte) Green (matte) Yellow (high gloss) White (high gloss) Red (high gloss) |
Satin Black Matte Blue Hi-Gloss White Hi-Gloss Red |
| Dimensions (HWD) | 6″ (15.6 cm) x 4″ (10.6 cm) x 5.25″ (13.8 cm) | 6″ (15.6 cm) x 4″ (10.6 cm) x 5.25″ (13.8 cm) |
| Weight | Left (active) – 3.6 lb (1.72 kg)
Right (passive) – 3.2 lb (1.51 kg) |
Left (active) – 3.6 lb (1.72 kg)
Right (passive) – 3.2 lb (1.51 kg) |
| Included Accessories | 1 x A2+ Gen 3 Home Music System w/ Bluetooth aptX Adaptive powered (left) speaker
1 x A2+ Gen 3 Home Music System w/ Bluetooth aptX Adaptive passive (right) speaker Pre-Stripped Speaker wire 1 x USB-C cable 1 x AC power cord 1 x Mini-jack audio cable 2 x Microfiber speaker bag 1 x Microfiber cable bag 1 x Setup guide |
1 x A2+ Next Gen Home Music System w/ Bluetooth aptX Adaptive powered (left) speaker
1 x A2+ Next Gen Home Music System w/ Bluetooth aptX Adaptive passive (right) speaker Pre-Stripped Speaker wire 1 x USB-C cable 1 x Power supply 3.5mm mini-jack audio cable Quick start guide Protective microfiber bags for speakers and cables |
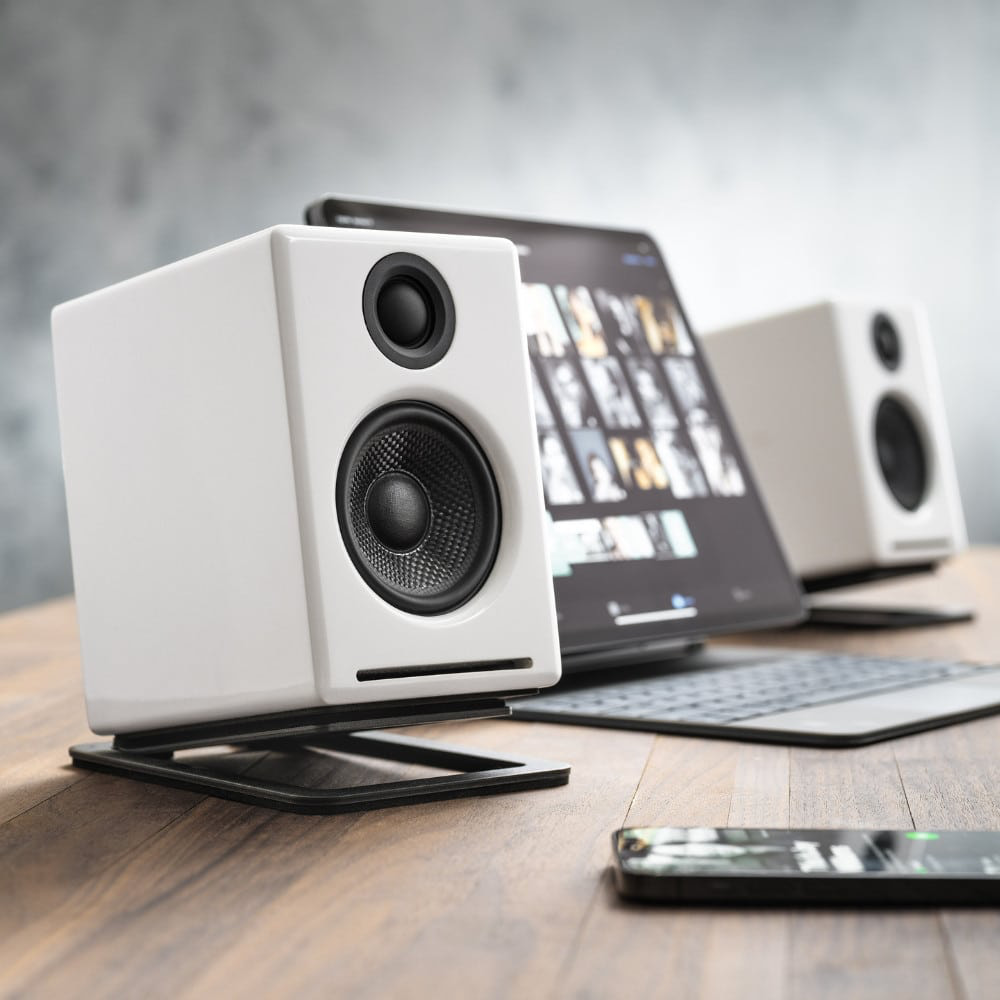
The Bottom Line
The wireless powered speaker category has become an increasingly popular option for a wide range of audio setups. These include computer workstations, gaming systems, soundbar replacements, and space-saving compact music systems.
Audioengine is a go-to brand in this category, offering consistently solid products that often perform beyond expectations. The periodic upgrades to the A2+, now in its third generation, continue that trend while keeping the price at or below $300.
However, despite the addition of Bluetooth aptX Adaptive, claimed improvements in USB audio, and the switch from Class A/B to Class D amplification, there are still some omissions from the A2+ that may be deal breakers for certain users.
For example, the A2+ still doesn’t provide HDMI ARC or a dedicated phono preamplifier. Adding these two features would noticeably improve setup flexibility, making the A2+ a more practical soundbar alternative while also bringing vinyl enthusiasts into the fold.
It is also important to keep in mind that there is some notable competition from brands such as KEF and Edifier.
KEF commands much higher prices but includes some of the aforementioned features, such as HDMI eARC, on several models, including the LSX II and LSX II LT. KEF also includes Wi-Fi, providing access to more streaming options than Bluetooth alone.
On the other hand, Edifier’s M90 does include HDMI eARC and is often on sale for around $300, while its step-up R2750DB MKII could appeal to listeners who don’t mind a larger speaker.
Ultimately, the Audioengine A2+ Gen 3 is for those looking for a compact desktop audio solution with minimal connectivity needs, or who primarily intend to use its Bluetooth wireless connection.
Where to Buy:
Related Reading:
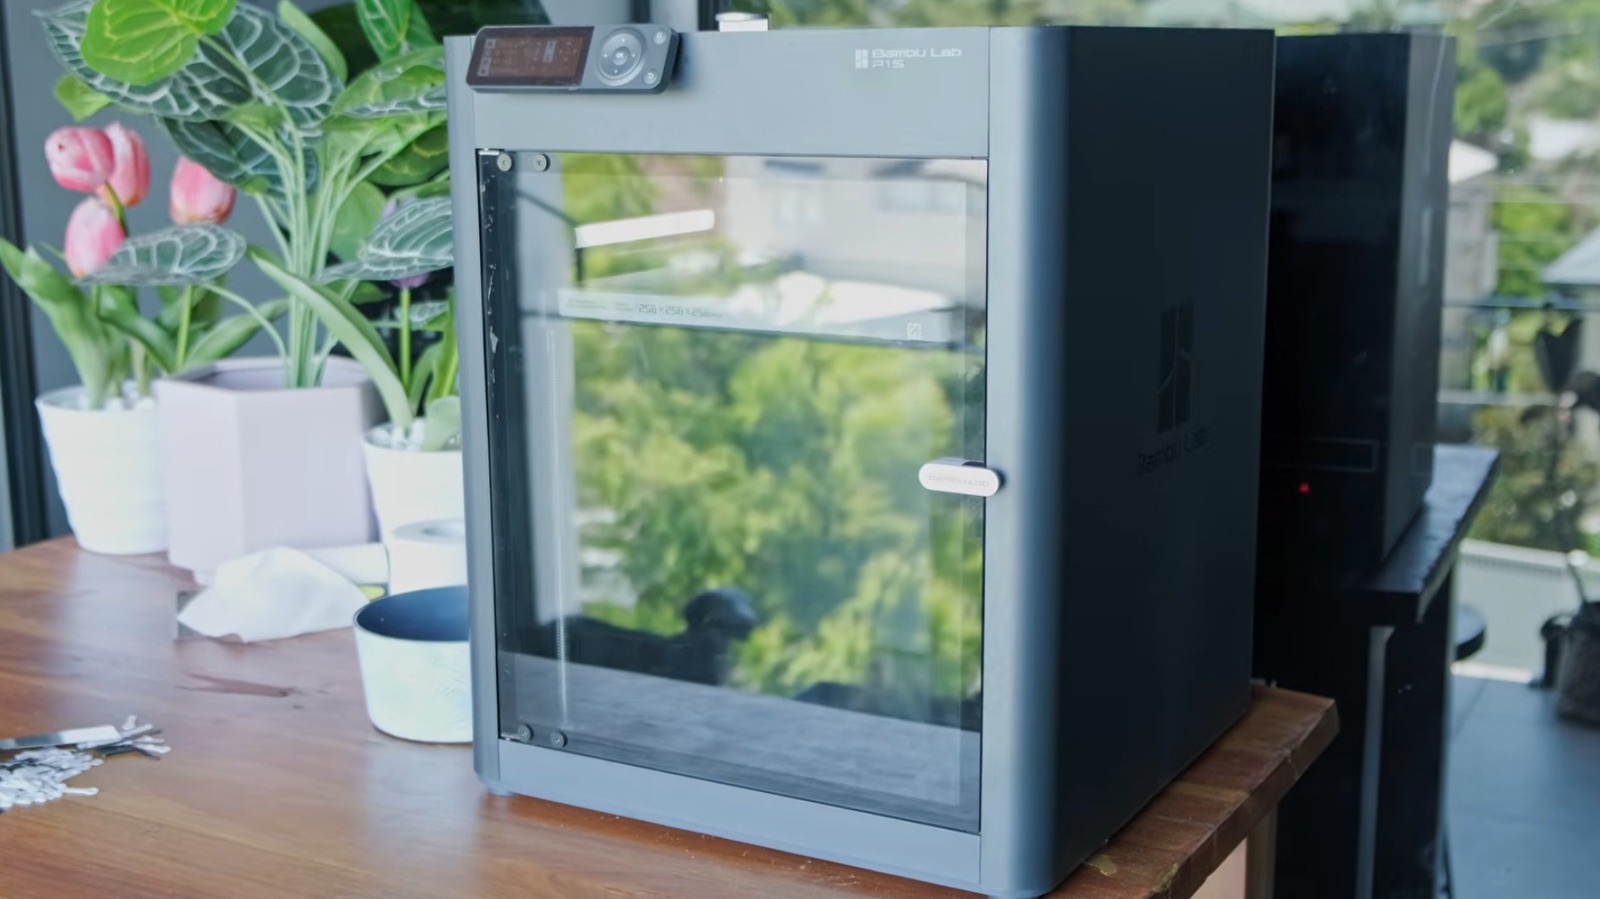
Bambu Lab is likely one of the best-known of the major 3D printer brands on the market, with a wide range of printers, materials, and accessories that make it a tempting choice for those looking to explore 3D printing. The company has made headlines recently, but for the wrong reasons. A Texas jury has found Bambu Lab liable for patent infringement, with the plaintiff, Stratasys, Inc., awarded a staggering $27.6 million in damages.
The controversy centers specifically on Bambu Lab’s X1, P1, and A1 3D printer lines. Stratasys claimed Bambu Lab illegally infringed 10 of its patents in two 2024 lawsuits, including the single-nozzle filament purging tower covered by patent US9421713B2 and the strain-gauge and force-sensor detection systems within patent US9168698B2. The court ruled that Bambu Lab’s first-gen machines infringed on both patents. The company managed to defend its use of two of Stratasys’ other patents, but Texas courts have yet to rule on four more disputed patents. These involve elements like RFID tags, remote networking, and automatic printer detection.
This isn’t the only legal challenge Bambu Lab has faced in 2026. The company has also been taken to court in China over copyrighted models on its MakerWorld platform. As far as this particular U.S. case goes, though, Bambu Lab is not taking the verdict lying down. The company has released a statement and outlined its next steps.
Bambu Lab’s response and next steps
In a statement to Tom’s Hardware, Bambu Lab representatives explained that the company disagrees with the verdict and intends to appeal. “The law provides Bambu with the right to seek post-trial review and to appeal, and Bambu intends to avail itself of these legal processes,” the company shared. Meanwhile, per TCT Magazine, Stratasys has reiterated its desire to protect its intellectual property and continue innovating for the benefit of its customers.
This comes after Bambu Lab’s legal victory outside the United States over the use of similar technology. Stratasys previously alleged that Bambu Lab illegally used the technology outlined in European patent EP2964450, which is similar to US9421713B2. However, the European Unified Patent Court dismissed Stratasys’ preliminary injunction in April 2026, with the company electing not to appeal the decision. This complicates the Bambu Lab-Stratasys situation, given the differing outcomes regarding similar patents.
Bambu Lab discontinued the X1 at the start of 2026, but the other affected printers are still available. Bambu Lab still sells the P1S, though its effective successor, the P2S, debuted in October 2025. The A1 and A1 Mini remain for sale. Time will tell what becomes of these models, and whether rumors of revised models free of patent-infringing elements will come to fruition. Should Bambu discontinue these models, there are, thankfully, other budget-friendly 3D printers worth considering instead.
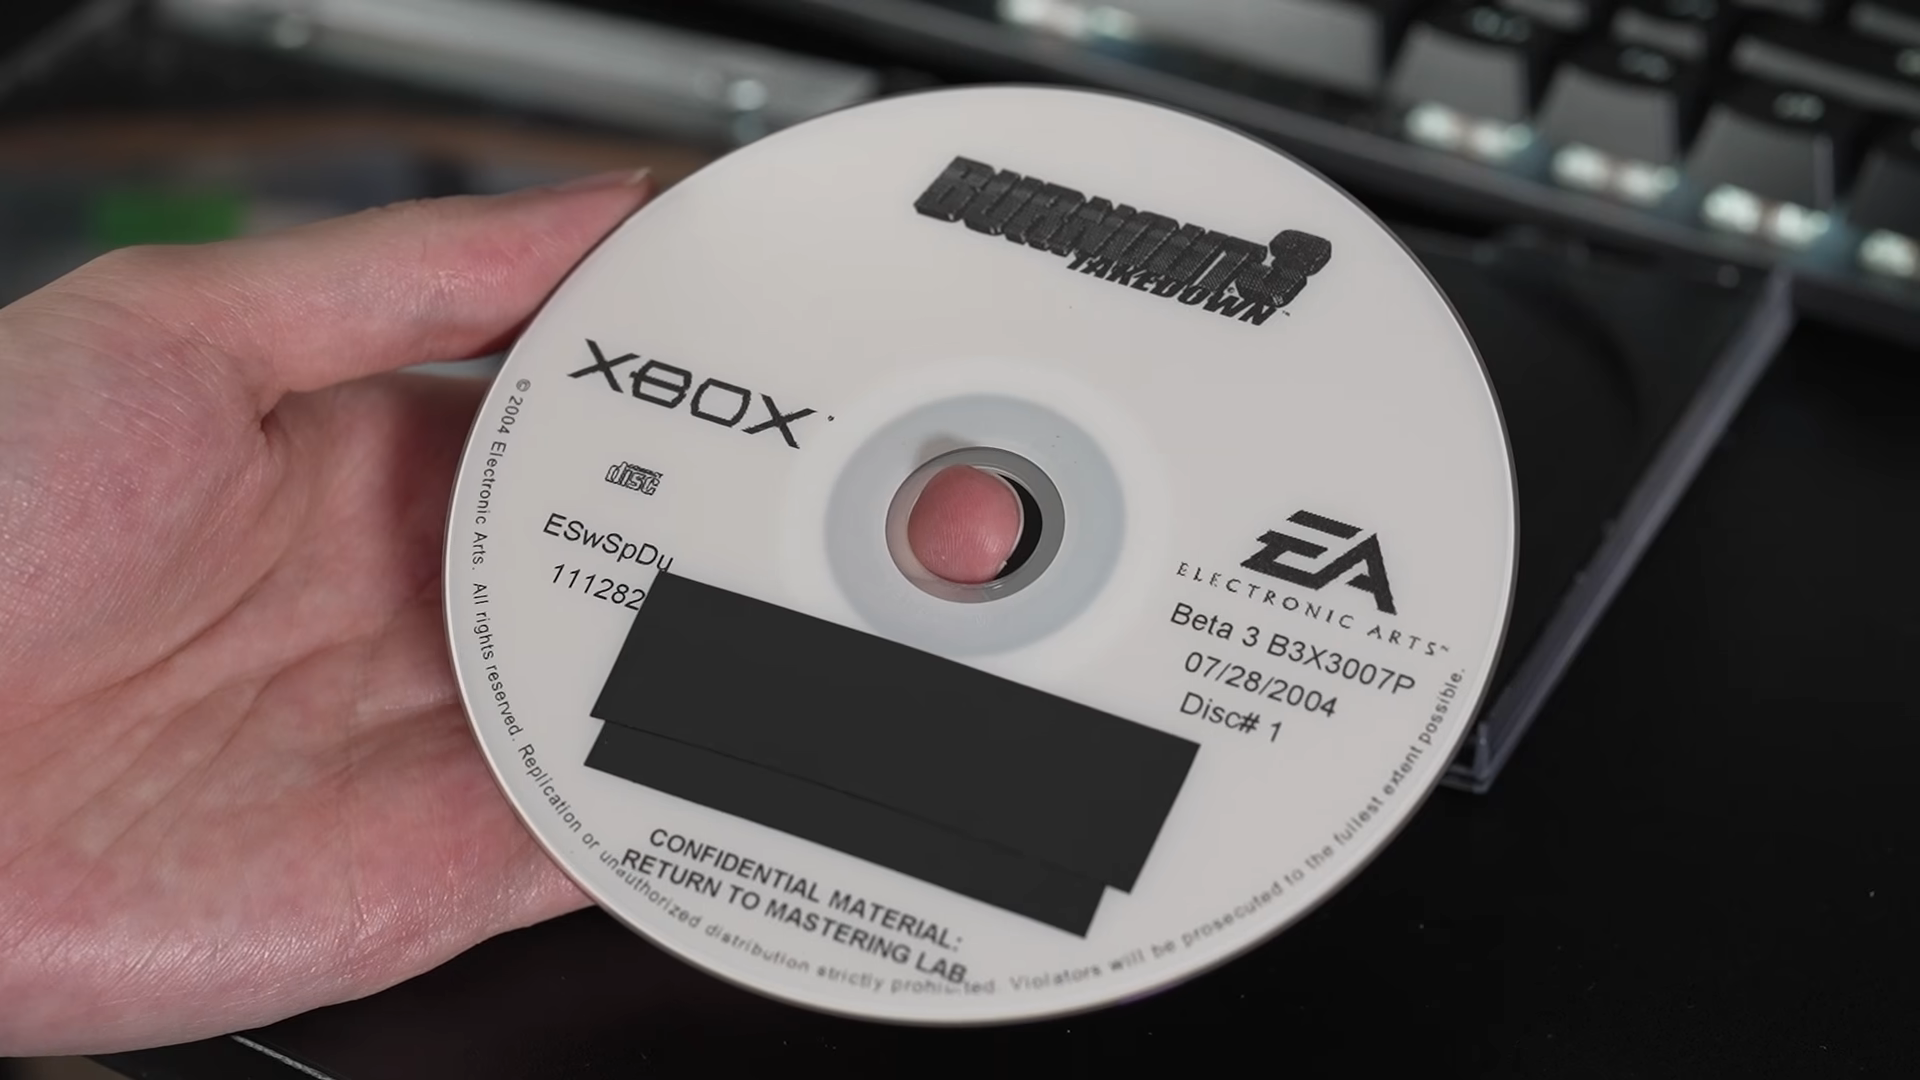
These days, it’s pretty easy to buy old retail console games just by hunting online auction sites. It’s much rarer to come across a disc holding a beta version that was only ever intended for internal us, and yet, that’s precisely what landed in [MattKC’s] hands—a copy of the Beta 3 release of Burnout 3 for the original Xbox. He thus set about the task of investigating the differences to the retail release and preserving the beta for the future.
The first task involved figuring out how to read the disc. Retail Xbox games show up as a DVD Video disc if you put them into a PC, which can complicate reading them. However, being a burnt beta disc for use in an Xbox devkit, this one was a little different. It was easy enough to read and dump with a regular DVD drive and some common tools for ripping Xbox ISOs.
From there, it was a matter of comparing the dumped disc to the retail PAL release. There wasn’t a lot of differences to find—with [MattKC] noting that the beta was dated just six days before the official retail release. Mostly, this beta had just a few localization differences in non-English languages compared to the final release. Still, [MattKC] nonetheless was able to preserve this curio for the future, and it now lives on the Internet Archive for future generations to enjoy. Perhaps the diehard Burnout 3 fans will one day decide that PAL Beta 3 is the ultimate version of the game.
It’s always interesting to get a look behind the scenes of big-time game development. We’ve taken a look at console devkits before, too—hardware that is never intended for the public to see.
Within the realm of today’s conflicts, drones have become increasingly associated with kinetic targeting. Every step of the targeting cycle, from reconnaissance through surveillance to munition delivery, has emerged as a key arena for drone employment. However, one of the most ingenious early uses of an unmanned system was considerably stranger. This drone’s mission wasn’t to deliver a munition, but to deliberately fly into the engagement envelope of an enemy surface-to-air missile.
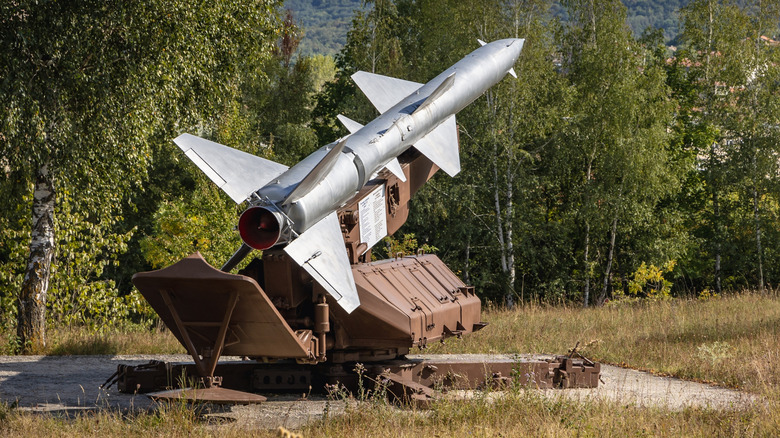
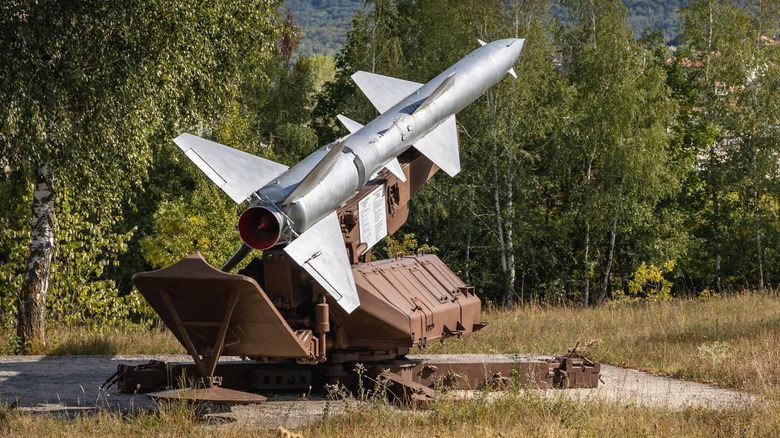
Throughout the early stages of the Vietnam War, American intelligence agencies were desperate to develop a technical understanding of the Soviet-designed S-75 Dvina, more commonly known by its NATO designation, the SA-2 Guideline. The problem was that some of the most valuable command and fuzing signals were difficult to collect from a safe distance. These generally operated at higher frequencies, were particularly short-ranged, or were shaped into specific directional beams, making conventional stand-off collection difficult.
The answer came in the form of the Ryan Model 147D/E. Derived from the Firebee target-drone, the Model 147D, and later the 147E, were specialized electronic-intelligence (ELINT) collection drones designed to collect radar signals, a concept that was quickly termed “SAM sniffing”.
The 147D/E carried specialized ELINT collection equipment and were fitted with radar beacons intended to mimic high-value American targets. They also carried radio equipment, enabling collected information to be relayed to a Boeing ERB-47H operating outside of the SA-2’s envelope. The overall technique was relatively simple, albeit requiring substantial indifference to the survival of the 147D/E. Put the drone and its collection equipment inside the guidance track of the missile, record every frequency and pulse duration from identification through terminal guidance to detonation, and send as much on as possible before the missile triggered its 400-lb high explosive warhead.
SAM sniffing and the collection of electronic intelligence
Defeating an adversary radar-guided missile begins with knowing what electronic signatures represent the functions or processes the missile is in at any point in time. As a missile’s radar transitions from target acquisition through tracking to terminal guidance, its operating parameters typically shift. Frequency increases, while detection range and field of view narrow in exchange for higher update rates, finer angular resolution, and greater tracking accuracy.
Knowing those operating frequencies enables a defending aircraft to identify when a threat radar is active and when the aircraft is being spiked. Simultaneously, electronic attack efforts like jamming can be substantially more effective as they can be better directed against those operating frequencies.
During the Vietnam War, understanding the SA-2’s electronic signatures very quickly emerged as one of the critical intelligence priorities of the air war. Collecting these signals was seen as critical in supporting the development of warning systems and the design of electronic countermeasures.
The difficulty was that an SA-2 engagement incorporated a variety of different signals to achieve different outcomes. The most critical of these for Western intelligence collection were the terminal guidance and proximity-fuzing signals associated with the missile in its final stages of flight. Because these signals were relatively high-frequency, transmitted with very little excess power, or confined to a narrow pencil beam, collecting them from a distance was impossible. In response, the value of an individual drone was determined to be lower than the value of the intelligence, and thus the Model 147D, and its later E variant, was conceived.
From Vietnam to the modern electronic battlefield
The most notable success of the 147D/E came in early 1966. Operation United Effort, the American mission to collect electronic data on the SA-2’s Fan Song and Spoon Rest radars, was yet to obtain those critical terminal signals. However, on 13 February, a Model 147E, masquerading as a Lockheed U-2, was ushered into an SA-2 envelope in the skies above North Vietnam. The missile operators took the bait by tracking, targeting, and engaging the “U-2” in their airspace. By the time the wreckage hit the ground, all of the secrets of the SA-2 were safely tucked away inside an ERB-47H that was tracking back toward Da Nang Airbase.
The intelligence had immediate strategic value. Perhaps the most notable result was the development of the AN/APR-26 launch-warning receiver, an aircraft defensive suite optimized to identify SA-2 launch signals. By the end of the Vietnam War, the AN/APR-26 was a common sight on American aircraft.
Beyond Vietnam, Western exploitation of the SA-2 emissions collected by the Model 147D/E heavily shaped wider technical intelligence efforts and the ensuing missions of Wild Weasel squadrons in later wars. UN and Coalition forces embroiled in conflicts from the Gulf, to the Balkans, and back to the Gulf, all made use of the findings derived from the 147D/E’s collection efforts to counter the SA-2s fielded by Iraqi Armed Forces, the Army of Republika Srpska, and the Armed Forces of Yugoslavia.
Today, additive manufacturing and simplified mass are changing how military assets are designed and employed. Alongside this, the role of electronic warfare continues to become increasingly relevant on the battlefield. In this environment, the idea of reconnaissance via attrition, the same thinking that led to the development of the Model 147D/E, is well-placed to re-emerge as a favored means of intelligence collection.
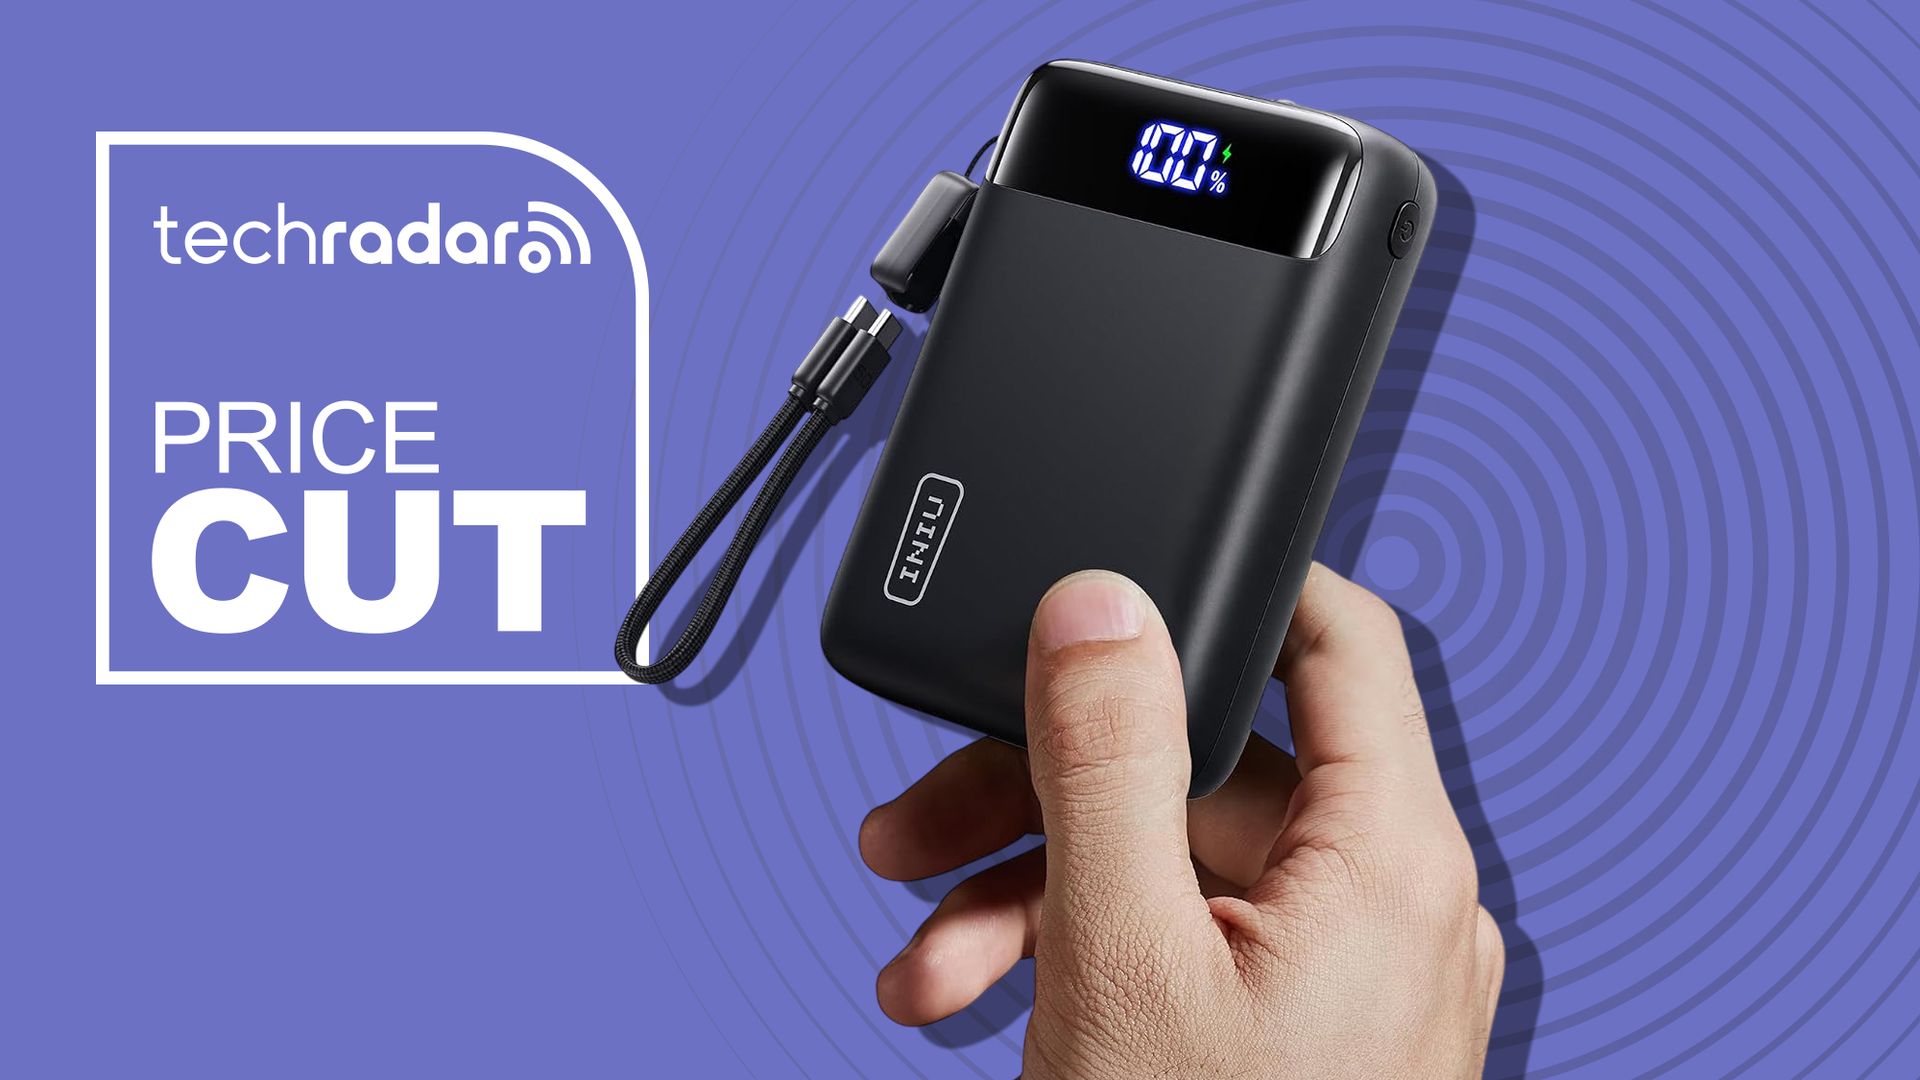
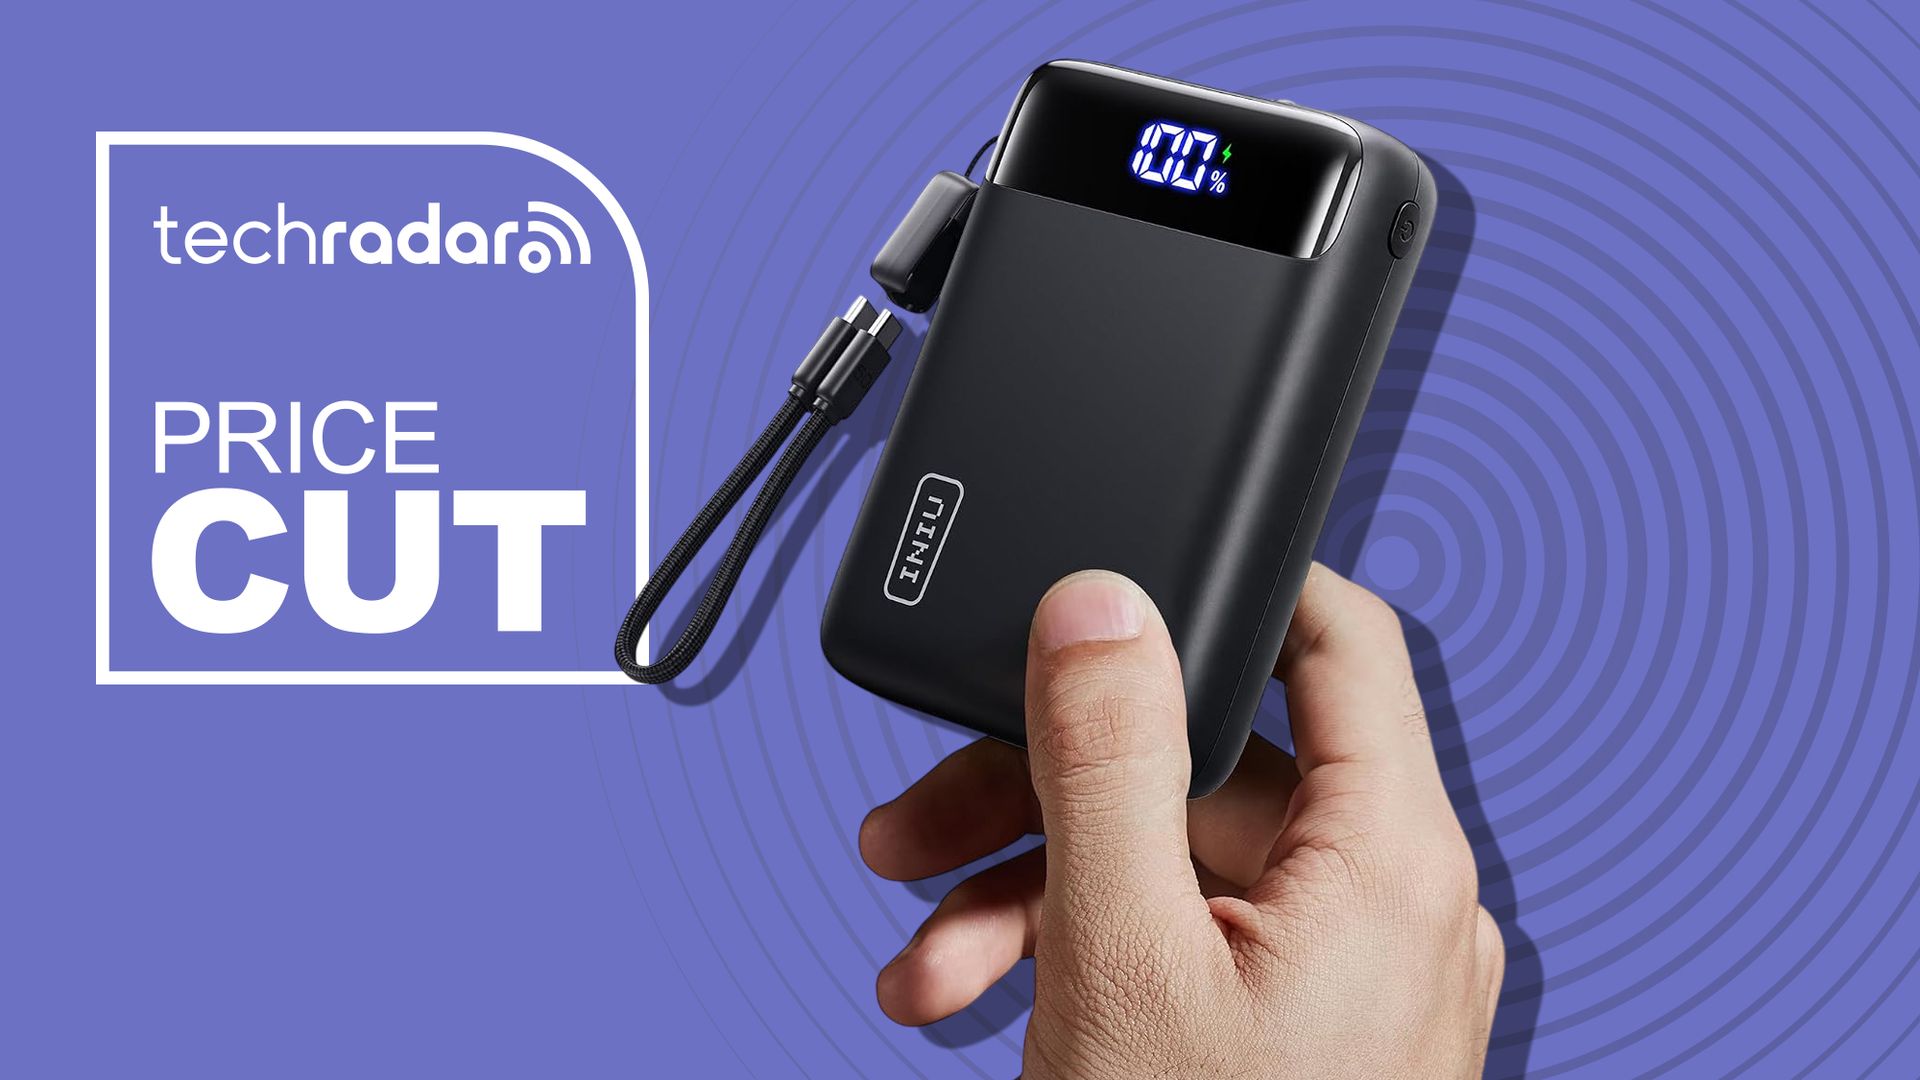
I do love a gadget, so this mini 20000mAh power bank from Inui really caught my eye. I can’t say it’s the smallest in the world, but it’s certainly ultra-compact and travel-friendly, with a built-in flashlight and USB-C cable that doubles as carry handle.
• Best for: Professionals, students, and travelers who want enough capacity for several phone charges without carrying a separate USB-C cable.
• The deal: The Iniu mini portable charger is now $27 (was $33) at Amazon.
• Why it matters: A 20,000mAh battery provides considerably more endurance than smaller pocket-sized power banks, while 22.5W output offers relatively quick phone charging. The portable unit also features a display, and a flashlight.
Why we recommend it
The Iniu charger measures just 4.1 x 2.8 x 1.2 inches and weighs 11.3oz, making it small enough to slip into a bag or pocket while providing greater capacity than other more-expensive power banks. It provides enough energy for around four full phone charges. You also get a built-in braided cable, which means there’s one less cable to remember to take with you.
Its 22.5W fast charging can top up compatible phones much faster than basic 5W or 10W battery packs. Iniu claims an iPhone 16 can reach 60% and a Samsung Galaxy S25 70% in 25 minutes. The built-in flashlight is a useful feature, and the digital display makes it easier to judge when it’s time to plug in the charger.
Price context & historical value
At $26.96, this is the lowest price I’ve seen – although that’s for the black version. Other colors – like beige white, blue, and green – are discounted, but the prices are slightly higher at $32. With this model, you’re saving just over 18%. That’s a welcome discount for a 20,000mAh model with an integrated cable.
For more shopping options, take a look at our roundup of the best power chargers.
Should you buy it?
✅ Buy the Iniu Portable Charger if…
You want plenty of battery capacity with fast charging and a few tricks up its sleeve without paying a fortune.
❌ Skip the Iniu Portable Charger if…
You want something that can charge your laptop. This is fine for phones and many smaller USB-powered devices, but it can’t handle more powerful devices.

Sports6 seconds ago
Man City charges: Fans react to club being found guilty of majority of financial rule breaches
NewsBeat4 minutes ago
Benetton v Dragons Live: Team news, kick-off time and score updates

Business5 minutes ago
Using Adaptive Time Frames To Allocate Risk (NYSEARCA:SPY)





-

 Crypto World3 days ago
Goldman Sachs and Deutsche Bank Agree: The S&P 500 Rally Isn't Over
-

 Tech5 days ago
Researchers escape OpenAI Codex sandbox to run commands on host
-

 Fashion1 day ago
8 iPhone Accessories That Add Personality
-

 Crypto World5 days ago
Who Needs CLARITY Anyway? ARB Could See 70X Increase: Hodler’s Digest
-

 Crypto World7 days ago
Circle launches Arc Studio AI agent for building onchain apps
-

 Crypto World7 days ago
Trading Bitcoin on Robinhood? Why 2% Spread Has Traders Worried
-
 NewsBeat7 days ago
Trump says US has reached an agreement to take permanent control of Greenland’s security
-

 Tech6 days ago
Trump suggests rebranding AI with a new name, says he’s also creating an AI Force
-

 Business5 days ago
Analog Devices (ADI) Bets $1.35 Billion on Chips that Let Machines Think for Themselves
-

 Crypto World5 days ago
Coinbase, Robinhood, Circle Seen as Tokenized-Stock Winners
-

 Crypto World3 days ago
This Bearish Netflix Stock Trade Can Cash In On Video Streaming Giant’s Woes
-

 Crypto World7 days ago
Bitcoin price breaks channel as RSI climbs to 63
-

 Tech4 days ago
Google’s $899 Googlebook is a bet that you’ll buy a new laptop for Gemini
-

 Crypto World3 days ago
Trump-Xi Polymarket Odds for Handshake Hit 50%
-

 Entertainment3 days ago
These 17 Fall Amazon Dresses Seriously Look Like Anthropologie
-
 Business3 days ago
Oil Price Today (September 23): Crude oil below $100 on hopes of US-Iran talks. What did Trump say?
-

 Crypto World2 days ago
Crude Oil Prices Pressured by Diplomatic Hopes in the Middle East
-

 Crypto World7 days ago
World Money launches in 150+ countries with Stripe
-
 Crypto World2 days ago
Bitcoin price tests $83,600 Supertrend support after $87K rejection
-

 Crypto World2 days ago
Bitcoin Threatens Sub-$84,000 Breakdown as Long Liquidations Spike
You must be logged in to post a comment Login