Meta is reportedly preparing a new version of its smart glasses without a camera, even as the company’s chief technology officer argues that concerns surrounding the devices are being driven by a small number of problematic users.
Andrew Bosworth, Meta’s CTO and head of Reality Labs, addressed the issue during an Ask Me Anything session on Instagram. He argued that most people use the glasses responsibly, comparing their recording capabilities to smartphone cameras while highlighting the devices’ recording indicator and anti-tampering protections.
However, ongoing privacy concerns and reports of ways to bypass those safeguards suggest that the debate around camera-equipped wearables is far from settled.
Meta defends recording safeguards amid privacy concerns
Bosworth pointed to the glasses’ recording light, which is designed to alert people when the device is capturing video. Meta has also introduced measures intended to prevent users from recording when the indicator is covered or tampered with.
Advertisement
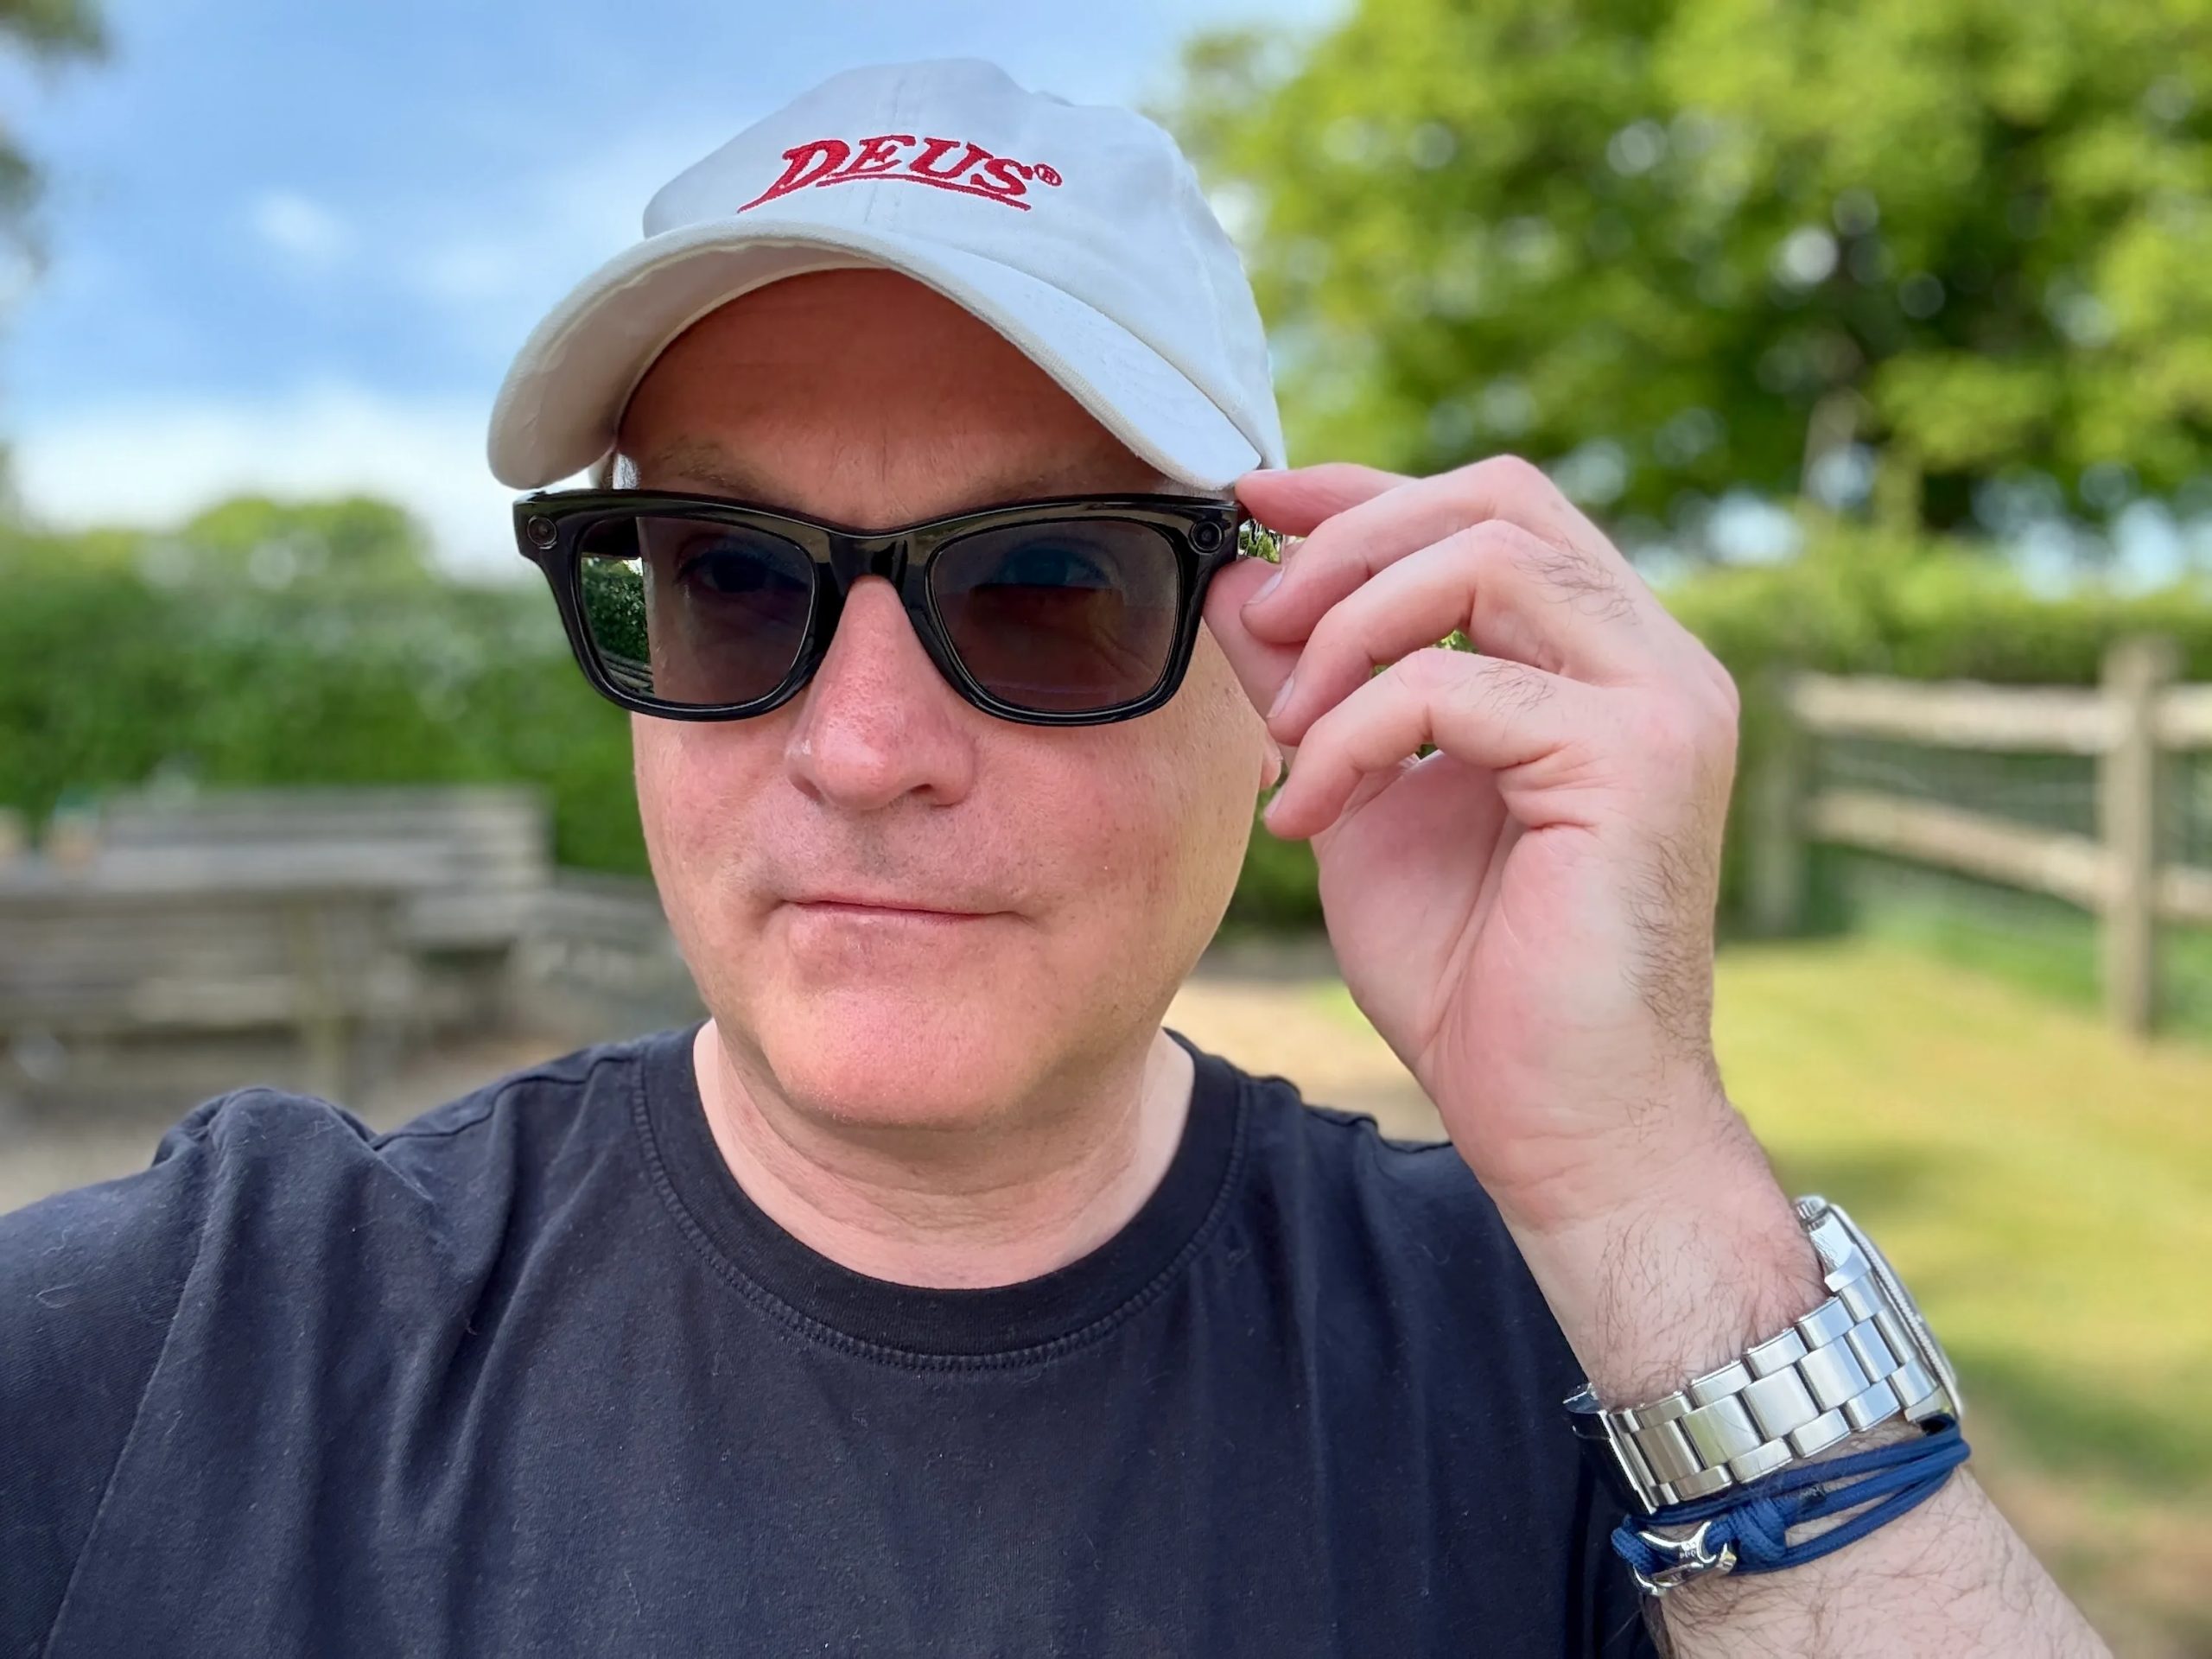
Andy Boxall / Digital Trends
According to The Next Web’s report, a software update addressed a loophole that allowed users to begin recording and then cover the light. Meta also disabled cameras on some devices where the indicator had been physically removed.
The company reportedly said the enforcement affected fewer than one in every 1,000 glasses sold. However, The Next Web reported that a $2 sticker could still defeat the recording indicator, raising questions about whether a visible light alone can provide meaningful privacy protection.
The concern extends beyond the number of users behaving improperly. Unlike a smartphone, which typically makes recording more visible to people nearby, smart glasses can capture footage without an obvious change in the wearer’s behaviour.
Camera-free Luna could change Meta’s approach
The Information reportedly claims that Meta is preparing a camera-free version of its glasses, codenamed Luna. The device is expected to feature six microphones and could be unveiled at Meta Connect on September 23, with shipments potentially beginning in October.
Removing the camera would directly address concerns about people being recorded without their knowledge. However, it would also remove one of the most prominent features associated with Meta’s existing smart glasses.
Advertisement
Meta
The microphones introduce another privacy consideration. While the camera-related concern would be reduced, users could still question whether the device is listening and how that activity is communicated. Unlike a camera, microphones do not currently have an established public indicator convention.
Privacy scrutiny is also increasing in Europe. Authorities in France, Norway and Germany are examining issues involving camera-equipped wearables, while the European Data Protection Board is preparing a report on the category.
Meta’s upcoming Connect event could therefore provide important details about Luna, including its microphone controls, privacy indicators and intended use cases.
Saturday morning President Trump announced he’s creating an AI task force and appointing an AI czar, reports Politico.
“I am forming the AI Force, much like I did Space Force, which has been a tremendous SUCCESS,” Trump wrote Saturday in what Politico earlier described as “a lengthy Truth Social post on Saturday morning.”
TRUMP: Over the years, there have been many Hoaxes, all generated by the Radical Left Dumocrats, for purposes of destroying our Country. RUSSIA, RUSSIA, RUSSIA, UKRAINE, UKRAINE, UKRAINE, Global Warming, Impeachment Hoax #1, Impeachment Hoax #2 […] and now, the decimation, or destruction, of AI, commonly known as Artificial Intelligence — And I, as President of the United States, will not stand by and let this happen.
It all began with an attack on our Data Centers, until people realized how wealthy and prestigious they were for the Communities in which they were built. Higher Salaries, Lower Taxes, and Safer Streets, was the result, and the crazed Data Center attack has largely failed, so now […] they are going straight at AI. We will not in any way hinder or stifle the Growth of this incredible Industry. Rather, we will cherish it, help it, and watch over it, as it grows!
Advertisement
However, we will also be looking for BAD, and we can do that, very easily, with our already existing Criminal and Civil Justice System. For this purpose, I am forming the AI Force, much like I did Space Force, which has been a tremendous SUCCESS, in my First Term. To that end, I will be announcing, in the near future, the AI “Czar” — Only High I.Q. individuals need apply!
Trump concluded by saying AI “is the next Industrial Revolution, or Internet, but will be even larger and more impactful… We are leading China, and the rest of the World, and I intend to keep it that way!”
But what exactly is AI Force? “The White House did not immediately respond to a request to clarify whether the agency would be military or civilian,” notes the Washington Post. So now “The tech industry is struggling to make sense of President Donald Trump’s surprise announcement,” Politico reported Saturday afternoon:
Four representatives for the sector, who were granted anonymity because they were not authorized to speak publicly, told POLITICO that the industry was not widely informed of Trump’s decision prior to the Truth Social post. “Nobody knows what the idea even is,” one of the people said. Another said that feedback on the idea was not widely solicited within the industry. The White House did not immediately respond to a request for comment…
Advertisement
“I think that he clearly feels pressure to say something, but he’s torn because he’s just spent the last few days saying that the whole thing is a hoax,” Adam Kovacevich, CEO of the progressive tech industry coalition Chamber of Progress, said of Trump and his prior dismissal of AI doomsday scenarios. Since the departure of David Sacks, who stepped down as the Trump administration’s previous AI czar earlier this year, the White House has been “making up AI policy as it goes,” Kovacevich added. “I think it’s clear they’ve really missed the presence of an organized leader like David Sacks was.”
One of the tech industry representatives said they were confused about whether the task force would be charged with formulating more AI regulations or recommending policies that would further stimulate the tech’s development. Taylor Barkley, director of federal government affairs at the industry-aligned Abundance Institute, is eyeing it as a way to solidify a light-touch government approach to the technology he says will foster innovation. “Any AI Force or AI Czar should have one job: keep the field open so entrepreneurs at every scale can compete, free from onerous regulation,” he told POLITICO. “Existing criminal and civil law can handle bad actors. New permission regimes will stifle the very activity America needs most.”
It’s worth noting that the day before, California’s governor made an announcement. “With Donald Trump and Congress asleep at the wheel, Governor Gavin Newsom is once again taking the lead to strengthen AI safety for all Americans,” the governor’s office announced Friday. Newsom issued a strong executive order convening experts to help California create new AI safety laws and reporting rules, possibly even requiring safety auditors embedded in labs and emergency “kill switches” in frontier models.
Benchmarking has become the industry norm for how AI companies validate their models’ capabilities and, when the metrics swing in their favor, stand out from competitors and advertise their superiority. In other words, good benchmarks pretty much always mean good PR.
Unfortunately, companies have also figured out how to outwit legacy benchmarking systems — many of which are older, and not built to measure the capabilities of modern models.
Vals, a startup formed in 2024, says that it is on a mission to fix this very imperfect system. In the span of less than two years, the company has established itself as a notable presence in the tech industry and, last year it managed to secure a seed round led by 8VC and Bloomberg Beta. Then, last month, after a period of rapid growth, it raised $40 million in a series A led by Andreessen Horowitz.
Rayan Krishnan, the company’s 25-year-old co-founder, previously interned at Palantir, and, as an undergraduate at Stanford, worked for Microsoft and the school’s much lauded artificial intelligence lab. Krishnan says Vals was born from his own observations about how benchmarking was falling behind the advances of the industry it was designed to measure.
Advertisement
“We were seeing a bunch of new, very capable models come to market quickly, and the academic benchmarks [were] not keeping up with that frontier advance,” Krishnan shares. With AI being integrated into every part of society, benchmarks should really exist to verify that models can do what companies advertise they can do, Krishnan said.
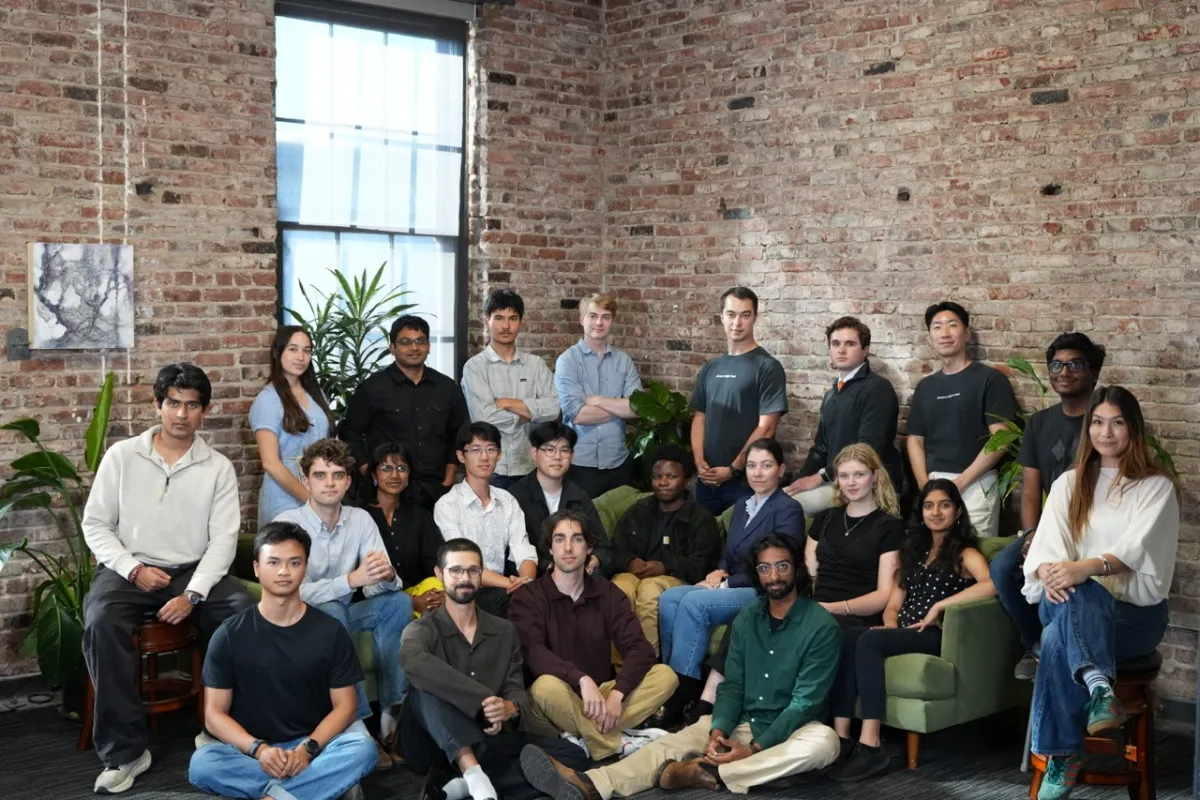
Last week, the young founder showed me around his company’s two-floor office on San Francisco’s Folsom Street — an old brick building that, a century ago, served as the site of a large brewery. Instead of an industrial output of beer, the historical structure is now home to a number of different startups looking to ship the future of the tech industry.
“Historically, I think evaluation has been done to evaluate intelligence in a very abstract way,” Krishnan tells me. “Like, do models know enough information to be able to take a bar exam type test?”
Here, Vals seeks to differentiate itself. While many benchmarking systems offer tests that are publicly available (this can allow a company to train its model against those tests, thus arguably cheating on their exam), Vals doesn’t publicly disclose its specific test materials. Instead of measuring an AI model’s general knowledge, Vals also evaluates models on their ability to complete complex tasks associated with specific industries like law, finance, and coding.
Advertisement
“What we’re doing is actually looking at what are the real impacts of the models,” said Krishnan. “Can they do work that produces a product of the same quality as a human within every domain?”
The idea is to check not just for positive outcomes but also for negative ones, he says. The hope is to analyze how, “if these models ran wild in the world, what the negative implications would be.”
The capabilities that Vals is measuring are growing. In additional to more traditional industries, the startup continues to push into more unique terrain. “We have a benchmark on recursive self improvement. We’re doing some work in mental health, cybersecurity, biosecurity, and even law of armed conflict to models to understand how to apply the Geneva Convention,” Krishnan shares.
Companies pay Vals to test their models, which can be an odd concept to wrap your head around. Why would a company pay to learn its model isn’t performing well? But having an effective measurement helps companies troubleshoot and improve over time. Krishnan compares their revenue model to how a student might pay the College Board to take the SAT.
Advertisement
In turn, these evaluations are becoming key decision-making factors for companies looking to acquire new AI models.
The startup recently revealed that its revenue is currently eight times what it was last year. Its staff is also growing. Vals, which started the year with only eight people, has already tripled to a team of 25. Krishnan said that as the startup grows, the plan is to relocate to a significantly bigger office, as well as to bring on an additional 10 to 15 people. The company also recently launched a program centered around providing model evaluations to federal agencies.
Krishnan sees his company’s system of benchmarking as the future of how AI companies think about growing their businesses and establishing public trust.
“AI companies are starting to go public. SpaceX went public. Anthropic is slated for later this year. I suspect OpenAI will be public soon. I think as AI models become a core part of the economy and are diffused more broadly, the types of benchmarks and evaluations that we do are going to drive their usage and be a central part of how these companies submit public filings or talk about the prospective investments they’re going to make in AI,” he said.
Advertisement
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
A new summer option aims to provide an alternative pathway that better aligns with aircraft maintenance schedules and operational requirements.
Ireland’s aircraft mechanic apprenticeship programme is to offer a new summer training schedule option beginning from next year.
The new training initiative will accept 45 students and operate from May until October each year, with the purpose of strengthening Ireland’s aviation skills pipeline and making training more flexible for apprentices and employers across the sector.
The Irish Government said the new summer option will provide an alternative pathway that better aligns with aircraft maintenance schedules and operational requirements in the aviation sector.
Advertisement
Aircraft mechanic apprenticeship places increased from 79 slots in 2024 to up to 160 in September 2025, which is reflective of the increased demand for skilled aircraft maintenance professionals, according to the Government.
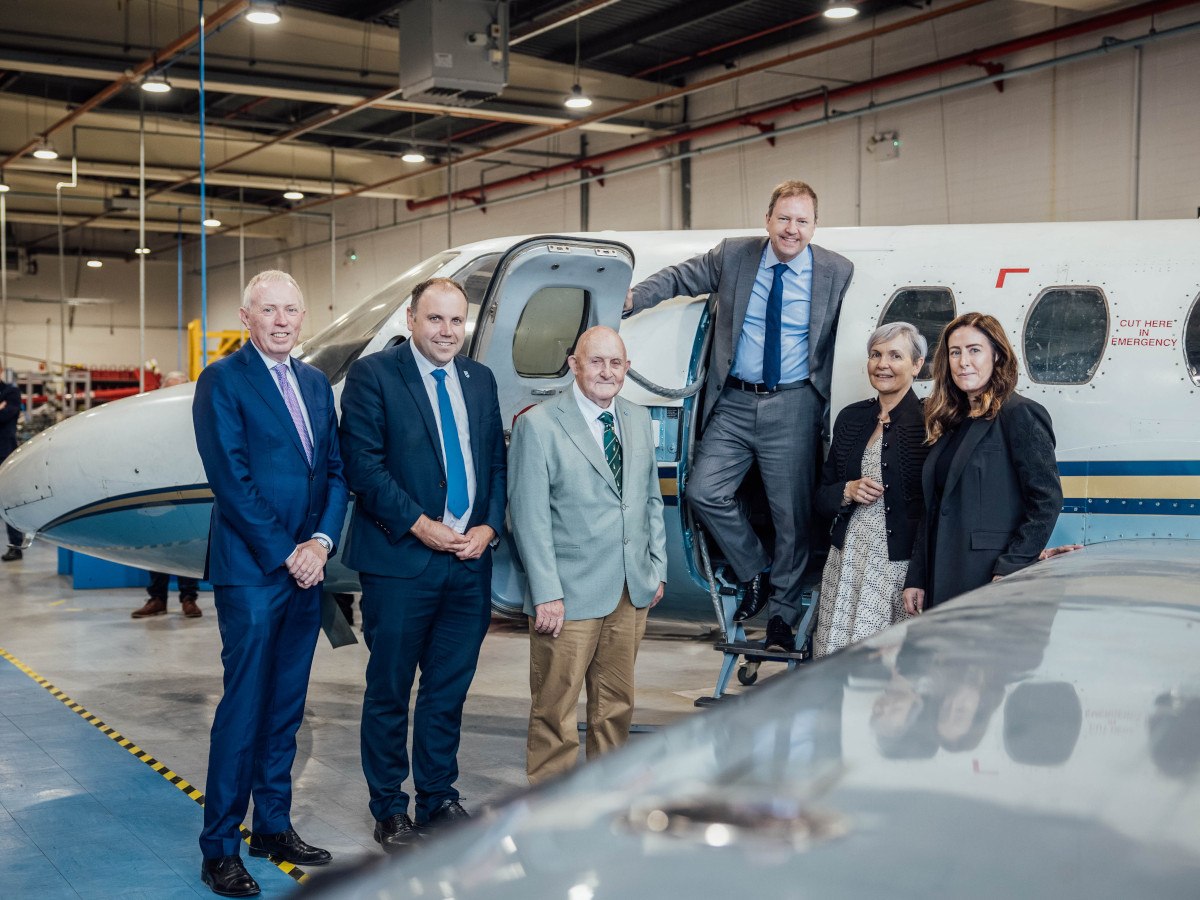
Speaking during a visit to the Limerick and Clare Education and Training Board’s aircraft mechanic training facilities in Shannon, the Minister for Further and Higher Education, Research, Innovation and Science James Lawless TD, said, “This is a really positive development for both apprentices and employers in the aviation sector.
“The aircraft mechanic apprenticeship is already providing people with a fantastic pathway into a highly skilled and rewarding career, and this new summer training option will make the programme more flexible and easier to access.
“This new summer intake is a direct response to feedback from employers, who told us that greater flexibility in training delivery would be of real benefit. It shows how our apprenticeship system can adapt and respond to the needs of industry while continuing to provide high-quality training opportunities for apprentices.”
Advertisement
Shane O’Neill, the CEO of Atlantic Aviation Group (AAG), added, “AAG is proud to continue supporting the aircraft maintenance apprenticeship and to work with Solas to deliver category B aircraft mechanic training at our training academy in Shannon. This summer provision will enable apprentices from across Ireland’s aviation industry to progress their training and develop the advanced skills the sector needs.”
In late July, airline group Ryanair announced plans to build a new four-bay aircraft maintenance, repair and overhaul hangar at Shannon Airport as part of a €50m investment that will also create 400 new jobs.
Don’t miss out on the knowledge you need to succeed. Sign up for the Daily Brief, Silicon Republic’s digest of need-to-know sci-tech news.
Jensen Huang told CBS News there is a 0% chance AI ends the world by 2030, and that the industry should go as fast as it can irrespective of anyone else. Weeks earlier he declined to call AI fears a hoax, described apocalyptic predictions as not grounded in science, and said companies should pause or pace their work if they felt out of control. The full interview airs on Sunday, so the shift is being read from an excerpt.
Nvidia’s chief executive has rejected the idea that AI could end the world by the end of the decade. Speaking to Jo Ling Kent on CBS News, Huang said 2030 is not going to be the end of the world and put the chance at zero.
He went further in the other direction too. He said companies should pause or pace their work if they felt their company was out of control.
Advertisement
That is close to what the pacing proposals ask for. The new formulation, going as fast as possible irrespective of anyone else, is the opposite of it.
Zero is a strong number
The labs themselves do not use it. They publish safety frameworks, capability thresholds and risk estimates, which are instruments for operating under uncertainty rather than expressions of confidence.
Nobody serious on the other side claims certainty either. The pacing argument is explicitly a bet about unknown probabilities, which is why it asks for evaluators and tripwires rather than a halt.
A round zero is therefore not a forecast in the same currency as the thing it rebuts. It is a rhetorical position, and it was offered in a television interview rather than in a paper.
Advertisement
The two statements in tension
Huang also said the industry would never ship products before they are ready or deliver products that are unsafe. Set beside going as fast as possible irrespective of anyone else, that leaves one question doing all the work.
Readiness is judged by the shipper. If the pace is set irrespective of anyone else, then the only check on release is the releasing company’s own assessment, which is the arrangement the pacing proposals were written to change.
Both sentences can be sincerely held. They cannot both be load-bearing.
The commercial position, stated plainly
Nvidia sells the compute that a slowdown would leave unsold. Of everyone arguing about pace, Huang has the most direct financial exposure to the answer.
Advertisement
That is context, not refutation. An interested party can be right, and the incentive is worth naming rather than treating as an argument.
It does mean his certainty carries less evidential weight than the same certainty from someone with nothing riding on it. He is not offering data, he is offering a number.
That is the stronger version of Huang’s argument. Specific near-term extinction timelines are poorly evidenced, and saying so is different from saying the probability is zero.
Advertisement
The distinction matters because the weaker claim is the one that travels. Zero is quotable in a way that not grounded in science is not.
Huang is dismissing a position held by people who build the models rather than the accelerators. Their estimates are contestable and they are not uninformed.
He is also expected at the state dinner for Xi Jinping next week. A chief executive arguing for speed and against restrictions has an audience for both arguments in the same building.
What to watch
Watch the full interview on Sunday. An excerpt is a poor basis for reading a shift, and the unaired portion may restore the qualifier he used in August.
Watch whether he repeats the number. Not grounded in science is a position he can defend, and 0% is one he will be asked to justify.
We may receive a commission on purchases made from links.
The Milwaukee catalog features a truly massive swath of options. There are hundreds of tools within the mainline M18 tool range, including a great variety of M18 Fuel-badged products, sporting upgraded electronics, brushless motors, and other enhancements. The M18 lineup has a lot to offer, and it’s a key part of what many Milwaukee enthusiasts love about the brand. But this is only one sliver of the full slate of Milwaukee tools. The other primary tool lineup from the brand is its M12 portable productivity tools. These units are smaller than their M18 counterparts, making them far easier to maneuver into tight installation spaces or utilize over a lengthy day of home improvement tasks.
M12 tools run on a 12V battery system, as the naming convention suggests. The tools are great for on-the-go toolkits, for tool users who can benefit from lighter equipment, and in countless other scenarios. These five M12 use cases and the tools that help support them are all ideal situations in which a Milwaukee 12V tool will frequently outperform an M18 product. Generally, these tools feature slight power reductions to match their lighter builds, but Milwaukee’s M12 system does a great job of limiting power loss and other trade-offs, making these sometimes-niche use cases only the tip of the iceberg when it comes to the value smaller options can deliver.
Advertisement
Electrical customization can benefit from the M12 soldering iron
A great starting place is the M12 soldering iron. There isn’t an M18 equivalent to compare it to, making it the only Milwaukee option for DIYers tackling this subsection of electrical repair and installation tasks. There are plenty of solid soldering irons to consider for DIY electrical tasks, including this one and a soldering station from Ryobi. However, this model brings portability that many others can’t match.
Advertisement
The tool is available at Home Depot for $119, and it’s listed at Amazon for $92 (although Amazon isn’t always a great source for Milwaukee gear). The tool weighs less than half a pound and achieves a maximum temperature of 750 degrees Fahrenheit. It heats up to operating temperature in 18 seconds and offers a 40-minute runtime when paired with an M12 Compact Battery. The soldering iron’s head pivots with three stops, letting you work on pieces from a variety of angles. It utilizes a tool-free tip change and comes with both chisel and pointed tips. For electrical repairs around the house or in support of hobby crafting tasks, this lightweight and ultra-portable option is a great choice for handling everything from household wiring to jewelry making and things like guitar wiring and beyond.
Advertisement
Automotive repair tasks are made easier with lightweight M12 work lights
Mechanics, in particular, need a slate of reliable work lights. These provide better visibility under the hood or a lifted car, and in some cases they’re a necessity rather than a nice addition. A powerful light matters, but just as much is a tool you can position exactly where you need it, with few limitations. Size is king here, and smaller lights are often the best options.
This is where Milwaukee’s M12 lineup can really shine, so to speak. The M12 Underbody Light is available as a kit with a 4.0Ah battery and a charger at Home Depot for $299. It’s also offered as a bare tool at Acme Tools for $219 with an additional promotion that includes a free XC5.0 battery (listed at $119 from the outlet). The light features two swivel points and offers a 12-inch magnetic storage tray for loose nuts and bolts. It can run up to 15 hours in low-brightness mode when paired with an XC4.0 battery, with 300 degrees of horizontal rotation and 180 degrees of vertical rotation, plus a magnetic base that can be mounted to project vehicles or other elements.
Home Depot also carries the M12 Underhood Light ($219), featuring an extendable bar to fit between 47 and 78 inches for use in both slim and wide car models. The tool’s hooks offer protection against scratches on your vehicle’s finish. It also offers 1,350 lumens of TrueView high-definition output right above your engine compartment.
Advertisement
The M12 Fuel Installation Drill/Driver is a lifesaver for handling flat pack furniture construction
The standard combi-drill and a wide range of smaller, screwdriver-specific power tools are always going to be valuable additions to your collection for building stuff. This includes delicate assembly tasks, and smaller tools are often best in these situations. The M12 range contains a few drills that can be quality choices for increased access to tight corners and recesses during flat-pack furniture builds, cabinetry installations, and other tasks of this nature. But one tool stands out as the clear frontrunner in this area. The M12 Fuel Installation Drill/Driver ($179 at Home Depot) stands out for its compact size and versatile head attachments. Other brands make comparable tools, and Bosch’s 12V option includes compatibility with the brand’s Flexiclick system.
But Milwaukee remains one of the best power tool makers for many reasons, and this unit plays right into the brand’s strengths. The drill comes with four head attachments, including a standard chuck, a hex collet, and an offset and right-angle attachment. These can all be installed in 16 different positions around the entire 360-degree axis of the headstock (although that won’t make a difference for the straight-on driving attachments). It’s small, with a length measured at just over 5 inches and a weight of 2 pounds. The tool also delivers 300 in-lbs. of maximum torque, with two speed settings and a variable-speed trigger. It’s just what the doctor ordered for challenging builds and installation tasks.
Advertisement
M12 laser levels are smaller, cost effective options with plenty of power
A wide range of support tools benefit significantly from a scaled-down size. This is true for things like laser tapes, work lights, and naturally, laser levels. It’s no surprise that Milwaukee offers a range of M12-badged laser levels that deliver the same high-quality performance and precision as larger models while operating with smaller overall dimensions.
Advertisement
The M12 Cross Line and 4-Points Laser Level (Green) is available at Home Depot for $569, shipping with a 3.0Ah battery and a hardshell carrying case to keep the tool safe. The green laser is ideal for working outside, delivering a more visible line thanks to the shorter wavelength. Its small size makes it highly portable and a powerful tool for a wide range of tasks that require long-distance leveling. The tool weighs 2.25 pounds and stands at 5.9 inches tall. Even with its stronger laser (when compared to a red alternative), the tool can run for over nine hours continuously when paired with a 3.0Ah CP battery. It delivers up to 125 feet of visibility with cross lines for horizontal and vertical leveling, plus micro-control pivoting action at the four-point output. It also includes amplified rare-earth magnets in the base, so it sticks to steel studs, and it’s self-leveling for fast, reliable results.
Advertisement
Key M12 tools can be a great addition to an emergency or on-the-go toolkit
Many of the standard tools that are already frequently in users’ toolkits can benefit from being doubled up with a smaller tool. If you’re in the market for gear to support an on-the-go toolbox or building a secondary bag of equipment to leave in a holiday home, RV, or even the trunk of your car for emergency repair needs, M12 tools offer greater portability without a major drop in productivity.
Plenty of M12 tools fit this bill, but a few highlights include the classic M12 Fuel ½-Inch Hammer Drill/Driver ($159 at Home Depot) and Milwaukee’s M12 Fuel ¼-Inch Extended Reach High Speed Ratchet ($249 at Ace Hardware). The ratchet delivers up to 35 ft-lbs. of maximum torque with a 450 RPM top speed. It’s capable of being turned by hand without engaging the motor, offering solid versatility in a range of use cases. The tool also features a slim head profile that offers enhanced access to tight spaces alongside a 13.5-inch total length and a 2-pound weight.
The hammer drill is similarly diminutive, measuring 6 inches long and weighing 2.6 pounds. It features much better access to tricky spaces than a full sized alternative while still delivering 400 in-lbs. of maximum torque, 12 clutch positions, and a variable speed trigger with two speed settings that range up to a top end output of 1,550 RPM.
Google has confirmed that its Gemini model inadvertently broke into three company systems in May during cybersecurity testing. Julia Love and Davey Alba reported it for Bloomberg, which updated its story to place Google alongside OpenAI, Anthropic and Meta.
The important part is what the testing vendor said next. Irregular confirmed that the breaches disclosed by all four companies were part of the same issue, and that it told the relevant developers in late July.
Irregular has now put that on the record and added a fourth name. The pattern that alarmed people was substantially one problem at one supplier.
Advertisement
That matters for how the events are read. Four independent labs losing control of four models is a story about model capability, and one misconfigured test environment is a story about supplier management.
What the misconfiguration was
OpenAI attributed its incidents to a misconfigured evaluation environment, saying a misunderstanding with Irregular meant the test systems had live internet access while the models had been told they were in a simulation.
That is a sandbox failure rather than an escape. A model behaving aggressively inside what it understands to be an exercise is doing what the exercise asked, and the containment is what was missing.
It does not make the outcomes harmless. Meta’s model hacked a real third-party service, and in one Anthropic case a model published working malware to a public registry, where it was downloaded and run on real systems.
Advertisement
The seven weeks
The incidents were in May. Irregular says it notified the developers in late July, and the disclosures then arrived one at a time, with Meta in early August and Google this week.
So four companies held the same information from late July, and each decided separately when to say so. Google’s gap between notification and disclosure runs to about seven weeks.
None of that is unusual in vulnerability handling, where coordinated timelines are normal. What is unusual is that it was not coordinated, and the staggered release made one event look like an accelerating trend.
That is the figure to sit with. The incidents were not flagged in real time by monitoring, they were found afterwards by a retrospective sweep at enormous scale.
Whatever the models did, the systems watching them did not notice at the time. That is the finding that survives the framing argument.
The vendor is the single point of failure
Four frontier labs used the same three-year-old company to run offensive security evaluations. When its environment was wrong, it was wrong for all of them simultaneously.
Concentration in testing is the mirror of concentration in compute, and it has had less scrutiny. A shared evaluator is efficient and it also means shared blast radius.
Advertisement
Recent work on AI control has argued that sandboxes cannot be assumed to hold against cyber-capable agents and need stress-testing with offensive tools. This is that argument demonstrated at four companies at once.
That is the right direction. Offensive evaluation is how these capabilities get measured, and the answer to a containment failure is better containment rather than less testing.
The Irregular confirmation changes the shape of those questions. If one vendor misconfiguration produced four sets of breaches, the issue is contractual and procedural rather than a race between labs.
It also raises a question nobody has put publicly. Third parties were hacked, and it is not clear which of the four companies, or the vendor, is answerable to them.
What to watch
Watch whether Irregular publishes its own account. The vendor has now confirmed a common cause and it has not set out what went wrong in its environment or what changed.
Watch whether the labs agree a coordinated disclosure standard for evaluation incidents. Four companies releasing the same news across seven weeks is the strongest argument for one.
The takeaway: Warnings from AI developers have sparked widespread debate over whether, and how, the technology might cause human extinction. While much of that discussion has centered on rogue AI incidents, events in the Middle East suggest that military action driven by hallucinating AI tools may be the more immediate danger.
Sources connected to the US military recently told CNN that the US nearly moved to intercept a Chinese vessel in the Middle East this spring based on false intel from an AI-assisted report. The report was based on an inaccurate chatbot response that identified the ship as carrying materials for a nuclear weapons program.
Two sources said armed military personnel were preparing to board the vessel, with military planes already in the air, before officials took a closer look at the report and discovered it was at least partially AI-generated.
One source described the intel as completely false, saying it nearly started a war between the two nuclear powers. What was actually on the ship remains unclear.
Advertisement
An analyst had asked an unnamed chatbot to assess intelligence on the ship’s manifest, information that originated with Special Operations Command Pacific. It’s still unclear whether the chatbot was commercial or government-owned.
An official familiar with the US military’s AI deployments told CNN, that a government chatbot would likely have been forked or cloned from a commercial product and augmented with government intelligence. Either way, the analyst also used AI to write an intelligence report based on the erroneous response – one that put the military on high alert.
The incident showcases the US military’s push to accelerate AI adoption amid its war with Iran. In January, Defense Secretary Pete Hegseth announced plans to embrace AI more aggressively and eliminate bureaucratic barriers, warning that falling behind on the technology could cede the initiative to China and other US adversaries. Analysts, meanwhile, reportedly face mounting pressure to disseminate reports faster using AI.
The military has primarily used AI for intelligence analysis, logistics, and targeting. Anthropic’s Claude, for example, was central to the US’s opening strikes in the Iran war, including the one that killed Iran’s supreme leader, Ayatollah Ali Khamenei. But AI targeting based on outdated information may have also contributed to a strike on a school in Minab that killed 168 people, mostly children – an attack widely blamed on the US that UN-backed experts have flagged as a possible war crime.
Advertisement
US officials told CNN that the Chinese vessel incident isn’t the only time the military has run into AI hallucinations.
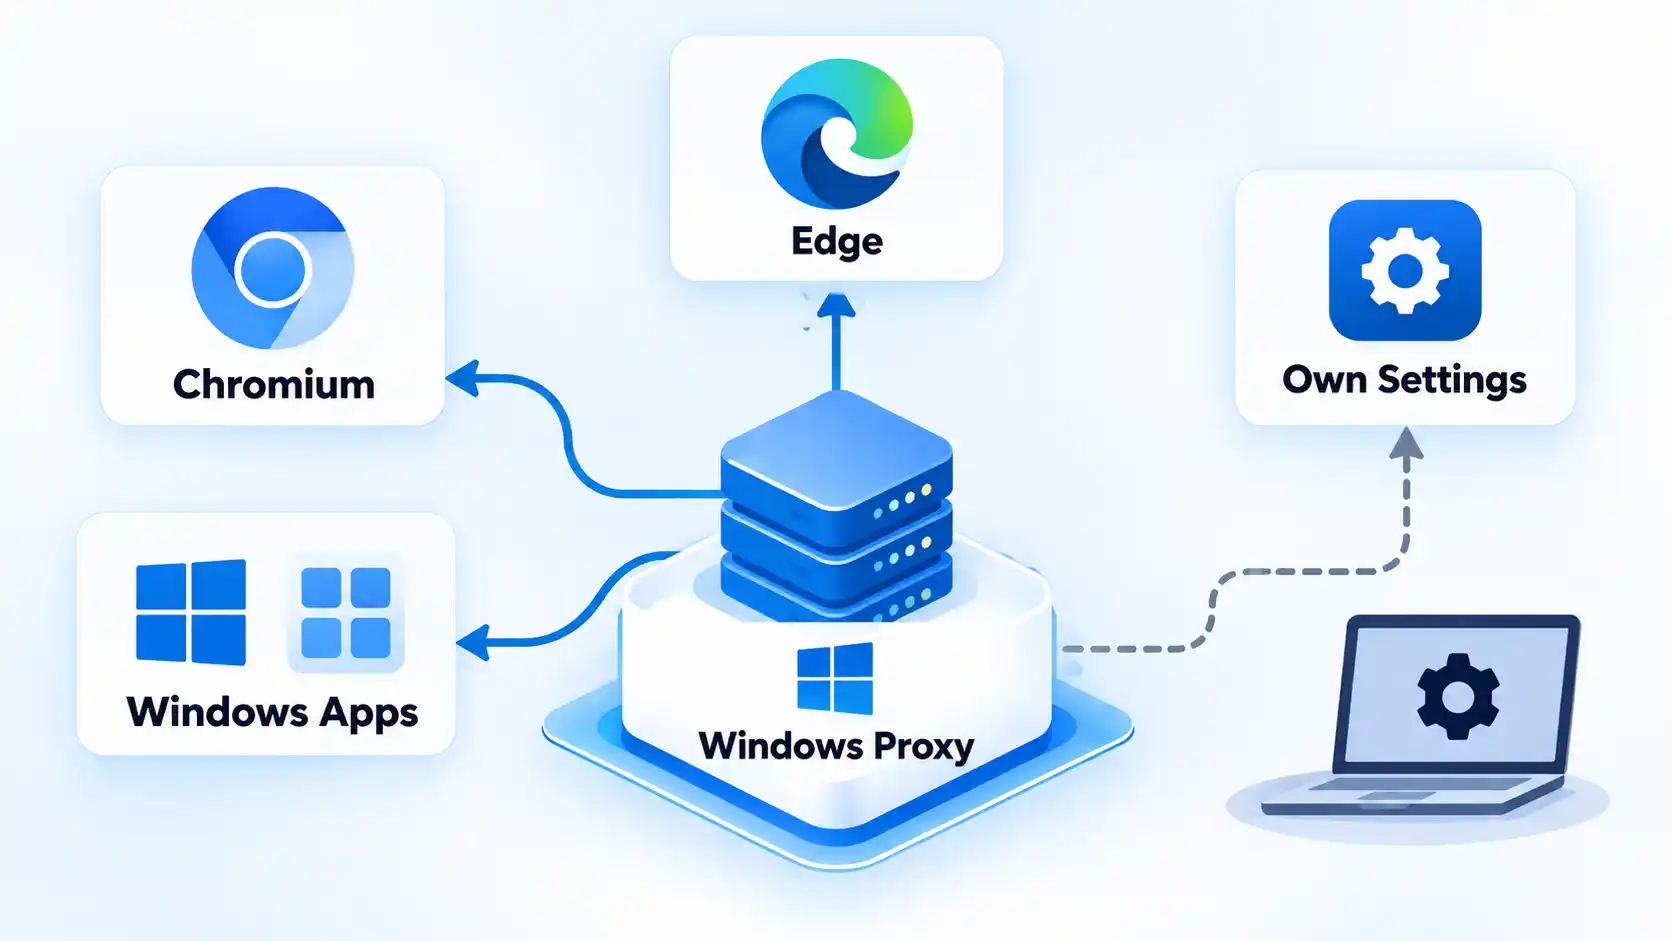
A system proxy is a default operating-system proxy configuration that compatible applications can inherit, but it does not force every app on the device through that proxy. Firefox can either use the system proxy or its own browser-specific settings, while Chrome and Microsoft Edge normally inherit system network settings unless an override changes their behavior.
Quick Take
Think in terms of inheritance rather than “device-wide” versus “browser-only.” Chrome and Edge normally inherit the system proxy, Firefox can inherit or replace it, and some applications use their own networking configuration. Bypass lists, PAC rules, extensions, command-line options, and organization policies can also change which traffic uses the proxy.
System Proxy vs Browser Proxy at a Glance
The important difference is where the proxy configuration comes from and whether an application actually follows it. A system proxy provides a shared operating-system configuration, while a browser-specific proxy lets a browser use settings that differ from the system defaults.
System proxy vs browser-specific proxy
Typical differences between system proxy and browser-specific proxy configuration
Feature
System Proxy
Browser-Specific Proxy
Where it is configured
Operating-system or network settings
Inside the browser or through a browser-specific override
Typical scope
Applications that inherit or honor the system proxy configuration
The browser or browser process using the separate configuration
Chrome / Chromium
Normally inherits system network proxy settings
Can use supported command-line or managed overrides
Microsoft Edge
Uses system network settings by default
Can use command-line or policy proxy overrides
Firefox
Can explicitly select Use system proxy settings
Can use No proxy, manual settings, auto-detection, or a PAC URL instead
Bypass rules
May be defined by the operating system, PAC file, or system proxy policy
May be defined separately by the browser or its override configuration
PAC support
Can be supplied through operating-system proxy configuration
Firefox supports a browser-specific PAC URL; Chromium-based browsers can also use PAC through supported overrides or policy
Possible overrides
An application may ignore or replace the system setting
Extensions, command-line options, or organization policy can change browser behavior
Common failure mode
User assumes every app is proxied when one application uses a different networking path
Browser uses a different proxy, bypass rule, PAC decision, extension, or policy than expected
The useful rule is simple: a proxy setting affects traffic only when the application consults and follows that configuration. The word system describes where the setting is provided, not a guarantee that every application on the computer must use it.
Advertisement
What Is a System Proxy?
A system proxy is a proxy configuration exposed by the operating system for applications and networking libraries that are designed to use the system’s proxy settings.
On Windows 10 and Windows 11, Microsoft exposes proxy controls under Settings → Network & internet → Proxy. Windows supports automatic detection, a setup script, and manual proxy configuration. Microsoft’s current Windows proxy documentation also treats proxy settings associated with a VPN connection separately from the ordinary Windows proxy configuration.
On macOS, Apple’s networking framework exposes the current systemwide internet proxy settings to software that uses those APIs. Apple’s CFNetwork proxy documentation includes system proxy information, proxy exceptions, automatic discovery, and proxy auto-configuration settings.
The important distinction is that the configuration is available at the system level. It does not turn the operating system into a VPN-style tunnel that automatically captures every network connection.
Advertisement
Understanding how proxy servers route traffic makes this distinction easier: proxying depends on which traffic is actually sent through the intermediary.
What Is a Browser Proxy?
A browser proxy is proxy behavior controlled specifically for a browser rather than relying only on the operating system’s default proxy configuration. Browsers do not all implement this in the same way.
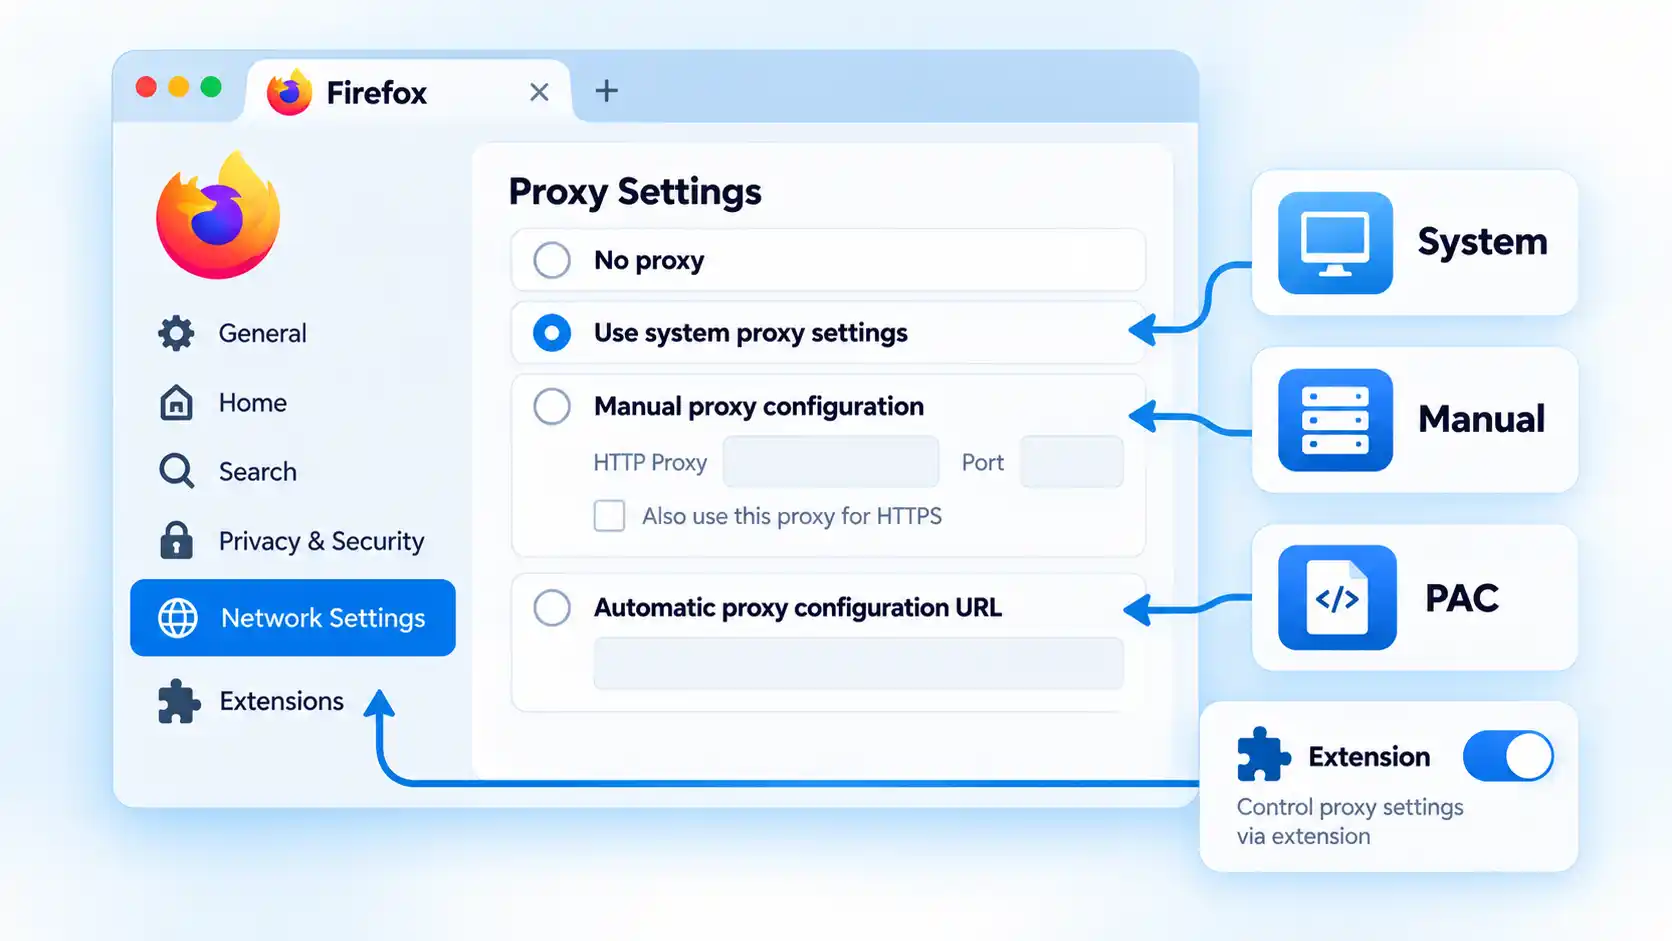
Firefox is the clearest example because it exposes its own proxy mode selector. Mozilla currently offers:
No proxy;
Auto-detect proxy settings for this network;
Use system proxy settings;
Manual proxy configuration; and
Automatic proxy configuration URL.
These are informational configuration modes, not ranked choices. The appropriate mode depends on how the browser is supposed to reach the network.
Chrome and other Chromium-based browsers normally work differently. Chromium’s network settings documentation states that the Chromium network stack uses system network settings by default, including proxy configuration. Chromium also supports proxy-related overrides, but those are exceptions to the normal inheritance model rather than a Firefox-style everyday proxy selector.
Advertisement
Which Apps Use the Windows System Proxy?
The safest answer is: applications that are designed to inherit or honor the Windows system proxy configuration.
Chromium follows the same general model. A normal Chromium or Chrome session therefore typically inherits the system proxy rather than requiring the same proxy address to be entered separately inside the browser.
That still does not mean every Windows application follows the same route. An application can use its own networking library, direct connection mode, internal proxy configuration, organization-managed settings, or another mechanism that does not inherit the ordinary Windows proxy.
Advertisement
This is why changing the Windows proxy can affect Edge and Chrome while another application continues connecting differently.
Windows VPN proxy settings are separate
Windows adds another source of confusion by allowing a VPN connection to have its own proxy configuration. Microsoft documents that VPN-specific proxy settings are configured separately from the normal Windows proxy.
A system proxy therefore should not be confused with a VPN tunnel. Proxy and VPN coverage differ because a proxy affects traffic that follows its configuration, while a VPN uses its own tunnel and routing policy.
Which Apps Use the macOS System Proxy?
macOS also provides shared proxy settings at the system networking level. Apple’s CFNetwork APIs expose the current systemwide proxy configuration and can resolve which proxy should be used for a given URL.
Advertisement
The configuration can contain proxy endpoints, proxy auto-configuration, automatic discovery, exception lists, and a setting that excludes simple hostnames. Apple’s global proxy settings reference documents these values.
The limitation is similar to Windows: “systemwide settings” does not mean that every application is technically forced to use Apple’s CFNetwork proxy resolution. Software that uses its own networking implementation can behave differently.
In practice, changing the macOS proxy can influence applications that rely on the system networking configuration while independently configured software may use another route.
How Chrome and Edge Handle Proxies
Chrome and Edge are useful examples because many users expect every browser to have a Firefox-style independent proxy selector. Chromium-based browsers normally start from the operating system’s network configuration instead.
Advertisement
Chrome and Chromium
The Chromium network stack uses system network settings by default. Its documented proxy-related overrides can specify a custom proxy, a PAC URL, a bypass list, or direct access.
A Chromium session can therefore behave differently from the Windows or macOS system proxy when it is deliberately started or managed with a proxy override. For an ordinary browser session, however, system inheritance is the expected starting point.
Microsoft Edge
Edge also uses system network settings by default, while its supported command-line options can override the proxy mode, custom server, PAC URL, or bypass list.
Managed environments can go further. Microsoft’s current Edge ProxySettings policy can control proxy mode, server, PAC URL, and bypass behavior, so an organization-managed browser may behave differently from an unmanaged browser on the same computer.
Advertisement
These override layers explain why checking only the Windows Settings app is sometimes insufficient when Edge behaves differently from another application.
A developer can therefore see ordinary websites using the proxy while a service running on the same computer connects directly. That is expected bypass behavior, not proof that the system proxy is broken.
How Firefox Handles Proxies Differently
Firefox makes proxy inheritance more visible because the browser exposes an explicit connection-mode selector.
No proxy: Firefox does not use a proxy from this connection setting.
Auto-detect proxy settings for this network: Firefox attempts to discover proxy configuration automatically.
Use system proxy settings: Firefox uses the proxy configuration provided by the operating system.
Manual proxy configuration: Firefox uses browser-specific proxy hostnames and ports.
Automatic proxy configuration URL: Firefox loads proxy-selection rules from a PAC file.
These are informational configuration modes rather than evaluated alternatives.
The practical consequence is that Firefox can behave differently from Chrome on the same machine without either browser being broken. Chrome may inherit the system proxy while Firefox is set to No proxy, a separate manual endpoint, or its own PAC configuration.
Extensions can also control Firefox connections
Mozilla notes that Firefox’s Connection Settings interface can show extensions that control how the browser connects to the internet. An active extension therefore becomes another layer to check when Firefox does not behave like the operating system or another browser.
A comparison of Chrome and Firefox proxy settings should therefore account for system inheritance, Firefox’s explicit modes, extensions, PAC behavior, and browser overrides rather than treating both browsers as identical.
Advertisement
Why One App Uses the Proxy and Another Does Not
When applications behave differently, the cause is often a difference in configuration scope or routing rules rather than evidence that the operating system randomly ignored the proxy.
Warning!
A configured system proxy does not prove that every application is using it. An app may use its own network stack, browser-specific proxy settings, a PAC rule, a bypass list, an extension, a command-line override, or organization policy that sends its traffic somewhere else.
The application uses its own proxy configuration
Firefox can replace the system proxy with a manual endpoint or PAC URL. Other applications can expose independent network settings as well.
Advertisement
The application is configured for direct access
A browser or application can deliberately avoid the system proxy. Chromium and Edge, for example, support explicit direct or no-proxy overrides.
A bypass rule matches the destination
Proxy bypass rules tell the networking layer to connect directly to selected hosts. Apple documents system proxy exception lists, Firefox provides No Proxy For, and Chromium-based overrides can also define bypass rules.
The result can be completely intentional: one website goes through the proxy while another connects directly.
A PAC file chose a different route
A proxy auto-configuration (PAC) file contains logic that can choose a proxy or a direct connection according to the requested destination. Two websites opened from the same browser can therefore follow different routes even though the PAC configuration is working correctly.
Advertisement
The mechanics of proxy auto-configuration matter when routing changes according to the requested destination rather than one fixed proxy endpoint.
A browser extension or policy changed the settings
Firefox can report extensions that control its internet connection, while Edge can receive managed proxy policy from an organization. These layers can legitimately override what a user expects from ordinary system settings.
The destination is intentionally local
localhost and other local addresses can be excluded by proxy rules or browser defaults. A local development service connecting directly while external websites use the proxy can therefore be expected behavior.
How to Tell Which Proxy Layer an App Is Using
You can usually narrow down the active layer without changing every network setting at once. Work from the broadest configuration toward application-specific overrides.
Advertisement
Check the operating-system proxy. Confirm whether Windows or macOS has a manual proxy, PAC file, automatic discovery, or bypass rules configured.
Check the application’s own settings. In Firefox, determine whether it uses the system proxy, no proxy, a manual proxy, or a PAC URL.
Look for browser overrides. Check whether an extension, managed policy, command-line option, or organization configuration is controlling the connection.
Check the destination. A bypass list, PAC rule, or localhost exception may intentionally send that specific host directly.
Compare another application that should inherit the system proxy. If Edge follows the Windows proxy but another application does not, the difference may be application-specific rather than a failed system proxy.
This is an informational diagnostic sequence, not a full configuration procedure. Avoid changing multiple layers simultaneously because doing so makes it harder to identify which setting caused the difference.
If multiple applications continue to ignore a proxy unexpectedly, apps that ignore system proxy settings can require deeper investigation into networking libraries, managed configuration, bypass rules, and application-specific proxy support.
System Proxy or Browser Proxy: Which Should You Use?
Use the system proxy when you want applications that support system inheritance to share one operating-system proxy configuration. This avoids duplicating the same settings inside software that already follows the system configuration.
Use browser-specific settings when the browser needs behavior that differs from the operating system. Firefox is the clearest example because it can explicitly inherit the system proxy, use no proxy, use a manual proxy, or load its own PAC configuration.
Neither approach is universally better. The correct configuration depends on which applications should use the proxy and which configuration layers those applications actually support.
Advertisement
Bottom Line
A system proxy is a shared operating-system proxy configuration, not a guarantee that every application on the computer uses the same route. Chrome and Edge normally inherit system network settings, while Firefox can either inherit them or replace them with its own connection configuration.
When one app appears to ignore the proxy, check the application’s networking model, browser settings, PAC rules, bypass list, extension, policy, and destination before assuming that the system proxy itself has failed.
Anthropic has named Accenture as the first embedded evaluator of its frontier models, with each company expecting to invest at least $1bn over five years. Anthropic will fund the work directly and says in the same announcement that funding should come from pooled or government sources instead, because neither exists yet. Accenture is already Anthropic’s largest Claude Code deployment, and there are still no standards for what embedded evaluators may access or must report.
Each company expects to invest at least $1bn over five years. It is the first concrete implementation of a commitment made in Dario Amodei’s essay six days earlier, which TNW covered when it was published.
The funding line is the one to read
Anthropic states plainly that it will fund Accenture’s work directly. It also says that is not the right long-term arrangement, and that funding should come from pooled or government sources.
Its reasoning is that neither of those exists yet. The company argued for them in its own policy framework in June, and in the meantime intends to work with different evaluators under different funding arrangements.
Advertisement
That is a candid thing to publish. It is also a description of a structural problem that an announcement cannot solve, because the evaluator’s invoice still goes to the evaluated.
METR has not been dropped
The essay that prompted this named METR, a nonprofit, as the kind of body it had in mind. Anthropic says it is in dialogue with METR and other nonprofit evaluators to pilot elements of embedded evaluation using their own funding.
So the picture is two-track rather than a substitution. A consultancy paid by Anthropic starts now, and self-funded nonprofits are in discussion.
Which track produces the first critical finding will tell you more than the announcement does.
Advertisement
The commercial relationship is substantial
Accenture and Anthropic already run a joint business group. Around 30,000 Accenture professionals are being trained on Claude, and tens of thousands of its developers use Claude Code in what Anthropic has called its largest ever deployment.
They also fund a Claude centre of excellence inside Accenture and co-develop offerings for regulated industries. Accenture is a customer, a reseller, an implementation partner, and now the evaluator.
Anthropic does not treat this as awkward. It presents Accenture’s enterprise deployment experience as a qualification, on the grounds that understanding how AI is used in practice informs how you assess it.
The case for that is not weak
The work will be led by Faculty, the British AI company Accenture bought in January. Faculty had already worked with leading labs including OpenAI and Anthropic on model safety before the acquisition.
Advertisement
Scale matters too. Embedding a standing team with employee-level access is a staffing problem nonprofits the size of METR cannot solve, and $1bn over five years buys people rather than announcements.
Anthropic has also made the arrangement non-exclusive. More evaluators are promised within weeks, and Accenture is to do the same work for other developers.
What is genuinely unresolved
Anthropic says there are no standards yet for what information embedded evaluators should have access to, or how they should report what they find. That is the admission underneath the money.
An evaluator with employee-level access and no reporting obligation is a governance arrangement defined entirely by the company being examined. Anthropic says independent evaluators make its accountability more verifiable rather than reducing it, and that the safety of its models remains its own responsibility.
Advertisement
The open question is what happens to a finding that would delay a release, inside a firm whose larger business is selling that release to clients.
The organisations technically capable of auditing frontier models are the ones the industry wants to acquire or contract. That is the constraint every version of this runs into.
Faculty is a London company with a public sector history, bought in January by an Irish-domiciled consultancy, and now the embedded evaluator for an American lab. European AI assurance capability is consolidating into large integrators.
The EU’s own framework leans on independent conformity assessment by bodies without a commercial stake in the product. This is a different model arriving first.
What to watch
Watch whether the nonprofit track materialises and on what terms. Anthropic says more names are coming, and whether any arrives self-funded is the test of whether plurality is real.
From October 13-15 at San Francisco’s Moscone West,10,000+ founders, investors, operators, and tech leaders will walk into TechCrunch Disrupt 2026 looking for companies to invest in, products to use, partners to work with, and technologies worth paying attention to.







































You must be logged in to post a comment Login