

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Tech
The Pixel Watch 5’s long-awaited Health Guardian features are finally here

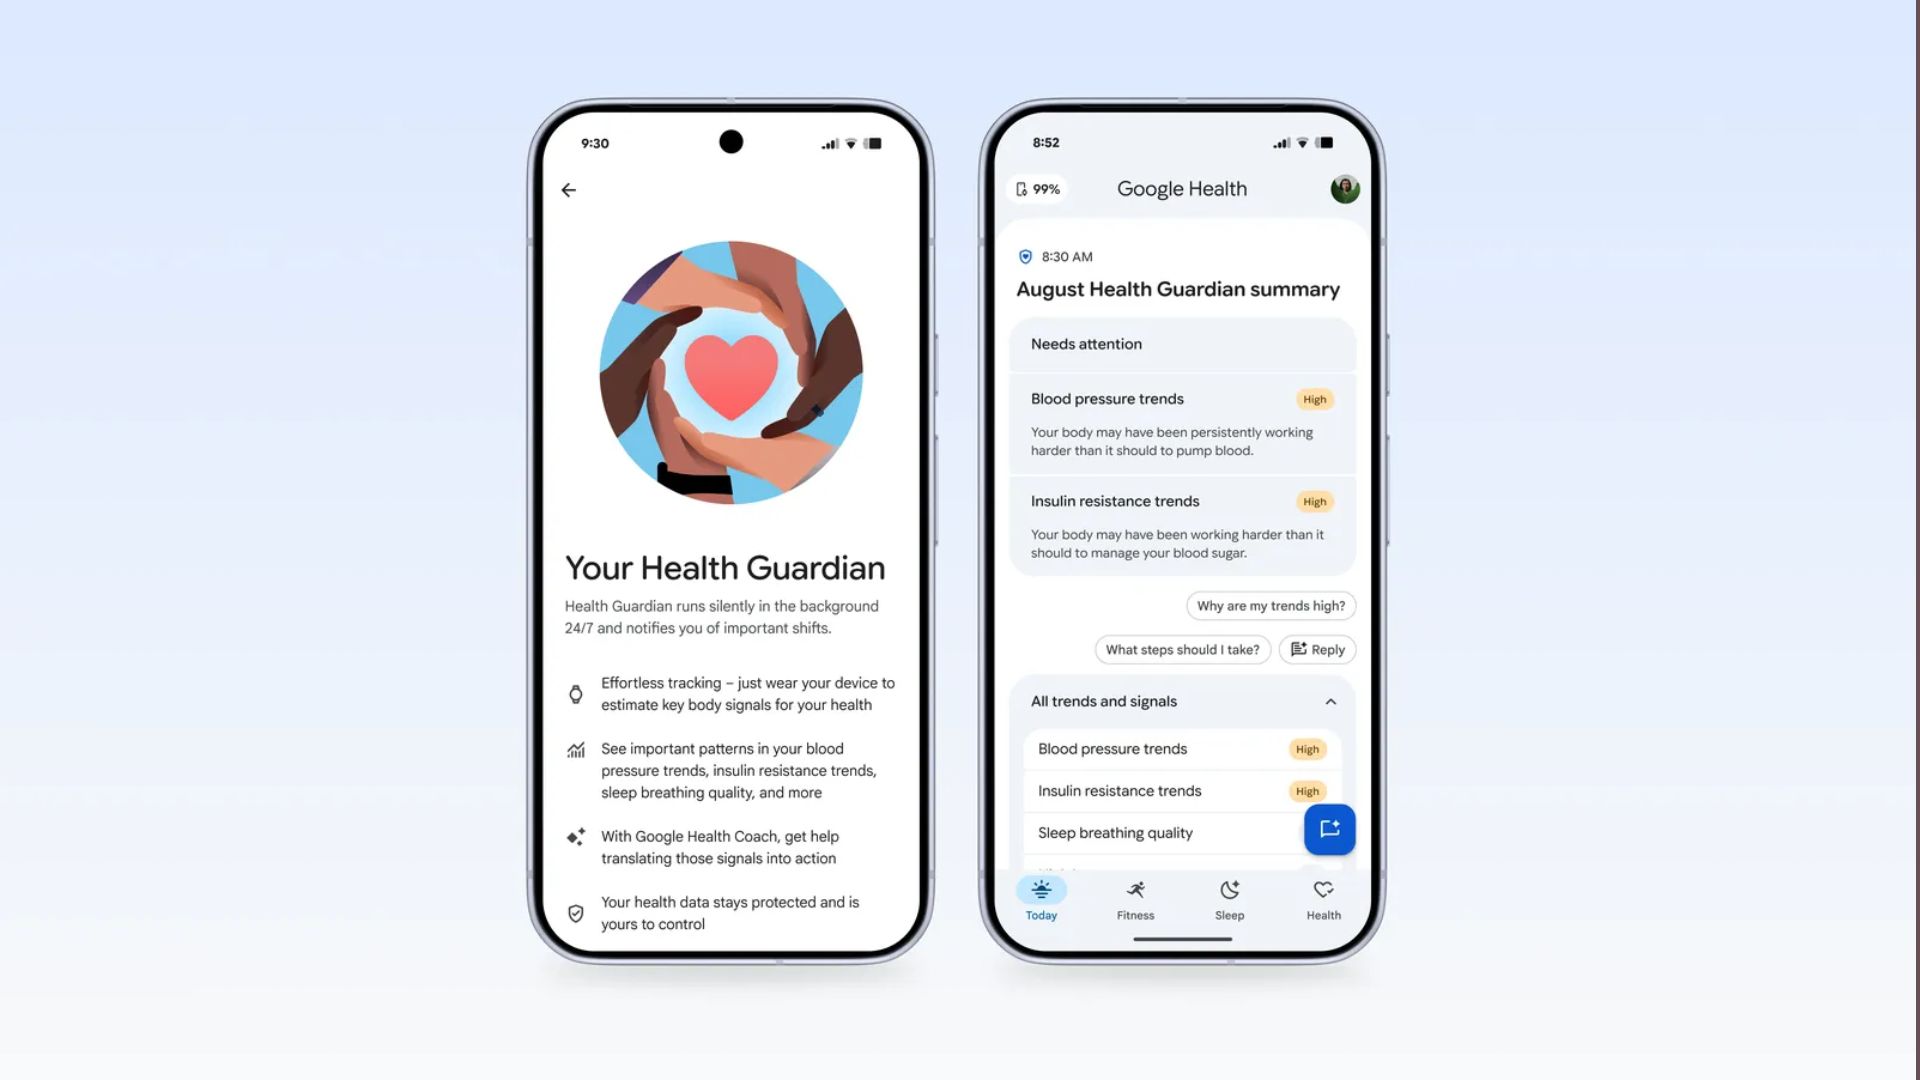
Google is finally rolling out the Pixel Watch’s long-awaited Health Guardian features, bringing blood pressure trends, insulin resistance trends and sleep breathing quality metrics to the Google Health app.
The new tools start appearing for eligible users today, September 24, with monthly trend reports expected to arrive in October. They’re available for free on the Pixel Watch 3, Pixel Watch 4 and Pixel Watch 5, while Fitbit Air users will eventually get access through a Google Health Premium subscription.
The features are designed to track subtle changes in your health over time rather than simply giving you another number to check. Google says they work in the background, using physiological data collected over weeks to identify longer-term trends.
Insulin Resistance Trends analyses multi-week physiological data to track changes in metabolic health without requiring a blood sample. Blood Pressure Trends uses pulse and motion patterns to estimate blood pressure trends without a cuff or manual calibration. Google recommends confirming any persistent changes with a home blood pressure monitor or healthcare professional.
There’s also Sleep Breathing Quality Trends, which gives you a daily view of how much of your sleep was spent with optimal breathing, with those measurements feeding into a monthly assessment.
These three features join the wider Health Guardian suite, which also includes Breathing Emergency Detection on the Pixel Watch 4 and 5 in select European countries. The opt-in feature can detect a dangerously low drop in blood oxygen and, if the wearer becomes unresponsive, can automatically call emergency services and, where applicable, emergency contacts.
Google says the features are backed by clinical validation. Its insulin resistance model was trained on more than one trillion minutes of sensor data from five million opted-in users, with accuracy validated against standard clinical blood tests and published in Nature. Its blood pressure system uses the WavesFM foundation model, trained on billions of minutes of heart and movement data.
Google Health Coach is also built into the experience, helping users interpret the information and offering guidance around lifestyle changes.
The company is positioning Health Guardian as a way to spot changes earlier, rather than replacing medical testing or professional advice. For Pixel Watch owners, though, it adds a considerably more detailed layer of health tracking to the smartwatch.
Continue Reading
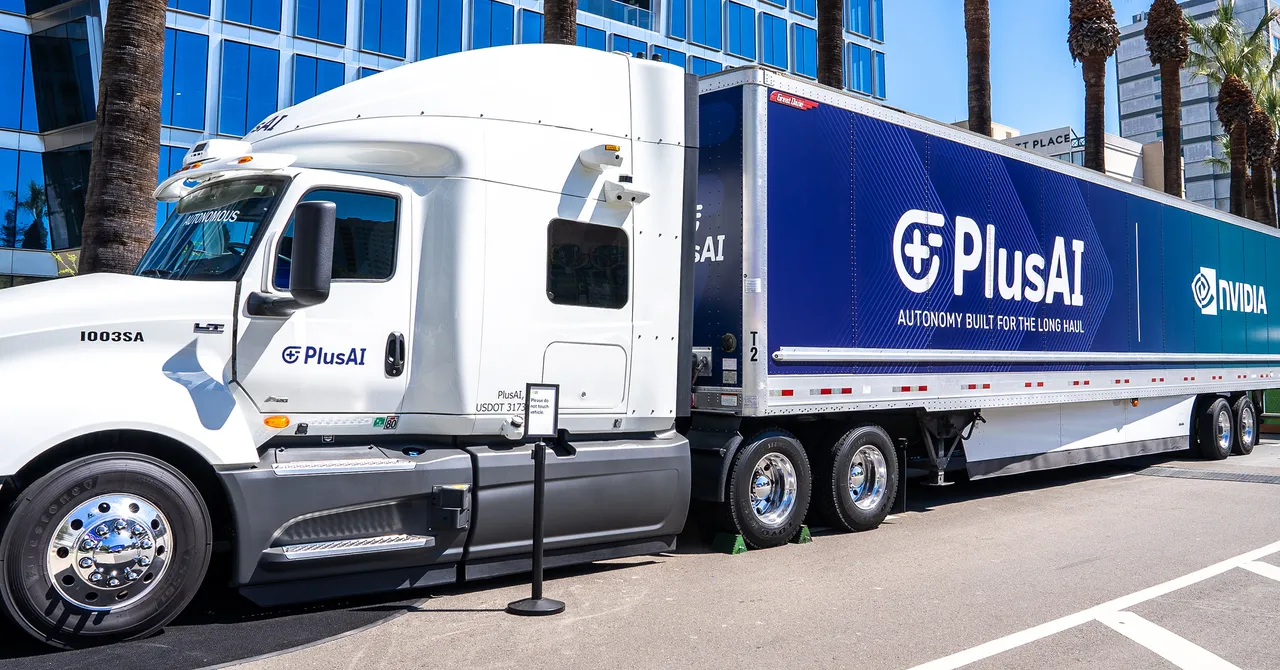
On Thursday morning, a top executive at self-driving truck developer PlusAI received an unexpected congratulatory text message from an acquaintance. “I have been proud of you for your adventure and success at Plus. Just saw two of your trucks near my work place! :)” the message said.
But PlusAI’s trucks weren’t supposed to be near this person’s office, in Newark, California. As of the last the company knew, the trailers were docked outside its warehouse, half a mile away. Soon, according to a police statement, cops were on the scene to help recover the two trailers, emblazoned with logos for PlusAI and Nvidia, the most valuable company in the world. The two companies are working together on AI software and autonomous truck technology.
That’s when PlusAI employees gave police a hint as to why whoever hooked their own cabs up to the trailers and drove away might have abandoned the whole thing after breaking them open: Each trailer was full of about 20,000 pounds of sand.
“PlusAI uses simulated loads in its trailers to assist with research and development testing,” says Lauren Kwan, a company spokesperson. The trailers were recovered with “40,000 pounds of sand intact.”
PlusAI’s tech-enabled truck cabs—where the driver typically sits and controls the vehicle—were parked inside its warehouse and weren’t taken, Kwan says. The trailers were secured with hand locks, which were broken.
The case is under investigation, and no arrests have been made, says Amy Gee, a spokesperson for the Fremont Police Department.
Nvidia didn’t immediately respond to a request for comment.
The incident comes at a time of rising theft targeting high-value computer equipment, especially chips and other electronics meant for use in data centers. In August, WIRED revealed two California incidents in which thieves deliberately struck the vehicles of security escorts that follow high-value tech loads to ensure they reach their destinations. The trucks involved were then driven to another destination. As of August, millions of dollars of data center equipment onboard had not been recovered.
This year, thieves have also targeted Tesla batteries and various bitcoin mining machines. Authorities have arrested suspects in some cases, but many crimes remain unsolved.
Some of the most common targets of cargo theft in recent months across the US include metals and enterprise-grade computer and networking equipment, according to Verisk CargoNet, an analytics and risk assessment firm.
This story has a happier ending. By Thursday afternoon, the sand trailers were back with PlusAI, the Fremont Police Department said.

Secure file-sharing software company Kiteworks is urging customers worldwide to temporarily shut down their servers on Saturday for a six-hour window after receiving threat intelligence warning of a potentially imminent cyberattack.
According to German technology publication Heise, Kiteworks CISO Frank Balonis emailed customers warning that the company had received “credible threat intelligence from law enforcement indicating an attack on Kiteworks systems may be imminent this weekend.”
“We strongly recommend you shut down your Kiteworks system for six hours,” the notification reportedly states.
Heise says the shutdown window applies to customers worldwide, with affected time zones ranging from Australian Eastern Standard Time (AEST) to Pacific Daylight Time (PDT).
In Central Europe, customers were instructed to shut down Kiteworks systems between 4:00 a.m. and 10:00 a.m. on Saturday, September 26. In New York, the shutdown window would be from 10:00 p.m. Friday to 4:00 a.m. Saturday.
The company reportedly recommends shutting down the servers before the scheduled window and says customers should take systems offline even if they are not directly accessible from the Internet.
The company confirmed the warning to BleepingComputer, stating it received intelligence from federal authorities that a threat actor may attempt to target some customer systems.
“Kiteworks received credible threat intelligence from federal intelligence authorities indicating that a threat actor may attempt to target some Kiteworks systems for customers,” the company told BleepingComputer.
“Out of an abundance of caution, we notified customers directly and recommended a precautionary shutdown window while we and our law enforcement partners work through the matter.”
Kiteworks stressed that the warning is precautionary rather than a response to a confirmed breach.
“We are not aware of any compromise of Kiteworks systems, and this advisory is preventative rather than a response to a confirmed breach,” the company said.
“All known vulnerabilities are addressed in our current release, 9.5.1, and we continue to recommend customers run the latest version.”
Potential zero-day concerns
While Kiteworks has not confirmed that attackers are exploiting an unknown vulnerability, Heise reports that Kiteworks customer support said the shutdown recommendation is intended to protect customers against potential zero-day attacks.
“The reason we’re asking you to shut down the servers is to protect against any potential zero-day attacks,” Kiteworks support reportedly told Heise when the publication contacted the company to verify the warning.
However, neither the statement provided to BleepingComputer nor the customer notification quoted by Heise confirms that a zero-day vulnerability has been discovered or exploited.
Instead, Kiteworks says all currently known vulnerabilities are fixed in version 9.5.1 and describes the shutdown as a precaution based on intelligence received from authorities.
Kiteworks develops secure file-transfer and communications products used by government organizations, financial institutions, and enterprises.
Because secure file-sharing platforms commonly store sensitive documents, they are a valuable target for cybercriminals who conduct data-theft extortion attacks.
While it is not known which threat actor is linked to these potential attacks, the Clop extortion gang has a long history of targeting enterprise platforms in data-theft attacks, including Accellion FTA, GoAnywhere MFT, SolarWinds Serv-U FTP, Cleo, and MOVEit Transfer.
The U.S. Department of State now offers a $10 million reward for any information linking the cybercrime gang’s attacks to a foreign government.

Local governments across China are competing to attract AI filmmakers with subsidised rent, living allowances and cheap computing power, Reuters reported on Friday.
Zhu Zhili set up an AI film studio in Shenzhen two years ago. He told the agency that officials from big cities and small towns now call him every day, asking him to move his technology or his company to them.
He also runs the AI-generated content department at China Wit Media, a Shenzhen production company.
The incentives follow the playbook China used to build its electric vehicle, solar and robotics industries.
In May, Shanghai started giving computing capacity and hosting AI models to micro-drama producers. Beijing has set up a 260 million yuan ($39 million) fund for film and video technology.
Beijing’s Huairou district, a centre of the Chinese film industry, also hands out vouchers that cut computing bills for AI short dramas. Shenzhen, for its part, offers technical support and cheaper rent to AI film talent.
Production costs have dropped fast. According to state broadcaster CCTV, making a minute of AI short drama cost 5,000 yuan at the start of 2026 and only a few hundred yuan by mid-year.
Pan Xiaojun, a film-directing student in Hainan, told Reuters he could create a surreal wedding scene with AI for 1,400 yuan, against 60,000 yuan for a conventional shoot. Local subsidies and rent waivers brought his computing costs down further.
Streaming platforms have joined in. iQIYI chief executive Gong Yu said in August that the company was going all in on AI, and it now subsidises some creators who publish AI content on its service.
The National Film Administration has also cleared Sanxingdui: Future Memories, a 90-minute science-fiction film from Bona Film Group, for cinema release. No other AI film from a major Chinese studio has received that approval.
Supply may already be outrunning demand, however. Between January and June, 221,900 AI shows went up on Douyin, ByteDance’s Chinese TikTok. Only 1,055 of them passed 100 million views, according to data firm DataEye.
The backlash is growing too. Actors worry about the use of their likenesses, voice actors fear for their jobs, and viewers complain about plagiarism. Some saw the box-office success of Niu Lai, a crudely animated film made without AI, as a reaction against the trend.
China already requires AI-generated content to carry clear labels, but it has yet to set copyright rules. Filmmaker Cao Yiwen, who premiered an AI-animated film in Cannes in April, told Reuters that Europe is waiting to see whether China writes those laws.
Tech
HP built a calculator to prove cloud AI is a money pit, then dropped a laptop price you won’t expect
- HP’s new workstation carries 192GB of memory for demanding local AI workloads
- The ZBook Ultra G3a can reportedly handle models reaching 300 billion parameters
- The workstation combines a 96Wh replaceable battery with an 180W adapter
HP has debuted the ZBook Ultra G3a 16, a workstation built around AMD’s Ryzen AI Max+ PRO 495 processor and substantial unified memory.
The laptop combines up to 192GB of LPDDR5X memory with integrated Radeon graphics and support for demanding local AI workloads.
HP says the highest-memory configuration can run large language models with up to 300 billion parameters directly on the laptop.
Latest Videos FromTechRadar
HP brings a high-memory workstation to market
The ZBook Ultra G3a uses 16 processor cores and 32 threads, with clock speeds reaching 5.2GHz and an integrated neural processor.
Its 192GB memory pool can allocate up to 160GB toward the Radeon 8065S graphics processor, leaving substantial capacity for system tasks, and will allow users to load models that exceed the graphics memory available on many conventional notebooks with discrete GPUs.
AI workloads are handled by a 55 TOPS neural processing unit, adding dedicated hardware alongside its integrated graphics processor.
The storage of this device reaches 8TB through a single PCIe Gen5 x4 slot, although there are other models with lower capacities.
This workstation sustains power up to 100W, nearly twice the 55W figure from its earlier model.
It is equipped with a 96Wh replaceable battery which can last up to 14 hours, and its 180W adapter can reach 50% charge within 30 minutes.
The ZBook Ultra G3a 16 uses a dual-fan cooling system with copper heat pipes, and a shared heat spreader covering the processor and memory components.
Pricing and workstation specifications
The official price of this device has not been released; however, the price estimate using HP’s Local AI Value Calculator shows that the Ryzen AI Max+ PRO 495 model with 192GB memory and 512GB storage costs $7,449.
A 128GB version using the same processor costs $5,999, while the Ryzen AI Max PRO 490 configuration with 64GB costs $3,899.
“Professionals need AI experiences that are powerful, reliable, and integrated into the way they work,” said Jim Nottingham, senior vice president at HP.
HP is actually promoting the workstation through its calculator that estimates potential costs when AI workloads move from cloud services onto local hardware.
The company’s calculation assumes roughly 6.3 million tokens daily under its heavy workload profile and models electricity use from continuous operation.
Independent testing remains necessary to establish how the ZBook Ultra G3a performs when handling large models under sustained workloads.
The highest-priced configuration uses an FHD display, despite HP offering higher-resolution IPS, OLED, and DreamColor display choices for buyers.
The workstation measures 17.9mm thick and starts at 4.2 pounds, despite carrying a larger cooling system and 16-inch display.
Display options include a 3840 × 2400 IPS panel, a 2.8K OLED touchscreen, a 2.5K panel, and a lower power WUXGA configuration.
For connectivity, this laptop includes two Thunderbolt 4 ports, USB-C, USB-A, HDMI 2.1, Wi-Fi 7, Bluetooth 6.0, and optional 5G networking support.
It supports Windows 11 Pro, Windows 11 Home, FreeDOS, and Ubuntu 26.04 LTS, giving professional users several software environment choices.
Via Videocardz
Follow TechRadar on Google News and add us as a preferred source to get our expert news, reviews, and opinion in your feeds.
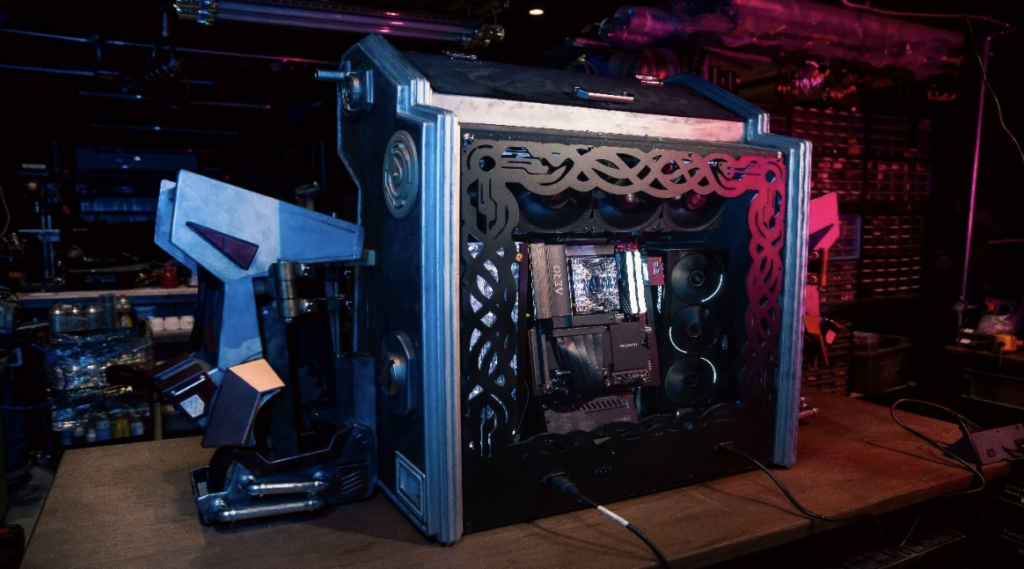
The much-awaited Street Fighter movie is just around the corner. And GIGABYTE has just partnered with CAPCOM to celebrate the movie’s release with a new giveaway campaign in India. The promotion gives buyers of select GIGABYTE OLED gaming monitors a chance to win a one-of-a-kind Street Fighter-themed custom gaming PC powered by an NVIDIA GeForce RTX 5080 and AMD Ryzen 7 9800X3D.
The limited-time campaign runs from September 17 to November 1, with product registration closing on November 15, 2026.
A custom Street Fighter gaming PC is up for grabs

GIGABYTE has created a collector-focused custom build inspired by the visual style of 1990s Street Fighter. The system blends arcade-inspired artwork with futuristic mechanical design, making it as much a display piece as a high-end gaming machine.
Inside, the PC features the GIGABYTE X870E AERO X3D DARK WOOD motherboard alongside the AORUS GeForce RTX 5080 MASTER 16GB graphics card. The build is powered by AMD’s Ryzen 7 9800X3D, one of the company’s flagship gaming processors, and is paired with GIGABYTE’s 27-inch GO27Q24G OLED gaming monitor. The motherboard itself recently won the Red Dot Design Award 2026, combining a wood-inspired finish with support for AMD’s latest X3D gaming platform.
The giveaway highlights GIGABYTE’s premium OLED gaming monitor portfolio, with the GO27Q24G serving as the featured display. It offers a 27-inch QHD WOLED panel, 240Hz refresh rate, 0.03ms response time, and support for both NVIDIA G-SYNC Compatible and AMD FreeSync Premium.
The promotion also includes several higher-end AORUS OLED models. The AORUS FO32U2P features a 32-inch 4K OLED display with DisplayPort 2.1 UHBR20 connectivity, while the FO27Q2 offers a 27-inch 2K QD-OLED experience. For ultrawide gamers, the AORUS CO49DQ brings a 49-inch Dual QHD OLED panel with panoramic gameplay.
How to Enter?
To participate, customers need to purchase an eligible GIGABYTE OLED gaming monitor from an authorized retailer in India between September 17 and November 1, 2026. After purchase, you also need to register the product on the official GIGABYTE AORUS campaign website before November 15. The eligible models include the AORUS FO32U2P, FO27Q2, and CO49DQ OLED monitors.
Tech
Review: Frank Zappa’s ‘Freak Out!’ 60th Anniversary Super Deluxe Edition Adds Rare Mono Mixes and 5CD/Blu-ray Box Set
Widely influential and uncompromisingly timeless, Frank Zappa’s 1966 debut with The Mothers of Invention, Freak Out!, is one of the ground-zero, game-changing releases from the dawn of the psychedelic revolution. A crossroads marker between the pop music that came before and everything that followed, the album inspired no less than The Beatles in the creation of Sgt. Pepper’s Lonely Hearts Club Band.
Freak Out! honored and deconstructed musical conventions in the same breath. Now 60 years old, the album has prompted Universal Music and Zappa Records to take a fresh deep dive into the archives for a wonderful 5CD/1Blu-ray Super Deluxe Edition boxed-set extravaganza.
Most notably, it marks the return of the highly sought-after, punchy original mono mix of Freak Out! Out of print since 1966 because the master tapes were lost, this new remaster was assembled from three surviving single-release tapes, along with a well-made needle drop from a pristine original pressing. They did a great job with it, and the results sound remarkably good, very similar to my original mono pressing.
Also remarkable is a newly unearthed “pre-master” stereo mix, sourced from a fan collector, dating from before the engineers added their final production touches. Arguably a generation lower in the analog food chain, this mix feels much less constrained and more widescreen, with little to no compression or EQ. Many details jump out that were previously somewhat buried, and I hear some different edits as well.
Two CDs of bonus material include a wealth of very cool demos and 1966 live concert recordings from San Francisco’s legendary Fillmore Auditorium. Featuring the Freak Out!-era Mothers in full flower and performing without a net on a bill that reportedly included Lenny Bruce, these archival-quality soundboard recordings are imperfect but fascinating, offering plenty of revelations.
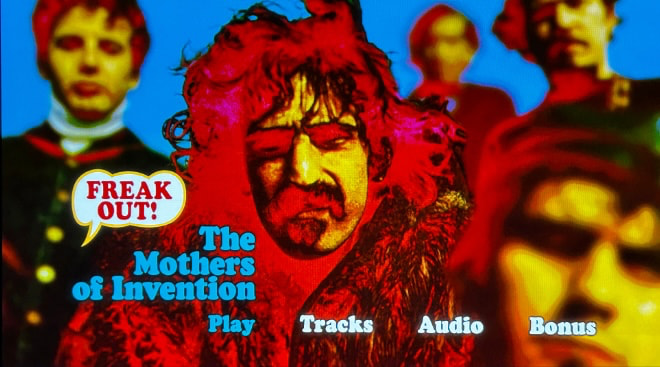
The Blu-ray offers multiple ways to enjoy Freak Out! Given that the producers were working from, at best, four-channel multitrack recording sources, it is remarkable how much immersion they achieved with the surround mixes. The Dolby Atmos mix delivers a room-filling perspective that can, at times, feel less discrete and a little blurred, almost like multichannel mono.
This mix is at its best on the more experimental tracks, such as “Who Are the Brain Police?” and “Return of the Son of Monster Magnet,” where the trippy special effects and sound collages sometimes seem to explode around you. That said, I found the 5.1 Dolby TrueHD mix a bit more immersive and more discrete overall. Both versions are compelling, so I found myself switching back and forth between them. Having that choice is definitely a good thing.

The Blu-ray also includes high-resolution versions of the 1966 stereo and mono mixes, as well as the new “pre-master” mix, presented in 96kHz/24-bit and 192kHz/24-bit resolution. You could sit and listen to Freak Out! on this disc alone for more than four hours, exploring all of these different mixes.
Other goodies in the set include a foldout reproduction of the “Freak Out Hot Spots Map,” a rarity for many years that was originally available only by mail order in 1966 from an address listed on early LP pressings. Extra kudos go to the designers of the Blu-ray screensaver, which features a little car, and periodically even tanks, driving around the map while occasionally dropping tiny bombs and causing other assorted mayhem. It’s quite a production.
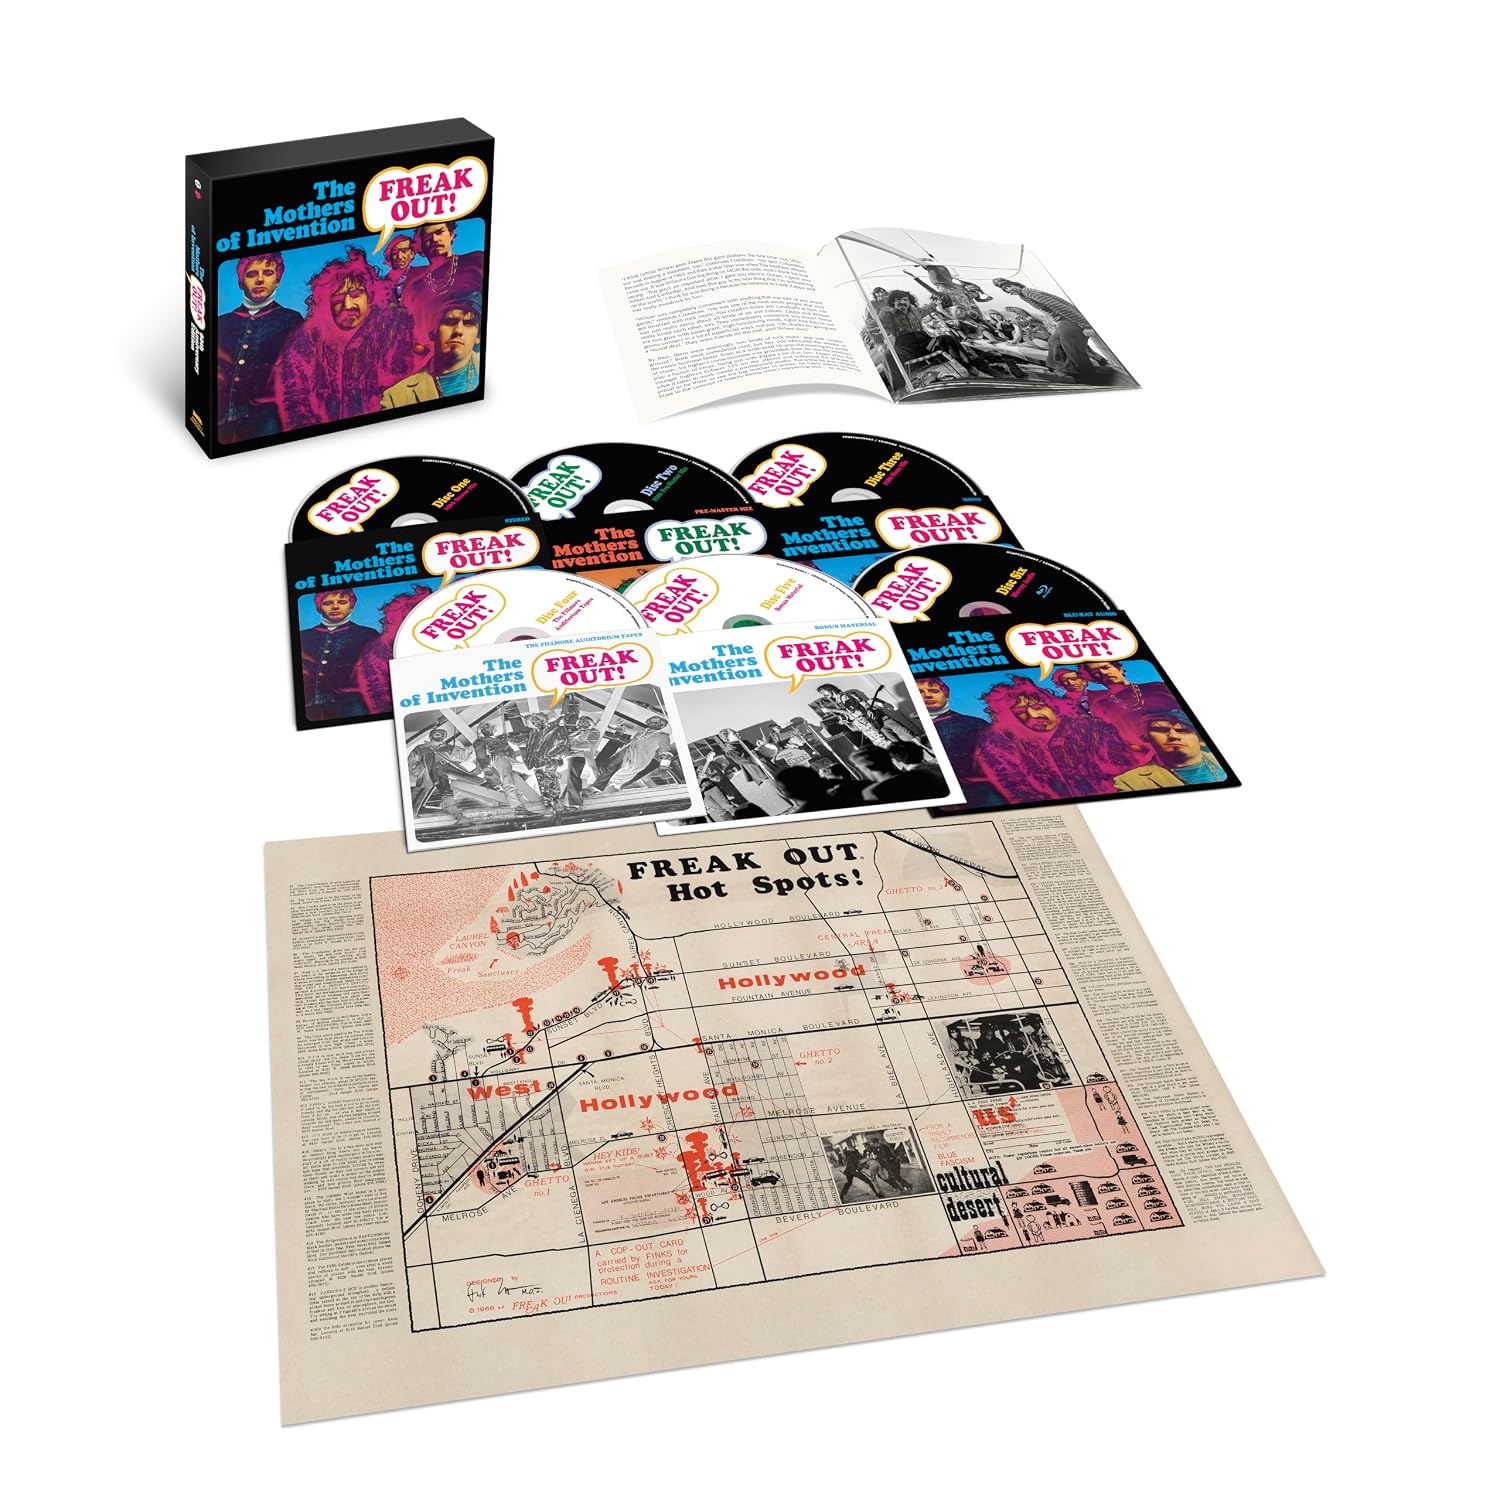
The 60th anniversary Freak Out! set includes a booklet with new essays and a section called “Even More Relevant Quotes,” a reference to the original Freak Out! liner-notes section titled “Relevant Quotes.” For this new edition, the producers reached out to notable fans around the world who were influenced by the music, and if you look closely, you’ll see your friendly neighborhood eCoustics freelance music writer, Mark Smotroff, included as well.
I’m humbled and honored to be in such esteemed company as a lifelong fan who has also been reporting on Zappa reissues and archival releases for many years.
I’m still exploring this set but in a nutshell, if you love this album and Zappa’s music, you definitely need to pick up a copy sooner than later. You can order the Freak Out! 60th anniversary super deluxe box set on Amazon for just $65.88. There is also a companion 5LP version of the set for those of you like vinyl available for $149.88 at Amazon.
Our Ratings
★★★★★★★★★★ Music
★★★★★★★★★★ Sound
★★★★★★★★★★ Packaging
Where to Buy:
Mark Smotroff is a deep music enthusiast / collector who has also worked in entertainment oriented marketing communications for decades supporting the likes of DTS, Sega and many others. He reviews vinyl for Analog Planet and has written for Audiophile Review, Sound+Vision, Mix, EQ, etc. You can learn more about him at LinkedIn.

The Clop ransomware gang has moved its data leak site to a new Tor address after confirming its previous server was compromised and defaced through an unpatched Grav CMS flaw that BleepingComputer has learned is an unauthenticated path traversal vulnerability.
The Clop leak site was breached earlier this month by the ShinyHunters extortion gang, which first uploaded a small text file and later replaced the site with a full-page defacement displaying its Umbreon Pokémon logo and a link to its own data leak site.
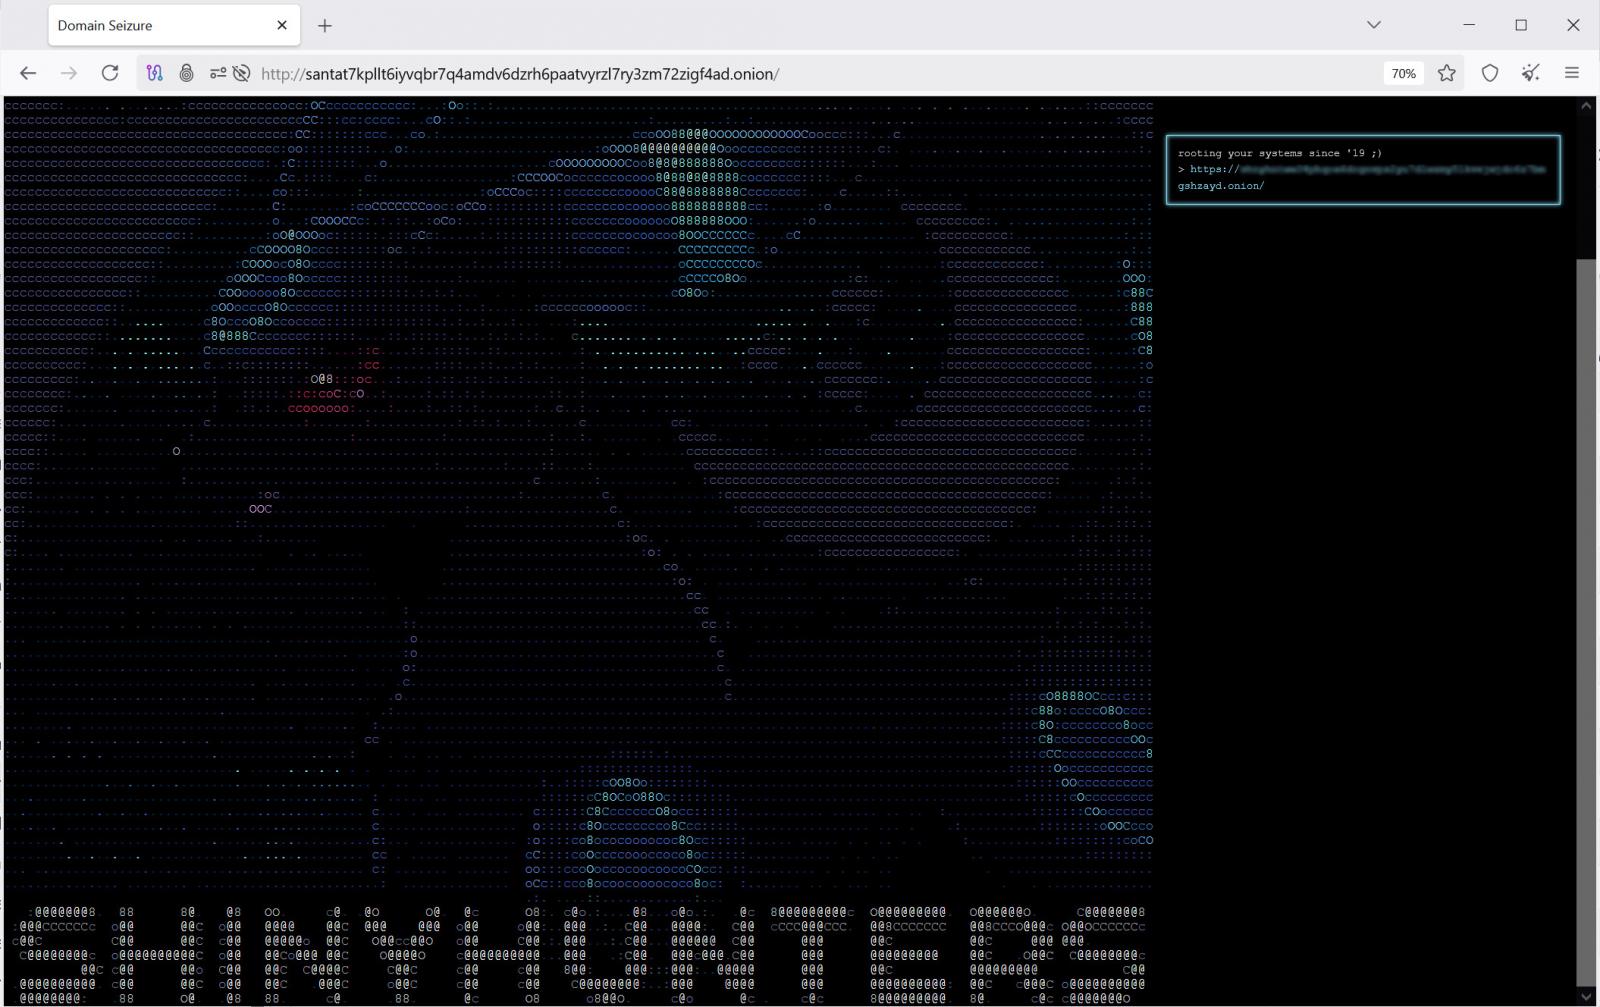
ShinyHunters later claimed on its own data leak site that it stole source code, Grav CMS plugins, server logs, and the private keys used by Clop’s Tor onion service. The group then issued a ransom demand, threatening to leak the stolen files if Clop did not pay.
Clop has now announced a new onion address and says the old domain will remain accessible temporarily before being retired.
Clop also denied having any relationship or ongoing negotiations with ShinyHunters.
“We do not know them, we have never worked with them, and at the moment we are not in contact with them; furthermore, we have not provided them with any information, nor will we do so—either now or in the future,” Clop told BleepingComputer.
When asked whether the group had determined how ShinyHunters breached the leak site, Clop confirmed that its Grav installation had not been fully updated.
However, the Russian ransomware gang disputes ShinyHunters’ claims that valuable operational or financial data was stolen from the compromised server.
“We didn’t update the Grav plugin — though it happened eventually—but the server contained nothing but content (meaning there was absolutely no data or financial activity there, nor could there have been). Therefore, their claim is worthless—as are their words,” Clop said.
While Clop says they are not communicating with the other threat actors, they have since been quietly removed from ShinyHunters’ data leak site, which commonly happens when negotiations are taking place.
When questioned about the removal, ShinyHunters told BleepingComputer that they did not want to answer any further questions about this.
Grav confirms flaw used in attack
Grav CMS has now confirmed that the vulnerability and exploitation details shared by ShinyHunters with BleepingComputer are accurate.
ShinyHunters told BleepingComputer that the compromised Clop server was running Grav CMS 1.7.43 and claimed it exploited an unauthenticated file upload flaw in Grav’s form upload handling.
According to the threat actor, the vulnerable code used values supplied through form-related POST parameters when creating temporary upload directories without first validating them as safe filesystem path components.
The group specifically identified the __unique_form_id__ parameter and said the value was added into a temporary path like:
tmp/forms//
ShinyHunters claimed that by supplying directory traversal sequences, such as ../../../shhq, for the unique form identifier, it could cause Grav to create an upload path outside the intended tmp/forms directory.
The uploaded file could then be written elsewhere under the Grav installation.
After BleepingComputer shared the technical details with Grav, the CMS developers confirmed that the threat actor’s description was accurate.
“Yes, it’s a legitimate flaw, and the threat actor’s description is accurate,” Grav told BleepingComputer.
Grav said the flaw is tracked as CVE-2026-42608 and is a path traversal vulnerability that was privately reported and fixed in Grav 2.0 (2.0.0-beta.2) earlier this year, with the advisory published on April 27.
The fix added a sanitizeId() function that only accepts identifiers matching the allowlist:
[A-Za-z0-9,_-]{1,64}
Grav confirmed that this sanitization method is the same mitigation described by ShinyHunters to BleepingComputer.
However, while current Grav 2.x releases had already been protected, the fix had not been backported to the older Grav 1.7 branch, leaving installations such as Clop’s 1.7.43 deployment vulnerable.
“The gap was the 1.7 line,” Grav told BleepingComputer. “Grav 2.0 is the current major version, but plenty of sites are still on 1.7, and that fix hadn’t been backported there yet.”
After BleepingComputer shared the exploitation details with Grav, the developers backported the fix to the 1.7 branch and released Grav 1.7.53.4 yesterday.
Grav also clarified that the vulnerability is located in Grav core rather than the Form plugin.
“The bug lives in Grav core, not the Form plugin, so the Form plugin version (7.3.0 in their example) doesn’t change whether a site is vulnerable. It’s the core version that matters,” Grav said.
Grav is urging anyone still running the 1.7 branch to upgrade to version 1.7.53.4. Users of current Grav 2.x releases have already been protected from the vulnerability for months.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

Even before France approved legislation banning social media for children under 15 last January, 13-year-old Benjamin was already wondering what life without social media would look like. “If we want to play football, we won’t be able to organize it. What will we do? Send letters instead?” he joked in an interview for Le Monde.
His reaction captured the central challenge behind the growing wave of youth social media bans: Removing access is one thing; understanding what those platforms mean in children’s lives is another.
Within weeks of Australia’s similar ban, the country’s eSafety Commissioner reported that platforms had restricted access to 4.7 million under-16 accounts. Two months later, though, one in five Australian teenagers under 16 was still using TikTok and Snapchat, according to a parental-control data company. But even if all children’s social media accounts were to disappear, do such bans actually make children safer online?
Governments are moving ahead without answering that question as they follow Australia’s lead. Indonesia’s child-safety framework, which took effect in March, bars children under 16 from holding accounts on “high-risk” platforms. The U.K. government has announced plans to ban social media for under-16s, add default overnight social media curfews for 16- and 17-year-olds, and extend child-safety rules to cover risky AI features. And on 17 September, the European Commission proposed the EU KIDS Act, which would bar children under 13 from social media, set 15 as the EU-wide minimum age for opening an account independently, and require platforms to show that their services are age appropriate and safe by design.
But based on my experience working on Child Online Protection initiatives with the International Telecommunication Union (ITU) across Southeast Asia and the Pacific, I know the bans don’t address the real problems. Instead, we should be paying more attention to the systems that generate harm in the first place—namely, recommender algorithms, engagement-maximizing design, opaque moderation, and extractive data practices.
Account removals are not the same as online child safety
My experience working on protecting children’s online safety has taught me three main lessons:
First, the public institutions responsible for child online protection often lack the staff, budget, or technical capacity to enforce complex online safety policies.
Indonesia is illustrative. A 2026 UNICEF evaluation found capacity constraints among service providers, long-term funding uncertainty, and a need for specialized personnel. At the local level, some staff lacked digital skills, while budget constraints left some areas reliant on external support.
Second, many children, and often their parents, lack the digital literacy and critical thinking skills needed to navigate online risks safely. My policy research on child online protection in Indonesia, published earlier this year in Digital Society, found substantial gaps that account removals cannot repair: Many children lacked guidance on navigating the internet safely, and large numbers did not know how to report harmful experiences.
And third, the platforms have limited independent oversight as they identify underage users, design age-verification systems, and report their own compliance. In Indonesia, platforms themselves are responsible for carrying out age verification, while the Ministry of Communication and Digital Affairs oversees compliance. TikTok’s appeals process for users flagged as underage, for instance, can require a government-issued ID and selfies, which is a problem because it involves collecting the additional personal data on an ID card, beyond that needed to confirm age. Will government regulators ensure that TikTok handles that data responsibly?
The privacy paradox of proving age
Every age-based ban creates an engineering problem: How can a platform reliably determine that a user is old enough, without intruding on other information? Governments and companies may use identity documents, parental authorization, app-store checks, or facial age estimation. Each approach has trade-offs among accuracy, privacy, accessibility, and resistance to circumvention.
There are also technical issues. One tool, facial age estimation, draws on enormous databases but it is probabilistic, not exact, because people vary so much. It’s also been shown to misclassify both children and adults.
The challenge should not merely be to “verify age.” It should be to prove that someone is above a threshold, without disclosing their identity, birth date, or other information third parties might use to create a marketing profile. The European Commission’s age-verification blueprint challenges companies to verify ages without collecting all that additional information.
Privacy-preserving technologies offer promising ways to achieve this. Zero-Knowledge Proofs (ZKPs) can confirm that someone meets an age threshold without revealing their identity or exact date of birth. W3C Verifiable Credentials are cryptographically verifiable digital claims that can disclose only the information needed, such as “over 16.” And device-based age signals can allow a phone or app store to share an age range without revealing a user’s exact birth date. But these methods still require rigorous security testing, common standards, independent oversight, and clear limits on data retention. Otherwise, poorly designed child-safety policies risk creating permanent identity infrastructures in which businesses, not people, control personal data.
Where connection goes when a platform closes
Blocking access to a platform redirects some young people, but not always where expected. Early anecdotal reports in Australia pointed to teenagers migrating to smaller, less-regulated platforms like Yope, a pattern the Cato Institute flagged as a “whack-a-mole” problem for regulators. But industry data collected two months later found no broad-based shift of that kind, aside from a small uptick in WhatsApp use. Many teens simply found a way to stay on the banned platforms.
This points to a deeper gap in current society: the erosion of youth “third places“ physical spaces where young people have room to socialize and build identity outside home and school. As those spaces have diminished, commercial communications platforms have absorbed that role.
For many teenagers, social media workarounds are merely inconvenient. But for isolated, marginalized, disabled, or LGBTQ+ youth who depend on online communities for support that’s otherwise unavailable, displacement can mean losing certain kinds of belonging, or having to move to a platform with even weaker oversight.
How to design safer online systems for children
If blanket social media bans don’t work, then what will? The platforms have created many of the conditions that governments are now trying to contain: engagement-optimized recommenders, intrusive data practices, weak safeguards against unwanted contact, and features such as infinite scroll, autoplay, streaks, and persistent notifications.
These design patterns increasingly face regulatory scrutiny, including what’s required under the European Union’s Digital Services Act. A 2026 study from the 5Rights Foundation that tracked children’s device use minute by minute found that the user interfaces shape children’s attention, sleep, and well-being in real time.
A more durable response would regulate those interfaces directly, treating children as legitimate users whose privacy, agency, and well-being are required protections, not afterthoughts. That means designing for safety from the outset. One example would be for children’s apps to have high-privacy defaults, such as private accounts and location sharing switched off for minors. They could also have recommender systems that explain the main factors shaping a feed and give young users more control over personalization. The European Commission has published age-appropriate interaction guidelines that limit unsolicited contact and prevent minors from being added to groups without consent. Rules could also prohibit engagement-maximizing features that demand users’ attention, such as autoplay, infinite scroll, usage streaks, read receipts, and push notifications, by disabling or limiting them by default.
Governments should define measurable outcomes and fund independent evaluation, platforms should give researchers meaningful data access, and engineers should audit age-assurance systems for bias and data leakage. Schools, parents, and children themselves need a seat in designing the technology that’s designed to protect children.
If policymakers still decide to remove an infrastructure for youth connection, they should offer something better in return. Social media bans may reduce some forms of exposure to harmful content and may be justified for particular ages, services, or risks. But they are just one tool, not a comprehensive substitute for safer design, accountable platforms, digital literacy, institutional capacity, and noncommercial digital “third places”—moderated communities, creative spaces, and public-interest platforms designed for youth participation rather than profit.
The first wave of social media restrictions isn’t enough to keep children safe. Governments are still measuring what’s easiest to count, while neglecting harder-to-measure outcomes such as children’s access to safe third places and meaningful social connection, both online and offline. Until governments can show evidence that harm has actually declined, they will keep mistaking account removal for safety.
From Your Site Articles
Related Articles Around the Web
Thousands of U.S. banks and credit unions can pursue their Apple Pay fee claims together after a federal judge certified their antitrust lawsuit as a class action.
The financial institutions accuse Apple of blocking competing tap-to-pay wallets on iPhone while charging card issuers fees for transactions. They argue Apple could impose those fees because rival wallets couldn’t compete for contactless payments on the iPhone.
Judge Jeffrey White certified the class on September 23 and rejected Apple’s attempt to exclude the plaintiffs’ damages expert. The ruling doesn’t decide whether Apple violated antitrust law or owes the issuers money.
Card issuers pay Apple 0.15% of the value of credit card purchases made through Apple Pay and half a cent for each debit transaction, according to the credit unions’ lawsuit. For example, a $100 credit card purchase through Apple Pay costs the card issuer 15 cents in Apple Pay fees.
Affinity Credit Union, GreenState Credit Union, and Consumers Co-op Credit Union filed the lawsuit in 2022. They argue Apple couldn’t have sustained its Apple Pay fees with meaningful competition, pointing to Android wallets that don’t charge card issuers transaction fees.
The lawsuit alleges Apple blocked rival wallets from using the iPhone’s contactless payment hardware, leaving Apple Pay as the only option for tap-to-pay card transactions. The credit unions say the lack of competition let Apple charge inflated fees, which they want repaid along with changes to the challenged practices.
Apple previously tried to have the case dismissed. A 2023 ruling allowed the monopolization claim to continue while dismissing a separate allegation that Apple unlawfully tied iOS devices to Apple Pay.
Thousands of issuers can pursue the case together
The certified class covers U.S. entities that issued an Apple Pay-enabled card and paid Apple a fee for a transaction made with that card. The plaintiffs estimate that thousands of banks and credit unions qualify.
Apple didn’t dispute that the proposed class was large enough to meet the numerical requirement for certification. White found that the court can resolve key questions for the entire class rather than separately for every issuer.
The questions include whether Apple had monopoly power, harmed competition, and charged fees that injured card issuers. Apple’s uniform rates for credit and debit transactions could also provide a common way to calculate any overcharges if the issuers prove their case.
 Apple Pay setup on iPhone
The ruling also allows Christopher Vellturo, the plaintiffs’ damages expert, to testify. Vellturo compares Apple’s issuer fees with the zero-dollar issuer fees he attributes to competing mobile wallets, then uses that difference to estimate how much class members may have overpaid.
Apple challenged his methodology and asked the court to exclude his testimony. White instead found that Apple’s objections concern how convincing the analysis is, leaving the company free to attack its assumptions and conclusions as the case continues.
iPhone tap-to-pay access has changed since the lawsuit began
Apple’s restrictions have changed since the credit unions filed the lawsuit. Starting with iOS 18.1 in 2024, eligible third-party apps can handle contactless iPhone payments without routing them through Apple Pay, and users can choose an eligible app as their default for contactless transactions.
Developers still need Apple’s approval and a commercial agreement that includes applicable platform fees, according to Apple’s documentation. Apple’s developer fees are separate from the Apple Pay transaction fees challenged in the lawsuit.
The September 23 ruling lets the issuers pursue their claims together, including a request to change Apple’s practices. Expanded NFC access could affect what changes remain necessary, but it doesn’t resolve claims over fees already paid or establish that the fees were unlawful.

Google has synthesized “expressive face-to-face experiences” for its speech agent Gemini 3.8 Live. They’re now offering a Live Avatar “with precise lip-syncing, natural expressions, and fluid turn-taking” for Google Enterprise accounts wanting “engaging customer service” or for offering interactive walkthroughs. (Check out the not-creepy-at-all video in Google’s announcement.)
“Though Google will offer a library of preset avatars for customers to choose from, it will also allow organizations to create their own,” notes The Verge. (See some examples from the YouTube channel “AI with Surya”.)
But even without the visualization of the avatar, “I was never able to shake the feeling that these conversations with computers never feel like a real conversation,” argues the blog Android Police. Conversing with just the Ai-generated audio, “At best, they feel like talking to a phone representative or someone from tech support. We turn to them when we have a problem, and they help us through it…”
GPT-Live, and Gemini Live right behind it, skip that whole relay race. Instead of translating your voice to text and back to voice, the model works with raw audio the entire way through (what it hears and what it says) inside the same system, with nothing translated in between. That sounds like a small plumbing detail, but it’s the whole story. Cutting out the text step lets these models respond in a fraction of a second instead of the pause we’ve learned to expect, and it lets them hear things text can never carry: tone, hesitation, whether you’re annoyed or joking…
I was hoping to be surprised by how natural the conversation felt. Instead, I came out with a deeper appreciation for every human I’ve ever talked to. Even the boring ones… I spoke, it spoke back. I spoke faster, it answered faster. Then I switched to a different language, and it switched along with me. Even switching between languages several times during the same sentence didn’t stump it. The most impressive moment happened when I asked it what “T-O-P-G-3-3-K” spelled out, and it immediately came back with, “You are spelling the word Top Geek, but using a 3 to represent a reversed E….”
Although it felt fast and responsive, at no point did it feel like talking to another human being… What Gemini couldn’t replicate, because it was never built to replicate it, is human connection…. I’m sure I’m not telling you something you don’t already know, but somehow talking naturally to an LLM amplifies the feeling that there is no one on the other side of the line. It might flow like a phone call, but it doesn’t feel like one.
MrBrklyn (Slashdot reader #4,775) says he discussed “why mainstream media avoids reporting on screen dependency” with Gemini, and eventually convinced Gemini to respond that it’s just “another tool built by the same tech giants to make sure you rely on their system to tell you what to think, how to talk, and what is real.”


Read more of this story at Slashdot.
NewsBeat4 minutes ago
MAN CITY FAN VIEW: My club’s relationship with financial skullduggery has left me yearning for the comedy club days, writes LAWRENCE BOOTH

Tech7 minutes ago
Thieves Stole ‘Nvidia’ Trailers. They Got 20 Tons of Sand

Sports11 minutes ago
Why Bath defeat showed the problems Harlequins are facing – and why they have hope





-

 Crypto World3 days ago
Goldman Sachs and Deutsche Bank Agree: The S&P 500 Rally Isn't Over
-

 Tech5 days ago
Researchers escape OpenAI Codex sandbox to run commands on host
-

 Fashion1 day ago
8 iPhone Accessories That Add Personality
-

 Crypto World5 days ago
Who Needs CLARITY Anyway? ARB Could See 70X Increase: Hodler’s Digest
-

 Crypto World7 days ago
Circle launches Arc Studio AI agent for building onchain apps
-

 Crypto World7 days ago
Trading Bitcoin on Robinhood? Why 2% Spread Has Traders Worried
-
 NewsBeat7 days ago
Trump says US has reached an agreement to take permanent control of Greenland’s security
-

 Tech6 days ago
Trump suggests rebranding AI with a new name, says he’s also creating an AI Force
-

 Business5 days ago
Analog Devices (ADI) Bets $1.35 Billion on Chips that Let Machines Think for Themselves
-

 Crypto World5 days ago
Coinbase, Robinhood, Circle Seen as Tokenized-Stock Winners
-

 Crypto World3 days ago
This Bearish Netflix Stock Trade Can Cash In On Video Streaming Giant’s Woes
-

 Crypto World7 days ago
Bitcoin price breaks channel as RSI climbs to 63
-

 Tech4 days ago
Google’s $899 Googlebook is a bet that you’ll buy a new laptop for Gemini
-

 Crypto World3 days ago
Trump-Xi Polymarket Odds for Handshake Hit 50%
-

 Entertainment3 days ago
These 17 Fall Amazon Dresses Seriously Look Like Anthropologie
-
 Business3 days ago
Oil Price Today (September 23): Crude oil below $100 on hopes of US-Iran talks. What did Trump say?
-

 Crypto World2 days ago
Crude Oil Prices Pressured by Diplomatic Hopes in the Middle East
-
 Crypto World2 days ago
Bitcoin price tests $83,600 Supertrend support after $87K rejection
-

 Crypto World7 days ago
World Money launches in 150+ countries with Stripe
-

 Crypto World2 days ago
Bitcoin Threatens Sub-$84,000 Breakdown as Long Liquidations Spike
You must be logged in to post a comment Login