Even before France approved legislation banning social media for children under 15 last January, 13-year-old Benjamin was already wondering what life without social media would look like. “If we want to play football, we won’t be able to organize it. What will we do? Send letters instead?” he joked in an interview for Le Monde.
His reaction captured the central challenge behind the growing wave of youth social media bans: Removing access is one thing; understanding what those platforms mean in children’s lives is another.
Within weeks of Australia’s similar ban, the country’s eSafety Commissioner reported that platforms had restricted access to 4.7 million under-16 accounts. Two months later, though, one in five Australian teenagers under 16 was still using TikTok and Snapchat, according to a parental-control data company. But even if all children’s social media accounts were to disappear, do such bans actually make children safer online?
Governments are moving ahead without answering that question as they follow Australia’s lead. Indonesia’s child-safety framework, which took effect in March, bars children under 16 from holding accounts on “high-risk” platforms. The U.K. government has announced plans to ban social media for under-16s, add default overnight social media curfews for 16- and 17-year-olds, and extend child-safety rules to cover risky AI features. And on 17 September, the European Commission proposed the EU KIDS Act, which would bar children under 13 from social media, set 15 as the EU-wide minimum age for opening an account independently, and require platforms to show that their services are age appropriate and safe by design.
Advertisement
But based on my experience working on Child Online Protection initiatives with the International Telecommunication Union (ITU) across Southeast Asia and the Pacific, I know the bans don’t address the real problems. Instead, we should be paying more attention to the systems that generate harm in the first place—namely, recommender algorithms, engagement-maximizing design, opaque moderation, and extractive data practices.
Account removals are not the same as online child safety
My experience working on protecting children’s online safety has taught me three main lessons:
First, the public institutions responsible for child online protection often lack the staff, budget, or technical capacity to enforce complex online safety policies.
Indonesia is illustrative. A 2026 UNICEF evaluation found capacity constraints among service providers, long-term funding uncertainty, and a need for specialized personnel. At the local level, some staff lacked digital skills, while budget constraints left some areas reliant on external support.
Advertisement
Second, many children, and often their parents, lack the digital literacy and critical thinking skills needed to navigate online risks safely. My policy research on child online protection in Indonesia, published earlier this year in Digital Society, found substantial gaps that account removals cannot repair: Many children lacked guidance on navigating the internet safely, and large numbers did not know how to report harmful experiences.
And third, the platforms have limited independent oversight as they identify underage users, design age-verification systems, and report their own compliance. In Indonesia, platforms themselves are responsible for carrying out age verification, while the Ministry of Communication and Digital Affairs oversees compliance. TikTok’s appeals process for users flagged as underage, for instance, can require a government-issued ID and selfies, which is a problem because it involves collecting the additional personal data on an ID card, beyond that needed to confirm age. Will government regulators ensure that TikTok handles that data responsibly?
The privacy paradox of proving age
Every age-based ban creates an engineering problem: How can a platform reliably determine that a user is old enough, without intruding on other information? Governments and companies may use identity documents, parental authorization, app-store checks, or facial age estimation. Each approach has trade-offs among accuracy, privacy, accessibility, and resistance to circumvention.
There are also technical issues. One tool, facial age estimation, draws on enormous databases but it is probabilistic, not exact, because people vary so much. It’s also been shown to misclassify both children and adults.
Advertisement
The challenge should not merely be to “verify age.” It should be to prove that someone is above a threshold, without disclosing their identity, birth date, or other information third parties might use to create a marketing profile. The European Commission’s age-verification blueprint challenges companies to verify ages without collecting all that additional information.
Privacy-preserving technologies offer promising ways to achieve this. Zero-Knowledge Proofs (ZKPs) can confirm that someone meets an age threshold without revealing their identity or exact date of birth. W3C Verifiable Credentials are cryptographically verifiable digital claims that can disclose only the information needed, such as “over 16.” And device-based age signals can allow a phone or app store to share an age range without revealing a user’s exact birth date. But these methods still require rigorous security testing, common standards, independent oversight, and clear limits on data retention. Otherwise, poorly designed child-safety policies risk creating permanent identity infrastructures in which businesses, not people, control personal data.
Where connection goes when a platform closes
Blocking access to a platform redirects some young people, but not always where expected. Early anecdotal reports in Australia pointed to teenagers migrating to smaller, less-regulated platforms like Yope, a pattern the Cato Institute flagged as a “whack-a-mole” problem for regulators. But industry data collected two months later found no broad-based shift of that kind, aside from a small uptick in WhatsApp use. Many teens simply found a way to stay on the banned platforms.
This points to a deeper gap in current society: the erosion of youth “third places“ physical spaces where young people have room to socialize and build identity outside home and school. As those spaces have diminished, commercial communications platforms have absorbed that role.
Advertisement
For many teenagers, social media workarounds are merely inconvenient. But for isolated, marginalized, disabled, or LGBTQ+ youth who depend on online communities for support that’s otherwise unavailable, displacement can mean losing certain kinds of belonging, or having to move to a platform with even weaker oversight.
How to design safer online systems for children
If blanket social media bans don’t work, then what will? The platforms have created many of the conditions that governments are now trying to contain: engagement-optimized recommenders, intrusive data practices, weak safeguards against unwanted contact, and features such as infinite scroll, autoplay, streaks, and persistent notifications.
These design patterns increasingly face regulatory scrutiny, including what’s required under the European Union’s Digital Services Act. A 2026 study from the 5Rights Foundation that tracked children’s device use minute by minute found that the user interfaces shape children’s attention, sleep, and well-being in real time.
A more durable response would regulate those interfaces directly, treating children as legitimate users whose privacy, agency, and well-being are required protections, not afterthoughts. That means designing for safety from the outset. One example would be for children’s apps to have high-privacy defaults, such as private accounts and location sharing switched off for minors. They could also have recommender systems that explain the main factors shaping a feed and give young users more control over personalization. The European Commission has published age-appropriate interaction guidelines that limit unsolicited contact and prevent minors from being added to groups without consent. Rules could also prohibit engagement-maximizing features that demand users’ attention, such as autoplay, infinite scroll, usage streaks, read receipts, and push notifications, by disabling or limiting them by default.
Advertisement
Governments should define measurable outcomes and fund independent evaluation, platforms should give researchers meaningful data access, and engineers should audit age-assurance systems for bias and data leakage. Schools, parents, and children themselves need a seat in designing the technology that’s designed to protect children.
If policymakers still decide to remove an infrastructure for youth connection, they should offer something better in return. Social media bans may reduce some forms of exposure to harmful content and may be justified for particular ages, services, or risks. But they are just one tool, not a comprehensive substitute for safer design, accountable platforms, digital literacy, institutional capacity, and noncommercial digital “third places”—moderated communities, creative spaces, and public-interest platforms designed for youth participation rather than profit.
The first wave of social media restrictions isn’t enough to keep children safe. Governments are still measuring what’s easiest to count, while neglecting harder-to-measure outcomes such as children’s access to safe third places and meaningful social connection, both online and offline. Until governments can show evidence that harm has actually declined, they will keep mistaking account removal for safety.
HP’s new workstation carries 192GB of memory for demanding local AI workloads
The ZBook Ultra G3a can reportedly handle models reaching 300 billion parameters
The workstation combines a 96Wh replaceable battery with an 180W adapter
HP has debuted the ZBook Ultra G3a 16, a workstation built around AMD’s Ryzen AI Max+ PRO 495 processor and substantial unified memory.
The laptop combines up to 192GB of LPDDR5X memory with integrated Radeon graphics and support for demanding local AI workloads.
HP says the highest-memory configuration can run large language models with up to 300 billion parameters directly on the laptop.
Latest Videos FromTechRadar
Advertisement
HP brings a high-memory workstation to market
The ZBook Ultra G3a uses 16 processor cores and 32 threads, with clock speeds reaching 5.2GHz and an integrated neural processor.
Its 192GB memory pool can allocate up to 160GB toward the Radeon 8065S graphics processor, leaving substantial capacity for system tasks, and will allow users to load models that exceed the graphics memory available on many conventional notebooks with discrete GPUs.
AI workloads are handled by a 55 TOPS neural processing unit, adding dedicated hardware alongside its integrated graphics processor.
The storage of this device reaches 8TB through a single PCIe Gen5 x4 slot, although there are other models with lower capacities.
Sign up to the TechRadar Pro newsletter to get all the top news, opinion, features and guidance your business needs to succeed!
This workstation sustains power up to 100W, nearly twice the 55W figure from its earlier model.
Advertisement
It is equipped with a 96Wh replaceable battery which can last up to 14 hours, and its 180W adapter can reach 50% charge within 30 minutes.
The ZBook Ultra G3a 16 uses a dual-fan cooling system with copper heat pipes, and a shared heat spreader covering the processor and memory components.
Advertisement
Pricing and workstation specifications
The official price of this device has not been released; however, the price estimate using HP’s Local AI Value Calculator shows that the Ryzen AI Max+ PRO 495 model with 192GB memory and 512GB storage costs $7,449.
A 128GB version using the same processor costs $5,999, while the Ryzen AI Max PRO 490 configuration with 64GB costs $3,899.
“Professionals need AI experiences that are powerful, reliable, and integrated into the way they work,” said Jim Nottingham, senior vice president at HP.
HP is actually promoting the workstation through its calculator that estimates potential costs when AI workloads move from cloud services onto local hardware.
Advertisement
The company’s calculation assumes roughly 6.3 million tokens daily under its heavy workload profile and models electricity use from continuous operation.
Independent testing remains necessary to establish how the ZBook Ultra G3a performs when handling large models under sustained workloads.
The highest-priced configuration uses an FHD display, despite HP offering higher-resolution IPS, OLED, and DreamColor display choices for buyers.
The workstation measures 17.9mm thick and starts at 4.2 pounds, despite carrying a larger cooling system and 16-inch display.
Advertisement
Display options include a 3840 × 2400 IPS panel, a 2.8K OLED touchscreen, a 2.5K panel, and a lower power WUXGA configuration.
For connectivity, this laptop includes two Thunderbolt 4 ports, USB-C, USB-A, HDMI 2.1, Wi-Fi 7, Bluetooth 6.0, and optional 5G networking support.
It supports Windows 11 Pro, Windows 11 Home, FreeDOS, and Ubuntu 26.04 LTS, giving professional users several software environment choices.
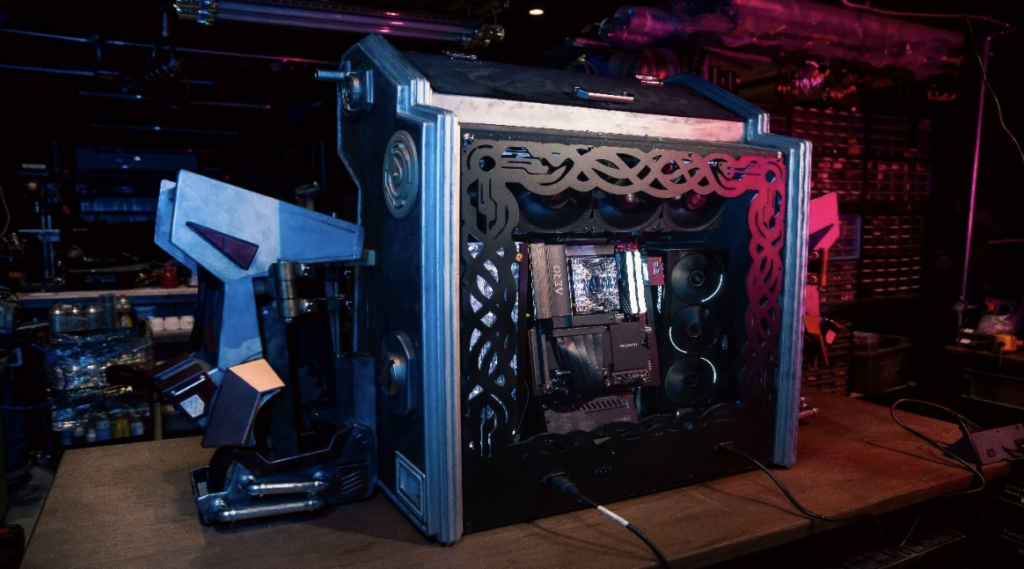
The much-awaited Street Fighter movie is just around the corner. And GIGABYTE has just partnered with CAPCOM to celebrate the movie’s release with a new giveaway campaign in India. The promotion gives buyers of select GIGABYTE OLED gaming monitors a chance to win a one-of-a-kind Street Fighter-themed custom gaming PC powered by an NVIDIA GeForce RTX 5080 and AMD Ryzen 7 9800X3D.
The limited-time campaign runs from September 17 to November 1, with product registration closing on November 15, 2026.
A custom Street Fighter gaming PC is up for grabs
GIGABYTE has created a collector-focused custom build inspired by the visual style of 1990s Street Fighter. The system blends arcade-inspired artwork with futuristic mechanical design, making it as much a display piece as a high-end gaming machine.
Inside, the PC features the GIGABYTE X870E AERO X3D DARK WOOD motherboard alongside the AORUS GeForce RTX 5080 MASTER 16GB graphics card. The build is powered by AMD’s Ryzen 7 9800X3D, one of the company’s flagship gaming processors, and is paired with GIGABYTE’s 27-inch GO27Q24G OLED gaming monitor. The motherboard itself recently won the Red Dot Design Award 2026, combining a wood-inspired finish with support for AMD’s latest X3D gaming platform.
The giveaway highlights GIGABYTE’s premium OLED gaming monitor portfolio, with the GO27Q24G serving as the featured display. It offers a 27-inch QHD WOLED panel, 240Hz refresh rate, 0.03ms response time, and support for both NVIDIA G-SYNC Compatible and AMD FreeSync Premium.
Advertisement
The promotion also includes several higher-end AORUS OLED models. The AORUS FO32U2P features a 32-inch 4K OLED display with DisplayPort 2.1 UHBR20 connectivity, while the FO27Q2 offers a 27-inch 2K QD-OLED experience. For ultrawide gamers, the AORUS CO49DQ brings a 49-inch Dual QHD OLED panel with panoramic gameplay.
How to Enter?
To participate, customers need to purchase an eligible GIGABYTE OLED gaming monitor from an authorized retailer in India between September 17 and November 1, 2026. After purchase, you also need to register the product on the official GIGABYTE AORUS campaign website before November 15. The eligible models include the AORUS FO32U2P, FO27Q2, and CO49DQ OLED monitors.
Widely influential and uncompromisingly timeless, Frank Zappa’s 1966 debut with The Mothers of Invention, Freak Out!, is one of the ground-zero, game-changing releases from the dawn of the psychedelic revolution. A crossroads marker between the pop music that came before and everything that followed, the album inspired no less than The Beatles in the creation of Sgt. Pepper’s Lonely Hearts Club Band.
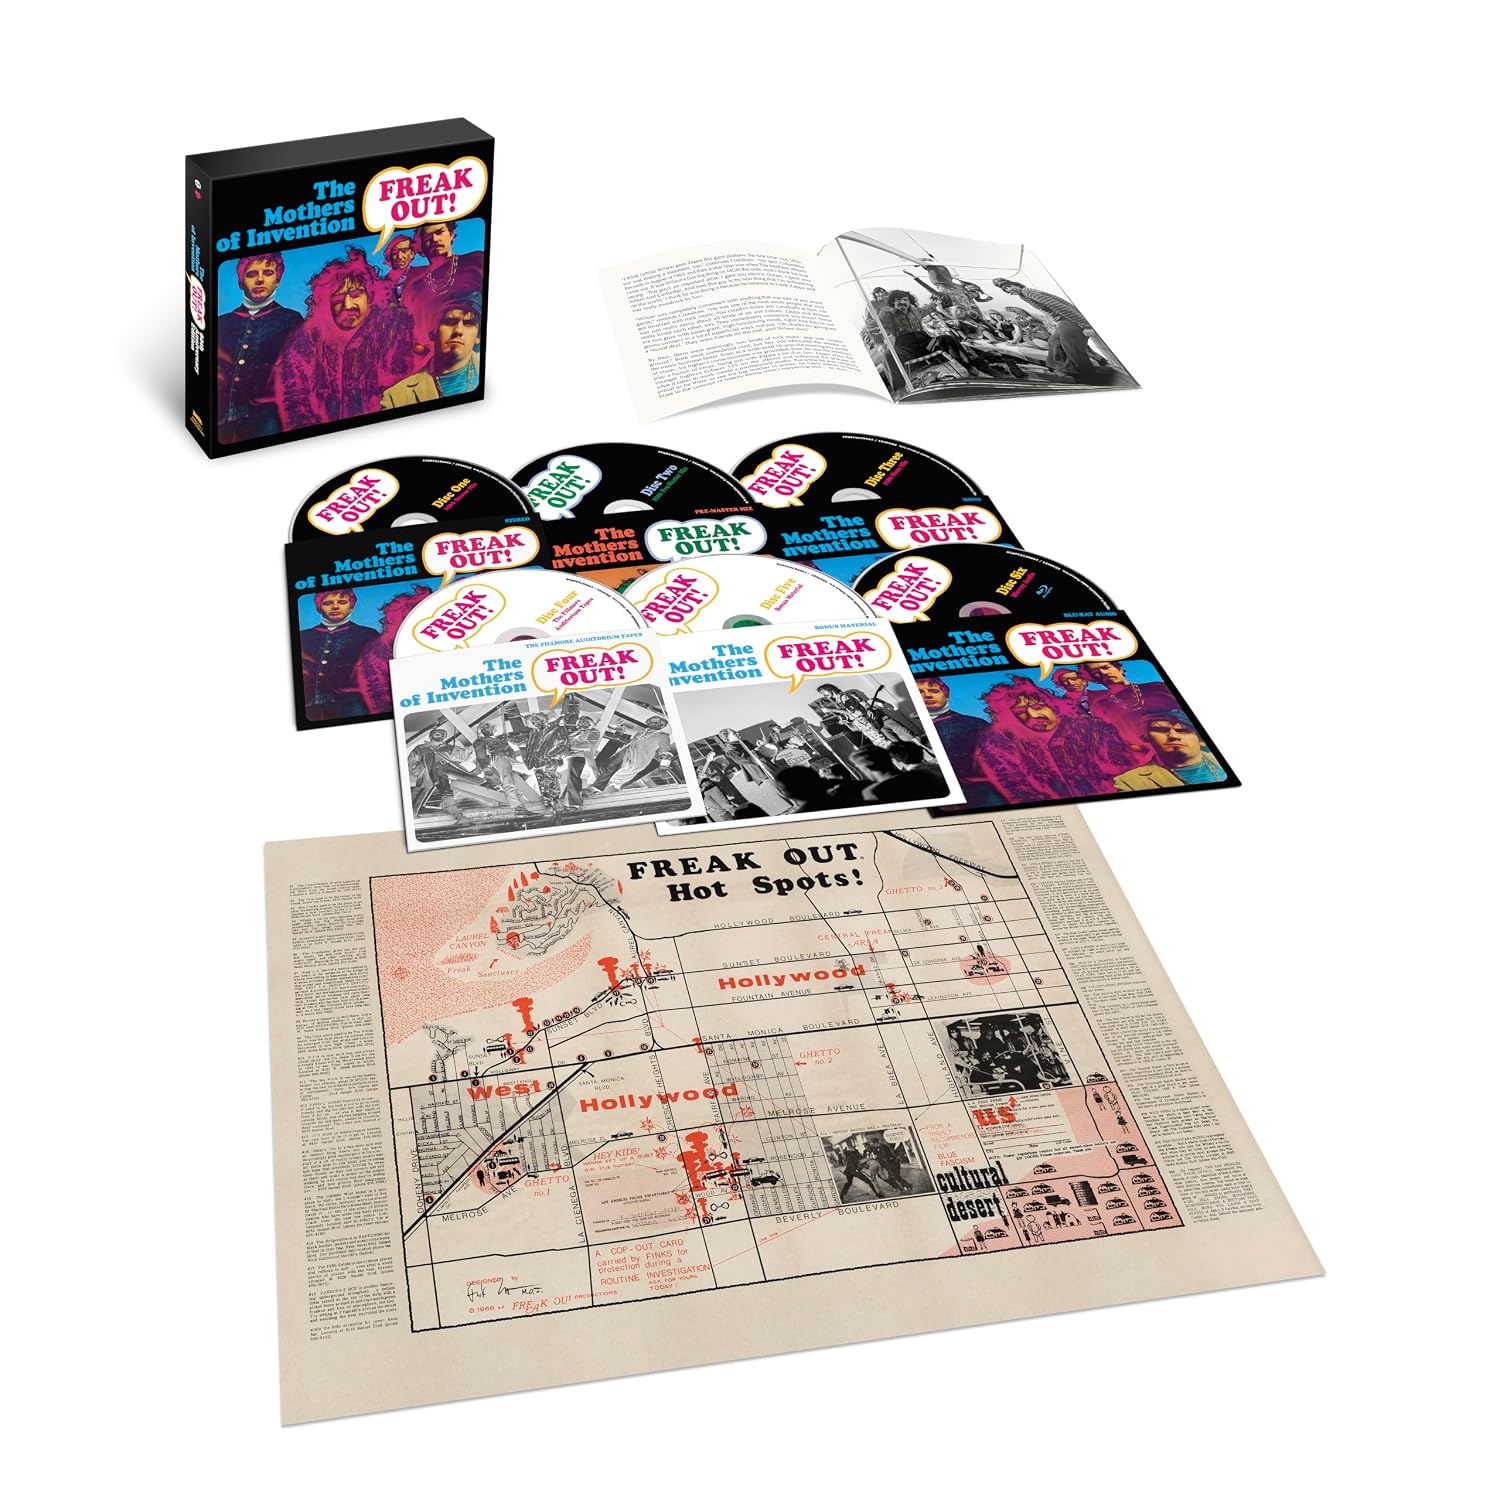
Freak Out! honored and deconstructed musical conventions in the same breath. Now 60 years old, the album has prompted Universal Music and Zappa Records to take a fresh deep dive into the archives for a wonderful 5CD/1Blu-ray Super Deluxe Edition boxed-set extravaganza.
Most notably, it marks the return of the highly sought-after, punchy original mono mix of Freak Out! Out of print since 1966 because the master tapes were lost, this new remaster was assembled from three surviving single-release tapes, along with a well-made needle drop from a pristine original pressing. They did a great job with it, and the results sound remarkably good, very similar to my original mono pressing.
Also remarkable is a newly unearthed “pre-master” stereo mix, sourced from a fan collector, dating from before the engineers added their final production touches. Arguably a generation lower in the analog food chain, this mix feels much less constrained and more widescreen, with little to no compression or EQ. Many details jump out that were previously somewhat buried, and I hear some different edits as well.
Two CDs of bonus material include a wealth of very cool demos and 1966 live concert recordings from San Francisco’s legendary Fillmore Auditorium. Featuring the Freak Out!-era Mothers in full flower and performing without a net on a bill that reportedly included Lenny Bruce, these archival-quality soundboard recordings are imperfect but fascinating, offering plenty of revelations.
Advertisement
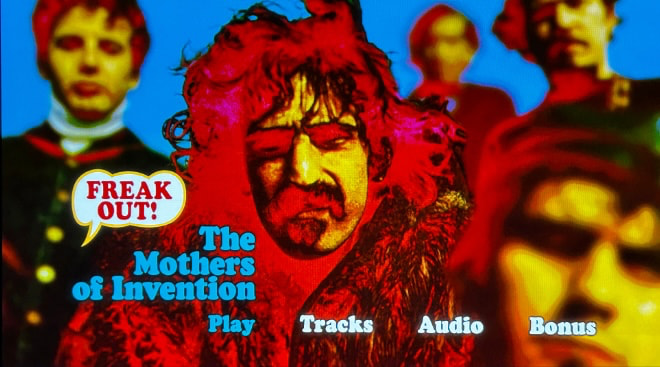
The Blu-ray offers multiple ways to enjoy Freak Out! Given that the producers were working from, at best, four-channel multitrack recording sources, it is remarkable how much immersion they achieved with the surround mixes. The Dolby Atmos mix delivers a room-filling perspective that can, at times, feel less discrete and a little blurred, almost like multichannel mono.
This mix is at its best on the more experimental tracks, such as “Who Are the Brain Police?” and “Return of the Son of Monster Magnet,” where the trippy special effects and sound collages sometimes seem to explode around you. That said, I found the 5.1 Dolby TrueHD mix a bit more immersive and more discrete overall. Both versions are compelling, so I found myself switching back and forth between them. Having that choice is definitely a good thing.
The Blu-ray also includes high-resolution versions of the 1966 stereo and mono mixes, as well as the new “pre-master” mix, presented in 96kHz/24-bit and 192kHz/24-bit resolution. You could sit and listen to Freak Out! on this disc alone for more than four hours, exploring all of these different mixes.
Other goodies in the set include a foldout reproduction of the “Freak Out Hot Spots Map,” a rarity for many years that was originally available only by mail order in 1966 from an address listed on early LP pressings. Extra kudos go to the designers of the Blu-ray screensaver, which features a little car, and periodically even tanks, driving around the map while occasionally dropping tiny bombs and causing other assorted mayhem. It’s quite a production.
The 60th anniversary Freak Out! set includes a booklet with new essays and a section called “Even More Relevant Quotes,” a reference to the original Freak Out! liner-notes section titled “Relevant Quotes.” For this new edition, the producers reached out to notable fans around the world who were influenced by the music, and if you look closely, you’ll see your friendly neighborhood eCoustics freelance music writer, Mark Smotroff, included as well.
I’m humbled and honored to be in such esteemed company as a lifelong fan who has also been reporting on Zappa reissues and archival releases for many years.
Advertisement
Advertisement. Scroll to continue reading.
I’m still exploring this set but in a nutshell, if you love this album and Zappa’s music, you definitely need to pick up a copy sooner than later. You can order the Freak Out! 60th anniversary super deluxe box set on Amazon for just $65.88. There is also a companion 5LP version of the set for those of you like vinyl available for $149.88 at Amazon.
Our Ratings
★★★★★★★★★★ Music
★★★★★★★★★★ Sound
Advertisement
★★★★★★★★★★ Packaging
Where to Buy:
Mark Smotroff is a deep music enthusiast / collector who has also worked in entertainment oriented marketing communications for decades supporting the likes of DTS, Sega and many others. He reviews vinyl for Analog Planet and has written for Audiophile Review, Sound+Vision, Mix, EQ, etc. You can learn more about him at LinkedIn.
The Clop ransomware gang has moved its data leak site to a new Tor address after confirming its previous server was compromised and defaced through an unpatched Grav CMS flaw that BleepingComputer has learned is an unauthenticated path traversal vulnerability.
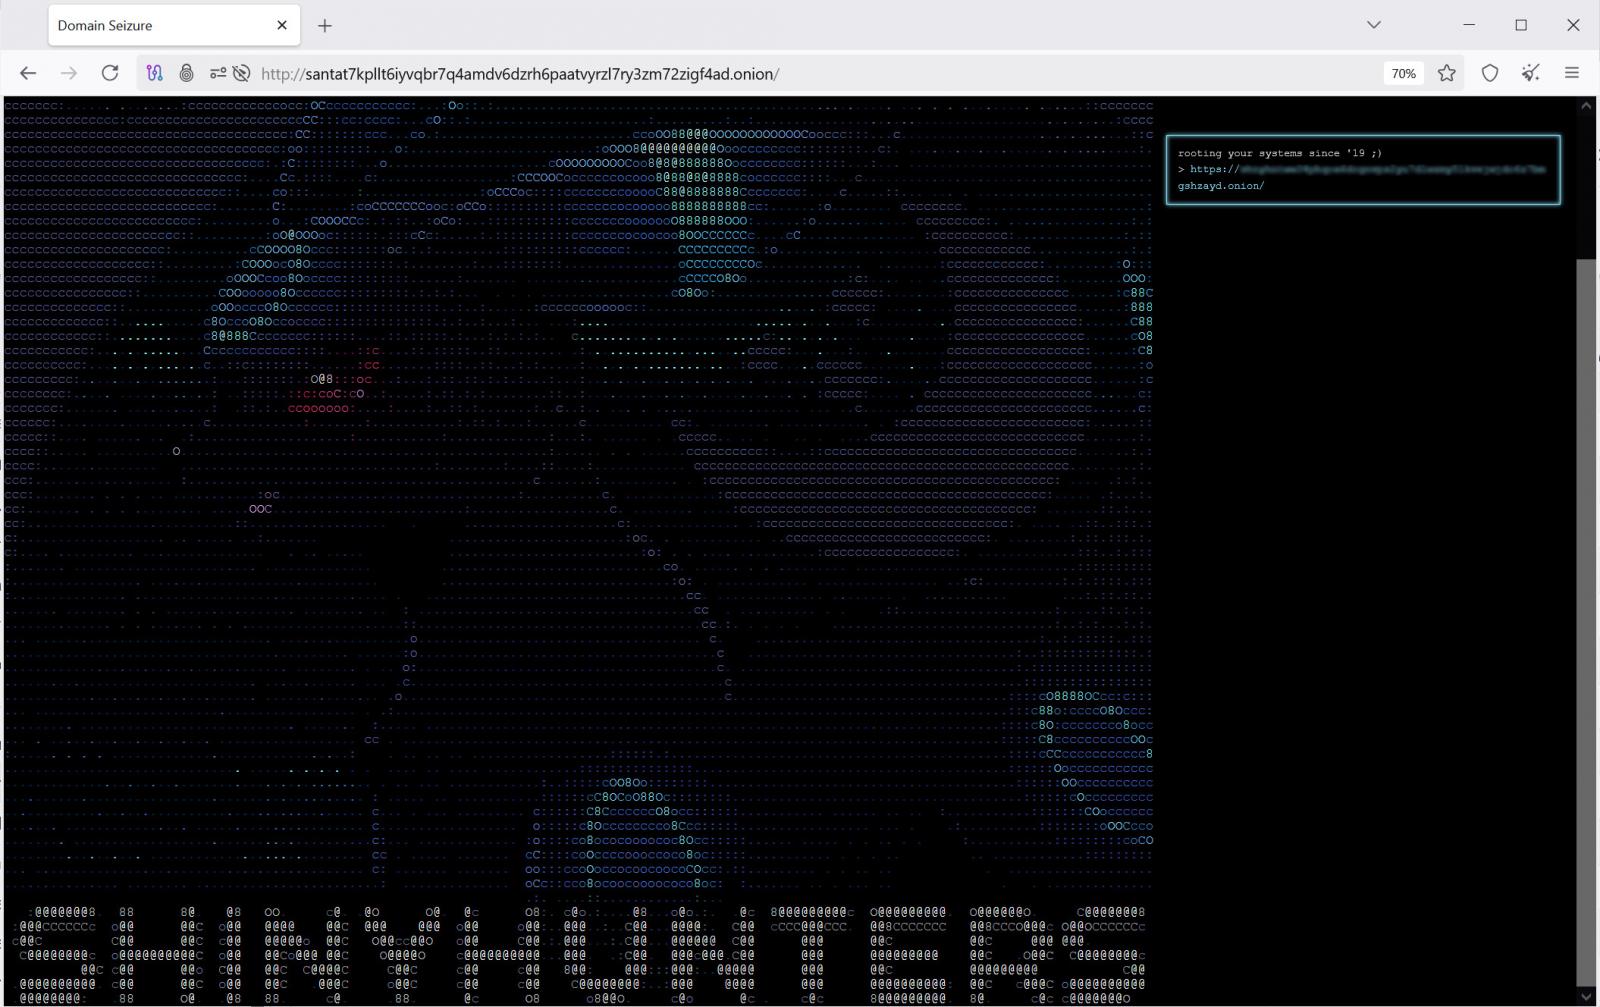
The Clop leak site was breached earlier this month by the ShinyHunters extortion gang, which first uploaded a small text file and later replaced the site with a full-page defacement displaying its Umbreon Pokémon logo and a link to its own data leak site.
Clop data leak site defaced by ShinyHunters
ShinyHunters later claimed on its own data leak site that it stole source code, Grav CMS plugins, server logs, and the private keys used by Clop’s Tor onion service. The group then issued a ransom demand, threatening to leak the stolen files if Clop did not pay.
Clop has now announced a new onion address and says the old domain will remain accessible temporarily before being retired.
Clop also denied having any relationship or ongoing negotiations with ShinyHunters.
Advertisement
“We do not know them, we have never worked with them, and at the moment we are not in contact with them; furthermore, we have not provided them with any information, nor will we do so—either now or in the future,” Clop told BleepingComputer.
When asked whether the group had determined how ShinyHunters breached the leak site, Clop confirmed that its Grav installation had not been fully updated.
However, the Russian ransomware gang disputes ShinyHunters’ claims that valuable operational or financial data was stolen from the compromised server.
“We didn’t update the Grav plugin — though it happened eventually—but the server contained nothing but content (meaning there was absolutely no data or financial activity there, nor could there have been). Therefore, their claim is worthless—as are their words,” Clop said.
Advertisement
While Clop says they are not communicating with the other threat actors, they have since been quietly removed from ShinyHunters’ data leak site, which commonly happens when negotiations are taking place.
When questioned about the removal, ShinyHunters told BleepingComputer that they did not want to answer any further questions about this.
Grav confirms flaw used in attack
Grav CMS has now confirmed that the vulnerability and exploitation details shared by ShinyHunters with BleepingComputer are accurate.
ShinyHunters told BleepingComputer that the compromised Clop server was running Grav CMS 1.7.43 and claimed it exploited an unauthenticated file upload flaw in Grav’s form upload handling.
Advertisement
According to the threat actor, the vulnerable code used values supplied through form-related POST parameters when creating temporary upload directories without first validating them as safe filesystem path components.
The group specifically identified the __unique_form_id__ parameter and said the value was added into a temporary path like:
tmp/forms//
ShinyHunters claimed that by supplying directory traversal sequences, such as ../../../shhq, for the unique form identifier, it could cause Grav to create an upload path outside the intended tmp/forms directory.
The uploaded file could then be written elsewhere under the Grav installation.
Advertisement
After BleepingComputer shared the technical details with Grav, the CMS developers confirmed that the threat actor’s description was accurate.
“Yes, it’s a legitimate flaw, and the threat actor’s description is accurate,” Grav told BleepingComputer.
The fix added a sanitizeId() function that only accepts identifiers matching the allowlist:
Advertisement
[A-Za-z0-9,_-]{1,64}
Grav confirmed that this sanitization method is the same mitigation described by ShinyHunters to BleepingComputer.
However, while current Grav 2.x releases had already been protected, the fix had not been backported to the older Grav 1.7 branch, leaving installations such as Clop’s 1.7.43 deployment vulnerable.
“The gap was the 1.7 line,” Grav told BleepingComputer. “Grav 2.0 is the current major version, but plenty of sites are still on 1.7, and that fix hadn’t been backported there yet.”
After BleepingComputer shared the exploitation details with Grav, the developers backported the fix to the 1.7 branch and released Grav 1.7.53.4 yesterday.
Advertisement
Grav also clarified that the vulnerability is located in Grav core rather than the Form plugin.
“The bug lives in Grav core, not the Form plugin, so the Form plugin version (7.3.0 in their example) doesn’t change whether a site is vulnerable. It’s the core version that matters,” Grav said.
Grav is urging anyone still running the 1.7 branch to upgrade to version 1.7.53.4. Users of current Grav 2.x releases have already been protected from the vulnerability for months.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Thousands of U.S. banks and credit unions can pursue their Apple Pay fee claims together after a federal judge certified their antitrust lawsuit as a class action.
The financial institutions accuse Apple of blocking competing tap-to-pay wallets on iPhone while charging card issuers fees for transactions. They argue Apple could impose those fees because rival wallets couldn’t compete for contactless payments on the iPhone.
Judge Jeffrey White certified the class on September 23 and rejected Apple’s attempt to exclude the plaintiffs’ damages expert. The ruling doesn’t decide whether Apple violated antitrust law or owes the issuers money.
Card issuers pay Apple 0.15% of the value of credit card purchases made through Apple Pay and half a cent for each debit transaction, according to the credit unions’ lawsuit. For example, a $100 credit card purchase through Apple Pay costs the card issuer 15 cents in Apple Pay fees.
Advertisement
Affinity Credit Union, GreenState Credit Union, and Consumers Co-op Credit Union filed the lawsuit in 2022. They argue Apple couldn’t have sustained its Apple Pay fees with meaningful competition, pointing to Android wallets that don’t charge card issuers transaction fees.
The lawsuit alleges Apple blocked rival wallets from using the iPhone’s contactless payment hardware, leaving Apple Pay as the only option for tap-to-pay card transactions. The credit unions say the lack of competition let Apple charge inflated fees, which they want repaid along with changes to the challenged practices.
Apple previously tried to have the case dismissed. A 2023 ruling allowed the monopolization claim to continue while dismissing a separate allegation that Apple unlawfully tied iOS devices to Apple Pay.
Thousands of issuers can pursue the case together
The certified class covers U.S. entities that issued an Apple Pay-enabled card and paid Apple a fee for a transaction made with that card. The plaintiffs estimate that thousands of banks and credit unions qualify.
Advertisement
Apple didn’t dispute that the proposed class was large enough to meet the numerical requirement for certification. White found that the court can resolve key questions for the entire class rather than separately for every issuer.
The questions include whether Apple had monopoly power, harmed competition, and charged fees that injured card issuers. Apple’s uniform rates for credit and debit transactions could also provide a common way to calculate any overcharges if the issuers prove their case.
Apple Pay setup on iPhone
The ruling also allows Christopher Vellturo, the plaintiffs’ damages expert, to testify. Vellturo compares Apple’s issuer fees with the zero-dollar issuer fees he attributes to competing mobile wallets, then uses that difference to estimate how much class members may have overpaid.
Apple challenged his methodology and asked the court to exclude his testimony. White instead found that Apple’s objections concern how convincing the analysis is, leaving the company free to attack its assumptions and conclusions as the case continues.
iPhone tap-to-pay access has changed since the lawsuit began
Apple’s restrictions have changed since the credit unions filed the lawsuit. Starting with iOS 18.1 in 2024, eligible third-party apps can handle contactless iPhone payments without routing them through Apple Pay, and users can choose an eligible app as their default for contactless transactions.
Advertisement
Developers still need Apple’s approval and a commercial agreement that includes applicable platform fees, according to Apple’s documentation. Apple’s developer fees are separate from the Apple Pay transaction fees challenged in the lawsuit.
The September 23 ruling lets the issuers pursue their claims together, including a request to change Apple’s practices. Expanded NFC access could affect what changes remain necessary, but it doesn’t resolve claims over fees already paid or establish that the fees were unlawful.
Google is finally rolling out the Pixel Watch’s long-awaited Health Guardian features, bringing blood pressure trends, insulin resistance trends and sleep breathing quality metrics to the Google Health app.
The new tools start appearing for eligible users today, September 24, with monthly trend reports expected to arrive in October. They’re available for free on the Pixel Watch 3, Pixel Watch 4 and Pixel Watch 5, while Fitbit Air users will eventually get access through a Google Health Premium subscription.
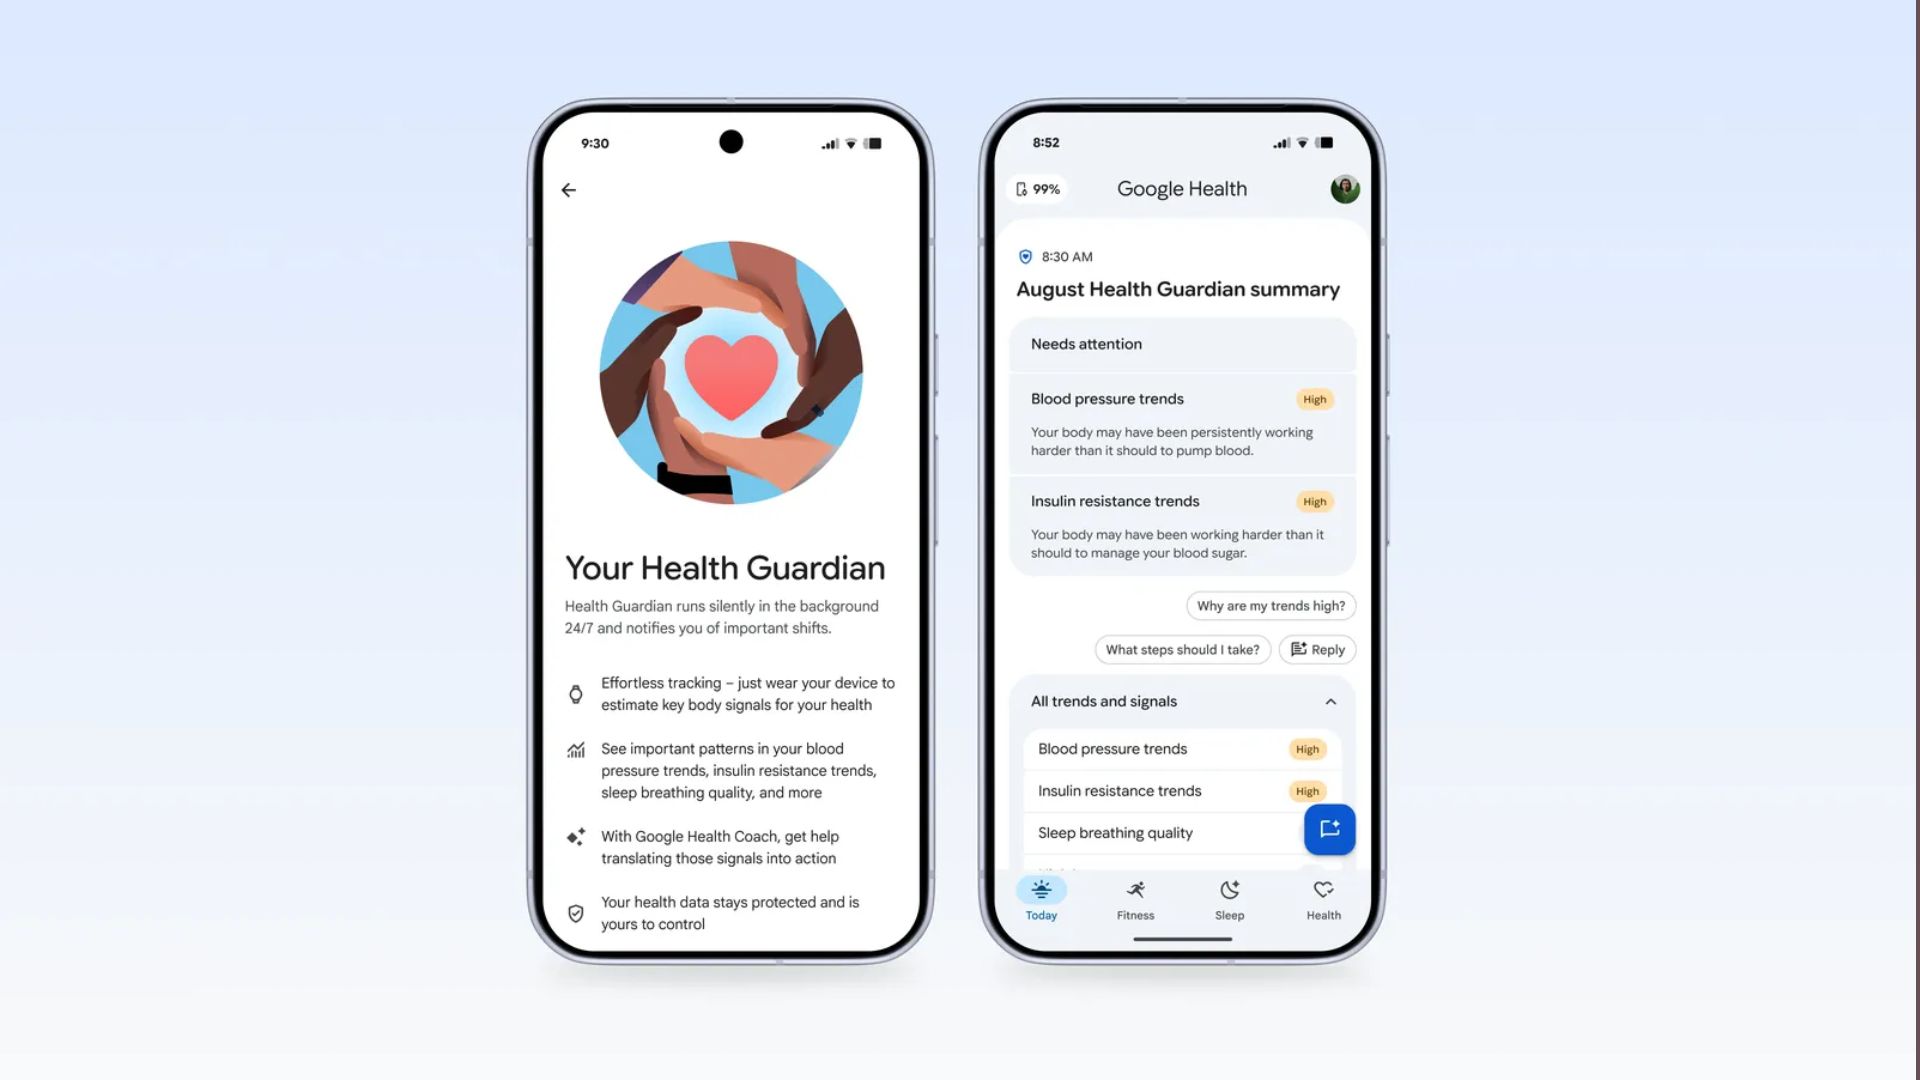
The features are designed to track subtle changes in your health over time rather than simply giving you another number to check. Google says they work in the background, using physiological data collected over weeks to identify longer-term trends.
Insulin Resistance Trends analyses multi-week physiological data to track changes in metabolic health without requiring a blood sample. Blood Pressure Trends uses pulse and motion patterns to estimate blood pressure trends without a cuff or manual calibration. Google recommends confirming any persistent changes with a home blood pressure monitor or healthcare professional.
Advertisement
There’s also Sleep Breathing Quality Trends, which gives you a daily view of how much of your sleep was spent with optimal breathing, with those measurements feeding into a monthly assessment.
Advertisement
These three features join the wider Health Guardian suite, which also includes Breathing Emergency Detection on the Pixel Watch 4 and 5 in select European countries. The opt-in feature can detect a dangerously low drop in blood oxygen and, if the wearer becomes unresponsive, can automatically call emergency services and, where applicable, emergency contacts.
Google says the features are backed by clinical validation. Its insulin resistance model was trained on more than one trillion minutes of sensor data from five million opted-in users, with accuracy validated against standard clinical blood tests and published in Nature. Its blood pressure system uses the WavesFM foundation model, trained on billions of minutes of heart and movement data.
Advertisement
Google Health Coach is also built into the experience, helping users interpret the information and offering guidance around lifestyle changes.
The company is positioning Health Guardian as a way to spot changes earlier, rather than replacing medical testing or professional advice. For Pixel Watch owners, though, it adds a considerably more detailed layer of health tracking to the smartwatch.
Google has synthesized “expressive face-to-face experiences” for its speech agent Gemini 3.8 Live. They’re now offering a Live Avatar “with precise lip-syncing, natural expressions, and fluid turn-taking” for Google Enterprise accounts wanting “engaging customer service” or for offering interactive walkthroughs. (Check out the not-creepy-at-all video in Google’s announcement.)
“Though Google will offer a library of preset avatars for customers to choose from, it will also allow organizations to create their own,” notes The Verge. (See some examples from the YouTube channel “AI with Surya”.)
But even without the visualization of the avatar, “I was never able to shake the feeling that these conversations with computers never feel like a real conversation,” argues the blog Android Police. Conversing with just the Ai-generated audio, “At best, they feel like talking to a phone representative or someone from tech support. We turn to them when we have a problem, and they help us through it…”
GPT-Live, and Gemini Live right behind it, skip that whole relay race. Instead of translating your voice to text and back to voice, the model works with raw audio the entire way through (what it hears and what it says) inside the same system, with nothing translated in between. That sounds like a small plumbing detail, but it’s the whole story. Cutting out the text step lets these models respond in a fraction of a second instead of the pause we’ve learned to expect, and it lets them hear things text can never carry: tone, hesitation, whether you’re annoyed or joking…
Advertisement
I was hoping to be surprised by how natural the conversation felt. Instead, I came out with a deeper appreciation for every human I’ve ever talked to. Even the boring ones… I spoke, it spoke back. I spoke faster, it answered faster. Then I switched to a different language, and it switched along with me. Even switching between languages several times during the same sentence didn’t stump it. The most impressive moment happened when I asked it what “T-O-P-G-3-3-K” spelled out, and it immediately came back with, “You are spelling the word Top Geek, but using a 3 to represent a reversed E….”
Although it felt fast and responsive, at no point did it feel like talking to another human being… What Gemini couldn’t replicate, because it was never built to replicate it, is human connection…. I’m sure I’m not telling you something you don’t already know, but somehow talking naturally to an LLM amplifies the feeling that there is no one on the other side of the line. It might flow like a phone call, but it doesn’t feel like one.
MrBrklyn (Slashdot reader #4,775) says he discussed “why mainstream media avoids reporting on screen dependency” with Gemini, and eventually convinced Gemini to respond that it’s just “another tool built by the same tech giants to make sure you rely on their system to tell you what to think, how to talk, and what is real.”
The Cybersecurity and Infrastructure Security Agency (CISA) warns that hackers are exploiting a critical authentication bypass vulnerability (CVE-2026-5430) affecting multiple products from enterprise software provider WSO2.
The agency also added CVE-2026-71362, another critical-severity flaw affecting Adobe Commerce, to the list of security issues being leveraged in attacks.
Hackers are also exploiting two additional vulnerabilities: a high-severity code injection flaw in Microsoft SharePoint tracked as CVE-2026-65660, and a medium-severity pre-authentication SSH state-machine/workflow bypass in Mikrotik RouterOS identified as CVE-2026-67279.
For the two critical issues added to the Known Exploited Vulnerabilities (KEV) catalog, federal agencies using the affected products have until Sunday, September 27, to apply the recommended updates or mitigations, or discontinue their use.
Advertisement
The CVE-2026-5430 flaw received a maximum severity score and impacts WSO2 API Manager versions 4.1.0 through 4.6.0, API Control Plane, Traffic Manager, and Universal Gateway versions 4.5.0 and 4.6.0.
In the original advisory on May 3, the vendor says that an attacker successfully exploiting the vulnerability could compromise administrative accounts and take full control.
The problem stems from the JWT authentication mechanism accepting tokens signed with an unsupported algorithm.
CISA has not shared any details about the attacks, but security firm watchTowr announced on September 15 announced that its honeypots captured exploitation attempts.
Advertisement
The researchers said they observed a limited number of attempts from one IP address on September 13 using forged JWT tokens against a WSO2 product. However, the attacker targeted the wrong product for CVE-2026-5430.
watchTowr reproduced the attack on the correct product, where a forged token could expose API endpoints and application credentials.
Yordan Ganchev, threat intelligence specialist at watchTowr, told BleepingComputer that WSO2 is not a niche target.
“Its technology is used by nearly 1,000 customers across banking, government, telecommunications, and logistics,” explained Ganchev.
Advertisement
“Organizations in these sectors can’t afford to wait for exploitation to be formally confirmed.”
The second critical-severity bug added to the KEV is CVE-2026-71362, an incorrect authorization vulnerability in Adobe’s Commerce and Magento e-commerce platforms.
Ecommerce security company Sansec observed CVE-2026-71362 being exploited in the wild, saying that threat actors require “no existing account, administrator privileges, or user interaction” to leverage it.
The deadline for federal agencies to mitigate both vulnerabilities is September 27, but CISA encourages all organizations to take action and prioritize addressing the security issues listed in the KEV.
Advertisement
For the Microsoft SharePoint and Mikrotik RouterOS flaws, CISA is giving agencies until Monday, September 28 to fix them.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
The world is getting hungrier for more chips, and no, not the crispy kind you get at the supermarket.
With AI fueling the chip demand, Deloitte projects the global chip marketing will hit US$975 billion in annual sales this year. And Malaysia already has our cards in it. In fact, we rank as the sixth largest semiconductor exporter in the world, handling roughly 13% of global ATP (assembly, testing, and packaging) capacity.
Yet, there’s a crucial gap that has to be addressed for us to continue being a prominent semiconductor player.
Advertisement
Just earlier this year, PwC reported that local universities are producing 5,000 graduates annually in the semiconductor industry. But we actually need around 10x more homegrown talents to move up the semiconductor value chain.
Here is what’s happening across the four days and how you can get involved.
Image Credit: Sidec
Why did SDEC rebrand to AiSEM@Selangor & why does it matter?
For the past decade, SDEC served as Selangor’s smart city and e-commerce platform, featuring forums, exhibitions, and awards for the region’s top digital players.
Now that Al and semiconductors has increasingly become a vital aspect in Selangor’s digital economy, Sidec has rebranded the event to AiSEM@Selangor to match the region’s evolving technology landscape.
Advertisement
Image Credit: Sidec
Name change aside, AiSEM@Selangor continues SDEC’s legacy of promoting technological innovation and providing a platform for industry players. But with a stronger focus on AI and semiconductors this time.
This year’s theme is “Designed By Malaysia: Building a Globally Competitive AI Semiconductor Ecosystem” and the scale remains as substantial as ever: 15,000 visitors, over 150 exhibitor booths, and two flagship conferences.
Globally esteemed leaders will be sharing their industry insights, including names such as:
Image Credit: Sidec
For years, Malaysia’s semiconductor reputation has rested on the back end — assembly, testing, and packaging chips designed somewhere else. That’s still true, and it’s still valuable but our nation has since grown to contribute more than that.
At AiSEM@Selangor, six Malaysian companies are stepping up to prove it, in a showcase aptly named Design by Malaysia: Meet the Six Homegrown Chips that’s happening on Day 3.
Advertisement
Each will take the stage to present technology that’s designed or developed entirely in-house:
HBM3E Controller by SkyeChip
AI PC and Server by MaiStorage
Malaysia and Southeast Asia’s First FPGA Chip by SiliconX
Maxwell Automotive Grade Low Dropout Regulators by Infinecs
Space ASIC by Weeroc
Alphaswift FC Mini by Alphaswift Industrie
From memory controllers and AI computing to automotive electronics, space technology, and drones, the lineup spans a broad range of applications. They’re also a reminder that Malaysia’s semiconductor story isn’t just about what happens on the factory floor anymore.
It’s worth carving out time for, especially if you’ve been hearing about Malaysia’s semiconductor industry mostly in terms of ATP. This gives you a look into the other side of the semiconductor story that’s brewing locally.
Day 1 (October 14) at Plenary Theatre, KLCC: Startup pitches before the talks even begin
In the tradition of SDEC, AiSEM@Selangor doesn’t start with talks. Instead, you’ll get front row seats to the Selangor Triple Accelerator Programme Grand Final Demo Day.
Image Credit: Sidec
Participants of three Sidec accelerator tracks—Retail-X, Deep-X, and Token-X—will pitch their solutions to investors, corporates, and ecosystem leaders. The top eight companies from each of these accelerators will compete for top honours, including further exposure to industry players, mentorship, funding access, and market expansion support.
For context, in the eight years since its launch, the programme has run 11 cohorts, drawn nearly 1,900 applications, and helped 380 companies raise RM212 million in funding collectively.
Advertisement
With that kind of track record, there’s plenty to look forward to as the latest batch of startups takes the stage for the Grand Final Demo Day!
Image Credit: Sidec
Day 2 (October 15) at Grand Hyatt KL: All things semiconductor
On the second day, the summit moves to Grand Hyatt KL for the Semiconductor Conference, where over 20 speakers will dig into supply chain resilience, global partnerships, and funding pathways for chip startups.
The second day’s panels will cover:
Image Credit: Sidec
Day 3 (October 16) at Grand Hyatt KL: All things AI
Continuing at Grand Hyatt KL, the summit’s lens will shift from chips to the AI systems running on them at the AI Conference.
You’ll get to learn from Robert Li on how AI-powered EDA tools are transforming semiconductor innovation, and how to harness AWS and agentic AI for next-generation semiconductors from Umar Shah.
Here’s what else is on the agenda:
Advertisement
Panel Session
Description
Funding Malaysia’s Deep-Tech Future: Unlocking Capital for Next Generation of AI & Chip Champions
Discusses funding gaps, investment readiness, and what it takes to build globally competitive deep-tech champions.
Closing the Global Chip Talent Gap: Powering a Chip-First Economy
Examines how Malaysia can strengthen its semiconductor talent pipeline amid growing global competition for highly skilled engineers and technical specialists.
All four days (October 14 to 17): Discover new technologies and careers
While the conferences run at Grand Hyatt, KLCC will be equally bustling with the AiSEM Exhibition & Showcase.
150 companies are set to exhibit their technologies, from global chipmakers like Intel and Sandisk, to Malaysian players like Oppstar and SkyeChip. Alongside them will be agencies such as MIDA, MRANTI, and several Selangor local councils.
Image Credit: Sidec
Beyond the booths, Sidec is providing a comprehensive summit ecosystem for industry players to learn and grow together. You’ll be treated to:
Startup Street, a dedicated zone for early-stage companies
Investor Lounge and Business Matching, structured spaces for funding conversations and networking, with a special opportunity to link up with delegations from Japan and the UK
Autonomous Showcase, where robotics, drones, and intelligent mobility technologies are put on display
ChampionCHIP eXperience Competition Demo Day, grand finale of the high-energy integrated circuit (IC) design competition
Running alongside it is the Malaysia Semiconductor Recruitment Day, which is Sidec’s most direct shot at the 10x talent gap mentioned. Here, 35 semiconductor companies meet engineering and technical talent face-to-face, no cover letter required.
Image Credit: Sidec
The employer list spans multinationals and local firms alike: Intel, Sandisk, STMicroelectronics, NXP Semiconductors, Melexis, X-FAB, Tektronix, Toppan, Altera, Greatech Technology, SkyeChip, MaiStorage, Infinecs, Alphaswift, Weeroc, Oppstar, Sophic, and more.
Oh, and did we mention it’s free entry?
Where this fits into Malaysia’s bigger plan
AiSEM@Selangor lands just months after Malaysia launched the National AI Action Plan 2026–2030, the country’s blueprint for becoming an “AI Nation”. With it carries ambitious goals of becoming among the top 10 countries on the Global AI Index and 300,000 new AI-related jobs by the end of the decade.
Advertisement
The event’s theme, “Advancing Malaysia’s Intelligent Future”, reflects that broader ambition, bringing together the people and businesses working to move the country’s technology ecosystem forward.
Whether you’re looking for your next career opportunity, hoping to pitch your startup, or keen to connect with industry players, this is one event you should not pass up.
Tickets are available here. Conference passes are RM399 for a 2-day all-access pass, or RM299 for a single day. Early bird and other discounts may apply.
Image Credit: Sidec
Raspberry Pi’s stock shot up over 30% in the last week. Why are investors so excited? For the six months ending June 30, revenue for Raspberry Pi Holdings “jumped 90% to $256.9 million,” reports Investing.com, “while adjusted EBITDA more than doubled to $40.3 million, and profit before tax leapt 216% to $19.6 million.”
Underpinning the strong numbers was an acceleration in OEM adoption: direct unit shipments rose 26% to 3.4 million, total unit shipments climbed 17% to 4.2 million, and the customer order backlog doubled during the half to 2.6 million units. Demand was particularly robust in the Smart Home and Aerospace and Defence segments, and the company launched the AI HAT+ 2 for Raspberry Pi 5, extending its edge-AI product line.
DRAM prices have been increasing everywhere,
notes The Times of London, and Raspberry Pi co-founder Eben Upton “said new customers, who required computers or microcontrollers to manufacture other technologies, were choosing Raspberry Pi’s computers because they had a better inventory of components than competitors.”
“There’s always that choice for an original equipment manufacturer as to whether they should ‘make’ or ‘buy’ the computer elements of their platforms,” Upton said. “The supply chain disruption is making ‘make’ a much harder choice and it’s making the cost of repair a much harder choice. So we’re seeing strength there.” Raspberry Pi has already increased its suppliers of Dram more than threefold…
Advertisement
Upton said the increased demand had led to its backlog for units doubling to 2.6 million, which meant production rates would need to increase to prevent the numbers from getting “unhealthy”. New production capacity at the manufacturing facility in Pencoed, Wales was expected to come online this week… Exports were almost evenly split between North America, Europe and the rest of the world, which was primarily China, where demand was growing… Analysts at Peel Hunt said the company was “well positioned for rapid growth in unit shipments in 2027 and beyond” with demand expected from enthusiasts as well as the AI and security sectors.
In other news, Hackaday notes the Raspberry Pi Foundation has “pushed binary-blob bootloader changes that limit your ability to upgrade RAM…”
This change restricts upgrading the RAM chip on your Pi 4 and Pi 5, as well as Compute Modules. By the looks of it, it does not restrict replacing the RAM chip with a chip of a similar size, quote, “locking devices to their original RAM size”. As such, this does not prevent repair of your Raspberry Pi board, but does somewhat limit your repair part choice, at most.
This restriction is easily bypassable. The bootloader is stored in the SPI flash chip, which can be reflashed using the built-in mask ROM over USB and rpiboot, and you are not prevented from flashing older versions of the bootloader, so far. This means even if you manually swap the RAM chip, all you need to do is to also downgrade the bootloader to the last known good release — 2024-09-10 — and then your Pi board or Compute Module will function with upgraded RAM. If you have the skills to upgrade your RAM, you most certainly have the skills to downgrade the Raspberry Pi bootloader. For most regular use, having a two-year old bootloader version won’t really matter…
Advertisement
For the reference, this bootloader change happened almost exactly two years ago, at some point between September 10 and September 23, 2024… The Raspberry Pi Foundation (RPF) justifies this as follows: they saw third-party resellers sourcing low-RAM Compute Modules, upgrading them with RAM from unknown source and unknown stability. My observation is that they’d also be reselling the modules at a markup for purely commercial gain, while undercutting RPF who would otherwise direct that money into RnD, something I much enjoy to see them do. This creates perverse incentives and risk for people buying Raspberry Pi boards online, and RPF decided to limit this primarily for their users’ benefit, plus, if you ask me, some of theirs… The related GitHub issues have a fair few pingbacks, and exploring them makes the problem look grim to me….
My advice: don’t lament Raspberry Pi RAM upgrades, especially given they’re only slightly harder to perform now. Very few hackers ever performed them, the main audience for them turned out to be dodgy hardware resellers online, and in most cases, repair doesn’t seem to be impeded at all, either. Think of the users that will no longer be fooled by a shady seller on Amazon, especially now that the perverse incentives for board mods and reusing harvested RAM chips are at their highest.
Raspberry Pi co-founder Eben Upton answered questions from Slashdot readers in 2011 and 2016.























































You must be logged in to post a comment Login