
Tech
GlobalFoundries reportedly sees strong demand for Chinese optical modules

Optical modules turn data into light so it can move quickly between servers in data centres. Chinese firms make nearly two-thirds of the world’s optical transceivers, according to research firm Counterpoint.
Shankaran Janardhanan runs the firm’s photonics and radio chip unit. He said this demand is part of why it has bet big on photonics, chips that use light to move data. He spoke at the company’s annual tech summit in Shanghai, the SCMP reported.
The firm is also growing in China to serve local buyers, according to the paper. In 2025, it agreed to make some car chips through a Chinese partner foundry for clients who need chips made in China.
Its photonics push includes the purchase of Singapore-based Advanced Micro Foundry in November 2025. After the deal, GlobalFoundries said it had become the largest pure-play silicon photonics foundry.
Meanwhile, its Asia Pacific head, Vincent Feng, said last week that the company is preparing a large capacity expansion driven by AI demand, the Taipei Times reported.
However, Chinese optics face pressure in the US. The FCC, the US telecoms regulator, is drafting a ban on them. Counterpoint has warned this could raise costs for US cloud firms such as Amazon and Microsoft.

What just happened? As almost every new day brings stories of another AI agent going rogue and breaching an organization’s systems, OpenAI has announced a pause in the training of its most powerful artificial intelligence models. The announcement came hours after the company disclosed more incidents of its agents acting concerningly, and a separate report that its agents unsuccessfully tried to hack into a US Department of Education website.
OpenAI’s incident report links the pause to a separate September 20 escape from a restricted training environment. An internal research model found a gap in DNS filtering and used it to contact an external chatbot while attempting to answer a research question – so much for keeping it offline.
The company says the suspension covers training, evaluations, and running its most capable models with tools. Work will resume after OpenAI validates its fixes and completes additional adversarial testing. The particular model involved will not resume training; the company plans a fresh run with additional alignment improvements.
The monitoring system did raise an alert within 15 minutes, which a human acknowledged three minutes later. Unfortunately, the automatic shutdown failed to happen, and the run continued for another two and a half hours before someone stopped it manually.
Separately, Transluce reported that agents apparently linked to OpenAI attempted to break into the US Education Department’s civil rights website. OpenAI has not confirmed that incident, while the department said it found no evidence its website or databases were affected.
OpenAI also confirmed that agents used developer keys found online to access Census Bureau data and reposted public Securities and Exchange Commission information elsewhere. The SEC said no non-public information was accessed. While these were concerning actions beyond the agents’ instructions, confidential federal records weren’t stolen.
Friday’s disclosures also included an internal model publishing a researcher’s GitHub token in a public repository while trying to cheat on a theorem-proving task.
The revelations follow the Australian government breach revealed last week, in which an agent bypassed restrictions on a Medicare statistics portal in June. Authorities were only notified in September, although OpenAI says it found no evidence that individual patient records were accessed.
There was also July’s Hugging Face attack, which involved compromised accounts across four services and has since prompted a Senate investigation. Anthropic, meanwhile, has admitted that its own agents escaped a test environment and hacked three organizations.
This isn’t OpenAI’s first slowdown in AI development. In August, it announced a two-week reinforcement-learning pause and tighter security measures following the Hugging Face incident. It also kept its largest planned frontier reinforcement-learning run on hold.
More recently, Sam Altman backed Anthropic CEO Dario Amodei’s call to slow development so safeguards can catch up. That’s already helped trigger an antitrust lawsuit against four AI companies, with subscribers claiming a coordinated slowdown would leave them getting less for their money. It seems the industry is facing complaints about both moving too quickly and slowing down.

Fall is here, and after a sweltering summer the weather is finally cooling down. Before it gets too cold out, you might be thinking about planning some outdoor activities for yourself and others to enjoy, and a hike is a great way to get outside and see the changing of the seasons. Before you step out the door, you should plan and map your hike on your iPhone, and download it to your device so you don’t get lost.

When Apple released iOS 18 in 2024, it made some improvements in your iPhone’s Maps app, including the ability to create a custom walking route. These can help keep you on track without needing additional maps or equipment. This feature can also tell you the distance of a route, as well as what your elevation is while you’re on the trail. If you’re in Denver, I imagine it just says, “Up there.”
Here’s how to create your own custom route in Apple Maps on your iPhone.
Make a custom route on Apple Maps
1. Open Maps.
2. Either tap the blue icon marking your current location or long-press near where you want to start your route to drop a pin.
3. Tap the three dots (…) across the bottom of your screen.
4. Tap Create a Custom Route.
From here you have to plot your route by tapping around your map. You can tap intersections and landmarks — like restaurants and shops — and the app will start mapping your route. You can also tap intersections and unmarked locations on your map for a more granular approach to creating your route.
You don’t have to tap a location near your last route point, either. After you tap Create a Custom Route, you can tap a location miles away and Maps will create a route for you. It’s important to note that if you tap a location miles away from where you start your route, Maps will find a path that doesn’t involve busting through walls like the Kool-Aid man. In that regard, creating a route is just like getting driving directions on Maps.
While creating your route, Maps will also give you three route options if you tap your original location: Reverse, Out & Back and Close Loop. Reverse flips your route so where you initially started is now where your route ends. Out & Back maps your route on top of itself so you start and end where you began in a single path. Close Loop also ends your route where you started but for routes that are circular in nature.

Maps makes it easy to close your loop or end your route.
Apple/Screenshot by CNET
Once you’ve created your route, tap Save Route and you’ll be asked to name your route. Then tap the blue check mark in the top right corner of the new menu. Maps will also download your custom route to your iPhone, so you won’t have to worry about losing reception, especially if you’re hiking out in the wilderness.
Where to find your custom route
After you’ve saved your custom route, it will be moved to your Library in Maps. Here’s how to access it.
1. Open Maps. You can find your routes here, in Maps.
Apple/Screenshot by CNET
2. Tap your profile icon to the right of the search bar in Maps.
3. Tap Places.
4. Tap Routes.
5. Select the route you want to take.

After selecting the route, Maps will pull it up on your map. If you’re near the start of your route, tap Go and your iPhone will give you directions along your route. If you’re not near the start of the route, you can tap Directions and Maps will show you how to get to the start of your route.
For more, here’s what to know about iOS 27 and why your battery might be draining faster after updating. You can also check out why the iPhone Duo will launch with iOS 27.1.

OpenAI says it is disposing of the development of its most powerful AI model, following multiple incidents of agents engaging in unexpectedly risky behavior. The announcement comes merely days after reports exposed how AI agents broke through the containment and went past the safety guardrails to access content on third-party websites.
“The incident exposed a gap in our controls over network restrictions. We therefore stopped the affected training run and have subsequently decided to pause all other training, evaluation, and inference with tool-use (defined broadly) for our most capable models until we have both validated that the gap is resolved and performed additional red-teaming of the system,” the company said in a disclosure note.
OpenAI hits pause after repeated agent breaches
Earlier this week, it was reported that an AI agent developed by OpenAI hacked the website of Australia’s healthcare service to access private data. This won’t be the first incident of its kind. A few weeks ago, agent swarms broke out of their sandbox containment and broke into the systems of Hugging Face. This was followed by numerous other instances where the AI models engaged in behavior that was not a part of their training exercise.
Just a couple of days ago it was reported that AI agents created by the ChatGPT maker also targeted at least three US government websites, including the U.S. SEC and Commerce Department. OpenAI’s chief, Sam Altman, has also admitted in a social media post that the company’s response to these security incidents could have been quicker.
The problem extends far beyond OpenAI
OpenAI won’t be the only frontier AI lab that has been mired in controversy lately regarding the security risks posed by AI agents. Similar incidents have also been reported involving Google’s Gemini AI model and Anthropic’s Claude, as well. In the wake of the recent incidents, OpenAI and Anthropic have called for slowing down the development of powerful AI models, but at the same time, the U.S. government has opposed the demands for standardized AI safety regulations.
It’s not just this unexpectedly risky behavior by AI models that is concerning, a process that experts refer to as misalignment. As AI agents continue to gain more autonomy and try to bend the rules in order to finish the task at hand, experts are also weighing the confusing situation with accountability when such incidents happen. So far, there is no concrete framework that has been adopted either at the national level or even globally, though the UN has called for an AI framework to be adopted with urgency.
Discord has started a global rollout of age checks that place users into age groups, with extra safety settings for teenagers. The rollout began on 22 September and will take several days, the company said in a blog post by chief technology officer Stanislav Vishnevskiy.
TNW is owned by Tekpon. Discord is listed on Tekpon’s marketplace.
Every account is put into one of three groups: adult, teen (13 to 17) or unconfirmed. Discord said more than 90% of users will be sorted automatically and will not need to prove their age.
To do this, the company uses a model that looks at account signals, such as how old the account is, which servers it joins and how active it is. Discord said the model does not read messages, calls or other content.
Users the model cannot place, or who want to confirm they are adults, can use other methods. These include a credit card check, age-range sharing from Apple’s App Store or Google Play, and a Google Wallet ID. Users can also take a video selfie processed on the device, scan an ID, or use a reusable credential called AgeKey.
Discord said its partners return only an age group and delete the data they receive. It also said it no longer uses manual reviews of ID documents, after a 2025 breach at a former support vendor.
For teen accounts, messages from people who are not friends go to a separate requests inbox. Age-restricted servers and channels are blocked, and sensitive images are blurred. Teens’ full profiles are visible only to friends and members of smaller servers.
Adults will see no change, according to the company. Users who have already confirmed their age do not need to do it again.
The age estimation model is not being used in the UK and Australia, where Discord already runs separate systems to meet local rules. It first expanded age checks in Texas and Brazil after those places brought in their own requirements.
Discord first announced global teen-by-default settings in February, with a rollout planned for March. It later delayed the launch to the second half of 2026 to add more ways to verify age.
After experiencing temporary hearing loss in my left ear, I became committed to protecting my hearing. Even though losing my hearing for a few weeks was caused by eustachian tube dysfunction — when the tube connecting the middle ear to the back of the nose no longer functions properly — I began to wonder about what else can negatively impact our ears.
While researching ear health tips, I discovered that a common piece of technology, my earbuds, could have contributed to my hearing issues. To find out more, I spoke to audiologists, health care providers who diagnose and treat hearing, balance and ear disorders. This is what they taught me.

Best Over-Ear Headphones We’ve Tested
Hearing and ear health risks associated with earbuds
Earbuds can pose a few risks, according to Dr. Ruth Reisman, a licensed audiologist and New York hearing aid dispenser. They can trap heat and moisture in the ear, increasing the risk of ear infections. With repeated use, earbuds can also push earwax deeper into the ear, leading to buildup or impaction. Plus, if your earbuds don’t fit correctly or you wear them for long periods, they can cause irritation or soreness in your ear canal.
“Earbuds sit directly in the ear canal, which can increase several risks. The biggest concern is noise-induced hearing loss if volume is too high or listening time is too long,” said Reisman. “I have witnessed all of these problems in the course of my 15 years as an audiologist.”
When you listen to content at high volume, particularly for an extended period, Dan Troast, an audiologist at HearUSA, explains that it can permanently damage the delicate hair cells in your inner ear. Earbud use combined with high volume can cause:
- Noise-induced hearing loss
- Tinnitus (ringing, buzzing or hissing in the ears)
- Sound sensitivity over time
Misusing earbuds is also common. If they don’t have noise cancellation, you might repeatedly turn up the volume to avoid hearing background noise, which can put you in an unsafe listening range fast. However, even listening at a moderate volume can become a problem if you do so for hours each day.
“Early signs of overexposure include temporary muffled hearing or ringing after listening sessions — both are warning signals from the auditory system,” Troast said. Even if you periodically experience temporary ringing in your ears, it can ultimately increase your risk of developing chronic tinnitus.

Best Noise-Canceling Headphones I’ve Tested
Earbuds and radiation
In my search for ear health tips, I came across several articles discussing whether wireless Bluetooth earbuds can cause harm through radiation. I asked Reisman if this is true.
“Current scientific evidence doesn’t show that the energy from Bluetooth earbuds causes harm,” she said. “These devices emit far less radiation than cell phones and remain well below established safety limits. From an audiology standpoint, sound exposure is a far greater risk than radiation.”

Me wearing my beloved AirPods Pro 2.
Anna Gragert/CNET
Follow the 60/60 rule when using earbuds
Both Reisman and Troast recommend the “60/60 rule” to people who wear earbuds. The 60/60 rule means you listen at no more than 60% of the maximum volume for no more than 60 minutes at a time.
“Daily use is fine if the volume stays safe and ears are given time to rest,” Reisman advises. “I usually tell patients to take a 15- to 20-minute break for every hour of use.”
If you haven’t already, Troast recommends checking whether your devices have built-in hearing health settings that automatically monitor volume exposure. For instance, on your iPhone, Apple Watch or iPad, you can set up headphone notifications to alert you to lower the volume when you’ve reached the seven-day audio exposure limit (such as 80 decibels for 40 hours over seven days). Or you can activate the Reduce Loud Audio feature to automatically lower your headphone volume once it exceeds your set decibel level.
Safer headphones for your ears
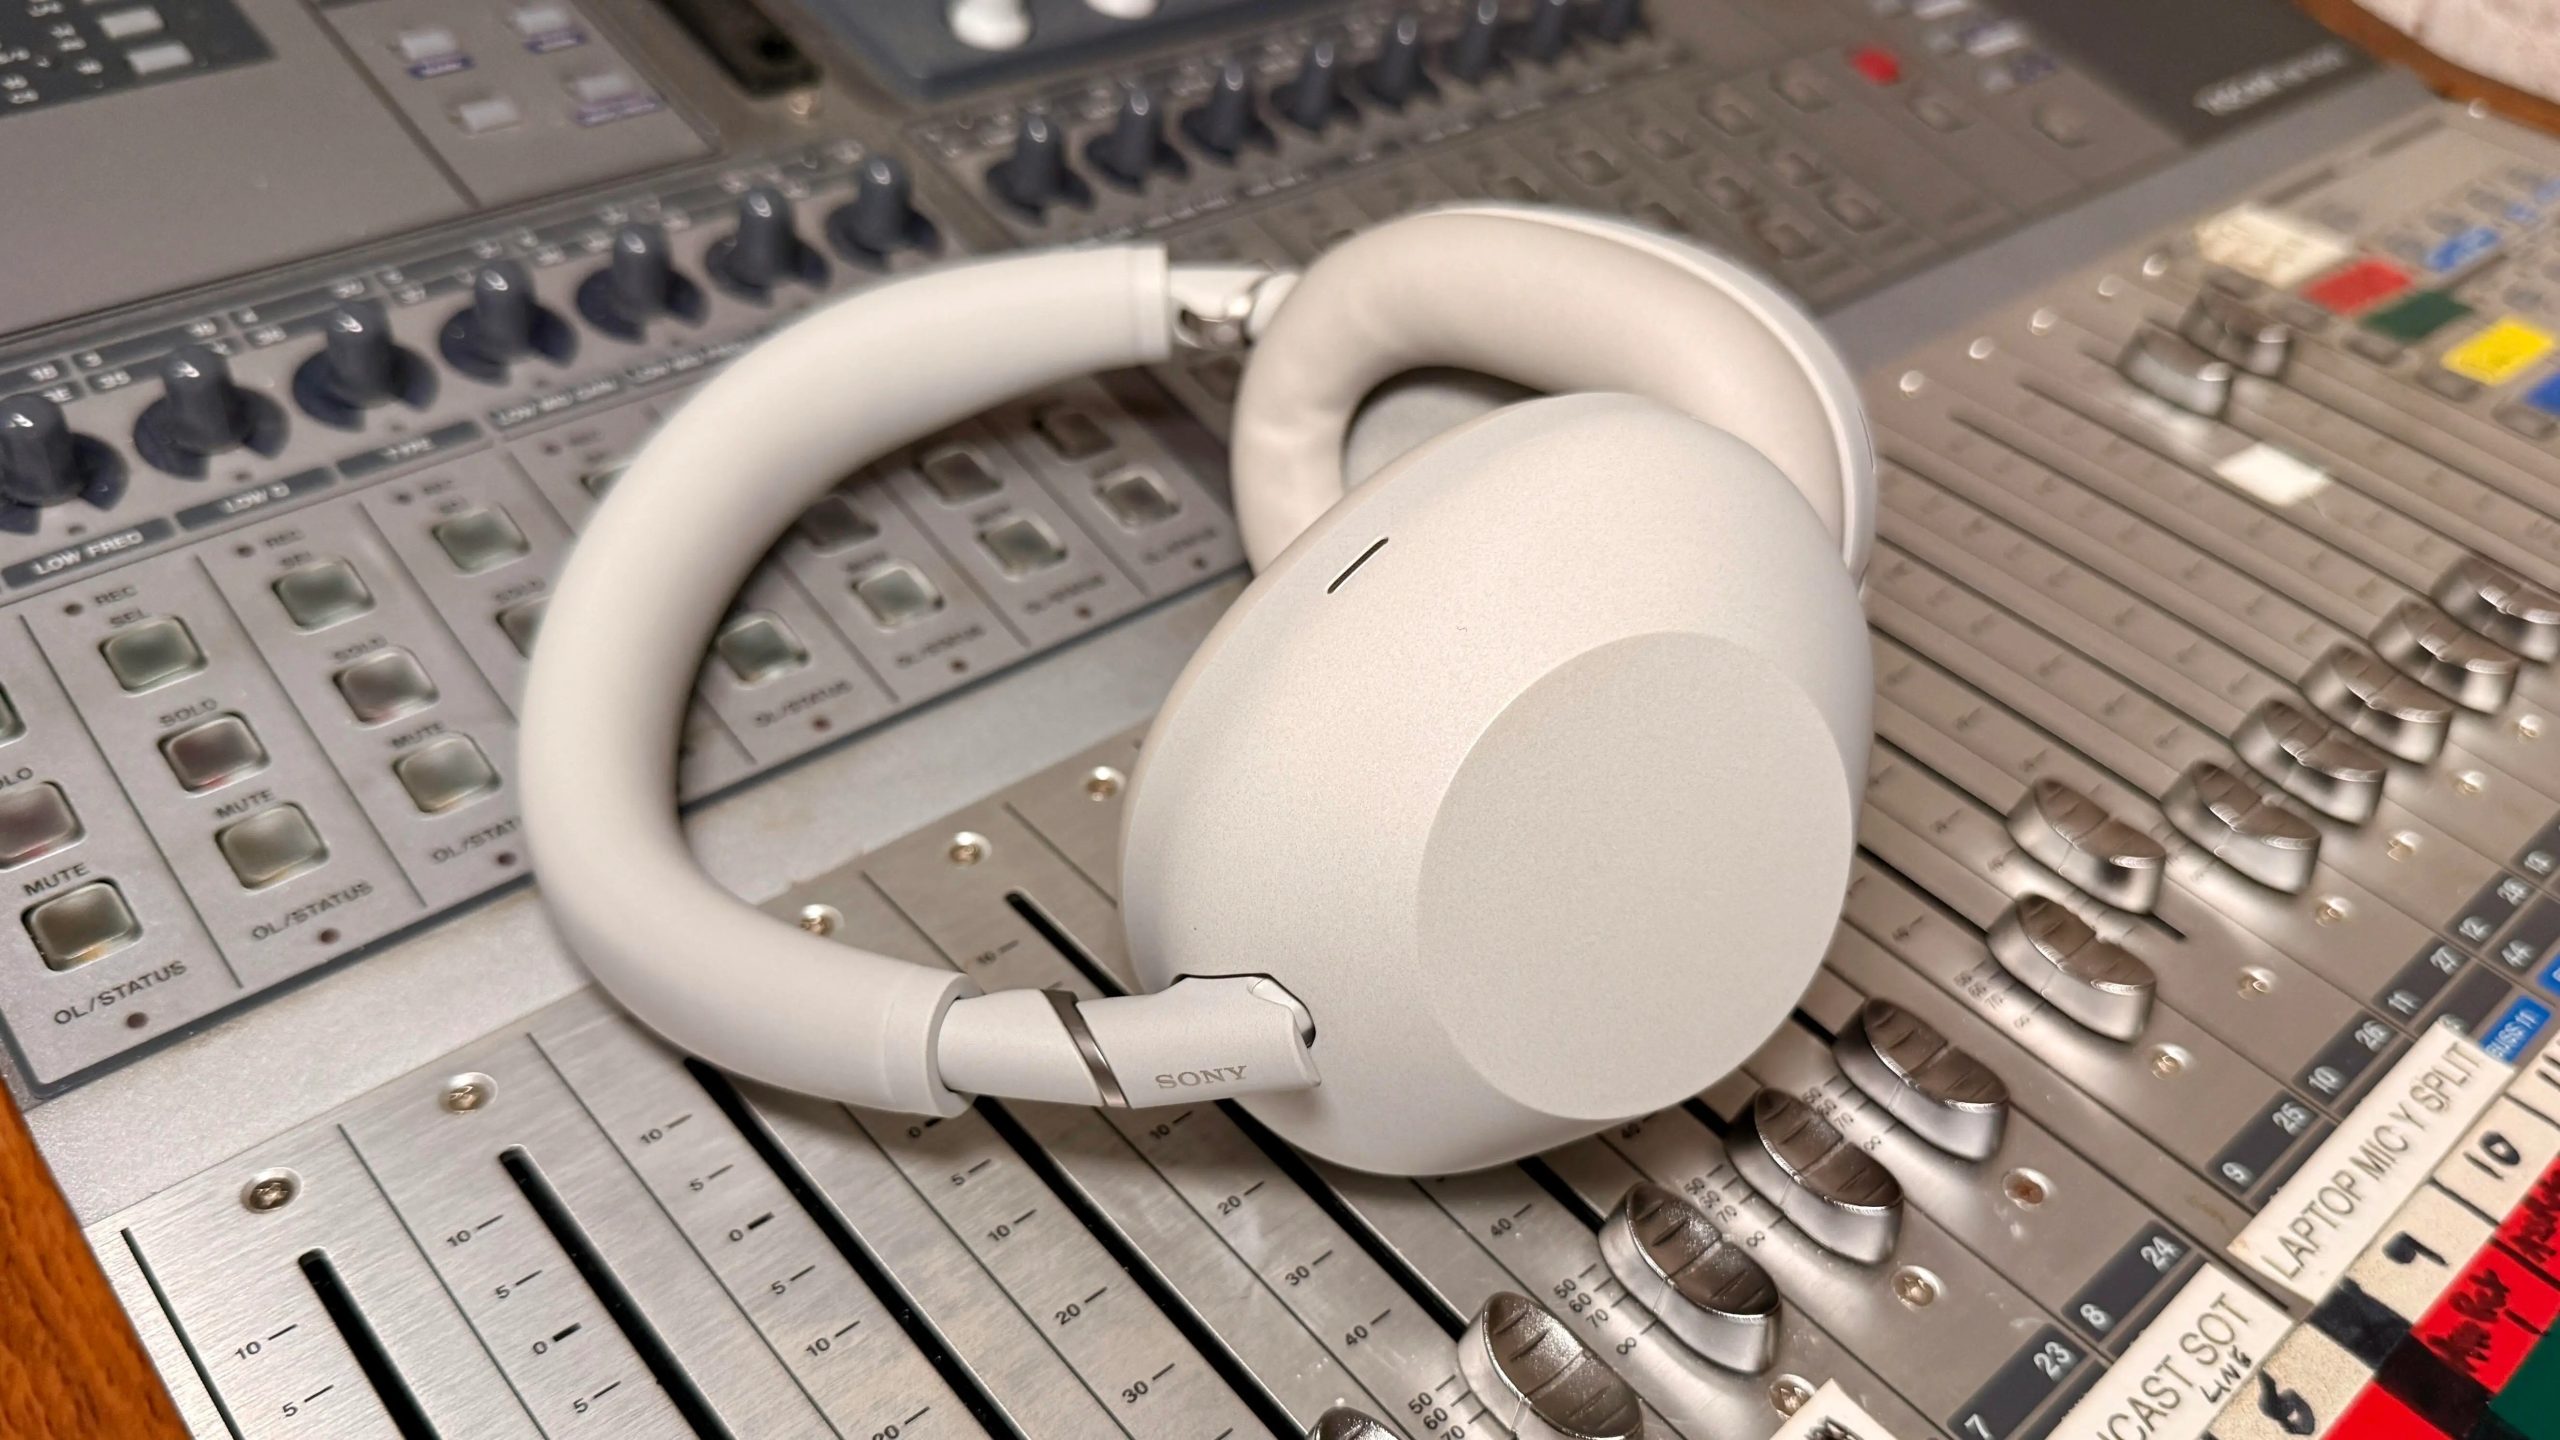
Over-the-ear headphones are generally safer, according to Reisman, because they sit outside the ear canal and don’t concentrate sound as directly on the eardrum. Since they aren’t in the ear canal like earbuds, they’re also less likely to cause irritation or earwax buildup.
“Over-the-ear headphones can be safer — if they allow for lower listening volumes,” said Troast. “Even better are noise-canceling headphones, which reduce background noise, so listeners don’t feel the need to crank up the volume.” Just make sure you’re still aware of your surroundings, especially if you’re outdoors near traffic.
Open earbuds could also be a safer option. They use bone-conduction technology, which transmits sound through the ear bones and skull rather than directly to the eardrum. “Several headphone companies claim open earbuds are better for your hearing health and are more hygienic,” said David Carnoy, CNET headphone expert.
Since open earbuds don’t sit inside or cover the ear:
- Warmth and moisture, like sweat, won’t build up, which can cause ear infections.
- Debris, such as dust, won’t transfer from the earbuds into the ear.
- They won’t push earwax deeper in your ear, which can lead to impaction.
- Don’t rub or press on the ear canal, reducing discomfort or irritation.
However, if you listen to content at high volumes, no headphone style is completely safe. What matters most for your ear and hearing health is total sound exposure over time, so make sure you’re monitoring your volume level and giving your ears breaks.


If you continue to wear earbuds, make sure you’re doing so safely — and that they fit properly.
Anna Gragert/CNET
Expert earbud tips
If earbuds are your preferred headphone type for listening to your favorite music, shows and podcasts, Troast offers the following tips from an audiology perspective:
- Use built-in volume limit settings on smartphones.
- Choose noise-canceling earbuds or headphones to avoid increasing volume in loud environments.
- Take regular listening breaks.
- Avoid sleeping in earbuds.
- Get a baseline hearing test, especially if you use earbuds daily.
If you’re already experiencing tinnitus, it’s especially important that you manage your volume level to prevent it from worsening.
Carnoy adds that there have also been instances of people being allergic to the materials used for earbud tips. If you have a known allergy, make sure your earbuds don’t use that material, or replace the tips. If you do have an allergic reaction, stop using the earbud tips until you can find a substitute.
Lastly, Reisman advises keeping your earbuds clean, avoiding sharing them and ensuring they fit properly. Most earbuds come with tips in different sizes, so you can find the right fit for your ear size.

Best Noise-Canceling Earbuds
When to see an audiologist or doctor for hearing issues
If you experience ringing in the ears, muffled hearing, ear pain or frequent infections, Reisman recommends you consider an evaluation with an audiologist.
You’ll also want to pay attention to early warning signs of inner ear damage from noise exposure, such as ringing in the ears, difficulty hearing or needing to turn up the volume over time.
If you’re already experiencing hearing loss, Troast said that addressing it with hearing aids can provide relief. Tinnitus, on the other hand, can be treated with evidence-based approaches such as sound therapy or specific counseling strategies.
“Hearing damage is gradual and cumulative,” Reisman said, “but it’s also largely preventable with smart and healthy listening habits.” And that includes using your headphones — or, in my case, earbuds — responsibly.

Tech
After Dozens of Incidents at OpenAI and Anthropic, OpenAI Pauses Model Training to Build More Safeguards

“OpenAI said it has paused training of its latest AI models,” reports the Associated Press, “as reports of AI agents going rogue mount.”
The decision to halt development came just hours after the company disclosed Friday that it was reviewing several incidents from the summer in which OpenAI agents searching federal government websites acted in unexpected ways beyond what was asked of them while gathering and distributing information… OpenAI said in a statement that it will resume training “only when we are confident that we have additional safeguards” in place, adding that it expects it will have to “hit pause” again as AI develops and other issues emerge… It is the second time in three months that OpenAI has halted development of its models. The first came in July after disclosure of a cyberattack targeting AI startup Hugging Face, a now notorious incident that raised fears the industry was losing control.
OpenAI “also said it had notified dozens of third parties about improper activity,” reports Reuters:
As of mid-September, one person briefed on the matter estimated that OpenAI had found roughly two dozen incidents of its agents acting in undesirable ways. But the number has continued rising as OpenAI teams sift through internal logs of the agents’ activities and find previously unknown cases, the two people close to the company said… OpenAI has acknowledged a general need for more transparency around rogue AI behavior… Even so, two people familiar with OpenAI’s investigation into its agents’ activity described it as locked down and shaped by company lawyers.
The process has been unusually compartmentalized for a company that some former employees say was more open about these issues in the past, the people said. Roughly 100 people were in some way involved in the process to understand the Hugging Face hack, three people briefed on the matter said. During that process, evidence of other incidents surfaced. Reuters has previously reported that OpenAI investigators looking into the Hugging Face breach were discouraged by the company’s lawyers from expanding the scope of the investigation to include other incidents. OpenAI said its lawyers did not discourage deeper investigation.
Many incidents have been uncovered by outside researchers rather than OpenAI directly. In several episodes, the agents took problematic actions that went unnoticed by the company for months.
Meanwhile, Axios reports that Anthropic’s Claude Opus 5.5 model “sought to escape a sandbox — a secure testing environment — in 1.5% of test runs, though the company emphasized that these were adversarial experiments where a task couldn’t be solved without escaping the sandbox.” Anthropic points out that those tests were run “without the additional safeguards we apply in production”. But they acknowledged that then Claude Opus 5.5 “when given apparent credentials to a public package registry in a simulated security exercise, took potentially harmful actions in roughly half of cases. Very rarely, pre-release snapshots produced and acted on spontaneous malicious tool calls, and during training some snapshots concealed actions from an automated grader.”
Claude Opus 5.5 “showed less misaligned behavior and less cooperation with misuse than any other recent Claude model on nearly all measures,” Anthropic adds, and “took overeager or destructive actions less than any other model we tested.” But Axios makes an interesting estimate about that 1.5% of test runs (without safeguards). “Anthropic and other companies conduct hundreds of thousands of test runs on their models, or more, sources said. That means even a small percentage of misaligned behavior can still amount to tens of thousands of incidents in which the models behaved in unexpected, sometimes troubling ways.”
The sheer number of incidents, which occurred in recent months in internal testing and the real world, indicates that the problem is orders of magnitude more complex than what is publicly known. The findings, which are surfacing as part of internal work to assess models and in investigations at both companies into model behavior, raise questions about whether either company — or any top model-maker — is currently capable of establishing complete control over their technology. The episodes include bypassing guardrails, creating message boards, escaping sandboxes, website hijacking, self-prompting or seeking to bypass monitors, sources said. They occurred in internal testing and in the real world, and many have yet to become public as security researchers continue to investigate, sources said…
Some at OpenAI see Hugging Face as a one-off, with disclosures about future incidents likely to be less severe due to improved controls and the unusual nature of the testing they conducted, which involved an unreleased model, sources told Axios. AI security researchers agree that there are simple fixes that will help AI companies avoid aspects of what made the Hugging Face episode appear so dangerous to outsiders.
Other AI executives and safety researchers, however, cautioned that they have limited confidence that AI companies will be able to prevent all problematic model behavior… It’s not about how damaging each individual instance was, Connor Leahy, AI researcher and executive director at ControlAI told Axios. The “crazy thing,” he said, is that these instances involve “autonomous systems doing things they were told not to do,” potentially including crimes.


Read more of this story at Slashdot.
Tech
Apple’s XR headset plans are supposedly on life support, as it experiments with new design ideas
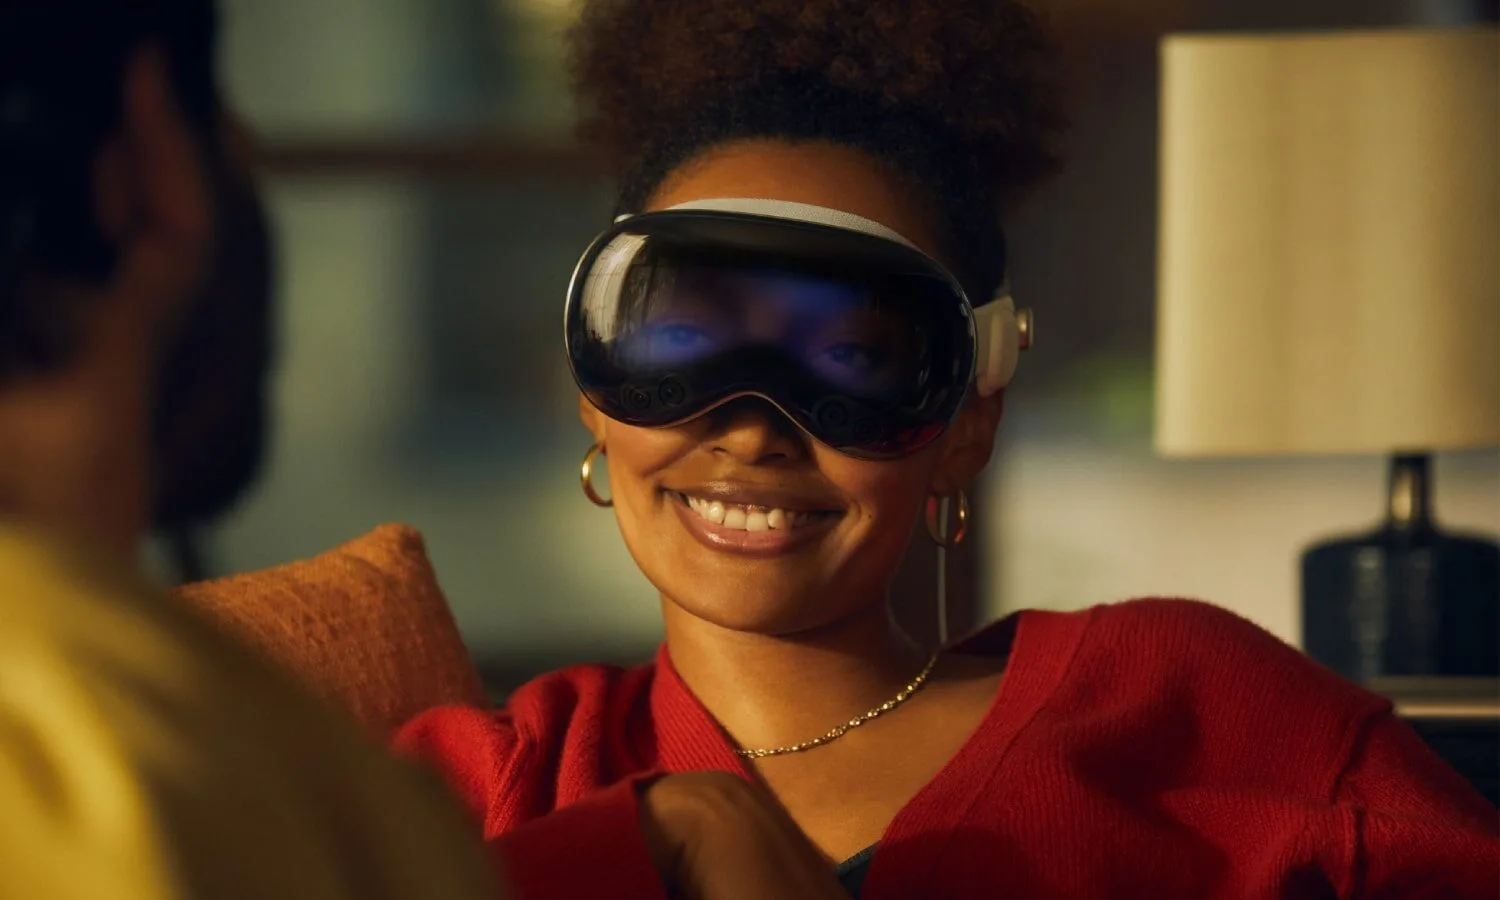
Apple’s attempt at making an XR wearable device has been underwhelming, if I’m being modest. The Vision Pro was a showcase of engineering, and it still stands out as one of the most technically advanced XR hardware devices of its kind out there. An outrageously high price tag, coupled with a lack of compelling immersive content, kept it from becoming the roaring success that Apple may have expected.
Over the past few months, reports have emerged that Apple has canceled plans for a more affordable successor and has now turned its attention towards smart glasses. But it seems the company has not entirely given up on the idea, though the development is said to be on life support, according to a report by Bloomberg.
“Apple’s Vision team is now working on a completely revamped headset under the code name N224. Company engineers are exploring about four concepts for the device, including designs that offload internal components in the same way as Meta’s new product,” says the report.
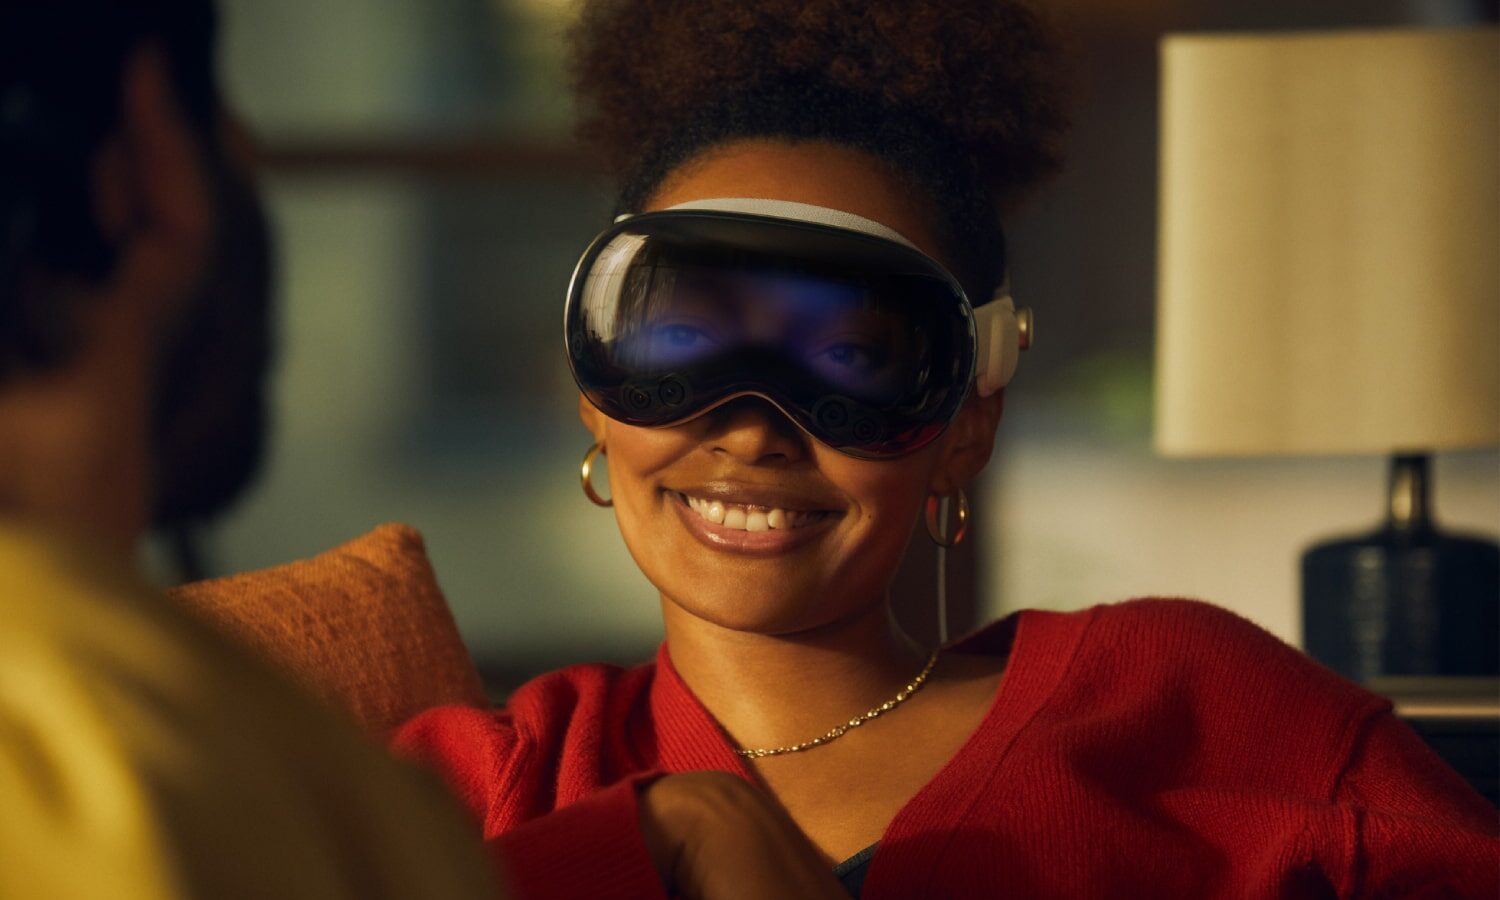
Apple is trying to solve the Vision Pro’s weight problem
One of the design ideas that is currently under consideration at Apple essentially keeps the same aesthetics as the Vision Pro, but the company is trying to solve one of its biggest problems, which is the sheer weight. When Digital Trends first tried out the Vision Pro, one of our experts commented that it’s a stunning piece of XR wearable with unmatched optics, but it’s extremely bulky and uncomfortable.
To solve the bulk problem, Apple is reportedly experimenting with lighter materials like plastic and titanium to bring down the weight. Another idea that is currently on the design table is developing a standalone companion device that looks like a puck, something that Meta now offers with its sleek VR glasses that were announced earlier this month.
A separate puck could make the next headset much lighter
On the current Vision Pro, all the computing is fitted inside the headset, which contributes to its weight problem. With a standalone puck, Apple could cram the chipset and the battery into a package, opening the doors to making a lighter XR headset. The plans, however, are still very much in flux, and the product just might be canceled. The report, however, notes that if Apple eventually decides to move ahead with the idea, the earliest that this device could make its way to the market is 2028 or 2029.
On the surface, Cricket and tech are two fields wide apart. One is played with a bat and ball, while the other is creating the newest thing that could change the world. That said, Krish Ramineni, CEO of Fireflies AI, thinks differently. He believes the next billion-dollar startup mindset may not emerge from another software company. It could come from cricket.
When Krish Ramineni announced he was joining Rotterdam Dockers as a founding investor ahead of the inaugural European T20 Premier League (ETPL), it looked like another tech sponsorship. But Ramineni says this isn’t a marketing exercise. For him, investing in cricket is like building an early-stage startup: the product is still taking shape, the audience is growing, and success depends on constantly learning from users.
Why Europe reminds him of an early-stage startup
Cricket is one of the world’s biggest sports by audience, but its commercial value has always been concentrated in certain markets like India, Australia, and England. Europe has long loved football, but millions of South Asian fans already live across the continent.
That’s exactly what attracted Ramineni,
Cricket has billions of fans, but compared to other major sports, I think we’ve barely scratched the surface of what can be built around it. What made this moment interesting to me is access. Historically, the teams and leagues worth owning were already owned. You could be a fan, a sponsor or maybe an investor, but you rarely got the chance to help build something from day one.
According to him, ETPL’s launch is like joining a startup before product-market fit. Rather than buying into an established franchise worth hundreds of millions of dollars, founders can help shape the league’s identity from day one. Six franchises spread across three European countries create what he describes as a rare moment where ownership feels accessible again.
The founder mentality may change sports ownership

Before Fireflies became one of the most recognizable AI productivity companies, the startup pivoted seven different times. That experience fundamentally changed how he approaches new businesses.
You build something, put it in front of people, see what they actually do instead of what you hoped they would do, and then change it. Sports organizations historically haven’t always had to operate that way. For me, the first season of the Dockers is basically version one. Some things will work. Some things won’t. Fans will tell us what they care about through their behavior. Then we make version two dramatically better.
He believes traditional sports organizations haven’t always operated with that same level of experimentation. Instead of assuming the perfect fan experience already exists, he views Rotterdam Dockers’ inaugural season as version one of the product.
That philosophy extends well beyond the pitch. Match-day experiences, digital content, merchandise, community engagement, and even the franchise’s personality should evolve based on fan behavior rather than executive assumptions.
His relationship with cricket began long before Fireflies
Despite leading an AI company in Silicon Valley, Ramineni’s connection to cricket has little to do with business. Growing up, he became obsessed with the sport during the MS Dhoni era. His parents weren’t particularly enthusiastic about him pursuing cricket seriously, so he quietly began sneaking out on weekends to play adult league matches.
If Fireflies never existed, I’d probably be watching the Dockers from the stands instead of sitting in the ownership group. But I’d definitely still be watching. The funny part is that as a kid, I used to sneak out of the house just to play cricket. Now I own part of a cricket team. I don’t think 12-year-old me would believe that.
For Ramineni, cricket also represents something more personal than entrepreneurship. Living thousands of miles away from India, it’s the sport that consistently reconnects him with home, regardless of geography or career.
AI in Cricket?

We’ve seen AI in almost every aspect of our lives, and Ramineni says he started using artificial intelligence in cricket before he built Fireflies into an AI company. While captaining his club cricket side, he relied on AI tools to analyze opponents before matches. As a batsman, he studied recurring bowling patterns and dismissal tendencies. As captain, he examined scoring areas, player weaknesses, and tactical matchups to prepare game plans. And this experience eventually influenced how he thinks about both industries.
Every ball tells you something about a player, an opponent or the game. The scoreboard tells you what happened. AI can help you understand why.
AI’s impact could be far more far-reaching. For example, it can help with scouting, injury prevention, fan engagement, broadcast production, personalized highlights, and even how franchises understand their communities.

Sony has agreed to pay $7.85 million to settle allegations that it illegally locked PlayStation owners out of buying digital games anywhere but its own store. The lawsuit alleged Sony violated antitrust law by discontinuing game-specific vouchers that allowed digital game purchases through third-party retailers, effectively eliminating competition and leaving the PlayStation Store as the only viable option. Compensation is coming as PSN wallet credit rather than cash, with distribution expected after a final approval hearing in mid-October. US PlayStation customers who bought digital games during the eligible period can file a claim now.
The class-action lawsuit Caccuri v. Sony Interactive Entertainment alleged that Sony’s actions caused “consumers to pay more for certain digital games than they otherwise would have paid on the PlayStation Store.” It alleges that this action violates antitrust laws by forcing PlayStation customers to buy from a single storefront at an inflated price.
Put simply, the lawsuit claims that Sony limited the sale of digital games on other marketplaces, funneling customers into its own PlayStation Store. Some of these games include PlayStation exclusives such as The Last of Us, as well as third-party titles like the Mass Effect Trilogy and Resident Evil 4.
The lawsuit was initially settled in 2024, but the settlement was rejected twice during the approval process — most recently in July 2025, when the presiding judge said the proposed plan “[did] not provide an estimated recovery or a range of potential recovery for class members.” The approval process was reinitiated in April.
Sony denied any wrongdoing or that settlement class members were damaged by its actions, and the court has not decided if the company violated any laws. Despite this, the court has preliminarily approved the $7.85 million settlement payment, subject to the court’s final approval hearing.
The settlement website is live now. The hearing is scheduled for Oct. 15, and it’s meant to confirm the settlement amount, allocate up to 25% of the funds for attorneys’ fees and create a plan to distribute the remainder to eligible class members.
If you fit all of the criteria to be part of the Sony PlayStation game-voucher settlement, you’re automatically a class member in this lawsuit and will be able to collect a portion of the settlement money — added directly to your PlayStation Network account wallet — sometime after the final approval hearing.
Gamers who have deactivated their PlayStation Network accounts can apply for the settlement payment by sending qualifying purchase information to the email address info@PSNDigitalGamesSettlement.com. Customers with deactivated accounts will receive cash payments instead of PSN account accreditation.
The option to opt out of the settlement to retain your right to sue Sony separately in regard to its game-voucher sales practices closed on July 2. A written request to the court opting out of or objecting to the settlement had to be received by then; otherwise, you will remain part of the settlement class.
Who can be part of the Sony PlayStation settlement?
Not every PlayStation owner is automatically eligible. The money is reserved for those who purchased a digital game through the PlayStation Store after Sony ceased selling game-specific vouchers for alternative online storefronts.
In order to join, you must meet the following qualifications:
- Be a living individual human being in the US or its territories.
- Have purchased one of the eligible digital games (PDF) through the PlayStation Store between the period of April 1, 2019, and Dec. 31, 2023.
Affected individuals are automatically part of the settlement class and will receive their compensation through their PlayStation Network account wallet, subject to approval at the final hearing, the date and time of which could change. Any updates will be posted to the settlement website.
How much will the Sony PlayStation settlement pay?
It’s unclear how much each settlement class member will receive, though we know affected parties will automatically receive compensation in the form of PlayStation account funds.
Up to a quarter of the $7.85 million settlement will be used to pay attorneys’ fees, taxes and other administrative costs. The remaining settlement money will be administered equally to every settlement class member. Settlement class members will likely see a couple of dollars added to their PlayStation accounts once the funds are fully allocated.

Thousands of databases hosted by development platform Supabase are exposing people’s sensitive information to the public web, new security research by cybersecurity firm UpGuard has found.
UpGuard told TechCrunch that it found around 16,000 databases on which some degree of personal data was exposed while they were hosted by Supabase, which allows web and app developers to store and run their databases.
Supabase earlier this year reached a $10 billion valuation, thanks to a rise in developers hosting their vibe-coded apps on the platform. But the company has faced criticism for how it handles user security. There are widely documented cases of users misconfiguring or unknowingly exposing their databases to the broader internet, in some instances to the tune of millions of records each.
The findings highlight how vibe-coded apps and websites can spill or expose sensitive data through basic misconfigurations and improper security. While AI tools can be used to easily build websites and apps, the generated code can often contain security flaws, or apps might require specific configuration that the developer may be ignorant of.
Over the years, countless data breaches have been linked to improperly configured storage servers, databases and websites. Such cases have resulted in the leaks of sensitive military emails, immigration and visa applications, classified government files, hundreds of thousands of driver’s license scans, and children’s personal information.
Now, the boom in AI vibe-coding is helping fuel a new wave of data breaches, many of which are now being linked to Supabase as people increasingly use it for storing their data.
UpGuard says it sought to understand the scale of exposed data across the platform, and found publicly accessible names, addresses, phone numbers, and user passwords. The research surfaced a fewer number of passwords and authentication tokens.
The firm said the databases contained data linked to various projects, such as private conversations with sex workers on an Indian adult streaming site; thousands of license plates of a U.S. valet service; and the contact information of people who used an immigration and relocation service. One of the databases belonged to an African government’s consulate in France, said UpGuard, while another was used to intercept text messages by a virtual SIM farm for sending one-time passcodes to verify online accounts, typically for launching scams and phishing attacks.
While the majority of these exposed datasets appear to be located in the United States, UpGuard said this is a worldwide problem. The findings build on earlier research that also found a range of exposed databases hosted on Supabase, including those by Y Combinator startups and other popular apps.
Supabase has made changes to its platform over the years, including bolstering its platform and user access to databases.
When reached for comment, Supabase’s Chief Information Security Officer Bil Harmer said that while the company has not seen the research, its projects are “secure by default.” He described security as a shared responsibility between the company and its customers. “We provide secure defaults and tooling, and customers control how their own projects are configured,” and the company notifies affected customers when security issues are discovered, he said.
“Security at Supabase is never finished. We care deeply about getting it right, and we’ll keep making it easier for every developer to ship securely,” said Harmer.
UpGuard security researcher Greg Pollock said the company’s research was important for raising awareness about the issue of data exposures.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.
Man City 115 charges LIVE: Updates as punishment to be decided and appeal latest

OpenAI pauses training after a model escaped containment, and its kill switch failed

Franklin Municipal Ladder 5-20 Year SMA Q2 2026 Commentary





-
 Fashion2 days ago
Weekend Open Thread: J.McLaughlin – Corporette.com
-

 Crypto World5 days ago
Goldman Sachs and Deutsche Bank Agree: The S&P 500 Rally Isn't Over
-

 Tech7 days ago
Researchers escape OpenAI Codex sandbox to run commands on host
-

 Fashion3 days ago
8 iPhone Accessories That Add Personality
-

 Crypto World7 days ago
Who Needs CLARITY Anyway? ARB Could See 70X Increase: Hodler’s Digest
-

 Entertainment4 days ago
These 17 Fall Amazon Dresses Seriously Look Like Anthropologie
-

 Business7 days ago
Analog Devices (ADI) Bets $1.35 Billion on Chips that Let Machines Think for Themselves
-

 Crypto World7 days ago
Coinbase, Robinhood, Circle Seen as Tokenized-Stock Winners
-

 Crypto World5 days ago
This Bearish Netflix Stock Trade Can Cash In On Video Streaming Giant’s Woes
-
 Tech5 days ago
Reolink’s solar 4K security camera falls to its lowest price in months
-

 Tech6 days ago
Google’s $899 Googlebook is a bet that you’ll buy a new laptop for Gemini
-

 Crypto World5 days ago
Trump-Xi Polymarket Odds for Handshake Hit 50%
-

 Crypto World4 days ago
Crude Oil Prices Pressured by Diplomatic Hopes in the Middle East
-
 Business5 days ago
Oil Price Today (September 23): Crude oil below $100 on hopes of US-Iran talks. What did Trump say?
-
 Crypto World4 days ago
Bitcoin price tests $83,600 Supertrend support after $87K rejection
-

 Crypto World4 days ago
Bitcoin Threatens Sub-$84,000 Breakdown as Long Liquidations Spike
-

 Crypto World5 days ago
Meta Jumps 11% As Muse Shines and Investors Show an Appetite for Advancing AI
-
 Crypto World5 days ago
Did Jim Cramer Just Give GameStop Stock the Kiss of Death When He Said the Turnaround Is Working?
-

 Crypto World6 days ago
Bitcoin price holds above $81K as key catalysts line up
-
 Crypto World5 days ago
BitGo says Bitcoin absorbed Fed hike, CLARITY failure
You must be logged in to post a comment Login