Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Tech & AI
PS5 Owners Get Big Graphics Upgrade For Free

After more than a decade of development, several delays, and a pretty significant leak, Rockstar Games is poised to release the long-awaited “Grand Theft Auto VI.” The game is available for pre-order, and it’s racked up considerable sales already, pulling in around $500 million as of mid-August 2026. While many players are incredibly excited to finally get their hands on the game, some might be concerned with how well it will look on their base model PlayStation 5.
After all, when Sony released the PS5 Pro, it pushed the console’s graphics capabilities far beyond the base model. However, the Pro console is expensive, and not everyone can afford one — especially if they already have a PS5. In an interesting move that appears to align with enhancing “GTA VI,” Sony is rolling out a major graphics upgrade to the PS5 base model, and it’s already gone into effect on all consoles.
The upgrade in question is called the Quick Spectral Super Resolution (QSSR) update, which is a type of AI upscaling that takes the baseline graphics and supercharges them in various notable ways. QSSR adds greater pixel-level clarity alongside better stability to a game’s environment, adding greater detail that pushes the PS5 closer to what the PS5 Pro can accomplish natively. While the update came along in time for other games, it seems likely that the real reason Sony is pushing out the free update is to better enhance “GTA VI’s” gameplay when it arrives on November 19, 2026.
The PS5 QSSR upgrade
The Playstation 5 Pro already uses a process called PSSR upscaling and other means, including advanced ray tracing, to upgrade the graphics capabilities of its games. QSSR is essentially the same thing as PSSR, though it’s not as powerful due to hardware limitations. That said, it should offer a significant boost in performance via AI upscaling to improve the overall look of PS5 games.
The PSSR relies on the PS5 Pro’s dedicated machine-learning hardware, which the base model lacks. The QSSR update is meant to sidestep this bottleneck but improving the efficiency of the existing hardware, effectively reducing the need for extra processing power. The update includes a means of taking on known PS5 issues with complex textures, subpixel shimmering, and less stable imagery. It also upgrades some ray-traced reflections.
Digital Foundry tested the new QSSR update and highlighted it as an excellent boost, though it did identify some issues. There’s a small performance cost in some games, though it’s small enough that some gamers might not even notice.
Developers who already know how to code for PSSR can apparently more easily adopt QSSR, as it’s designed to be more streamlined. The QSSR update arrived on October 1, 2026, alongside the releases of “Marvel’s Wolverine” and “Ghost of Yōtei,” so it’s only a matter of time before players see the improvements in “GTA VI.”
Continue Reading
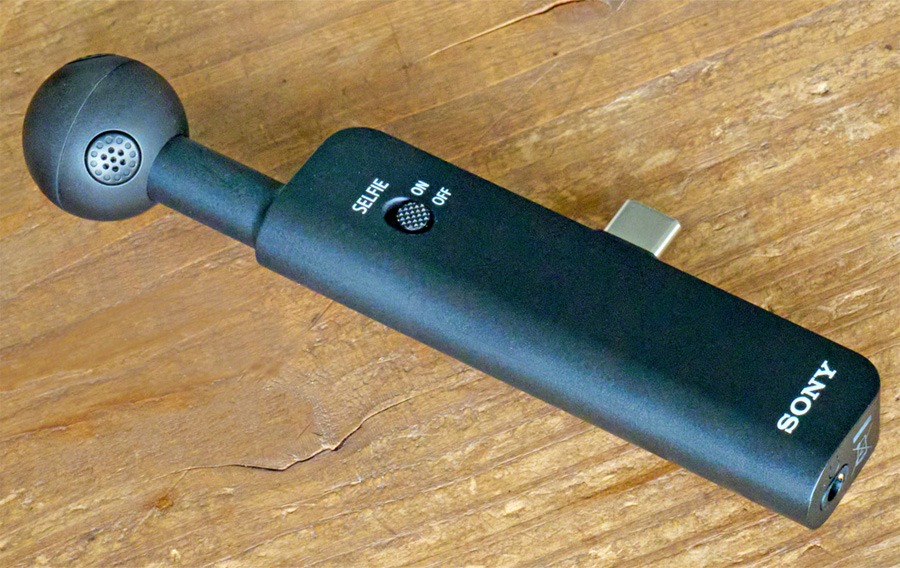
Sony might be best known to consumers for BRAVIA TVs, headphones and home theater gear, but pro audio has been part of the company’s DNA for decades. In 2026 alone, Sony expanded that side of the business with products including the affordable IER-M500 professional IEMs, and it is now turning its attention toward something potentially more consequential: making spatial audio easier to capture at the source.
The new Sony ECM-AX10 Spatial Audio Microphone is aimed at professional and hobbyist content creators, but its ability to capture first-order Ambisonics for use in Eclipsa Audio production workflows makes this more than another microphone announcement. Eclipsa Audio is built on the open, royalty-free IAMF spatial-audio format developed through the Alliance for Open Media and backed heavily by Google and Samsung. YouTube already accepts Eclipsa Audio content, while compatible TVs and soundbars can reproduce it at home.
So where is Sony going with this? The ECM-AX10 suggests the company wants a larger role in the entire immersive-audio workflow, from recording and production to distribution and playback. Sony already describes its professional strategy in terms of supporting creators from acquisition through delivery, and its growing emphasis on spatial-audio production makes the AX10 look less like a one-off microphone and more like another piece of that puzzle.
Related Reading: Watch Out, Dolby Atmos: Google’s Eclipsa Audio Is Coming For You
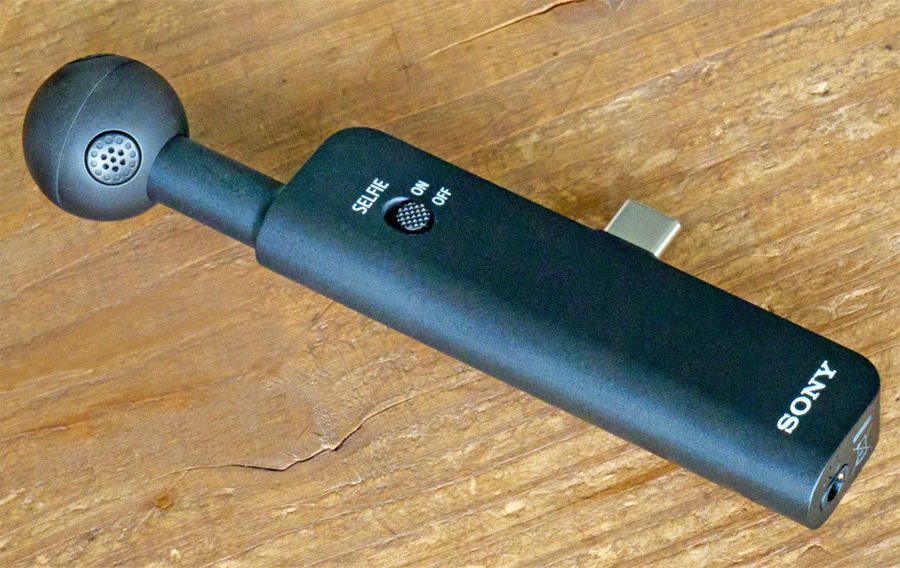
Why the Sony ECM-AX10 Matters for Smartphone Content Creators
Smartphones have come a long way, and an increasing number of creators now use them to record both video and audio.
However, while many smartphones can capture surprisingly high-quality video, their built-in audio recording often falls short. That is hardly surprising, considering those microphones also have to handle phone calls, meetings and everyday voice communication.
To expand the live audio recording capabilities of smartphones and other compatible devices, Sony has introduced the ECM-AX10, a very compact microphone that plugs directly into the USB Type-C port of a smartphone.
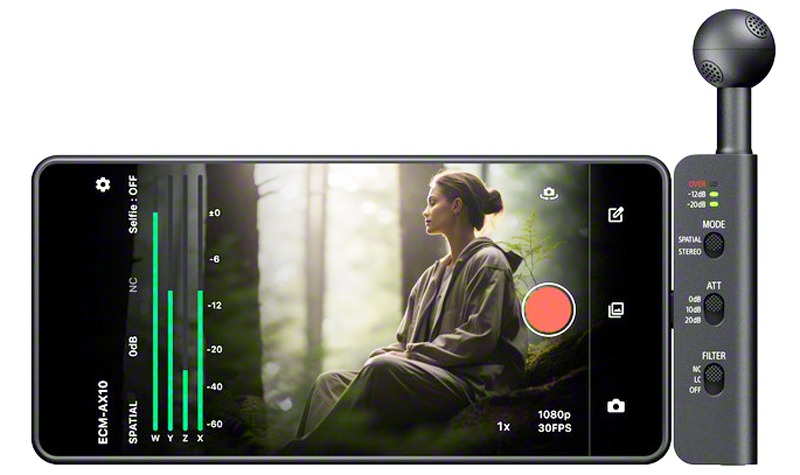
Once plugged in, the ECM-AX10 elevates a smartphone’s live recording capabilities with professional-quality spatial audio. Users can capture audio and video simultaneously without the need for separate synchronization.
ECM-AX10 use examples include:
- Travel, city walks and food experiences
- Music performances and live events
- Sports, motorsports and enthusiast content
- Family events, personal archiving and 360° video
- Capturing natural sounds, sound effects and ambience for post-production
With its built-in technology and flexible recording options, the ECM-AX10, when paired with a smartphone, can support a range of spatial and immersive audio workflows, including Eclipsa Audio, Ambisonic, binaural and stereo audio.
As a result of its built-in technology and flexible use possibilities, the ECM-AX10 in combination with a smartphone becomes a tool for supporting Eclipsa and Ambisonic, Binaural and stereo Audio workflows
Ambisonics: This is a four-channel, scene-based capture method used for immersive audio production. Ambisonics B-format is a full-sphere, speaker-independent spatial audio format that captures sound from all directions, including horizontal azimuth and vertical elevation.
Pro Tip: Sony’s spatial-audio processing converts audio captured with the ECM-AX10 into first-order Ambisonics, preserving direction, ambience and low-frequency detail.
Binaural: This supports two-channel spatial listening over headphones and is compatible with many existing apps.
Stereo: The ECM-AX10 also supports high-quality, atmospheric two-channel recording for broad compatibility with speakers, devices and apps.
Eclipsa Audio: The ECM-AX10 captures first-order Ambisonics spatial audio, which can then be used to create Eclipsa Audio content based on the IAMF (Immersive Audio Model and Format) standard. Sony is also a licensed Eclipsa Audio adopter.
For the ECM-AX10’s mobile workflow, Eclipsa Audio output for YouTube requires Sony’s free editing app. The app processes the Ambisonics recording and prepares it for Eclipsa Audio distribution. Without that additional Eclipsa processing step, content can be exported for conventional stereo or binaural playback.
Similar to Dolby Atmos, Auro-3D, DTS and Sony 360 Reality Audio, Eclipsa Audio extends beyond traditional surround sound by incorporating height information. Sounds can be positioned around and above the listener to create a more immersive three-dimensional presentation.
Eclipsa Audio is based on the open IAMF standard and is designed to adapt immersive content to different playback environments and compatible devices, including TVs and soundbars. For ECM-AX10 users, the important distinction is that the microphone provides the spatial Ambisonics capture; Eclipsa Audio is created during post-production rather than recorded directly by the microphone.
Publishing Destinations: Stereo and binaural versions can be prepared for broad distribution through platforms such as Instagram, X, Facebook and other compatible services. For immersive Eclipsa Audio playback, the ECM-AX10 workflow can create an IAMF/Eclipsa Audio version for YouTube using Sony’s free editing app. Actual Eclipsa Audio playback also requires a compatible device.
ECM-AX10 Features
- Microphone Type: Spatial audio microphone for smartphones.
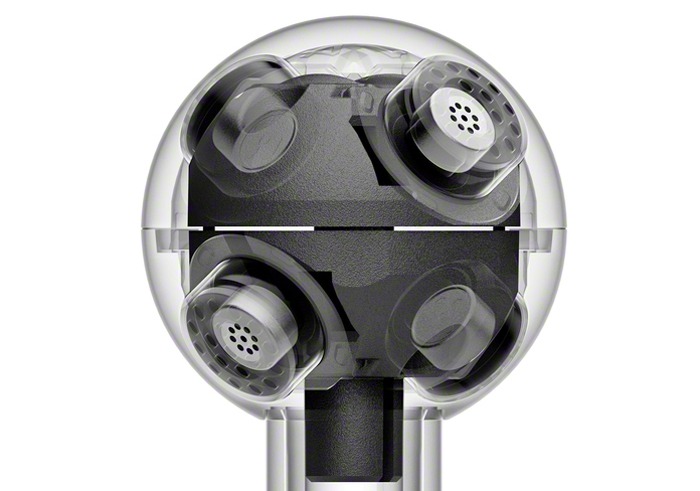
- Microphone Array: Four omnidirectional microphone capsules are arranged around a newly developed spherical module.
- Mode Selection Switch: Switches between Spatial Audio and Stereo modes.
- Peak Level Meter: Provides an indication of the strength of the incoming audio signal. If the input level is too high, attenuation may be necessary to prevent clipping.
- ATT (Attenuation): If an input signal is too strong, it can overload the system, resulting in clipping and harsh digital distortion. ATT reduces the input level to keep the recorded audio clean and within safe operating limits.
- Noise Control: Noise Cut and Low Cut settings help reduce unwanted noise.
- Selfie Mode: A Front alignment selector makes it easier to maintain proper sound orientation when recording selfies or front-facing video with a smartphone.
- Accelerometer: A built-in accelerometer automatically detects the microphone’s tilt angle, helping keep recorded spatial audio aligned with the video based on the smartphone’s orientation.
- Audio Recording Format Support: First-order Ambisonics, binaural and stereo.
- Audio Post-Production Format Support: Ambisonics (48 kHz, 32-bit float, four-channel AmbiX, Eclipsa Audio) and binaural/stereo (48 kHz, 16-, 24- or 32-bit). Audio editing can also be performed directly on the same smartphone used for recording.
- Input: USB Type-C direct connection for smartphones and other compatible recording devices.
- Output: 3.5 mm headphone monitoring output, compatible with the Sony IER-M500 IEMs and other wired IEMs and headphones.
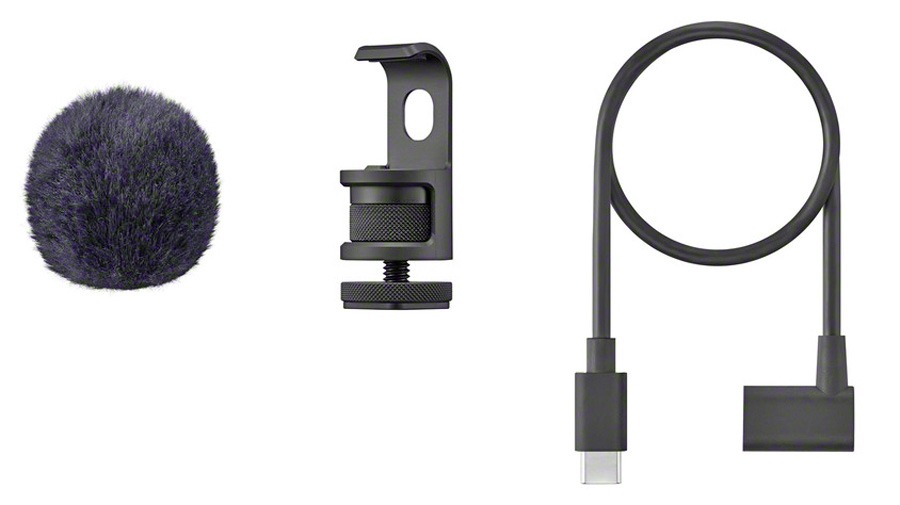
- Included in the Package
- Windscreen
- USB Type-C extension cable
- Cold-shoe microphone holder
- Spacer sheet
The Bottom Line
At $249, the Sony ECM-AX10 packs an unusual amount of recording capability into a microphone small enough to plug directly into a smartphone. Its real advantage is not simply better audio quality, but the ability to capture both conventional stereo and spatial audio without requiring a separate recorder, microphone array or complicated synchronization workflow.
That makes the ECM-AX10 particularly interesting for creators who want to move beyond basic smartphone audio. Its four-capsule design supports first-order Ambisonics capture, binaural and stereo production, while Eclipsa Audio support provides another path for creating and distributing immersive content. Editing can also remain within a mobile workflow, depending on the software being used.
What makes the ECM-AX10 genuinely different is how much of the immersive audio production chain Sony has condensed into one compact device. A creator can capture spatial audio alongside video on a smartphone, monitor the recording through wired headphones or IEMs, and then move that material into an Ambisonics or Eclipsa Audio post-production workflow without hauling around a conventional field-recording rig.
For monitoring, Sony’s $119 IER-M500 professional IEMs could also make a logical companion to the ECM-AX10, providing a relatively affordable Sony-based recording and monitoring setup for creators who want to keep the entire kit portable.
Price & Availability
The Sony ECM-AX10 Spatial Audio Microphone is priced at $249.99 USD (CAN $349.99) and is available through Sony.
Related Reading:
The closures come as receivers Kroll prepare Crystal Jade for sale
Crystal Jade has closed another four outlets in Singapore, leaving nine restaurants in operation. No further closures are expected, Channel News Asia reported.
Three of the four outlets were Crystal Jade La Mian Xiao Long Bao locations, at Bugis Junction, Toa Payoh and i12 Katong. The fourth was a Crystal Jade GO at Punggol Oasis Terrace. All ceased operations on Tuesday, Oct 6.
About 120 workers across the affected outlets and some corporate functions were issued termination notices.
The closures are part of a reorganisation of Crystal Jade’s Singapore business ahead of a proposed sale, financial and risk advisory firm Kroll said in a media release on Wednesday, Oct 7.
Kroll representatives were appointed receivers of the holding companies for Crystal Jade’s Singapore and Hong Kong operations on Sep 29. In a receivership, an appointed receiver takes control of certain assets of a company, typically to protect or recover their value.
Kroll said the restaurant premises would be handed back to landlords.
“All affected employees have been informed directly and will receive salary payments up to their final date of employment. Restaurant staff will continue to serve their applicable notice periods and will be compensated in accordance with their employment contracts,” the firm added.
Employees who need help with final pay or benefits may continue to contact the HR team.
About 210 employees will remain at Crystal Jade’s Singapore holding company after the reorganisation, Kroll said.

Kroll said it intends to market the business for sale as a going concern, aiming to preserve the brands, operations and value Crystal Jade has built over more than 30 years.
The proposed sale is intended to support the business’s continuity and future growth and is not expected to result in further operational restructuring. The nine remaining restaurants in Singapore will continue operating as usual.
Separately, Crystal Jade Food Manufacturing, the group’s central kitchen, ceased operations on Monday, Oct 5. It falls outside the receivership, and Kroll said management decided to close it as part of the group’s wider restructuring.
To support affected employees, Kroll said that it and Crystal Jade have been engaging the Food, Drinks and Allied Workers Union (FDAWU) and other associations since Sept 30.
FDAWU, an affiliate of the National Trades Union Congress (NTUC), said in a media statement on Oct 7 that Crystal Jade is not unionised, but that it had been approached by the appointed receivers to support affected union members and workers.
2026 has been a rough year for Crystal Jade. Prior to this, it had already shuttered five Singapore outlets at Hillion Mall, Suntec City, The Clementi Mall, Jurong Point and Great World.
It is also facing a court charge for failing to submit its complete income tax return for FY2025 on time, where it could be fined up to S$5,000.
Founded in Singapore in 1991, Crystal Jade was one of the country’s fastest-growing Chinese restaurant groups, reaching 120 restaurants worldwide in 2015.
However, that footprint is closer to 100 restaurants across 25 cities now.
- Read other articles we’ve written on Singaporean businesses here.
Featured Image Credit: Ricky Tho via Google Reviews
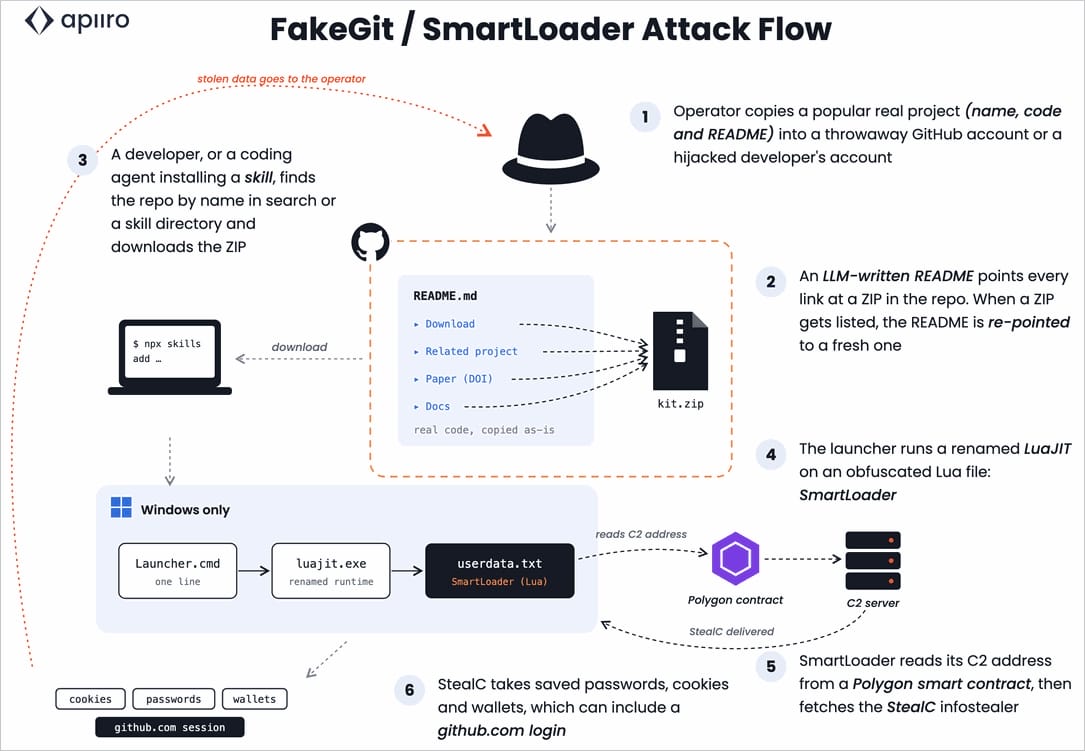
More than 17,000 fake repositories on GitHub are distributing the SmartLoader malware after the FakeGit campaign reactivated earlier this month to push the StealC infostealer.
The operator uses mostly throwaway accounts, but researchers identified at least 700 accounts that appear to belong to legitimate developers.
The malicious repositories use convincing README instructions with a download button pointing to a ZIP archive containing the initial payload, SmartLoader, that is used to distribute other malware.
While similar activity with various payloads has been observed since at least January, the FakeGit term was associated with this operation in July, when researchers at enterprise browser platform Island published a report on 7,600 fake GitHub repositories pushing the SmartLoader malware.
Island noted at the time that 800 of the malicious repositories masqueraded as AI skills or MCP servers that appeared in public AI registries and catalogs.
A new report from researchers at software supply-chain security platform Apiiro says that FakeGit resumed its activity on October 4 and now uses 17,610 repositories on GitHub.
In just 34 hours, FakeGit pushed more than 13,000 repos, peaking at 2,999 an hour.
“In the commits we sampled, 97% touched only the README, and 88% pointed its “Download” button at a ZIP that installs SmartLoader,” Apiiro says.
“Nobody had to create a single new repo. The fleet was already there. It just got re-aimed,” the researchers added.
Source: Apiiro
How FakeGit survived
According to the researchers, the reason behind FakeGit’s survival is that removing repositories is based on lists that cover only a fraction of the malicious repos.
Also, blocklisted payloads and backup copies remain accessible, so attackers can simply change the download links while keeping the same repositories active.
“71% of the fleet was missing from URLhaus before our report, and a domain-level DNS blocklist can’t block one file on GitHub without blocking GitHub,” Apiiro explains.
The researchers found malicious archives in forks, older files, release assets, issue attachments, and separate download-hosting repositories, which makes deleting one link at a time ineffective.
“Delete one file and the operator can point the lure at a spare copy: a fork, an older ZIP, a release asset or an issue attachment,” the researchers said.
Apiiro researchers recommend that users verify the repository’s owner. Furthermore, the source for installing AI skills and MCP servers should be official registries or vendor repositories.
If SmartLoader execution is suspected, users should treat the incident as a potential GitHub account compromise, revoke active sessions and access tokens, and move to passkeys.

Tech & AI
Wikipedia says rogue AI agents from OpenAI edited its private wikis and hammered its servers
Wikimedia Foundation, the organization that hosts Wikipedia and other major wiki-based collaboration projects, is once again clashing with AI companies over their alleged abuse of its servers. In particular, the foundation said that OpenAI was “caught” performing unauthorized operations through its supposedly autonomous, and most certainly “rogue,” AI agents.
Read Entire Article
Source link
Schools across the nation are trying to reduce chronic absentee levels. A recent study from The GRAD Partnership, Everyone Graduates Center and the Partnership for Student Success, finds that small and rural districts are recovering attendance rates faster than larger, more urban and suburban districts.
The study reported that rural districts with fewer than 1,000 students brought their chronic absenteeism back to within 2% of their pre-pandemic baseline by the 2024-25 school year at about twice the rate as urban districts with more than 50,000 students.
While some small and rural districts have bounced back, many districts across the country still have a long way to go to get back to pre-pandemic attendance rates. EdSurge talked with a deputy superintendent, a director of attendance and student supports, and an instructional coach at different districts nationwide to understand how they tackle the issue.
The researchers couldn’t find a clear reason as to why small and rural districts have bounced back quicker. California and Iowa accounted for over 30% of the small and rural districts that bounced back, despite taking two different approaches.
California opted for a larger scale approach, changing its absenteeism and truancy laws and investing more funding in schools’ pandemic recovery statewide. On the other hand, Iowa took the more granular path, offering technical assistance and templates to districts and using data to identify needs and increase attendance.
Finding the connection among the standout bounce-back states and districts is the next central research question, according to the study, which looked at 8,586 school districts across 34 states and the District of Columbia.
A Proactive Approach
At Earlville Community Unit School District 9 in Illinois, School Social Worker Michele Fahrlander uses a proactive program to ensure attendance.
“Because we are a smaller district, we are able to take a more individualized approach,” she says. That means family outreach centers on early intervention and consistent communication.
“We try not to wait until attendance becomes a major concern before reaching out. When we start noticing a pattern of absences or a decline in attendance, we make contact to try to better understand what might be contributing to the student’s absences and how we can support both the student and the family,” she says.
The program helped increase district-wide attendance from 62% in 2022 to 88% in 2026, with high school attendance climbing from 61% to 90%.
“We use several different methods of communication depending on what works best for each family. This might include phone calls, texts, emails, letters, or meetings,” she says. “The frequency of contact really depends on the individual student and their needs.”
For some, a single conversation and some additional support may be enough. For students with more significant or ongoing attendance concerns, “we increase communication and may have regular check-ins with students, attendance meetings, or develop an individualized attendance plan or contract,” she says.
Should a student’s absences increase, “families receive attendance letters at specific thresholds, including after five and 10 days of absence,” she says. “The 10-day letter also communicates the additional documentation requirements for future absences.”
Along with this general approach, “we also focus on creating positive motivation for students to want to attend school,” she said. At the junior high level, for example, Earlville Community Unit School District 9 offers the Not Being Absent (NBA) Attendance Incentive Program. “Students earn points for attendance as part of their homeroom team, which creates some friendly competition and gives students recognition for being at school,” Fahrlander says.
At the high school level, there are quarterly attendance incentive field trips for students who meet the attendance expectations.
“Overall, our goal is to combine positive motivation for all students with more individualized support for students who are at greater risk,” she says. “In a small, rural district, it is often easier to notice when a student starts to struggle with attendance because our staff know the students and families well. A student is not just a name or number on an attendance report.”
Reframe the Messaging
At Moline Coal Valley School District in Illinois, a small district serving about 7,300 students across 15 schools, Deputy Superintendent Brian Prybil focuses on the content of the outreach. He encourages a positive tone, with an eye toward building trust.
“For example, I had one principal who intentionally worked on making personal phone calls to the parents,” he says.
The calls were never scolding. “It was, ‘Hey, hope everything’s going OK. This is what Billy missed today,’ instead of building a punitive type message,” says Prybil, who is also the co-author of “Sixth Essential: A Playbook For School Leaders.”
There are many reasons for absenteeism, some of which schools can help families to address. With that in mind, Prybil says a key message in those calls is, “If you need anything, let us know.”
Teachers can support that effort. “The number one thing for teachers is to build trust with their students,” he says. “Not every day is going to be perfect. But we can invest in getting to know our students and letting them know that we’re all in this together.”
In high school in particular, “it’s really easy to blame kids” for not showing up, he says. But as long as they are present, teachers can “try to be positive with them, try to build that relationship and accomplish what you can accomplish with the time you have with them.”
Automated Routines
Automating the logistics around attendance frees staff to focus on those human conversations.
Chris Miller serves as director of attendance and student support at the North Central Ohio Educational Service, which supports schools in multiple rural districts. Previously, as an assistant principal at a high school, he was in charge of attendance, and it was a logistical nightmare.
“It was difficult to keep up,” he says. “Every day, kids are missing, and your report that you run on Monday, on Tuesday is outdated already. And we’ve got to do it again and again and again.” When manual tracking proved ineffective, he built an app, Attendance K12.
With help from technology, “we’ve curbed the time on figuring out the who, and now we can spend people’s time discussing with families about the why,” he says. “That’s where the rural districts really have an advantage, because those conversations often fall on the ears of people who are familiar with [school staff].”
Teachers play a key role: Technology can help to track and manage absenteeism, but educators are the front line of remediation.
Rather than just focusing on missed work when a kid returns to class, teachers should be focused on “creating an environment that is welcoming when they return,” he says. “By creating that space that feels comfortable, it eliminates some of that return-to-school anxiety that sometimes builds when they start stacking absences.”
Coordinating a Strategic Effort
At Stanfield Elementary School in rural North Carolina, instructional coach Jessica Dunn approaches attendance response as a coordinated endeavor.
Rather than one person handling it alone, “we’re involving administration, the counselor, the social worker,” she says, with those efforts based on timely reports from a data manager. “We do it as a team, truthfully.”
When the team goes into action, it focuses on addressing the factors that cause absenteeism in the first place. For example, the team sends home bags of food that a church partner provides. “That alleviates that stress for them, and our counselor does a great job of getting those bags out,” she says. With one less thing to worry about, “they can focus on getting the kids here.”
While attendance is always hard to manage, Dunn believes the nature of a rural community makes all this a little easier. Teachers, counselors, and administrators “know everybody, they can connect to them,” she says. In a rural community, or a small school, keeping attendance up “is all about support, connection, and relationships.”
Elon Musk has questioned the influence of Indian billionaire Mukesh Ambani as SpaceX struggles to launch its Starlink satellite internet service in the country. Musk’s comments, which were posted on X, escalate a dispute over regulatory delays after the Indian government rejected his claims that powerful business interests were blocking its entry.
Musk accused on Wednesday unnamed “oligarchs” of blocking Starlink’s launch in India to maintain what he called their “monopolistic chokehold” on the country, without identifying them or providing evidence for his claim. He called the alleged blocking a “crime against the people of India” and argued that Starlink could bring affordable, high-speed internet to people who lack internet access.
Hours later, India’s Ministry of Communications pushed back, saying its regulatory framework for satellite communications is “fair and non-discriminatory.” The ministry said in a statement that Starlink and two other licensed satellite operators are all at “broadly the same regulatory stage.” It added that all three companies are undergoing security assessments that must be completed before they can seek spectrum, the radio frequencies that satellites use to send signals.
Musk went further on Thursday, questioning the influence of Reliance Industries chairperson Mukesh Ambani.
”Is Ambani the real boss of India?” he wrote on X, after claiming that Starlink had spent years complying with Indian regulations and questioning why it still lacked a license.
Starlink has spent more than five years trying to enter India, a market with more than a billion internet subscribers. But it has yet to begin commercial services despite securing key regulatory approvals and partnering with telecom giants Reliance Jio and Bharti Airtel last year. SpaceX has also set up a local team as it prepares for a launch, appointing former Payoneer executive Prabhakar Jayakumar to lead its India operations in December.
Musk’s comments came hours after Lauren Dreyer, Starlink’s vice president of business operations, appeared at India Mobile Congress, a telecom industry conference in New Delhi and reiterated the company’s commitment to the market.
“We stand ready to serve India,” Dreyer said, adding that Starlink wants to help realize Prime Minister Narendra Modi’s goal of achieving universal connectivity across the country.
Starlink said it already has more than 20 gateway sites (the ground stations that link its satellites to the internet) and hundreds of antennas on the ground in India, and has adapted its operations to meet the country’s regulatory, security, and data-sovereignty requirements. Moreover, SpaceX has positioned its satellite network as a complement to — rather than a replacement for — India’s terrestrial telecom networks.
SpaceX first attempted to launch Starlink in India in 2021. The company, however, had to refund preorders for its equipment in early 2022 after the Indian government called it out for “booking/rendering the satellite internet service” before getting the necessary licenses.
Starlink has also previously clashed with India’s largest telecom operators over how satellite spectrum should be allocated. Starlink pushed for spectrum to be assigned administratively, while Reliance Jio argued that it should be auctioned — a position that could have made Starlink’s entry more expensive. India ultimately sided with Starlink’s preferred approach, deciding to allocate satellite spectrum administratively rather than through an auction.
Jio and Airtel, India’s two biggest telcom operators, are also pursuing their own satellite internet services, even as they have agreed to distribute Starlink in India. Jio is working with satellite operator SES on satellite broadband, while Airtel is a major backer of Eutelsat OneWeb, another licensed satellite operator in India.
While the timing of Starlink’s India launch remains unclear, the company this week launched Starlink Mobile, which connects ordinary phones to satellites, in neighboring Bangladesh.
Starlink, India’s Ministry of Communications, Reliance Jio, and Bharti Airtel did not immediately respond to requests for comment.
Update: This article was originally published at 11:14 p.m. PDT and has since been updated to include Musk’s comments questioning Reliance Industries chairperson Mukesh Ambani’s influence in India.
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

The company employs more than 2,000 in its Dublin tech hub.
Mastercard is opening a second office at its Leopardstown campus tech hub in Dublin alongside announcing a number of commitments to expand its payments infrastructure in Europe.
The new building was officially opened today (8 October) by Taoiseach Micheál Martin, TD. It comes two decades after the company first established a base in the country. Since 2008, Mastercard’s workforce has grown from 36 to more than 2,000 in Dublin.
Mastercard is also committing to expand critical payments operations in Europe, with plans to bring in all components of local transactions into Europe by 2030. It already processes domestic transactions in France, Germany and Spain through its new European infrastructure.
The payments giant also said that all new Mastercard European credit and debit cards issued from next year will support offline payments.
A number of European countries, including Finland, Sweden, Norway, Denmark and Estonia, are rolling out offline payments in the region in response to heightened geopolitical tensions in the region as banks act to ensure payment infrastructure continues to work in case of an internet blackout.
“The opening of Mastercard’s new office is a strong endorsement of Ireland’s reputation as a leading location for innovation, technology and digital transformation,” said Taoiseach Martin.
“Mastercard has played a key role in shaping the future of payments and financial technology globally, and its continued expansion in Ireland highlights the strength of our talented workforce, pro-business environment and vibrant technology ecosystem.
“I warmly welcome this investment and look forward to seeing Mastercard continue to innovate and grow from its Irish base in the years ahead.”
Ed McLaughlin, the president and chief technology officer at Mastercard added: “From AI and cybersecurity to next-generation payments infrastructure that brings greater resilience and speed to commerce, the work happening here is helping build the future.
“This expansion of our European tech hub reflects the growth of our teams in Dublin, our confidence in Ireland’s talent, and our ambitions for the years ahead.”
Don’t miss out on the knowledge you need to succeed. Sign up for the Daily Brief, Silicon Republic’s digest of need-to-know sci-tech news.
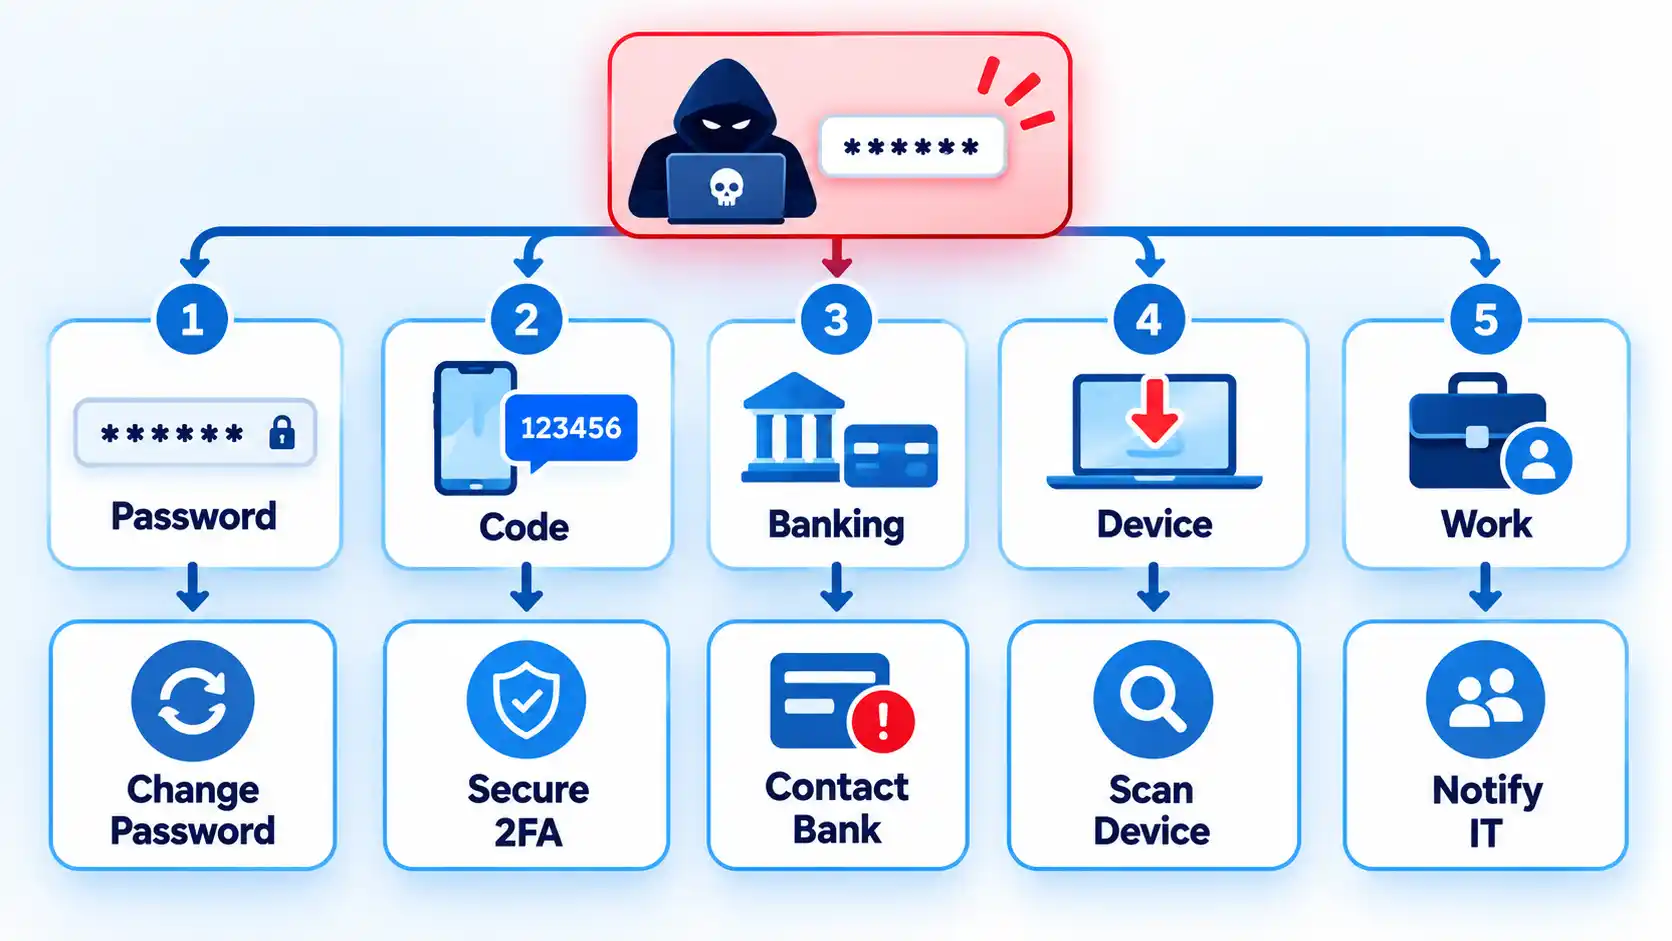
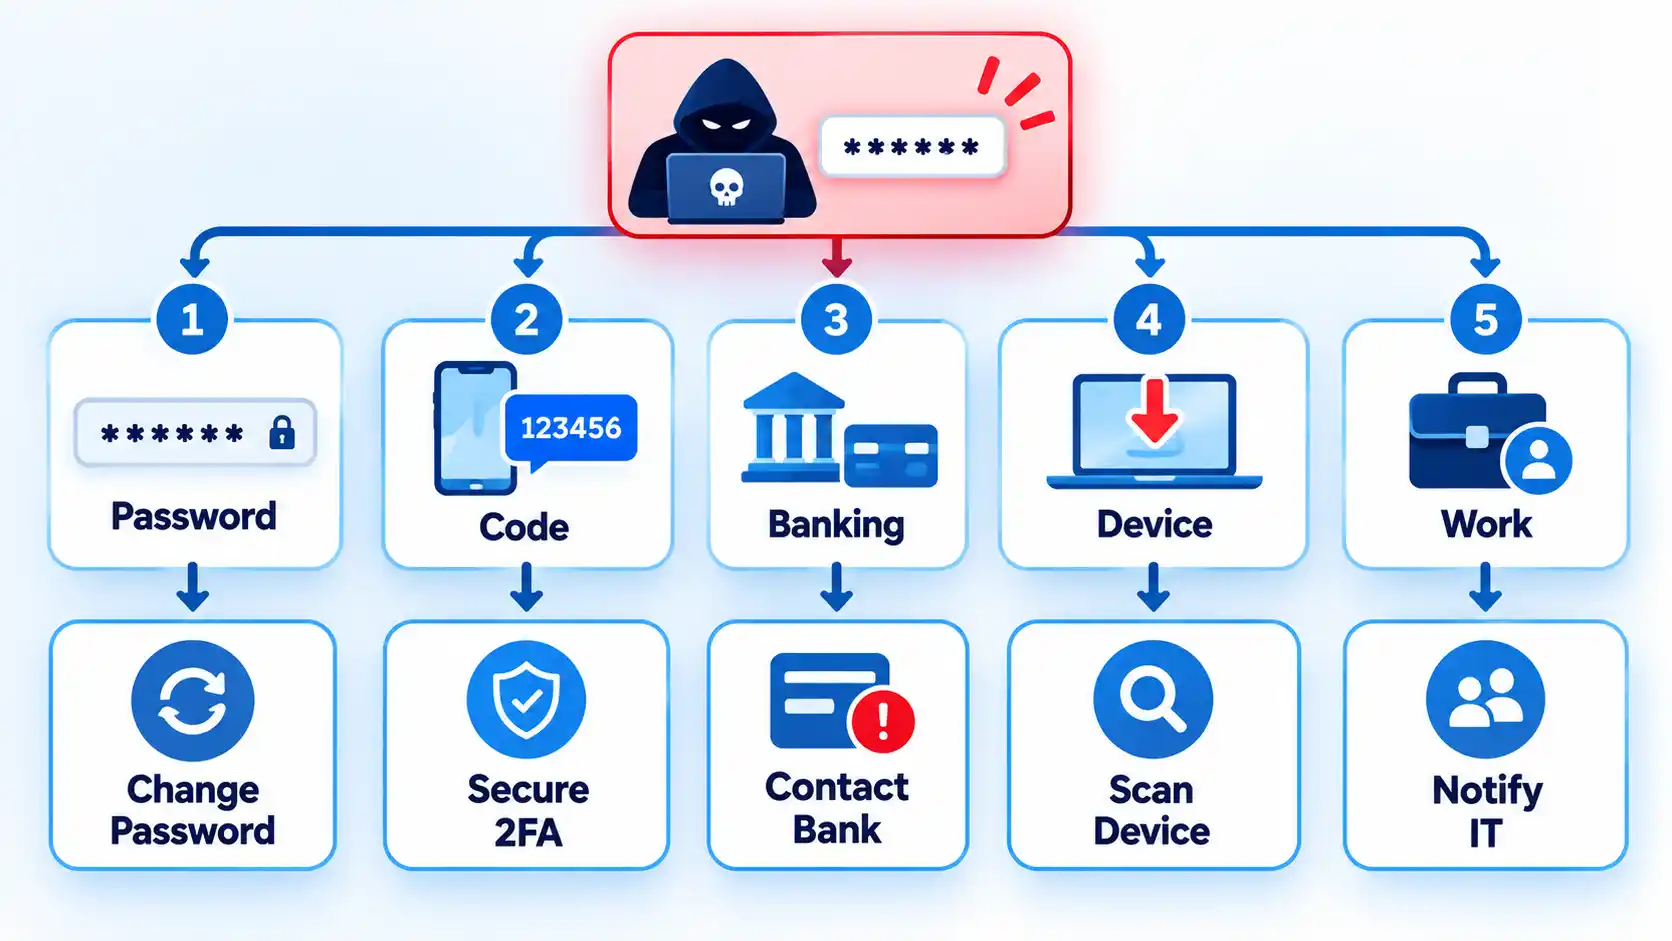
If you entered your password on a phishing site, treat that password as exposed even if you have not seen any suspicious activity yet. Leave the fake page, open the real service independently, and secure the account before checking what else may have been affected.
Quick Take
Change the exposed password through the real service, replace the same password anywhere else you used it, end unfamiliar sessions where the service allows it, check recovery details, and enable two-factor authentication. If you are already locked out, use the provider’s official account-recovery process instead.
What to Do After Entering Your Password on a Phishing Site
Start with the account whose password you entered. The exact menus differ between services, so use the provider’s real website or app rather than returning through the phishing message or page.
If you also installed suspicious software, gave someone remote access to the device, or followed instructions that may have compromised the device itself, deal with that device exposure before relying on it for sensitive account recovery. The FTC’s response for computer or phone access puts security-software updates and a scan before password changes.
Warning
Do not go back to the phishing page to change your password, confirm your identity, enter another code, or follow a supposed security link. Reach the real service independently.
- Leave the phishing page and open the real service. Close the suspicious page or message. Open the service from an app you already trust, a saved bookmark you know is genuine, or an address you verify independently. This prevents the attacker from collecting another password or verification code while you try to recover.
- Change the password if you can still sign in. Create a new password that you have not used on another account. We advises people who gave a scammer their account credentials and can still log in to replace the compromised password. Do not simply add a character to the exposed password or switch back to an older password that you have used before.
- Use official account recovery if you are locked out. If the real password no longer works, or the recovery phone number or email has been changed, use the provider’s own account-recovery process. Google, for example, directs users to its account recovery process if someone changed the password or recovery phone number, or if the user cannot sign in for another reason.
- Replace the same password on your other accounts. Password reuse turns one exposed credential into a risk for several services. We specifically advises changing the password on any other account where you used the same password. Prioritize your primary email and other important accounts because access to one service can sometimes help an attacker reach others.
- End sessions you do not trust. Many services provide a security page showing signed-in devices or active sessions. Review the controls your provider offers and remove access you do not recognize. Google, for example, lets users inspect recently signed-in devices and sign out unfamiliar devices or sessions. Changing a password and signing out active sessions address different routes an attacker may use to remain connected.
- Check your recovery information and account settings. Confirm that recovery email addresses, phone numbers, and other recovery methods still belong to you. If the affected account is email, also inspect forwarding rules and filters for settings you did not create. I will recommend checking recovery information after regaining control and removing email-forwarding rules you did not set up.
- Turn on two-factor authentication. Two-factor authentication, often shortened to 2FA, means the account requires two different kinds of proof when you sign in rather than relying on the password alone. The FTC notes that even someone who knows the username and password cannot complete a protected sign-in without the second authentication factor. Use a method the service supports and that you can recover safely if you lose your usual device.
Check for Signs the Account Was Used
Typing a password into a phishing page makes that password unsafe, but it does not by itself prove that the attacker successfully signed in. After securing the credential, look for evidence that somebody actually used the account.
- Unfamiliar devices or sessions: review the provider’s security or sign-in activity for devices, browsers, or sessions you do not recognize. Check the surrounding details before removing access because one physical device can sometimes create more than one session.
- Unexpected security alerts: look for notices about sign-ins, password resets, new devices, recovery changes, or other security events you did not initiate.
- Changed recovery details: confirm that recovery phone numbers, email addresses, security methods, and similar account controls still belong to you.
- Messages or posts you did not send: check sent mail, social-media messages, posts, and other outgoing activity. Unauthorized messages are a practical sign that someone may have used the account.
- Email forwarding or filtering you did not create: an attacker with email access may create rules that forward messages elsewhere or hide security and password-reset emails from your normal inbox.
- Purchases or service activity you do not recognize: check account-specific history where relevant, such as orders, subscriptions, payment activity, cloud files, or profile changes.
Google’s device history is one example of why account activity needs context: several sessions can belong to the same device, so inspect the details before deciding whether an entry is unfamiliar. If you find unauthorized activity, follow the provider’s security or recovery process and remove access where that control is available.
Broader signs that someone logged into your account can include security-setting changes, unfamiliar devices, and actions performed without your permission. If you need to investigate beyond the affected account, these signs your data has been compromised provide a wider audit of account, email, financial, and breach indicators.
What If You Shared More Than a Password?
A phishing incident can collect more than one type of information. Do not automatically perform every recovery action below. Identify what the site actually received or what you did on the device, then follow the matching branch.
| What was exposed | What it changes | First response |
|---|---|---|
| Password only | The password may be used against that account or other accounts where you reused it. | Complete the account-recovery procedure above, including password replacement, session review, recovery checks, and stronger authentication. |
| One-time code or sign-in approval | The attacker may have obtained the additional proof needed for a sign-in or another protected account action. | Review recent security activity immediately, remove unfamiliar access where possible, and use the provider’s recovery or security process if you see activity you did not authorize. If you shared a phishing verification code, do not assume that changing the password alone reverses whatever the code may have authorized. |
| Bank or card details | The incident may also involve financial fraud rather than only account access. | Contact the bank immediately through a channel you obtain independently from the phishing message or page. |
| Government ID or other identity document | An identity document cannot be protected by changing an online password. | If you uploaded an ID to a scam website, preserve evidence and follow the document-specific recovery steps for the ID and any other information the site received. |
| Downloaded file, installed software, or device access | The device itself may be at risk in addition to the account. | If you installed suspicious software or gave someone access to the device, update trusted security software and run a scan before relying on the device for further sensitive work. I recommend scanning a computer or phone after giving a scammer access. These steps for situations where you downloaded or ran suspicious software cover the broader malware response. |
| Work or school account or device | The incident may affect organization-managed email, files, applications, or other resources as well as the individual account. | If the phishing happened on a work device, contact the organization’s IT team and explain what happened. Also follow your employer’s or school’s incident-reporting process when one exists. |
A password-only incident does not automatically mean your device has malware, your bank details were stolen, or your identity documents were exposed. The response should expand only when the phishing interaction or later evidence shows another type of exposure.
How to Know the Account Is Secure Again
The immediate account-recovery phase is complete when you have addressed the realistic routes an attacker could still use. That does not prove nobody viewed or copied information while the password was exposed.
Verify the result
- The affected account now uses a new password that is not reused on another service.
- Every active account that used the exposed password has been changed or otherwise secured.
- You can access the genuine account normally, or you have entered the provider’s official recovery process if access has not yet been restored.
- Recovery email addresses, phone numbers, and other recovery methods are yours and have not been replaced by unfamiliar details.
- Unfamiliar sessions or devices have been signed out where the provider gives you that control.
- Unauthorized forwarding rules, filters, messages, posts, or other account changes found during your review have been removed or corrected.
- Two-factor authentication is enabled where the account supports it, and you can still access the recovery method for that second factor.
- If the incident also involved suspicious software or device access, that device has entered the appropriate scan or remediation process before you rely on it for sensitive activity.
- Any other exposure, such as banking information, an ID document, a verification code, or work credentials, has moved into its appropriate recovery process.
Continue watching security notifications and account activity after the immediate cleanup. If new unauthorized activity appears, use the provider’s official security or account-recovery process rather than returning to the phishing message.

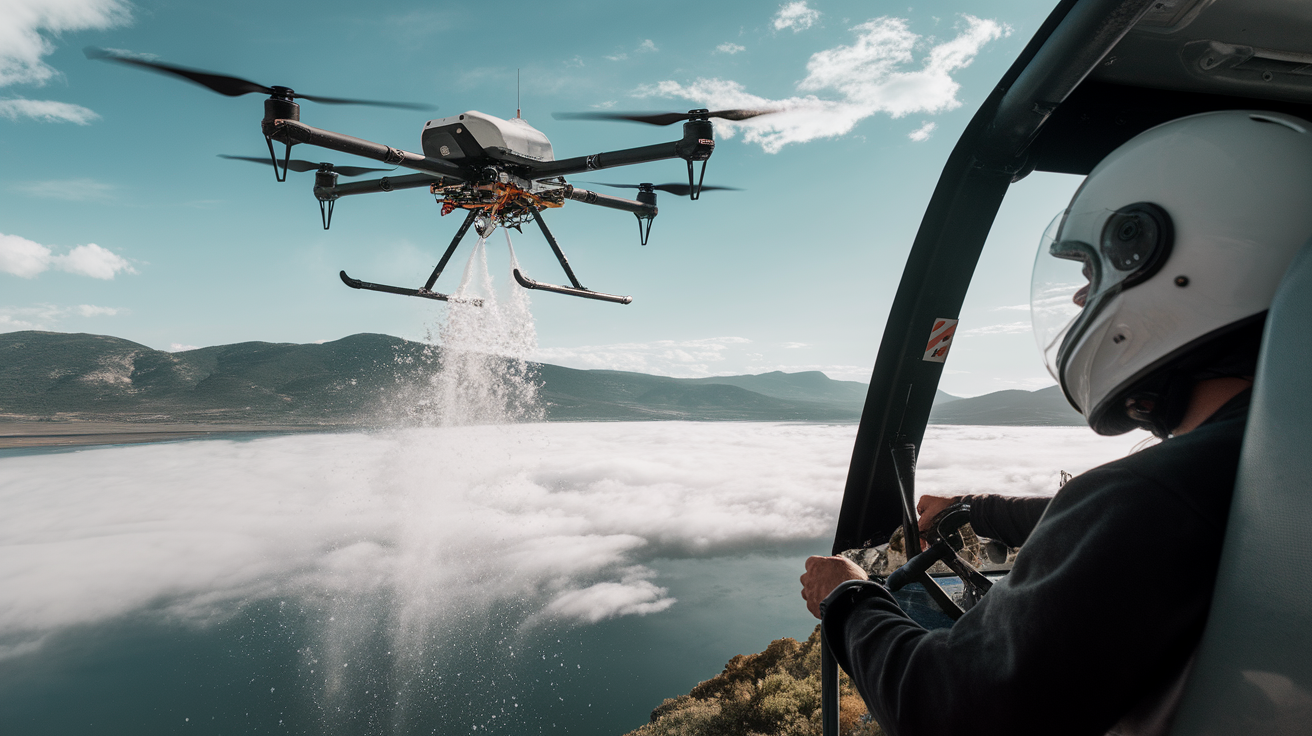
Thousands of residents in Homer, Alaska had no idea the clouds above their homes were being seeded this past August. A San Francisco start-up called Rainmaker had quietly sent cloud seeding drones into the sky, dispersing a silver compound meant to trigger precipitation, and claims the three-hour operation produced 19 million US gallons of water. Most locals only found out after the fact.
The episode has become a flashpoint in a debate that is unfolding across more than 50 countries now experimenting with weather modification: can technology meaningfully ease water shortages, and should companies be allowed to alter the sky over people’s homes without clearly telling them first?
How Cloud Seeding Drones Work
Cloud seeding itself is not new. The technique dates back to 1946, when scientists at General Electric’s research laboratory first used dry ice to coax rain from clouds. Silver iodide followed a year later and proved far more effective, since dry ice evaporates into gas too quickly to be useful. The chemistry speeds up a natural process: compounds dispersed into a cloud form ice crystals, which grow heavy enough to fall as rain or snow once gravity takes hold.
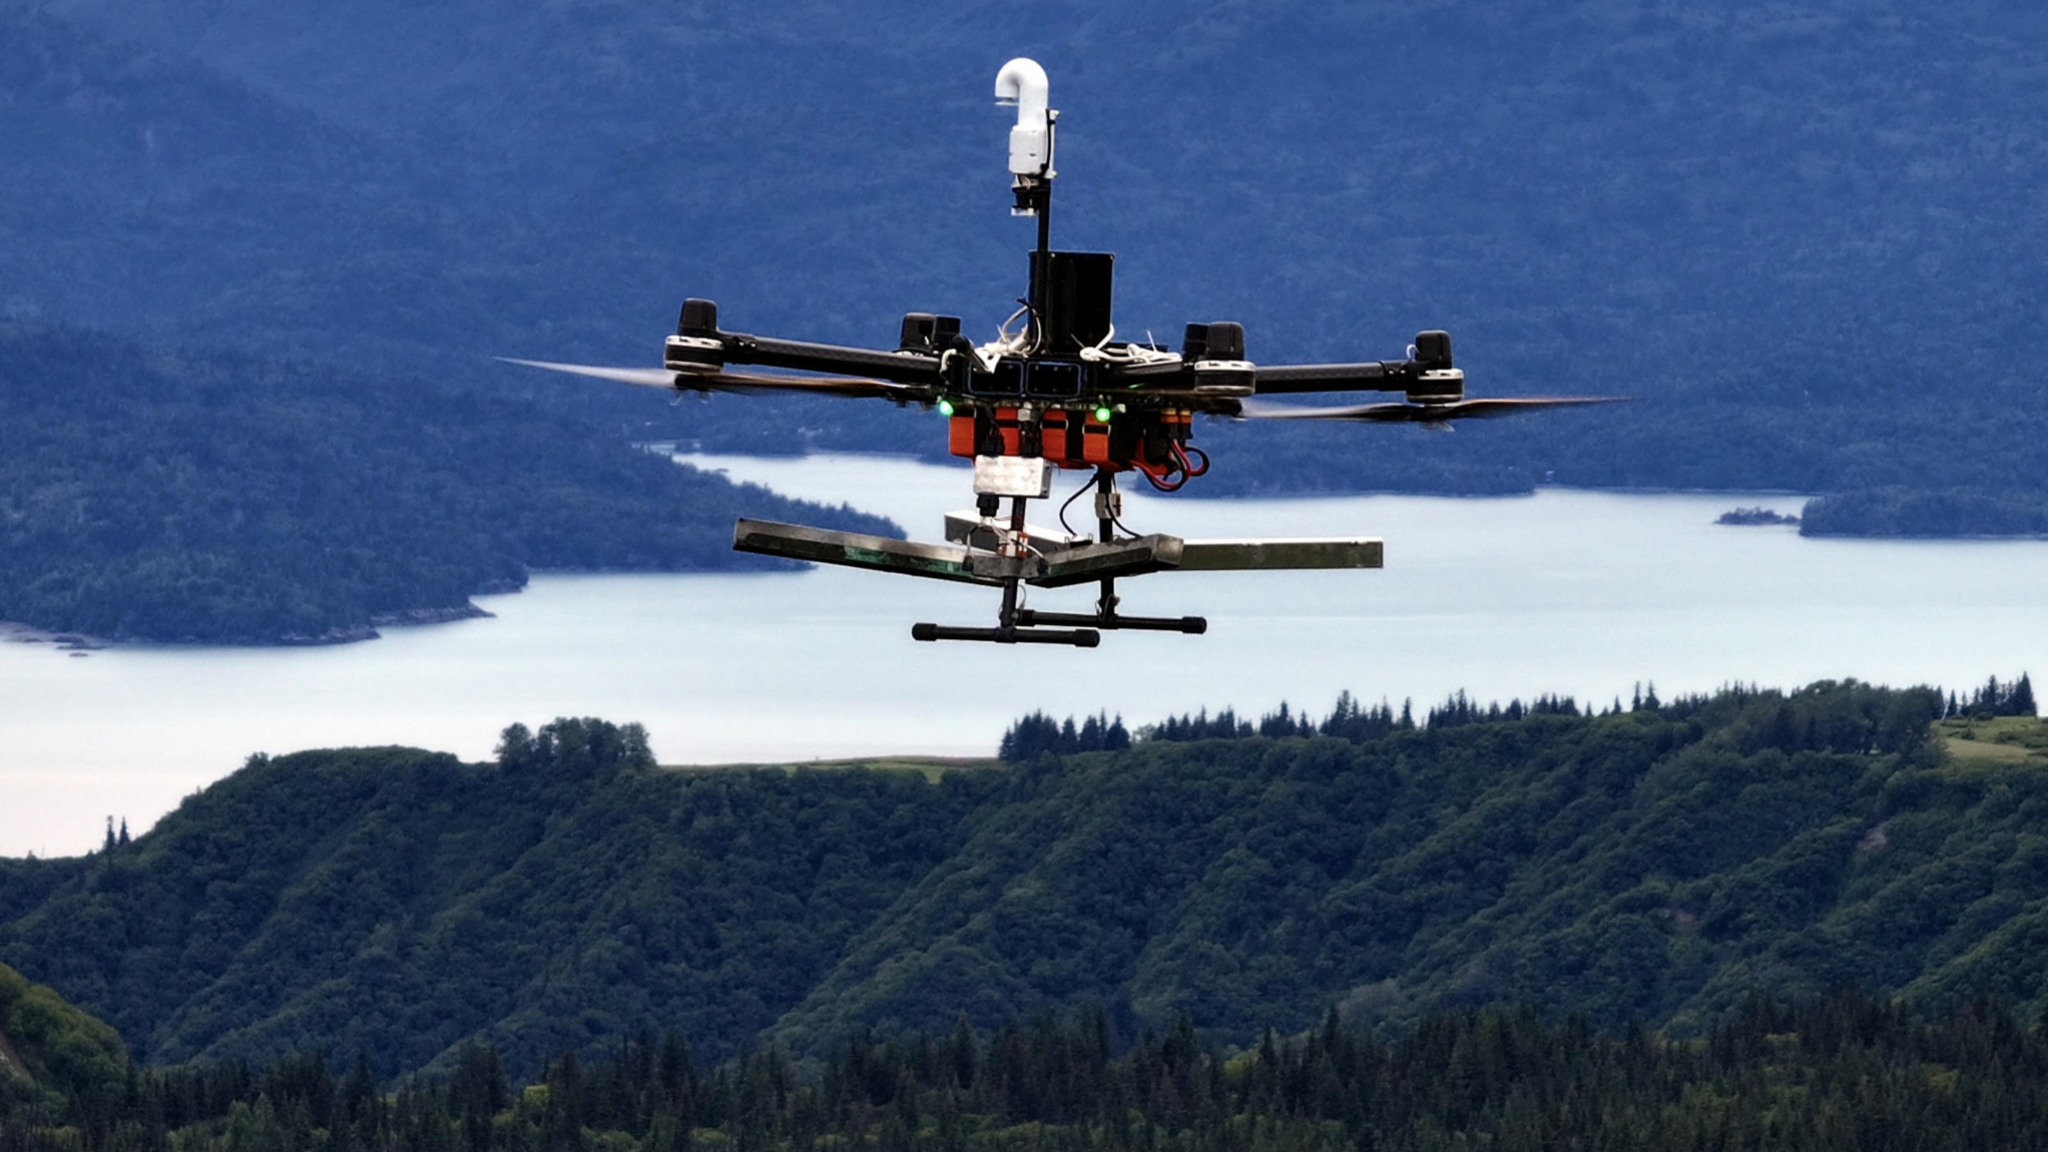
What has changed is the delivery method. Instead of relying solely on piloted aircraft, companies like Rainmaker now use autonomous cloud seeding drones to fly directly into storm systems, releasing silver iodide flares that burn and atomize water particles so they stay suspended in freezing air long enough to form crystals. Rainmaker founder and CEO Augustus Doricko says each flight releases just 20 grams of silver, spread across thousands of square kilometres, resulting in ground concentrations he describes as “parts per quadrillion” — far below thresholds set by the US Food and Drug Administration.
The drones give operators a more surgical approach than older methods. “They offer a more targeted nature to these clouds we hope will be responsive,” says Jon Meyer, an assistant state climatologist at the Utah Climate Center, who has watched the technology evolve from a niche academic curiosity into a growing commercial sector. Rainmaker already operates across Idaho, Utah, Colorado and parts of the Middle East, including Jordan, where Doricko says chronic water scarcity leaves residents with utility water only a few hours a week.
Modest Gains, Bigger Questions
Even enthusiasts concede that cloud seeding drones are no silver bullet. Meyer notes that under ideal conditions, seeding might squeeze out an extra 5 to 10 percent of precipitation — a meaningful boost in drought-stricken regions, but nowhere near enough to manufacture a downpour from clear skies. Rainmaker’s own Alaska results illustrate the limits: 19 million gallons sounds dramatic, but spread across 100 square miles it amounts to roughly 0.01 inch of rain.
A 2017 study using radar and precipitation gauges offered some of the first solid evidence that silver iodide seeding behaves as scientists predicted, lending credibility to a field that had long struggled to prove its effectiveness. That research, combined with advances in drone technology, has helped fuel a wave of new start-ups chasing contracts from governments and utilities desperate for more reliable water supplies.
But not everyone is convinced the benefits outweigh the risks. Cooper Freeman, Alaska director of the Center for Biological Diversity, says he’s troubled that Homer residents were not clearly warned before the Rainmaker operation, and he questions whether anyone tracked what happened to the silver iodide after it fell. “It doesn’t appear that there was any downstream monitoring to verify that this silver iodide didn’t impact the environment,” he says. He also worries that pouring money into cloud seeding drones distracts from the harder, less glamorous work of conserving water in the first place. “Having a company come in to do this seeding isn’t going to solve our water woes,” Freeman argues.
A Thirsty Planet, A Growing Industry
The stakes behind this debate are considerable. United Nations Secretary-General António Guterres warned in July that the world is using freshwater faster than it can be replenished, and separate research has found the past five years to be the driest stretch for global rivers in more than three decades. Against that backdrop, it’s little surprise that governments from the American West to the Middle East are willing to experiment with any technology that might coax a bit more rain from the sky.
Some companies are even rethinking the chemistry involved. Recast Systems, another San Francisco venture, is testing a protein-based alternative to silver iodide, hoping to sidestep environmental concerns altogether while still triggering ice formation inside clouds.
Whether cloud seeding drones ultimately become a serious tool against water scarcity or remain a marginal, controversial experiment likely depends on two things: whether the modest rainfall gains prove worth the cost and regulatory headache, and whether companies can convince both scientists and the public that what they’re spraying into the sky is genuinely safe. For now, residents like those in Homer are left asking a more basic question — not whether the technology works, but whether anyone plans to tell them before it’s used over their heads again.
Sources:
Explore more on this topic with Vexel Search.

Google has released Chrome 155 with support for decoding JPEG XL images, a format that offers 30-50% better compression than JPEG along with lossless compression, JPEG transcoding, HDR, animation, and progressive decoding. From a blog post: We expect that JPEG XL is most helpful for high-fidelity or lossless compression, especially of photographic images or in cases in which fine-grained progressive decoding is preferred. In this post, we share why we brought JPEG XL to Chrome, how we used Rust to ensure memory safety first, the extensive performance work that makes it fast, and what the journey tells us about developer feedback and the web standards ecosystem.
[…] With JPEG XL officially landing in Chrome, the web becomes faster, richer, and safer. We encourage developers, content creators, and platform owners to start using .jxl images and animations in their pipelines. Try it out, file bugs, and help us continue building a faster and safer web for everyone.


Read more of this story at Slashdot.

Tech & AI19 minutes ago
Sony ECM-AX10 Spatial Audio Microphone Adds Eclipsa Audio Support for Smartphone Creators
Sports53 minutes ago
Asiad selection row: Para-shooters allege corruption; PCI denies claims | Asian Games 2026
Entertainment59 minutes ago
10 Flawless Movies With the Cleverest Protagonists


-
 Fashion6 days ago
Weekend Open Thread: Veronica Beard
-
 Tech & AI3 days ago
Common Mistakes You Should Avoid When Using Foldable Phones
-
 Tech & AI6 days ago
Fireflies.ai Launches Fireflies Talk for Free, Unlimited Voice Dictation
-
 Tech & AI6 days ago
Excellent hardware badly hampered by too-small SSD
-
 Crypto7 days ago
NEAR Intents hacked days after freezing stolen Bitget funds
-
 Tech & AI7 days ago
Whatever AI Safety Is, It’s Not This
-
 Sports12 hours ago
Saracens’ Venter Brands Premiership Rugby ‘Autocratic’ Over £5,000 Media Fine
-
 Tech & AI6 days ago
Mystery AMD Chip “Gainsborough” Fuels Steam Deck 2 Speculation — But Don’t Get Too Excited Yet
-
 Tech & AI7 days ago
Can Schools Trust AI Features in Edtech Products?
-
 Gaming6 days ago
Reigns Studio Nerial Shuts Down as Founders Step Back “To Our Roots”
-
 Tech & AI6 days ago
Sony’s new PS5 Pro lottery requires 60 hours of playtime just to apply
-
 Crypto7 days ago
Bitcoin edges higher ahead of U.S. jobs report as global bond yields surge
-
 Tech & AI5 days ago
Koreans Left With Spoiled Food Due To Borked Samsung Firmware Update For ‘Smart’ Fridges
-
 Entertainment6 days ago
Russo Brothers Tease Very Surprising Ending for Avengers: Doomsday
-
 Business & Hustles5 days ago
Beyond Ozempic: Lilly and Novo Chase the Next Obesity Blockbuster With Amylin
-
 Entertainment6 days ago
From Horror Reboots to Soul Reinventions: This Week’s Entertainment Headlines
-
 Tech & AI5 days ago
Muse Creates Detailed Profiles of All Your Friends and Family
-
Tech & AI7 days ago
CDC Opens Up COVID Vaccine Procurement Without Explanation
-
 Gaming5 days ago
Sony’s Late-Stage Listening Tour on Physical Games Raises More Questions Than It Answers
-
 Tech & AI5 days ago
Apple Clamps Down on Mac Privacy Setting as AI Agents Raise New Security Fears
You must be logged in to post a comment Login